
Archived
selenium-wire
 wkeeling/selenium-wire
Extends Selenium's Python bindings to give you the ability to inspect requests made by the browser.
api-security-testinginformation-gatheringpenetration-testing+2
wkeeling/selenium-wireExtends Selenium's Python bindings to give you the ability to inspect requests made by the browser.
 nccgroup/argumentinjectionhammer
A Burp Extension designed to identify argument injection vulnerabilities.
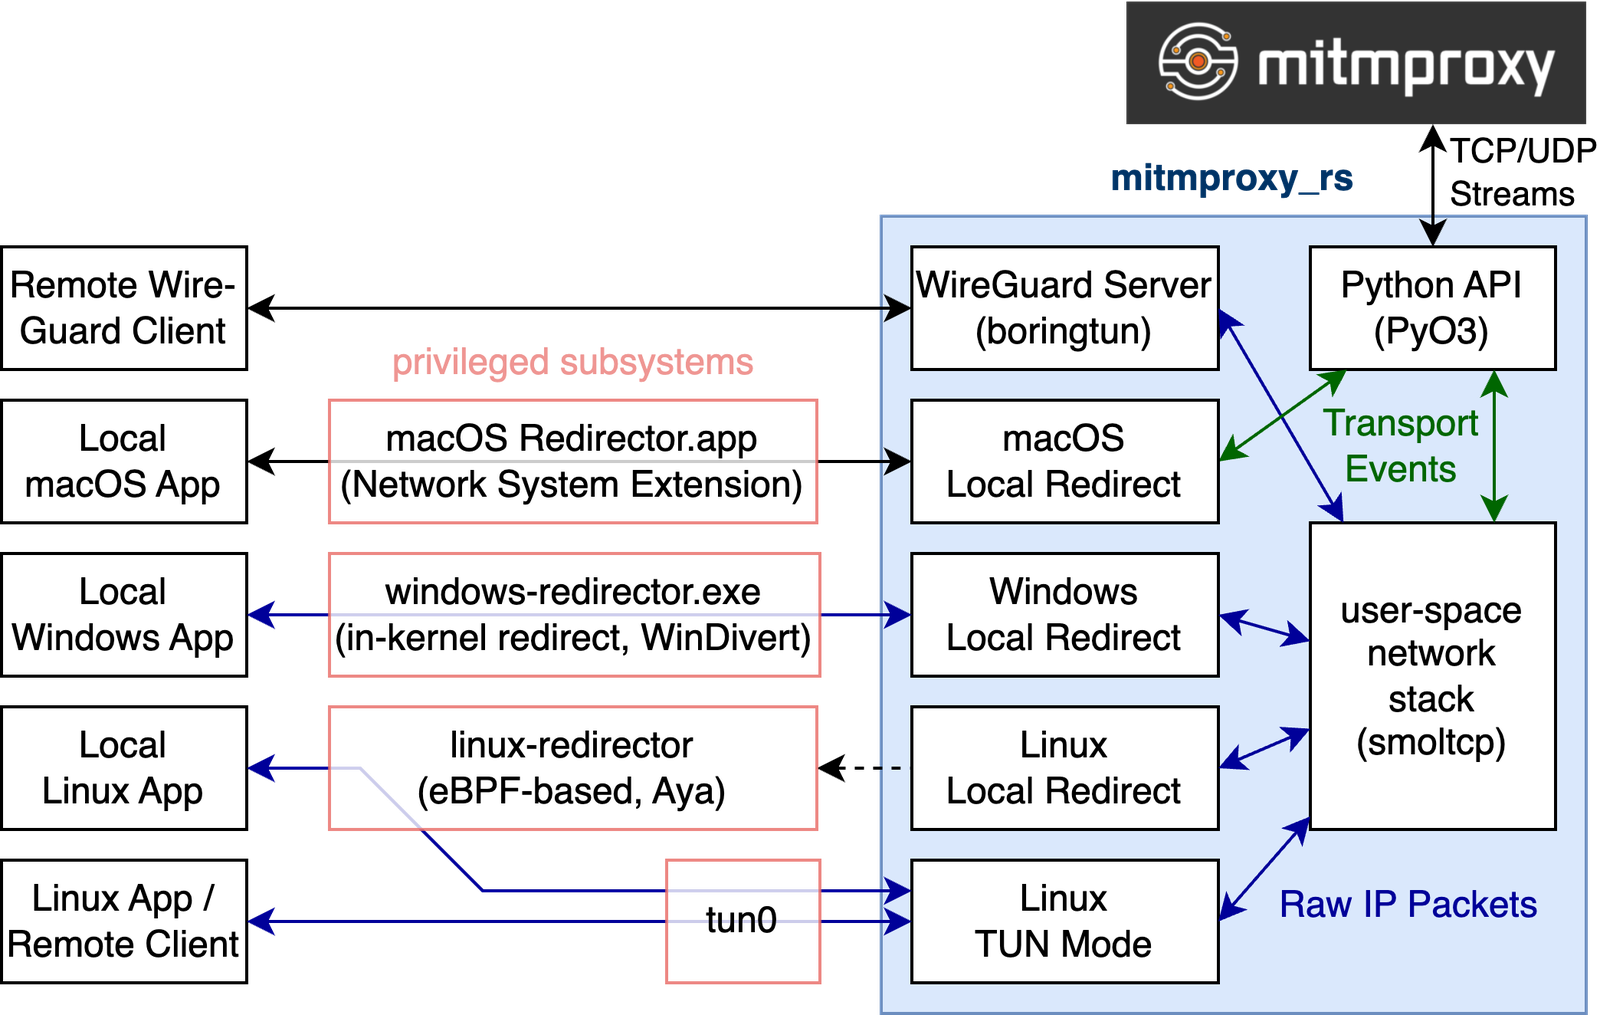 mitmproxy/mitmproxy_rs
Rust components for traffic interception and redirection, enabling WireGuard device proxying and local app redirection across macOS, Windows, and…
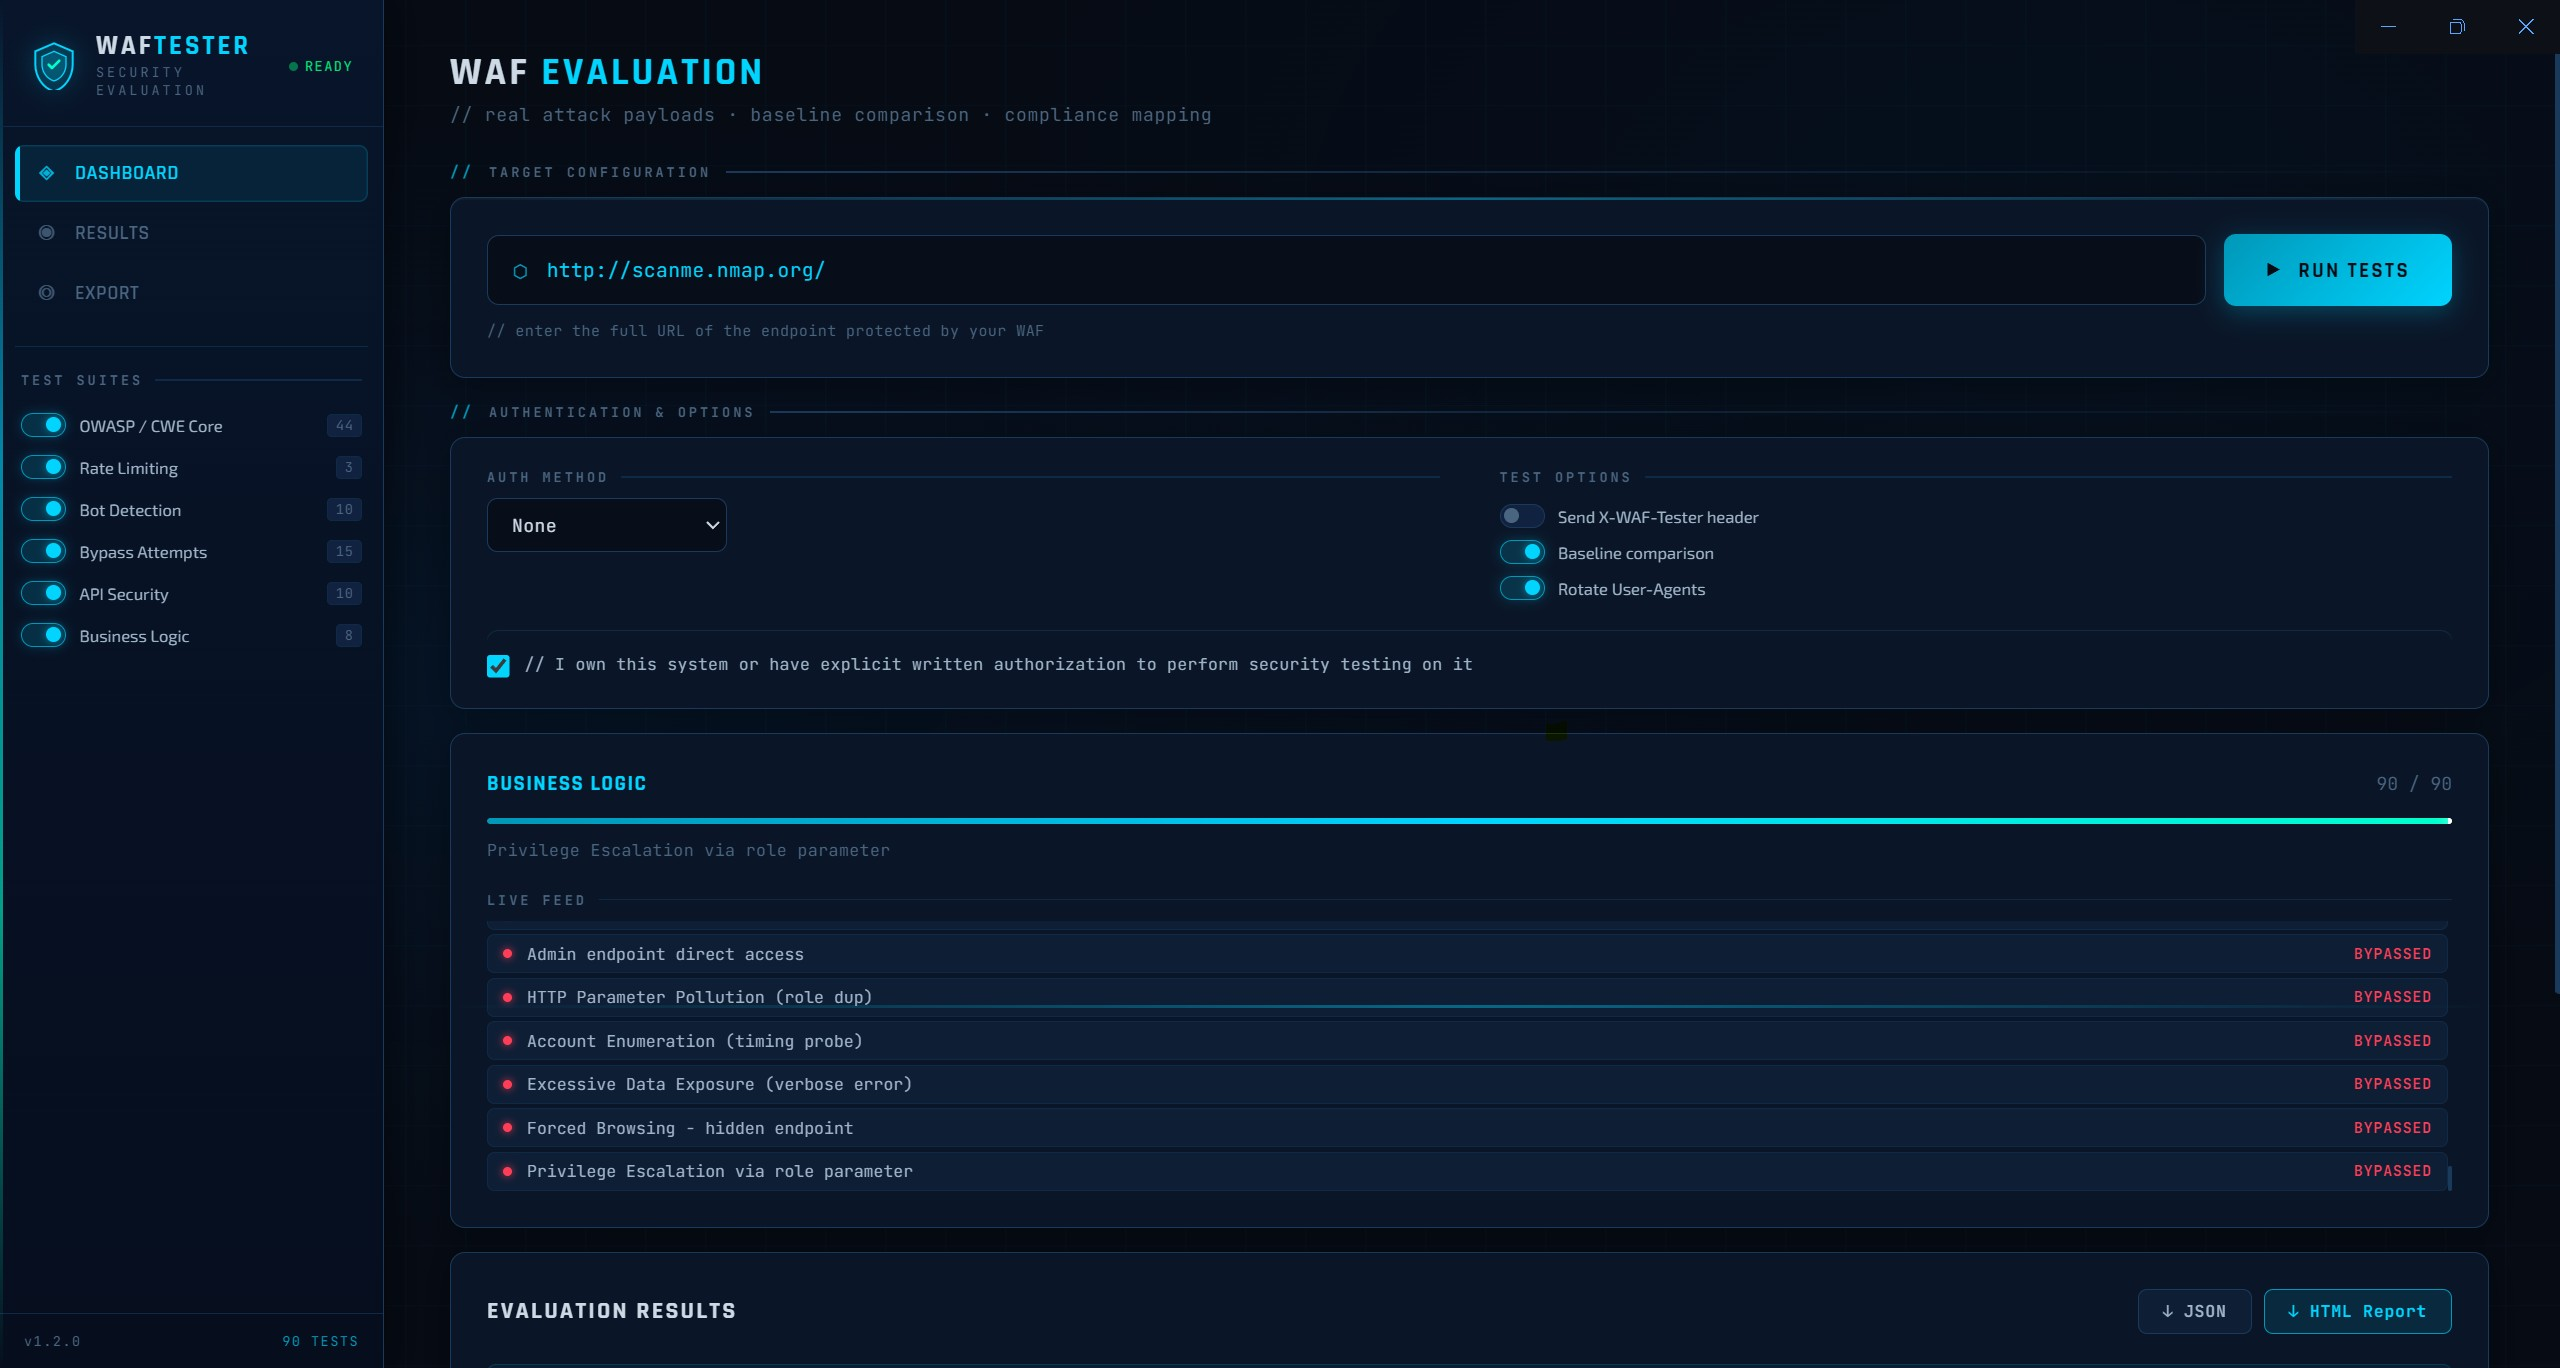 kpomin57/waf-tester
A program for testing WAF functionality
 owasp/offat
Automated API security testing tool that generates tests from OpenAPI specs, fuzzes inputs, and checks for OWASP API Top 10 vulnerabilities including…
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
 digeex/raider
DEPRECATED, please use the new repository from OWASP: https://github.com/OWASP/raider
 owasp/crapi
Deliberately vulnerable microservices API designed for hands-on training in the OWASP API Security Top 10 risks, with built-in challenges and a…
 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 zilbonn/owasp-wstg-rag
OWASP Web Security Testing Guide RAG system with ChromaDB, MCP for Claude Code
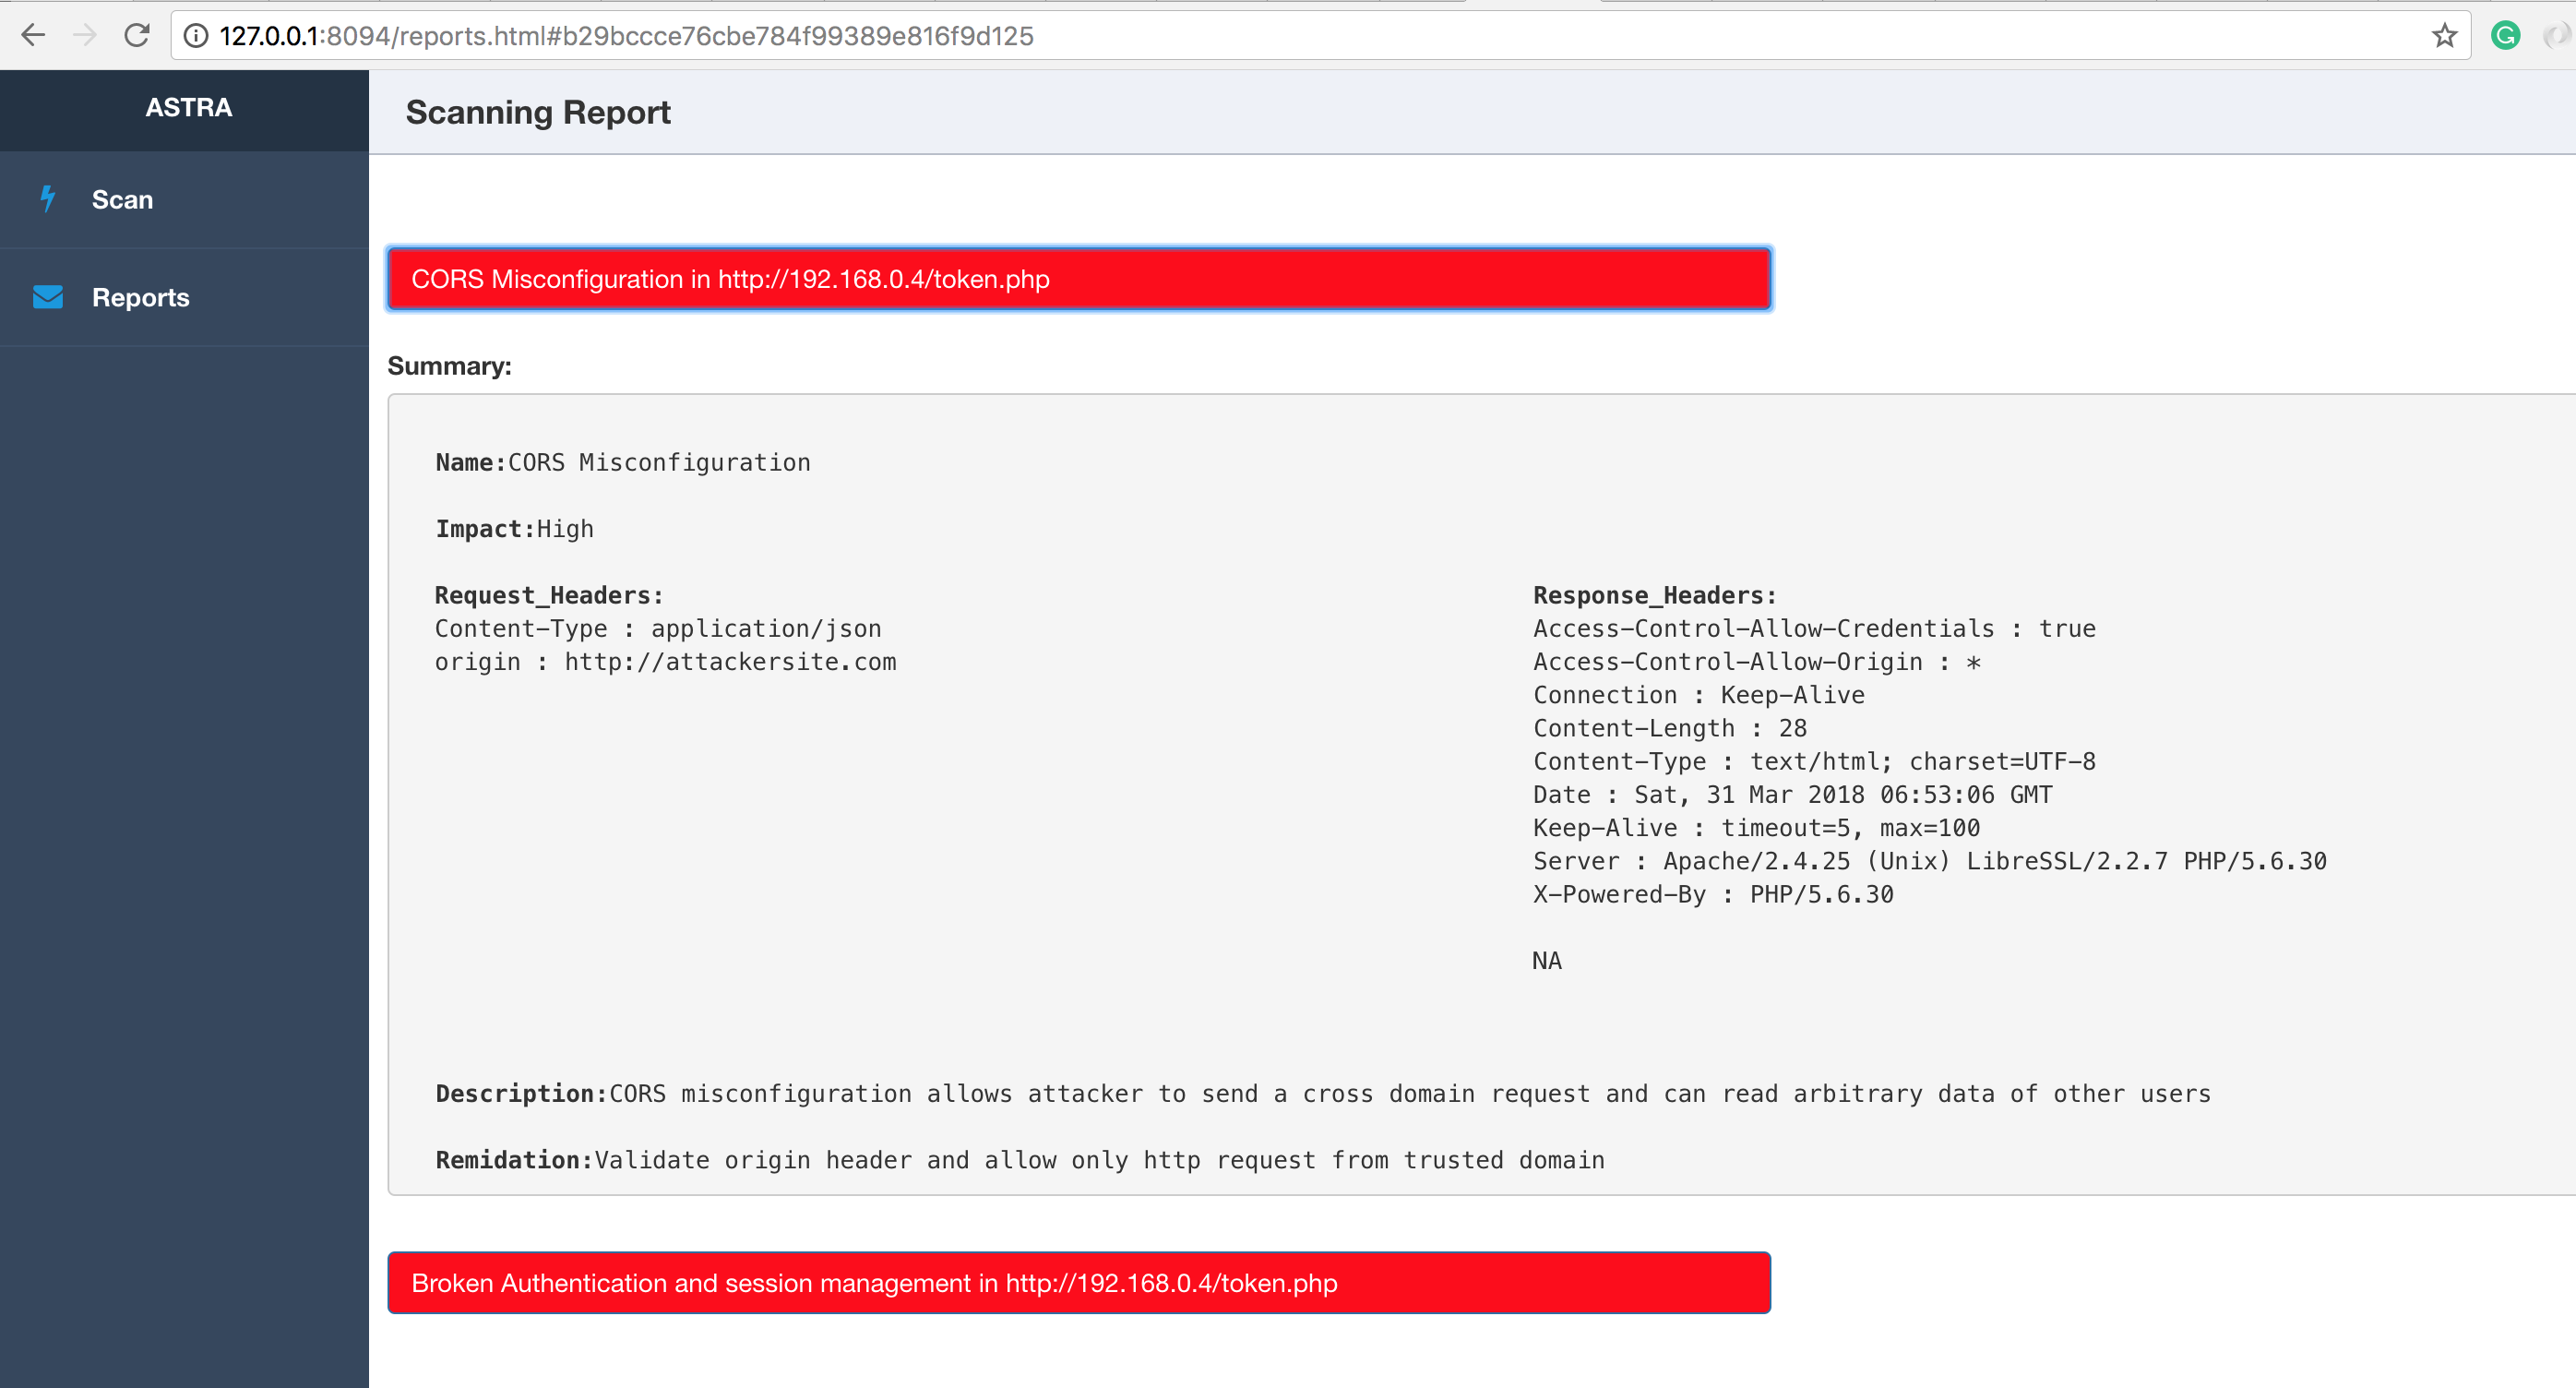 flipkart-incubator/astra
Automated Security Testing For REST API's
 owasp/dvsa
a Damn Vulnerable Serverless Application
 owasp/apicheck
Modular DevSecOps toolset for REST API security testing, designed for developers, sysadmins, and penetration testers to automate security checks…
 dipjyotimetia/hybridtestframework
End to End testing of Web, API, Cloud, Events and Security
 keygraphhq/shannon
Shannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes…
 silentchainai/silentchain
AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 httptoolkit/httptoolkit
HTTP Toolkit is a beautiful & open-source tool for debugging, testing and building with HTTP(S) on Windows, Linux & Mac :tada: Open an issue here…