reburp
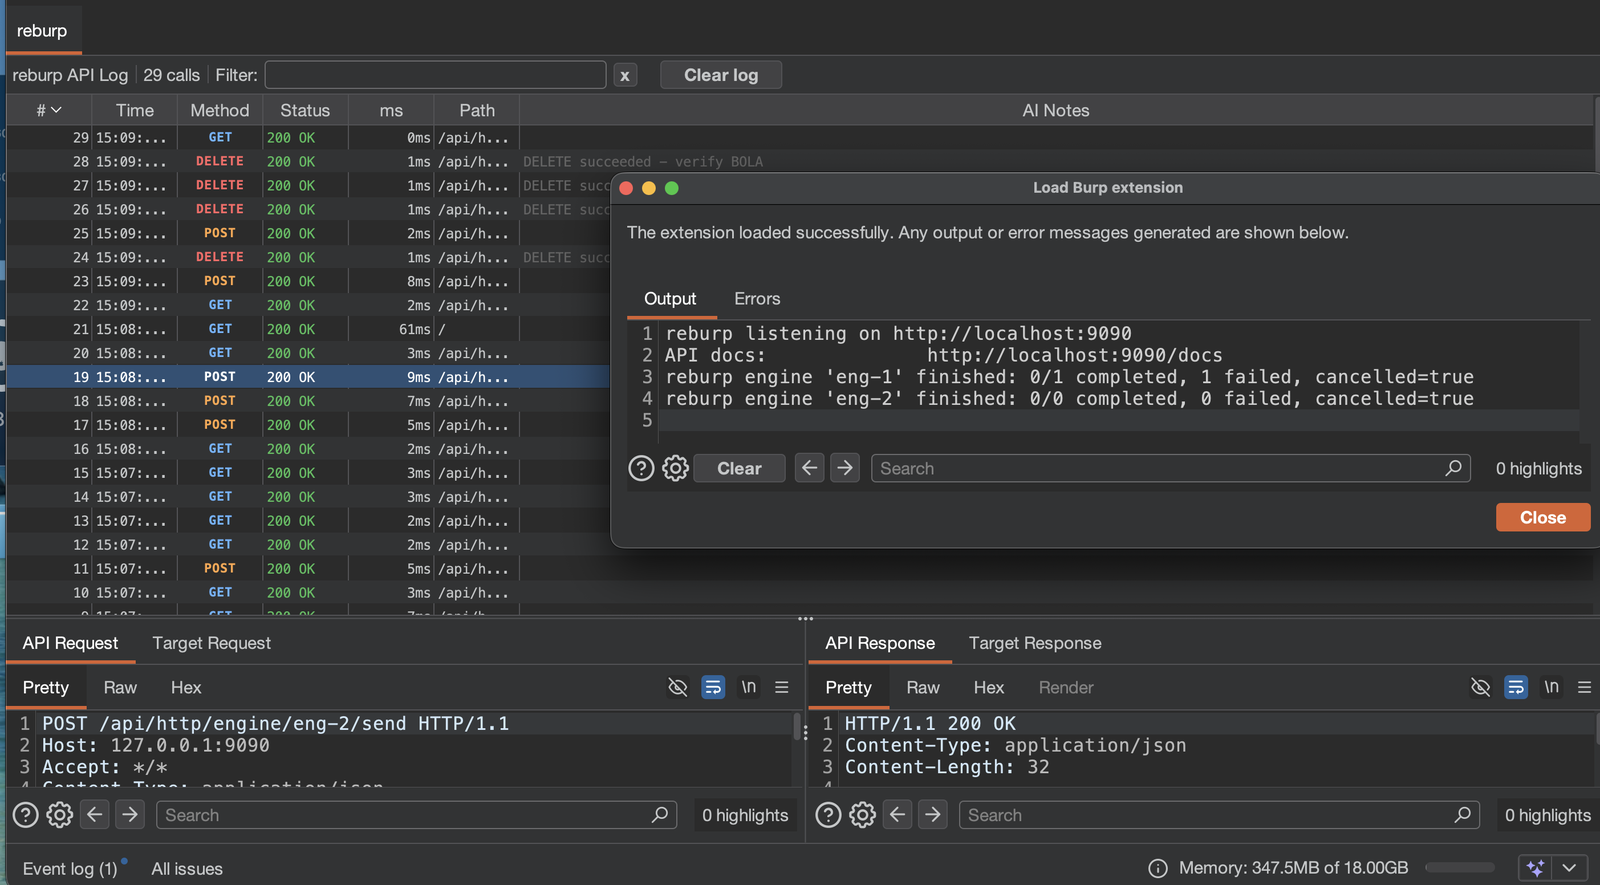
 forefy/reburp
A Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI
ai-securityapi-security-testingfuzzing+7
forefy/reburpA Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI
 weirdmachine64/redom
A Burp Suite extension that brings full DOM rendering capabilities directly into Burp, enabling effective security testing of modern JavaScript-heavy…
 cspf-founder/api-scanner-docker
Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …
 7h30th3r0n3/cve-2026-53625-glpi-poc
GLPI Privilege Escalation via authtype Manipulation PoC - CVE-2026-53625. Ethical PoC for the GLPI vulnerability allowing a Technician to take full…
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
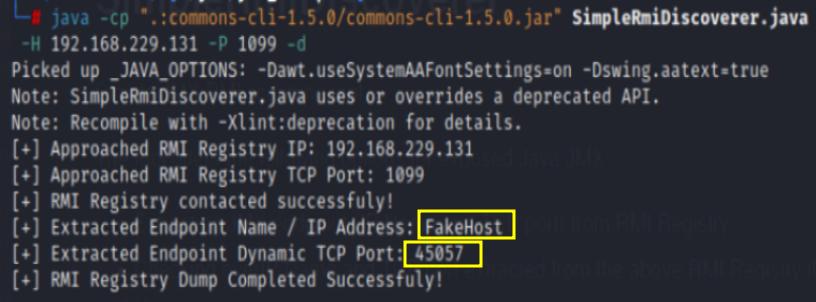 marcin-wolak/simplermidiscoverer
Simple JMX RMI scanning tool
 zavisco/cve-2026-64849.yaml
Detects unauthenticated MLflow webhook SSRF (CVE-2026-64849) that accesses internal or cloud metadata services and leaks response details via…
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
 7megaumka7/foskiller
FOSSBilling CVE-2026-53647 & CVE-2026-53646 PoC — Unauthenticated API key disclosure & password reset token reuse
 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks