
RatRace
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
api-security-testingdevsecopsexploitation+5
10
bogdanticu88/ratraceA lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
 akto-api-security/akto
Open-source API security platform for continuous API discovery, vulnerability testing, and runtime threat detection. Integrates with CI/CD pipelines…
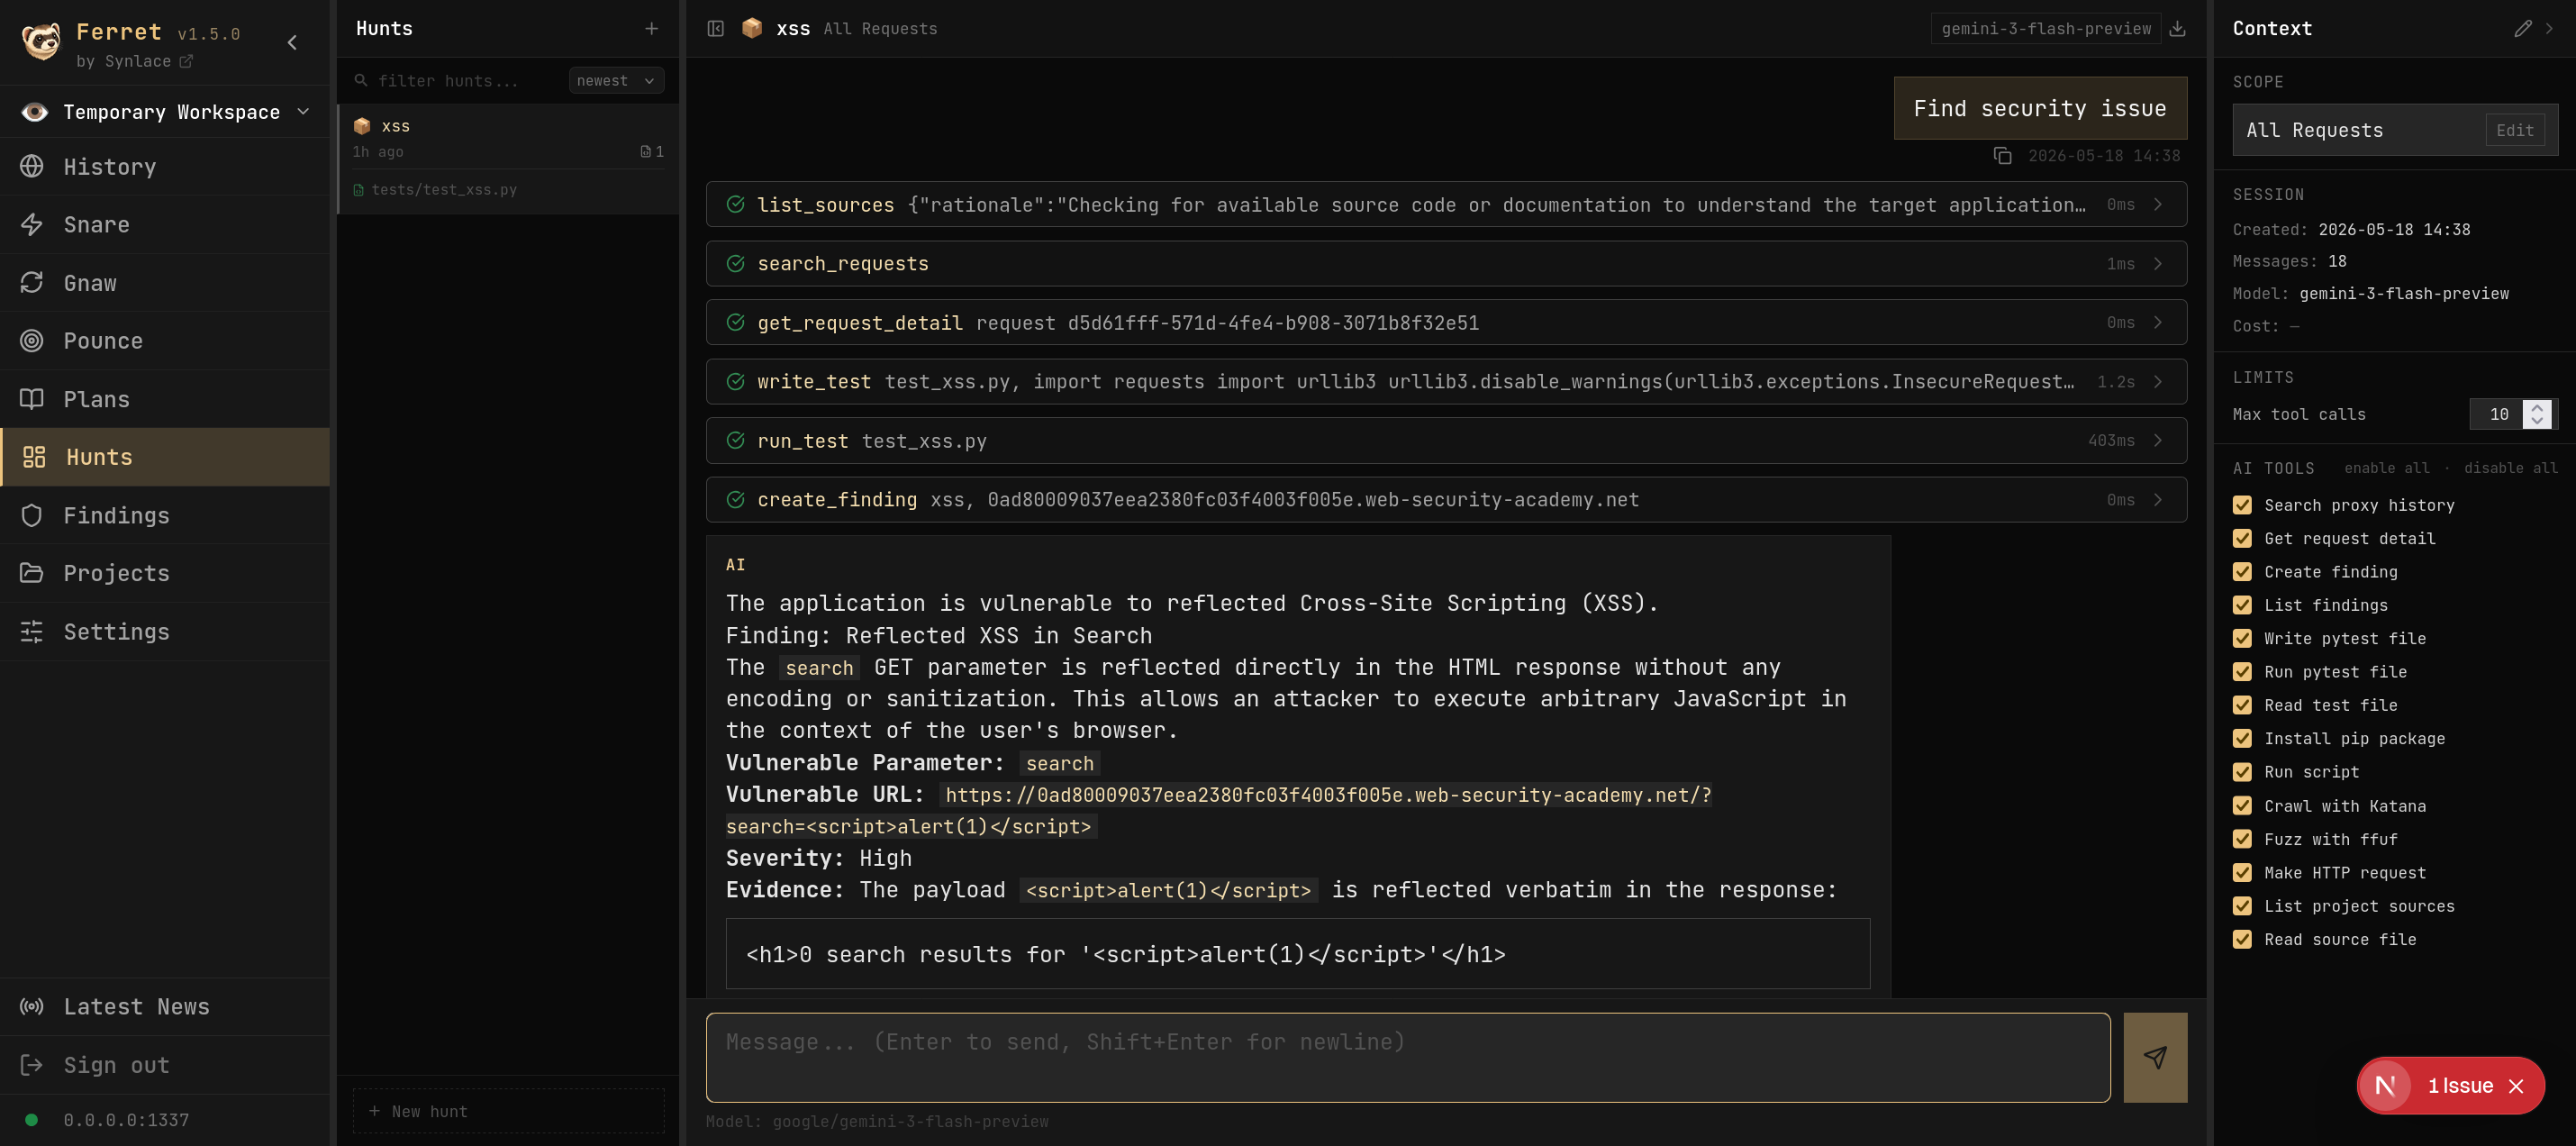 synlace/ferret
The collaborative web app pentest suite
 moopinger/smugglefuzz
A rapid HTTP downgrade smuggling scanner written in Go.

 projectdiscovery/chaos-client
Go client to communicate with Chaos DB API.
 intelligencex/sdk
SDK for querying the Intelligence X search engine and data archive, supporting selectors like email, domain, IP, and phone. Includes API wrappers in…
 momenbasel/vulnhawk
AI-powered SAST scanner that finds auth bypass, IDOR, and logic bugs Semgrep/CodeQL miss. Free GitHub Action. Supports Python, JS/TS, Go, PHP, Ruby.
 joanbono/gurp
Burp Commander written in Go
 m4xsec/wp2shell-exploit-waf-bypass
WordPress Pre-Auth RCE Exploit + Scanner + WAF Bypass | CVE-2026-63030 + CVE-2026-60137 | Go + Python + Metasploit modules + Docker lab
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 spectolabs/hoverfly
Lightweight service virtualization/ API simulation / API mocking tool for developers and testers
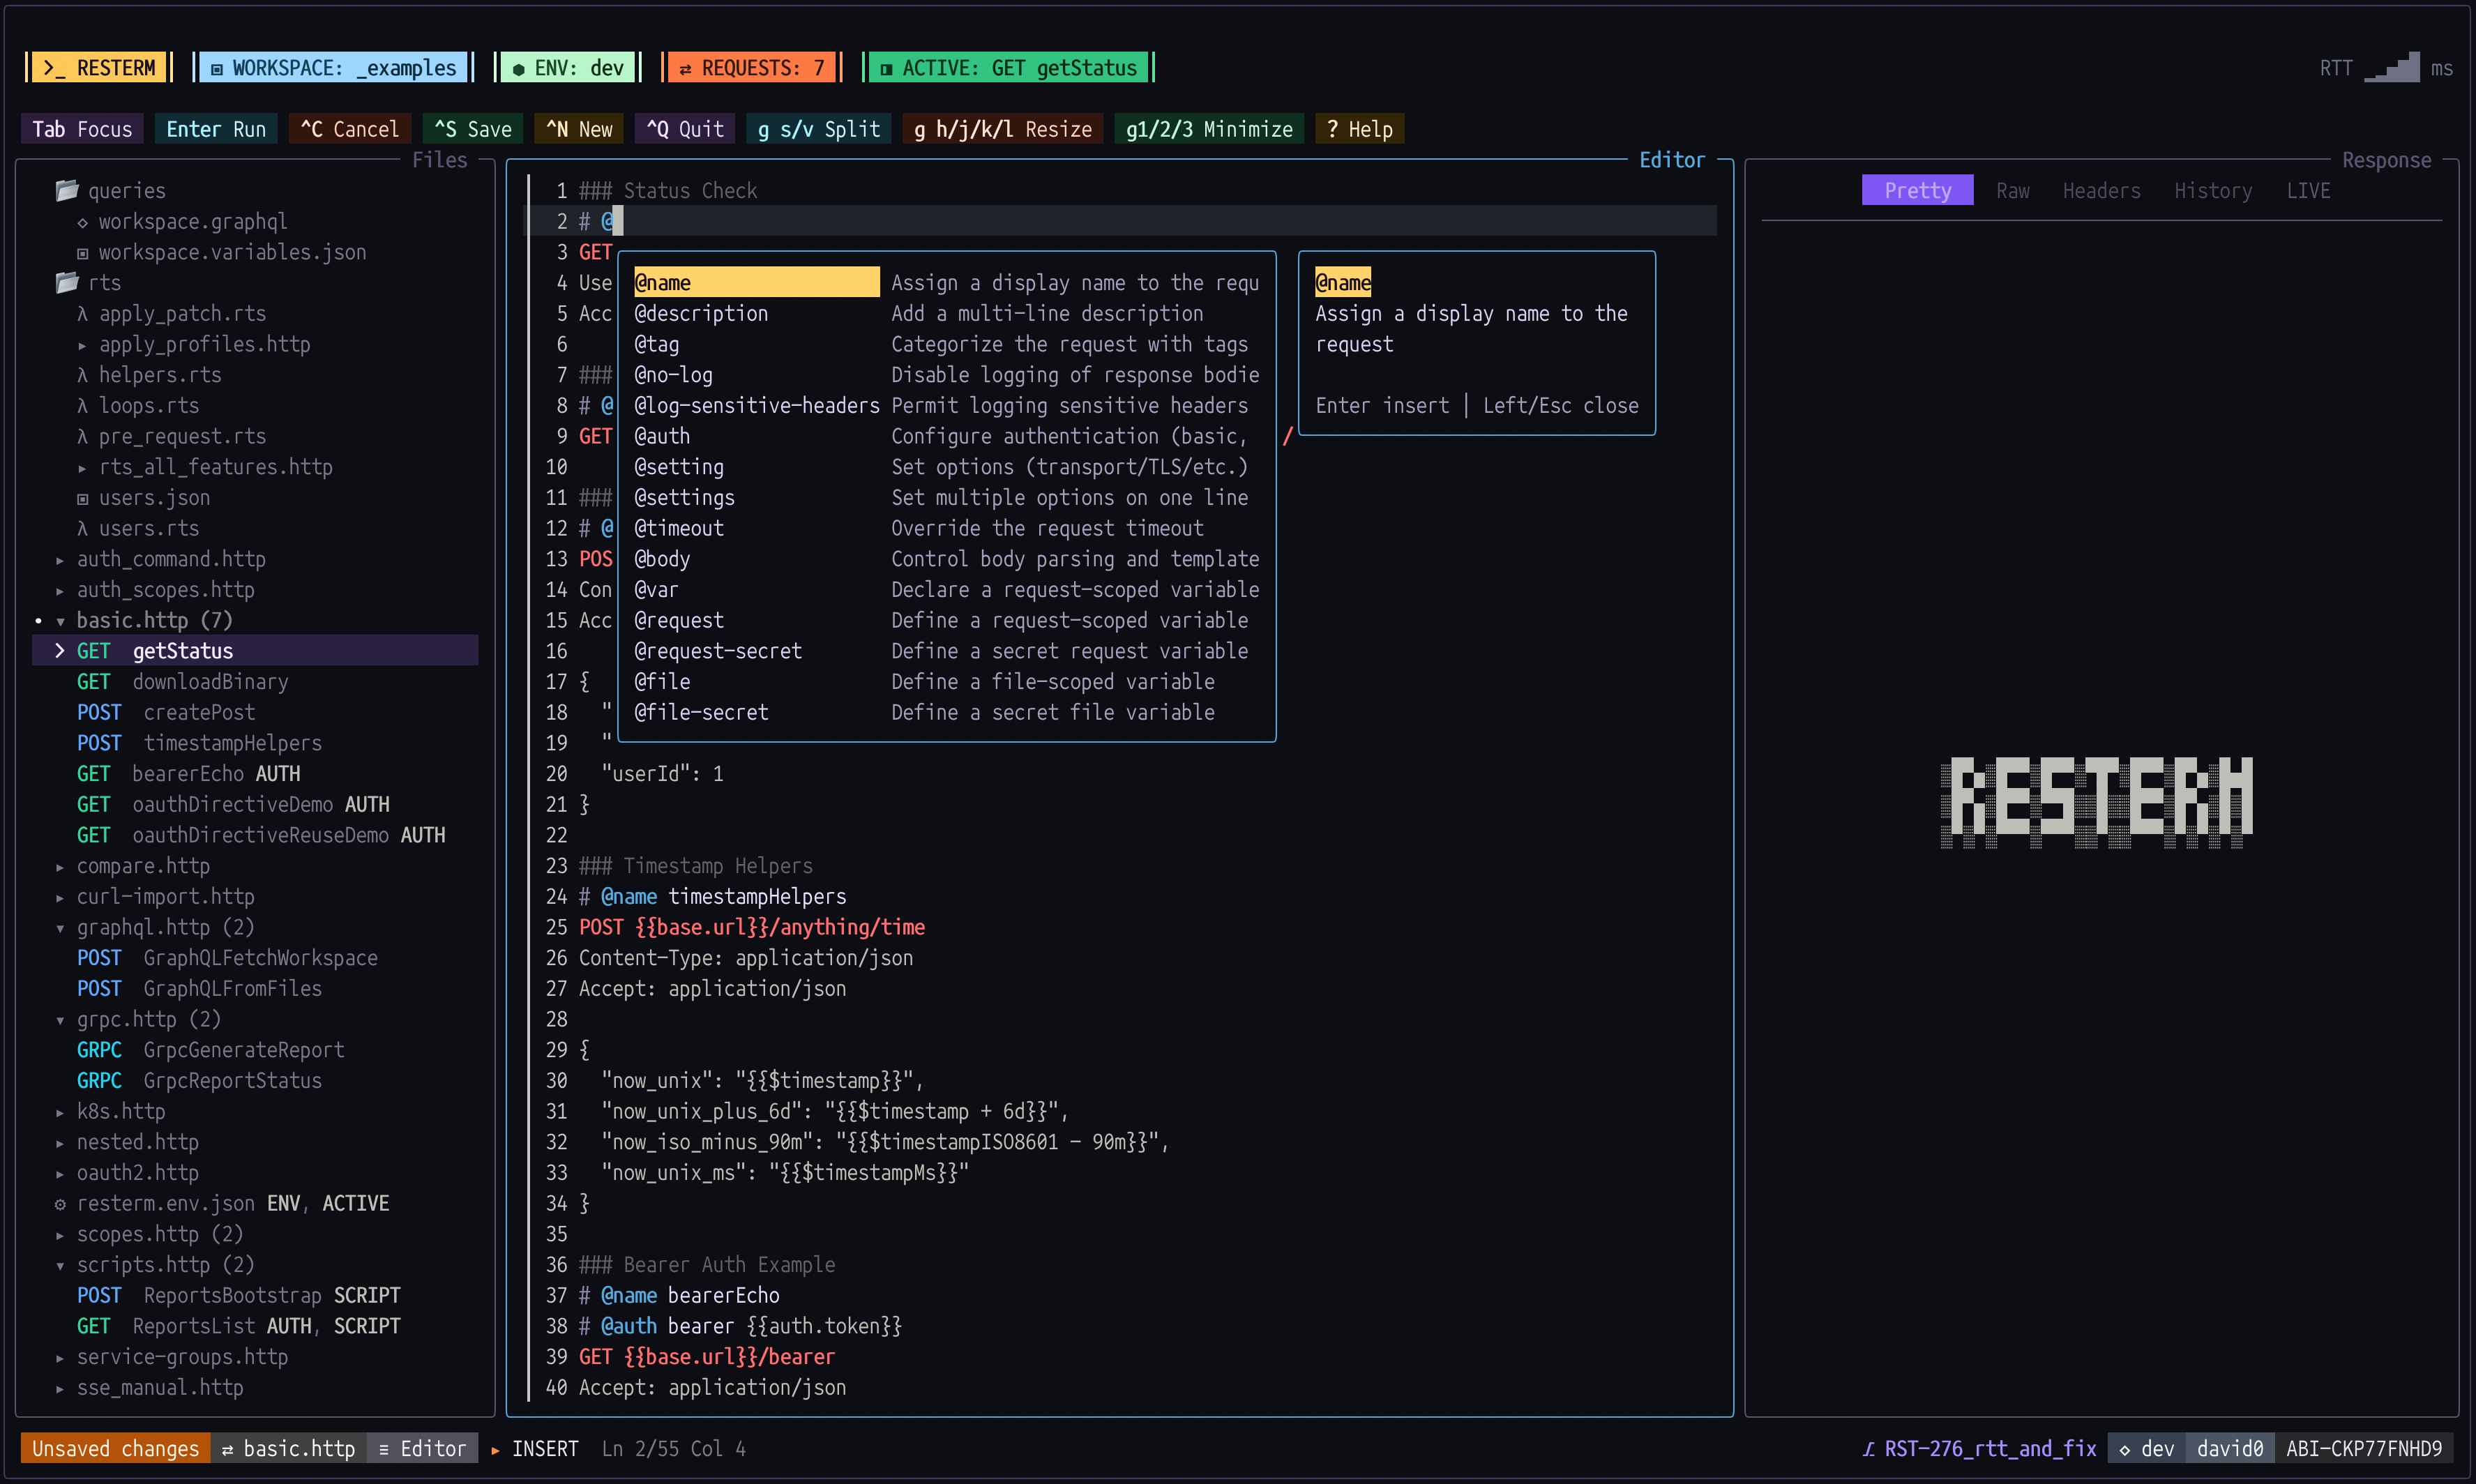 unkn0wn-root/resterm
Terminal API client for HTTP, GraphQL and gRPC. Plain .http files you can diff and version, with workflows, mocks, profiling, tracing, OpenAPI…
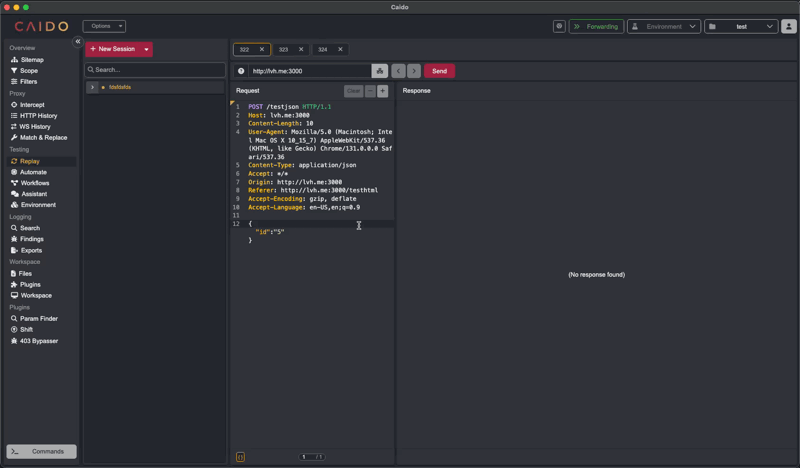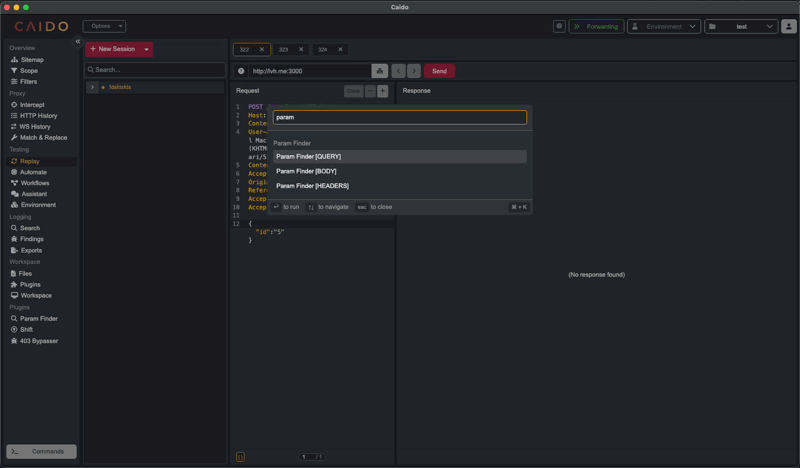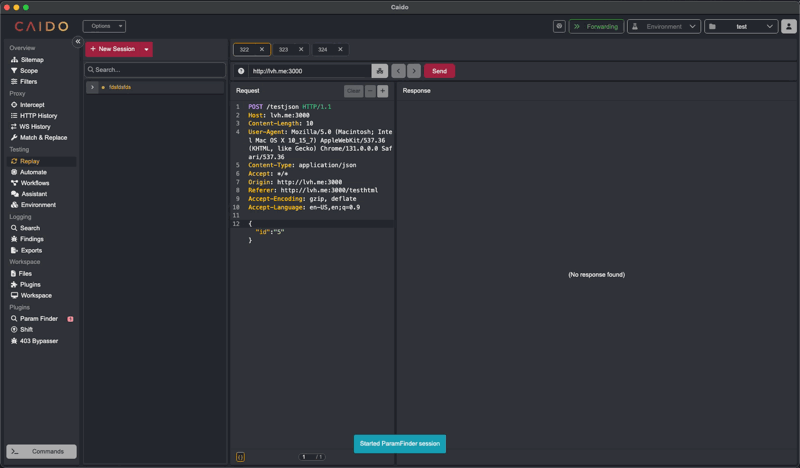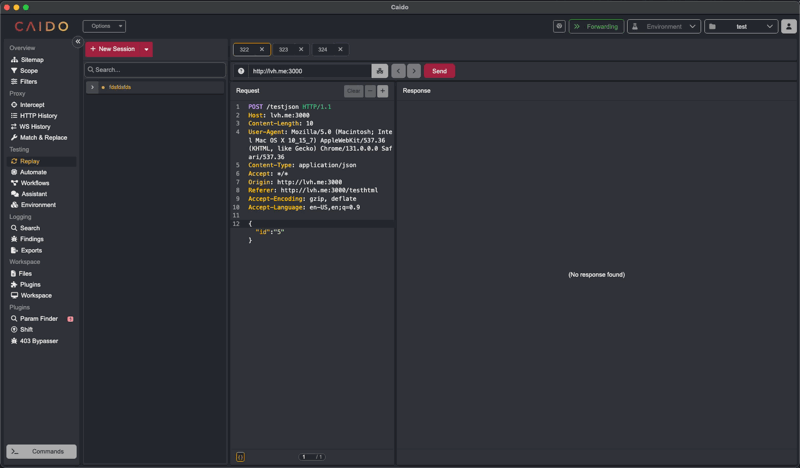 caido-community/paramfinder
Discover hidden parameters in Caido
 infobyte/faraday_zap
Zap Extension for collaboration in Faraday
 s0md3v/arjun
HTTP parameter discovery tool that finds valid query parameters for URL endpoints using a large dictionary, supporting GET/POST/JSON/XML requests,…