
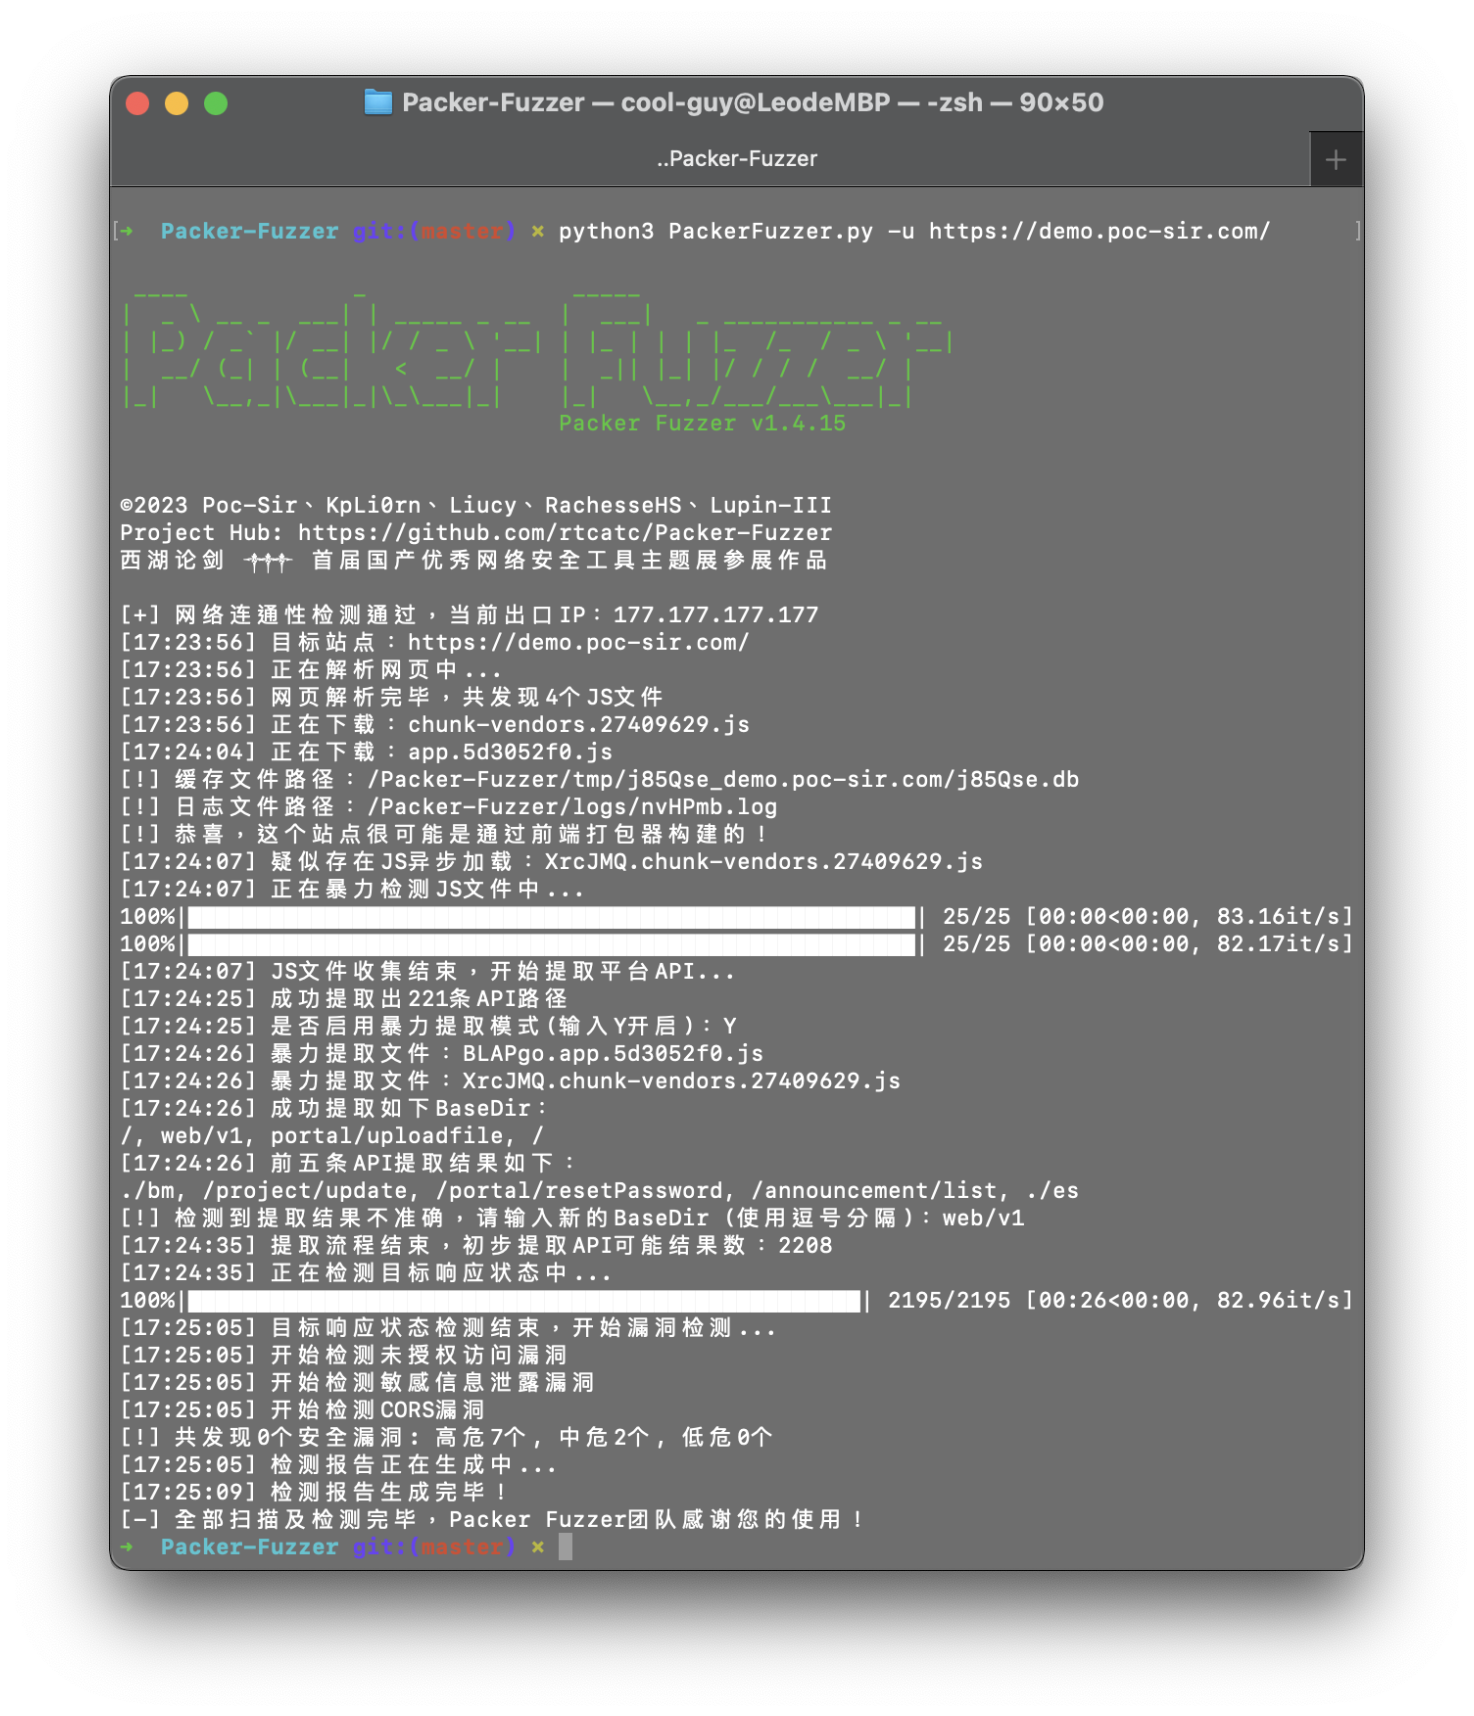
Packer-Fuzzer
 rtcatc/packer-fuzzer
Packer Fuzzer is a fast and efficient scanner for security detection of websites constructed by javascript module bundler such as Webpack.
api-security-testingfuzzingvulnerability-scanners+1
3.3k
rtcatc/packer-fuzzerPacker Fuzzer is a fast and efficient scanner for security detection of websites constructed by javascript module bundler such as Webpack.
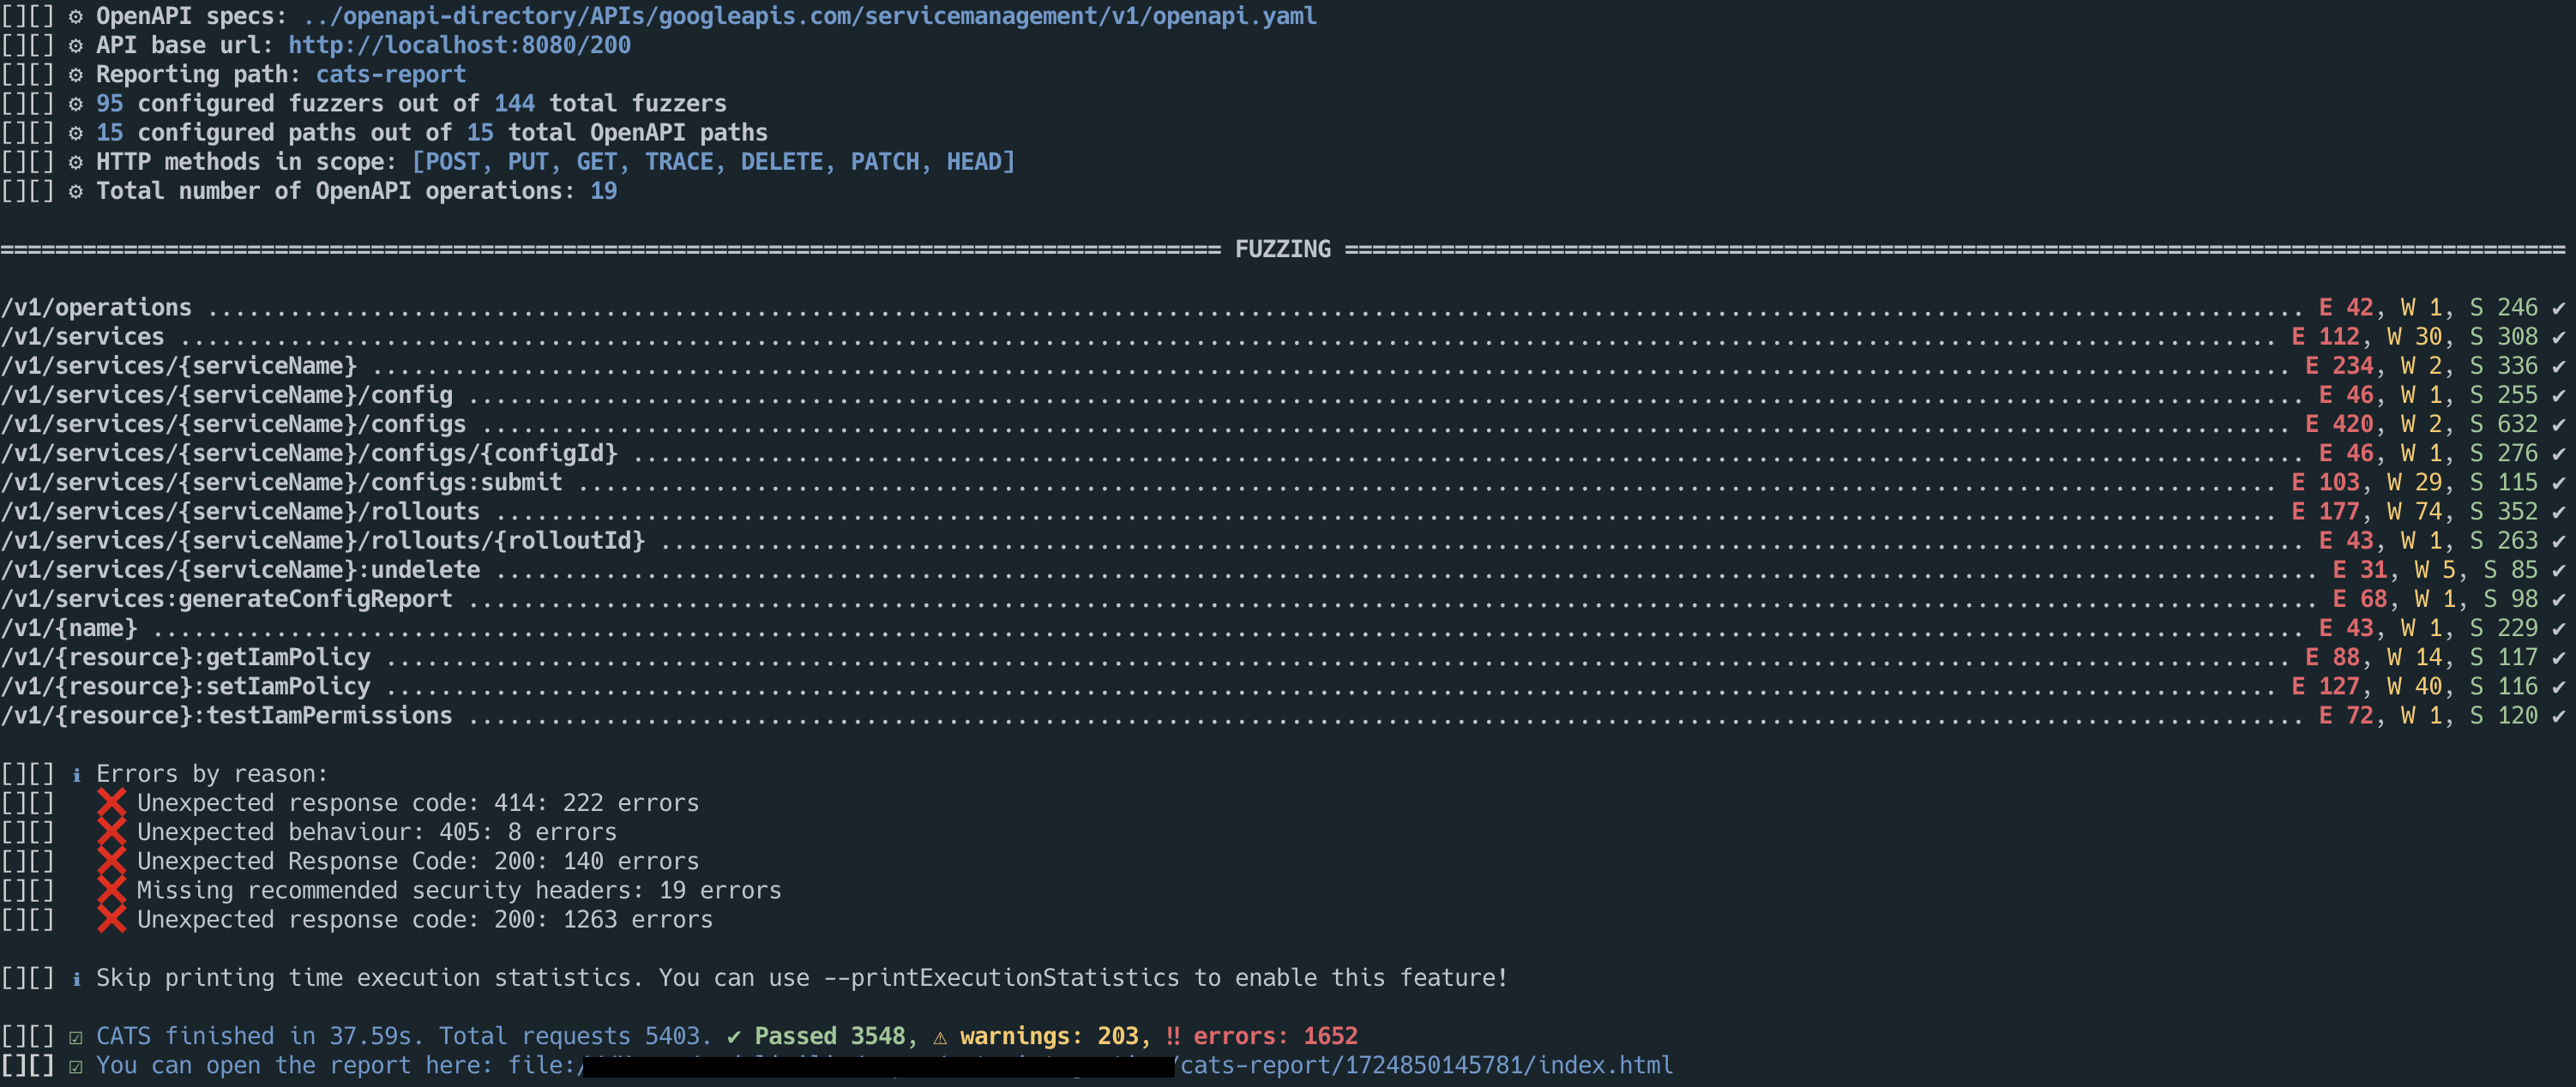 endava/cats
Automated REST API fuzzer and negative testing tool for OpenAPI endpoints. Generates, runs, and reports thousands of self-healing tests with no…
 chrislockard/api_wordlist
A wordlist of API names for web application assessments
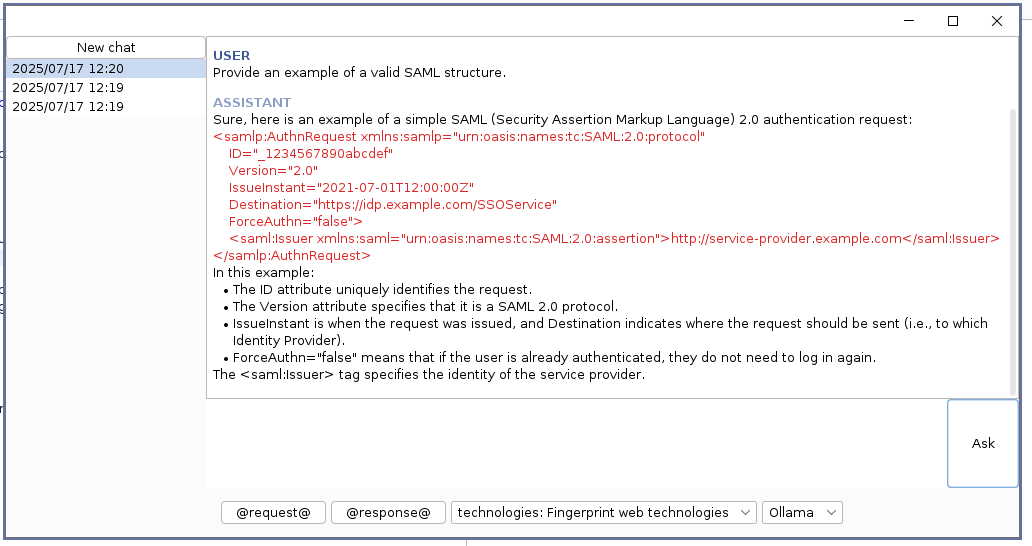 synacktiv/hopla
HopLa Burp Suite Extender plugin - Brings AI capabilities, autocompletion support, and a set of useful payloads to Burp Suite
 dolevf/graphql-cop
Lightweight Python utility for automated security auditing of GraphQL APIs. Detects misconfigurations, information leaks, and denial-of-service…
 aws/http-desync-guardian
Analyze HTTP requests to minimize risks of HTTP Desync attacks (precursor for HTTP request smuggling/splitting).
 ethicalhackingplayground/ssrf-king
SSRF plugin for burp Automates SSRF Detection in all of the Request
 opaxial/cve-2026-9830
CVE-2026-9830 Proof of Concept
 tno-s3/wuppiefuzz
A coverage-guided REST API fuzzer developed on top of LibAFL
 ethicalhackingplayground/tproxer
A Burp Suite extension made to automate the process of finding reverse proxy path based SSRF.
 dipjyotimetia/hybridtestframework
End to End testing of Web, API, Cloud, Events and Security
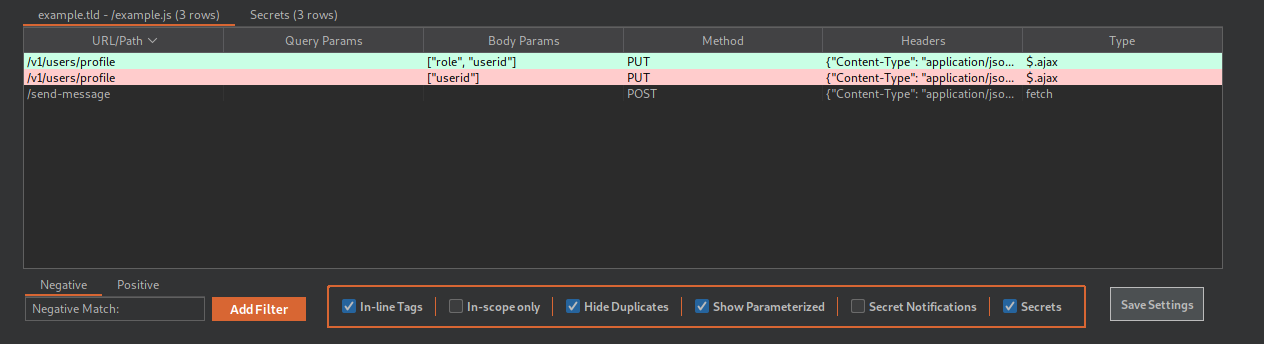 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
 net-hunter121/api-wordlist
Curated wordlists of API function names, verbs, and nouns for fuzzing web application endpoints with Burp Suite Intruder.
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
 trailofbits/slither-mcp
MCP server for Slither static analysis of Solidity smart contracts
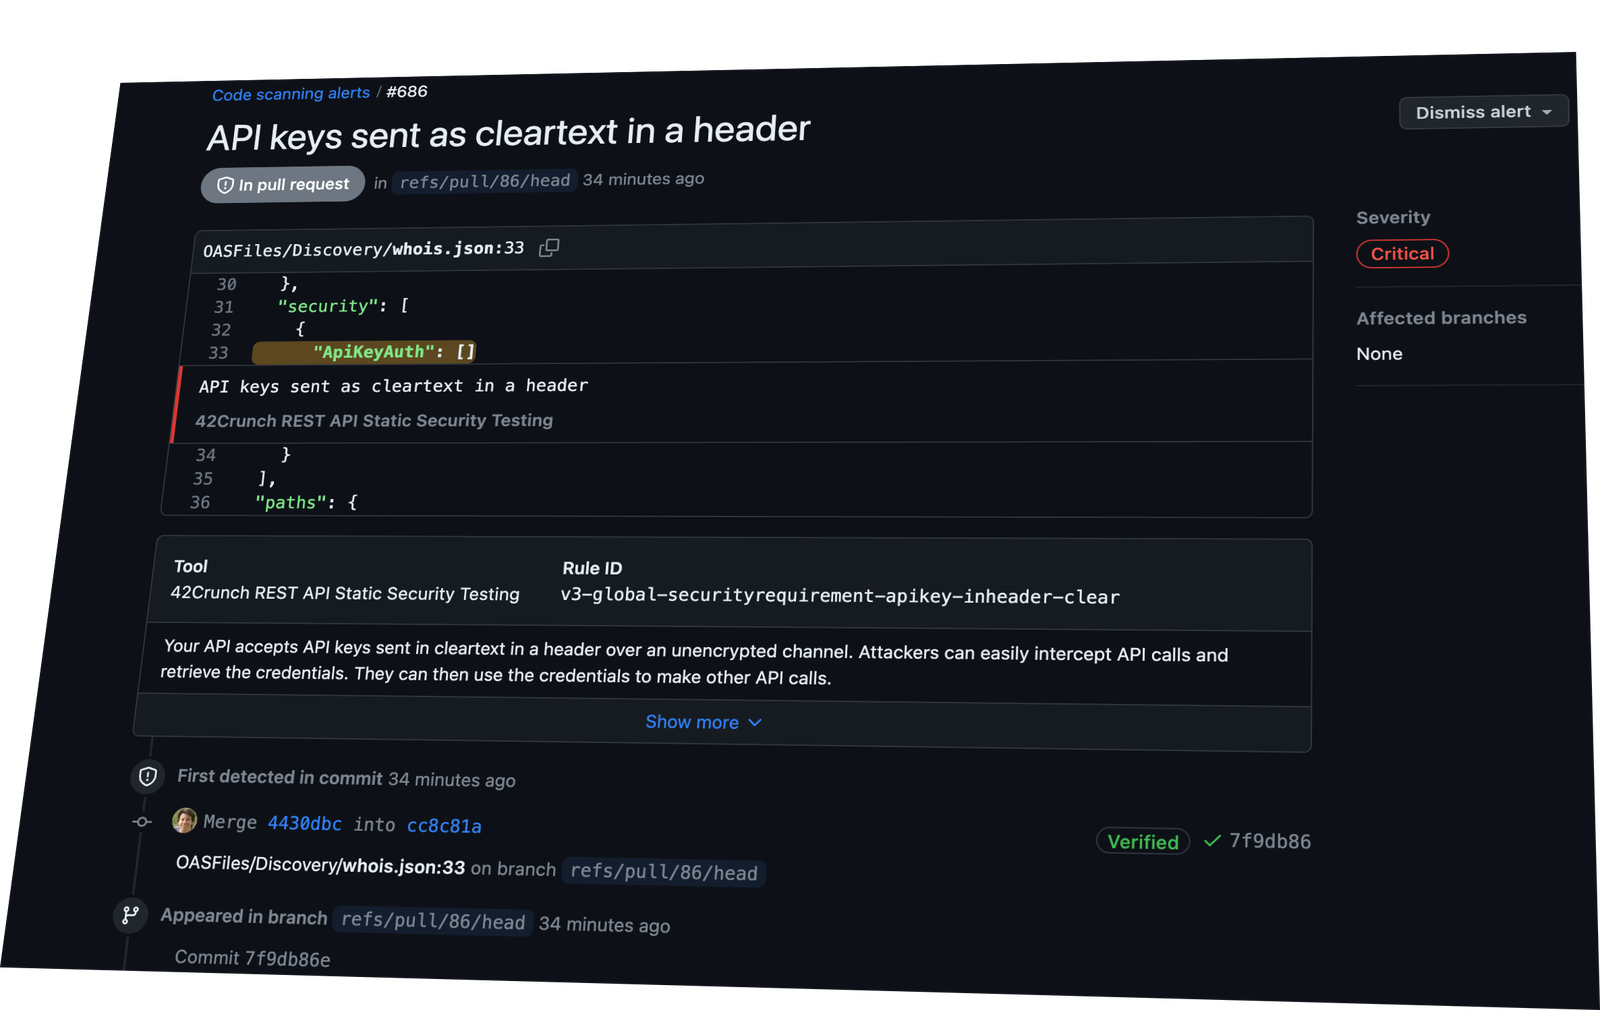 42crunch/api-security-audit-action
Automates static API security auditing of OpenAPI contracts in CI/CD, running 300+ checks for authentication, authorization, and data constraints,…
 agentsid-dev/agentsid-scanner
Security scanner for MCP servers. Grades auth, permissions, injection risks, and tool safety. The Lighthouse of agent security.
 letsencrypt/test-certs-site
A simple server to host the valid, revoked, and expired certificates required by Section 2.2 of the CA/Browser Forum Baseline Requirements.