android-reverse-engineering-skill

Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…

Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…

Modular DevSecOps toolset for REST API security testing, designed for developers, sysadmins, and penetration testers to automate security checks…

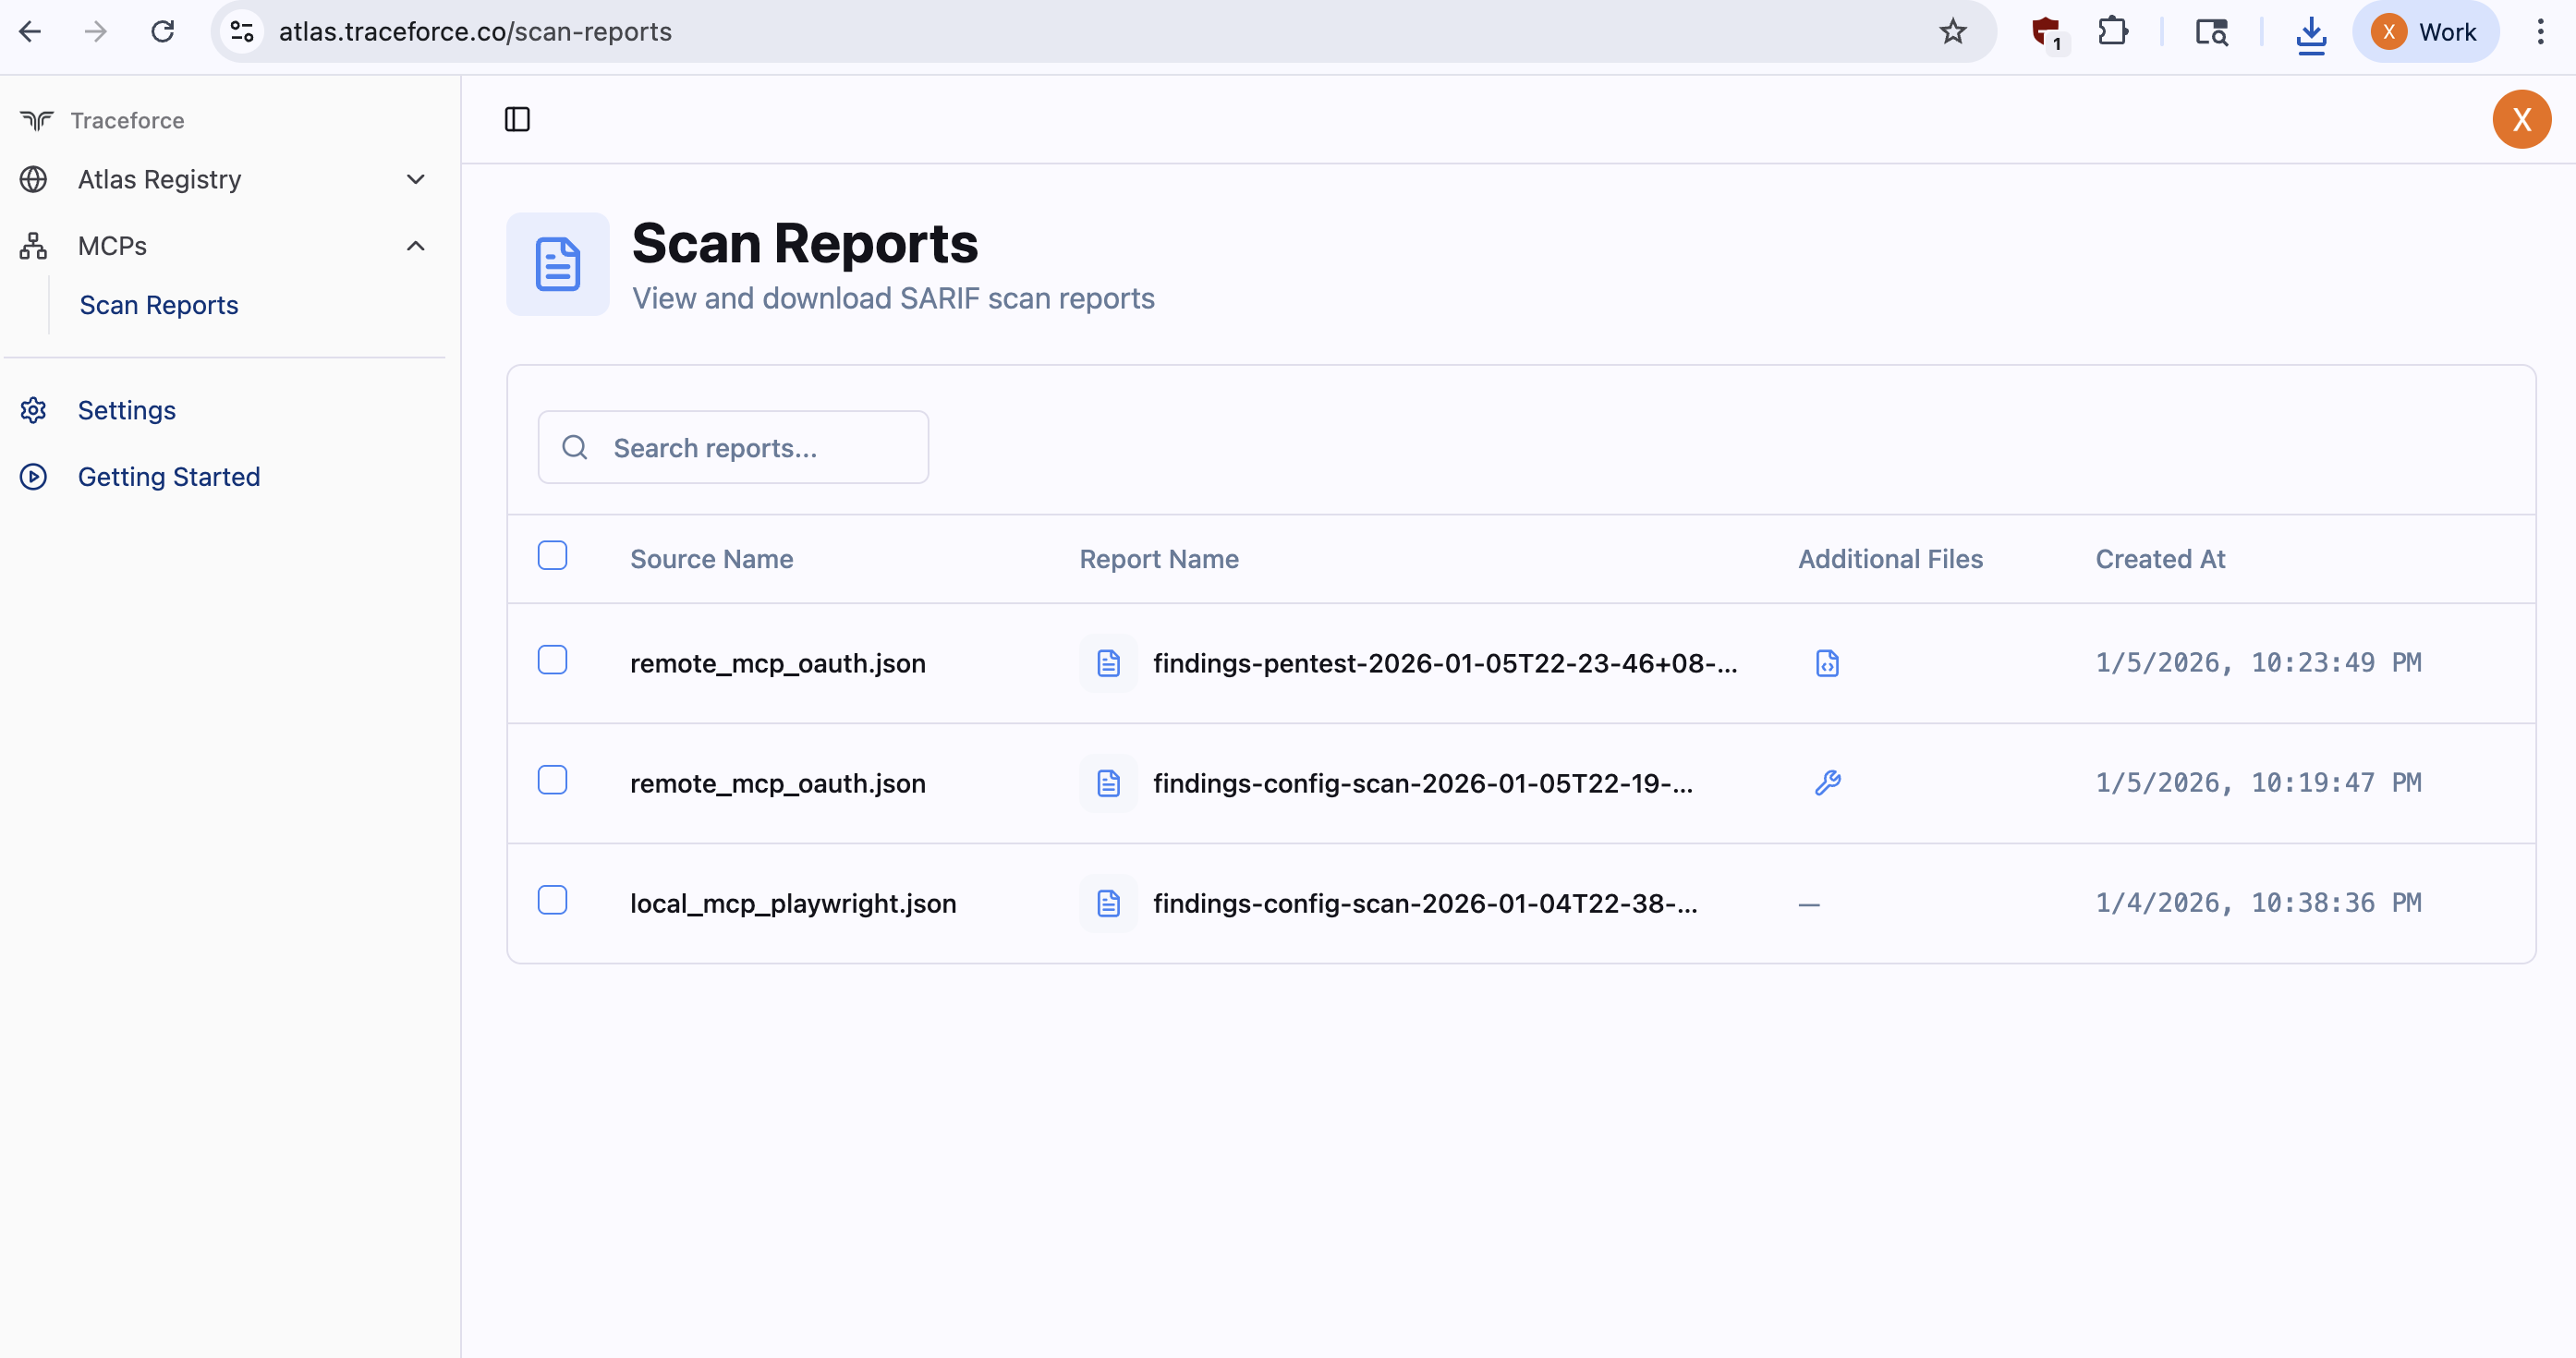
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…

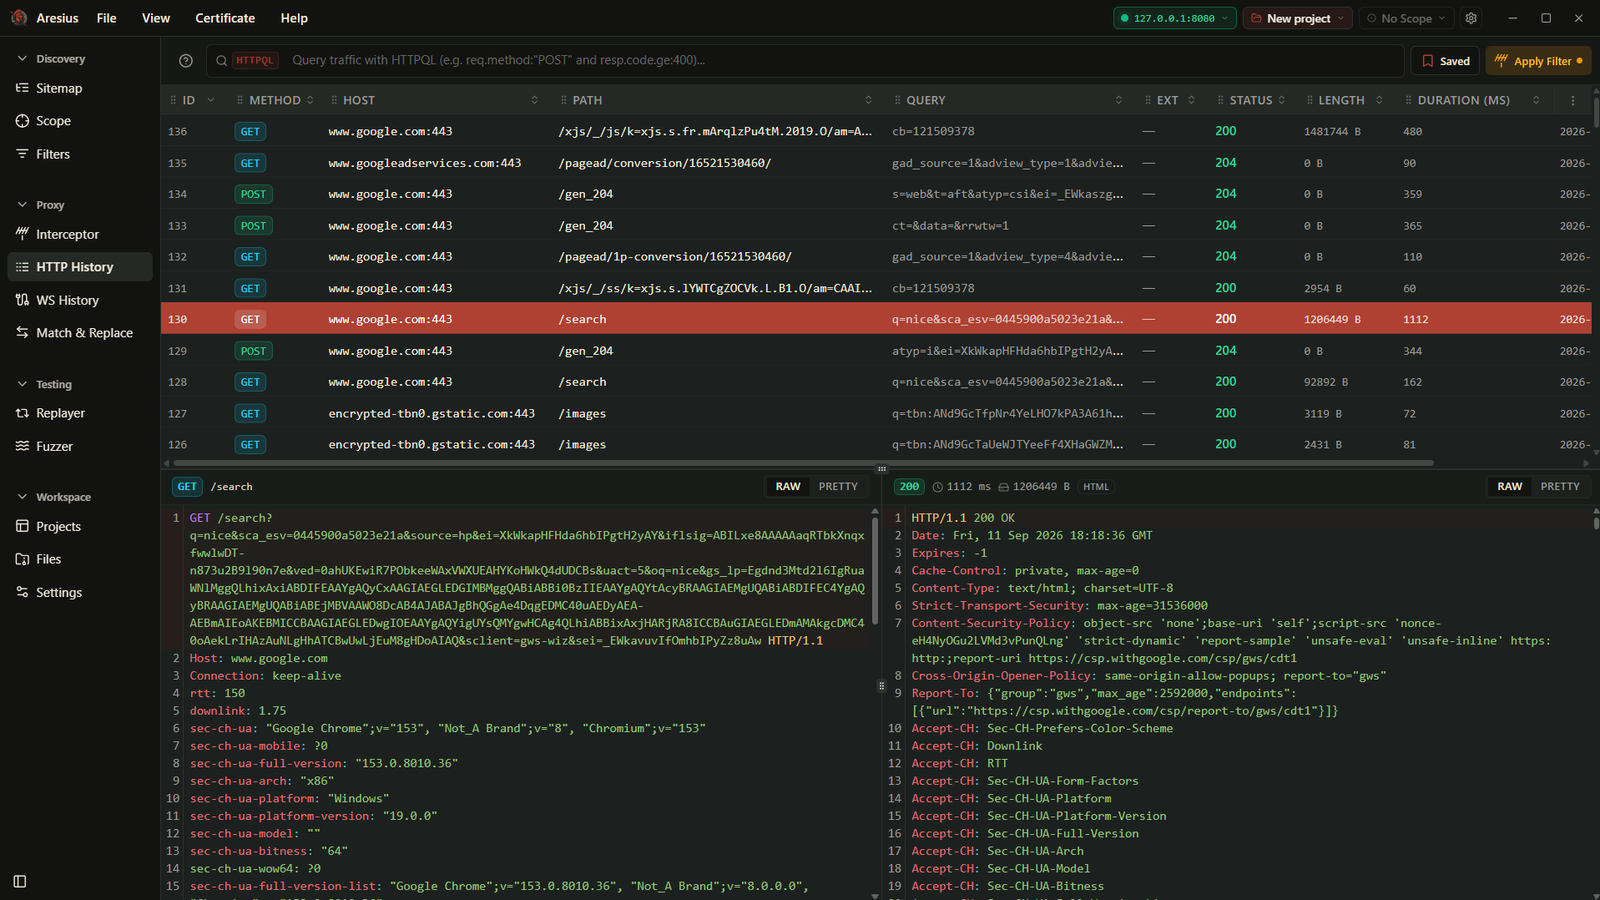
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.

Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…

Automated GraphQL schema enumeration and data extraction tool that iterates introspection documents, reconstructs queries, and saves responses for…

Native HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…

Abdal CVE-2026-63030 is a professional WordPress vulnerability scanner designed to detect exposure to CVE-2026-63030 through version analysis and…

Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Android Package Inspector - dynamic analysis with api hooks, start unexported activities and more. (Xposed Module)

Model Context Protocol server for Firefox DevTools - enables AI assistants to inspect and control Firefox browser through WebDriver BiDi

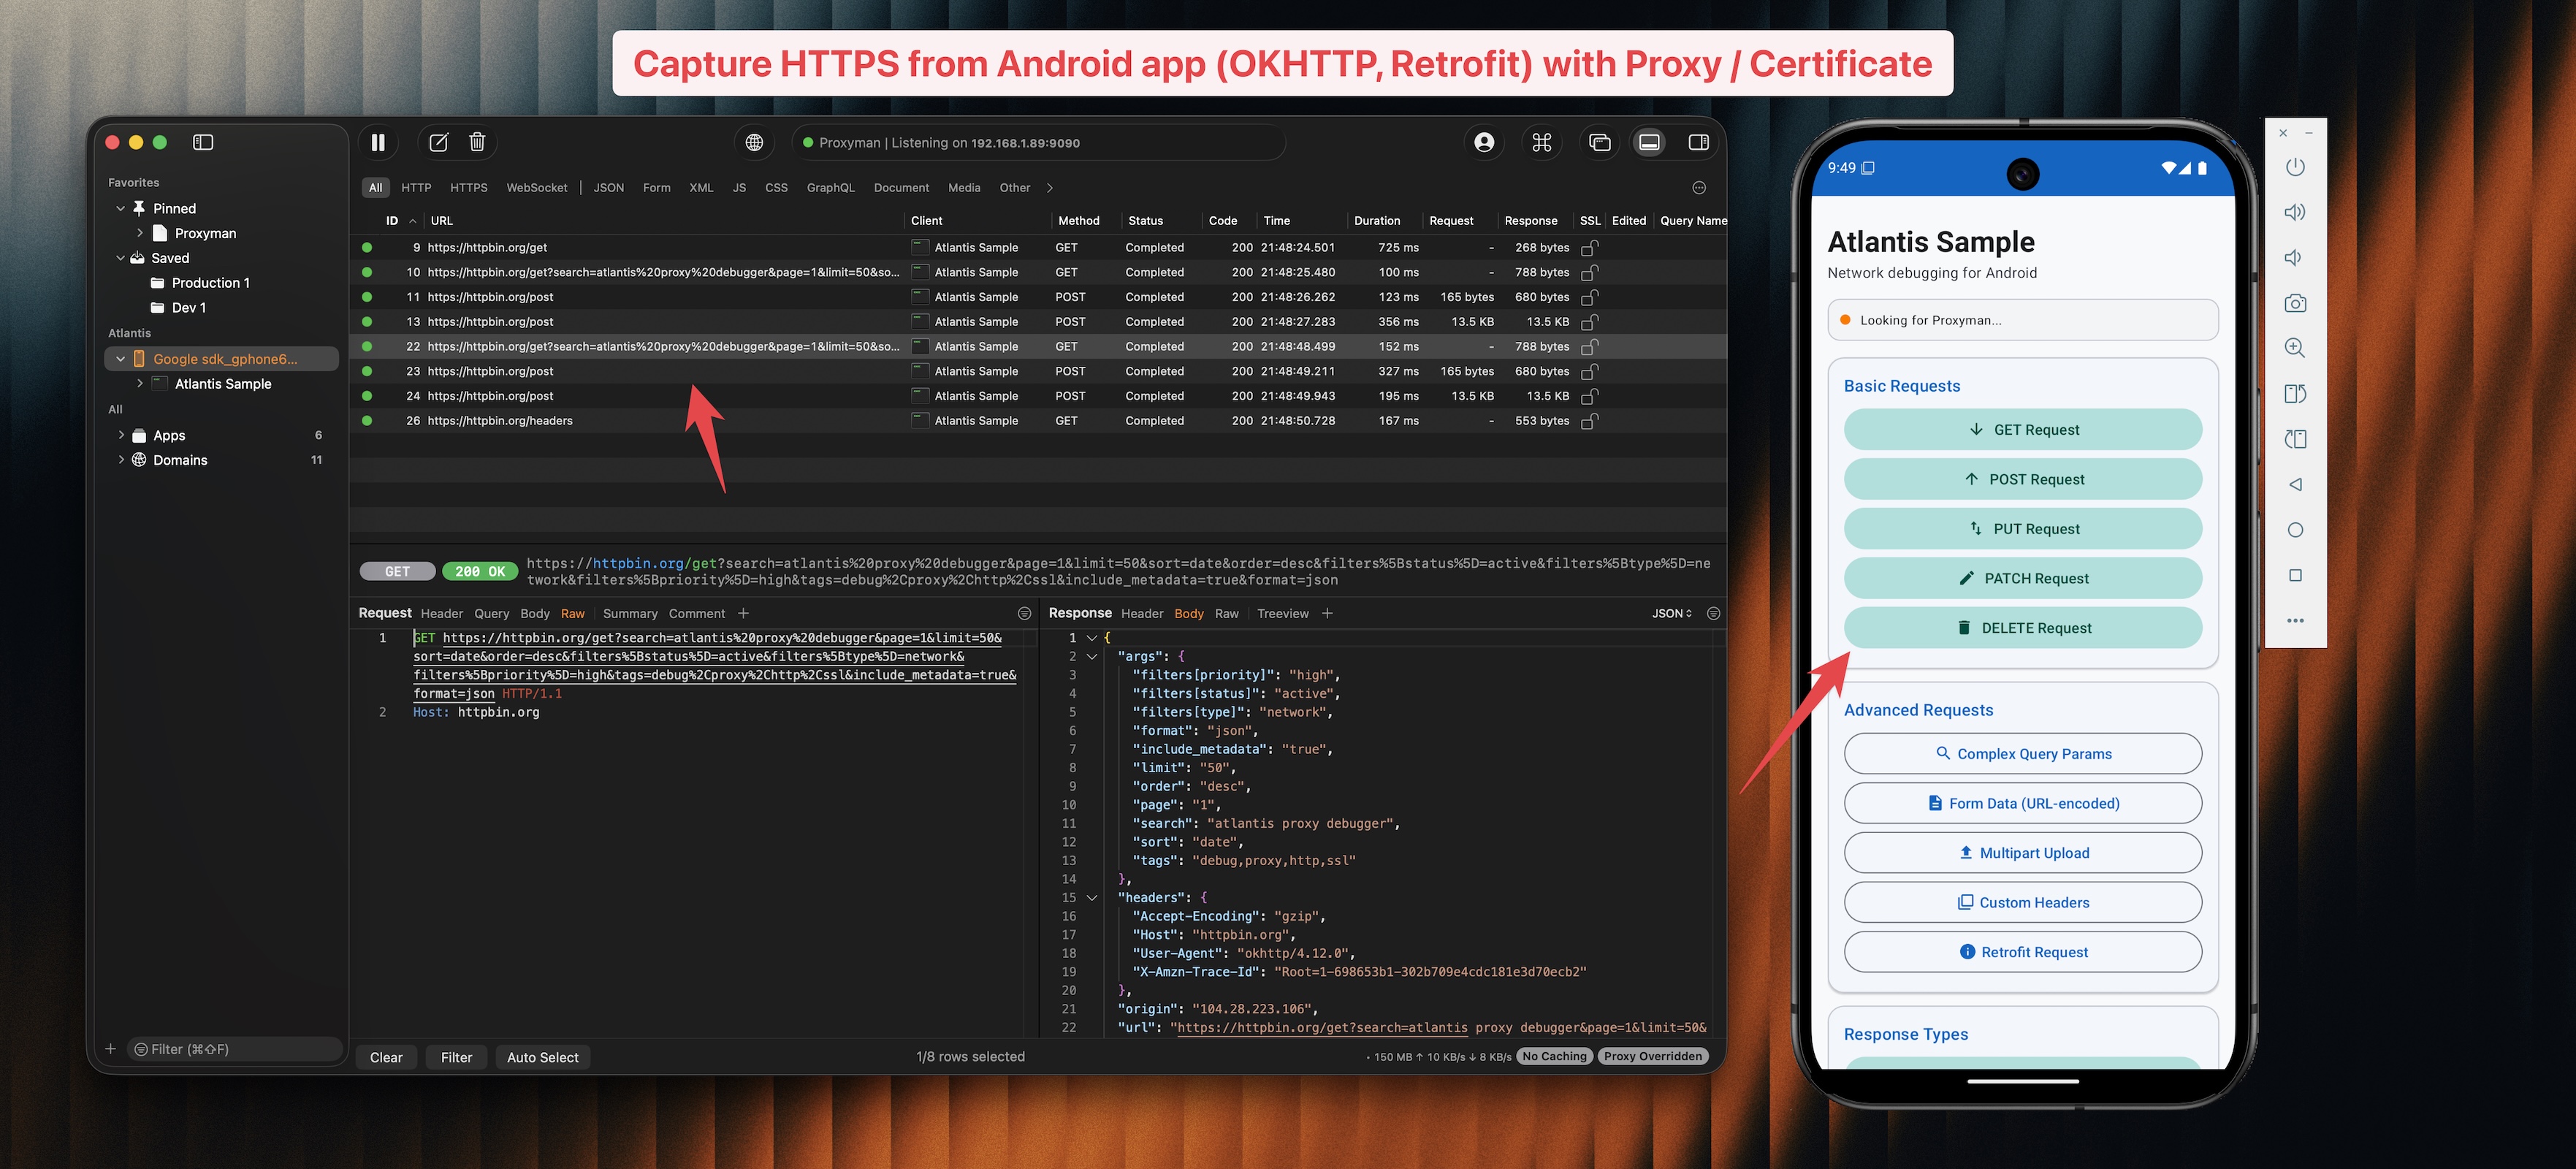
Capture HTTP/HTTPS traffic from Android apps and send to Proxyman for debugging.

Hooker is an opensource project for dynamic analyses of Android applications. This project provides various tools and applications that can be use to…

Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.

A Burp Suite Extension for Application Penetration Testing to map flows and vulnerabilities

Comprehensive web application security testing platform featuring advanced scanning engine, intercepting proxy, and automated vulnerability detection…

Burp Suite Extension useful to verify OAUTHv2 and OpenID security