Mobile-Security-Framework-MobSF

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

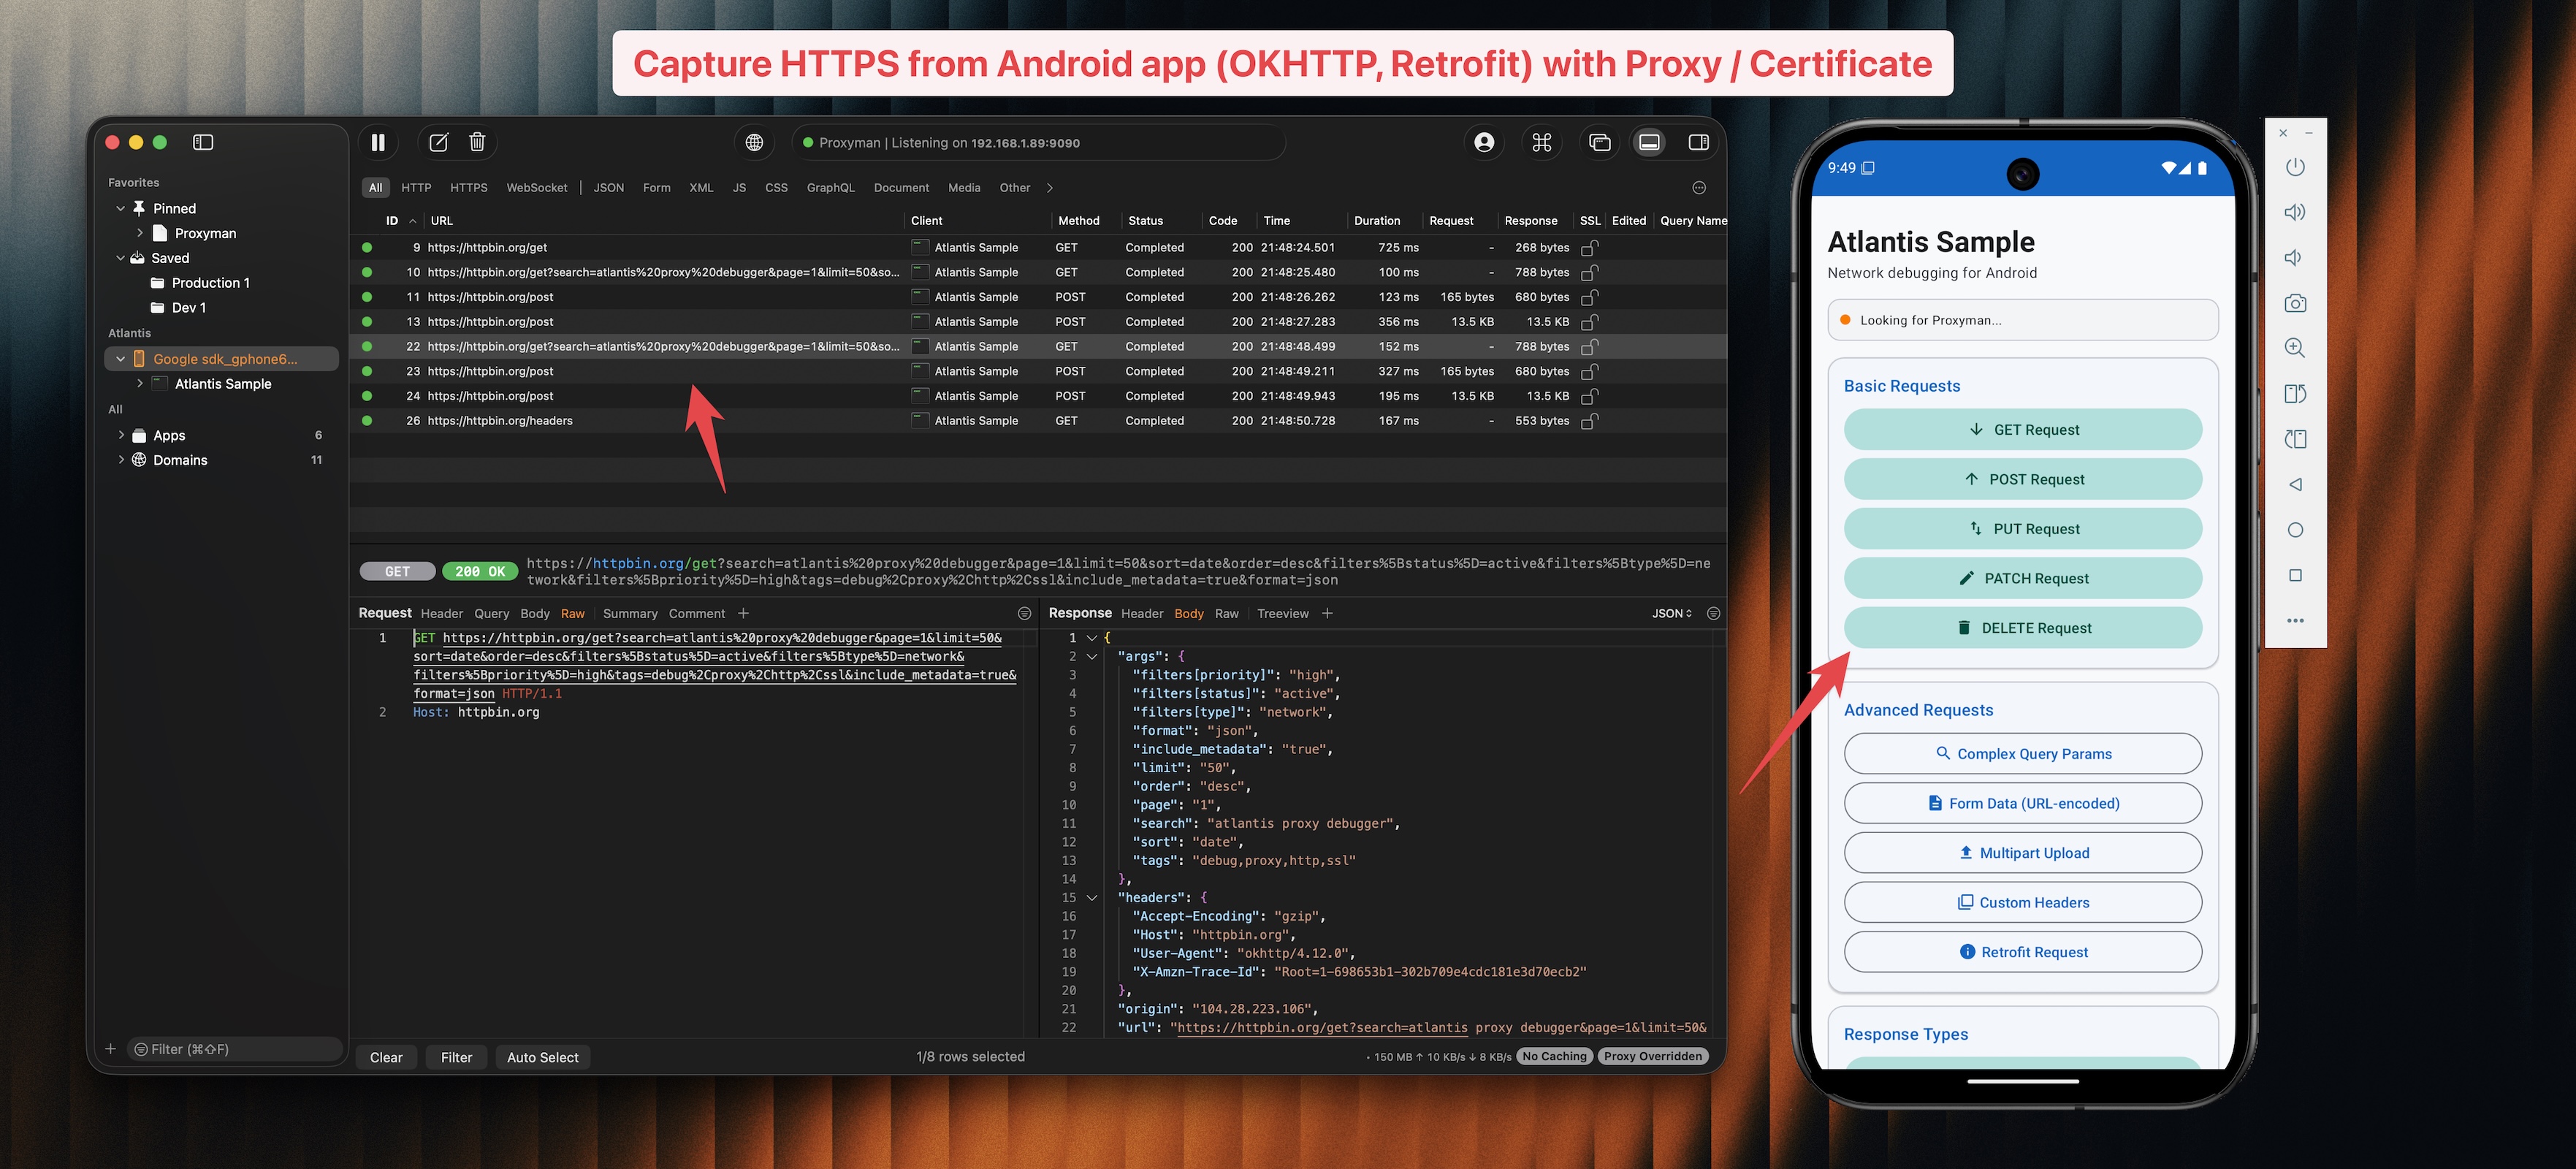
Capture HTTP/HTTPS traffic from Android apps and send to Proxyman for debugging.

Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…

Android Package Inspector - dynamic analysis with api hooks, start unexported activities and more. (Xposed Module)

Hooker is an opensource project for dynamic analyses of Android applications. This project provides various tools and applications that can be use to…

An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.

Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…

The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…

Model Context Protocol server for Firefox DevTools - enables AI assistants to inspect and control Firefox browser through WebDriver BiDi

High-performance HTTP/HTTPS/SOCKS5 MITM proxy in Rust with TLS interception, rule-based request rewriting, traffic capture, breakpoints, script…

Standard-library Python security triage engine that scans web apps, APIs, LLMs, and mobile packages via passive header inspection, active canary…

This experimetal fuzzer is meant to be used for API in-memory fuzzing.