
mzap
 hahwul/mzap
⚡️ Multiple target ZAP Scanning
api-security-testingdevsecopsdynamic-analysis-sandboxing+3
hahwul/mzap⚡️ Multiple target ZAP Scanning
 traceforce/mcp-xray
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…
 impact-i/x8-burp
Hidden parameters discovery suite
 mda2av/http11probe
An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
 portswigger/pentest-mapper
A Burp Suite Extension for Application Penetration Testing to map flows and vulnerabilities
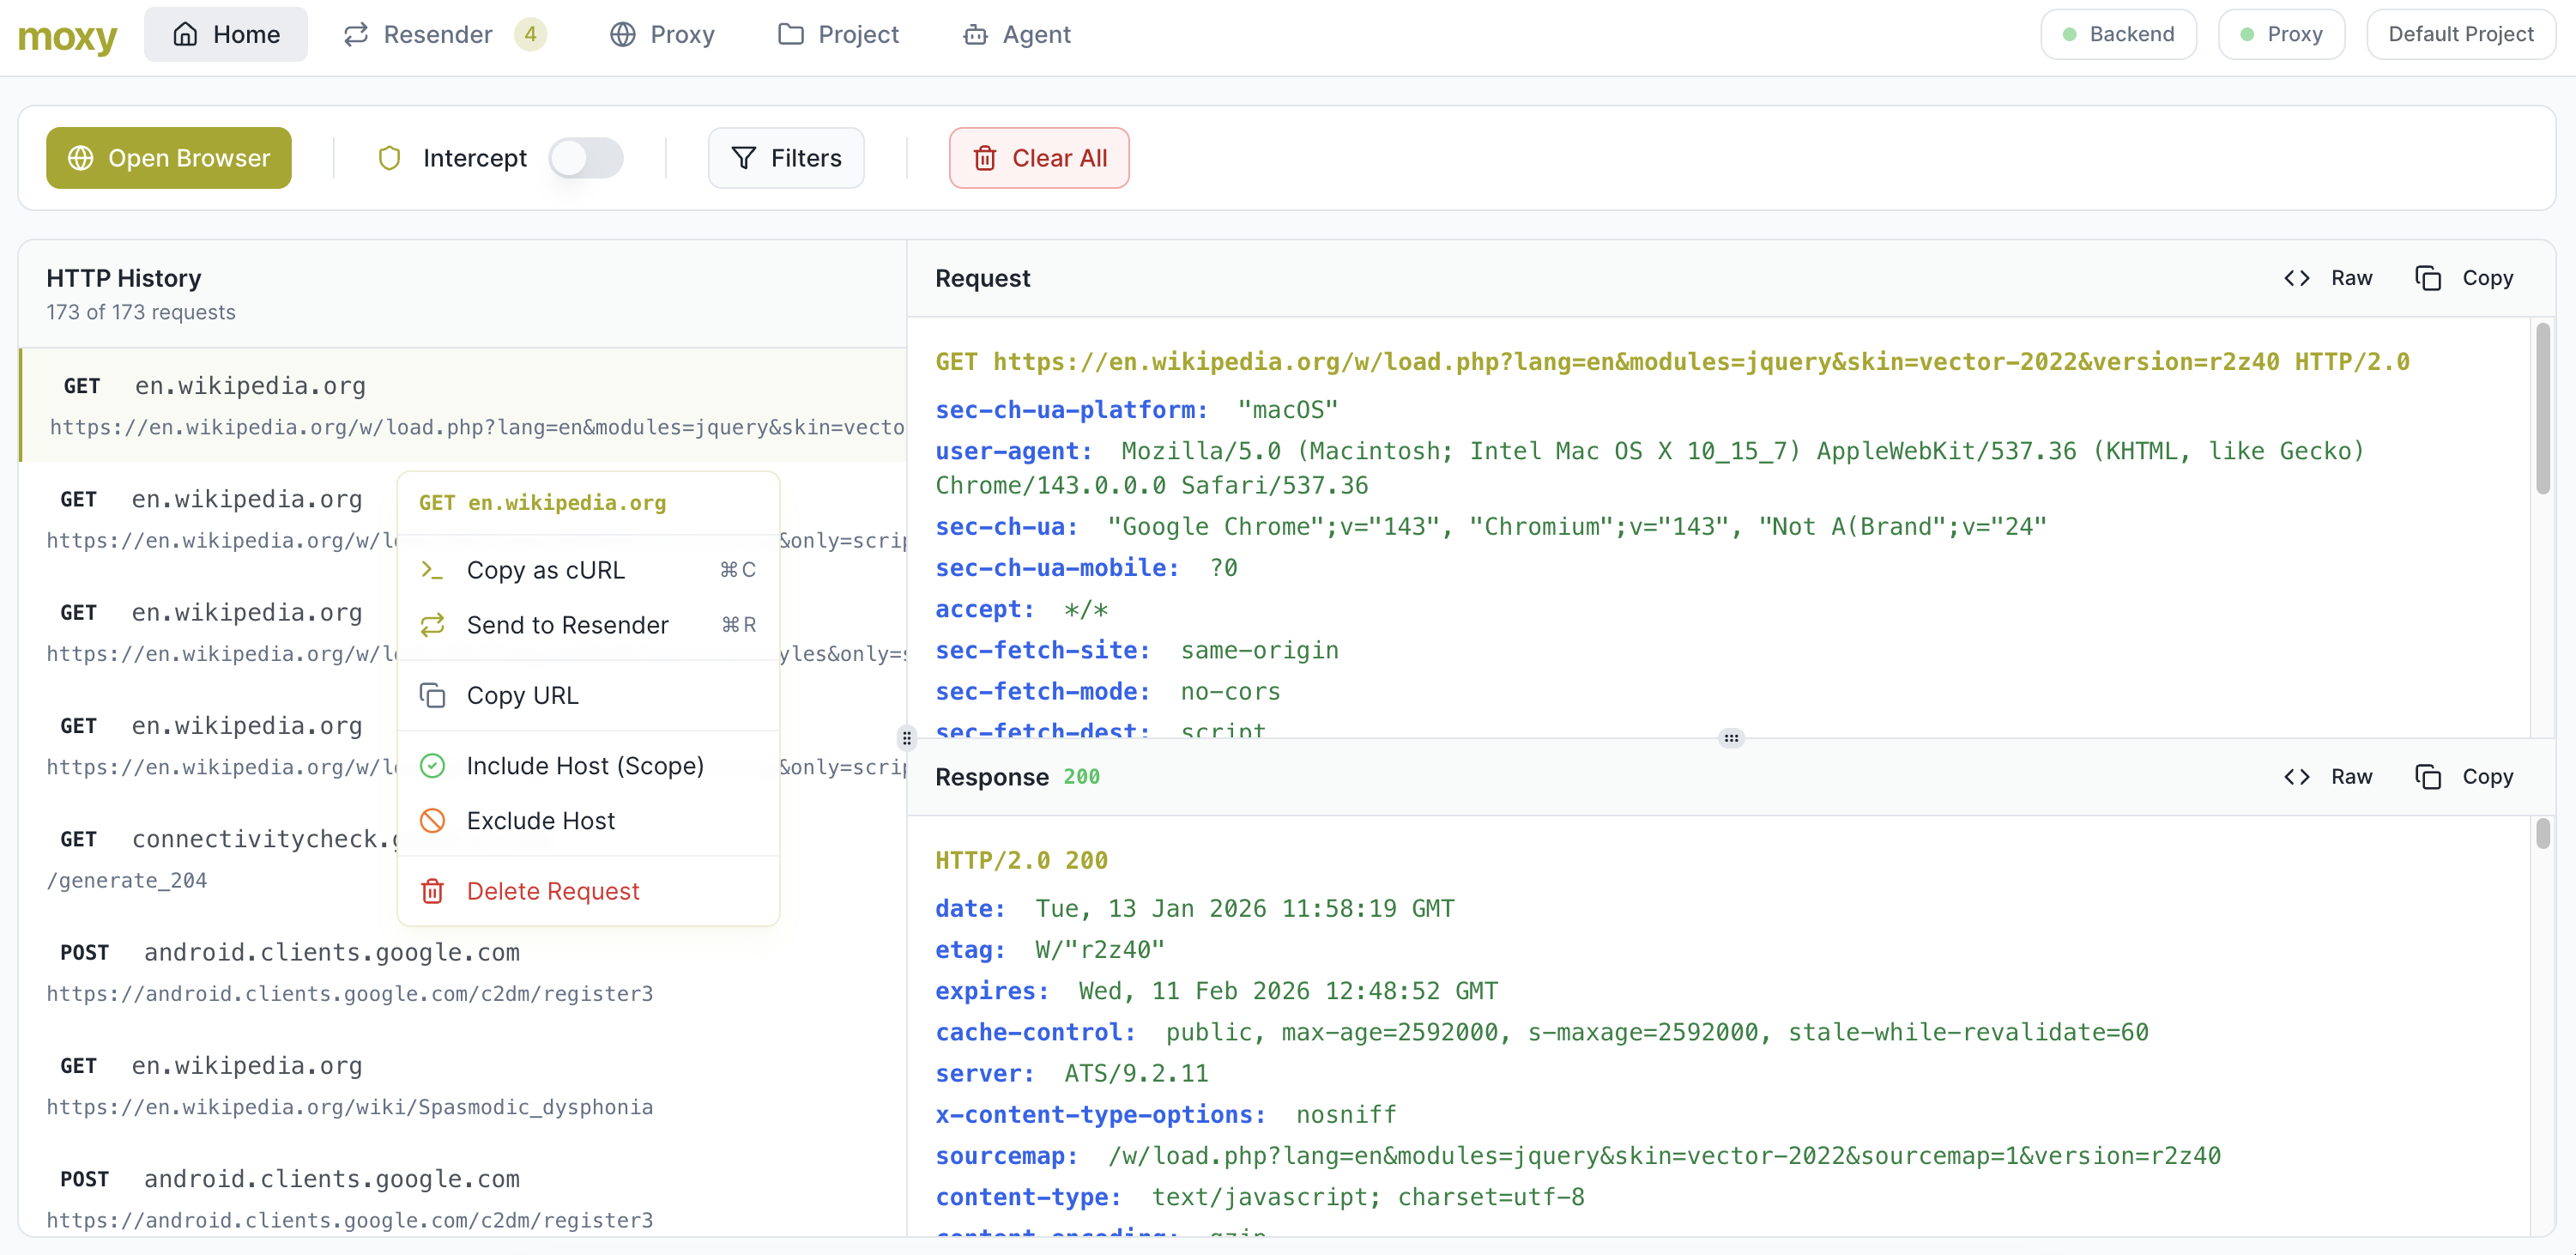 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 owasp/agent-security-regression-harness
Executable security regression testing for agentic applications and MCP-integrated systems.
 momenbasel/vulnhawk
AI-powered SAST scanner that finds auth bypass, IDOR, and logic bugs Semgrep/CodeQL miss. Free GitHub Action. Supports Python, JS/TS, Go, PHP, Ruby.
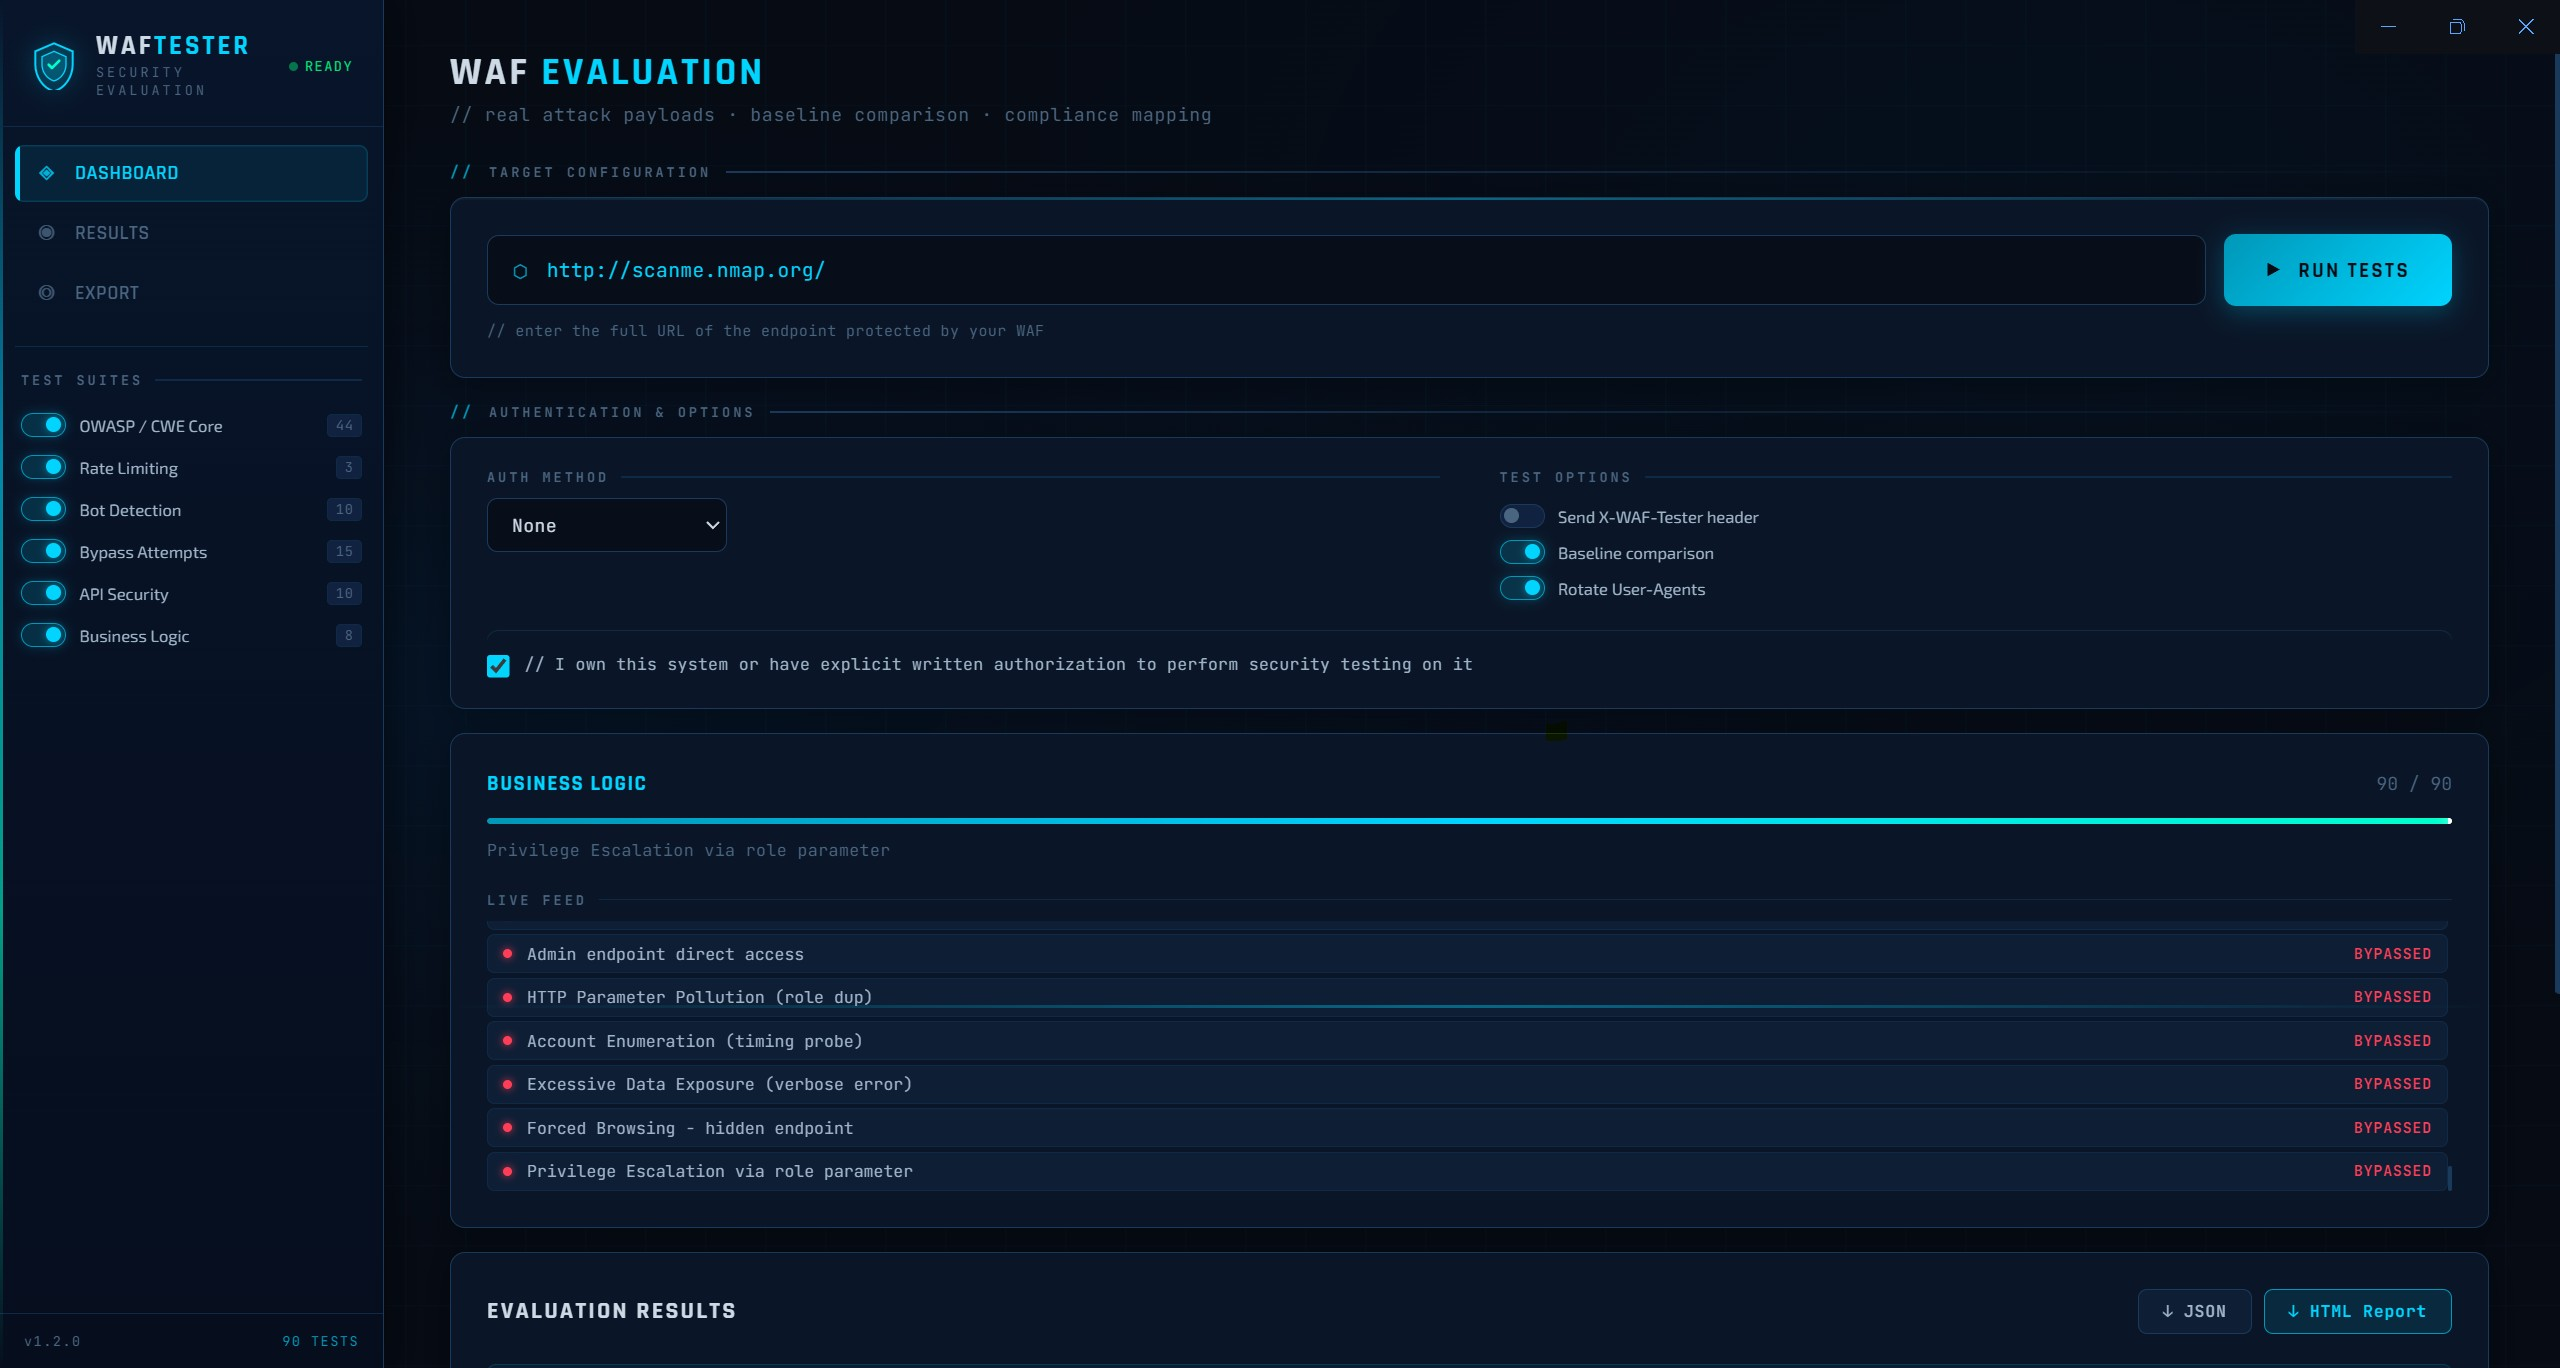 kpomin57/waf-tester
A program for testing WAF functionality
 horizon3ai/cve-2023-27532
Proof-of-concept exploit for CVE-2023-27532 in Veeam Backup and Replication that abuses an unsecured API endpoint to extract credentials from the…
 coffinxp/google-api-key-scanner
Validates Google Maps API keys against 21 endpoints, revealing exposed services with PoC URLs, proxy support, and quiet mode for focused auditing.
 sobri3195/pegasus-pentest-arsenal
A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 shaniidev/bug-reaper
Web2 bug bounty Agent Skill — evidence-based, no AI slop. Covers 18 vulnerability classes across HackerOne, Bugcrowd, Intigriti, and YesWeHack.
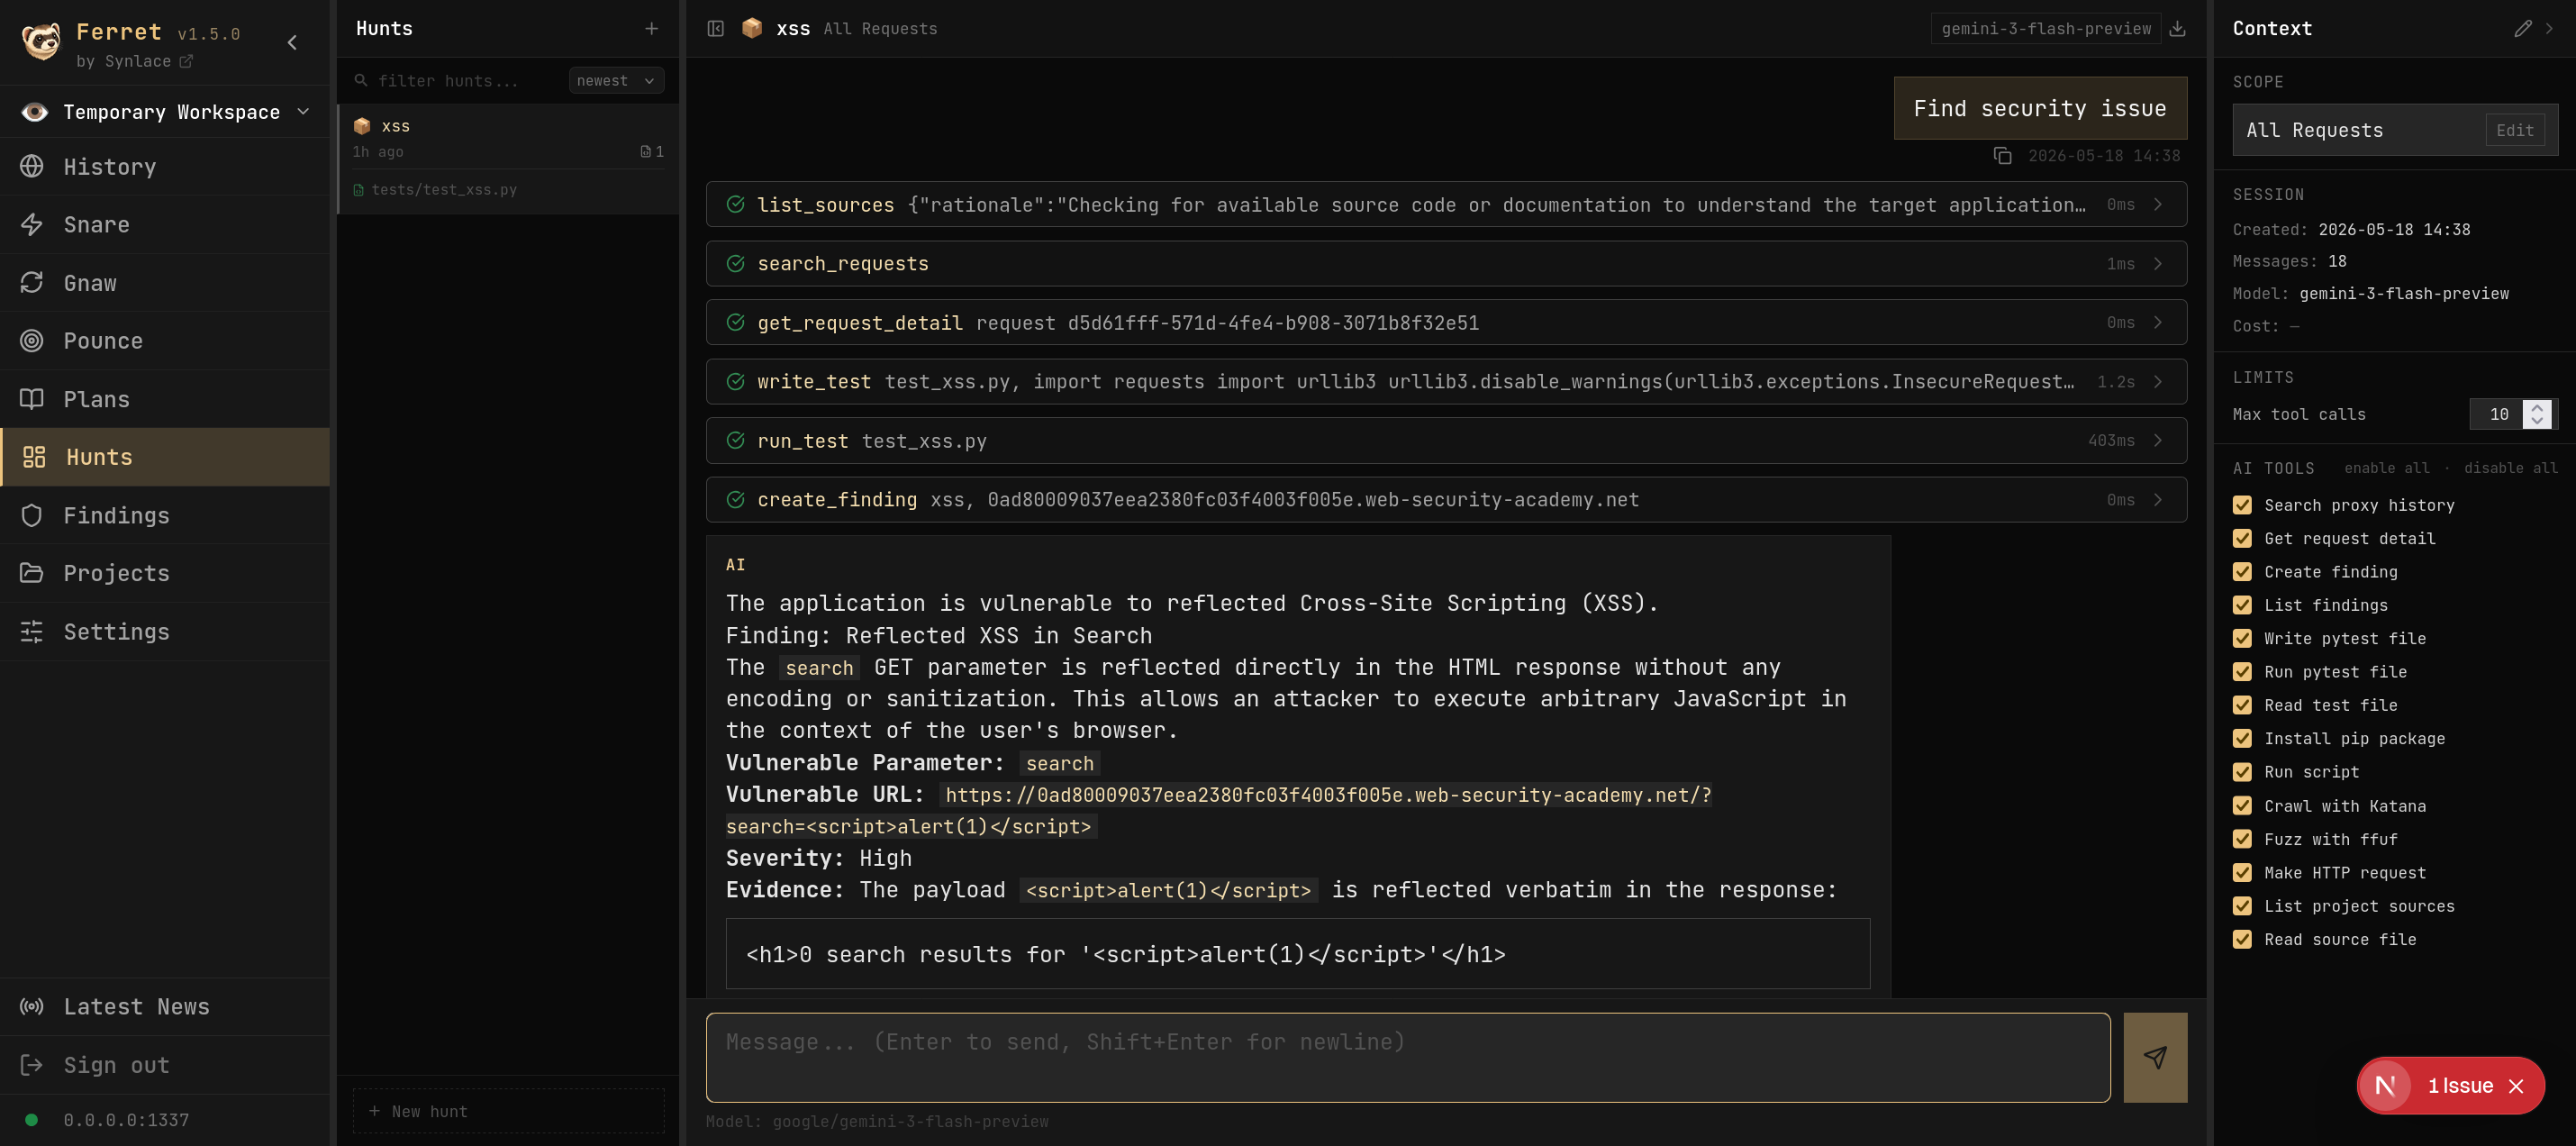 synlace/ferret
The collaborative web app pentest suite
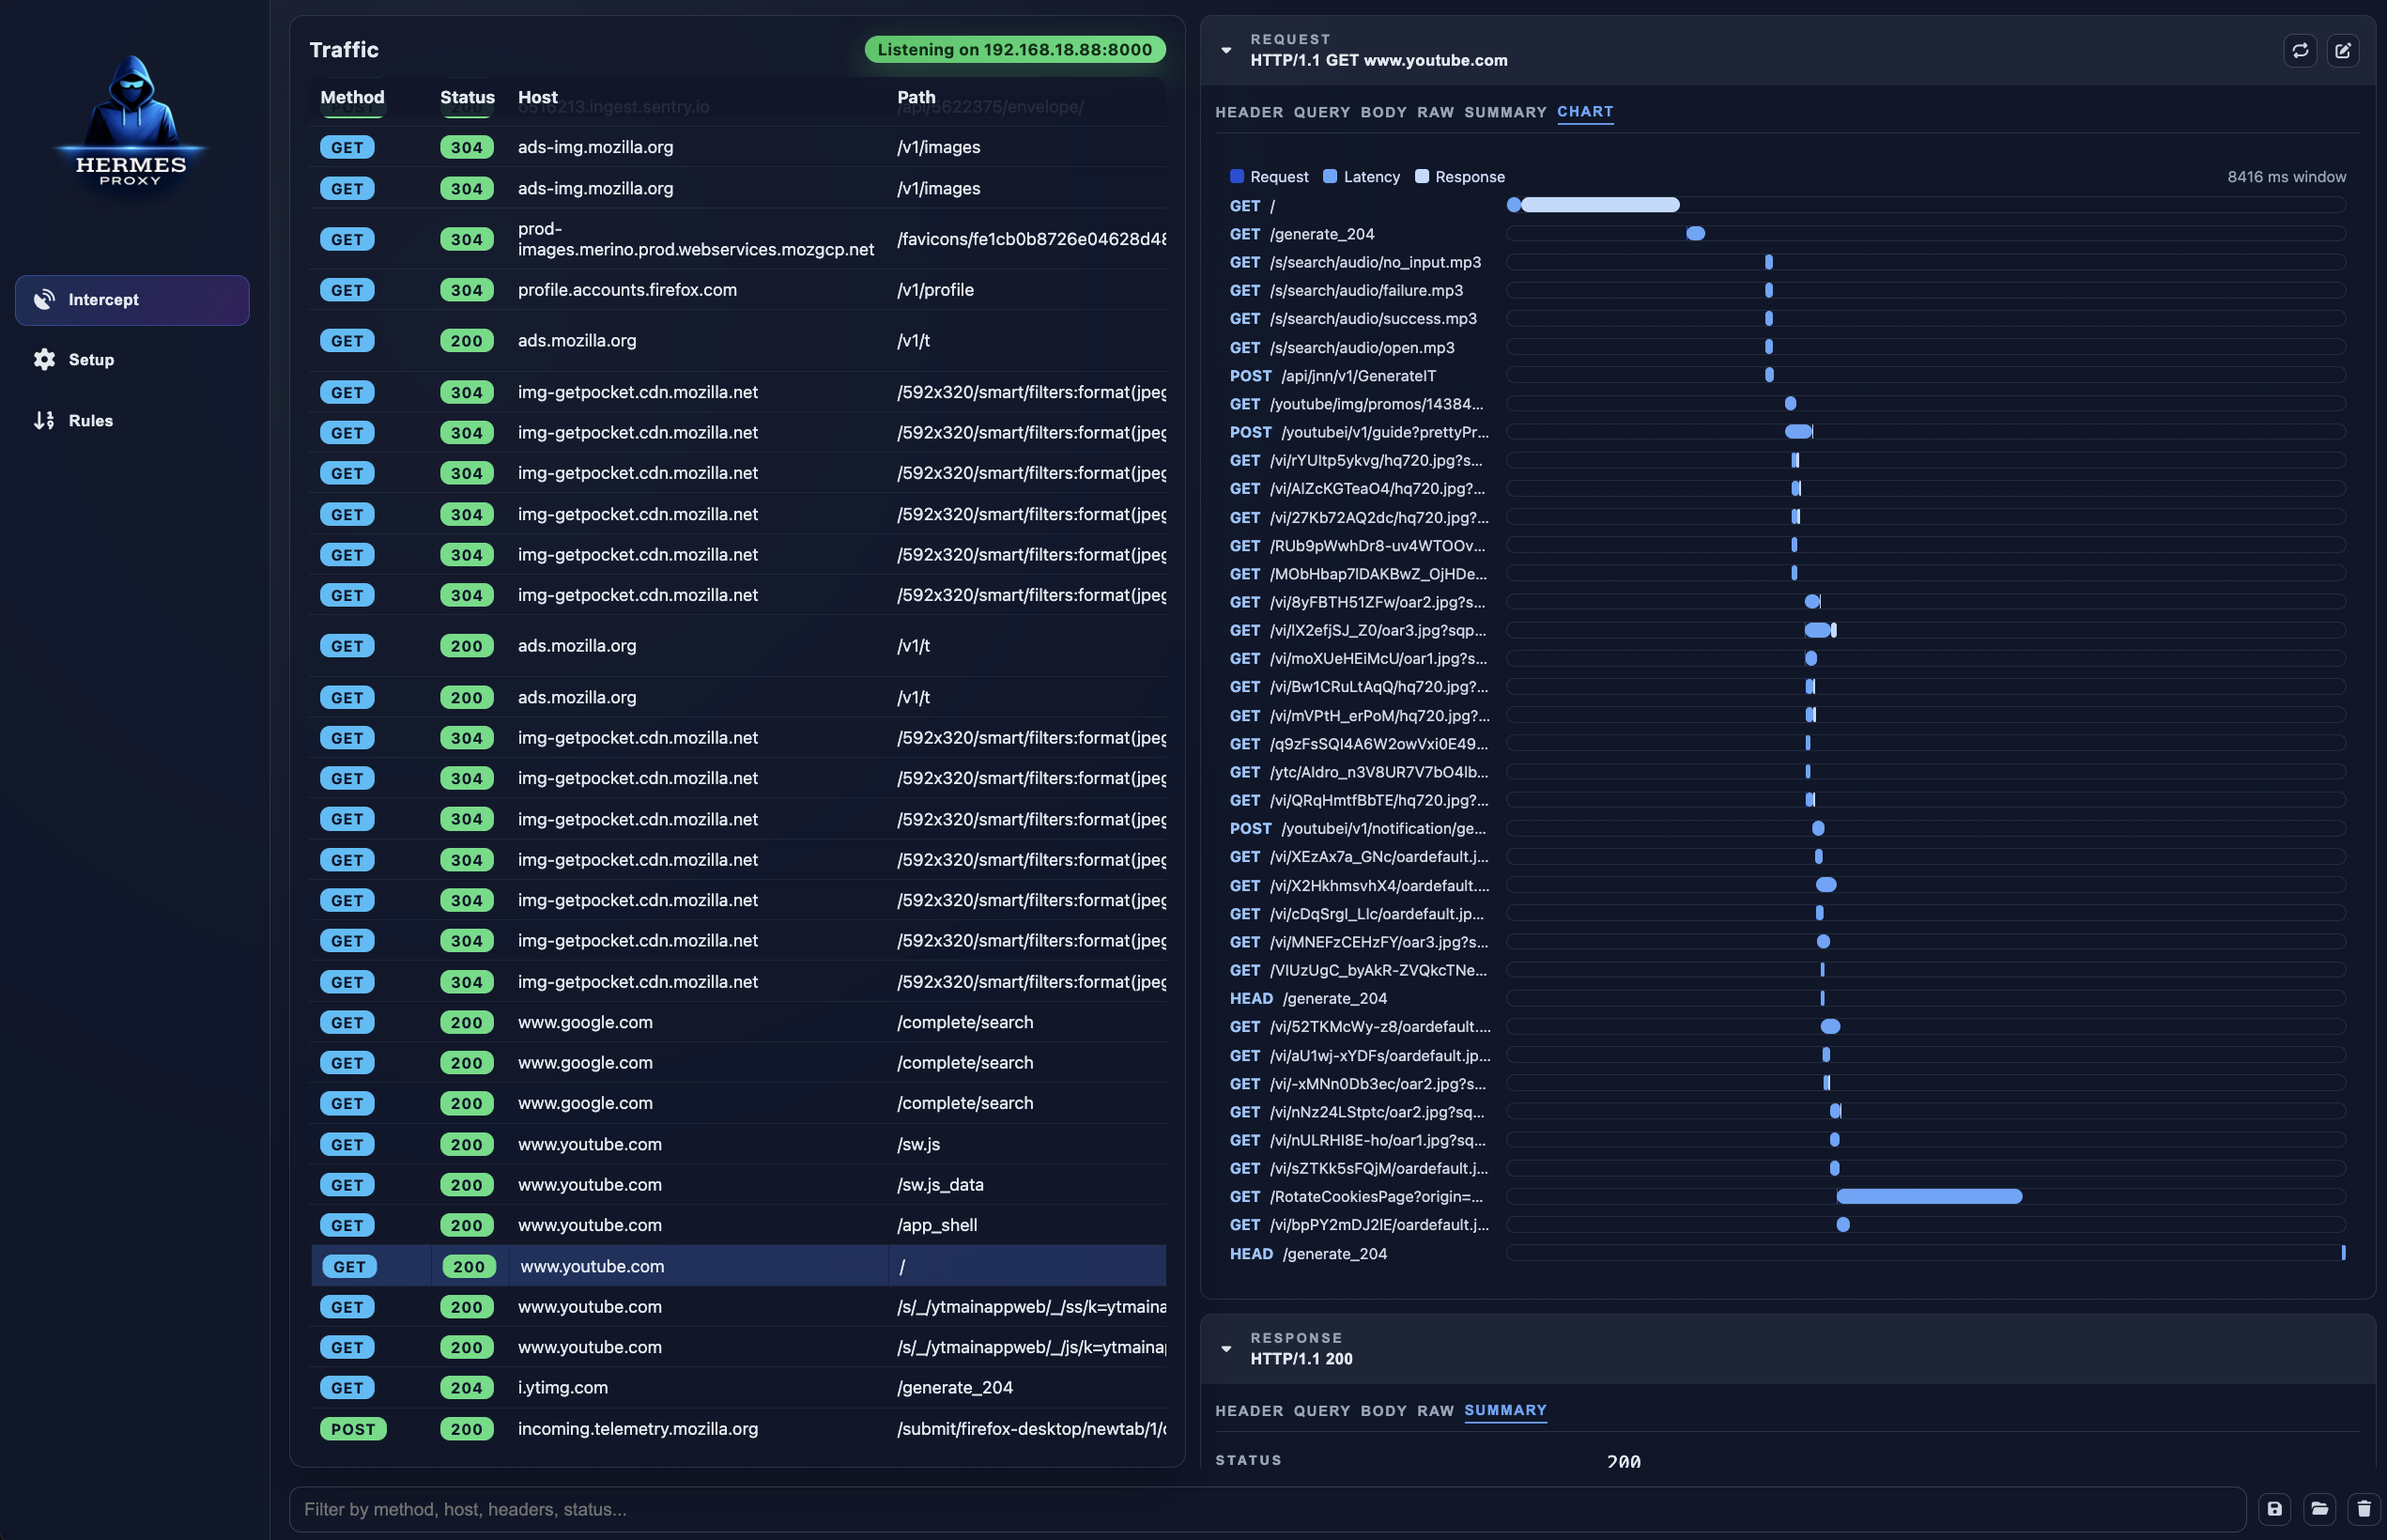 jp/hermes-proxy
Hermes Proxy - HTTP Traffic Analyzer