
Archived
burp-rest-api
 vmware-archive/burp-rest-api
REST/JSON API to the Burp Suite security tool.
api-security-testingpenetration-testingscripting-automation+4
vmware-archive/burp-rest-apiREST/JSON API to the Burp Suite security tool.
 wkeeling/selenium-wire
Extends Selenium's Python bindings to give you the ability to inspect requests made by the browser.
 digeex/raider
DEPRECATED, please use the new repository from OWASP: https://github.com/OWASP/raider
 themalwareguardian/brokeclaudia
CVE-2025-41090 (brokeCLAUDIA): Broken access control in microCLAUDIA, the anti-ransomware platform by CCN-CERT.
 r4nd0mth1ngs/brainproxy
Fast, AI-first web security testing toolkit in Rust: an open-source alternative to ZAP, Burp Suite and the like. Intercepting proxy, scanner, fuzzer…
 keygraphhq/shannon
Shannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes…
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.

 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
 simoneavogadro/android-reverse-engineering-skill
Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…
 ticarpi/jwt_tool
:snake: A toolkit for testing, tweaking and cracking JSON Web Tokens
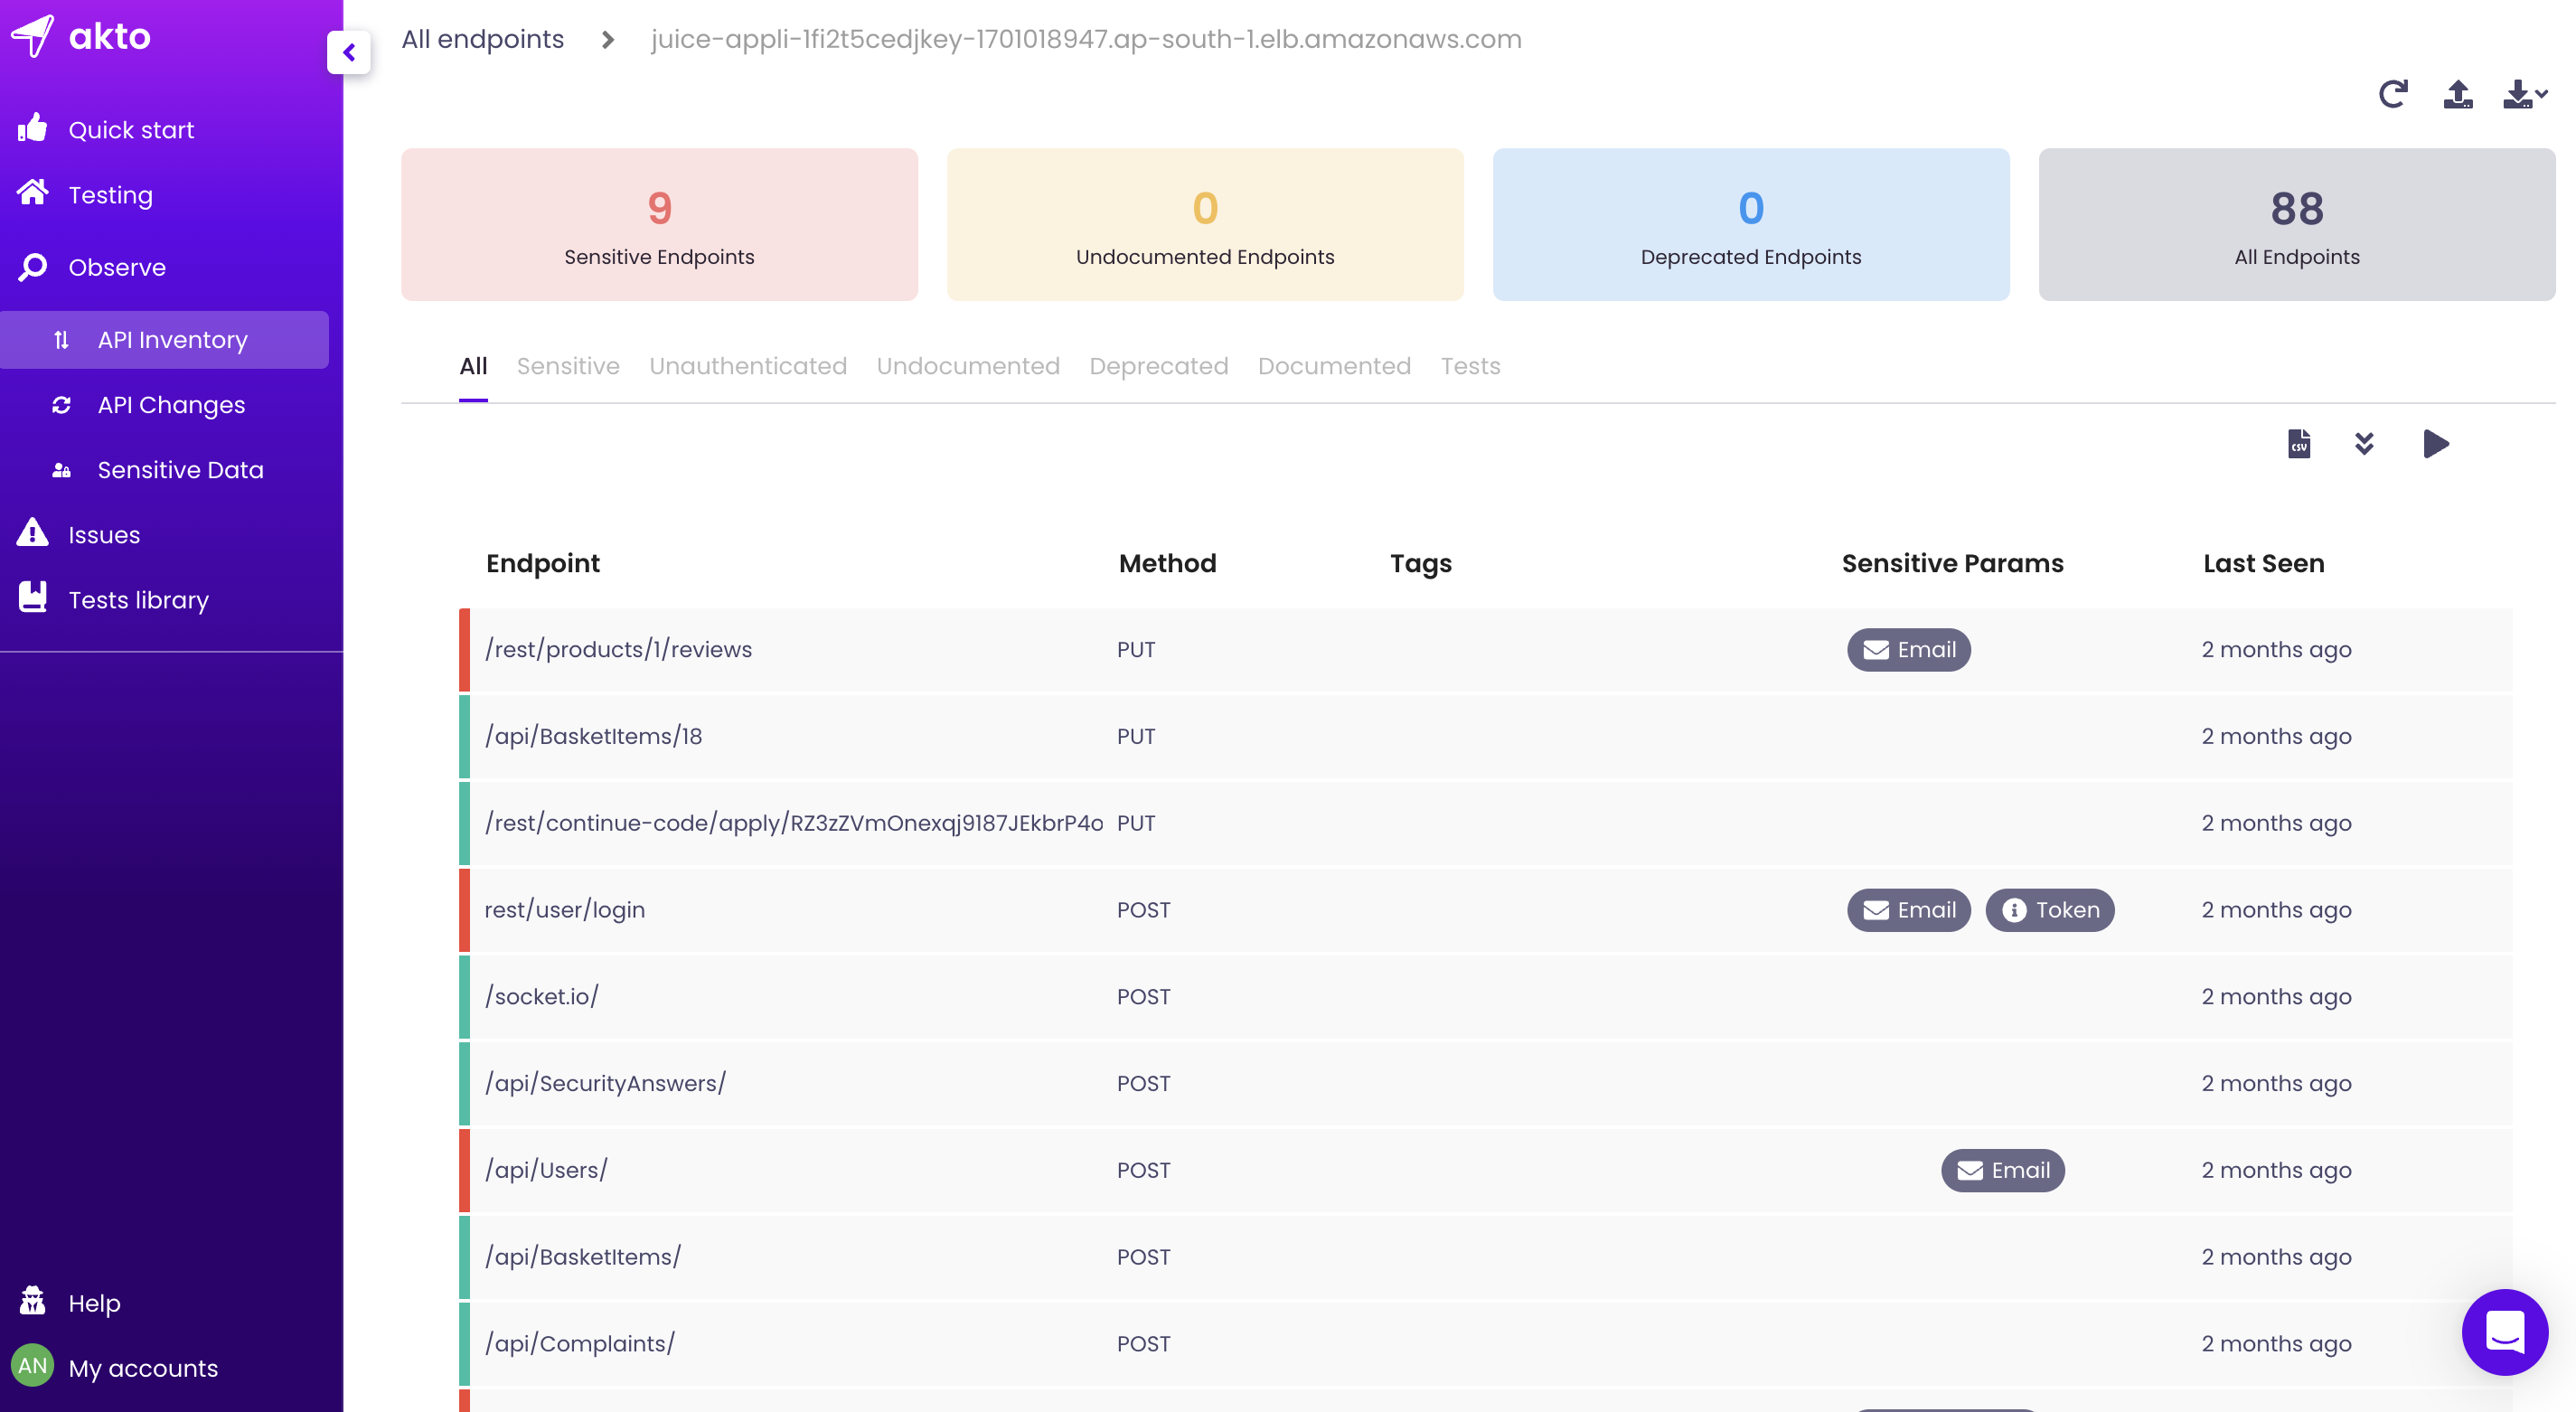 akto-api-security/akto
Open-source API security platform for continuous API discovery, vulnerability testing, and runtime threat detection. Integrates with CI/CD pipelines…
 assetnote/kiterunner
High-speed API and web content discovery tool that bruteforces routes using compiled Swagger datasets, supporting depth scanning, custom wordlists,…
 erev0s/vampi
Vulnerable REST API with OWASP top 10 vulnerabilities for security testing
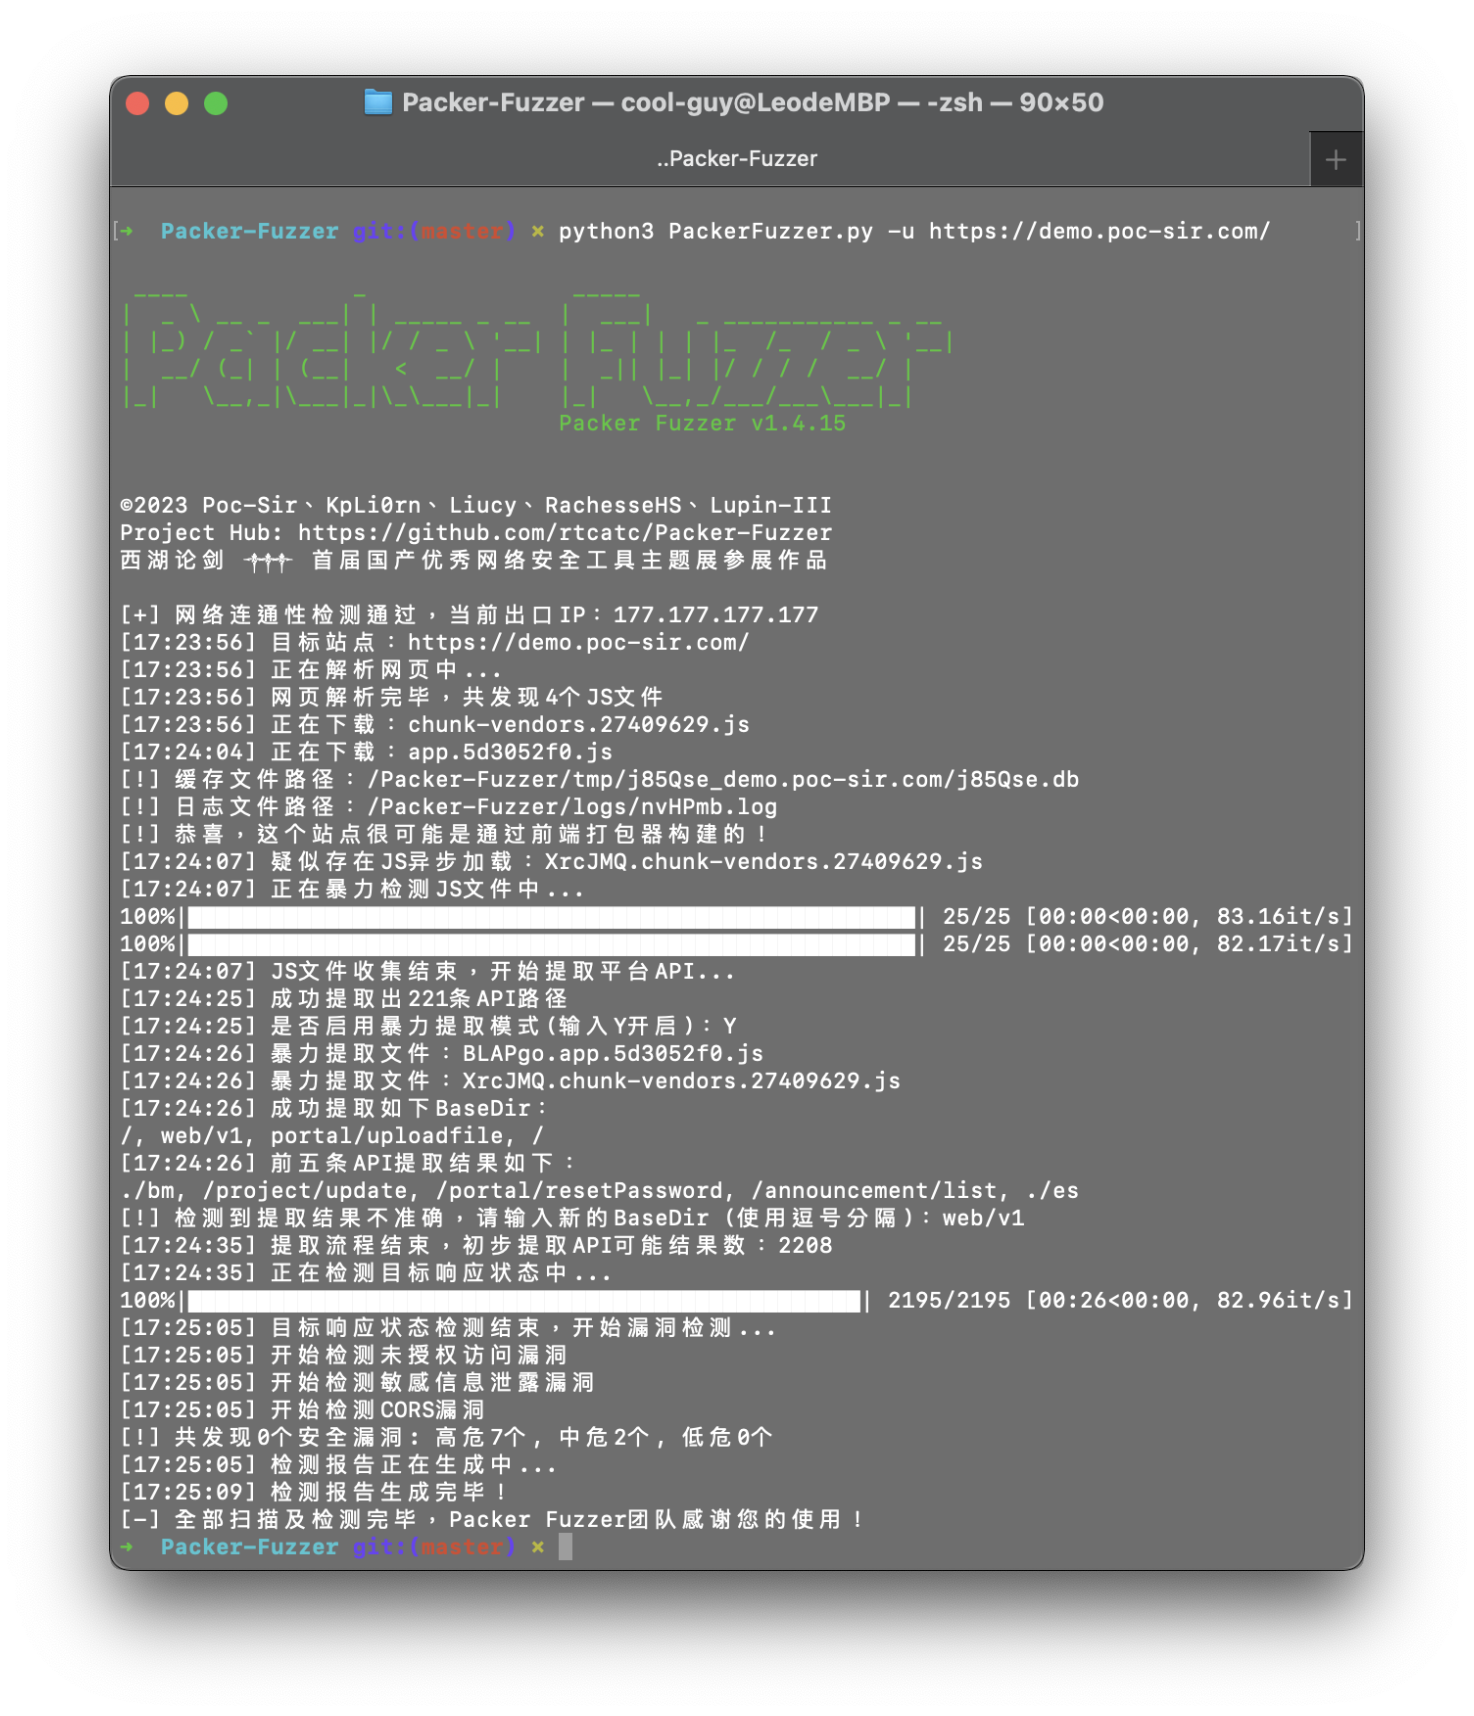 rtcatc/packer-fuzzer
Packer Fuzzer is a fast and efficient scanner for security detection of websites constructed by javascript module bundler such as Webpack.
 projectdiscovery/nuclei-burp-plugin
Burp Suite plugin for generating and executing Nuclei vulnerability templates directly from HTTP requests and responses, with YAML auto-complete and…