
http-desync-guardian
 aws/http-desync-guardian
Analyze HTTP requests to minimize risks of HTTP Desync attacks (precursor for HTTP request smuggling/splitting).
api-security-testingstatic-analysisvulnerability-analysis+1
274
aws/http-desync-guardianAnalyze HTTP requests to minimize risks of HTTP Desync attacks (precursor for HTTP request smuggling/splitting).
 ethicalhackingplayground/ssrf-king
SSRF plugin for burp Automates SSRF Detection in all of the Request
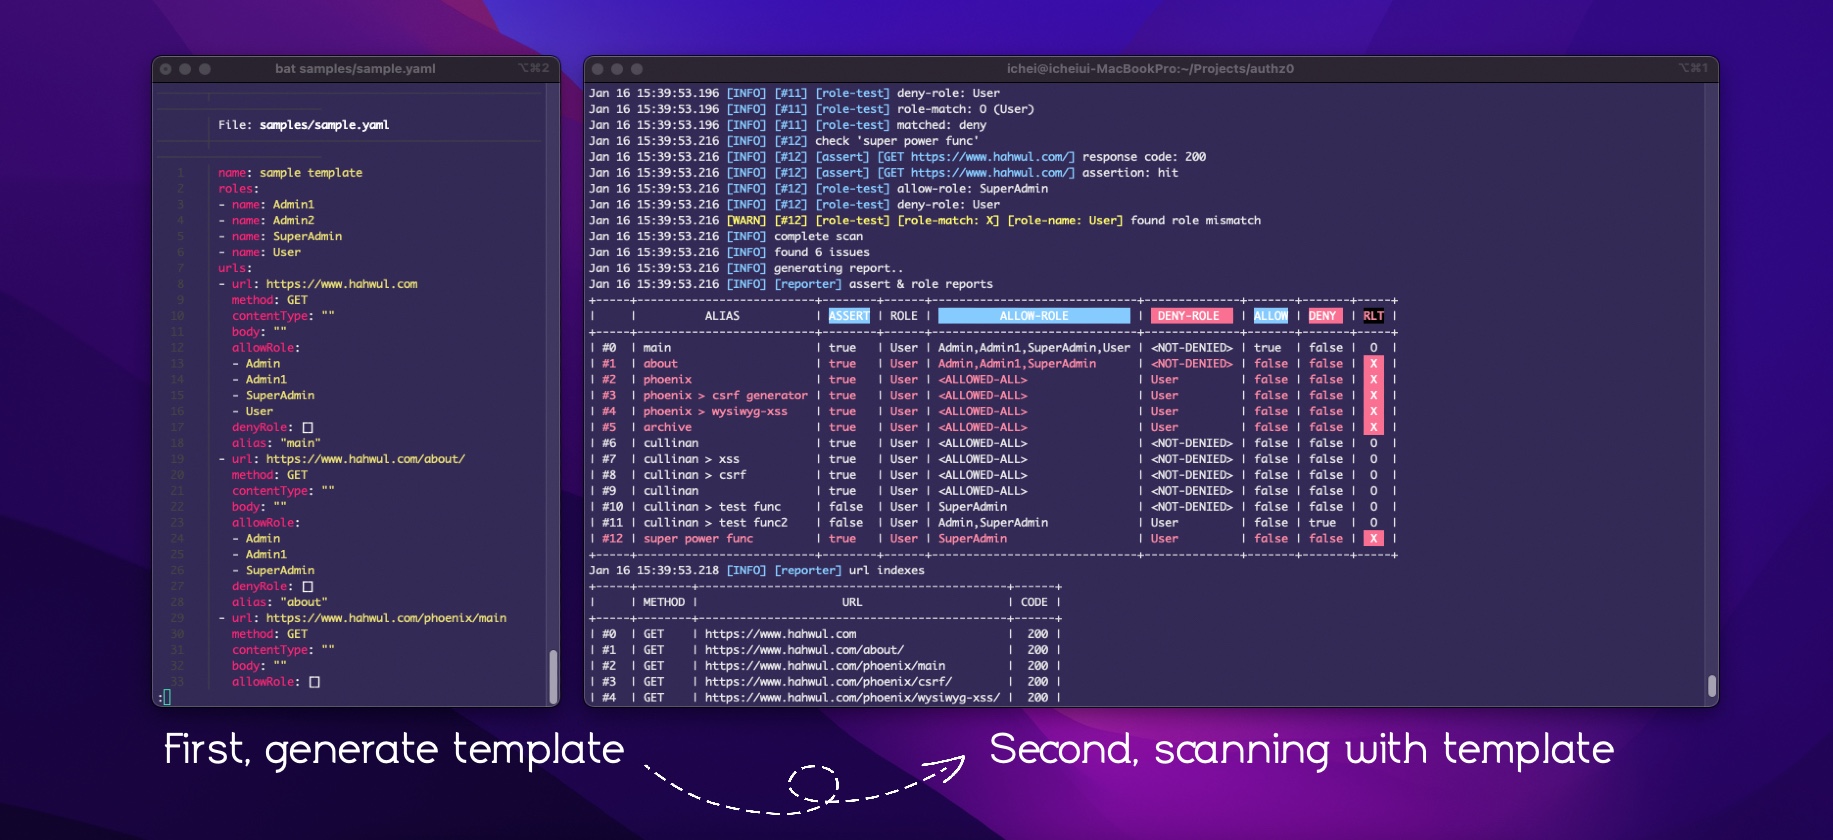 hahwul/authz0
Automated authorization testing tool that detects unauthorized access by scanning URLs with role-based credentials using YAML templates.
 codewatchorg/sqlipy
SQLiPy is a Python plugin for Burp Suite that integrates SQLMap using the SQLMap API.
 opaxial/cve-2026-9830
CVE-2026-9830 Proof of Concept
 yalcinyolalan/wssat
WEB SERVICE SECURITY ASSESSMENT TOOL
 ethicalhackingplayground/tproxer
A Burp Suite extension made to automate the process of finding reverse proxy path based SSRF.
 ngalongc/openapi_security_scanner
Automated authorization security scanner for OpenAPI-based APIs. Tests GET endpoints with multiple credential sets to detect privilege escalation and…
 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
 brinhosa/apidetector
Multi-threaded scanner for detecting exposed Swagger/OpenAPI endpoints across web domains and subdomains, with automatic XSS detection, PoC…
 net-hunter121/api-wordlist
Curated wordlists of API function names, verbs, and nouns for fuzzing web application endpoints with Burp Suite Intruder.
 impact-i/x8-burp
Hidden parameters discovery suite
 moopinger/smugglefuzz
A rapid HTTP downgrade smuggling scanner written in Go.
 moniik/poc_salesforce_lightning
Academic purposes only. Attack against Salesforce lightning with guest privilege.
 nicholasaleks/crackql
GraphQL penetration testing tool that exploits weak rate limits and cost analysis to brute-force credentials, bypass 2FA, enumerate users, and fuzz…
 hahwul/mzap
⚡️ Multiple target ZAP Scanning
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 hahwul/smugglex
Rust-powered HTTP Request Smuggling Scanner.