

CVE2022-1388_TestAPI
 bandit92/cve2022-1388_testapi
A Test API for testing the POC against CVE-2022-1388
api-security-testingexploitationpenetration-testing+2
4
bandit92/cve2022-1388_testapiA Test API for testing the POC against CVE-2022-1388
 7h30th3r0n3/cve-2026-53625-glpi-poc
GLPI Privilege Escalation via authtype Manipulation PoC - CVE-2026-53625. Ethical PoC for the GLPI vulnerability allowing a Technician to take full…
 kabiri-labs/cve-2024-40094
This script exploits the CVE-2024-40094 vulnerability in graphql-java
 oscerd/cve-2026-48206
Reproducer for CVE-2026-48206: Apache Camel camel-jira IssueKey (and other non-Camel-prefixed) header injection driving arbitrary JIRA issue…
 biitts/cve-2026-54917-seaweedfs-cross-bucket-traversal
PoC + analysis for CVE-2026-54917 — SeaweedFS S3 gateway cross-bucket path traversal (CVSS 10.0, <4.30). Read/write any bucket via .. in the object…
 sevdakhidirova/cve-2025-32375-poc
Python proof-of-concept exploit for CVE-2025-32375 in BentoML, demonstrating and validating the vulnerability against affected deployments.
 oscerd/cve-2026-49099
PoC reproducer for CVE-2026-49099 (Apache Camel camel-salesforce): the non-Camel-prefixed sObjectQuery header escapes the HTTP header filter and…
 oscerd/cve-2026-48204
Reproducer for CVE-2026-48204: Apache Camel camel-mongodb-gridfs gridfs.* header injection overriding the GridFS operation (enumerate/read/delete…
 oscerd/cve-2026-46592
Reproducer for CVE-2026-46592: Apache Camel camel-cxf operationName header injection redirecting the invoked SOAP operation (confused deputy) from a…
 loaxert/cve-2025-59528-poc
PoC for CVE-2025-59528 used to achieve remote code execution on the Silentium machine at HTB
 dz-y/azure-apim-dev-portal-signup-bypass
Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…
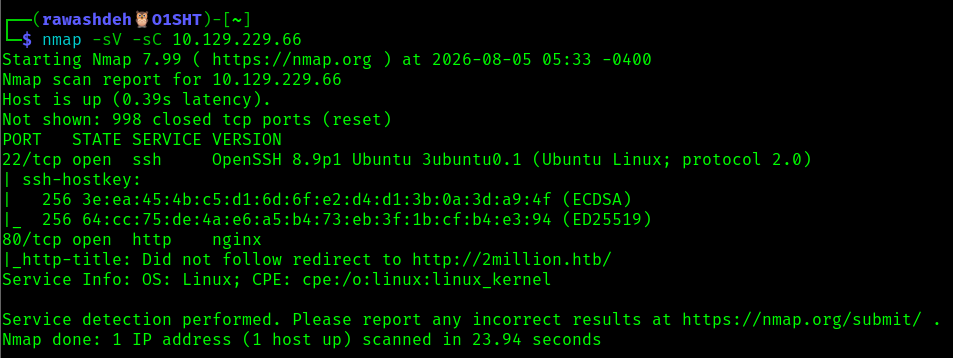 abedallarawashdeh/htb-twomillion-machine
Hack The Box TwoMillion machine writeup — JWT/invite-code bypass, IDOR, command injection, and CVE-2023-0386 privilege escalation.
 csinexus/mcpshield
Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)
 curtail-inc/hello-regrade-security
Find the vulnerability your tests were never written to catch. A ReGrade demo modeling CVE-2023-5968: catch a password-hash leak by comparing an app…
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
 foxcornlab/thc-bloodmiami
AI chat-box pentesting tool in C: fires language (SQLi/NoSQL/XSS/SSTI) and prompt injection payloads at chat interfaces and flags the ones that bite
 renzi25031469/cve-2026-19478
Detects CVE-2026-19478 in GitLab CE/EE with a non-destructive Nuclei template that triggers the GraphQL fallback-field method invocation via touch…
 y-security/ylog4j
PortSwigger Burp Plugin for the Log4j (CVE-2021-44228)