

gori
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
api-security-testingfuzzinginformation-gathering+8
hahwul/goriA fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 akabe1/oauthscan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
 impact-i/x8-burp
Hidden parameters discovery suite

 invuls/pentest-projects/pcf
Opensource, cross-platform and portable toolkit for automating routine processes when carrying out various works for testing!
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
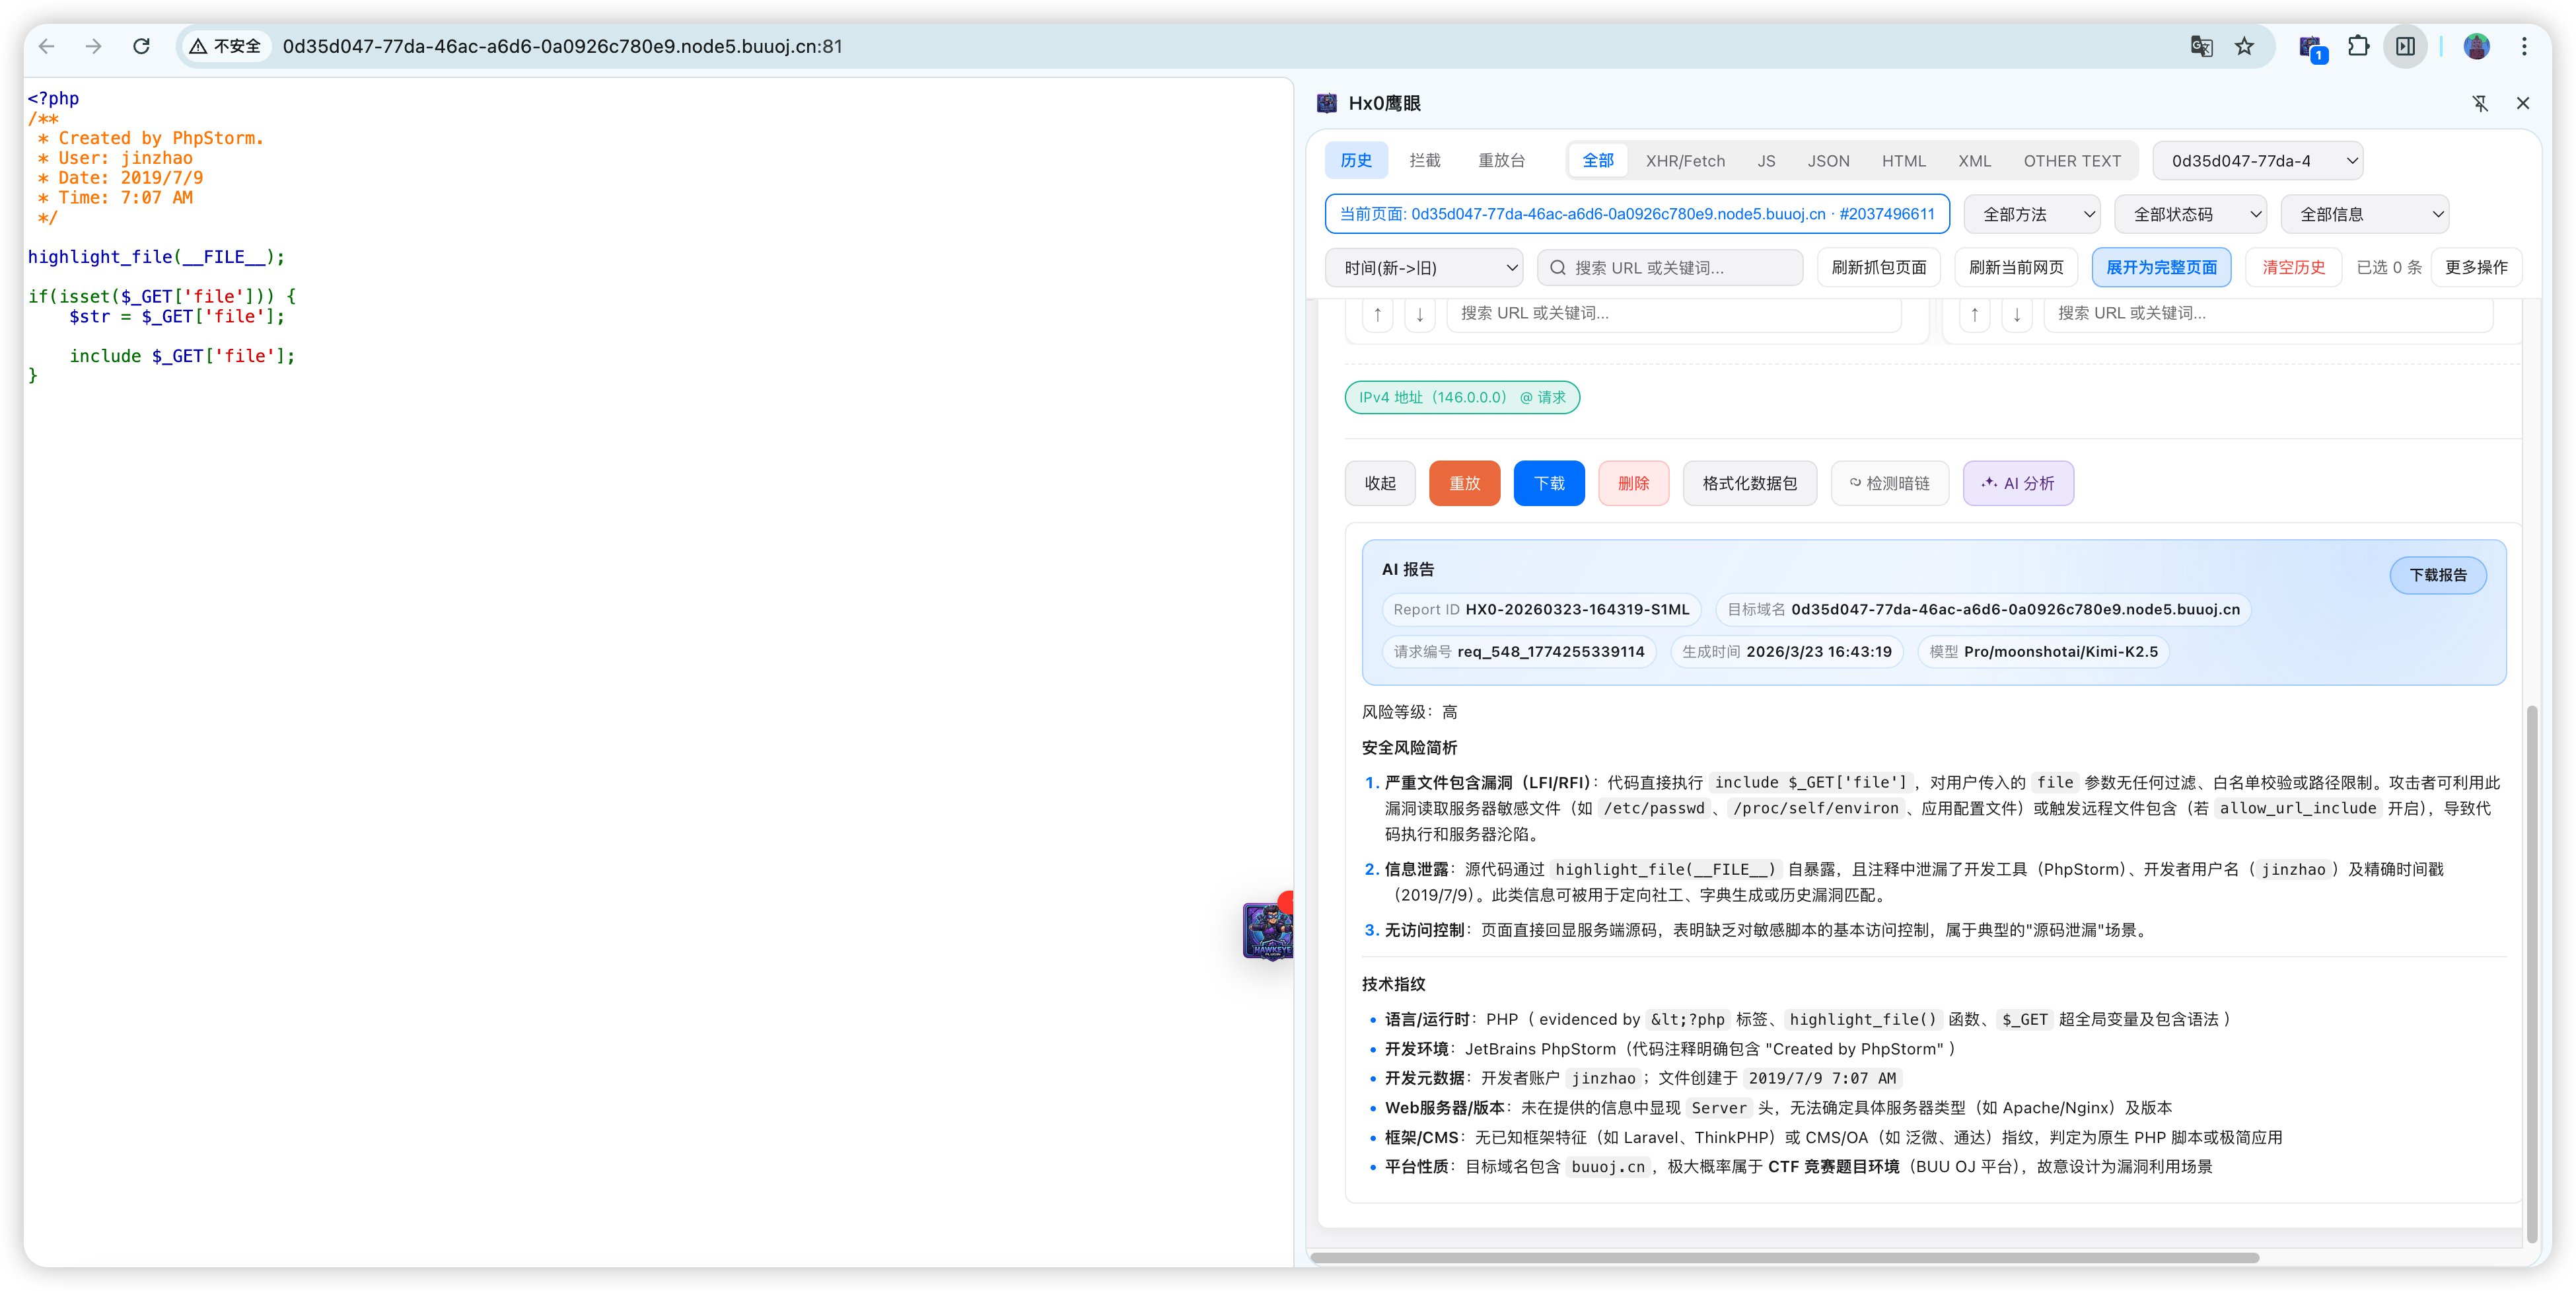 asaotomo/hx0-hawkeye
一个轻量级浏览器抓包与安全分析扩展,在浏览器侧边栏中即可完成抓包、拦截、修改、重放、规则检测与AI辅助分析的完整工作流。(A lightweight browser extension for traffic capture and security analysis, enabling…
 google/aura-inspector
Automated security testing tool for Salesforce Experience Cloud that discovers misconfigured Aura applications, accessible records, and unauthorized…
 pentestgeek/burpcommander
Ruby command-line interface to Burp Suite's REST API
 cybervelia/graphicator
Automated GraphQL schema enumeration and data extraction tool that iterates introspection documents, reconstructs queries, and saves responses for…
 rub-nds/rest-attacker
Automated penetration testing framework for REST APIs with OpenAPI-driven test generation, 32 OWASP-based security tests, and built-in access control…
 coffinxp/google-api-key-scanner
Validates Google Maps API keys against 21 endpoints, revealing exposed services with PoC URLs, proxy support, and quiet mode for focused auditing.
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
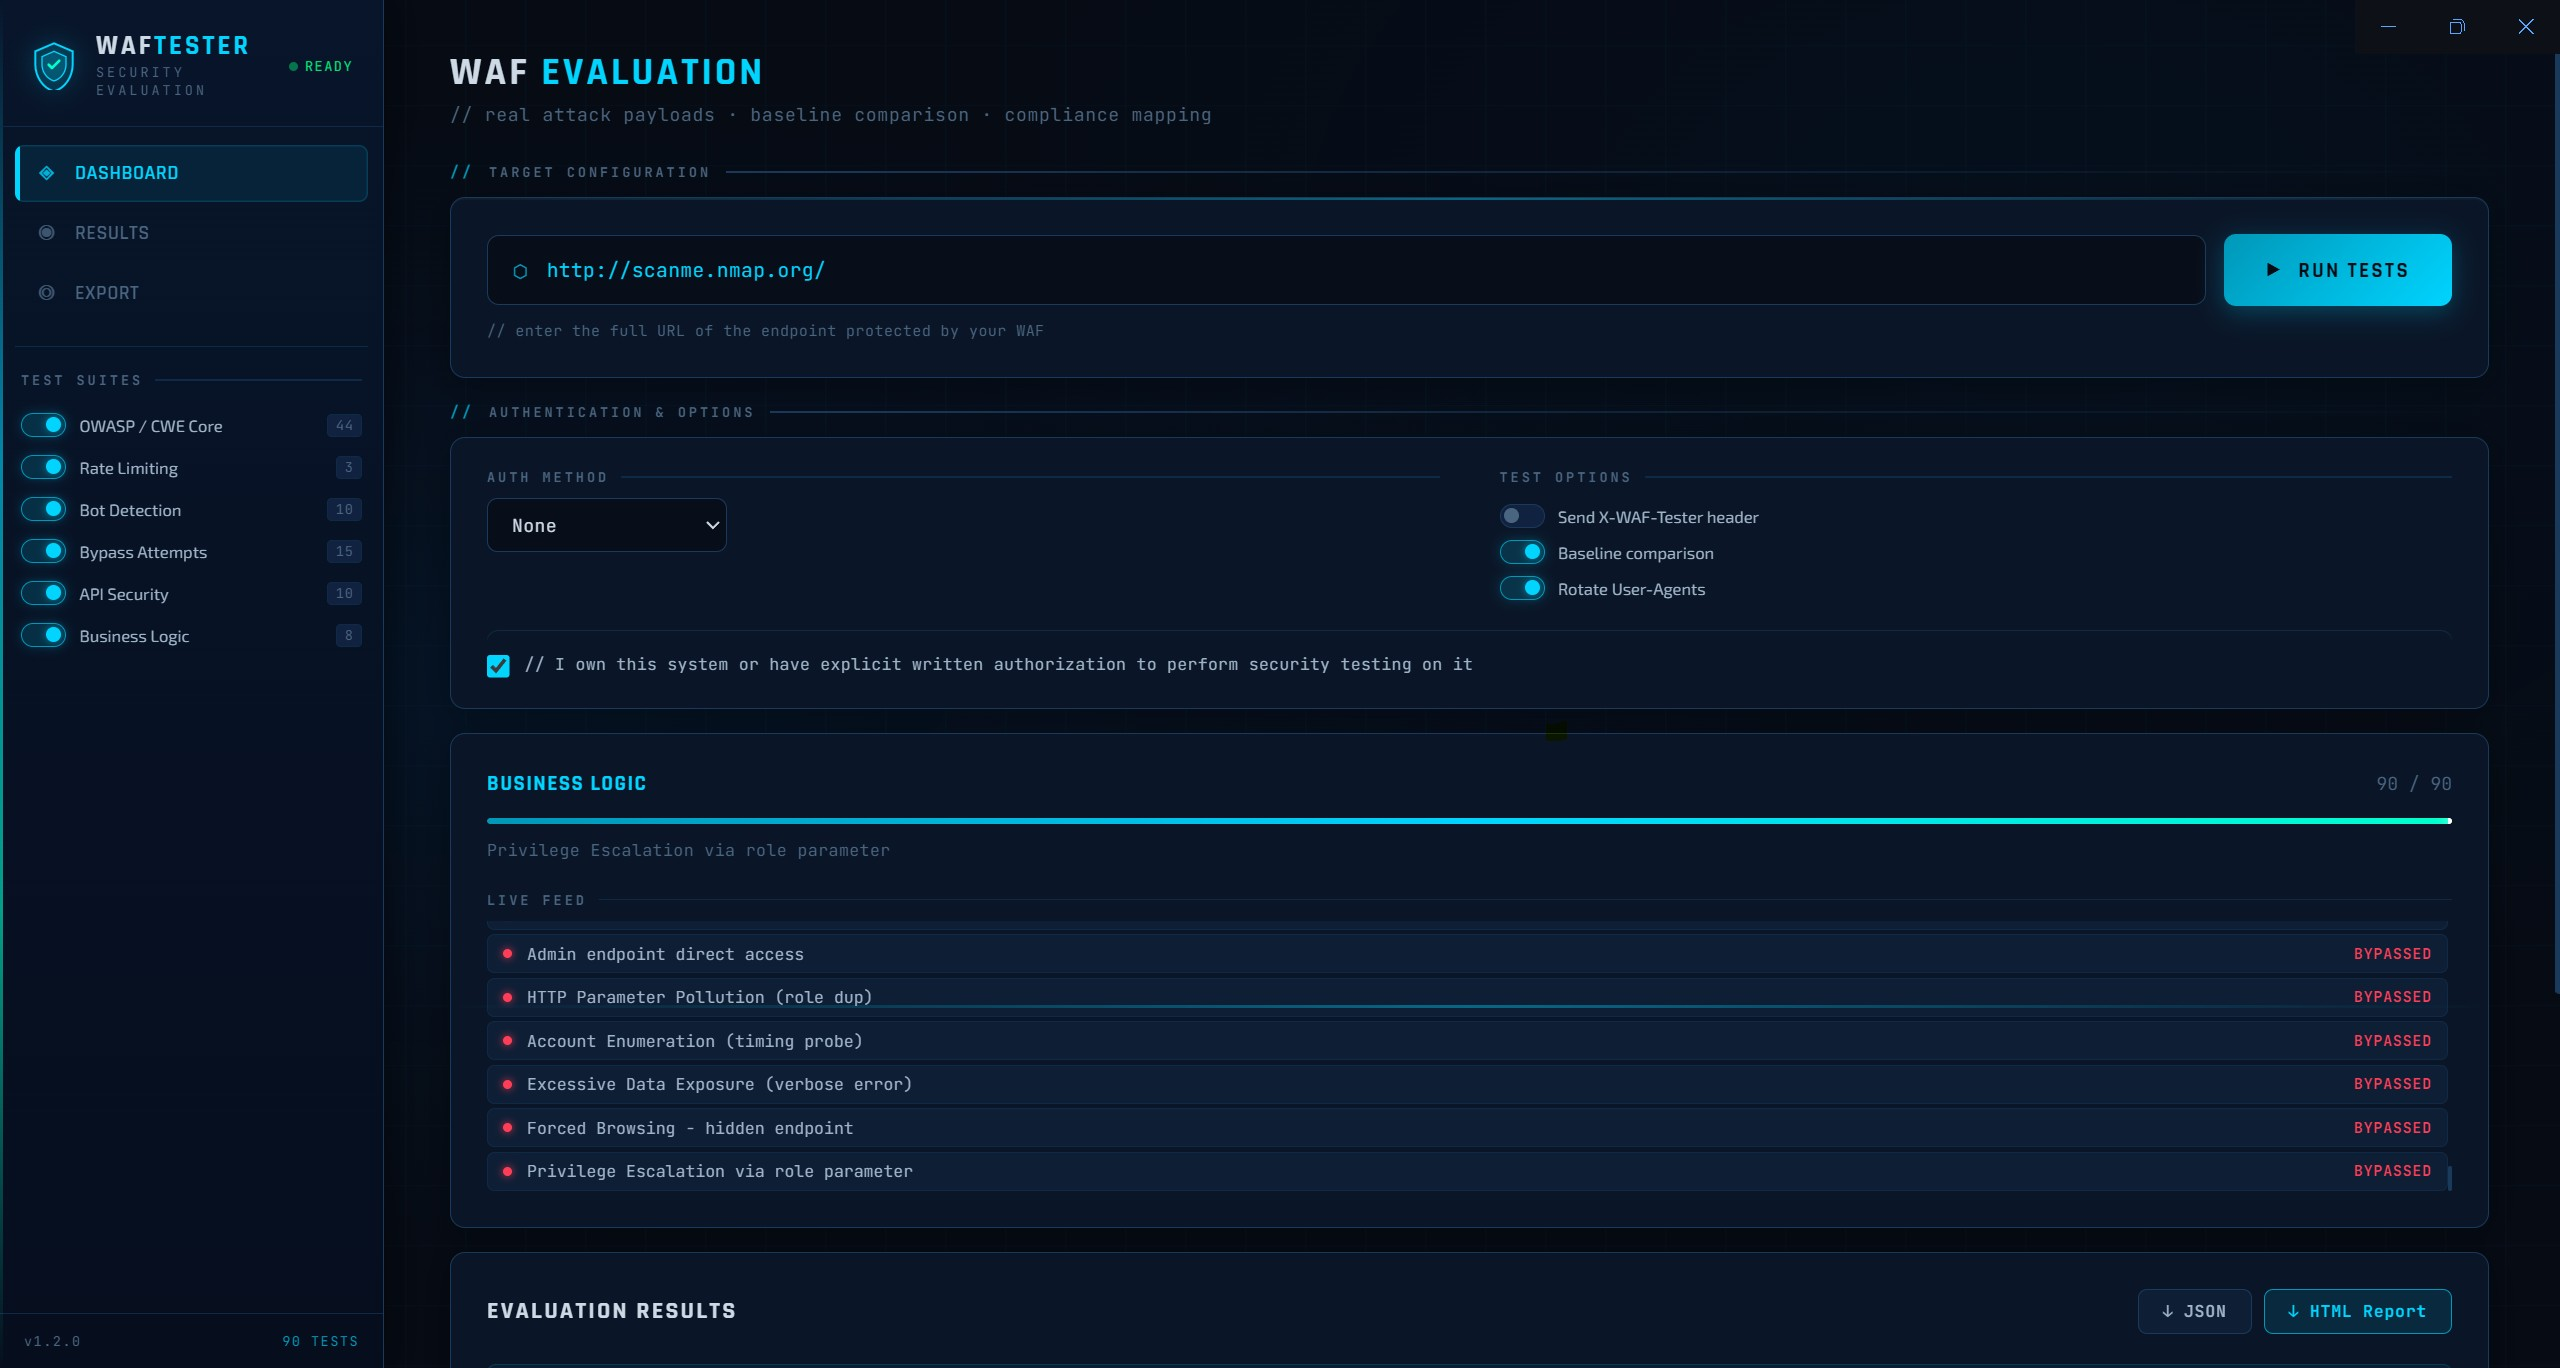 kpomin57/waf-tester
A program for testing WAF functionality
 jas502n/burpsuite_pro_v1.7.37
Comprehensive web application security testing platform featuring advanced scanning engine, intercepting proxy, and automated vulnerability detection…
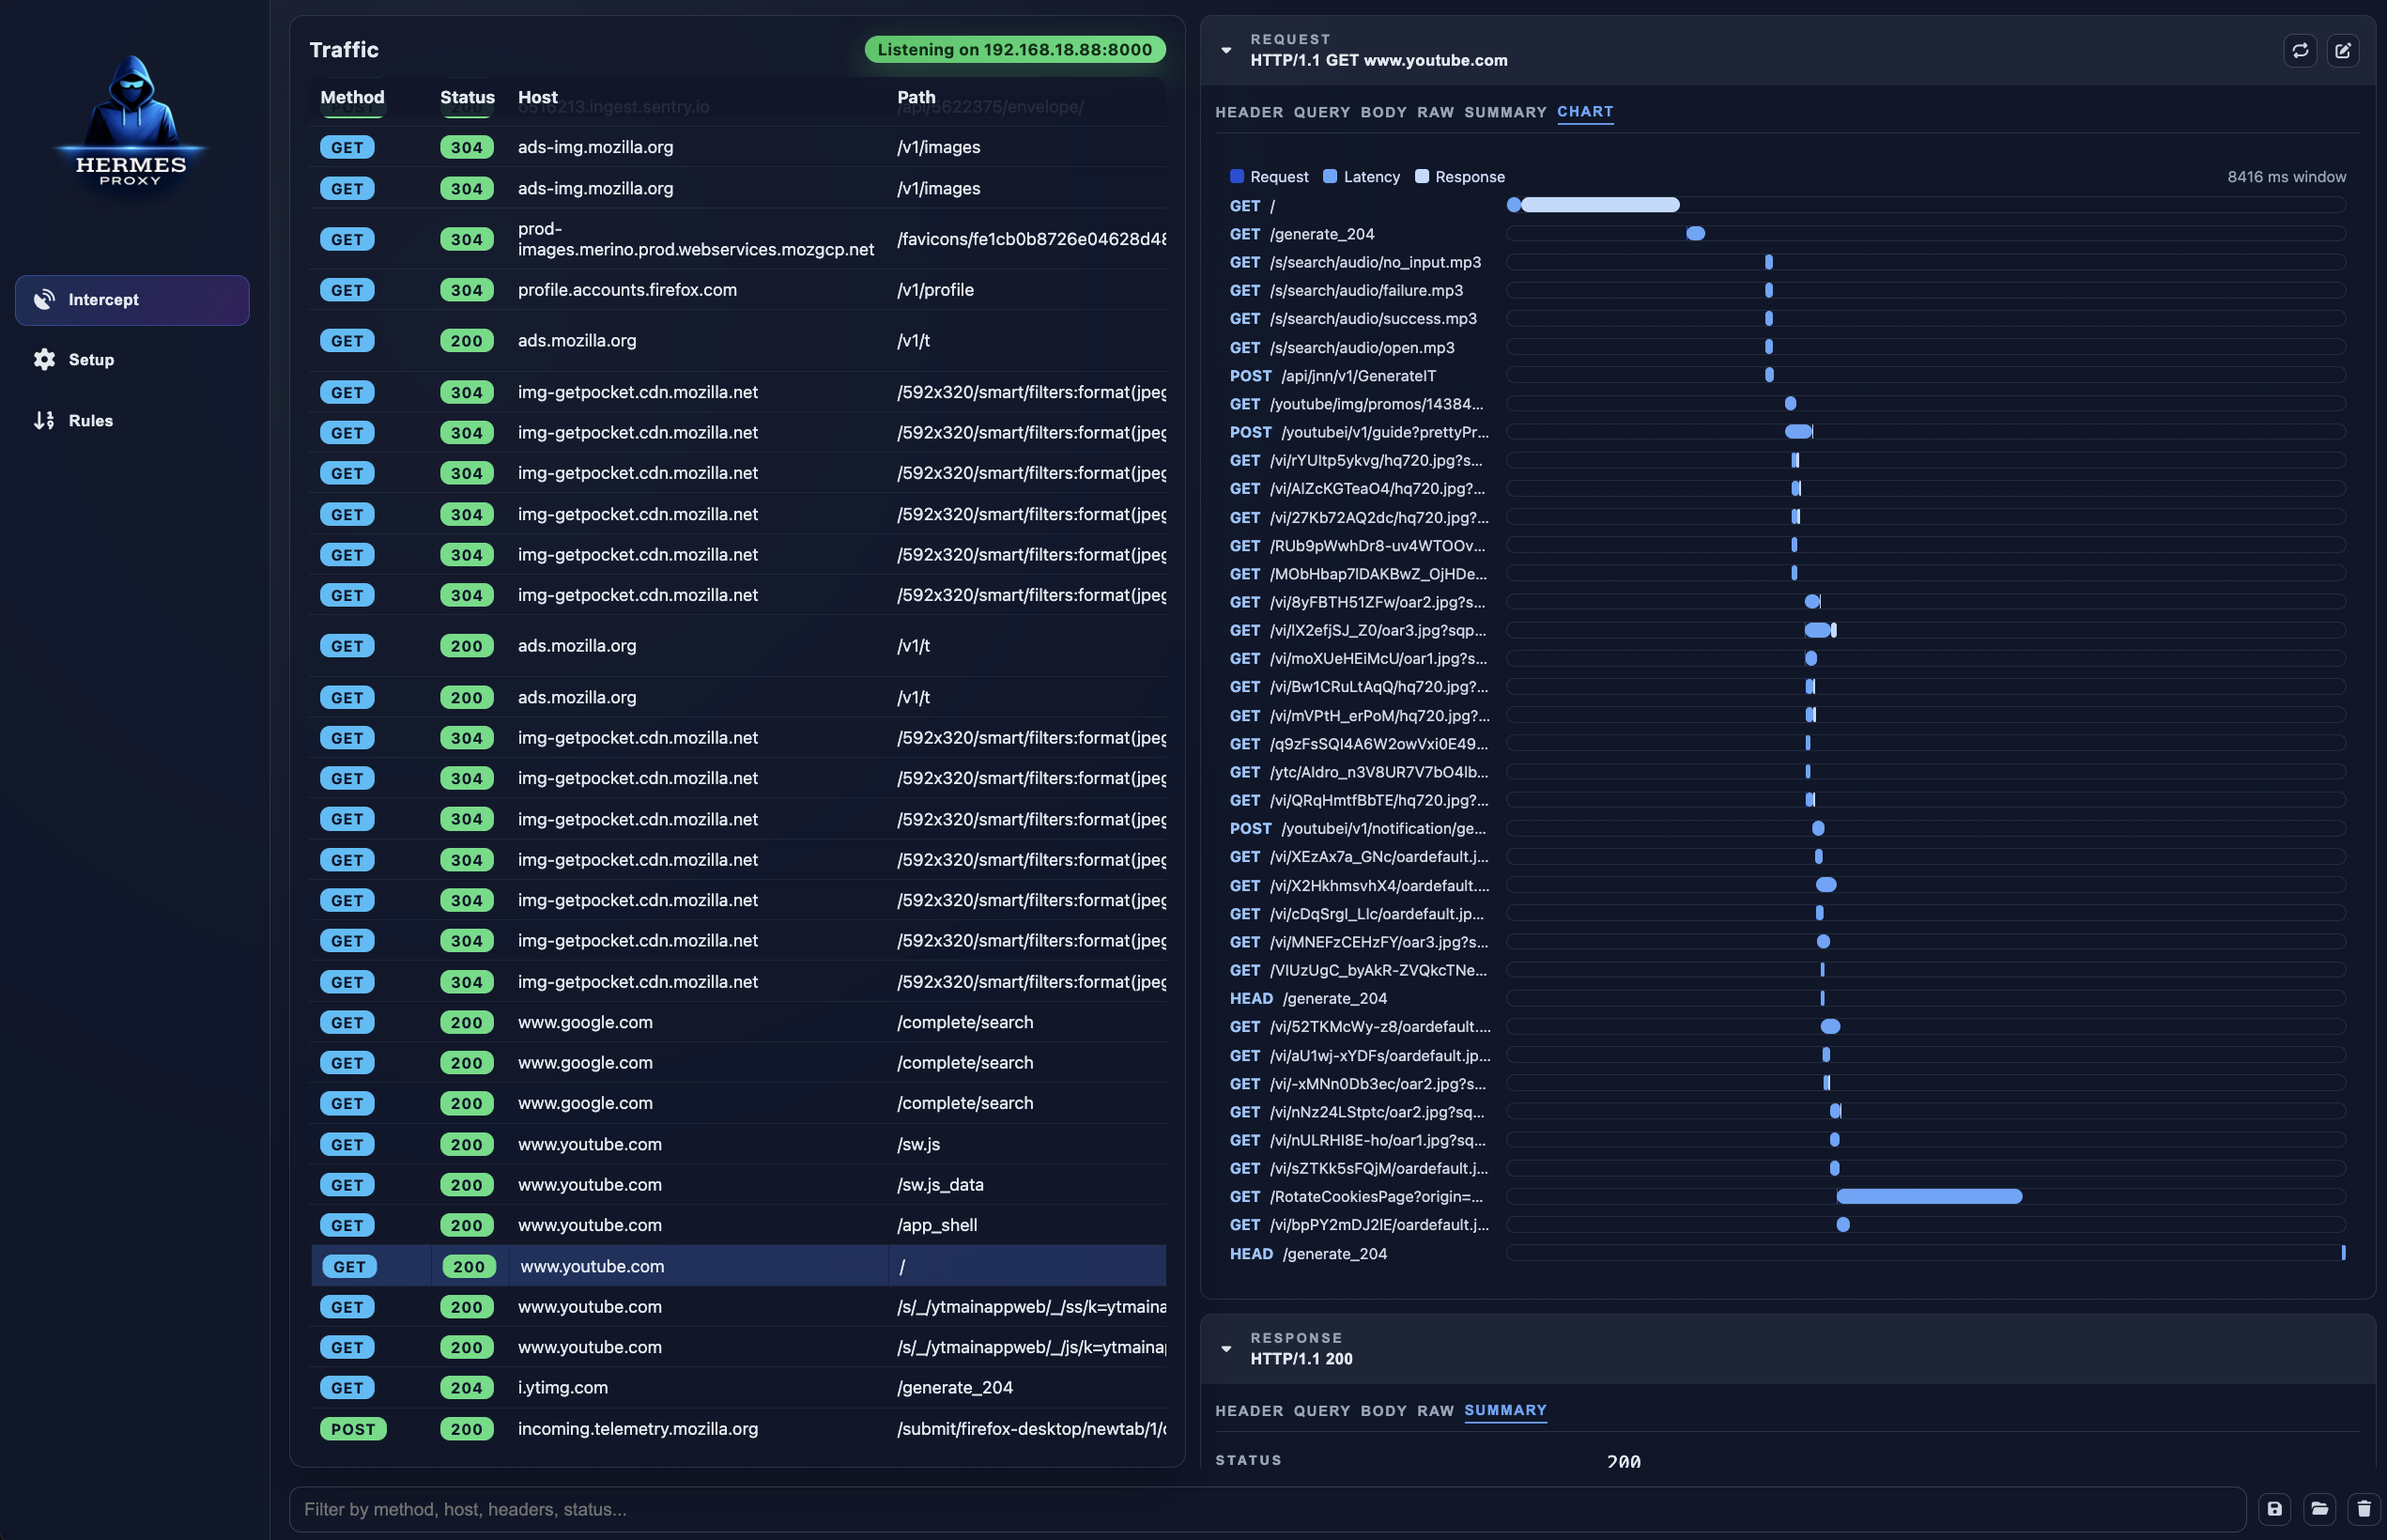 jp/hermes-proxy
Hermes Proxy - HTTP Traffic Analyzer
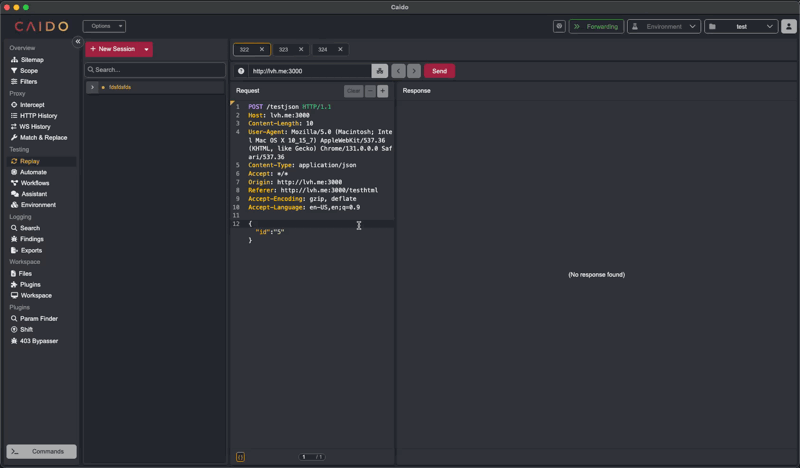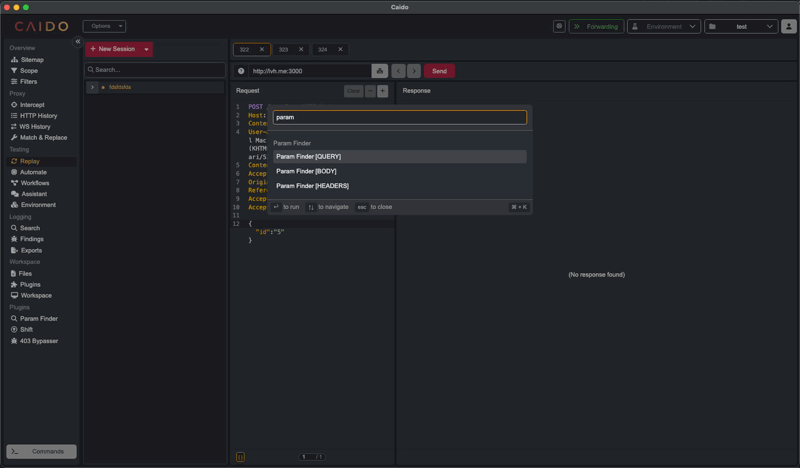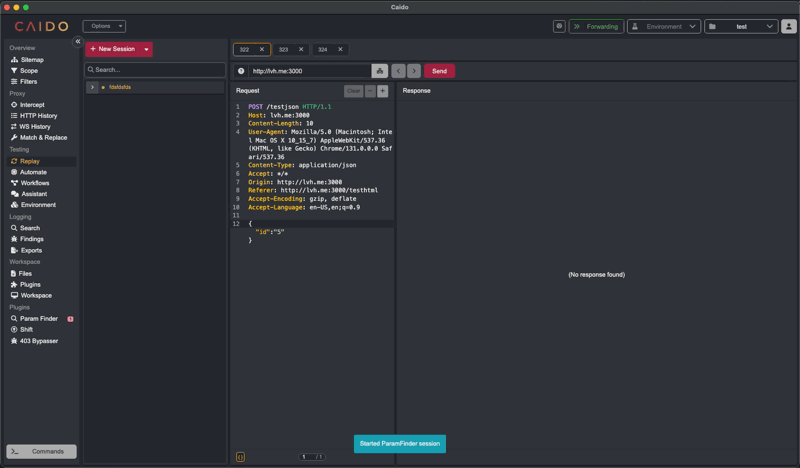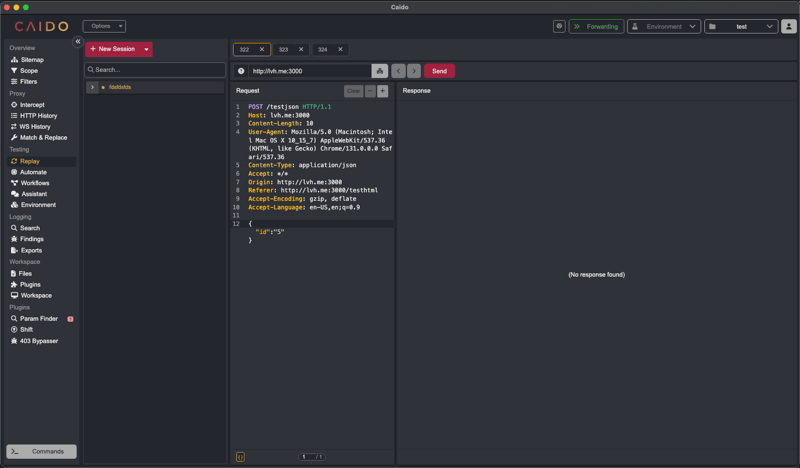 caido-community/paramfinder
Discover hidden parameters in Caido
 sobri3195/pegasus-pentest-arsenal
A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.