CVE-2021-4191_Exploits

Exploit script for CVE-2021-4191 that enumerates GitLab users via the GraphQL API, useful for security assessments and validating exposure.

Exploit script for CVE-2021-4191 that enumerates GitLab users via the GraphQL API, useful for security assessments and validating exposure.

Reproduction of a high severty security problem that allows XXE (XML eXternal Entity) attacks on Ktor's XML serialization.

MCP-Inspector-vulncheck is a Python script that checks if an MCP Inspector server is vulnerable to CVE-2025-49596. It tests whether the /sse endpoint…

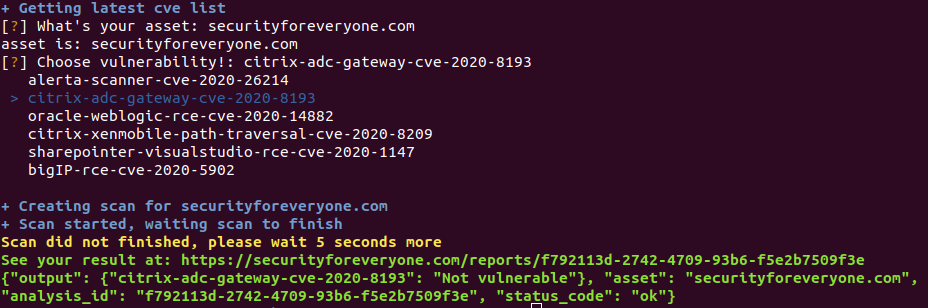
API-based scanner that retrieves and lists the latest Common Vulnerabilities and Exposures (CVEs) for automated security assessment and vulnerability…

A bash automation that exploits the vulnerable endpoints for the Joomla! API 4.0 - 4.2.7

Automatic SQL injection and database takeover tool

Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…

An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses

Damn Vulnerable GraphQL Application is an intentionally vulnerable GraphQL service implementation designed for learning about and practising GraphQL…

Metlo is an open-source API security platform.

Rust components for traffic interception and redirection, enabling WireGuard device proxying and local app redirection across macOS, Windows, and…

Model Context Protocol server for Firefox DevTools - enables AI assistants to inspect and control Firefox browser through WebDriver BiDi

SSRF plugin for burp Automates SSRF Detection in all of the Request

Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…

Hidden parameters discovery suite

Executable security regression testing for agentic applications and MCP-integrated systems.

Unofficial Acunetix CLI tool for automated pentesting and bug hunting across large scopes.

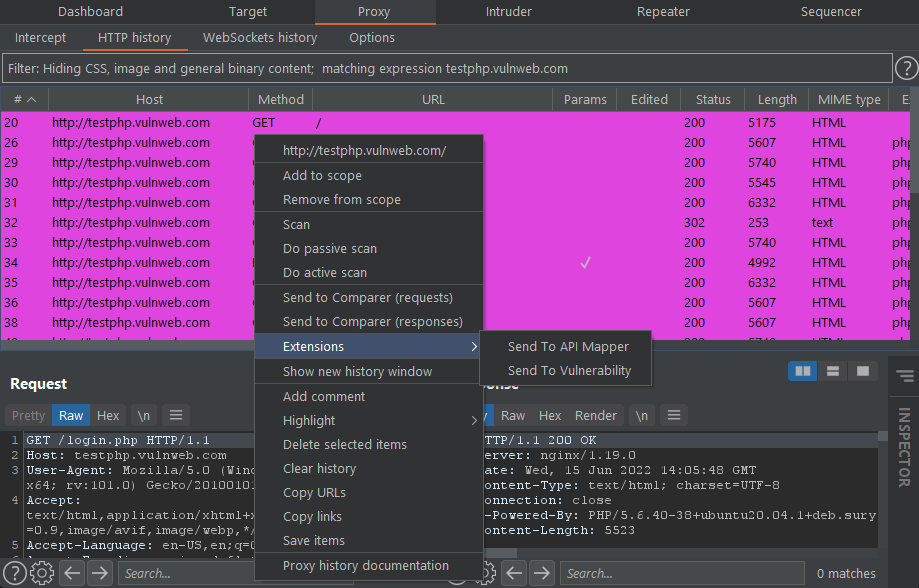
A Burp Suite Extension for Application Penetration Testing to map flows and vulnerabilities