
Burp_CVE-2025-31324
 blueowl-overlord/burp_cve-2025-31324
Python-based Burp Suite extension is designed to detect the presence of CVE-2025-31324
api-security-testingexploitationpenetration-testing+3
blueowl-overlord/burp_cve-2025-31324Python-based Burp Suite extension is designed to detect the presence of CVE-2025-31324
 osirium/suds
Clone of suds 0.4 + suds-0.4-CVE-2013-2217.patch
 digeex/raider
DEPRECATED, please use the new repository from OWASP: https://github.com/OWASP/raider
 usebruno/bruno
Opensource IDE For Exploring and Testing API's (lightweight alternative to Postman/Insomnia)
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…

 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 s0md3v/arjun
HTTP parameter discovery tool that finds valid query parameters for URL endpoints using a large dictionary, supporting GET/POST/JSON/XML requests,…
 spectolabs/hoverfly
Lightweight service virtualization/ API simulation / API mocking tool for developers and testers
 ipa-lab/hackingbuddygpt
Helping Ethical Hackers use LLMs in 50 Lines of Code or less..
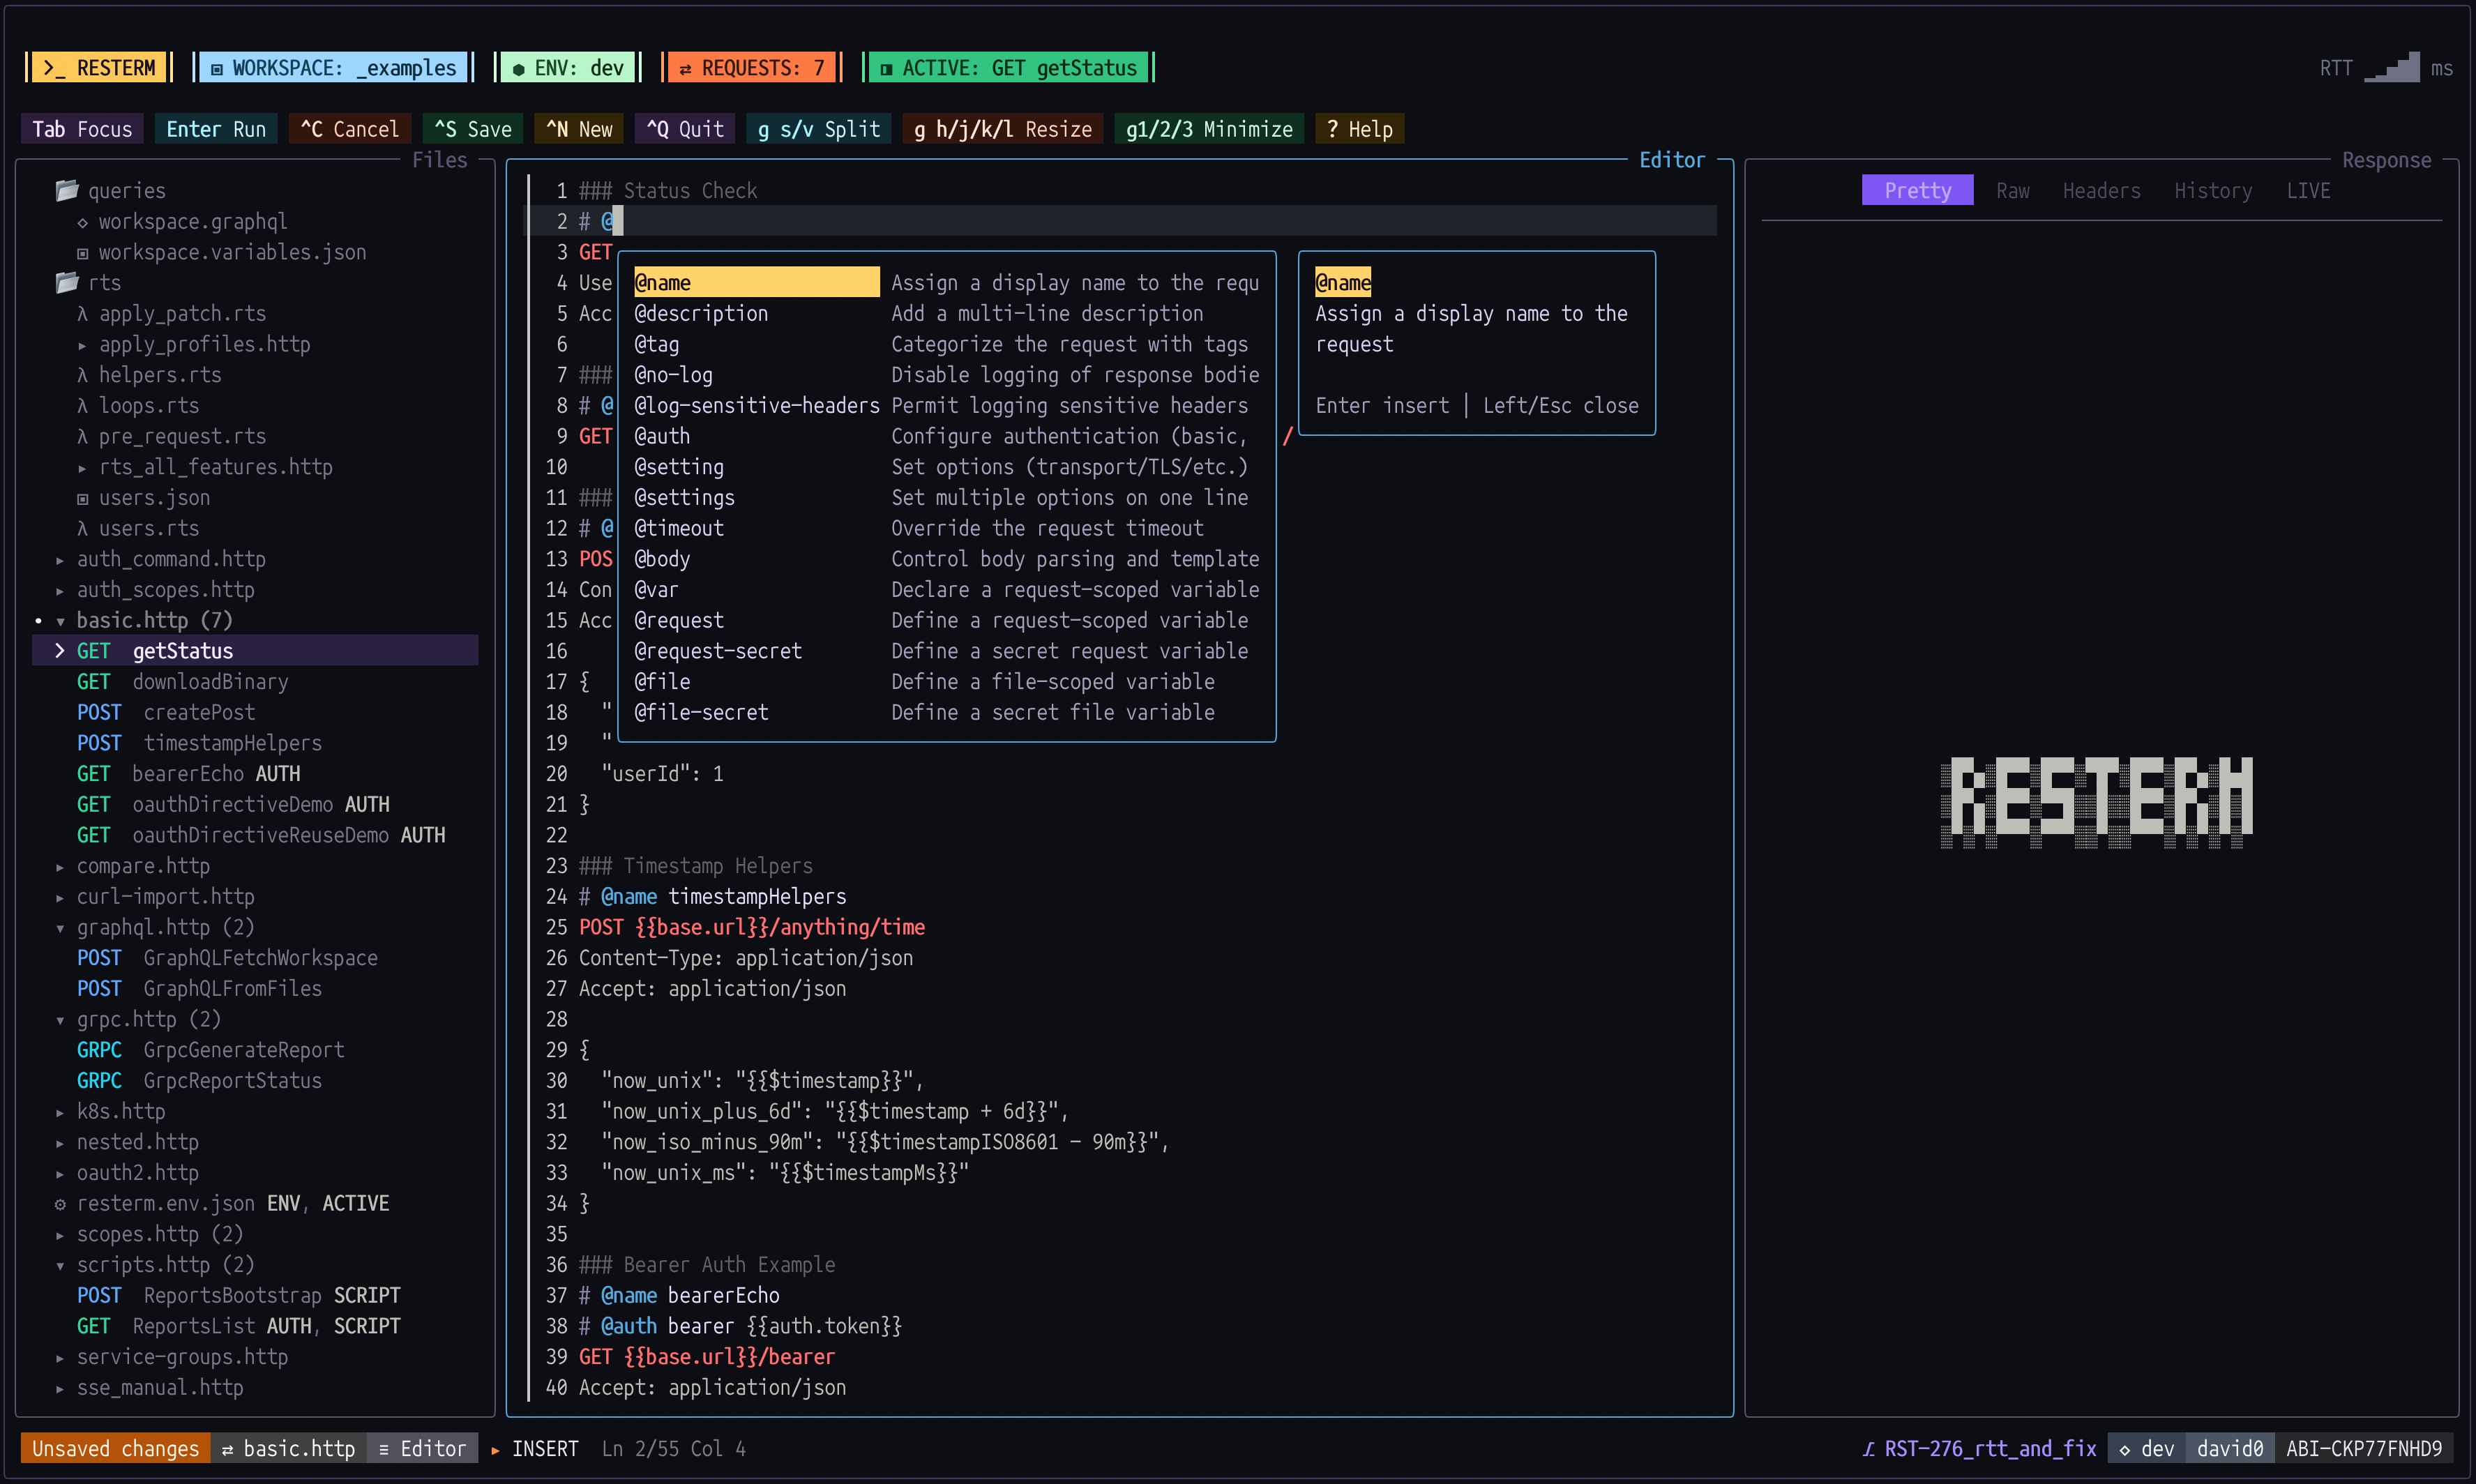 unkn0wn-root/resterm
Terminal API client for HTTP, GraphQL, gRPC, WebSocket and SSE. Plain .http files you can diff and version, with scripted tests, workflows, mocks,…
 saffron-health/libretto
The AI toolkit for building reliable browser automations
 owasp/offat
Automated API security testing tool that generates tests from OpenAPI specs, fuzzes inputs, and checks for OWASP API Top 10 vulnerabilities including…
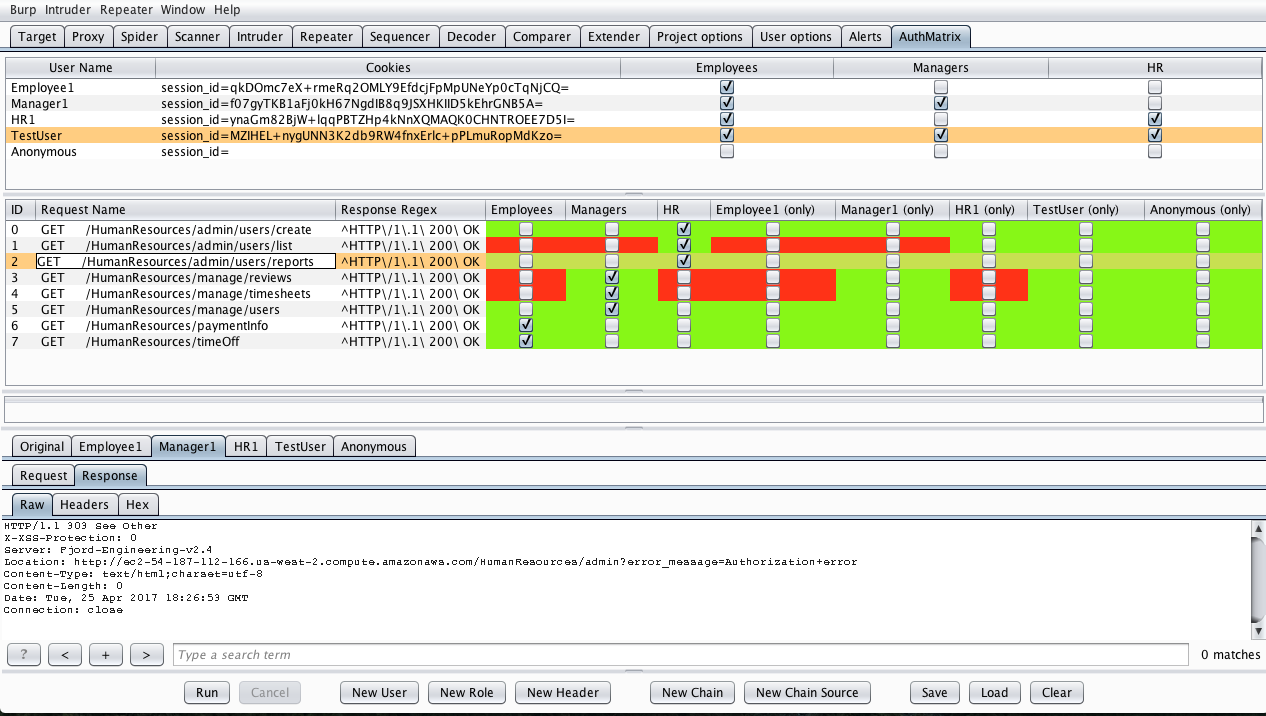 securityinnovation/authmatrix
AuthMatrix is a Burp Suite extension that provides a simple way to test authorization in web applications and web services.
 mitmproxy/mitmproxy_rs
Rust components for traffic interception and redirection, enabling WireGuard device proxying and local app redirection across macOS, Windows, and…
 owasp/dvsa
a Damn Vulnerable Serverless Application
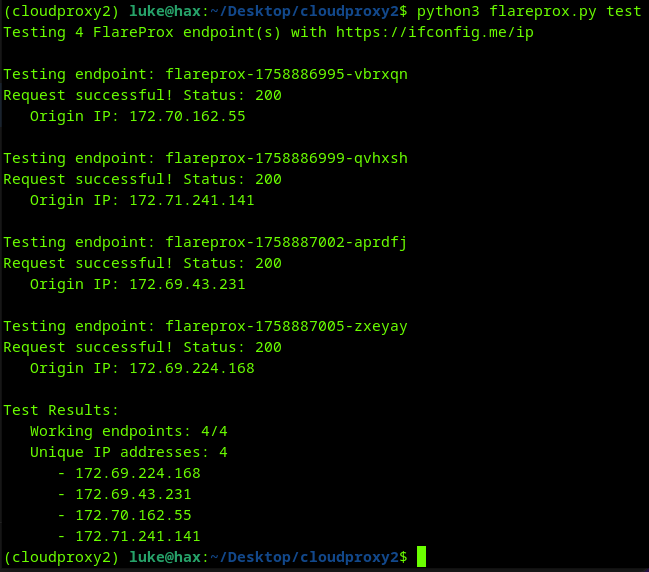 mrturvey/flareprox
Use Cloudflare to create HTTP pass-through proxies for unique IP rotation, similar to fireprox
 devcop95/bugbounty-lab101
A complete bug bounty workspace for HackerOne researchers. Includes scope enforcement, automated recon/vuln pipeline (400+ tools), report templates,…