
HuntCyberArk
 logisek/huntcyberark
CyberArk Security Audit
api-security-testingauthenticationcloud-security+7
25
logisek/huntcyberarkCyberArk Security Audit
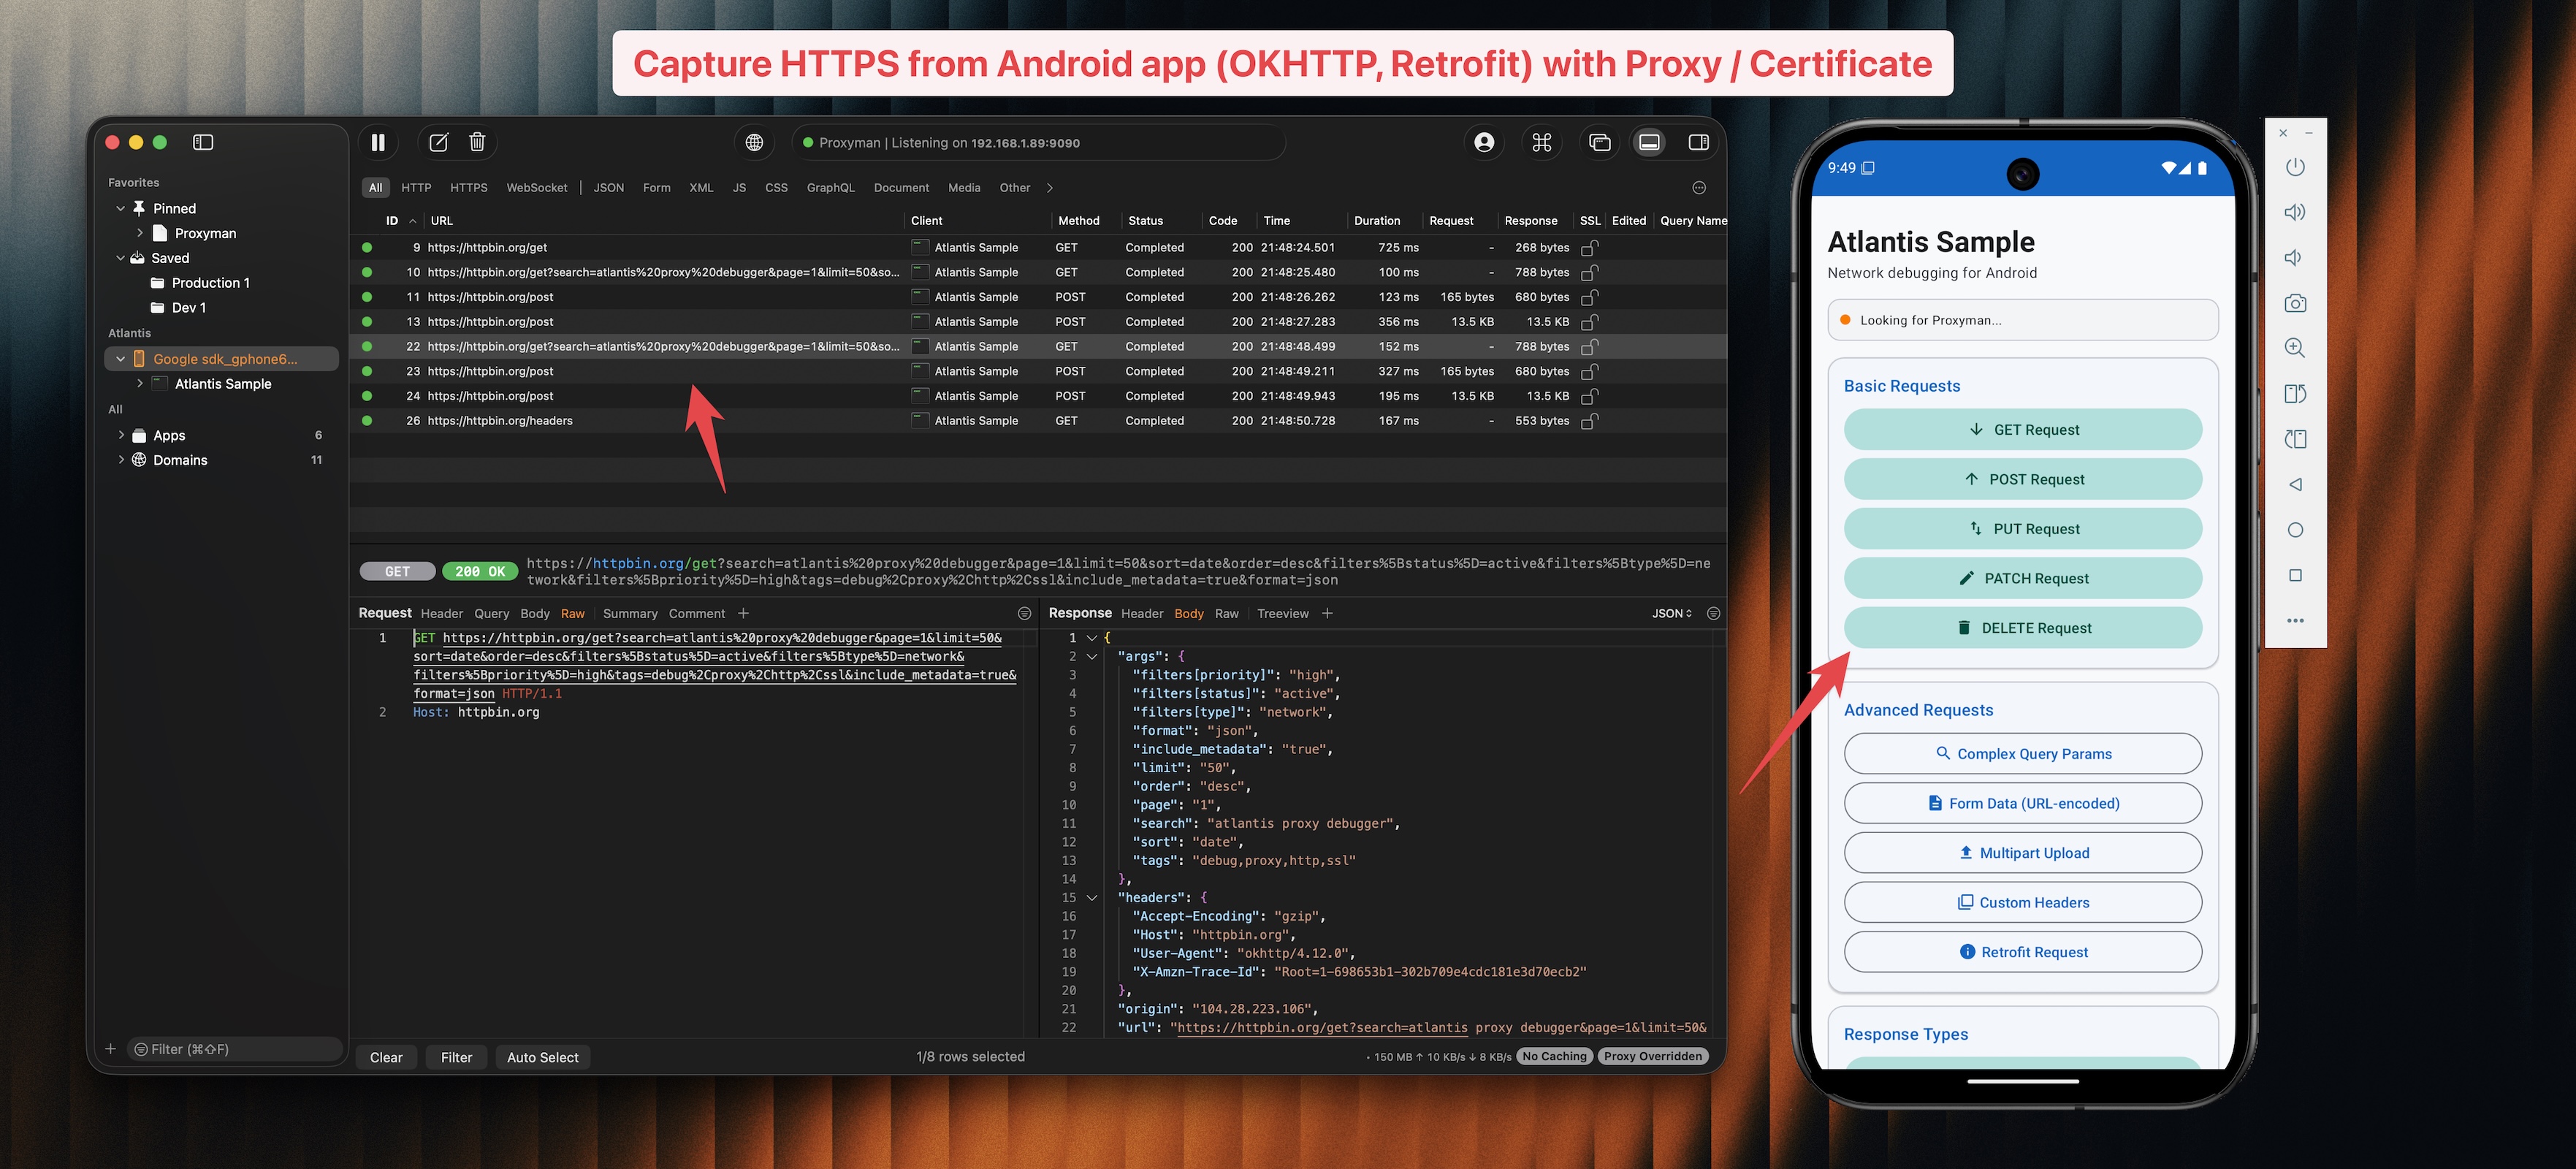 proxymanapp/atlantis-android
Capture HTTP/HTTPS traffic from Android apps and send to Proxyman for debugging.
 brinhosa/apidetector
Multi-threaded scanner for detecting exposed Swagger/OpenAPI endpoints across web domains and subdomains, with automatic XSS detection, PoC…
 pentestgeek/burpcommander
Ruby command-line interface to Burp Suite's REST API
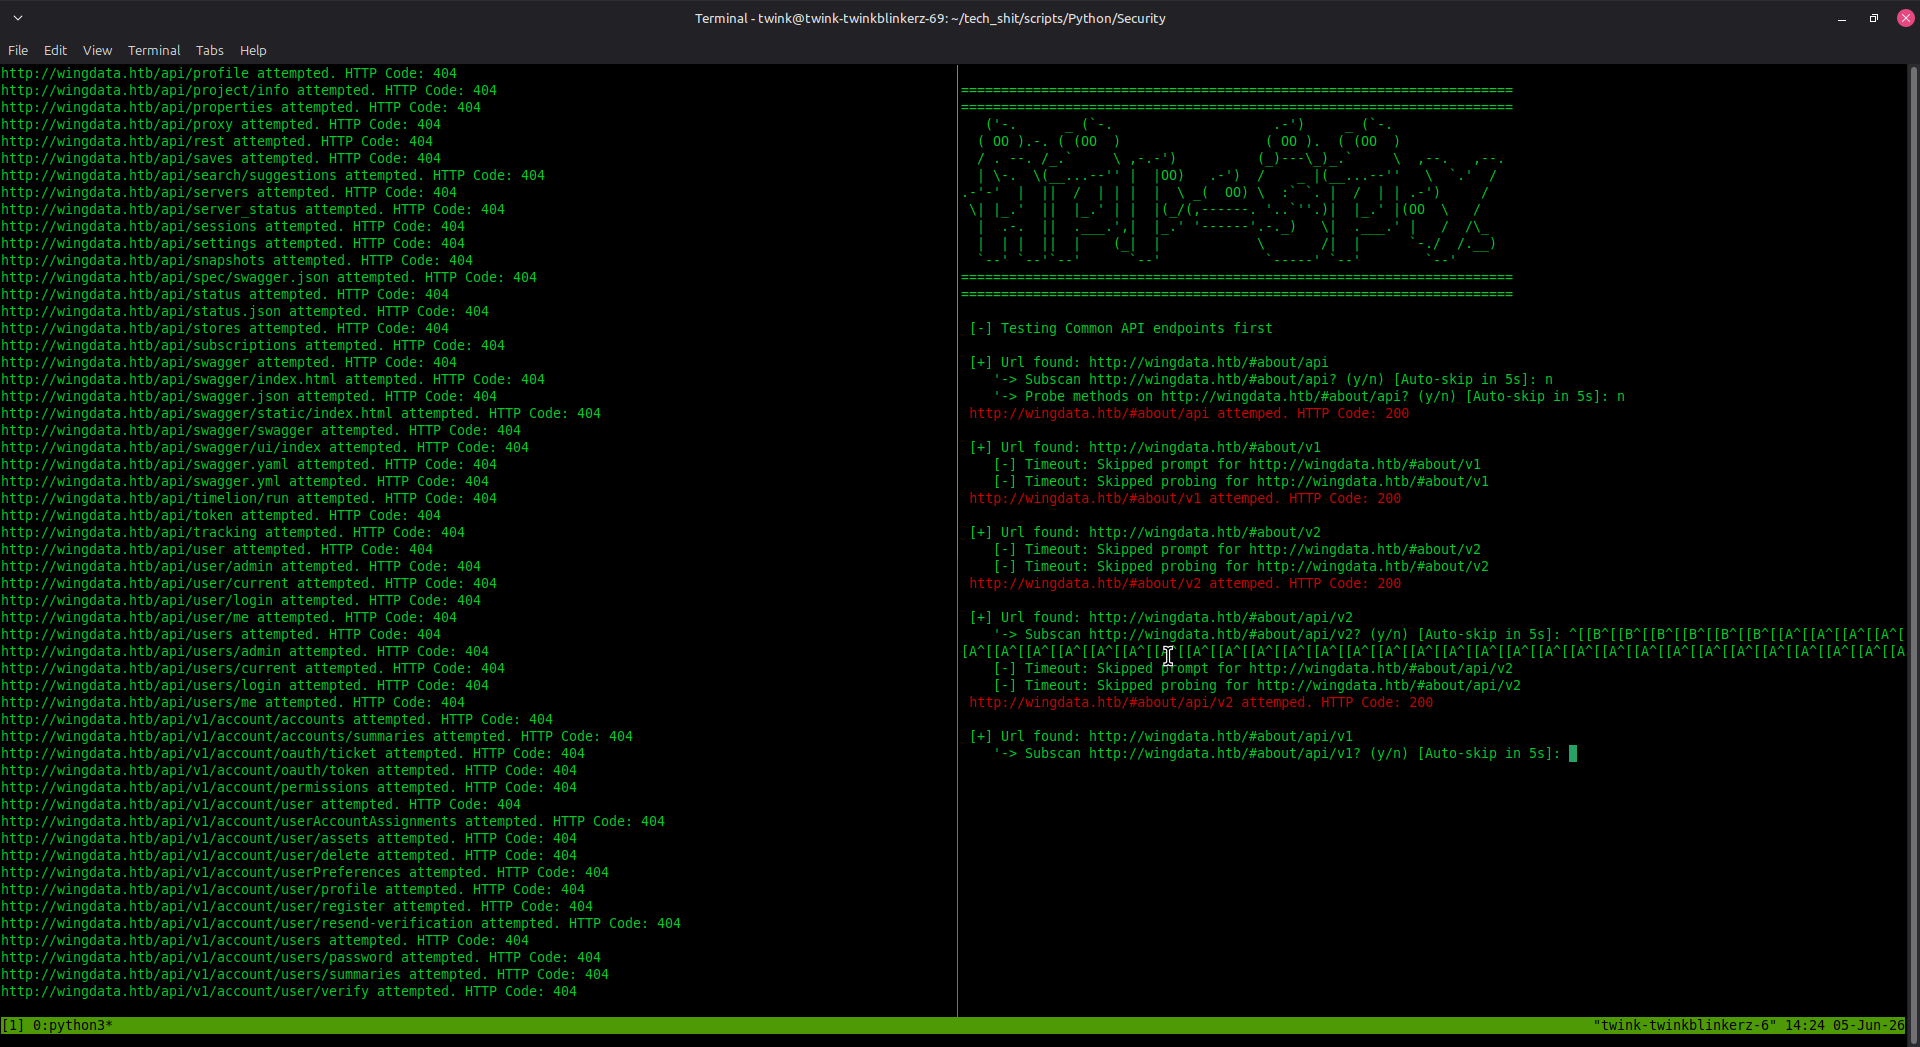 austinjump-sec/api-spy-api-probe
A powerful directory brute-force tool that's tailored for recursive/multiplex operations, API discovery and enumeration, JS file scraping, and lists…
 cve-2023-49954/cve-2023-49954.github.io
SQL Injection in 3CX CRM Integration
 loaxert/cve-2025-59528-poc
PoC for CVE-2025-59528 used to achieve remote code execution on the Silentium machine at HTB
 nxploited/cve-2024-9707-poc
he Hunk Companion Plugin for WordPress: Vulnerable to Unauthorized Plugin Installation/Activation (Versions Up to and Including 1.8.4)
 andreafioraldi/frida-fuzzer
This experimetal fuzzer is meant to be used for API in-memory fuzzing.
 wi3memake/react2shell-scanner
Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…
 google/martian
Martian is a library for building custom HTTP/S proxies
 owasp/dvsa
a Damn Vulnerable Serverless Application
 portswigger/pentest-mapper
A Burp Suite Extension for Application Penetration Testing to map flows and vulnerabilities
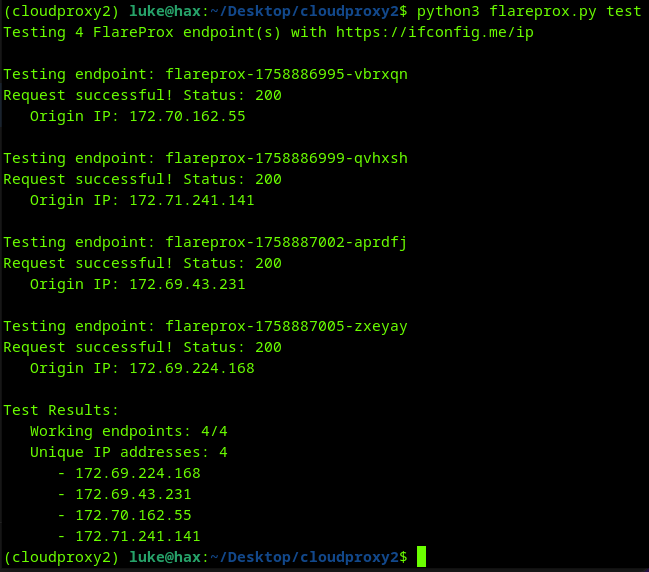 mrturvey/flareprox
Use Cloudflare to create HTTP pass-through proxies for unique IP rotation, similar to fireprox
 randomrobbiebf/cve-2024-11423
Ultimate Gift Cards for WooCommerce <= 3.0.6 - Missing Authorization to Infinite Money Glitch
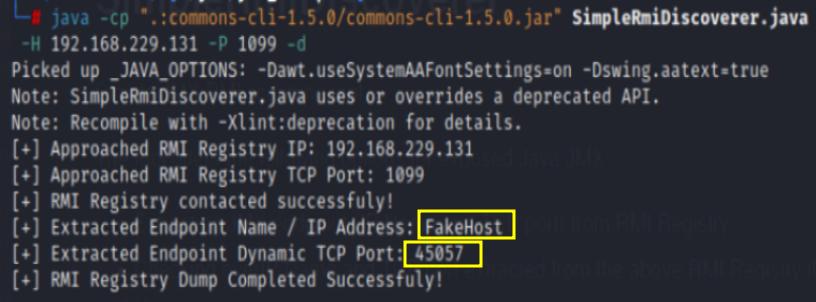 marcin-wolak/simplermidiscoverer
Simple JMX RMI scanning tool
 hunt-benito/bring-your-own-key-cve-2026-73678-unauthenticated-rce-in-mindsdb-cowork
PoC exploit for CVE-2026-73678: unauthenticated RCE in MindsDB Cowork via attacker-supplied LLM key and unsandboxed scratchpad exec to run OS…
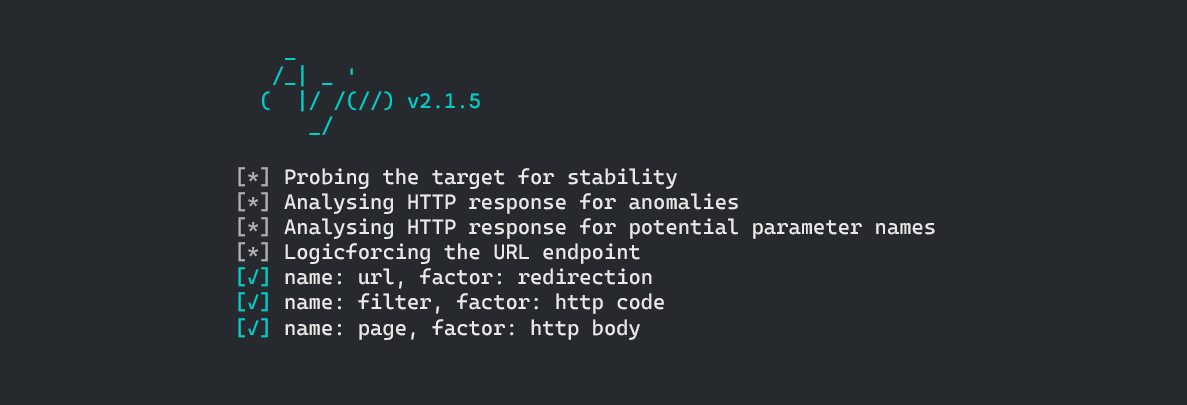 s0md3v/arjun
HTTP parameter discovery tool that finds valid query parameters for URL endpoints using a large dictionary, supporting GET/POST/JSON/XML requests,…