
RatRace
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
api-security-testingdevsecopsexploitation+5
10
bogdanticu88/ratraceA lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
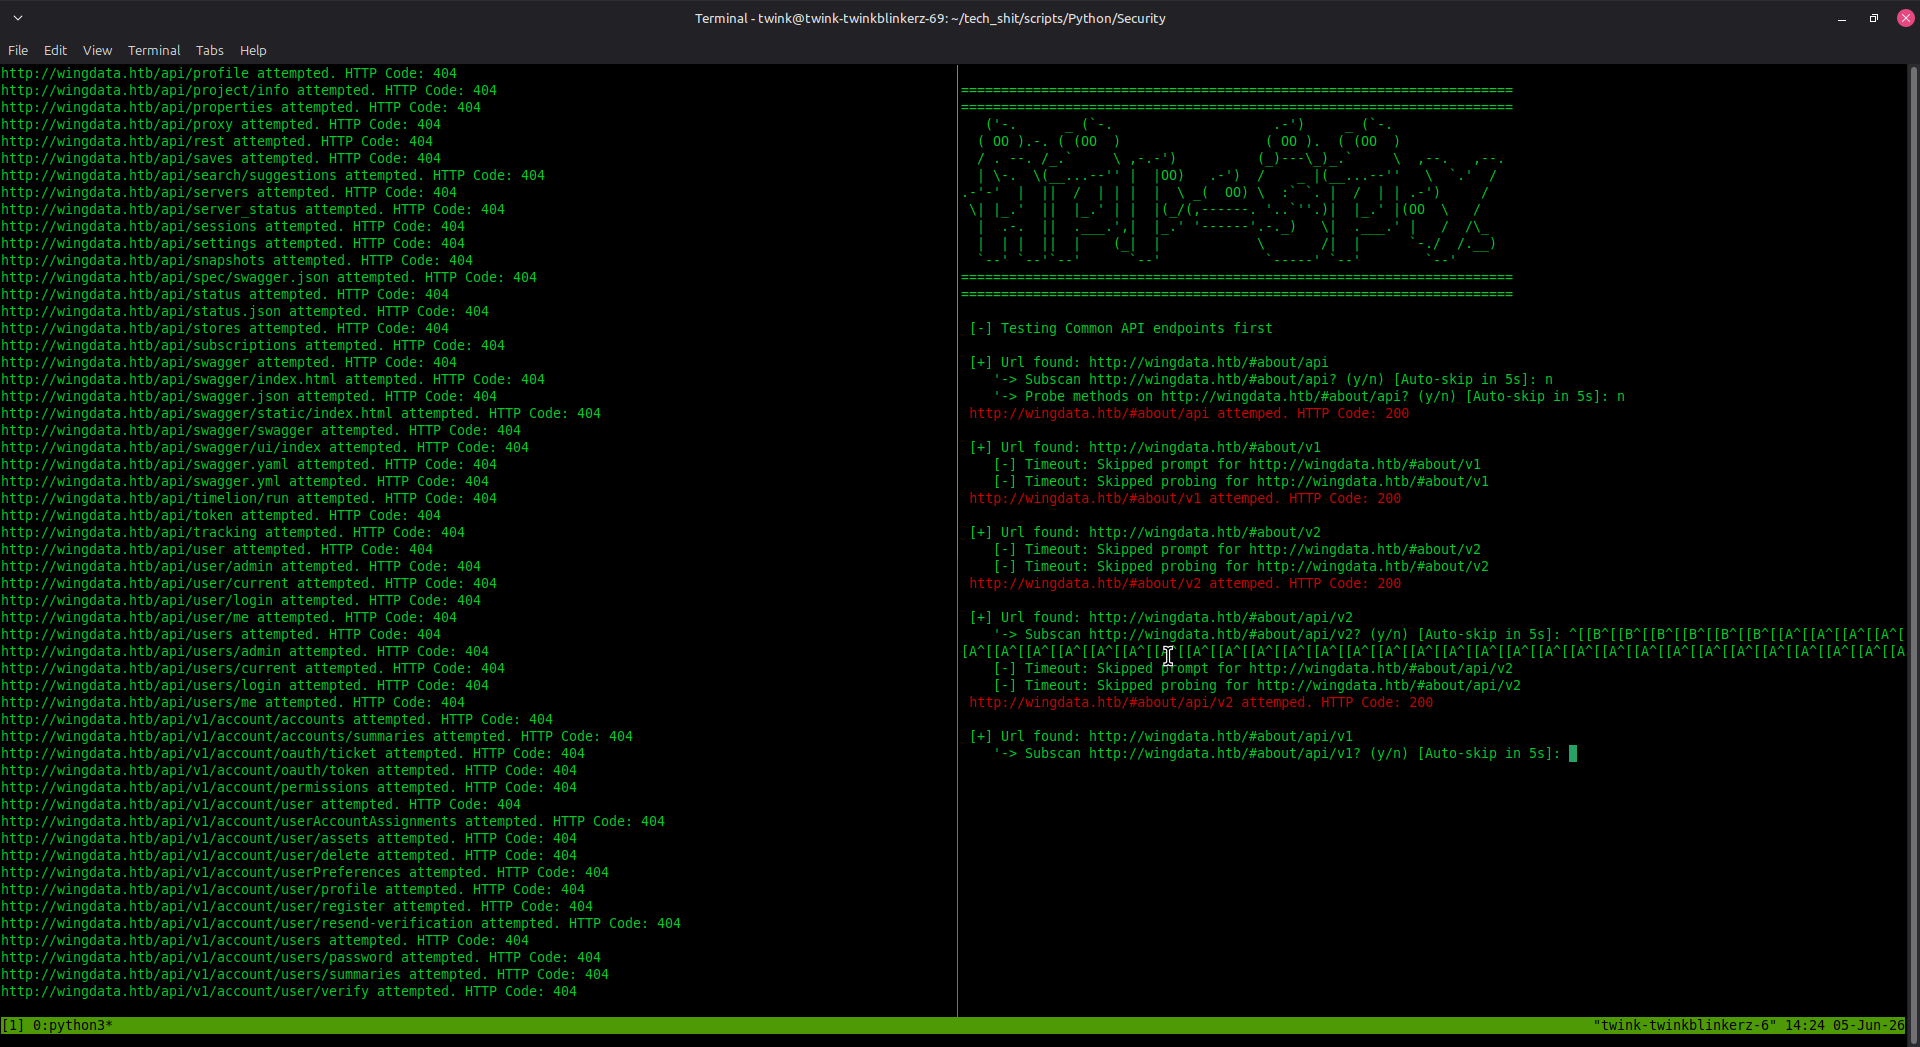 austinjump-sec/api-spy-api-probe
A powerful directory brute-force tool that's tailored for recursive/multiplex operations, API discovery and enumeration, JS file scraping, and lists…
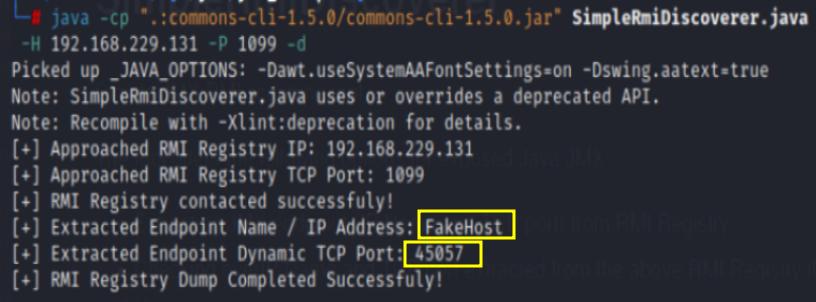 marcin-wolak/simplermidiscoverer
Simple JMX RMI scanning tool
 cropnet/ni8mare
Comprehensive vulnerability detection tool for n8n workflow automation instances. Detects the critical CVE-2026-21858 vulnerability (CVSS 10.0)…
 amnnrth/cve-2025-34291_cors_security_scanner
A lightweight Python-based security assessment tool for detecting dangerous Cross-Origin Resource Sharing (CORS) misconfigurations - CVE-2025-34291.
 omar2535/graphqler
☸The first ever dependency-aware GraphQL API testing tool!
 vmware-archive/burp-rest-api
REST/JSON API to the Burp Suite security tool.
 openstack-archive/syntribos
Python API security testing tool from OpenStack Security Group
 google/nogotofail
An on-path blackbox network traffic security testing tool
 ticarpi/jwt_tool
:snake: A toolkit for testing, tweaking and cracking JSON Web Tokens
 0xsteph/pentest-ai
Open-source AI pentester that proves every finding. Machine oracles re-run each exploit; verified bugs ship a proof capsule you can replay yourself.
 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 ac-pm/inspeckage
Android Package Inspector - dynamic analysis with api hooks, start unexported activities and more. (Xposed Module)
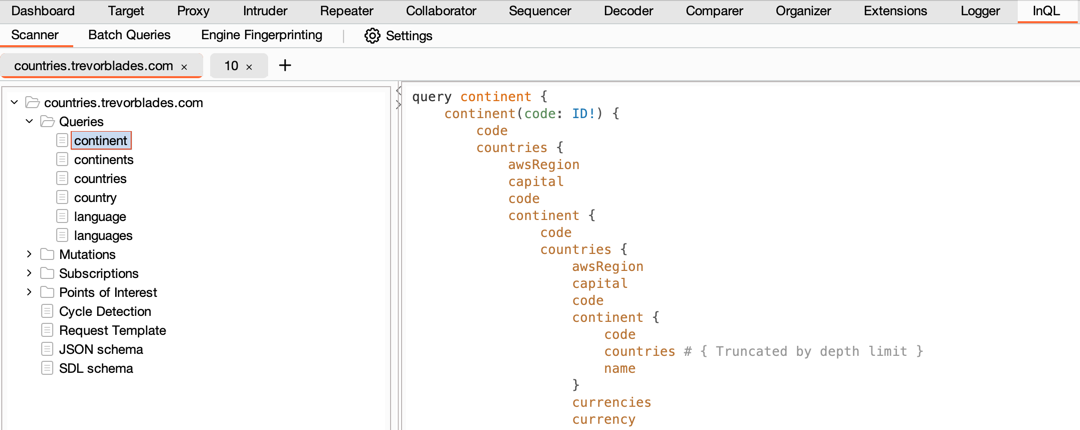 doyensec/inql
InQL is a robust, open-source Burp Suite extension for advanced GraphQL testing, offering intuitive vulnerability detection, customizable scans, and…
 brinhosa/apidetector
Multi-threaded scanner for detecting exposed Swagger/OpenAPI endpoints across web domains and subdomains, with automatic XSS detection, PoC…
 moniik/poc_salesforce_lightning
Academic purposes only. Attack against Salesforce lightning with guest privilege.
 hahwul/smugglex
Rust-powered HTTP Request Smuggling Scanner.
 impact-i/x8-burp
Hidden parameters discovery suite