
CVE-2025-51867
 secsys-fdu/cve-2025-51867
Demonstrates an Insecure Direct Object Reference (IDOR) vulnerability in Deepfiction AI's chat API, allowing attackers to consume other users'…
api-security-testinginformation-gatheringpenetration-testing+3
secsys-fdu/cve-2025-51867Demonstrates an Insecure Direct Object Reference (IDOR) vulnerability in Deepfiction AI's chat API, allowing attackers to consume other users'…
 crackercat/cve-2022-24112
Apache APISIX apisix/batch-requests RCE
 skysliently/cve-2022-22947-pb-ai
一个由AI生成的漏洞验证应用
 5qu1n7/cve-2025-55817
ChilliCream Nitro GraphQL version 28.0.13 is vulnerable to multiple Stored Cross Site Scripting (XSS) Vulnerabilities
 ashiqrehan-21/mcp-inspector-cve-2025-49596
MCP-Inspector-vulncheck is a Python script that checks if an MCP Inspector server is vulnerable to CVE-2025-49596. It tests whether the /sse endpoint…
 fevar54/forticlient_ems_cve_2026_35616_poc.py
PoC de CVE-2026-35616: control de acceso indebido en FortiClient EMS.
 omar2535/graphqler
☸The first ever dependency-aware GraphQL API testing tool!
 functori/dev/gaia
Global API Integrity Assessor
 mayank-s16/swagger-html-injection-cve-2025-8191
XSS Test Swagger 3.14.1 to 3.37.0
 randomrobbiebf/cve-2024-54369
Zita Site Builder <= 1.0.2 - Missing Authorization to Arbitrary Plugin Installation
 blueowl-overlord/burp_cve-2025-31324
Python-based Burp Suite extension is designed to detect the presence of CVE-2025-31324
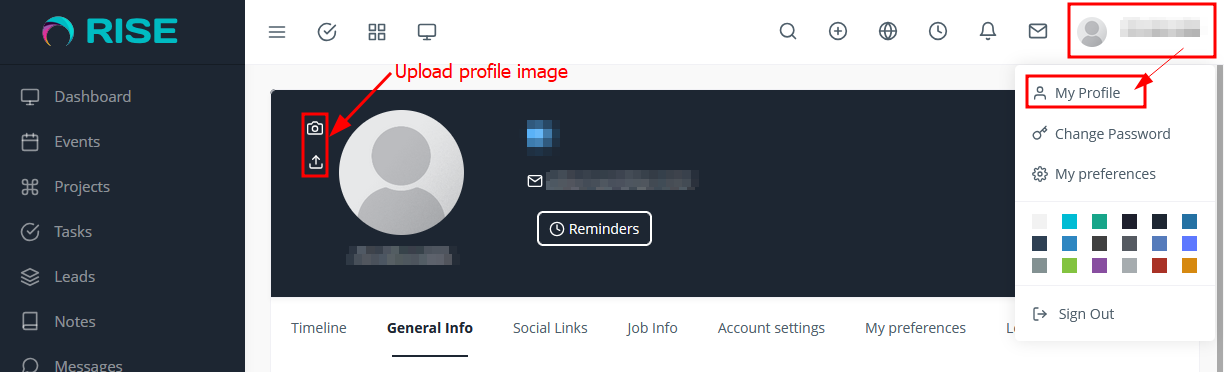 l4zyfox/rise-ultimate_project_manager_e_crm
CVE-2025-3855 - RISE Ultimate Project Manager - IDOR
 randomrobbiebf/cve-2023-6289
Swift Performance Lite <= 2.3.6.14 - Missing Authorization to Unauthenticated Settings Export
 havoc10-sw/detect_polyfill_cve-2024-38537-
Here's a Python script that checks if the polyfill.io domain is present in the Content Security Policy (CSP) header of a given web application.
 corgizz/springcloud
Spring Cloud Config CVE-2019-3799|CVE_2020_5410 漏洞检测
 vmware-archive/burp-rest-api
REST/JSON API to the Burp Suite security tool.
 rapid7/hackazon
A modern vulnerable web app
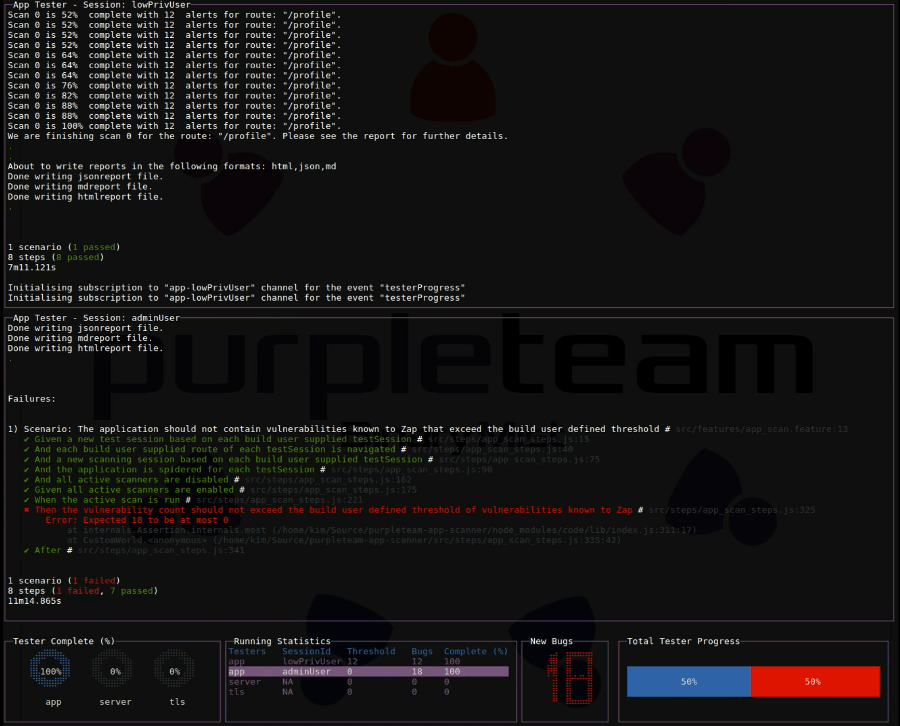 purpleteam-labs/purpleteam
CLI component of purpleteam