CVE-2023-31719
 mateustesser/cve-2023-31719
Proof-of-concept exploit for CVE-2023-31719, demonstrating SQL injection in the FUXA web application's /api/signin endpoint via a crafted JSON…
api-security-testingdatabase-securityexploitation+3
mateustesser/cve-2023-31719Proof-of-concept exploit for CVE-2023-31719, demonstrating SQL injection in the FUXA web application's /api/signin endpoint via a crafted JSON…
 grtmaldet/big-ip-next-cve-2024-26026
Proof-of-concept exploit for CVE-2024-26026: unauthenticated SQL injection in F5 BIG-IP Next Central Manager API, enabling remote data extraction and…
 nxploited/cve-2024-9707-poc
he Hunk Companion Plugin for WordPress: Vulnerable to Unauthorized Plugin Installation/Activation (Versions Up to and Including 1.8.4)
 shoucheng3/perwendel__spark_cve-2018-9159_2-7-1
Lightweight Java 8 web framework with routing, filters, and static file serving. Includes security advisory for older versions and CRUD API examples.
 randomrobbiebf/cve-2024-54369
Zita Site Builder <= 1.0.2 - Missing Authorization to Arbitrary Plugin Installation
 shoucheng3/perwendel__spark_cve-2018-9159_2_7_2_fixed
Lightweight Java 8 web framework for building REST APIs and web applications, with built-in routing, static file serving, and template engine support.
 blueowl-overlord/burp_cve-2025-31324
Python-based Burp Suite extension is designed to detect the presence of CVE-2025-31324
 aureum01/cve-2023-23752
A bash automation that exploits the vulnerable endpoints for the Joomla! API 4.0 - 4.2.7
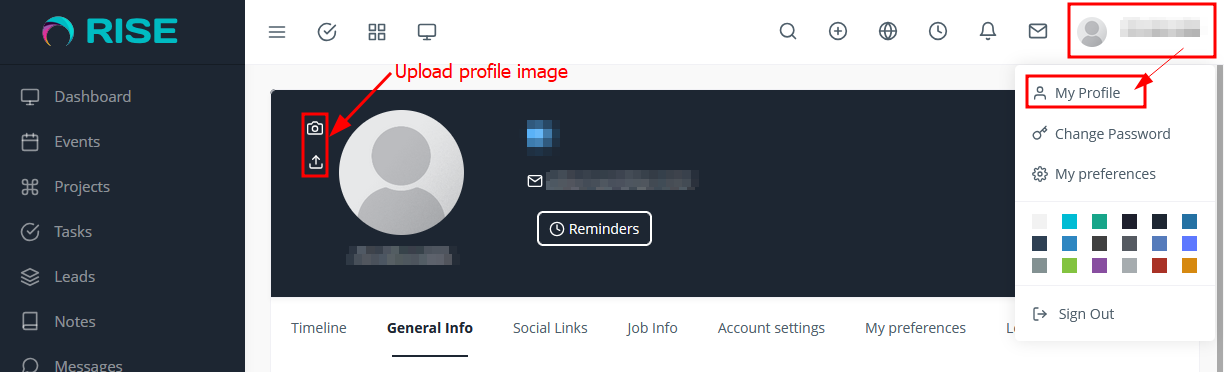 l4zyfox/rise-ultimate_project_manager_e_crm
CVE-2025-3855 - RISE Ultimate Project Manager - IDOR
 randomrobbiebf/cve-2023-6289
Swift Performance Lite <= 2.3.6.14 - Missing Authorization to Unauthenticated Settings Export
 havoc10-sw/detect_polyfill_cve-2024-38537-
Here's a Python script that checks if the polyfill.io domain is present in the Content Security Policy (CSP) header of a given web application.
 palmtreeforest/codepath_week_7-8
CodePath Assignment for Weeks 7 & 8: CVE-2017-14719, CVE-2019-9787 & Unauthenticated Page/Post Content Modification via REST API
 corgizz/springcloud
Spring Cloud Config CVE-2019-3799|CVE_2020_5410 漏洞检测
 osirium/suds
Clone of suds 0.4 + suds-0.4-CVE-2013-2217.patch
 shoucheng3/square__retrofit_cve-2018-1000850_2-4-0
Type-safe HTTP client library for Android and Java, enabling REST API communication with annotation-based request configuration and converter support.
 epicosy/retrofit-1
Type-safe HTTP client for Android and Java with annotation-based API binding, converter support, and integration with OkHttp for network…
 vmware-archive/burp-rest-api
REST/JSON API to the Burp Suite security tool.