
PacketPirate
 d0rb/packetpirate
A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.
api-security-testingeducationinformation-gathering+6
d0rb/packetpirateA headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.
 epicosy/retrofit-1
Type-safe HTTP client for Android and Java with annotation-based API binding, converter support, and integration with OkHttp for network…
 elmasy-com/columbus-server
API-first subdomain discovery service using Certificate Transparency logs for fast, passive enumeration of subdomains via a REST API with JSON or…
 google/nogotofail
An on-path blackbox network traffic security testing tool
 ticarpi/jwt_tool
:snake: A toolkit for testing, tweaking and cracking JSON Web Tokens
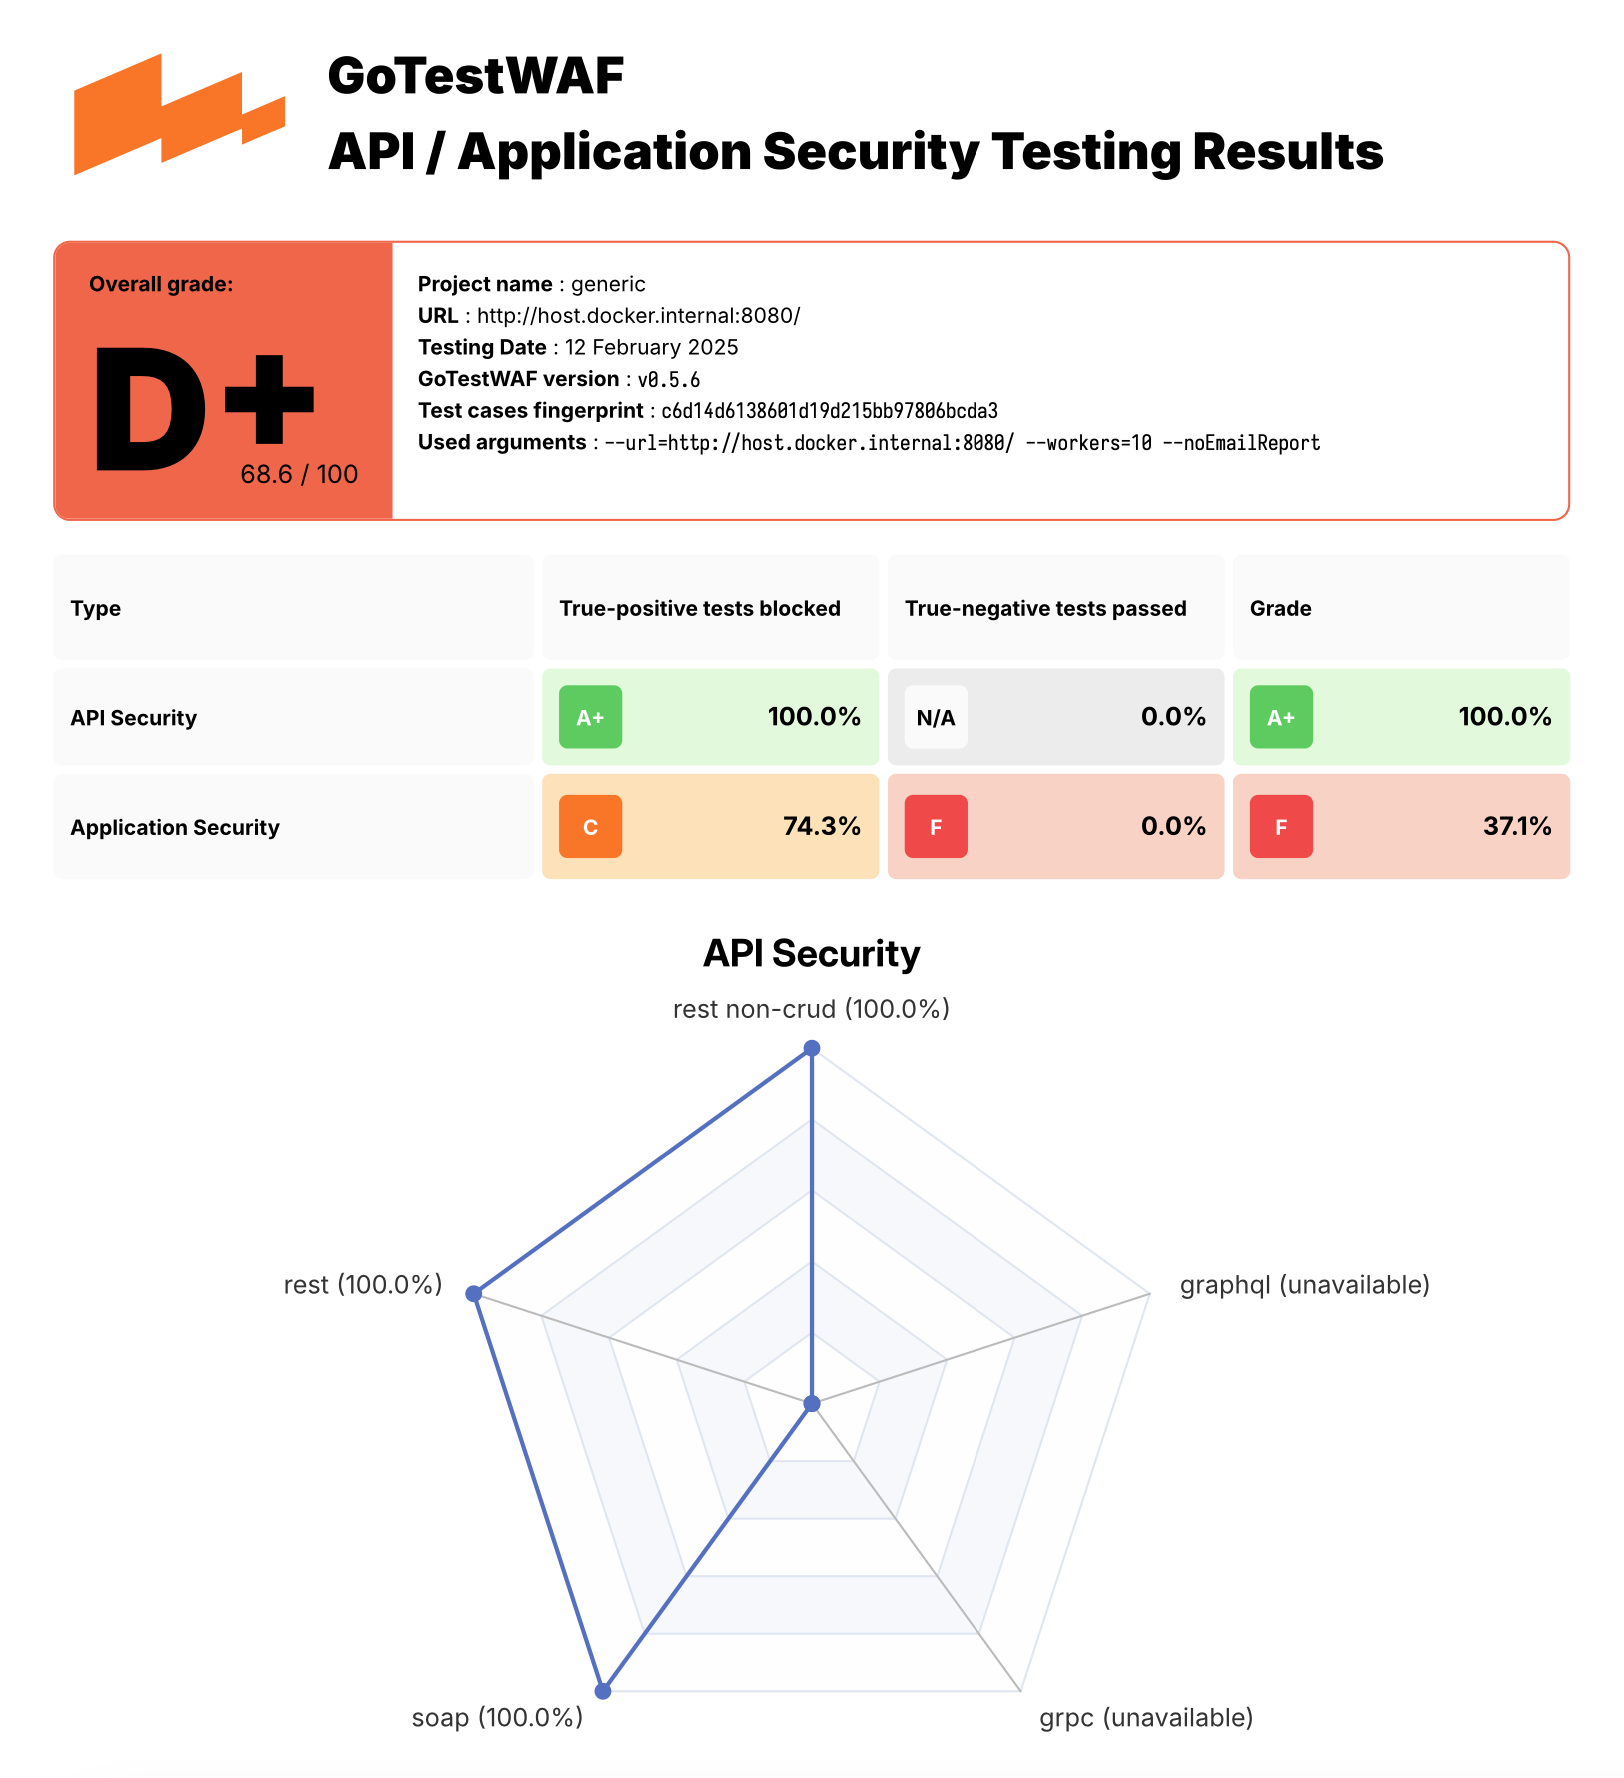 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
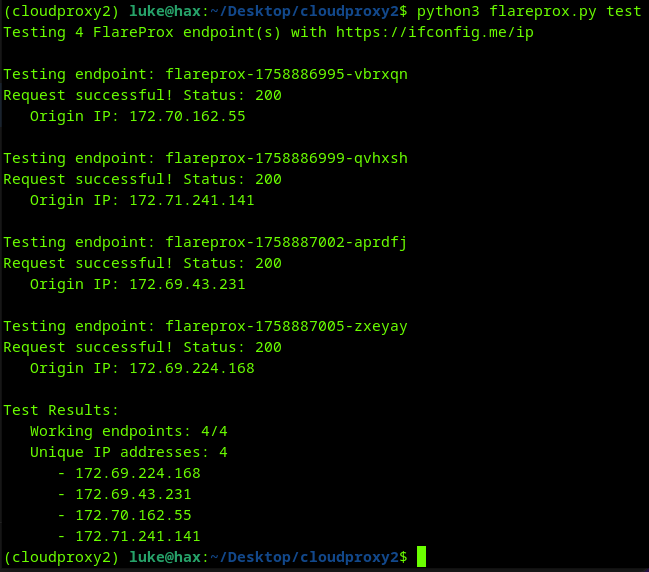 mrturvey/flareprox
Use Cloudflare to create HTTP pass-through proxies for unique IP rotation, similar to fireprox
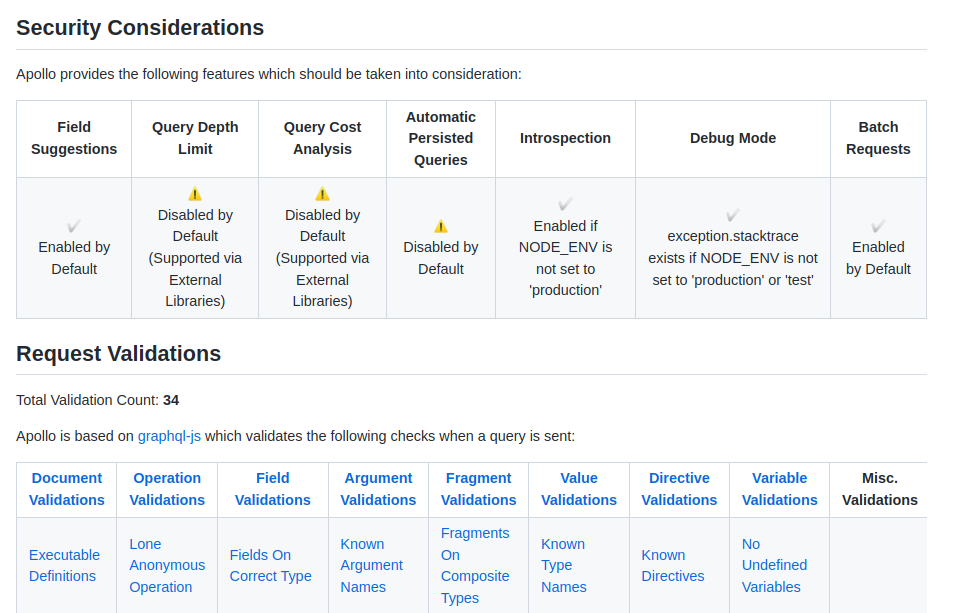 dolevf/graphw00f
GraphQL server engine fingerprinting tool that sends benign and malformed queries to identify backend technology and assess security defenses via the…
 brutelogic/unkover
Bash 403/401 access bypass tester that probes a URL with header spoofing, method tampering, path normalization, and encoding techniques, returning a…
 moniik/poc_salesforce_lightning
Academic purposes only. Attack against Salesforce lightning with guest privilege.
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 randomrobbiebf/cve-2023-32117
Integrate Google Drive <= 1.1.99 - Missing Authorization via REST API Endpoints
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
 fopje/cve-2022-36539
Insecure Permissions WeDayCare
 ex-cal1bur/cve-2026-44596
YAMCS yamcs-core < 5.12.7 lacks rate limiting on POST /auth/token. An unauthenticated attacker can perform unlimited brute-force attempts against any…
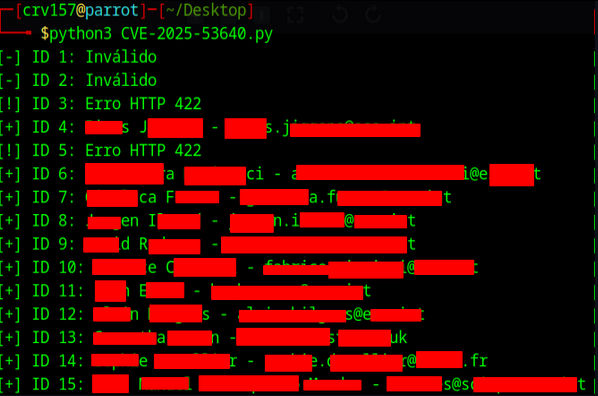 rafaelcorvino1/cve-2025-53640
Broken Object Level Authorization (BOLA) in CERN's Indico leads to authenticated user enumeration.
 alt3kx/cve-2018-7690
The SSC REST API contains Insecure Direct Object Reference (IDOR) vulnerabilities in Fortify Software Security Center (SSC) 17.10, 17.20 & 18.10
 alt3kx/cve-2018-7691
The SSC REST API contains Insecure Direct Object Reference (IDOR) vulnerabilities in Fortify Software Security Center (SSC) 17.10, 17.20 & 18.10