
bola-CVE-2023-27524
Demonstrates CVE-2023-27524 Broken Object Level Authorization (BOLA) vulnerability with vulnerable and fixed Flask API implementations for security…

Demonstrates CVE-2023-27524 Broken Object Level Authorization (BOLA) vulnerability with vulnerable and fixed Flask API implementations for security…

ChilliCream Nitro GraphQL version 28.0.13 is vulnerable to multiple Stored Cross Site Scripting (XSS) Vulnerabilities

MCP-Inspector-vulncheck is a Python script that checks if an MCP Inspector server is vulnerable to CVE-2025-49596. It tests whether the /sse endpoint…

☸The first ever dependency-aware GraphQL API testing tool!

Deliberately vulnerable C# API application for practicing web application exploitation and security testing. Includes Docker setup and documentation…

RumbleTalk Live Group Chat <= 6.1.9 - Missing Authorization via handleRequest

Proof-of-concept exploit for CVE-2024-50633, a Broken Object Level Authorization (BOLA) vulnerability in Indico v3.2.9–v3.3.2, enabling unauthorized…

XSS Test Swagger 3.14.1 to 3.37.0

Proof-of-concept exploit for CVE-2023-31719, demonstrating SQL injection in the FUXA web application's /api/signin endpoint via a crafted JSON…

Proof-of-concept exploit for CVE-2024-26026: unauthenticated SQL injection in F5 BIG-IP Next Central Manager API, enabling remote data extraction and…

he Hunk Companion Plugin for WordPress: Vulnerable to Unauthorized Plugin Installation/Activation (Versions Up to and Including 1.8.4)

Lightweight Java 8 web framework with routing, filters, and static file serving. Includes security advisory for older versions and CRUD API examples.

Zita Site Builder <= 1.0.2 - Missing Authorization to Arbitrary Plugin Installation

Lightweight Java 8 web framework for building REST APIs and web applications, with built-in routing, static file serving, and template engine support.

A bash automation that exploits the vulnerable endpoints for the Joomla! API 4.0 - 4.2.7

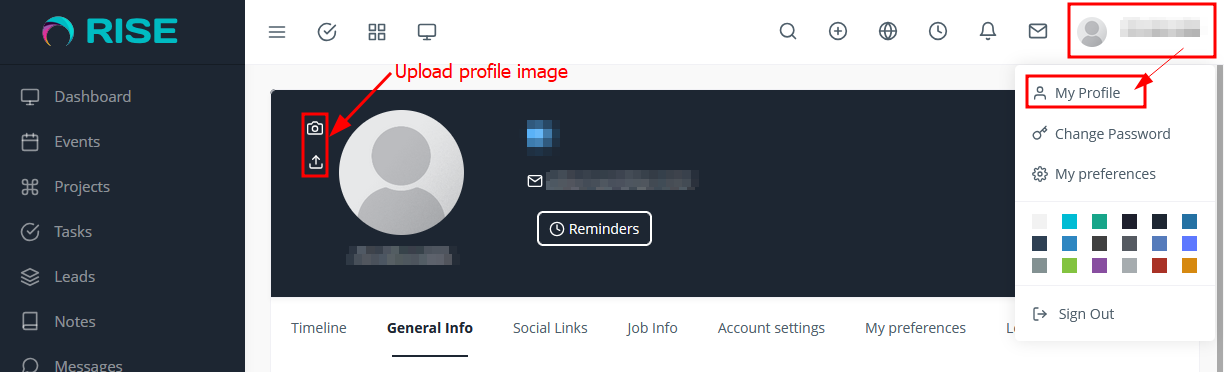
CVE-2025-3855 - RISE Ultimate Project Manager - IDOR

Swift Performance Lite <= 2.3.6.14 - Missing Authorization to Unauthenticated Settings Export

CodePath Assignment for Weeks 7 & 8: CVE-2017-14719, CVE-2019-9787 & Unauthenticated Page/Post Content Modification via REST API