
nuclei-burp-plugin
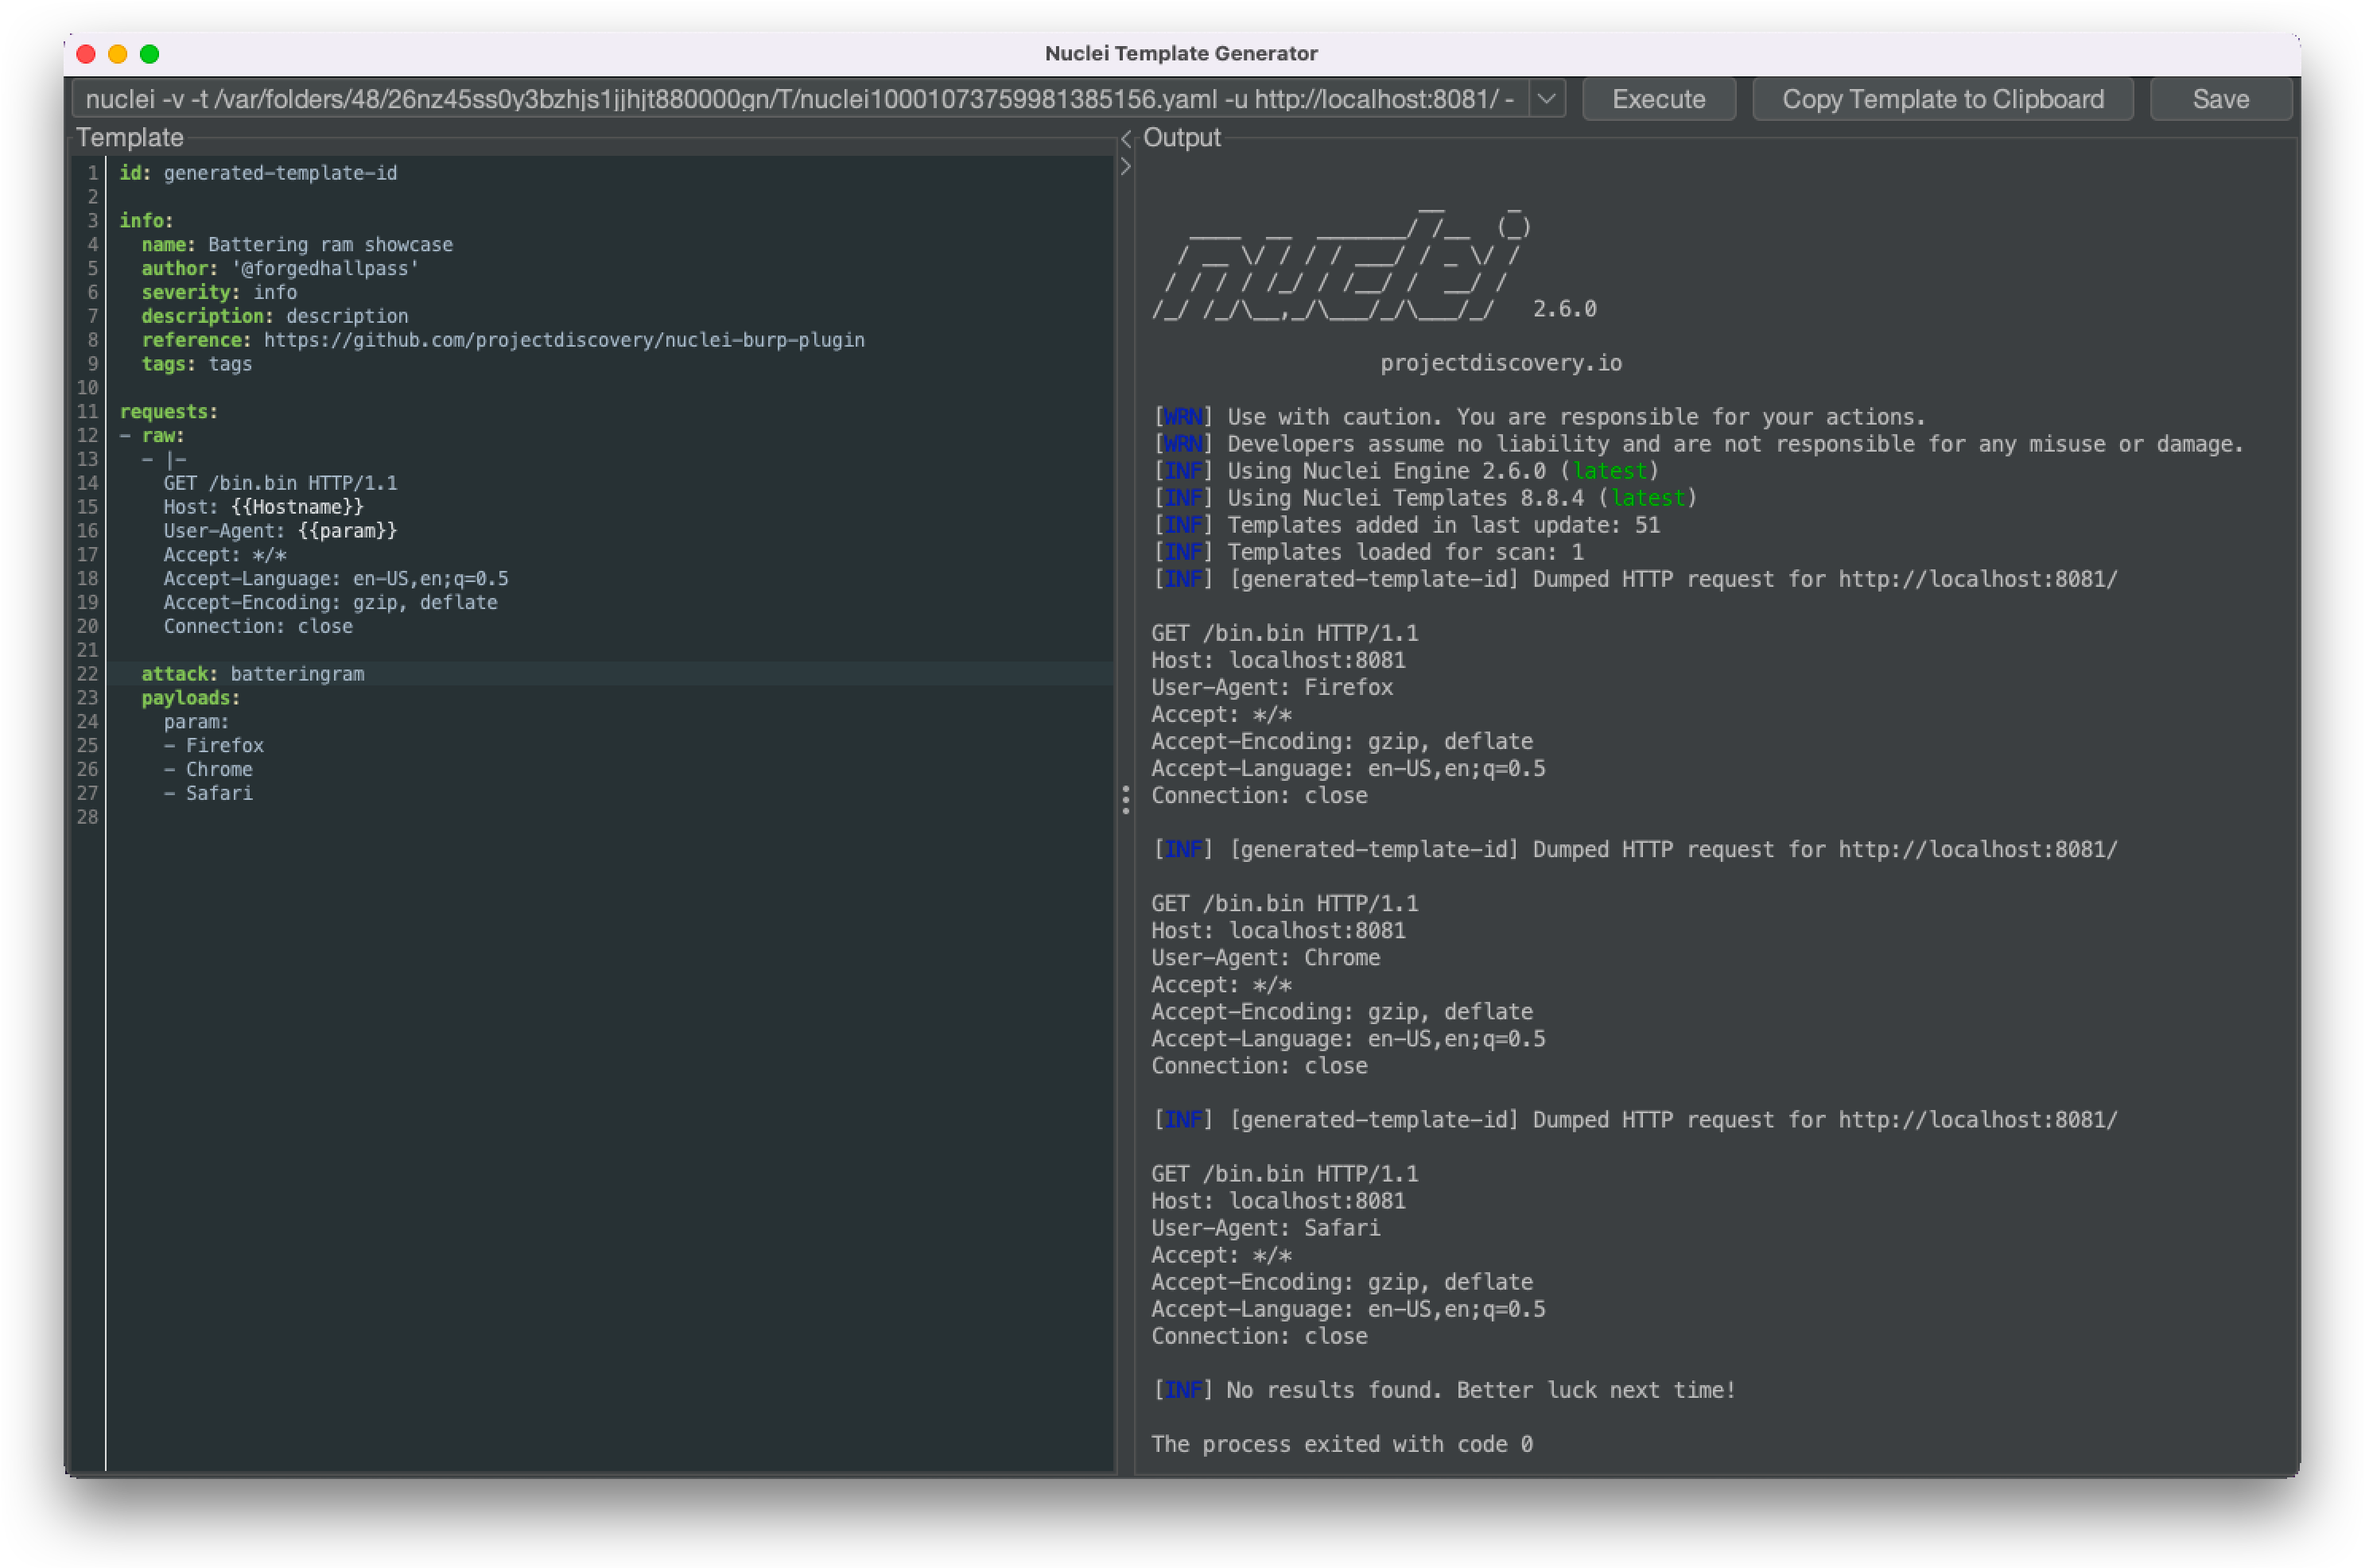
Burp Suite plugin for generating and executing Nuclei vulnerability templates directly from HTTP requests and responses, with YAML auto-complete and…

Burp Suite plugin for generating and executing Nuclei vulnerability templates directly from HTTP requests and responses, with YAML auto-complete and…

Wire-level proxy firewall for AI agents that intercepts and gates SQL, Kubernetes, and HTTP traffic using HCL rules, with per-process tunnel…

Automated penetration testing framework for REST APIs with OpenAPI-driven test generation, 32 OWASP-based security tests, and built-in access control…

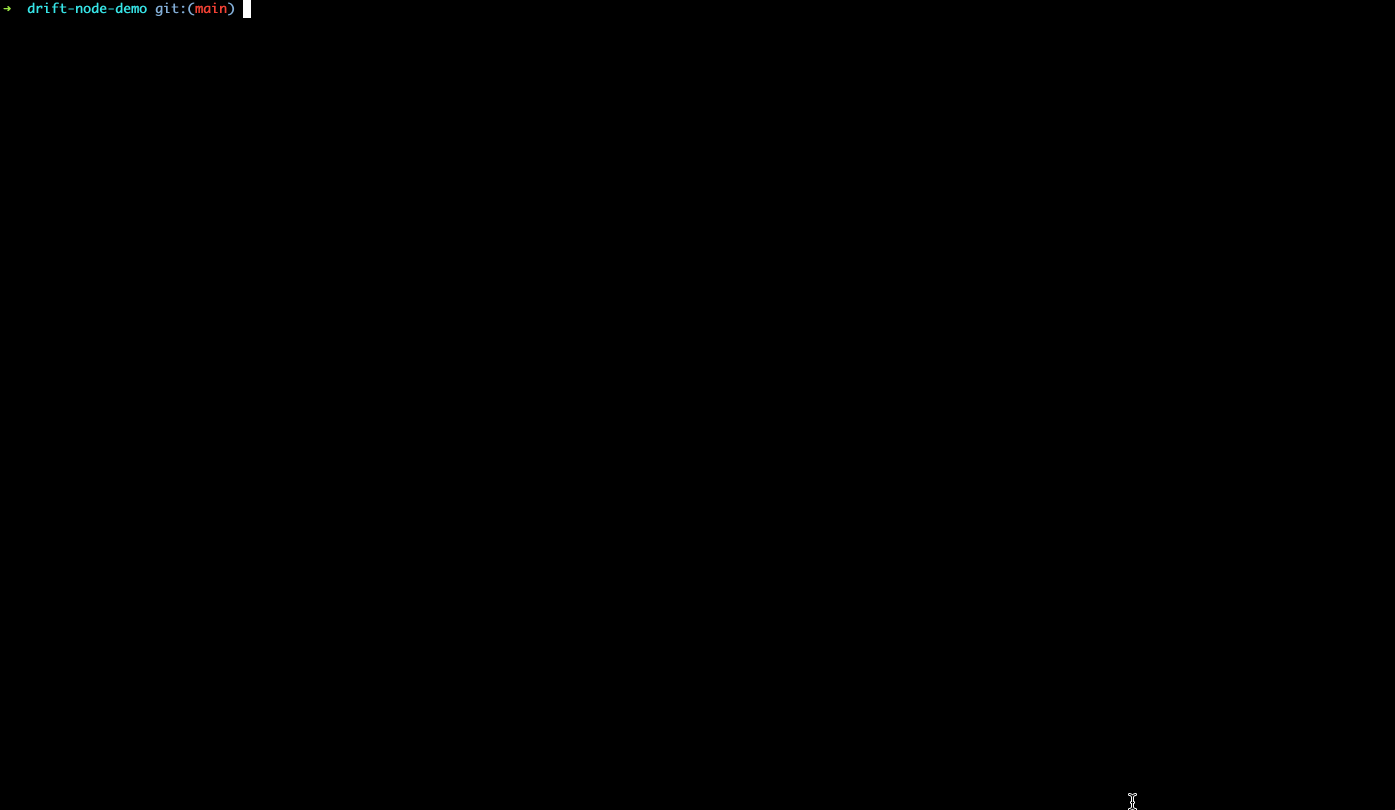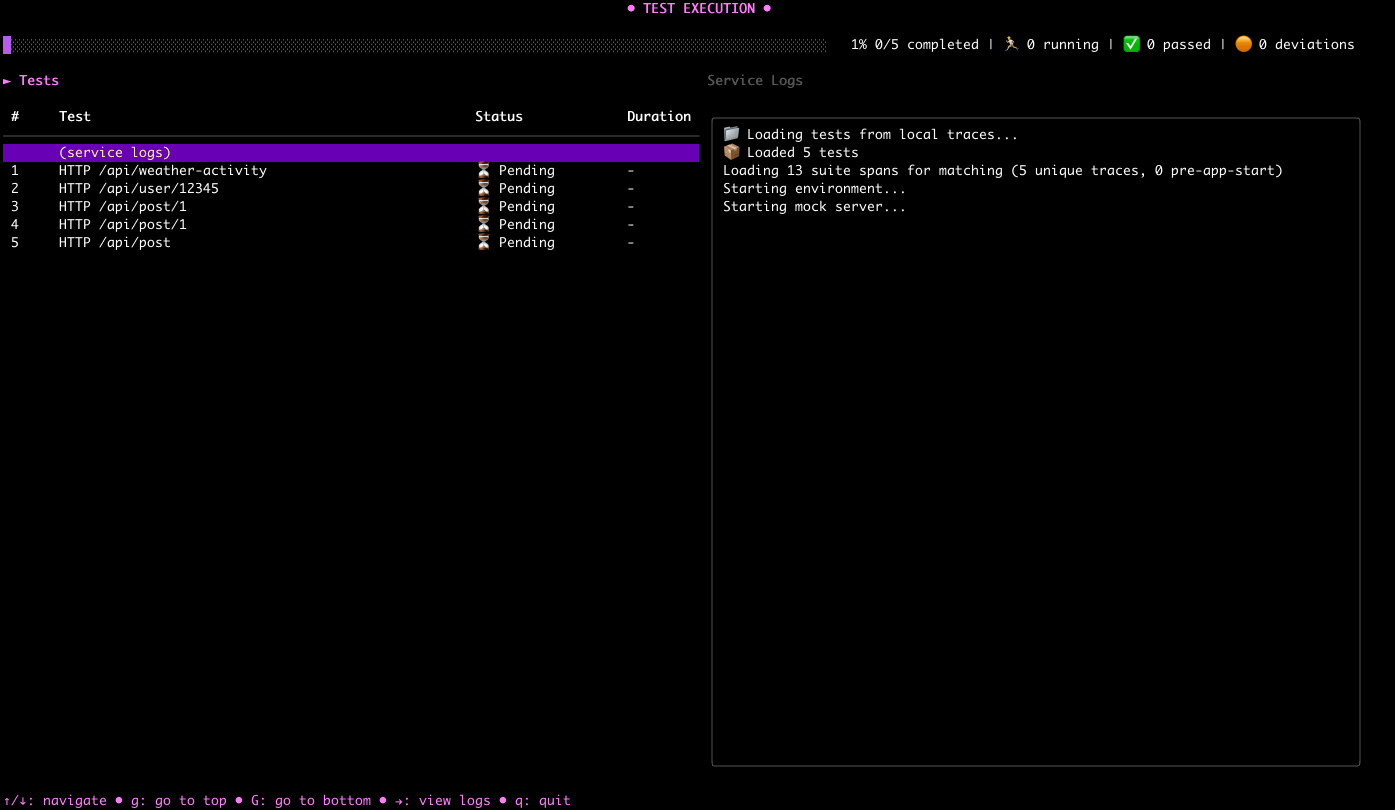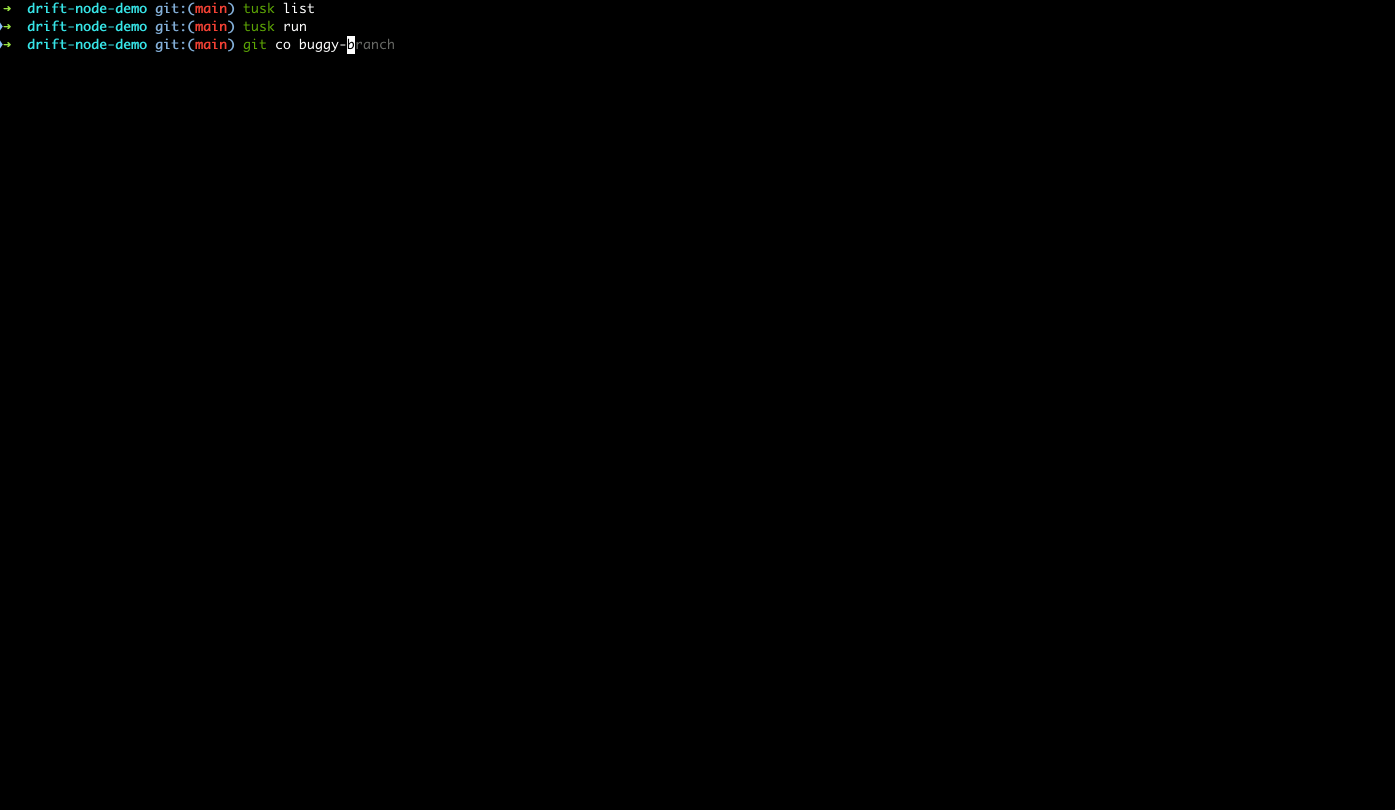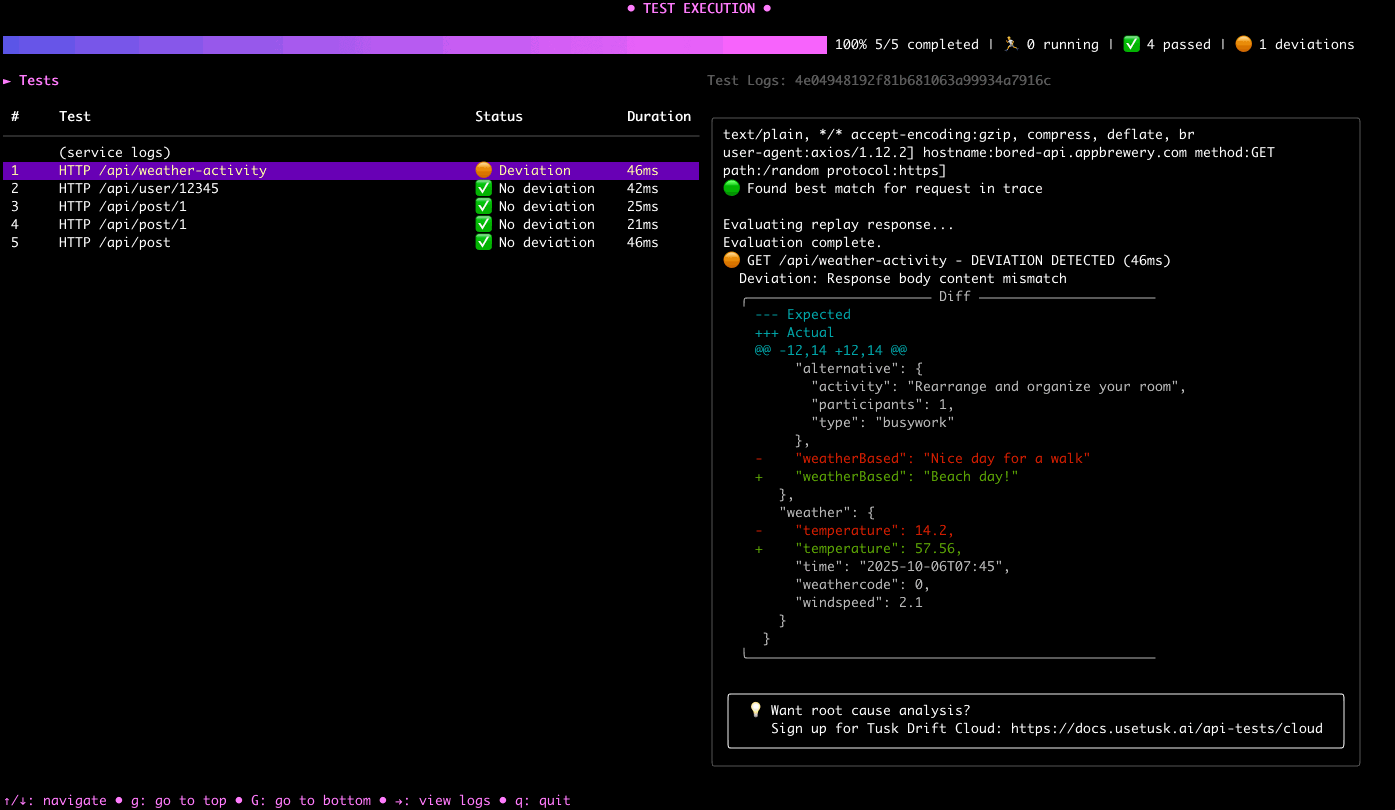
Node.js SDK for capturing and replaying API calls made to/from your service

Burp Commander written in Go

Vulnerability Assessment Scanner with Report Generation

Integrate Google Drive <= 1.1.99 - Missing Authorization via REST API Endpoints

Alexa skill example for Faraday API

Proof-of-concept exploit and advisory for CVE-2026-54356, a Budibase missing-authorization flaw that lets low-privilege users mint S3 pre-signed…

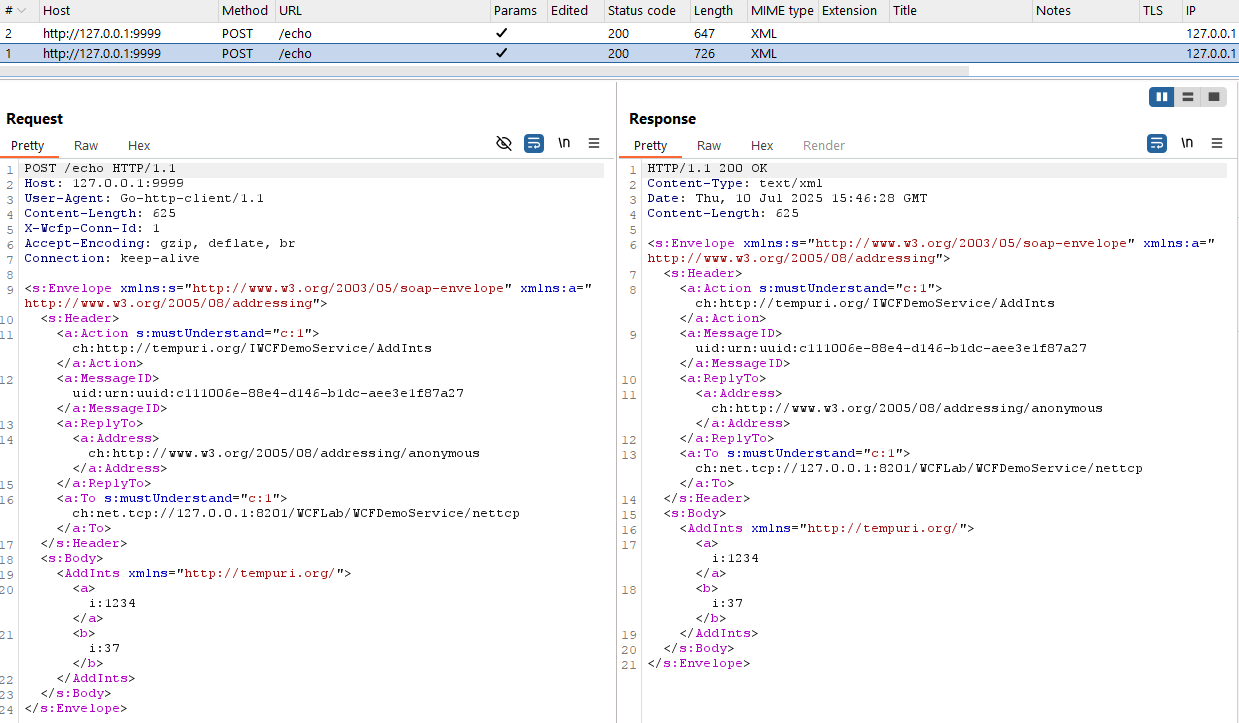
A proxy for net.tcp-based WCF traffic.

Spring4Shell , Spring Framework RCE (CVE-2022-22965) , Burpsuite Plugin

Burp Bounty profile for detecting Apache Text4Shell (CVE-2022-42889), an RCE in Commons Text 1.5-1.9, by scanning HTTP requests.

PoC for CVE-2026-71554 - h2 duplicate Host header request smuggling primitive (fixed in 4.4.1)

Reproducer for CVE-2026-46453 — Apache Camel camel-elasticsearch-rest-client unprefixed-header injection (operation/query override via inbound HTTP…

Local Docker lab for reproducing CVE-2026-55255, an IDOR vulnerability in Langflow's Responses API. Validates cross-user flow execution in vulnerable…

CVE-2023-23752 nuclei template

Keyless active-probe security auditor for Directus CMS. Proves public-role data exposure, user enumeration, unauthenticated version/schema leaks,…

Provides PoC exploits and root-cause analysis for two GitLab GraphQL `@gl_introduced` directive vulnerabilities: unauthenticated method execution and…