
CVE-2026-25126
 jvr2022/cve-2026-25126
Proof-of-concept for CVE-2026-25126 demonstrating vote count manipulation in PolarLearn via improper runtime validation of the forum vote direction…
api-security-testingexploitationpenetration-testing+2
1
jvr2022/cve-2026-25126Proof-of-concept for CVE-2026-25126 demonstrating vote count manipulation in PolarLearn via improper runtime validation of the forum vote direction…
 tno-s3/wuppiefuzz
A coverage-guided REST API fuzzer developed on top of LibAFL
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.
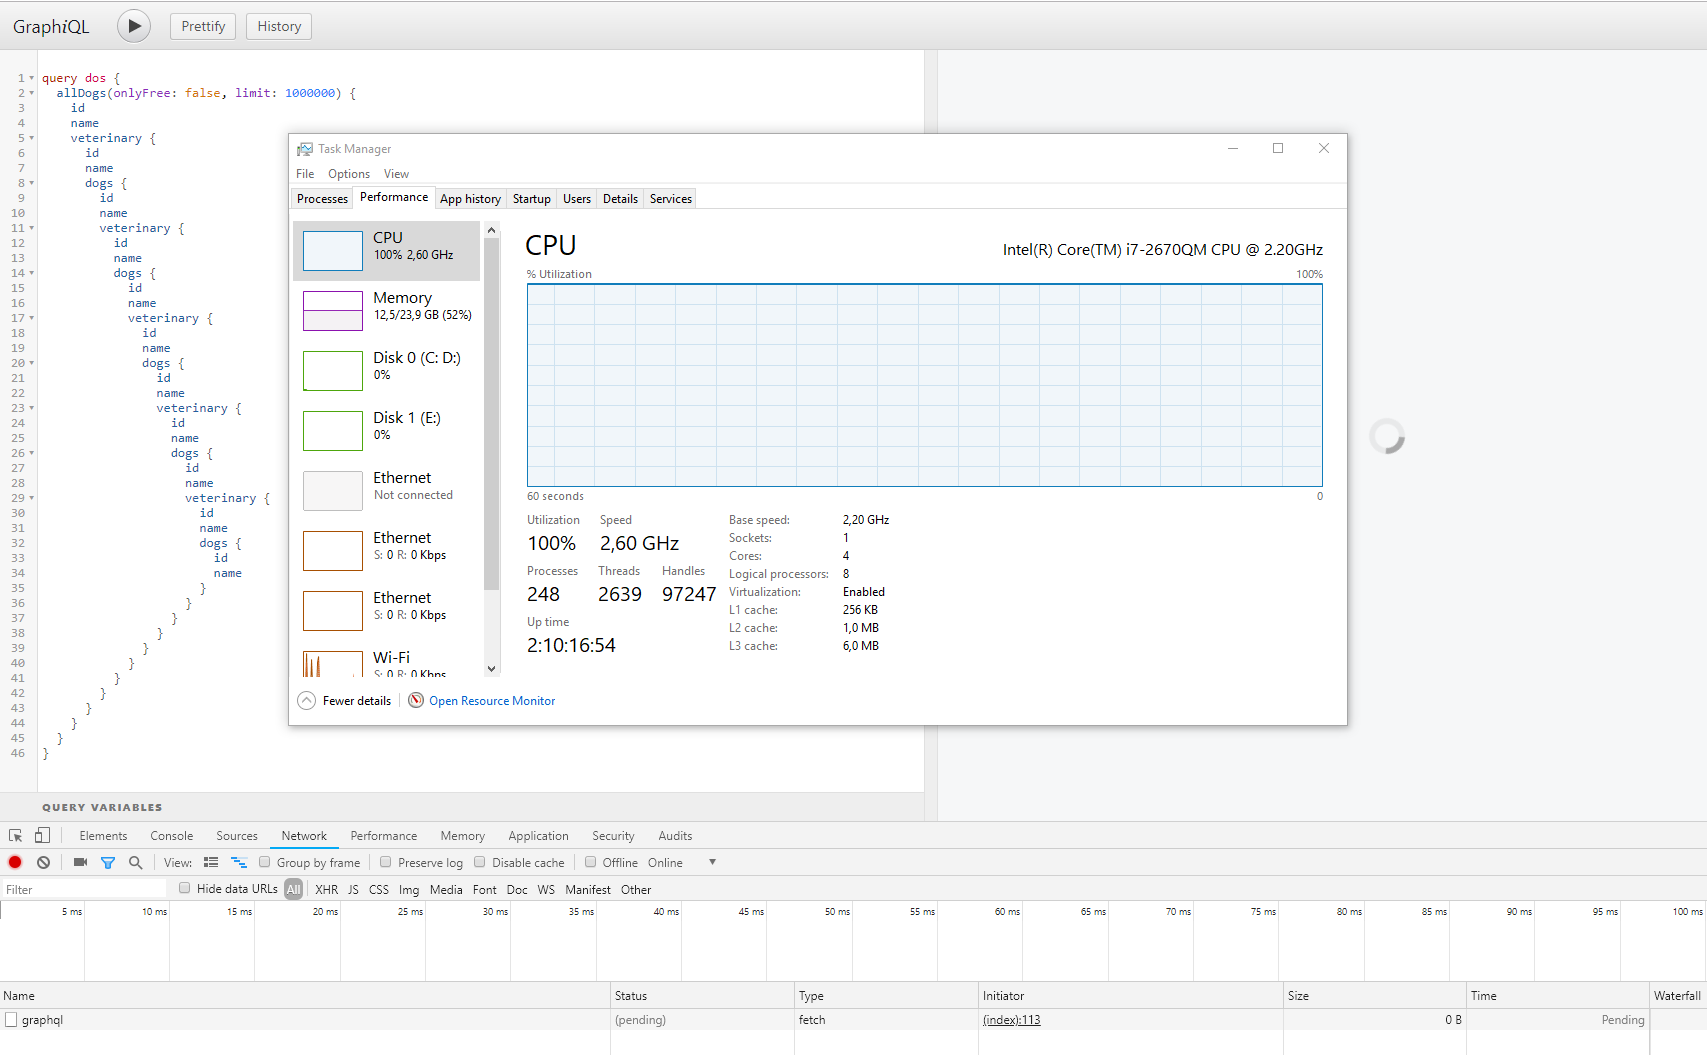 righettod/poc-graphql
Research on GraphQL from an AppSec point of view.
 roottusk/vapi
vAPI is Vulnerable Adversely Programmed Interface which is Self-Hostable API that mimics OWASP API Top 10 scenarios through Exercises.
 george0papasotiriou/cve-2026-11103-graphql-batching-alias-rate-limit-bypass
Proof-of-concept exploit for CVE-2026-11103 demonstrating GraphQL rate-limit bypass through batching and field aliases; includes vulnerable Node.js…
 httpie/cli
🥧 HTTPie CLI — modern, user-friendly command-line HTTP client for the API era. JSON support, colors, sessions, downloads, plugins & more.
 rtcatc/packer-fuzzer
Packer Fuzzer is a fast and efficient scanner for security detection of websites constructed by javascript module bundler such as Webpack.
 asamassekou10/ship-safe
The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…
 chrislockard/api_wordlist
A wordlist of API names for web application assessments
 saffron-health/libretto
The AI toolkit for building reliable browser automations
 bbva/apicheck
The DevSecOps toolset for REST APIs
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
 opaxial/cve-2026-9830
CVE-2026-9830 Proof of Concept
 codewatchorg/sqlipy
SQLiPy is a Python plugin for Burp Suite that integrates SQLMap using the SQLMap API.
 net-hunter121/api-wordlist
Curated wordlists of API function names, verbs, and nouns for fuzzing web application endpoints with Burp Suite Intruder.
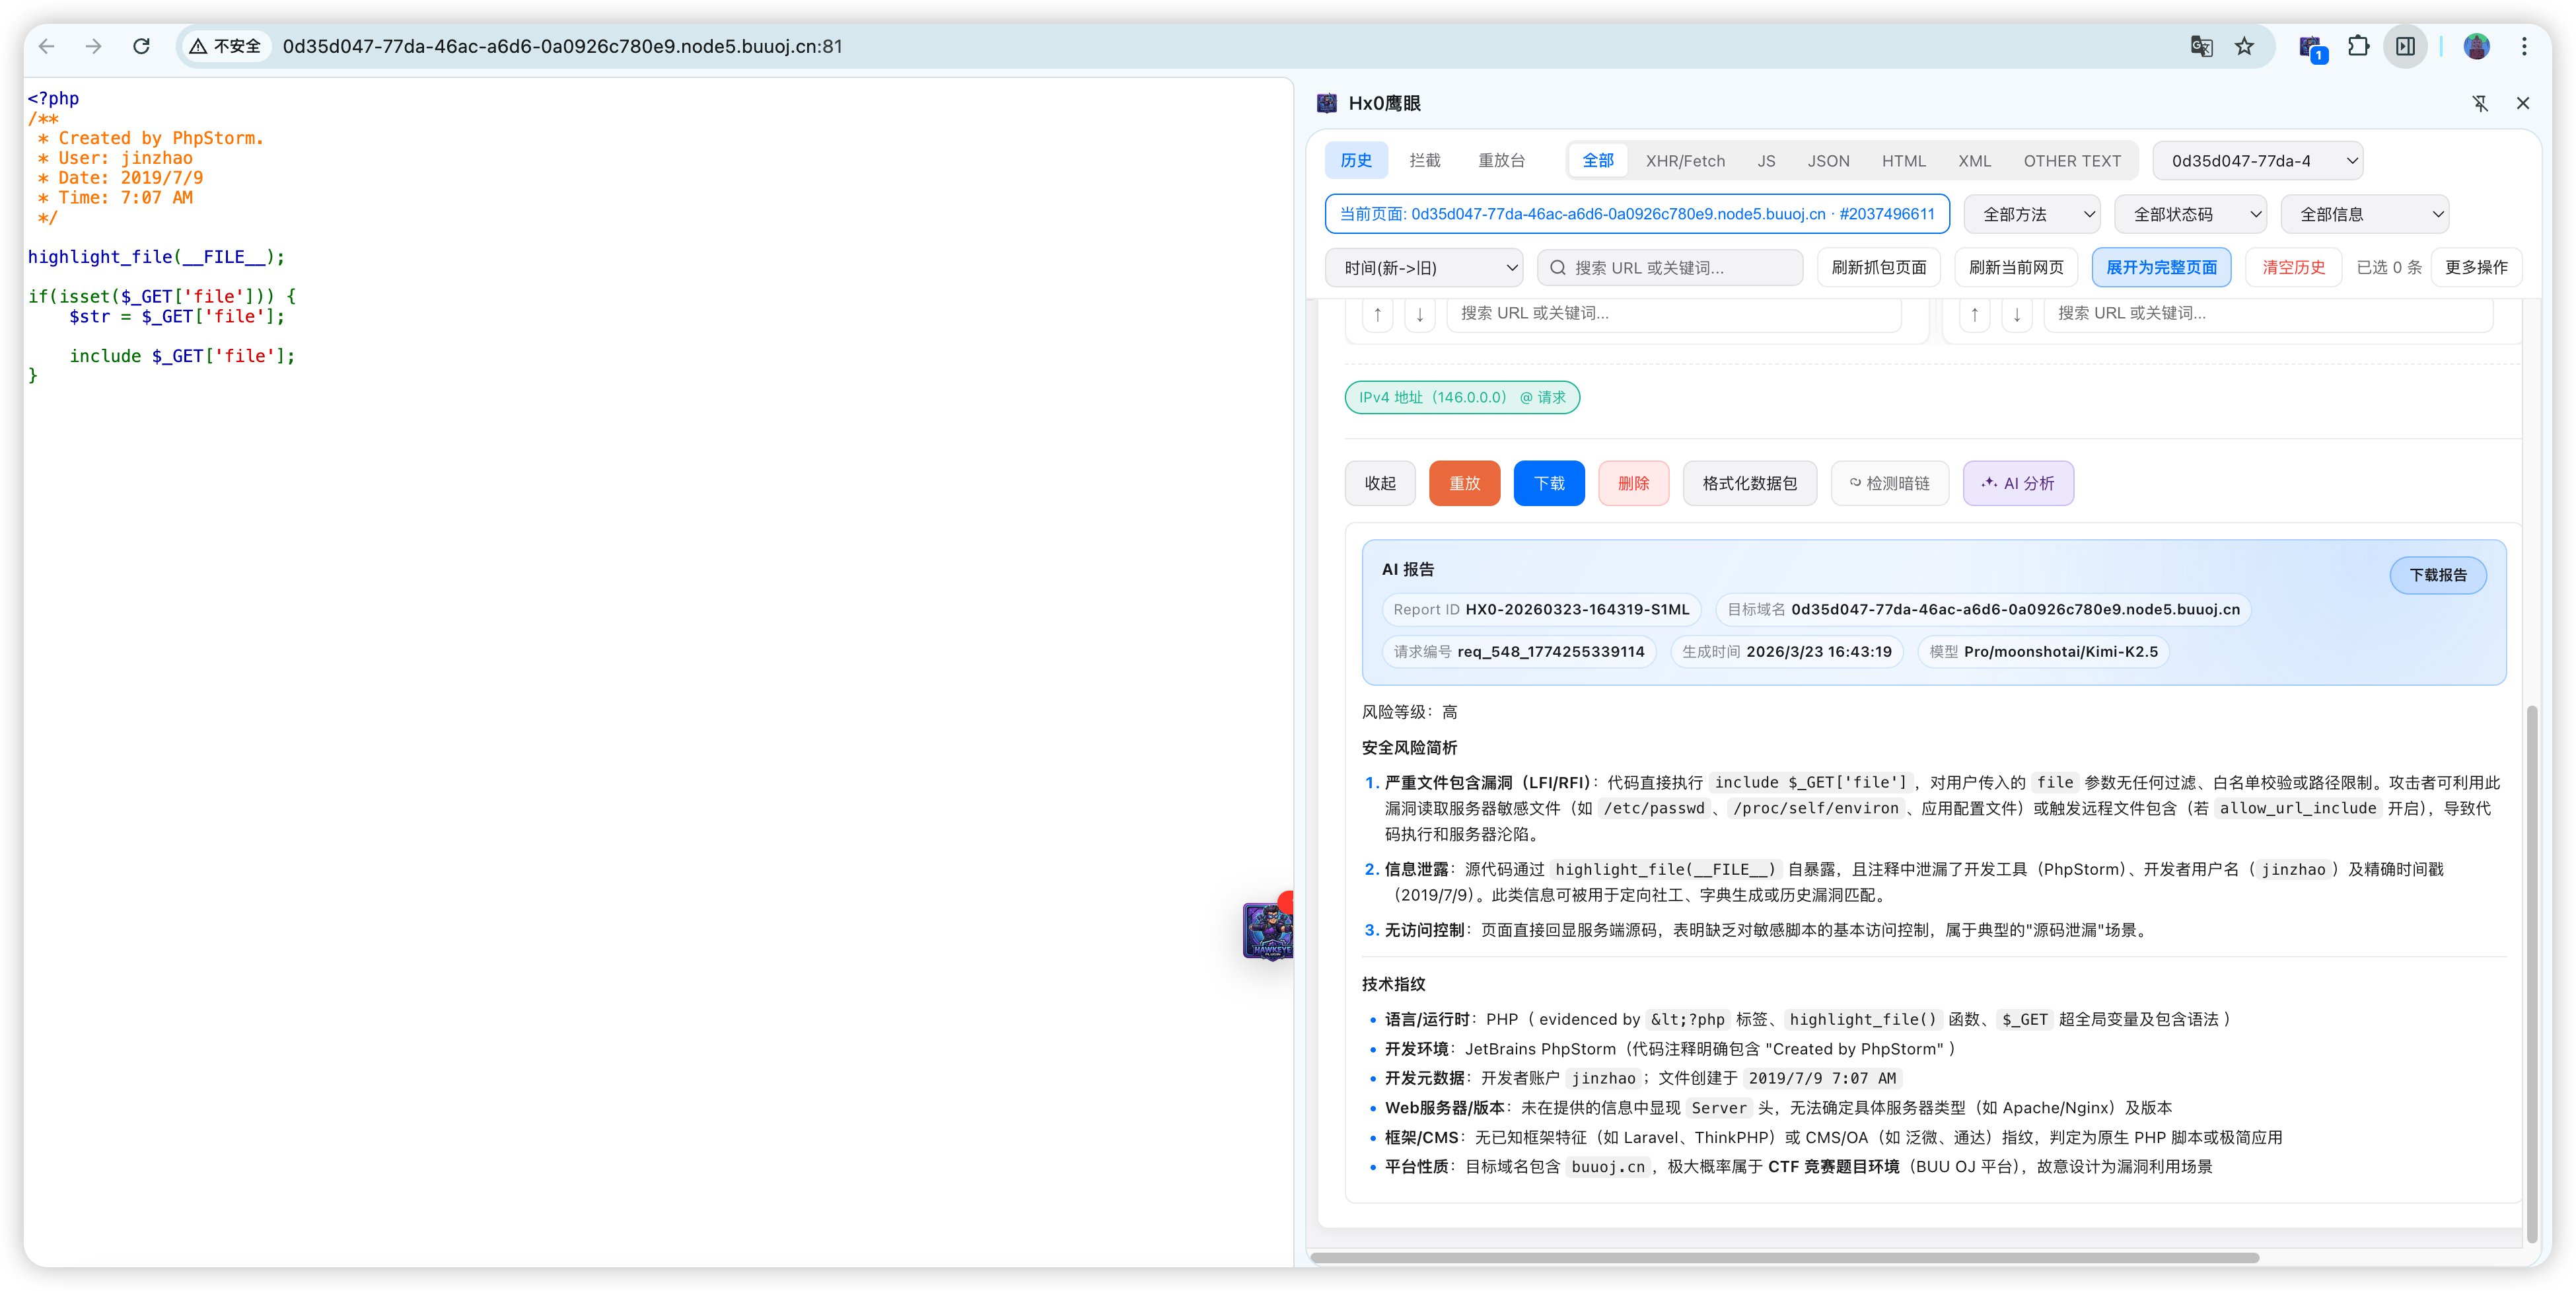 asaotomo/hx0-hawkeye
一个轻量级浏览器抓包与安全分析扩展,在浏览器侧边栏中即可完成抓包、拦截、修改、重放、规则检测与AI辅助分析的完整工作流。(A lightweight browser extension for traffic capture and security analysis, enabling…
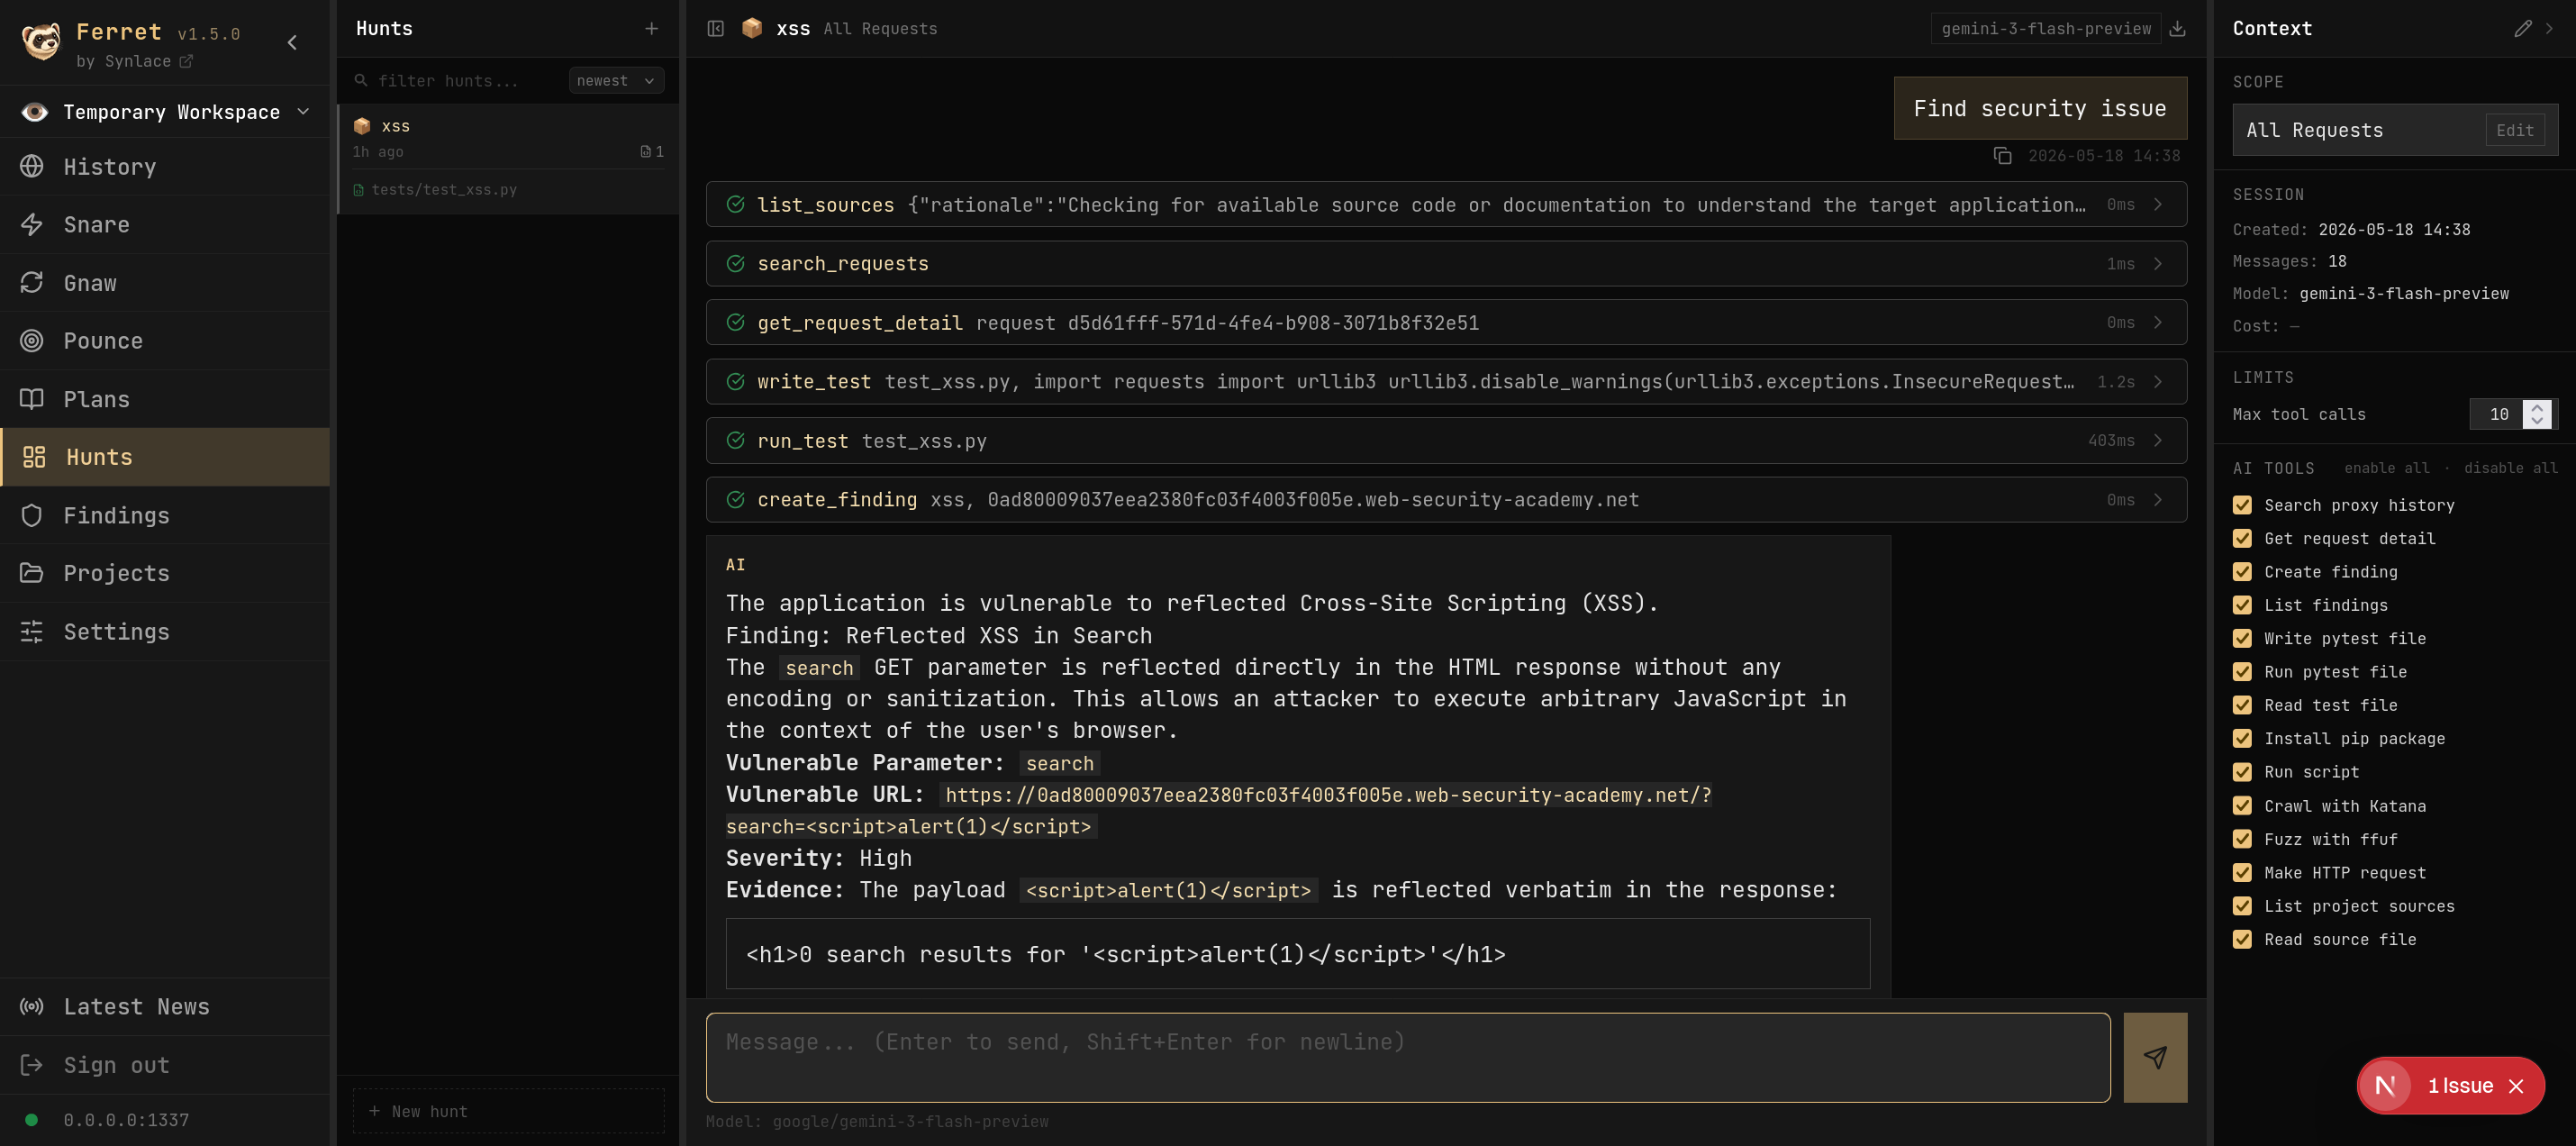 synlace/ferret
The collaborative web app pentest suite