

x8-Burp
 impact-i/x8-burp
Hidden parameters discovery suite
api-security-testinginformation-gatheringreconnaissance+2
2253 years ago
impact-i/x8-burpHidden parameters discovery suite
 moniik/poc_salesforce_lightning
Academic purposes only. Attack against Salesforce lightning with guest privilege.
 akabe1/oauthscan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
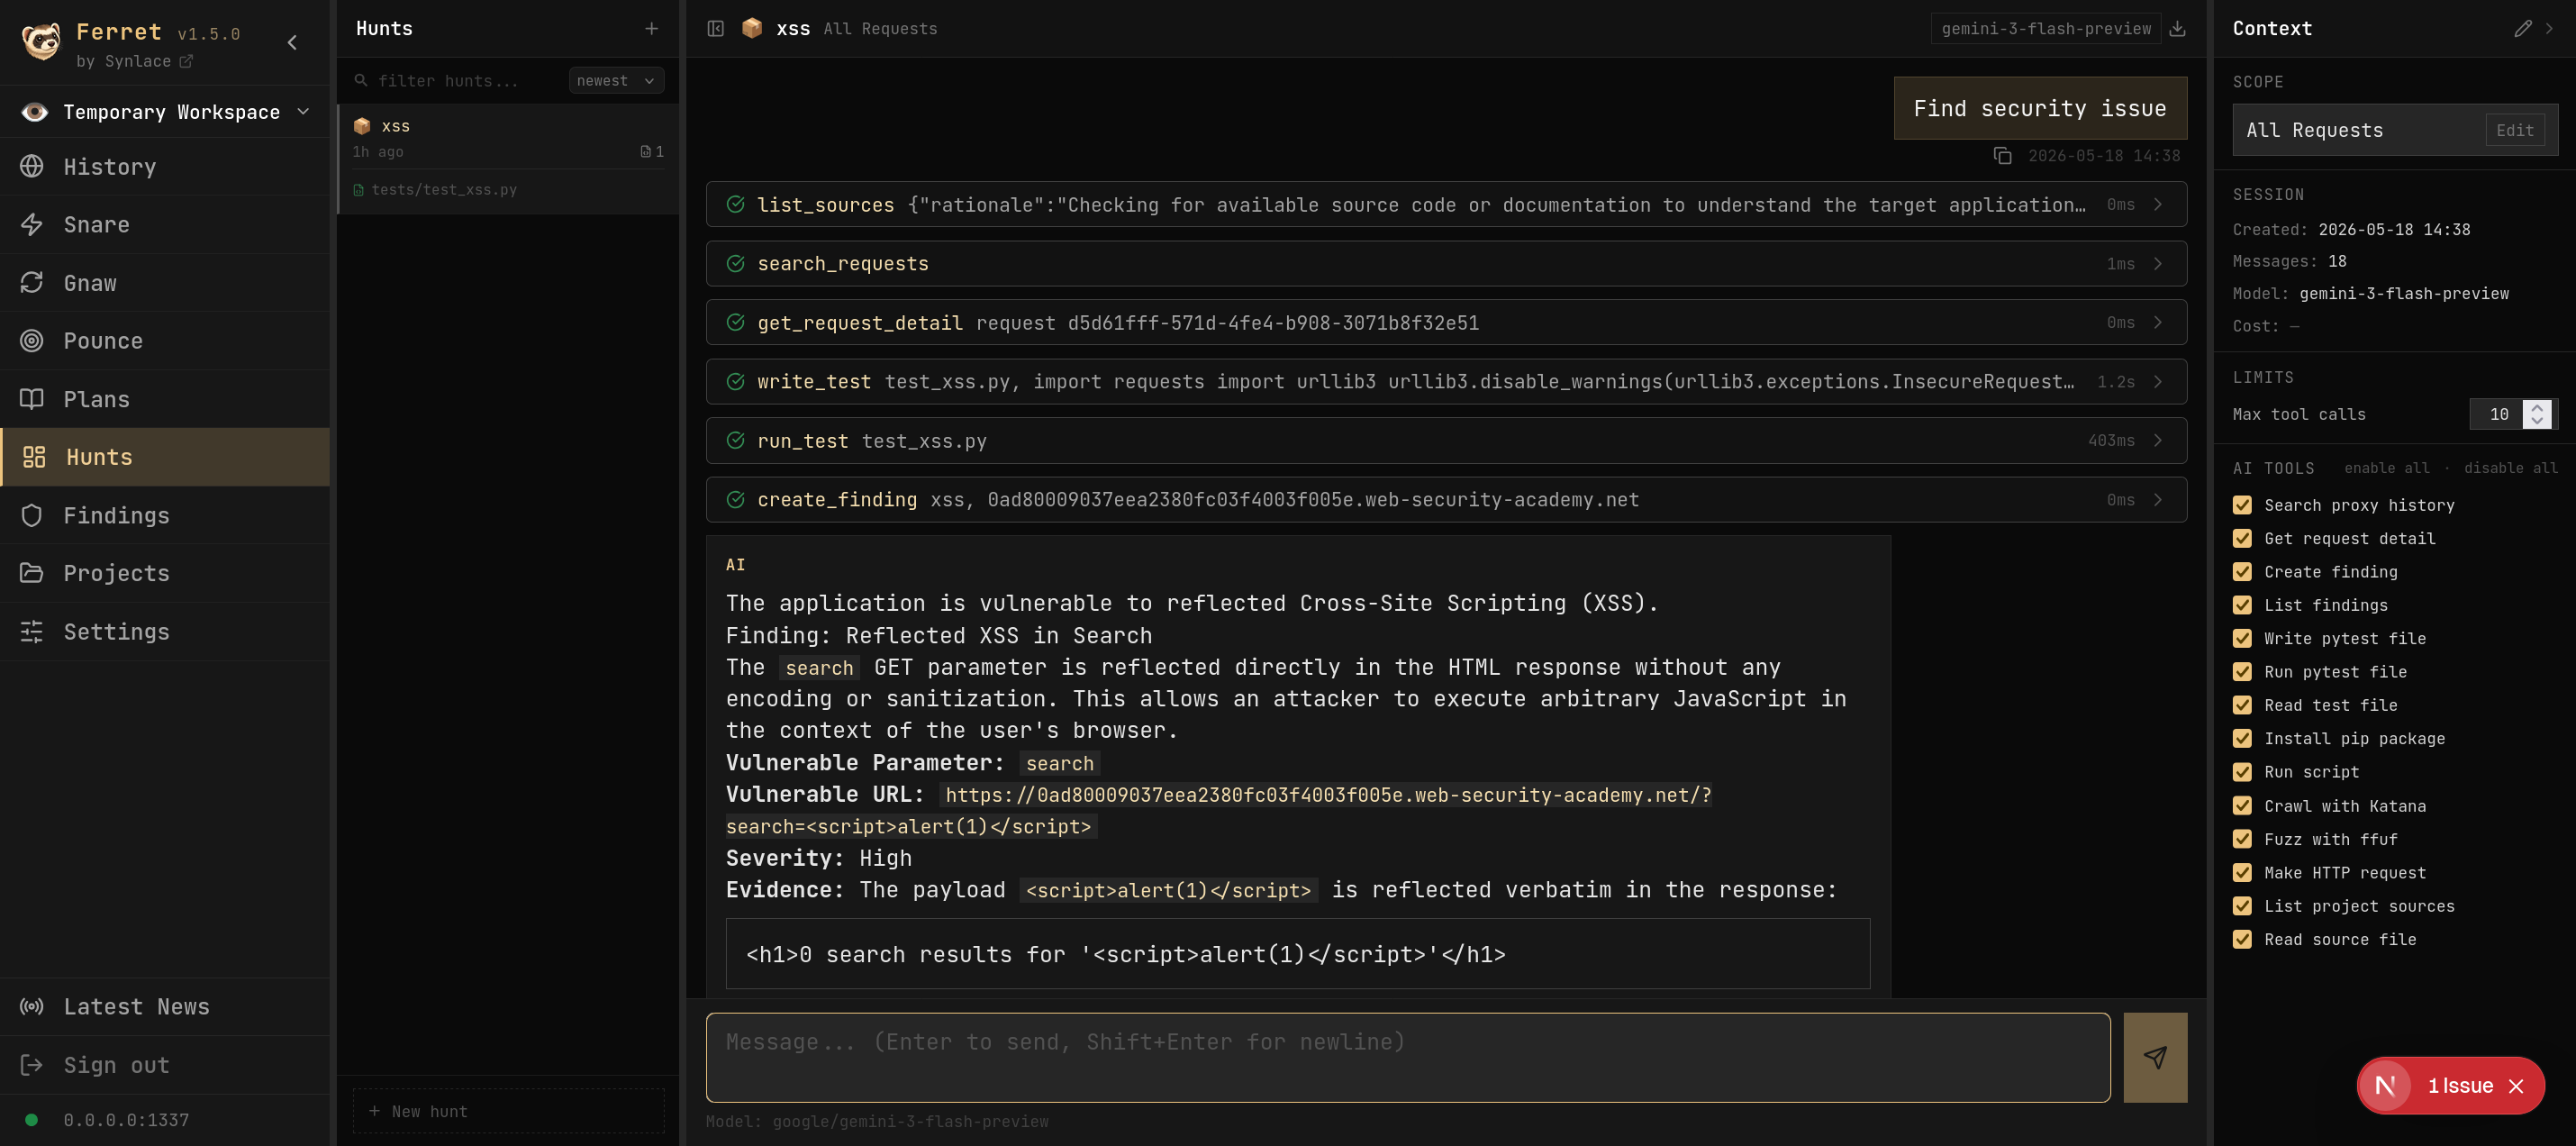 synlace/ferret
The collaborative web app pentest suite
 mda2av/http11probe
An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
 justmorpheus/burp-automation
Performing automated scan using Burp Suite Pro & Vmware Burp Rest API
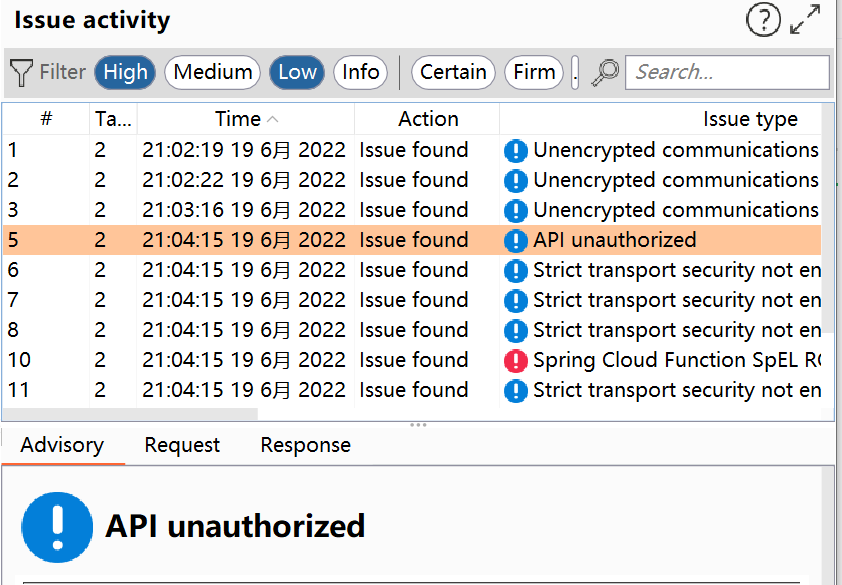 tpt11fb/springvulscan
burpsuite 的Spring漏洞扫描插件。SpringVulScan:支持检测:路由泄露|CVE-2022-22965|CVE-2022-22963|CVE-2022-22947|CVE-2016-4977
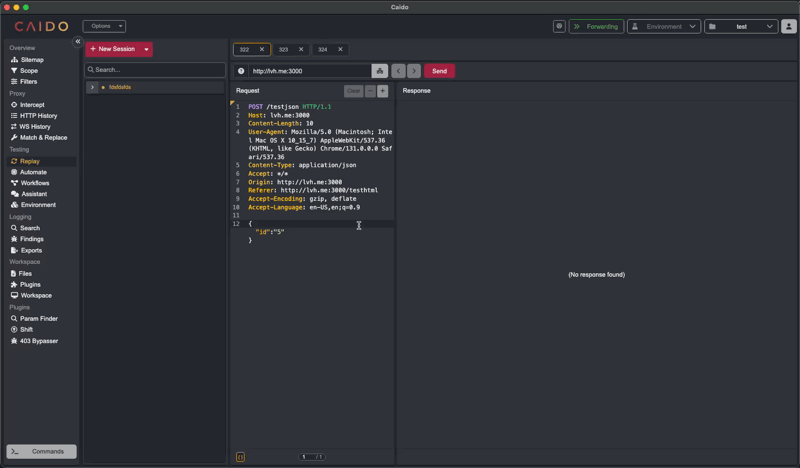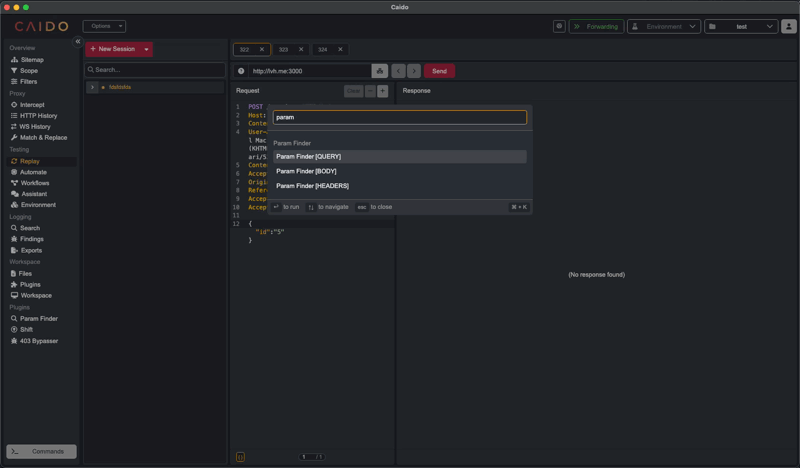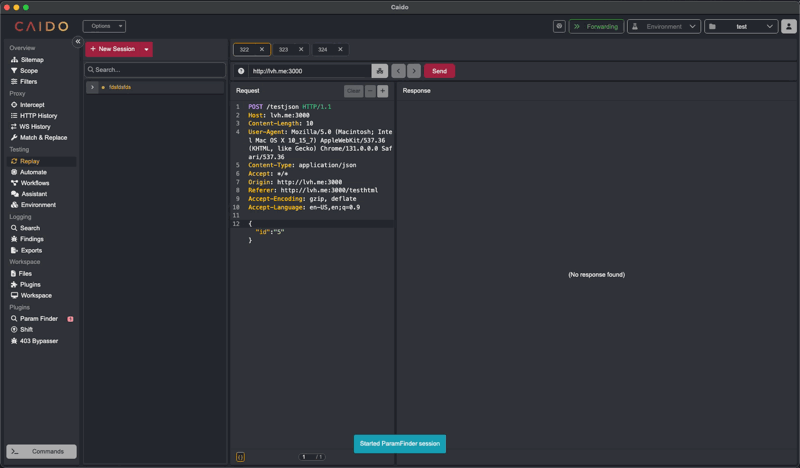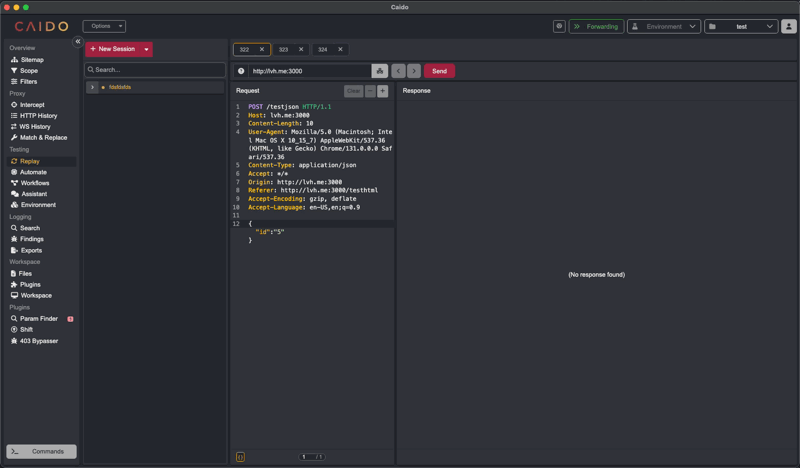 caido-community/paramfinder
Discover hidden parameters in Caido
 shaniidev/bug-reaper
Web2 bug bounty Agent Skill — evidence-based, no AI slop. Covers 18 vulnerability classes across HackerOne, Bugcrowd, Intigriti, and YesWeHack.
 nccgroup/wcfdser-ngng
A Burp Extender plugin, that will make binary soap objects readable and modifiable.
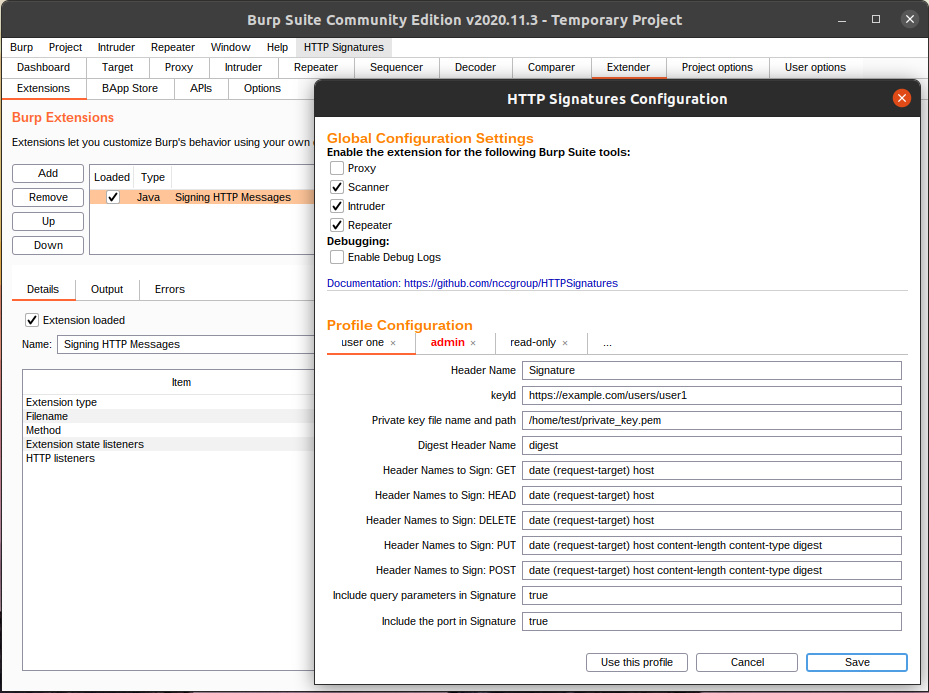 nccgroup/httpsignatures
A Burp Suite extension implementing the Signing HTTP Messages draft-ietf-httpbis-message-signatures-01 draft.
 nccgroup/amfdser-ngng
A Burp Extender plugin, that will take deserialized AMF objects and encode them in XML using the Xtream library
 weirdmachine64/redom
A Burp Suite extension that brings full DOM rendering capabilities directly into Burp, enabling effective security testing of modern JavaScript-heavy…
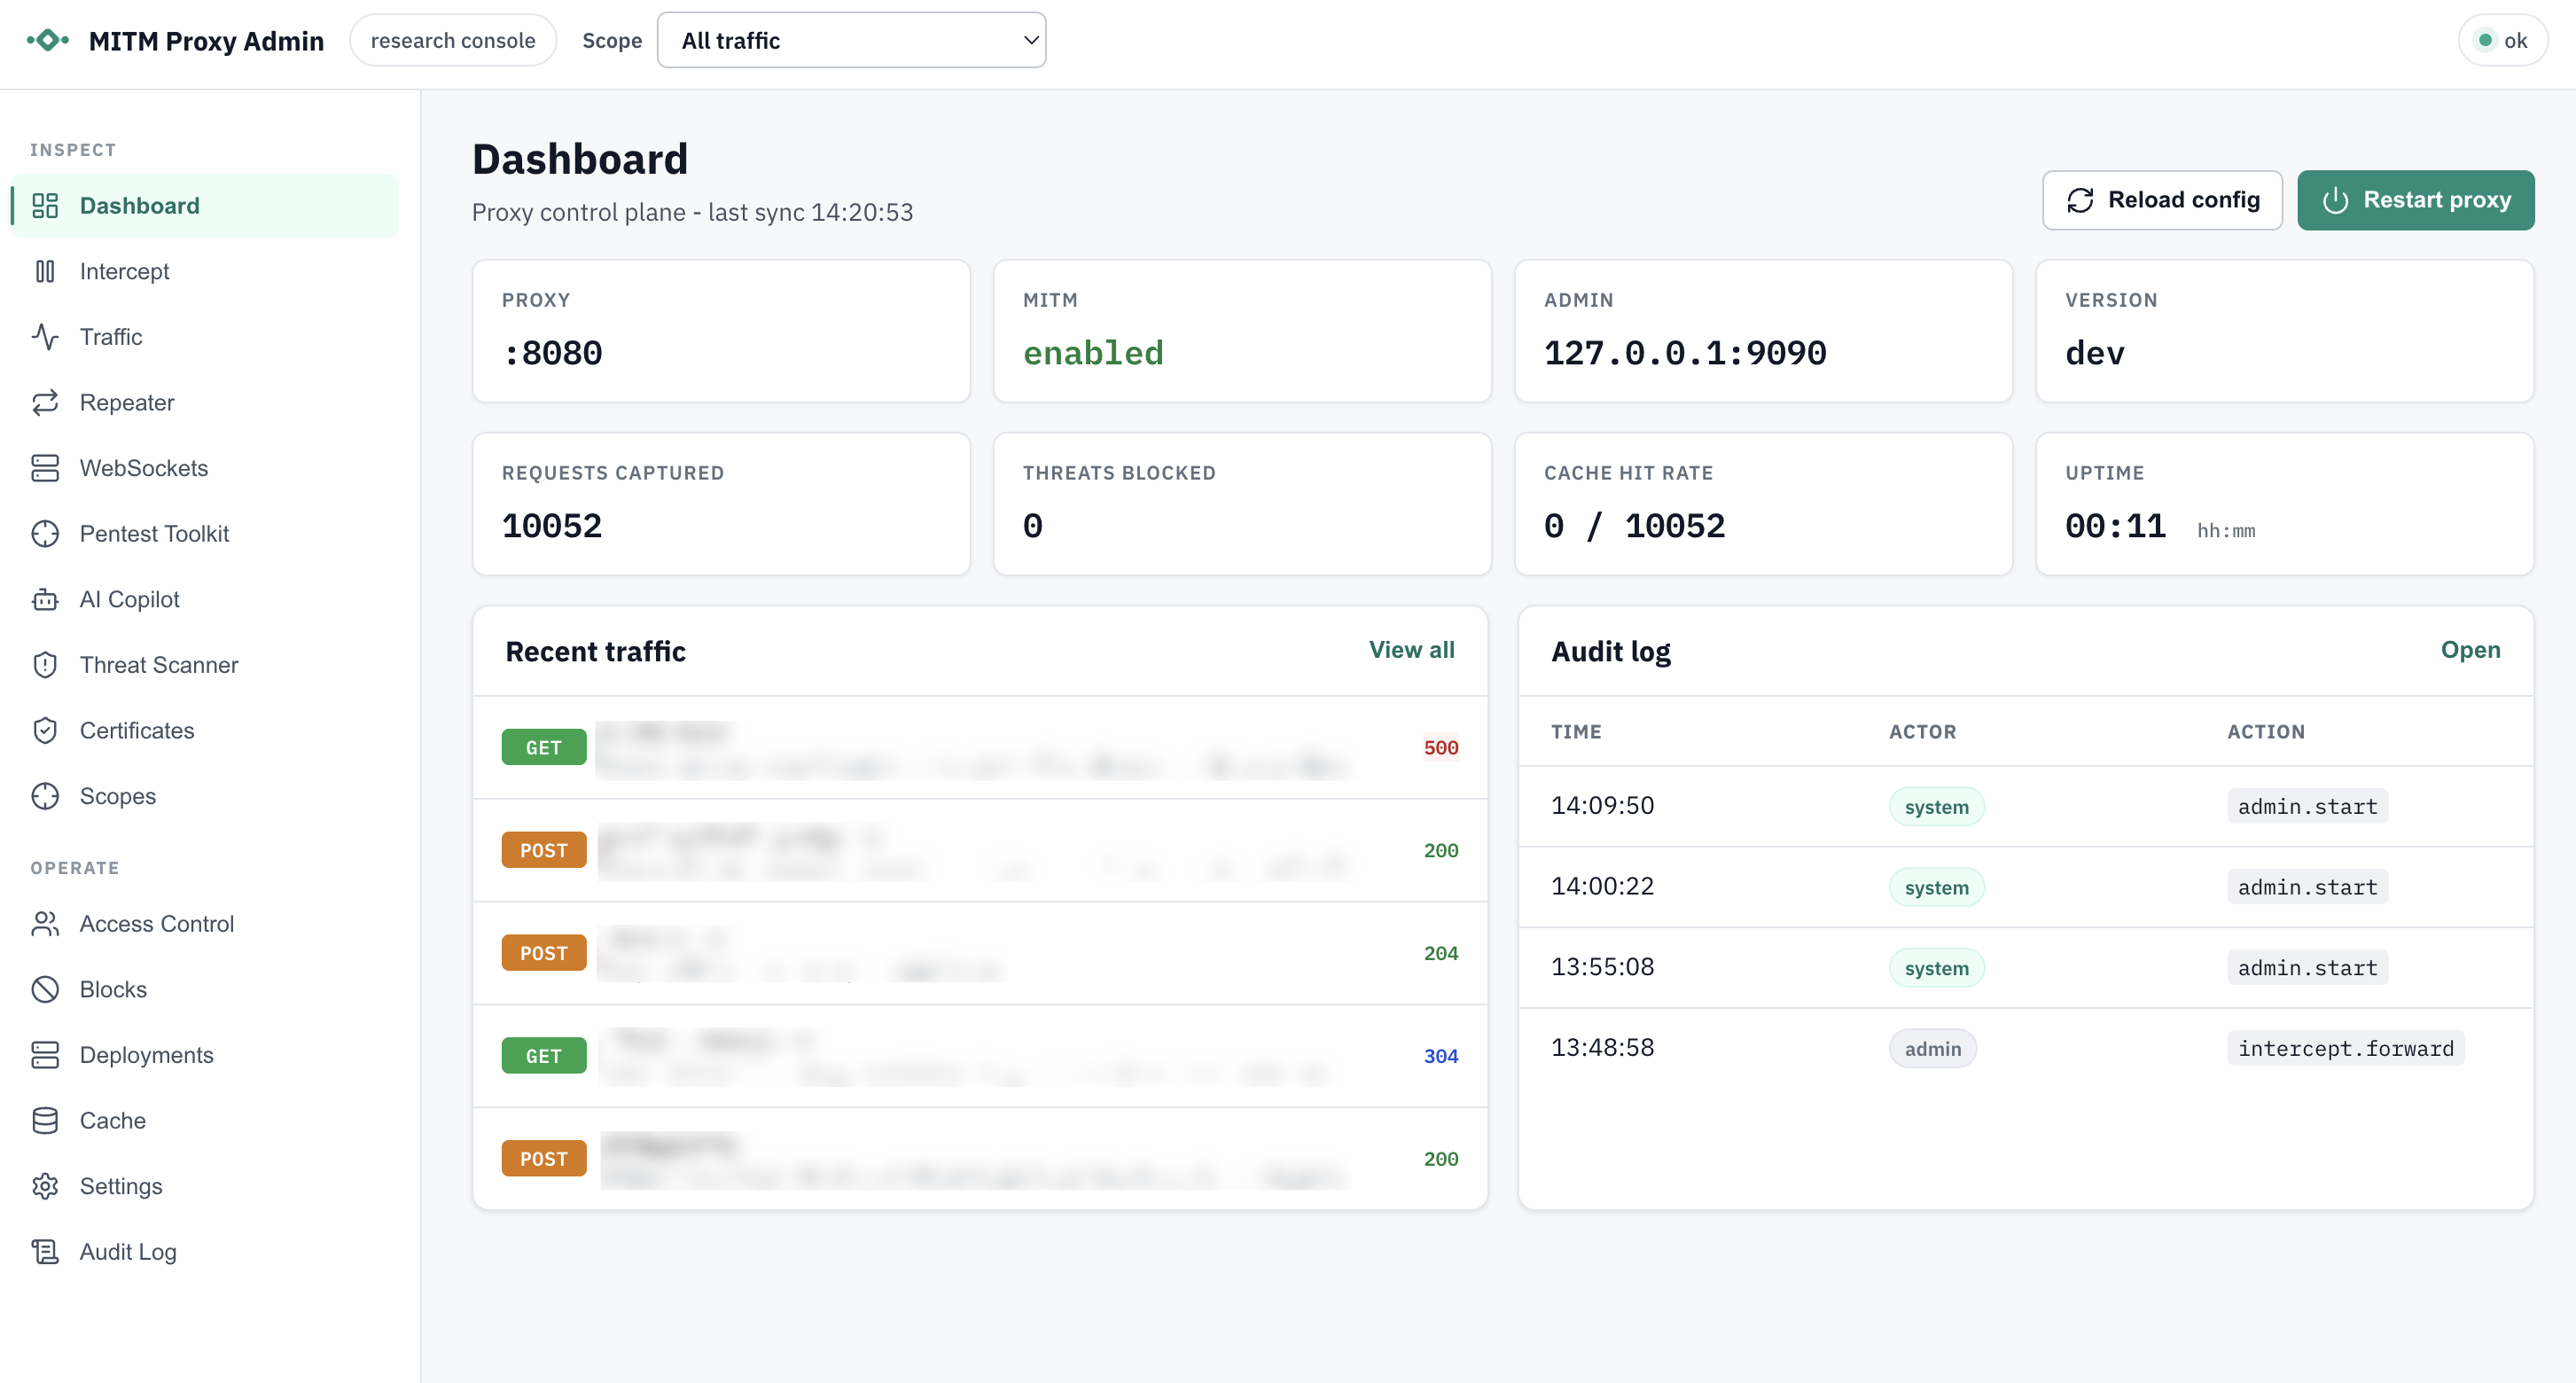 welfordian/mitm-proxy
Go-based MITM HTTP/HTTPS proxy with HTTP/2 and HTTP/1.1 interception, local CA/per-host cert generation, CONNECT/WebSocket tunneling, disk caching,…
 b0rn2d/spring-cloud-gateway-nacos
Nacos下Spring-Cloud-Gateway CVE-2022-22947利用环境
 hunzi0/cve-2022-22947-rce_poc
批量url检测Spring-Cloud-Gateway-CVE-2022-22947
 yutusec/apisix_crack
Apisix系列漏洞:未授权漏洞(CVE-2021-45232)、默认秘钥(CVE-2020-13945)批量探测。