
toolbox
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
api-security-testingcrawlerdynamic-analysis-sandboxing+8
43
go-appsec/toolboxCollaborative application security testing between humans and agents via CLI and MCP
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 sobri3195/pegasus-pentest-arsenal
A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
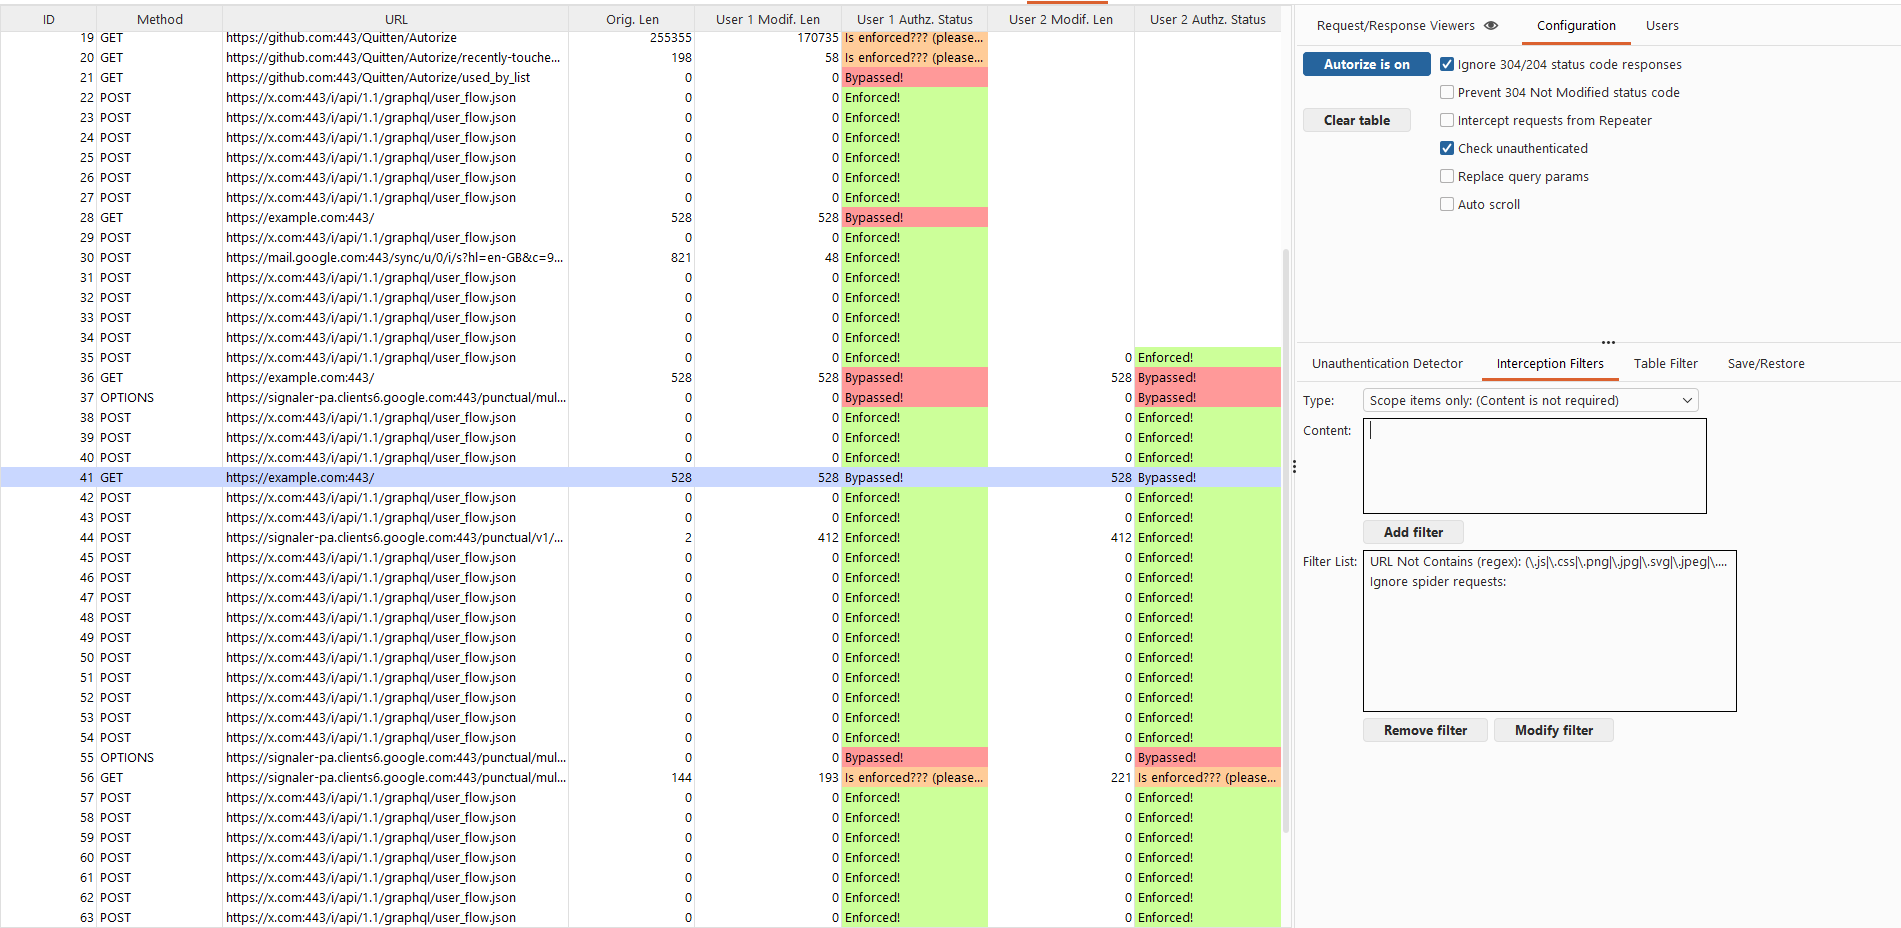 quitten/autorize
Automatic authorization enforcement detection extension for burp suite written in Jython developed by Barak Tawily in order to ease application…
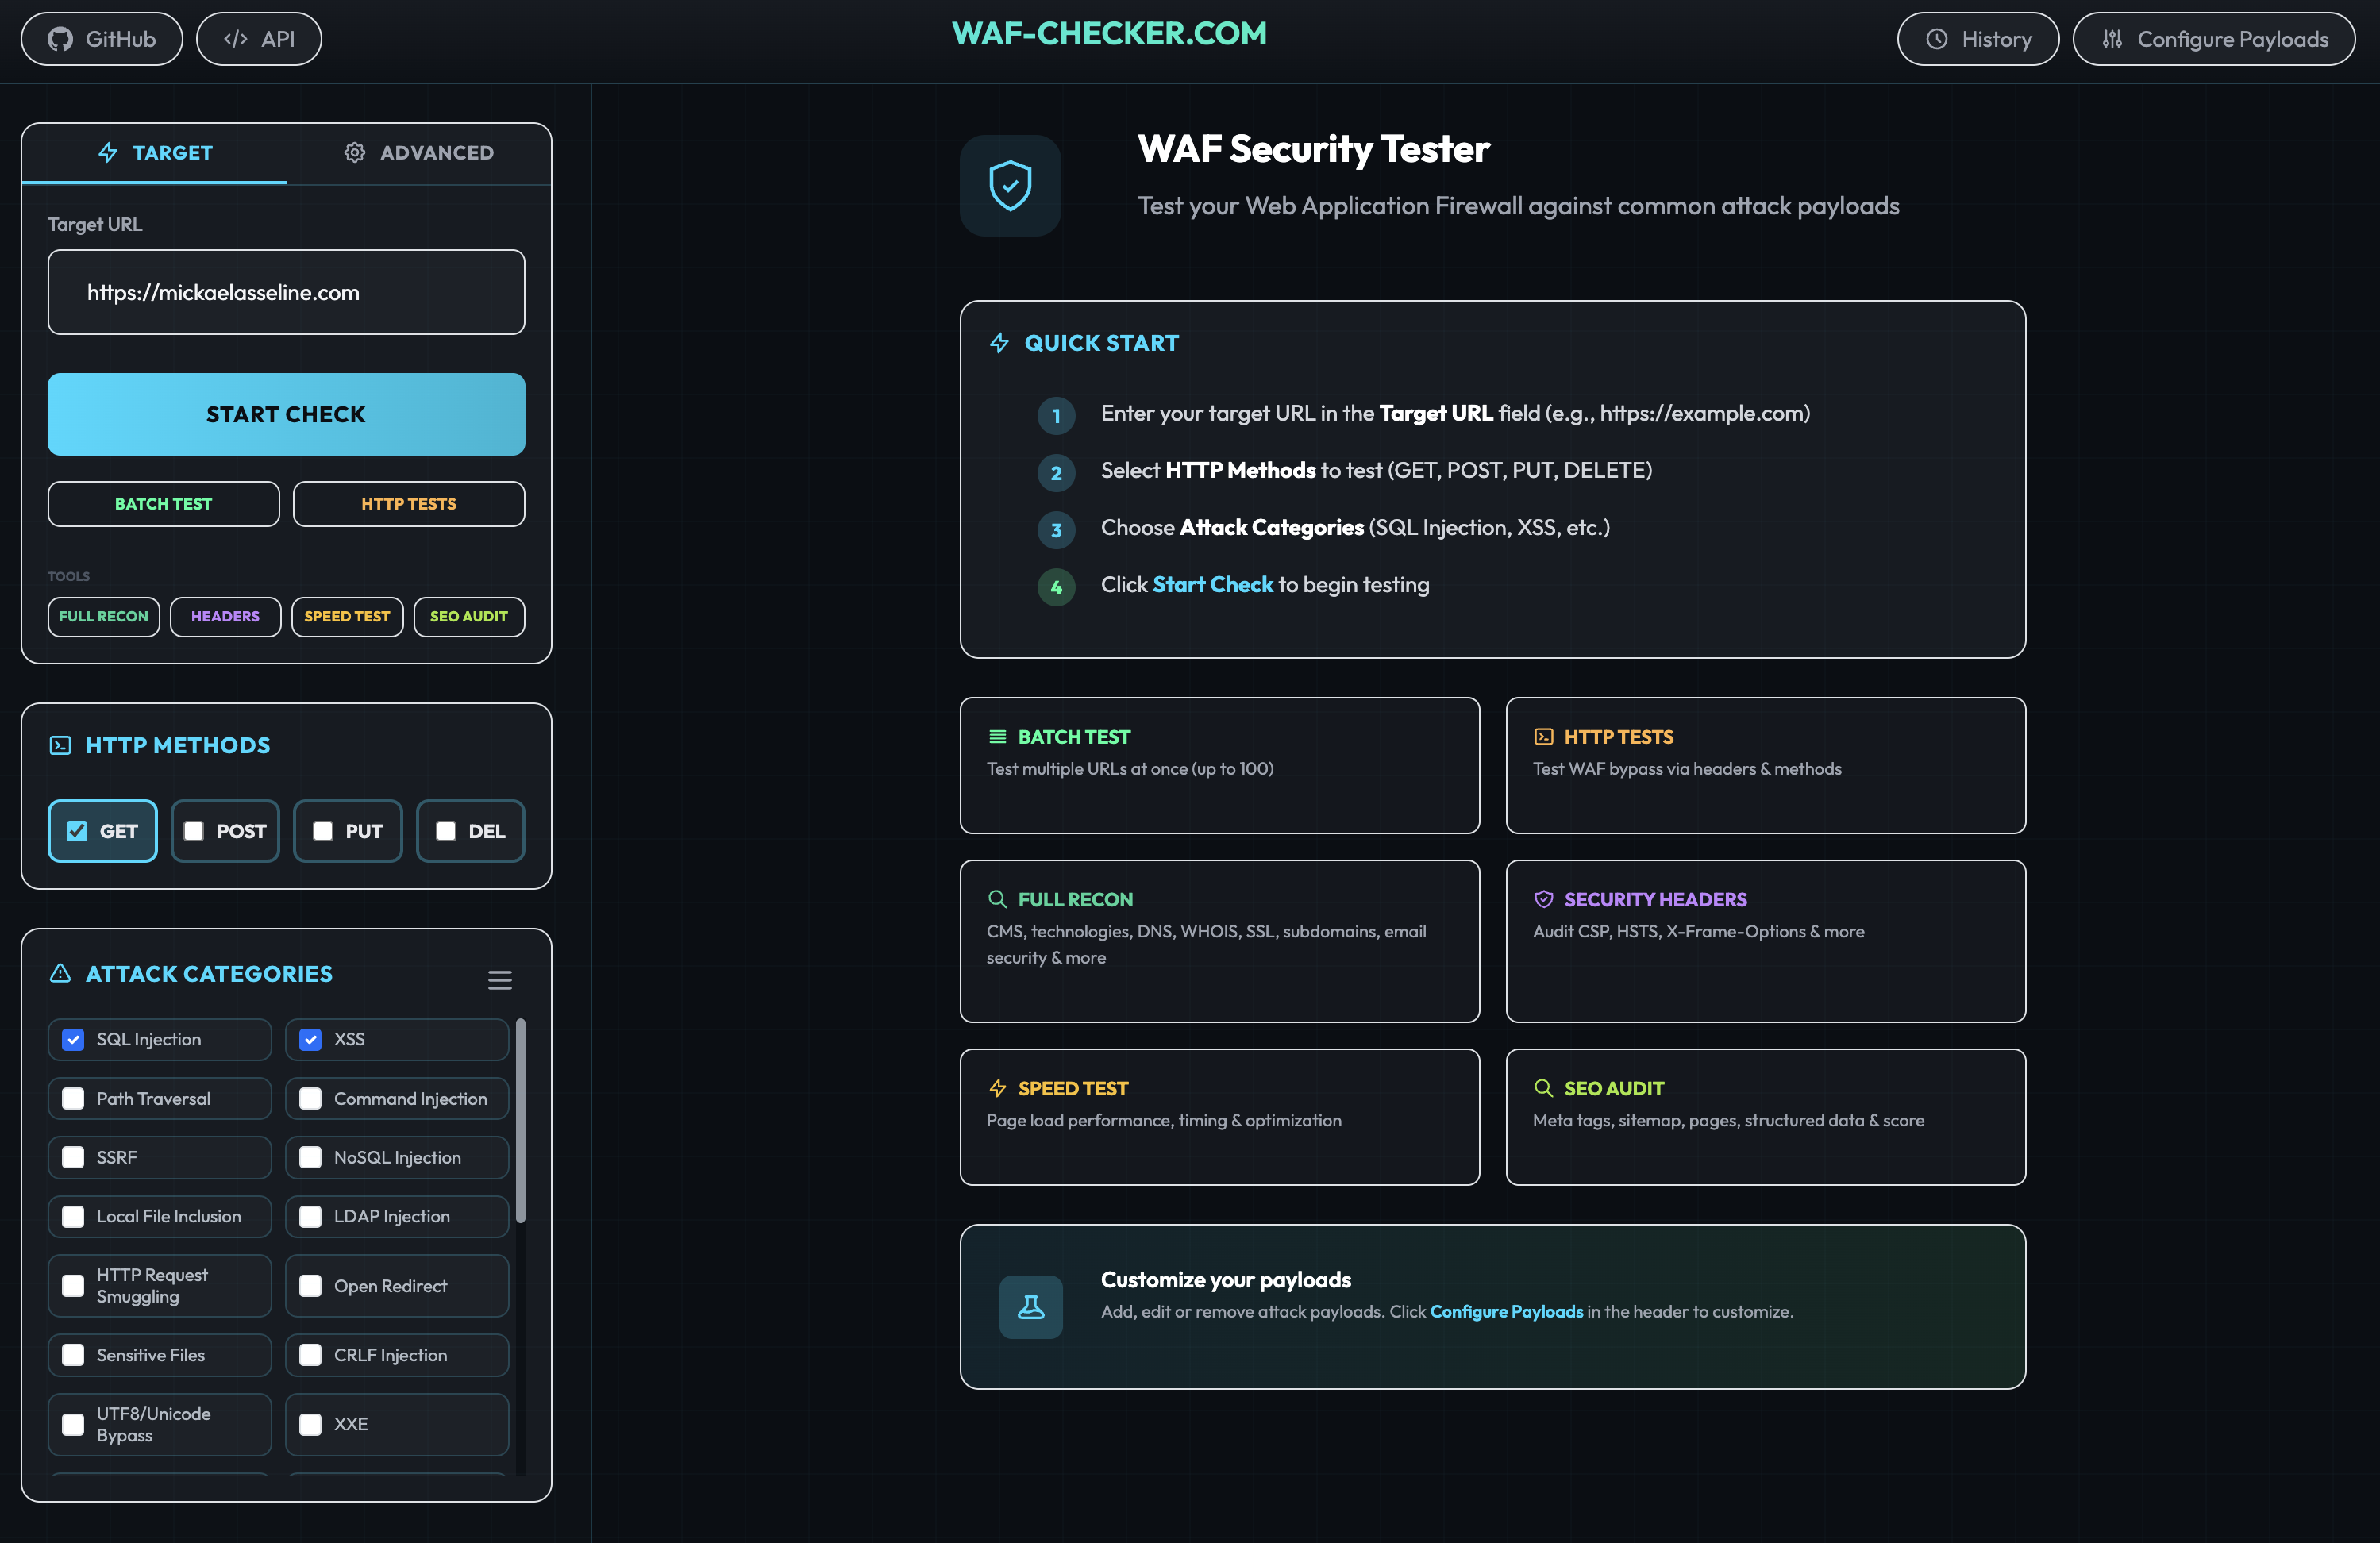 papamica/waf-checker
Tests your WAF with +160 payloads
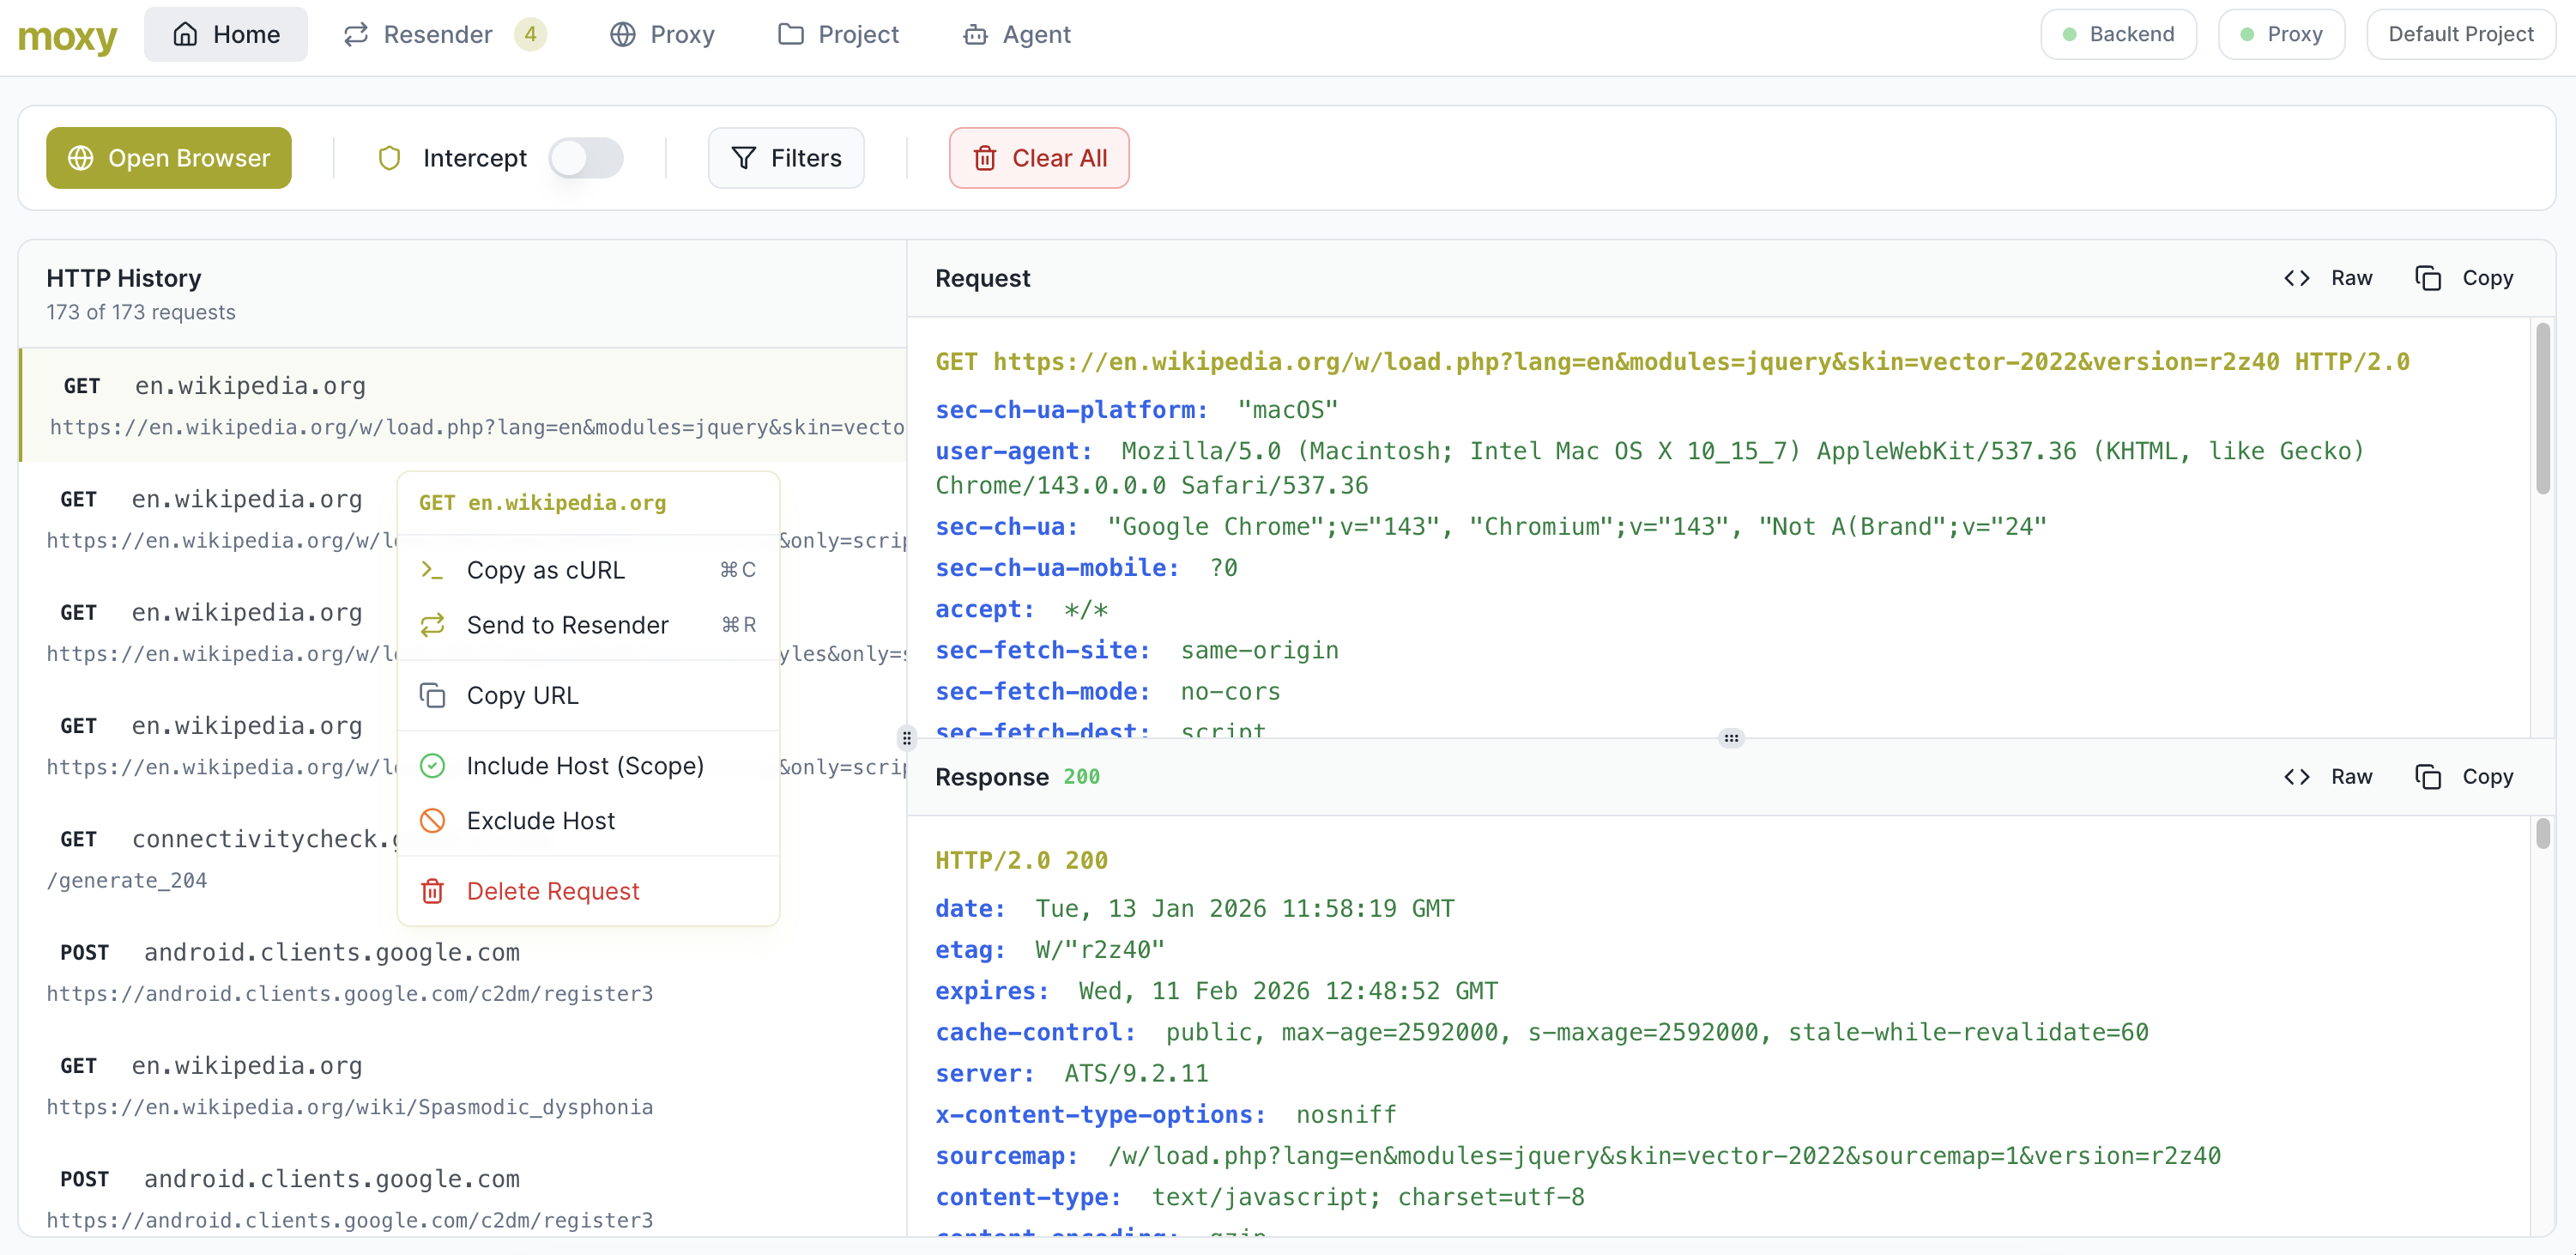 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 theronielanddaronpodcastshow/svja
The Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…
 sharma19d/cve-2025-61148
The vulnerability exists in the Student Payment API. The application fails to properly validate whether the user requesting a receipt is authorized…
 secsys-fdu/cve-2025-51862
Demonstrates an IDOR vulnerability in TelegAI's chat API allowing unauthorized conversation tampering, leading to phishing and XSS-based account…
 chrislockard/api_wordlist
A wordlist of API names for web application assessments
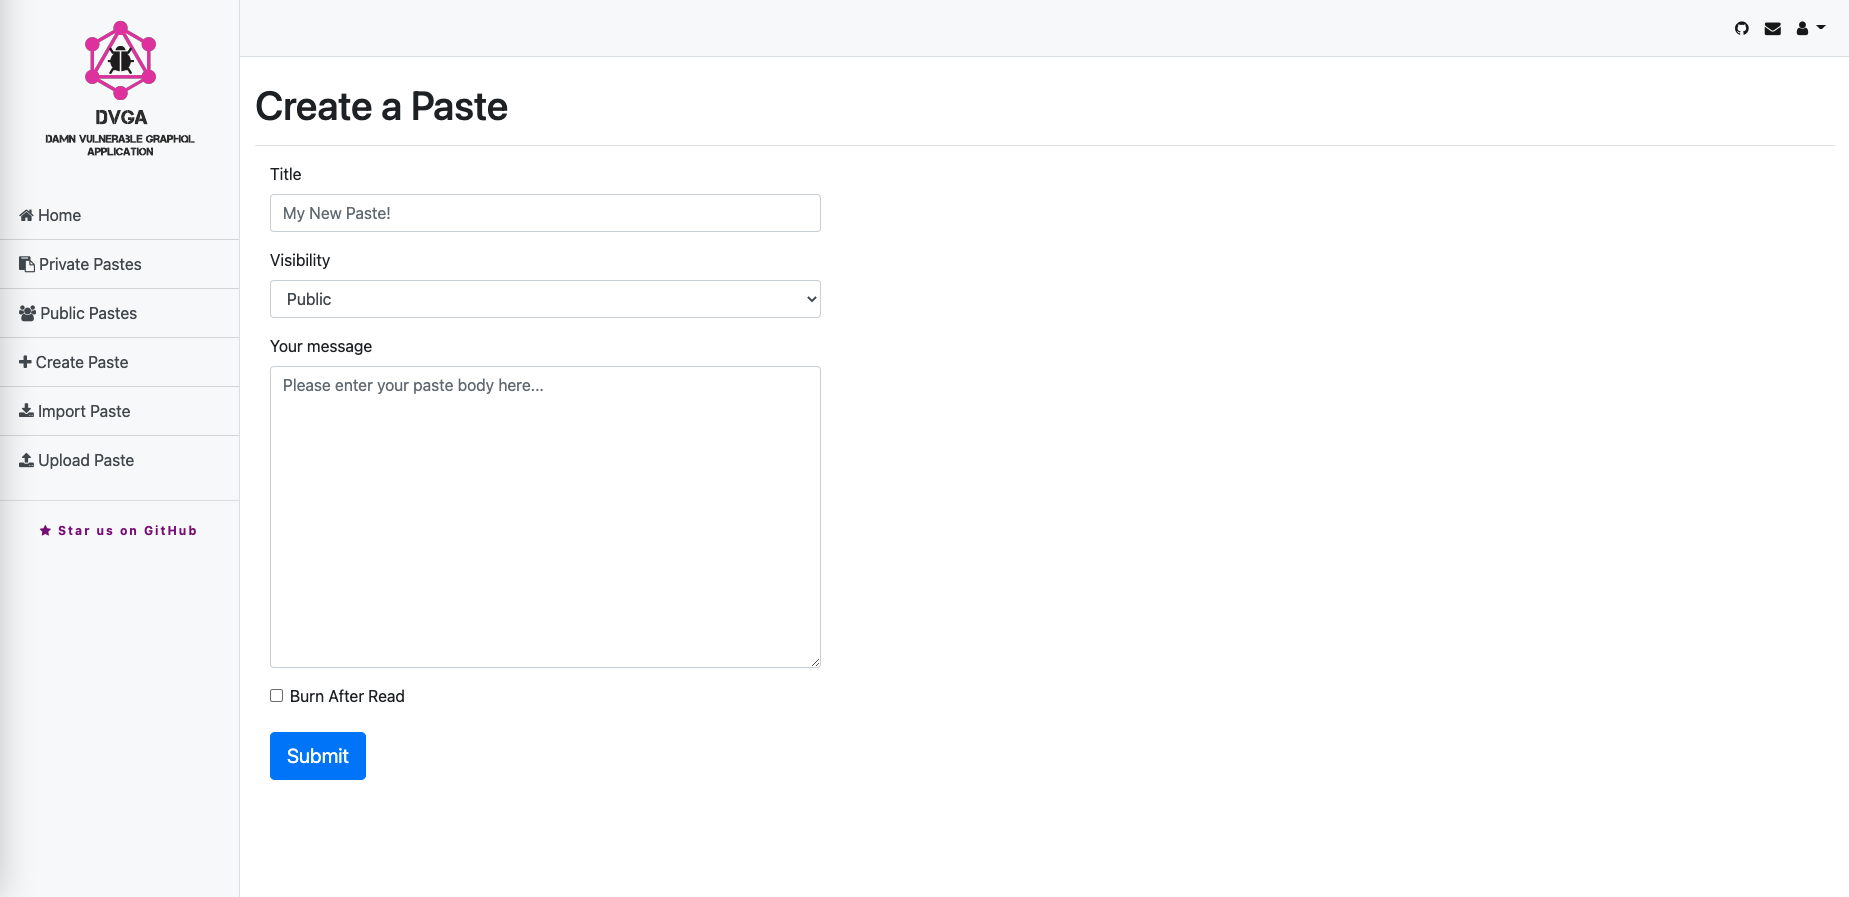 dolevf/damn-vulnerable-graphql-application
Damn Vulnerable GraphQL Application is an intentionally vulnerable GraphQL service implementation designed for learning about and practising GraphQL…
 infobyte/faraday_burp
Burp Extension for collaboration in Faraday
 mindpatch/simple-maven
Deliberately vulnerable C# API application for practicing web application exploitation and security testing. Includes Docker setup and documentation…
 havoc10-sw/detect_polyfill_cve-2024-38537-
Here's a Python script that checks if the polyfill.io domain is present in the Content Security Policy (CSP) header of a given web application.