
HuntCyberArk
 logisek/huntcyberark
CyberArk Security Audit
vulnerability-scannersapi-security-testingconfiguration-auditing+7
238 months ago
logisek/huntcyberarkCyberArk Security Audit
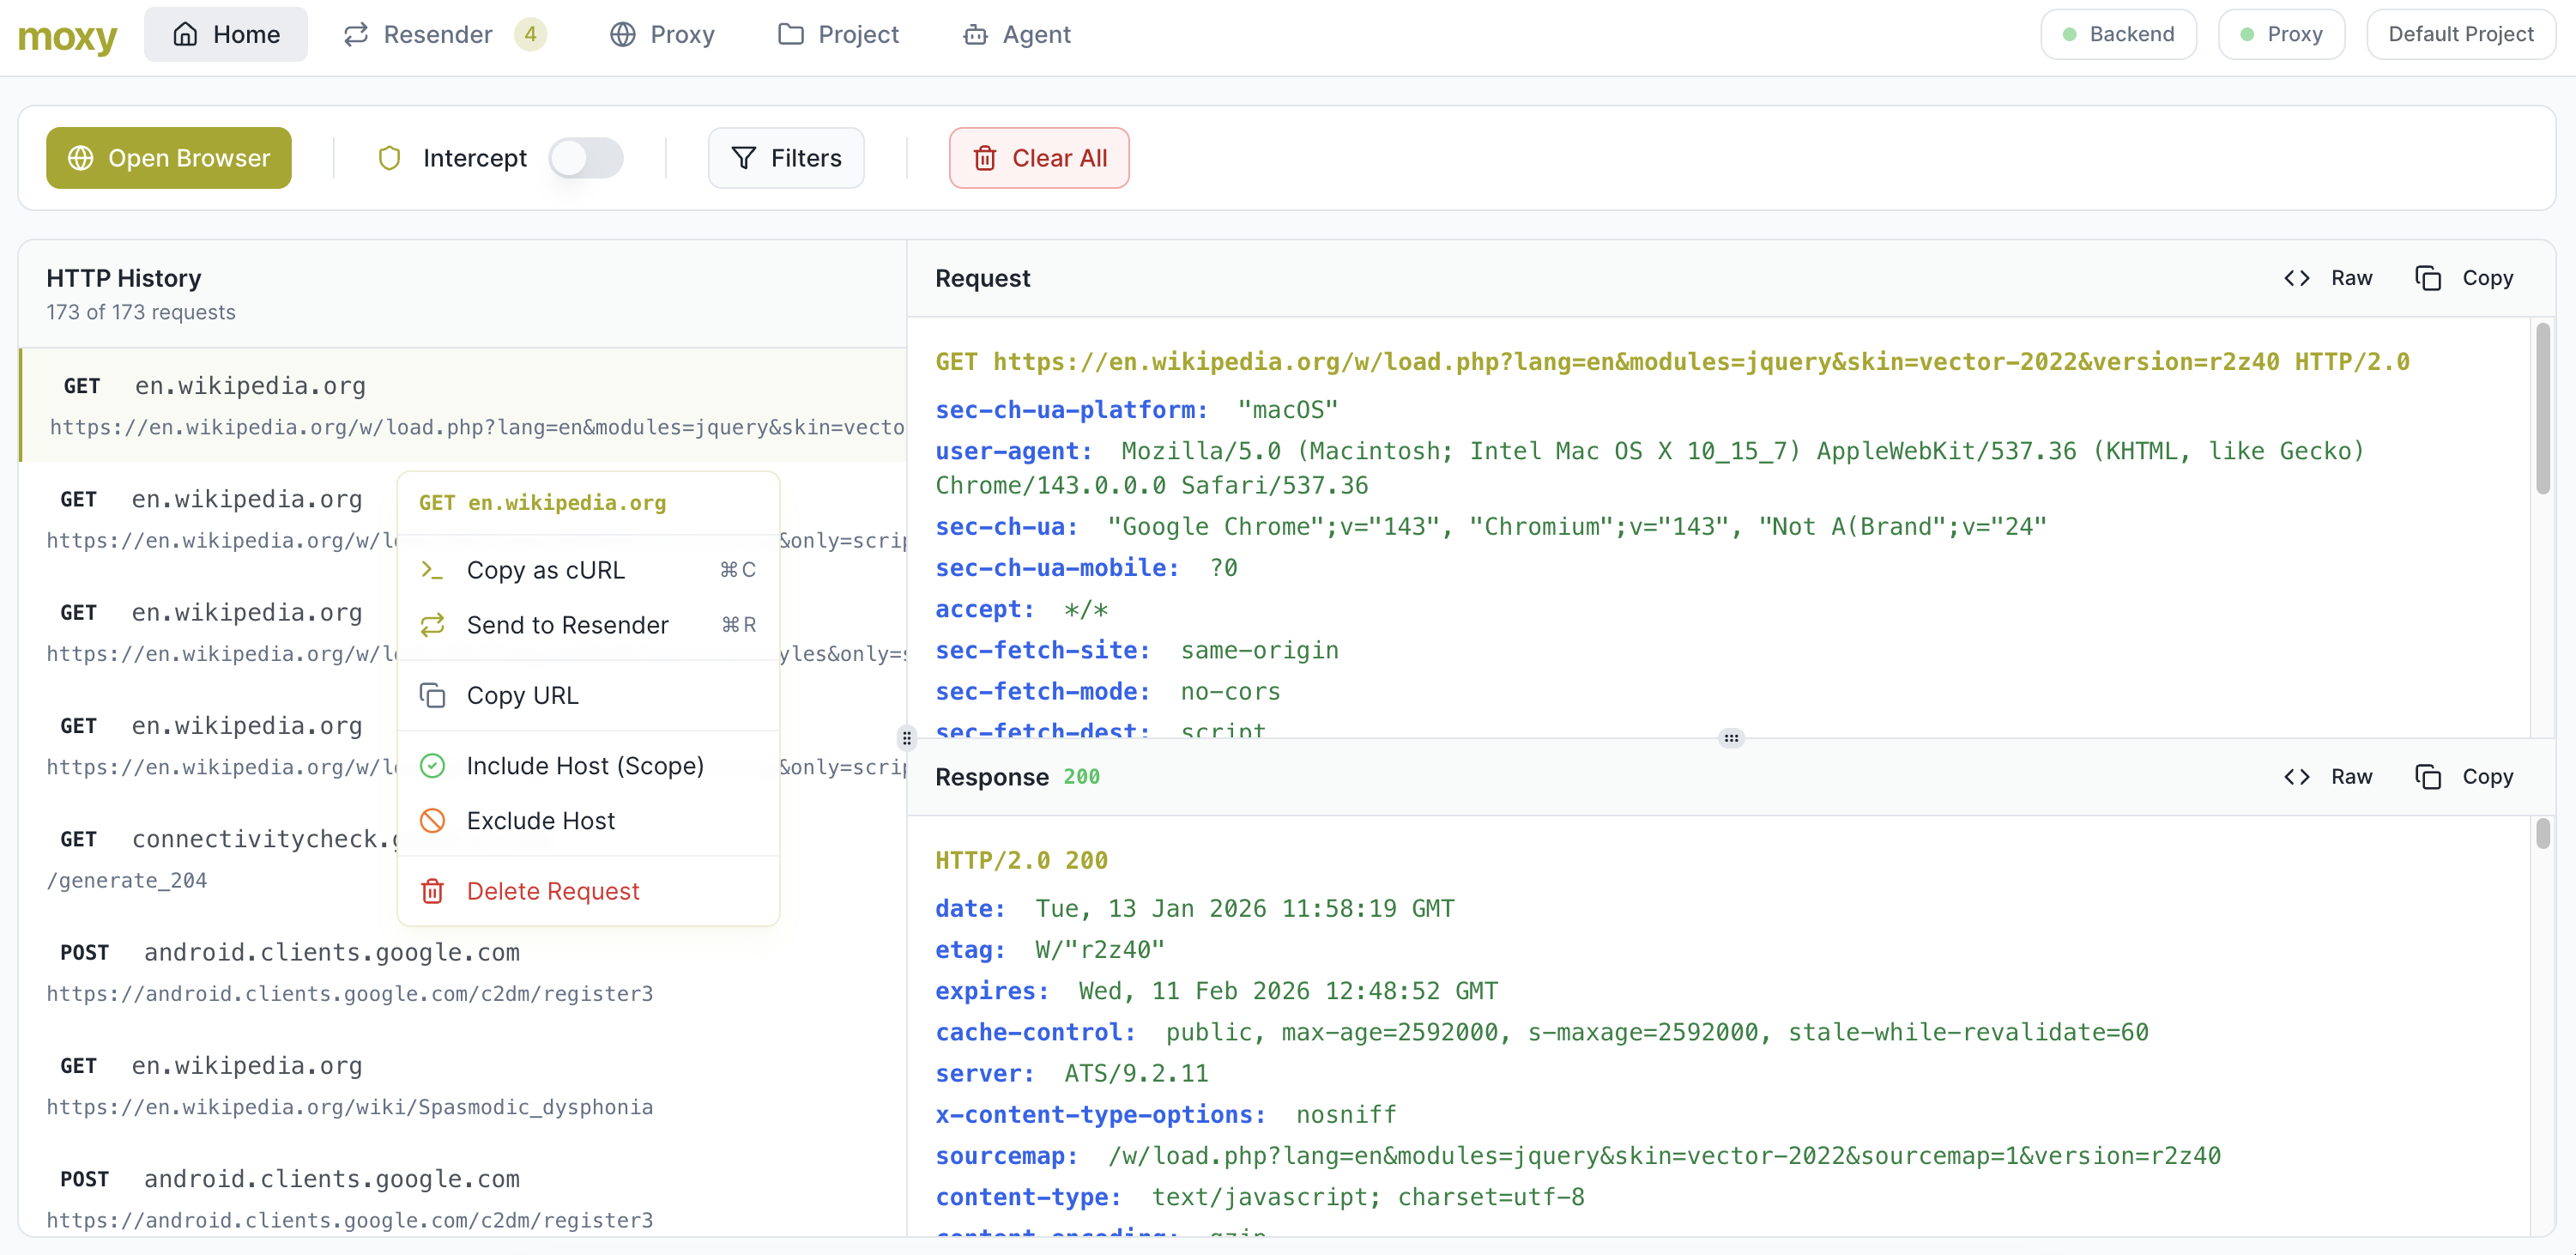 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
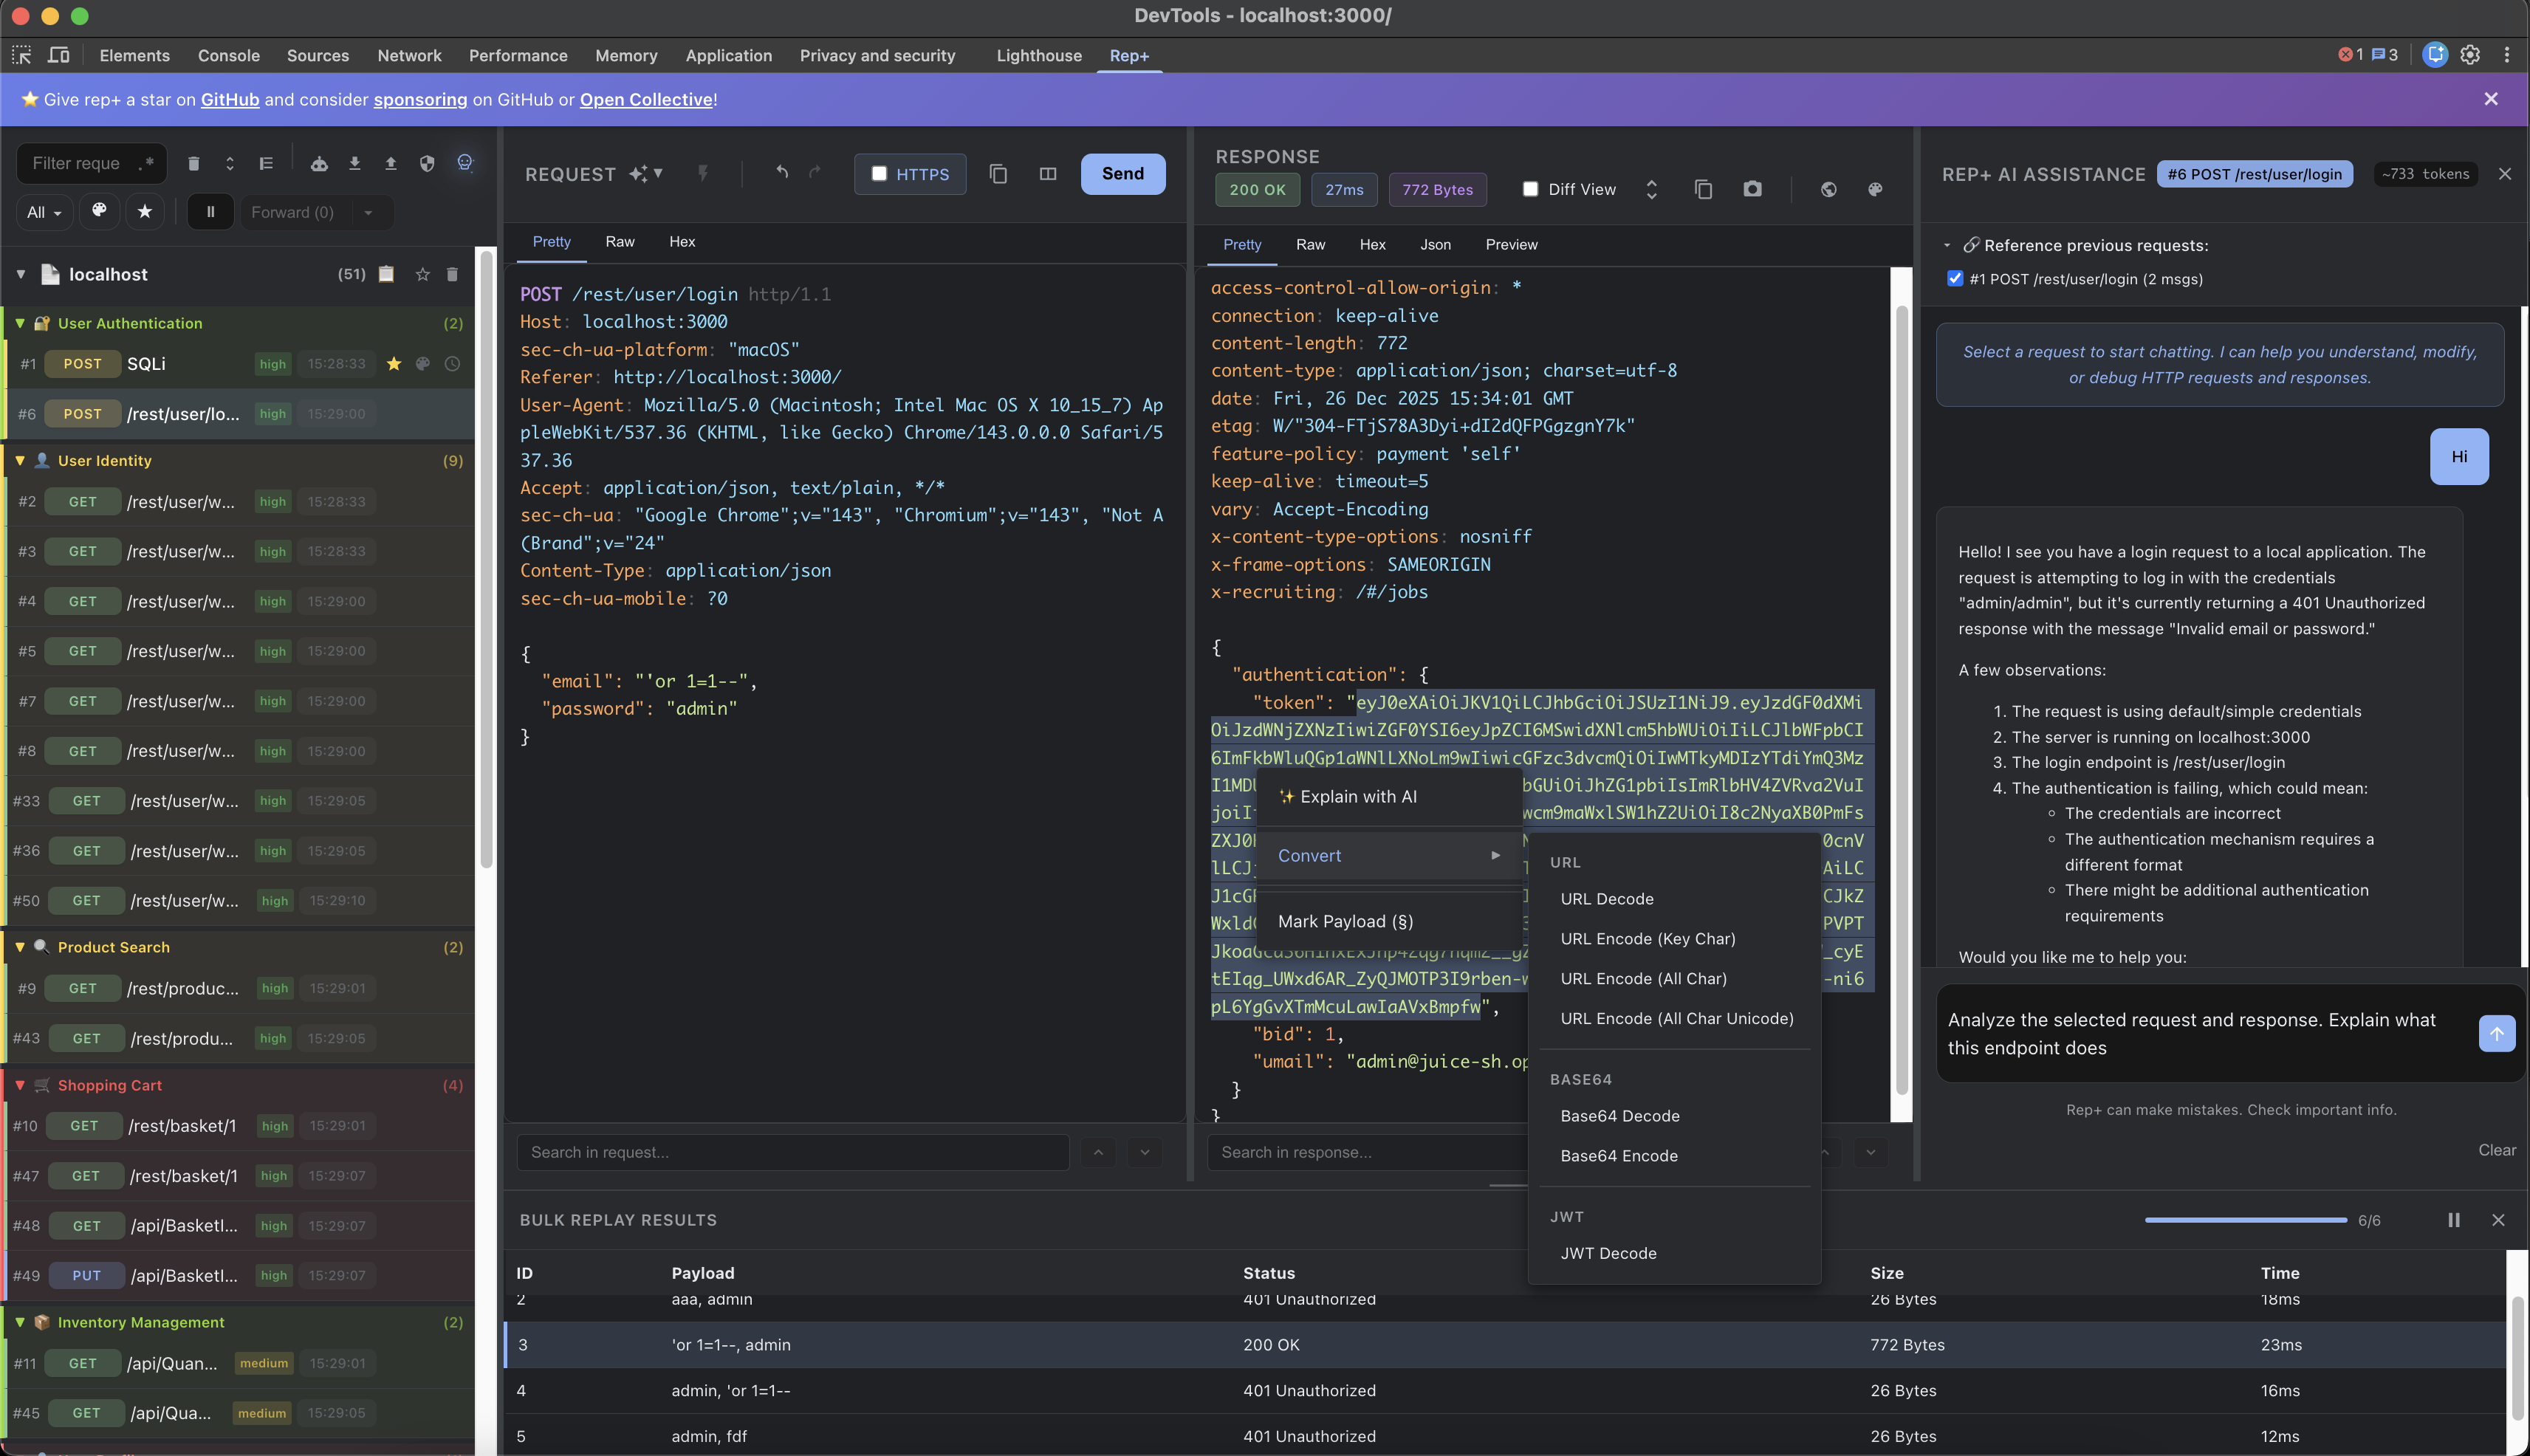 repplus/rep-chrome
rep+ — Burp-style HTTP Repeater for Chrome DevTools with built‑in AI to explain requests and suggest attacks
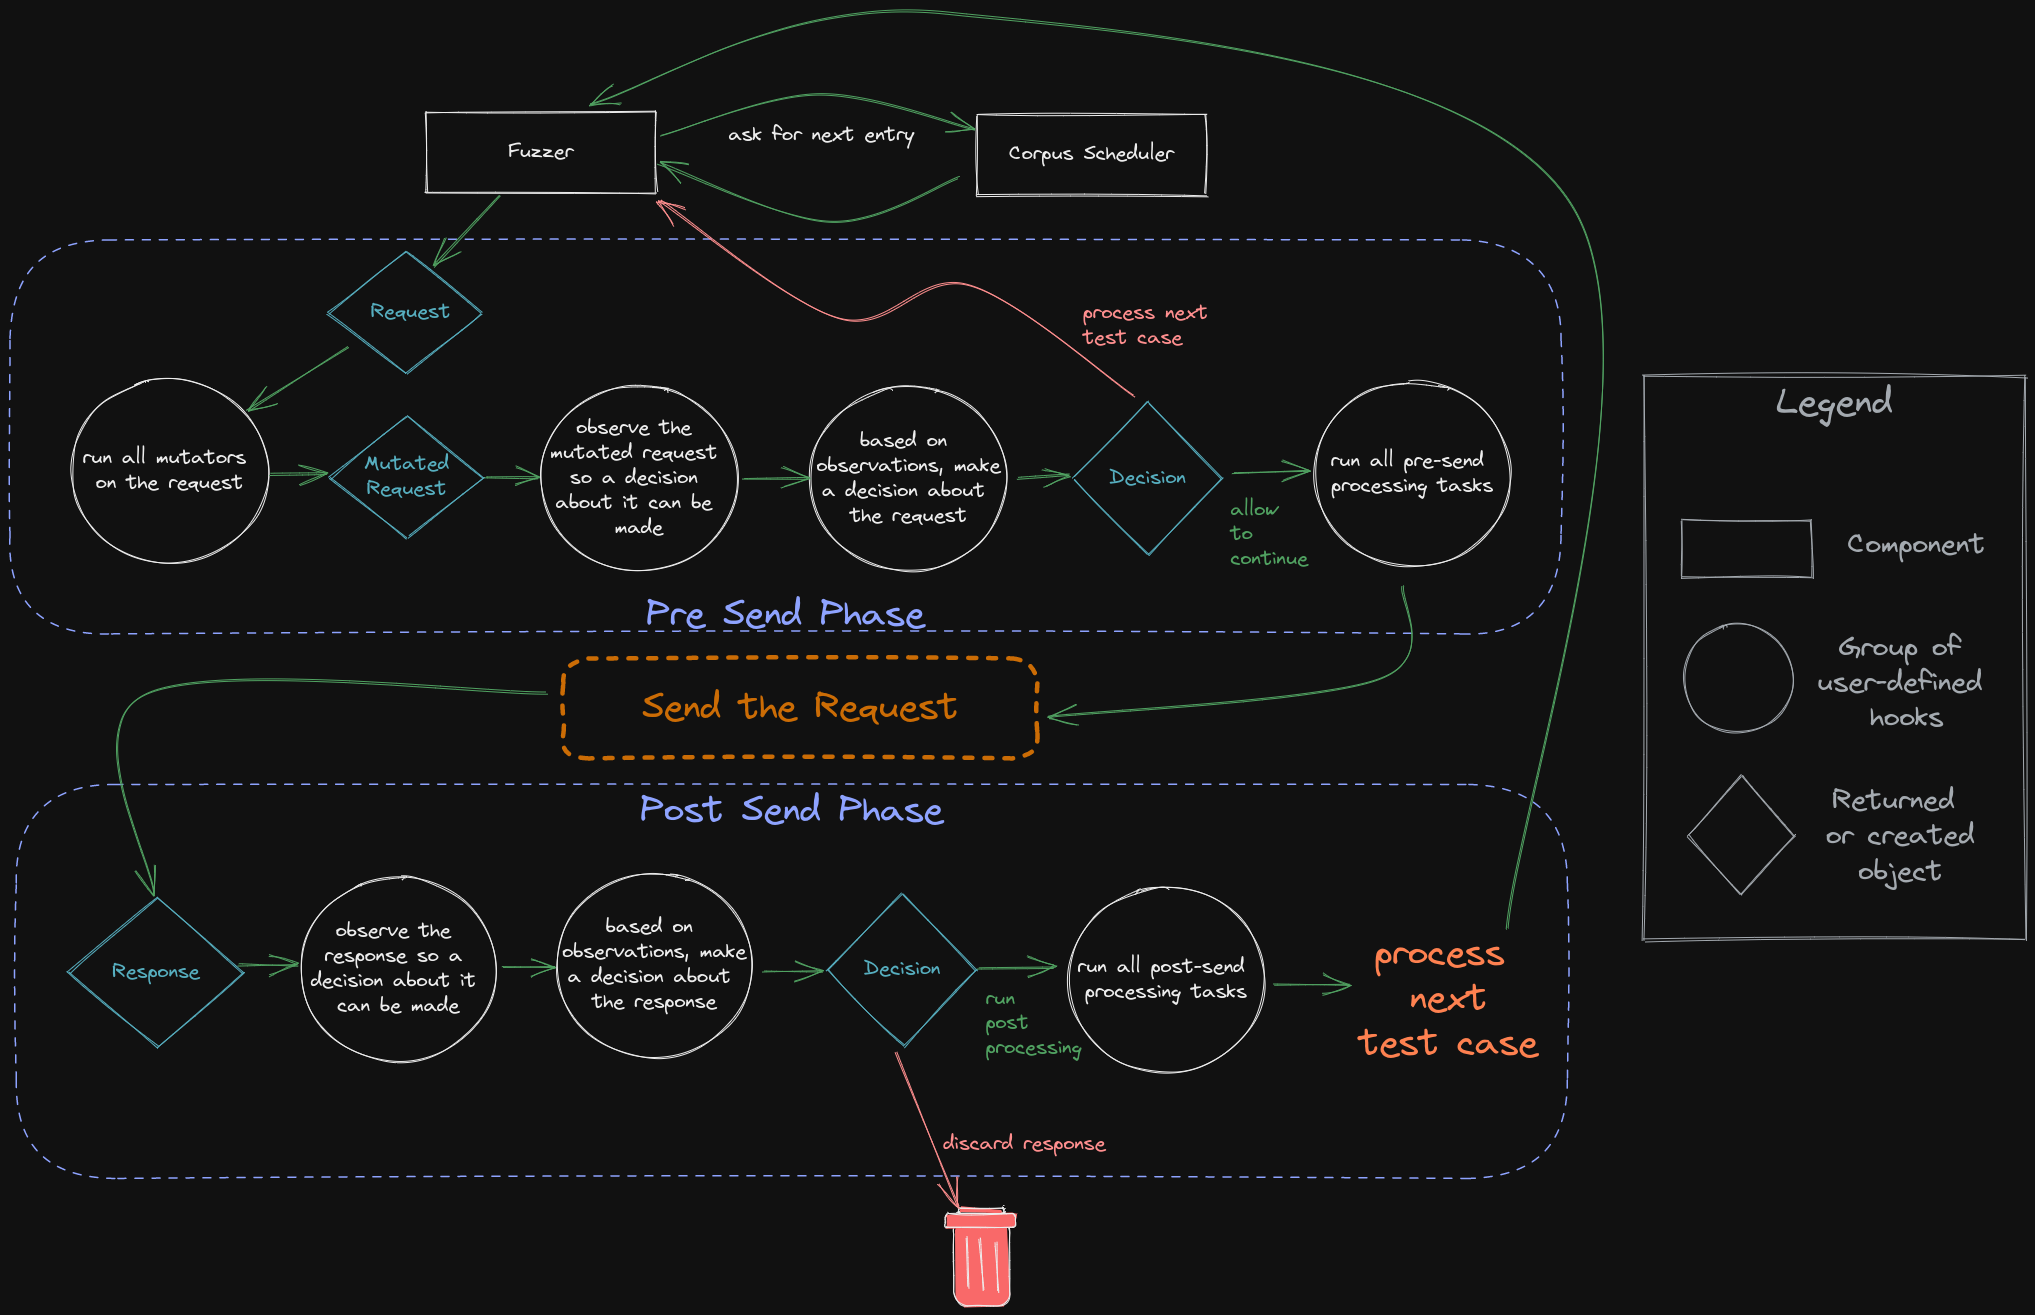 epi052/feroxfuzz
Build structure-aware black-box HTTP fuzzers in Rust with composable mutators, schedulers, observers, deciders, and processors for custom web and API…
 cropnet/ni8mare
Comprehensive vulnerability detection tool for n8n workflow automation instances. Detects the critical CVE-2026-21858 vulnerability (CVSS 10.0)…
 torxx666/propox
High-performance Rust HTTP/HTTPS proxy with active defense: rate limiting, reputation-based access, WAF (anti-bot, anti-injection, path protection),…
 theronielanddaronpodcastshow/svja
The Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…
 wi3memake/react2shell-scanner
Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…
 d0rb/packetpirate
A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.
 zilbonn/owasp-wstg-rag
OWASP Web Security Testing Guide RAG system with ChromaDB, MCP for Claude Code
 d0ge/xsw
XML Signature Wrapping Burp Suite Extensions
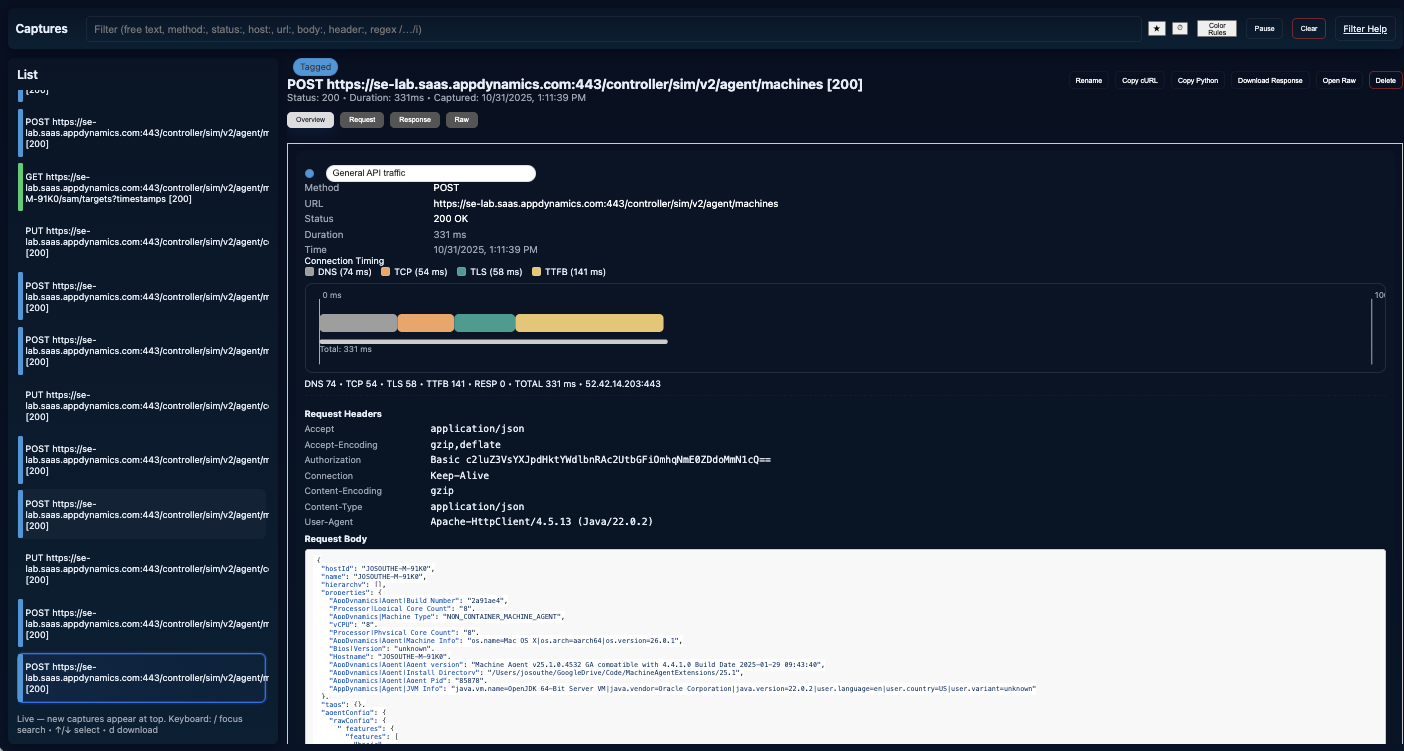 jbsouthe/http-breakout-proxy
HTTP Proxy Analysis for reverse engineering protocol communication
 vertexcover-io/strot
API Scraper Agent for Web API's
 hackvertor/shadow-repeater
Burp Suite Repeater extension that automatically mutates payloads and analyzes responses to uncover path traversal, SQL injection, XSS, and other web…
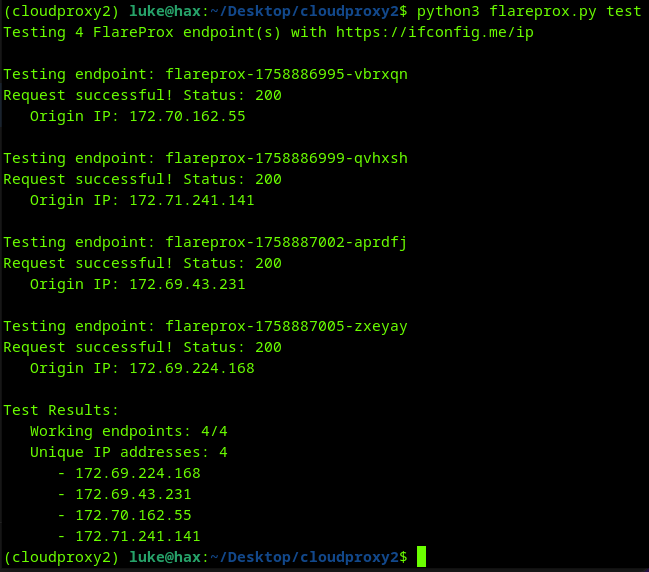 mrturvey/flareprox
Use Cloudflare to create HTTP pass-through proxies for unique IP rotation, similar to fireprox
 dolevf/graphql-cop
Lightweight Python utility for automated security auditing of GraphQL APIs. Detects misconfigurations, information leaks, and denial-of-service…
 dipjyotimetia/hybridtestframework
End to End testing of Web, API, Cloud, Events and Security
 shoucheng3/perwendel__spark_cve-2018-9159_2_7_2_fixed
Lightweight Java 8 web framework for building REST APIs and web applications, with built-in routing, static file serving, and template engine support.