
vimana-framework
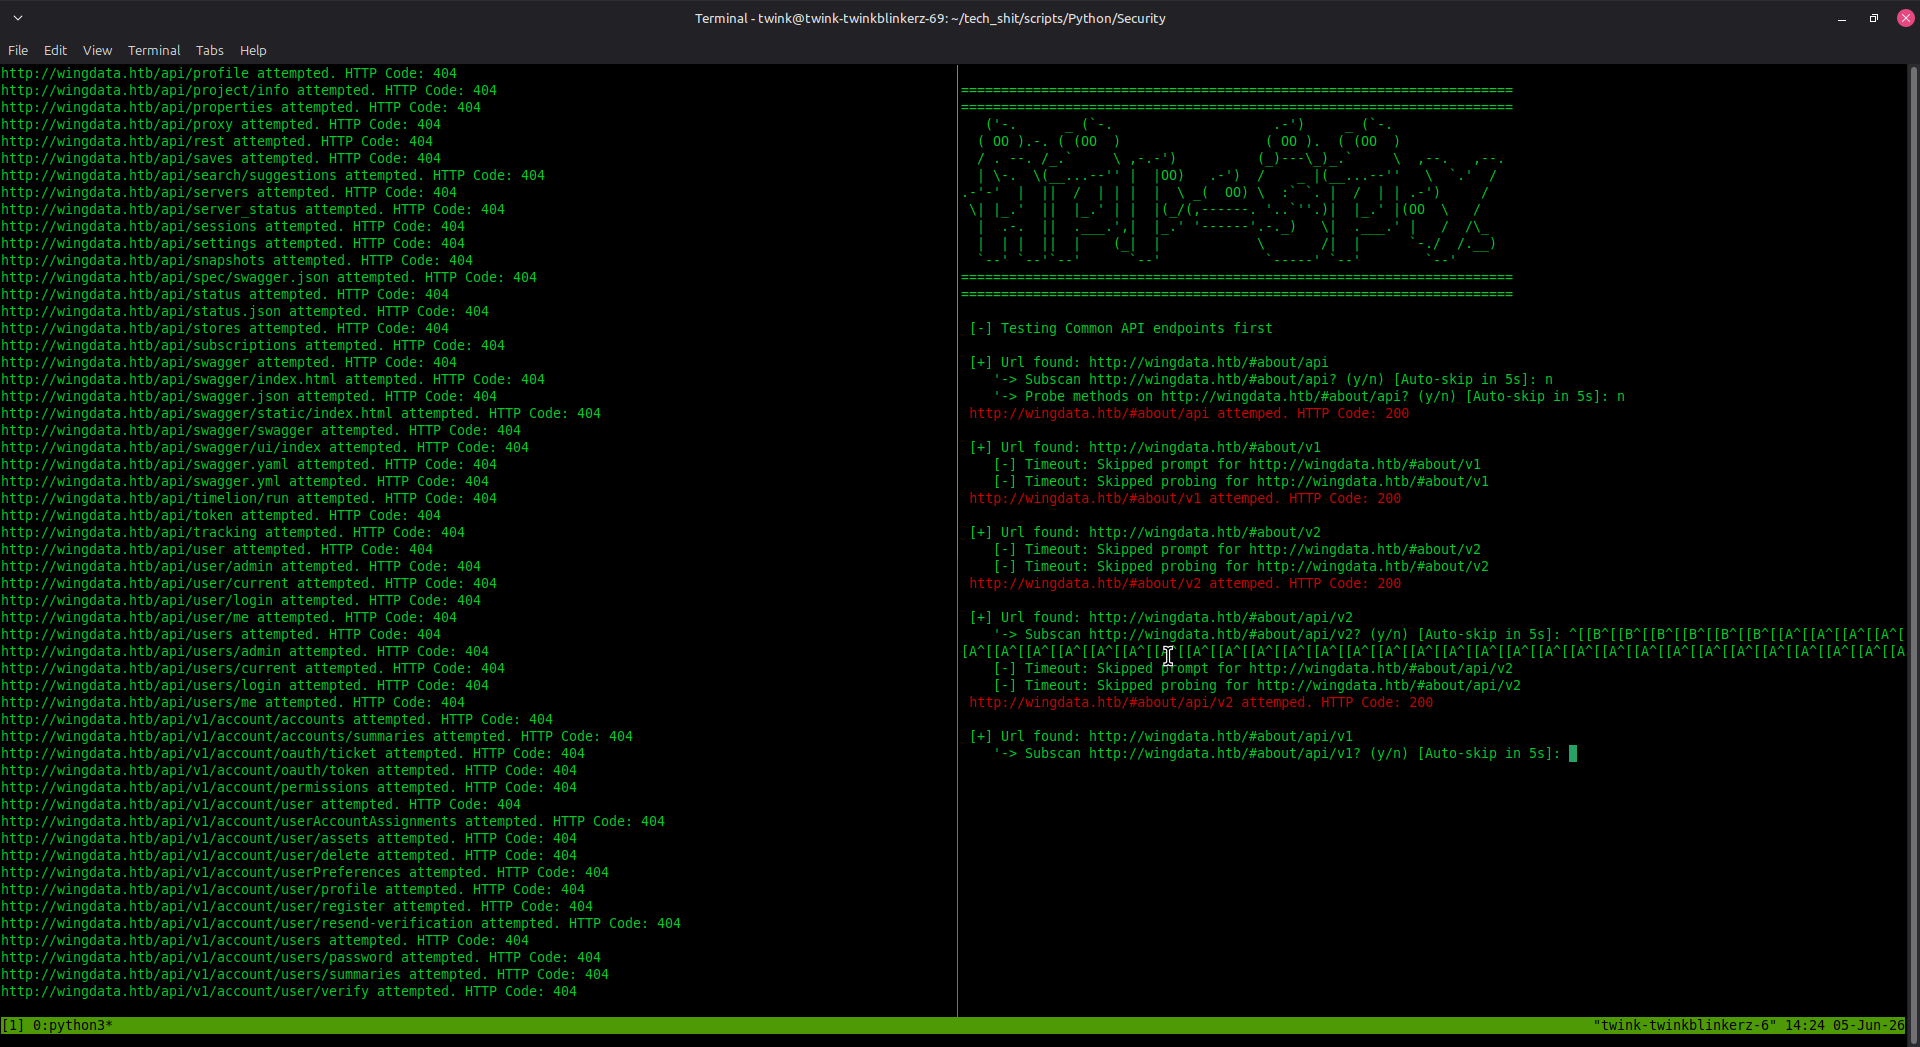
Vimana is a modular security framework for auditing Python APIs and Web applications. The plugin-based architecture enables security professionals to…

Vimana is a modular security framework for auditing Python APIs and Web applications. The plugin-based architecture enables security professionals to…

Reproducer for CVE-2026-48204: Apache Camel camel-mongodb-gridfs gridfs.* header injection overriding the GridFS operation (enumerate/read/delete…

Executable security regression testing for agentic applications and MCP-integrated systems.

Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, code injection, and known CVEs like…

The collaborative web app pentest suite

Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)

The one shot API attacker tool - finds the API url from the given root simulate the automated attacks

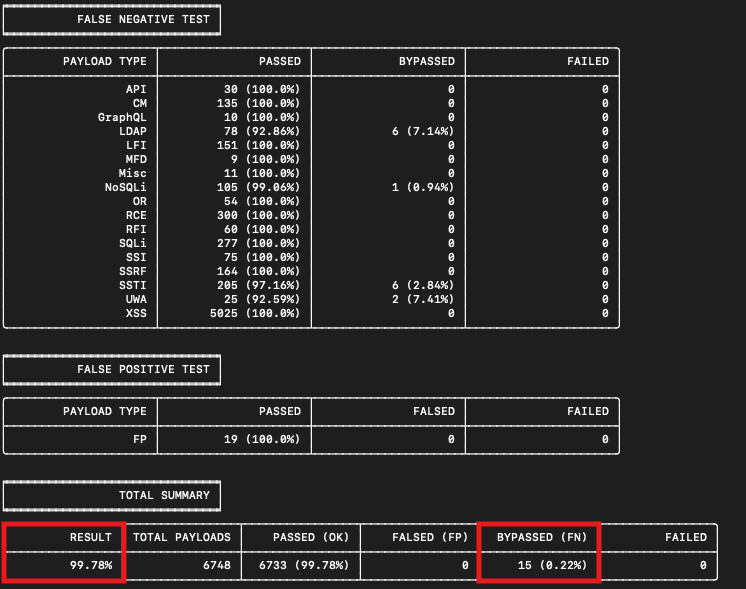
Automated WAF security testing tool that detects false positives and false negatives using 15+ payload categories including SQLi, XSS, RCE, and…

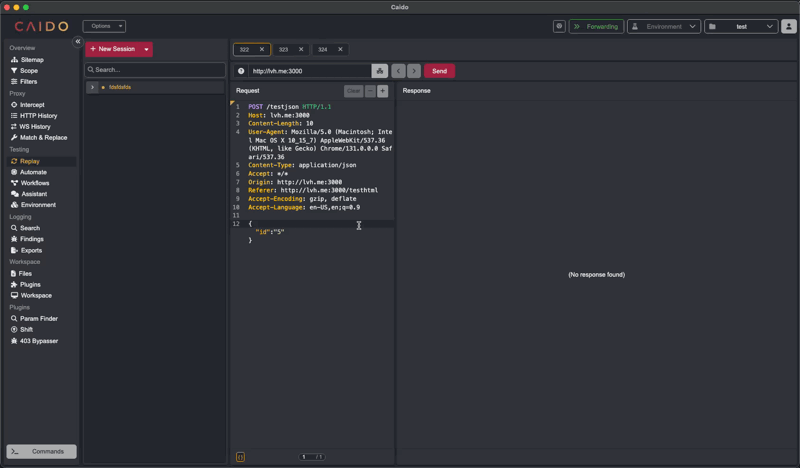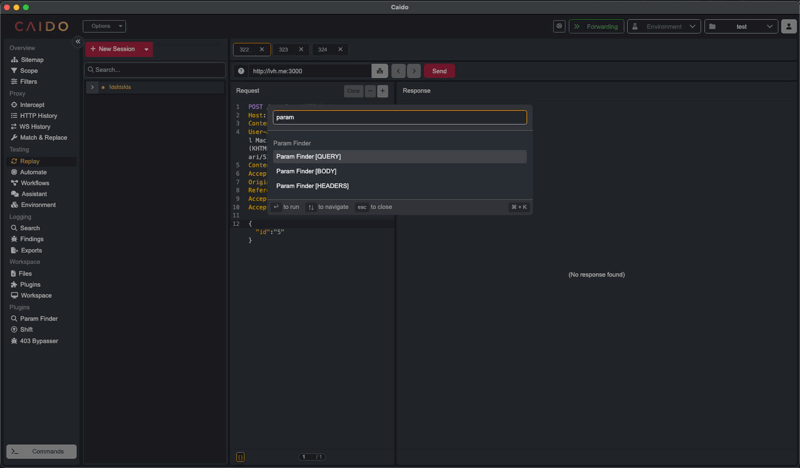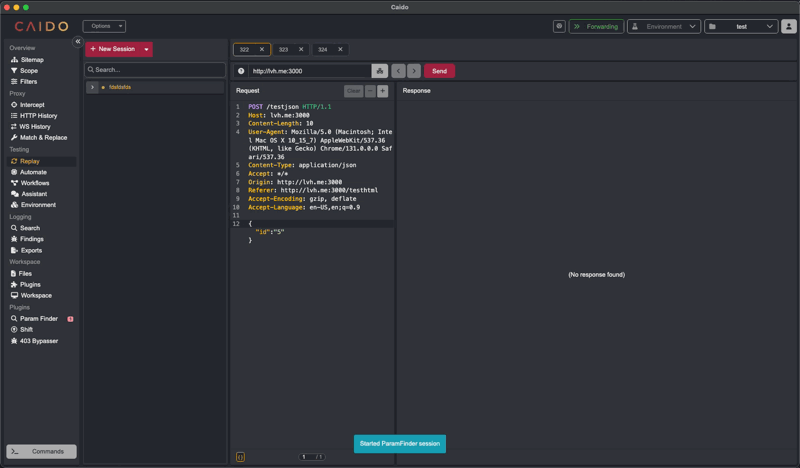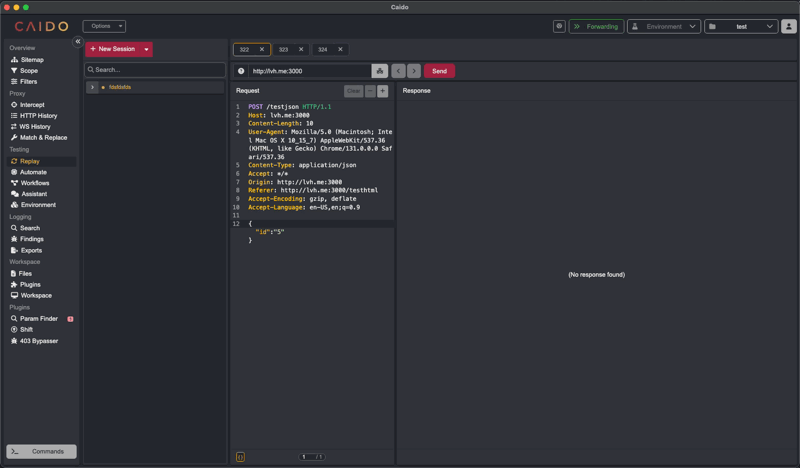
Discover hidden parameters in Caido

Validates Google Maps API keys against 21 endpoints, revealing exposed services with PoC URLs, proxy support, and quiet mode for focused auditing.

find sensitive data leaking from ServiceNow instances.

Sample Burp Suite extensions demonstrating the Montoya API, covering HTTP and proxy handlers, custom scan checks, Intruder payloads, WebSocket…

Keyless active-probe security auditor for Directus CMS. Proves public-role data exposure, user enumeration, unauthenticated version/schema leaks,…

Analyze HTTP requests to minimize risks of HTTP Desync attacks (precursor for HTTP request smuggling/splitting).

An API hooking framework for intercepting and monitoring Windows applications

AI-powered SAST scanner that finds auth bypass, IDOR, and logic bugs Semgrep/CodeQL miss. Free GitHub Action. Supports Python, JS/TS, Go, PHP, Ruby.

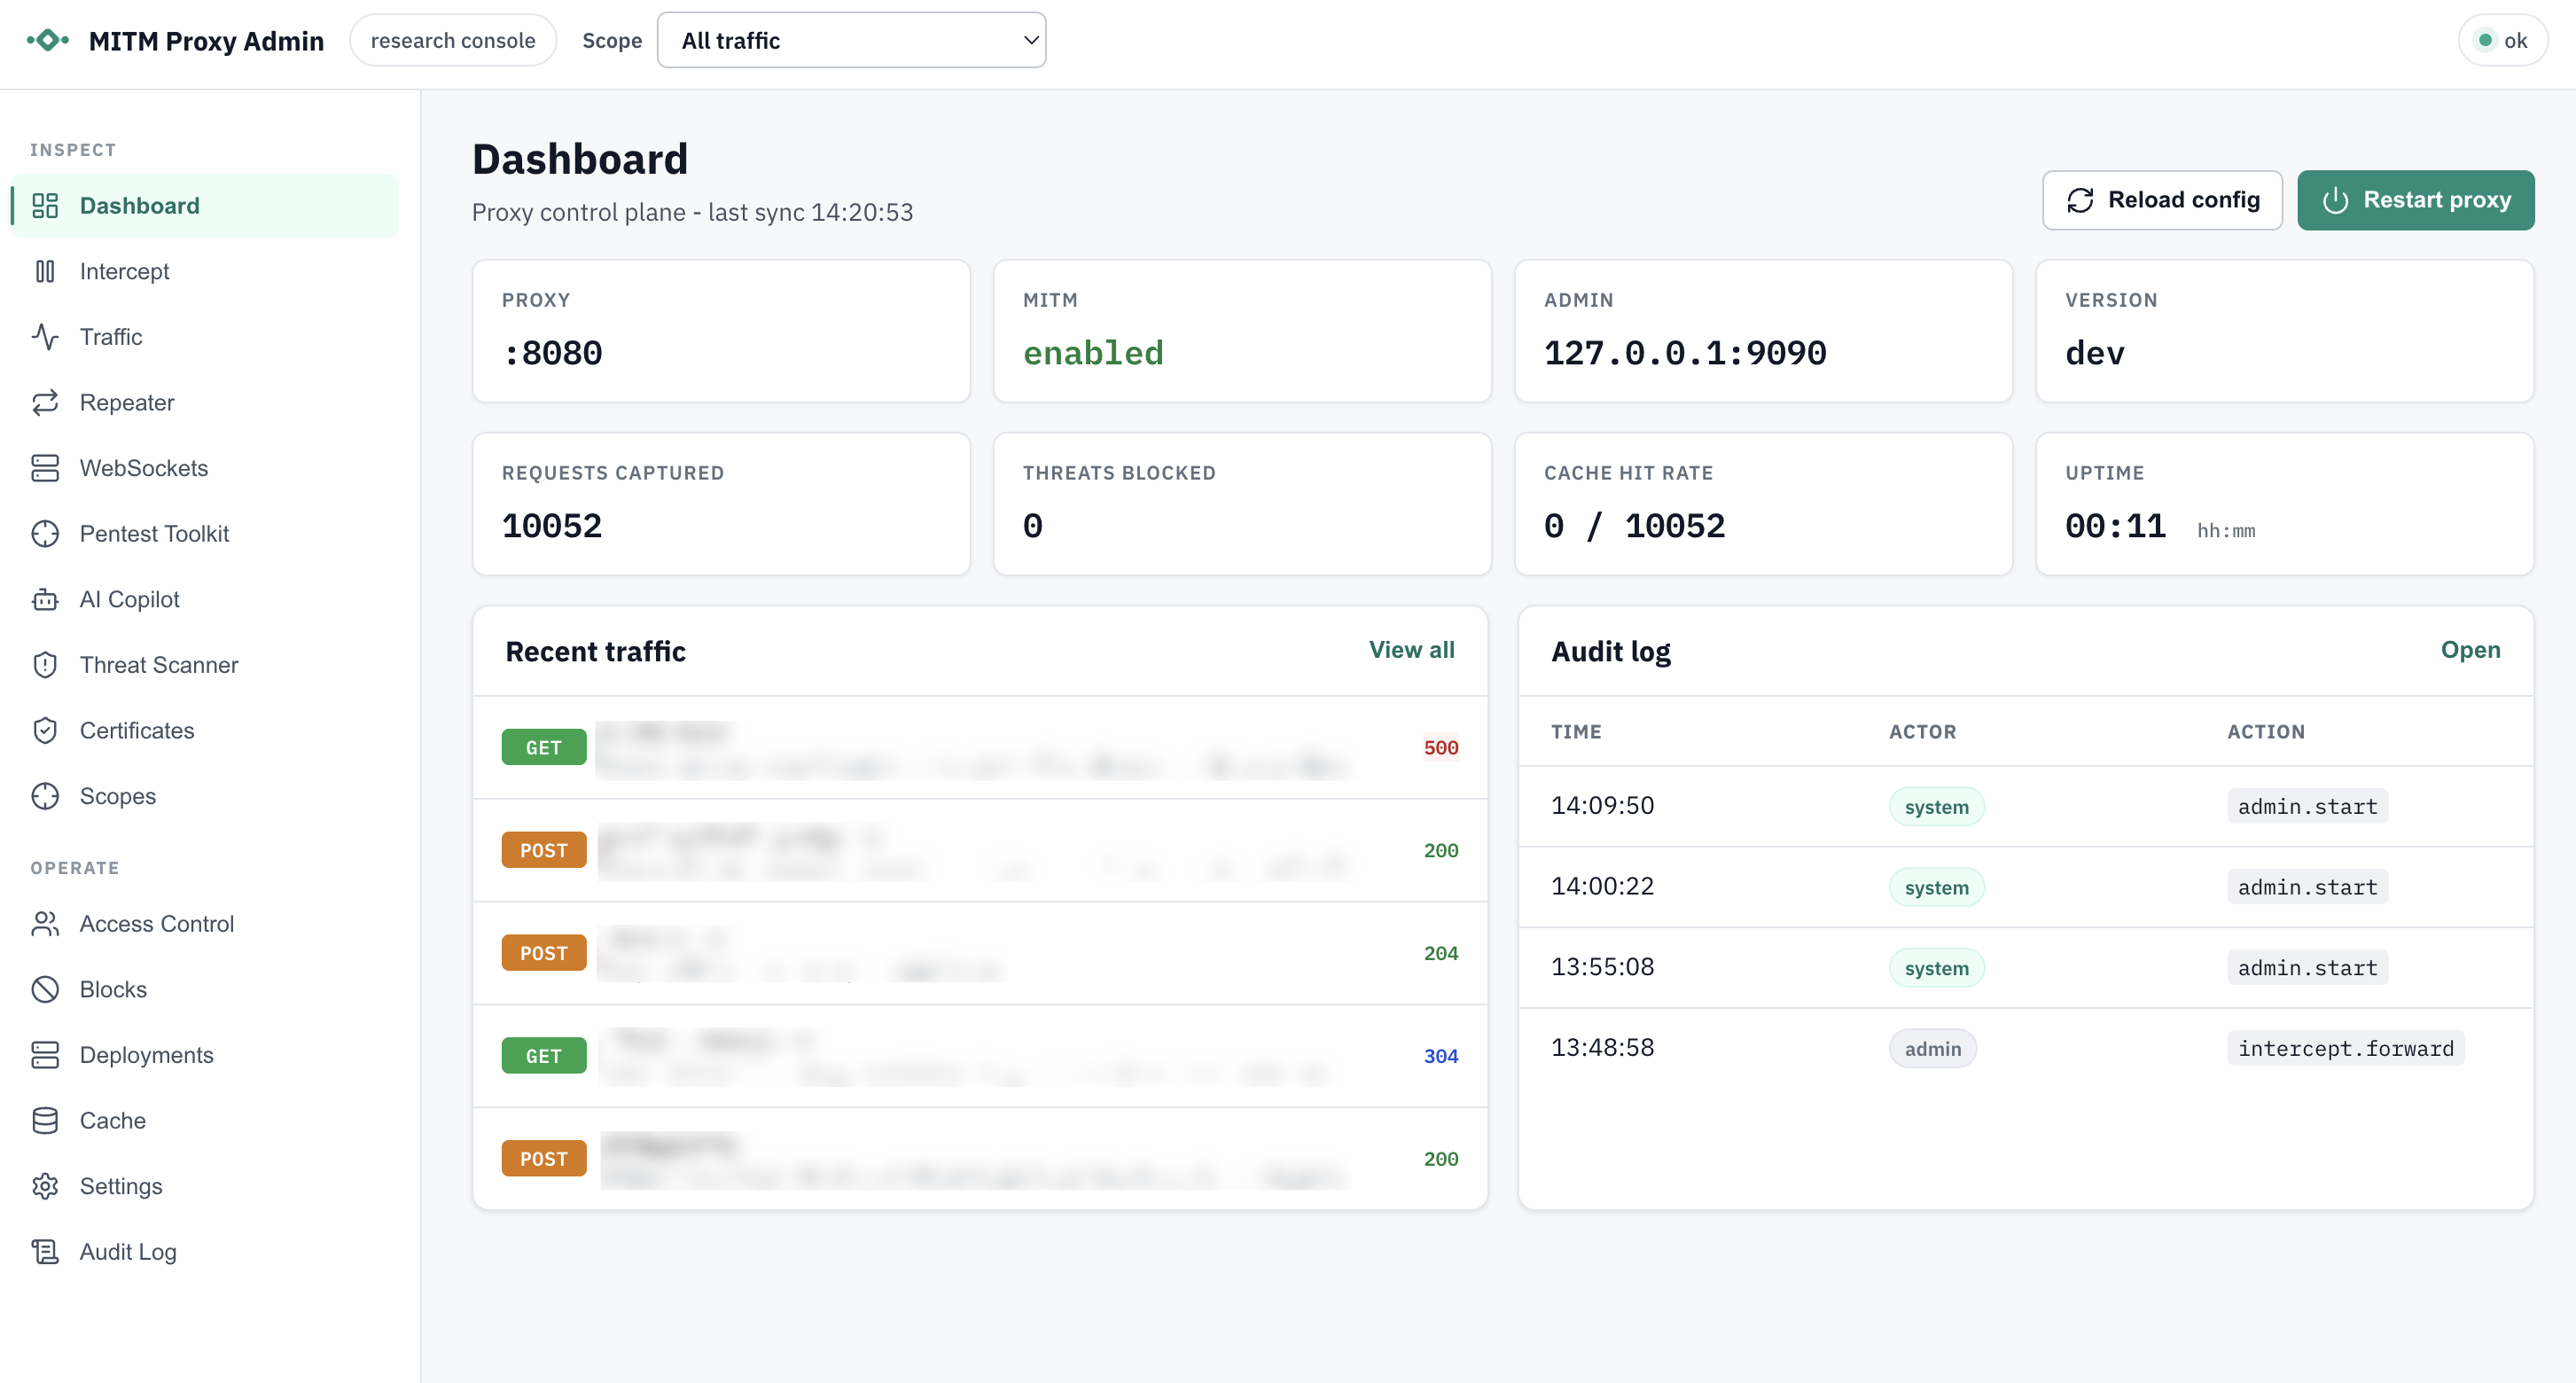
Go-based MITM HTTP/HTTPS proxy with HTTP/2 and HTTP/1.1 interception, local CA/per-host cert generation, CONNECT/WebSocket tunneling, disk caching,…

A powerful directory brute-force tool that's tailored for recursive/multiplex operations, API discovery and enumeration, JS file scraping, and lists…