
milvus-auth-audit
 qianlijaingshan/milvus-auth-audit
Milvus 认证安全检测脚本:CVE-2025-64513 (sourceid后门) / CVE-2026-26190 (/expr弱token) / 内部端口53100
api-security-testingauthentication-authorizationdatabase-security+4
qianlijaingshan/milvus-auth-auditMilvus 认证安全检测脚本:CVE-2025-64513 (sourceid后门) / CVE-2026-26190 (/expr弱token) / 内部端口53100
 k3ystr0k3r/cve-2026-9198
PoC and detection guide for the critical unauthenticated RCE in IBM Langflow OSS, covering the auto_login token bypass and unsafe /validate/code…
 traceforce/mcp-xray
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…
 filipegaudard/cve-2026-30944-poc
Python proof-of-concept for CVE-2026-30944, exploiting a BOLA vulnerability in StudioCMS to escalate privileges via insecure API token generation.
 ridhinva/langflow-cors-scanner
Scanner: CVE-2025-34291 Langflow Origin Validation Error / CORS Misconfiguration — Python checker (CISA KEV)
 portswigger/ator
Burp Suite plugin for automated token extraction and replacement in HTTP requests, supporting JSON, XML, cookies, and URL parameters to streamline…
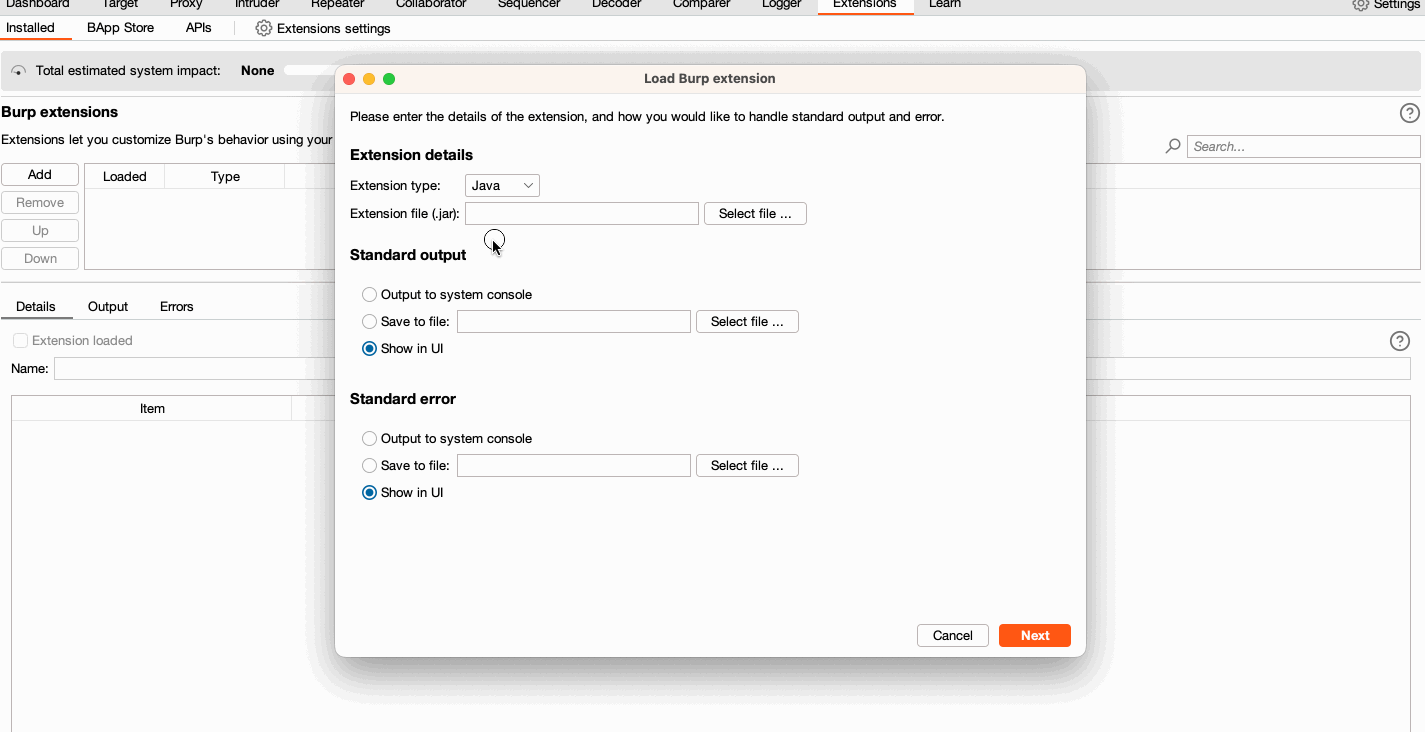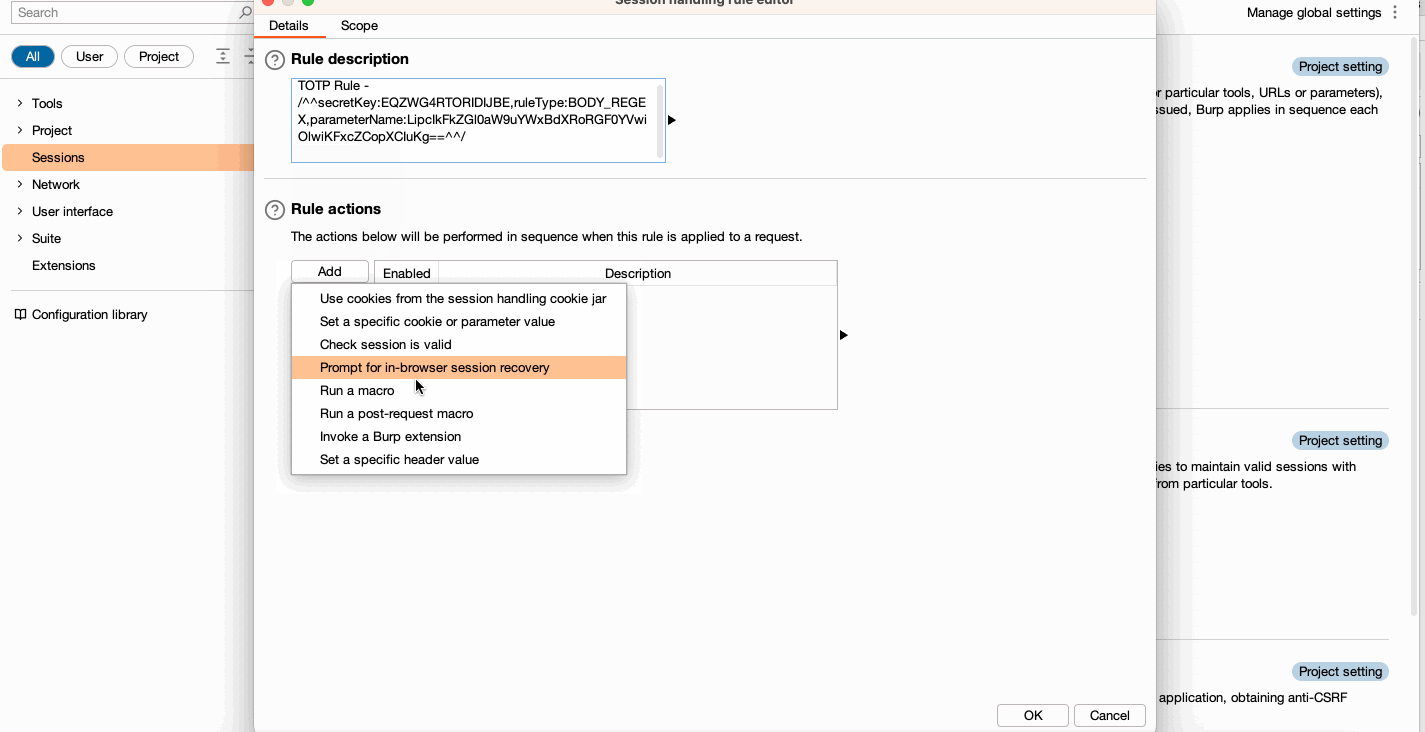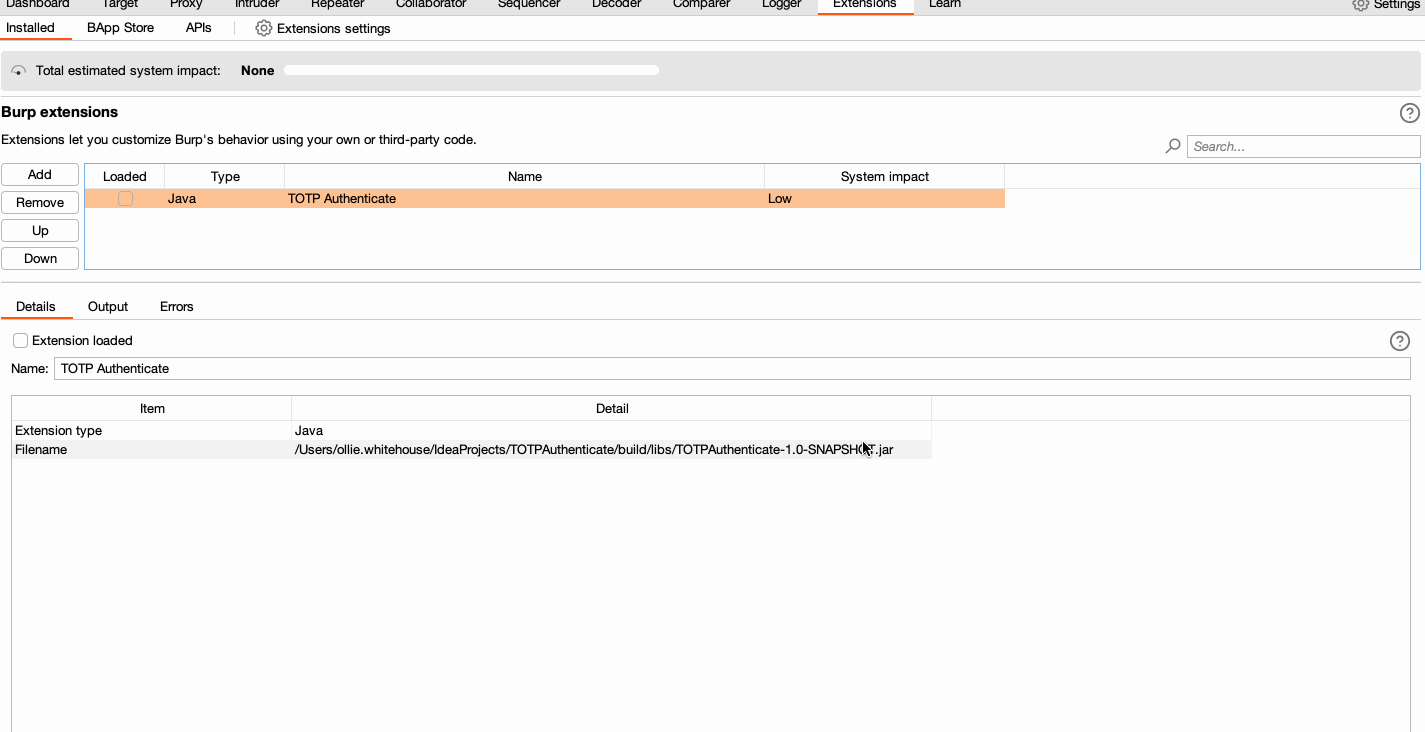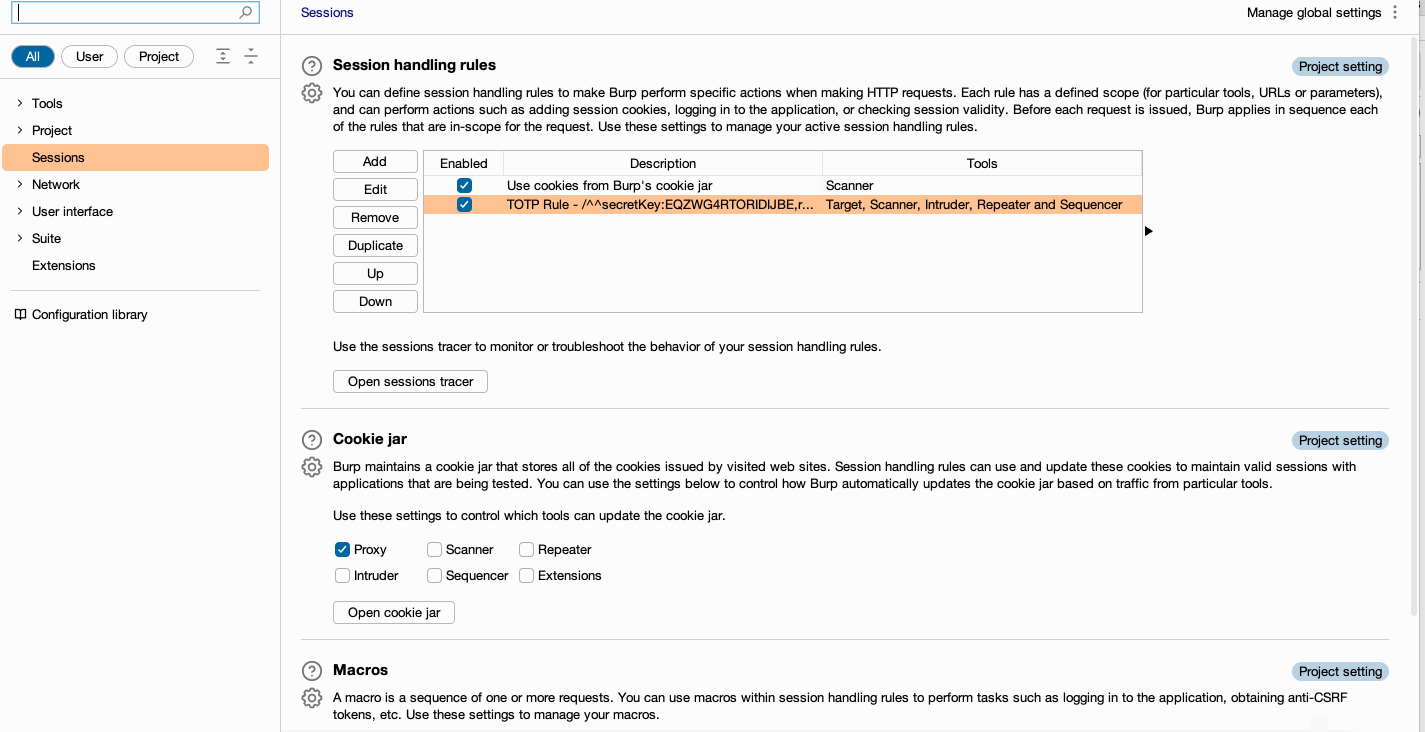 hannah-portswigger/totpauthenticate
This extension, for Burp Suite Enterprise Edition, utilizes session handling rules to provide a TOTP token to outgoing requests.
 kavishkagihan/cve-2022-24112-poc
Apache APISIX 2.12.1 Remote Code Execution by IP restriction bypass and using default admin AIP token
 7megaumka7/foskiller
FOSSBilling CVE-2026-53647 & CVE-2026-53646 PoC — Unauthenticated API key disclosure & password reset token reuse
 fuyuooumi1027/cve-2023-45857-demo
Interactive demo for CVE-2023-45857 (axios XSRF token bypass). Step-by-step guide to reproduce the vulnerability in a controlled dev container…