
authz0
 hahwul/authz0
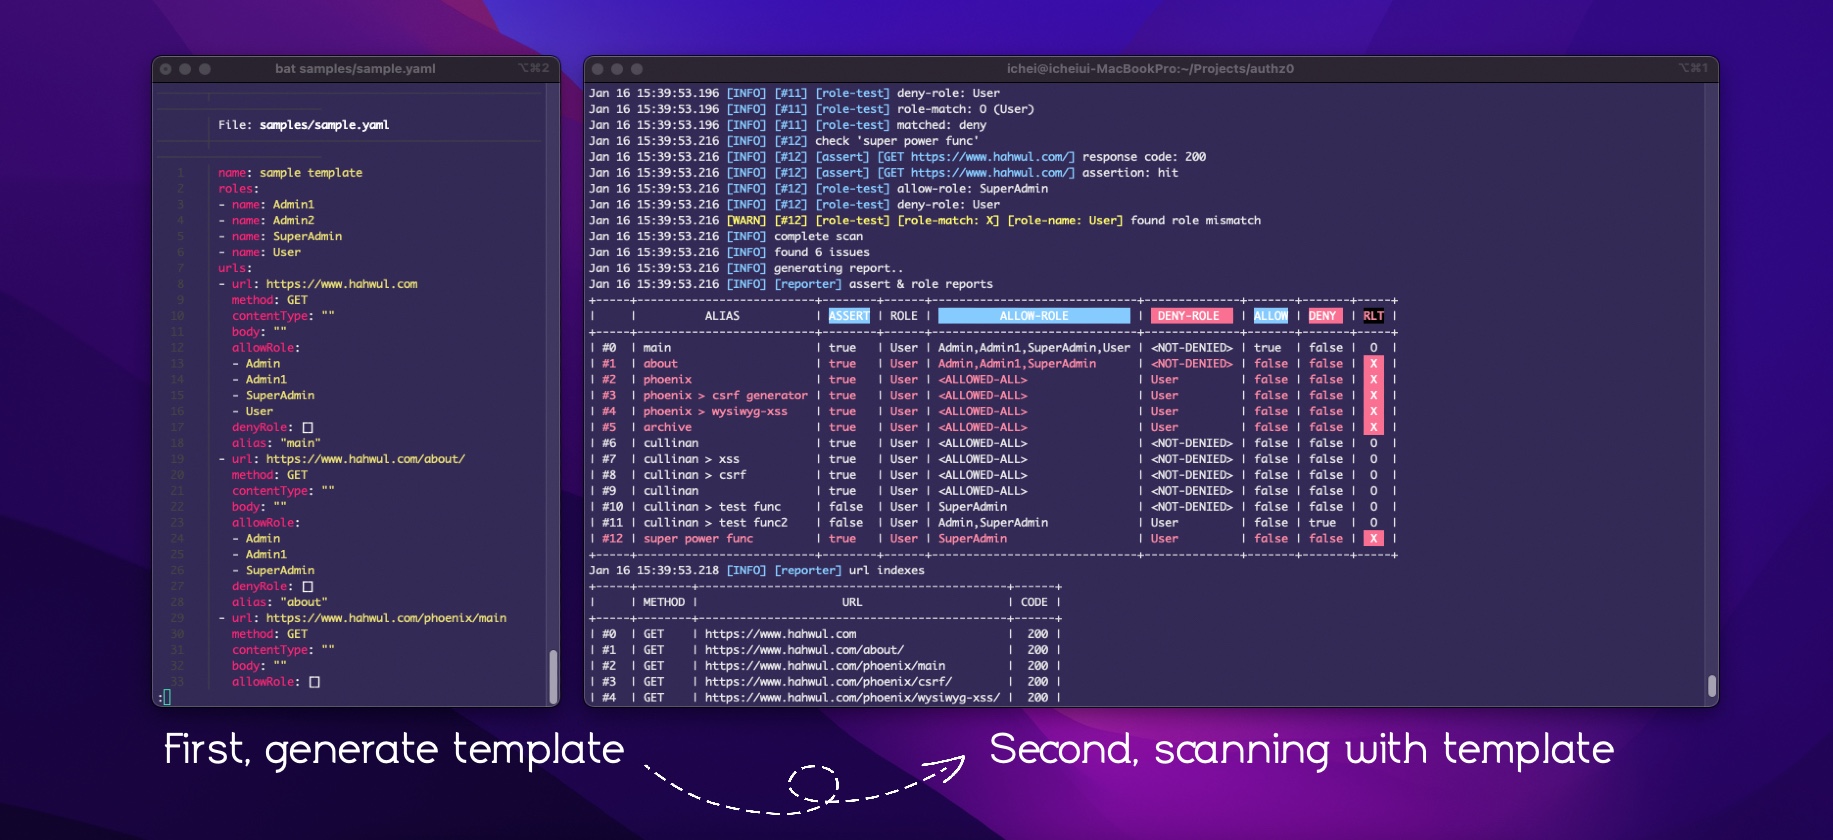
Automated authorization testing tool that detects unauthorized access by scanning URLs with role-based credentials using YAML templates.
api-security-testingvulnerability-scannersweb-security
hahwul/authz0Automated authorization testing tool that detects unauthorized access by scanning URLs with role-based credentials using YAML templates.
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 bishopfox/cve-2026-35616-check
Non-destructive scanner for CVE-2026-35616, a pre-authentication API bypass in FortiClient EMS. Detects vulnerability by comparing HTTP responses…
 nemesida-waf/waf-bypass
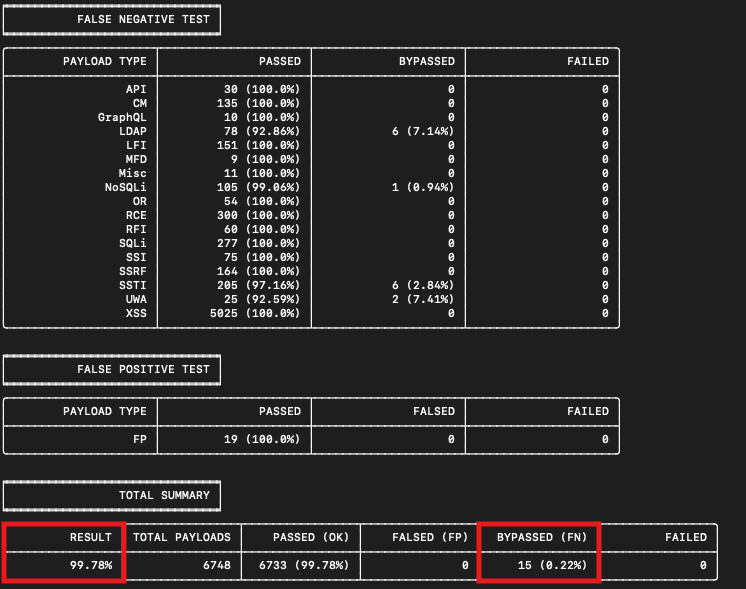
Automated WAF security testing tool that detects false positives and false negatives using 15+ payload categories including SQLi, XSS, RCE, and…
 dolevf/graphql-cop
Lightweight Python utility for automated security auditing of GraphQL APIs. Detects misconfigurations, information leaks, and denial-of-service…
 traceforce/mcp-xray
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…
 hahwul/smugglex
Rust-powered HTTP Request Smuggling Scanner.
 mannansainicyber/url_checker
Hybrid ML and heuristic-based URL phishing detector with real-time analysis, explainable confidence scores, and REST API for programmatic security…
 renzi25031469/cve-2026-19478
Detects CVE-2026-19478 in GitLab CE/EE with a non-destructive Nuclei template that triggers the GraphQL fallback-field method invocation via touch…
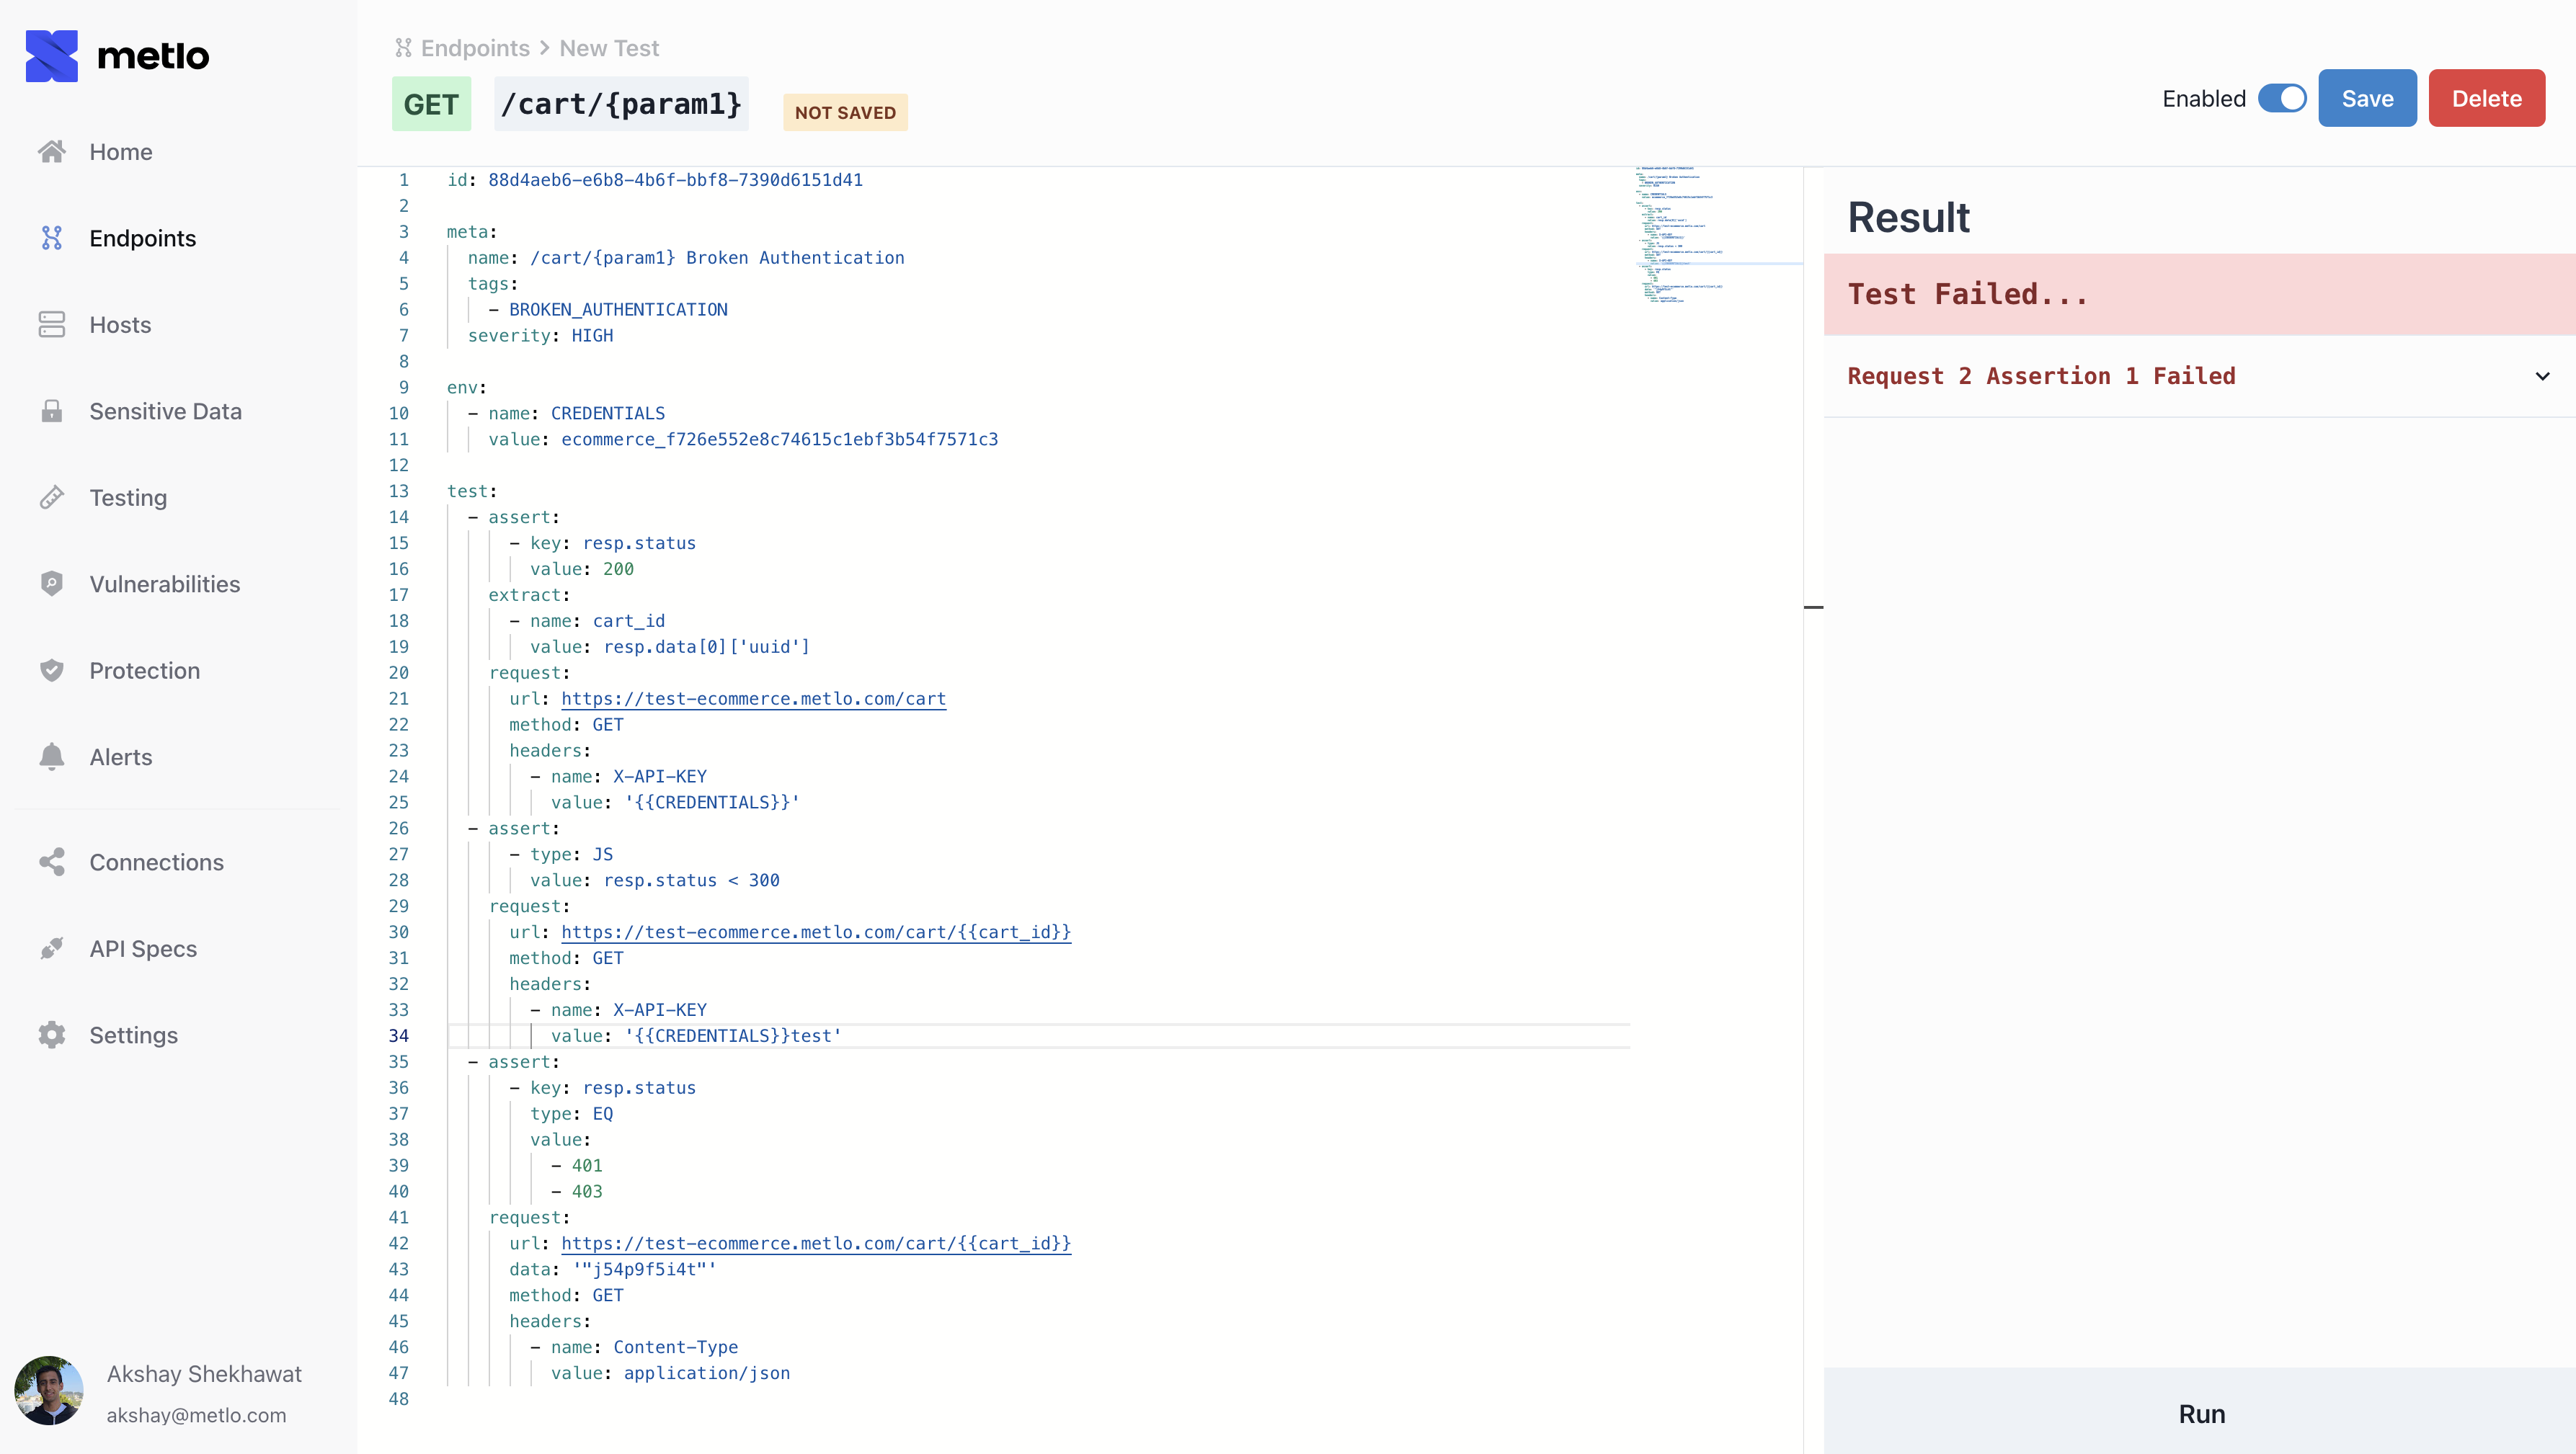 metlo-labs/metlo
Metlo is an open-source API security platform.
 cropnet/ni8mare
Comprehensive vulnerability detection tool for n8n workflow automation instances. Detects the critical CVE-2026-21858 vulnerability (CVSS 10.0)…
 ridhinva/litellm-sqli-scanner
Scanner: CVE-2026-42208 LiteLLM SQL Injection — Python scanner for BerriAI LiteLLM proxy instances
 zavisco/cve-2026-64849.yaml
Detects unauthenticated MLflow webhook SSRF (CVE-2026-64849) that accesses internal or cloud metadata services and leaks response details via…