
cerbos
 cerbos/cerbos
Authorization engine for context-aware access control with YAML policies, RBAC/ABAC support, check/plan APIs, and GitOps-friendly deployment.
api-securityauthenticationauthentication-authorization+3
4.6k
cerbos/cerbosAuthorization engine for context-aware access control with YAML policies, RBAC/ABAC support, check/plan APIs, and GitOps-friendly deployment.
 softrams/bulwark
An organizational asset and vulnerability management tool, with Jira integration, designed for generating application security reports.
 agentrust-io/cmcp
cMCP: Confidential MCP Gateway. Hardware-attested policy enforcement for MCP tool calls.
 6mile/gimmepatz
Personal Access Token (PAT) recon tool for bug bounty hunters, pentesters & red teams
 helixar-ai/mcp-security-checklist
MCP is being adopted rapidly. Security guidance is lagging behind. This checklist gives security engineers, platform teams, and technical leaders a…
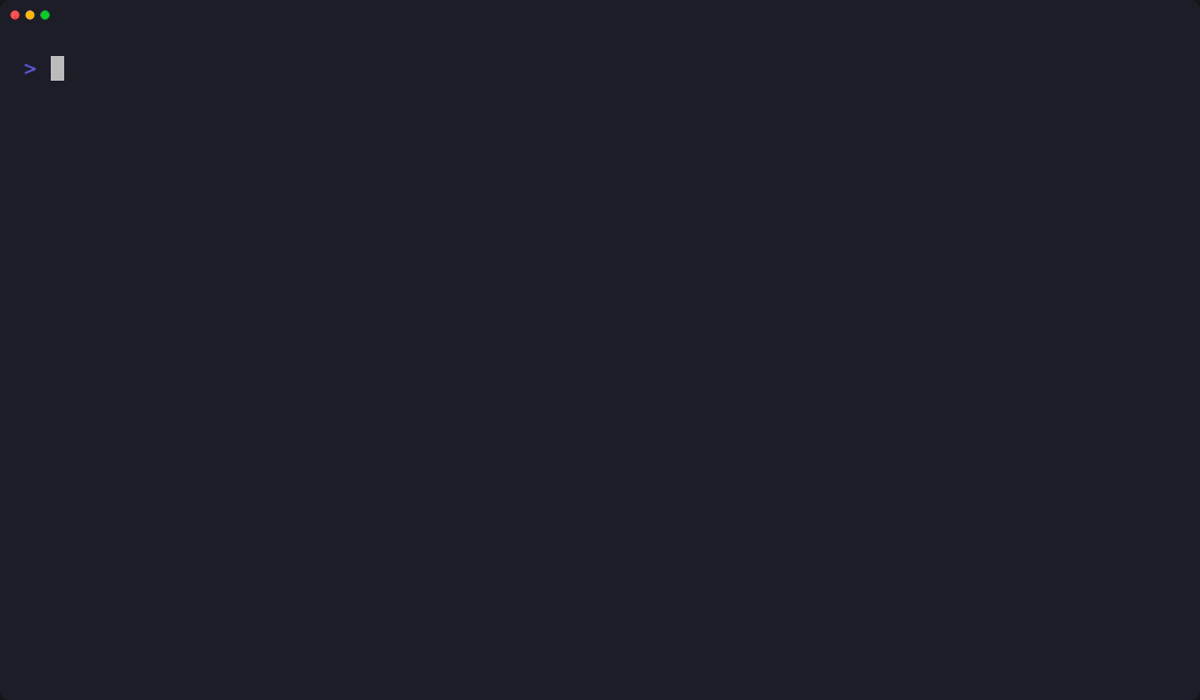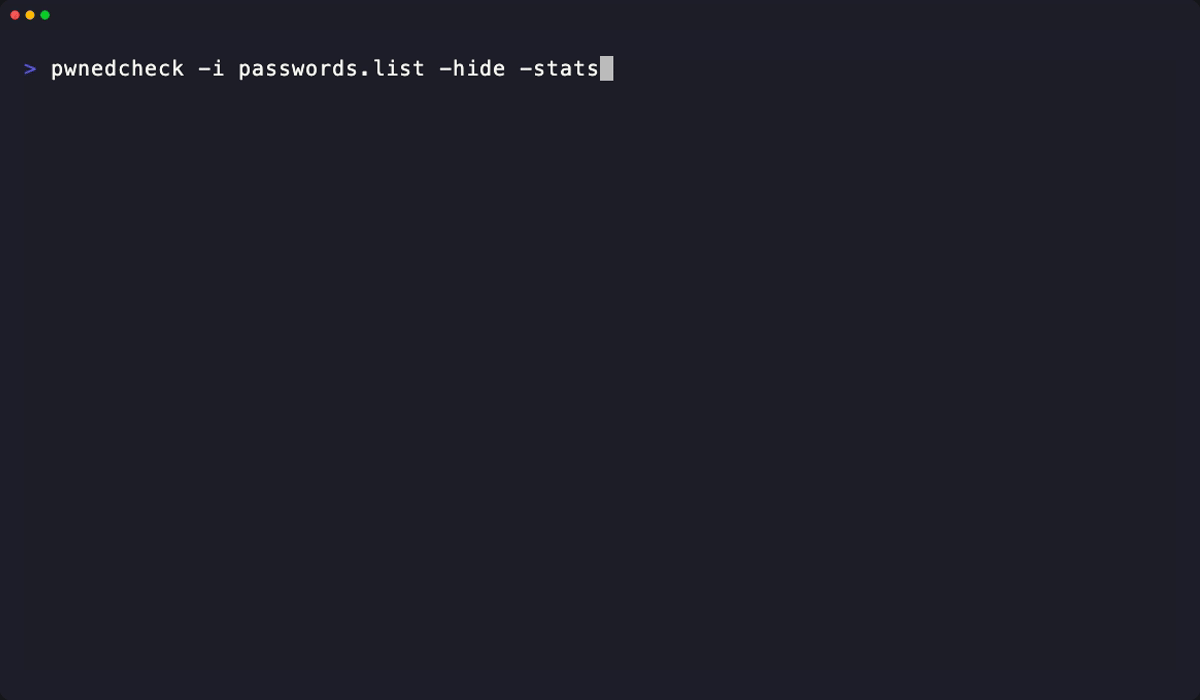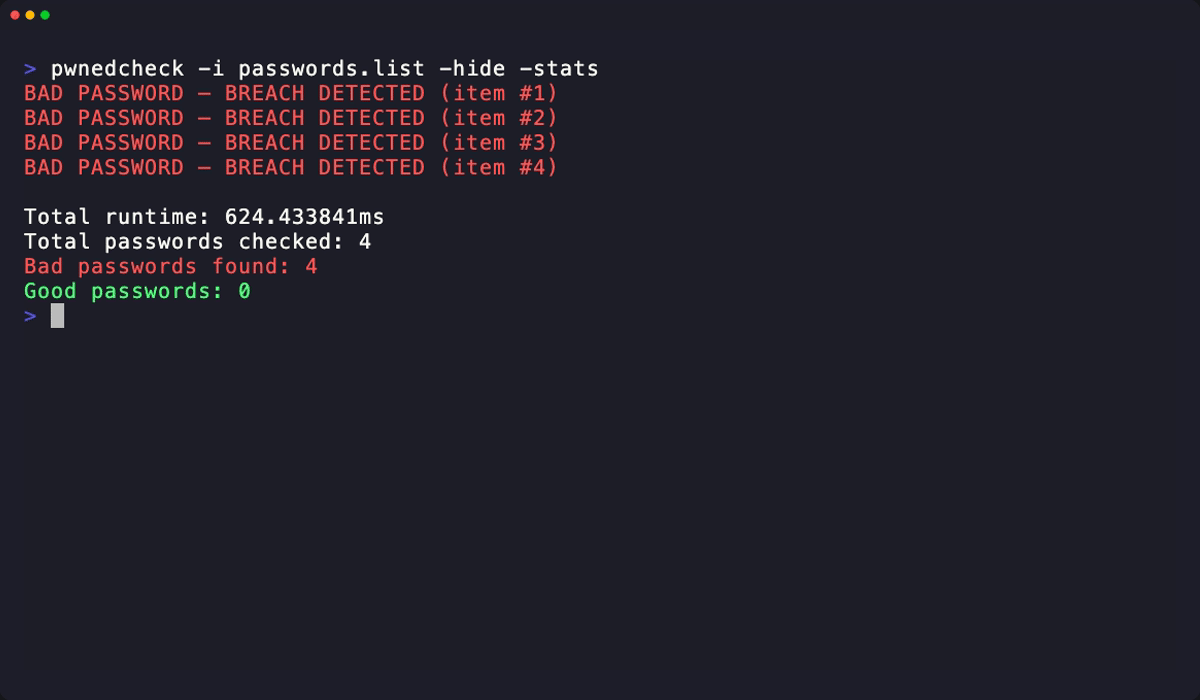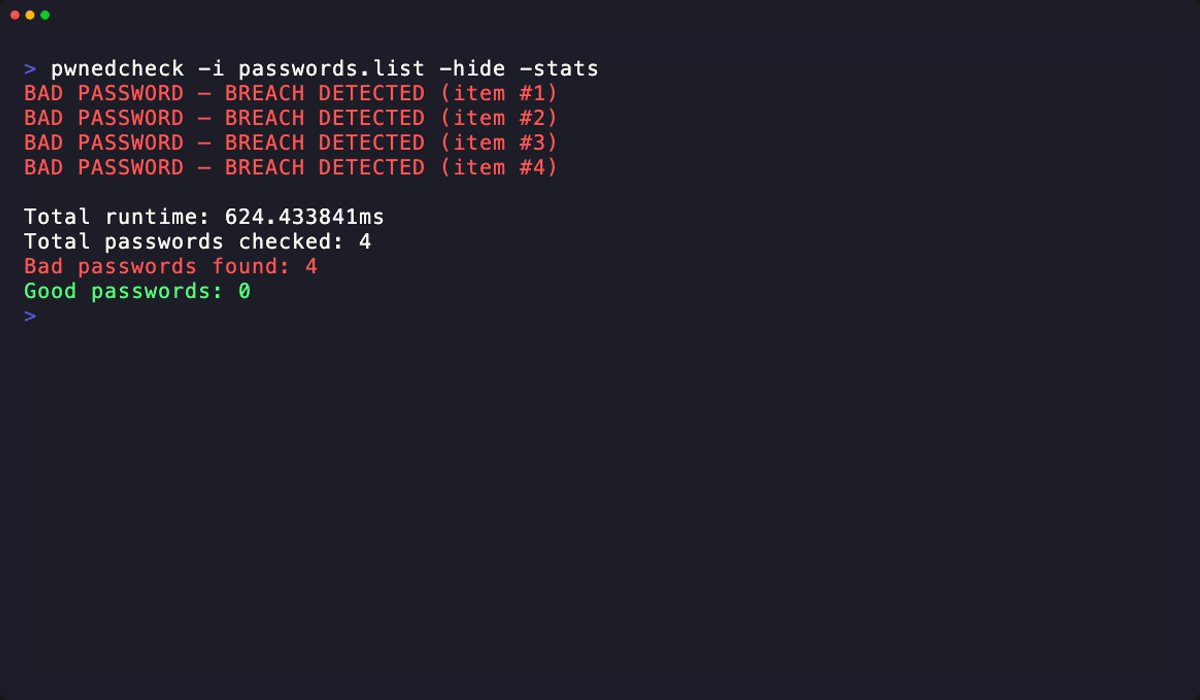 mohamedation/pwnedcheck
A command-line tool to check if passwords have been exposed in data breaches using the Have I Been Pwned (HIBP) API.
 rajsidwadkar/uap-protocol
A unified, security-first wire protocol for tool access and agent coordination. UAP eliminates CVE-2025-49596 and MCP tool-poisoning vulnerabilities…
 tuskira/ai-agent-gateway
Open-source gateway that secures, governs, and observes AI agents' MCP tool calls and LLM traffic, with API-key authentication and an admin console…
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
 s0md3v/arjun
HTTP parameter discovery tool that finds valid query parameters for URL endpoints using a large dictionary, supporting GET/POST/JSON/XML requests,…
 owasp/threat-dragon
An open source threat modeling tool from OWASP
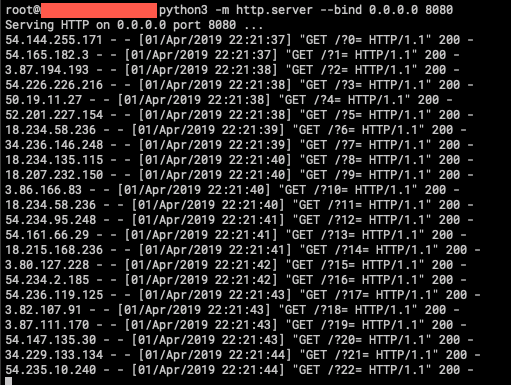 ustayready/fireprox
AWS API Gateway management tool for creating on the fly HTTP pass-through proxies for unique IP rotation
 assetnote/kiterunner
High-speed API and web content discovery tool that bruteforces routes using compiled Swagger datasets, supporting depth scanning, custom wordlists,…
 owasp/offat
Automated API security testing tool that generates tests from OpenAPI specs, fuzzes inputs, and checks for OWASP API Top 10 vulnerabilities including…
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
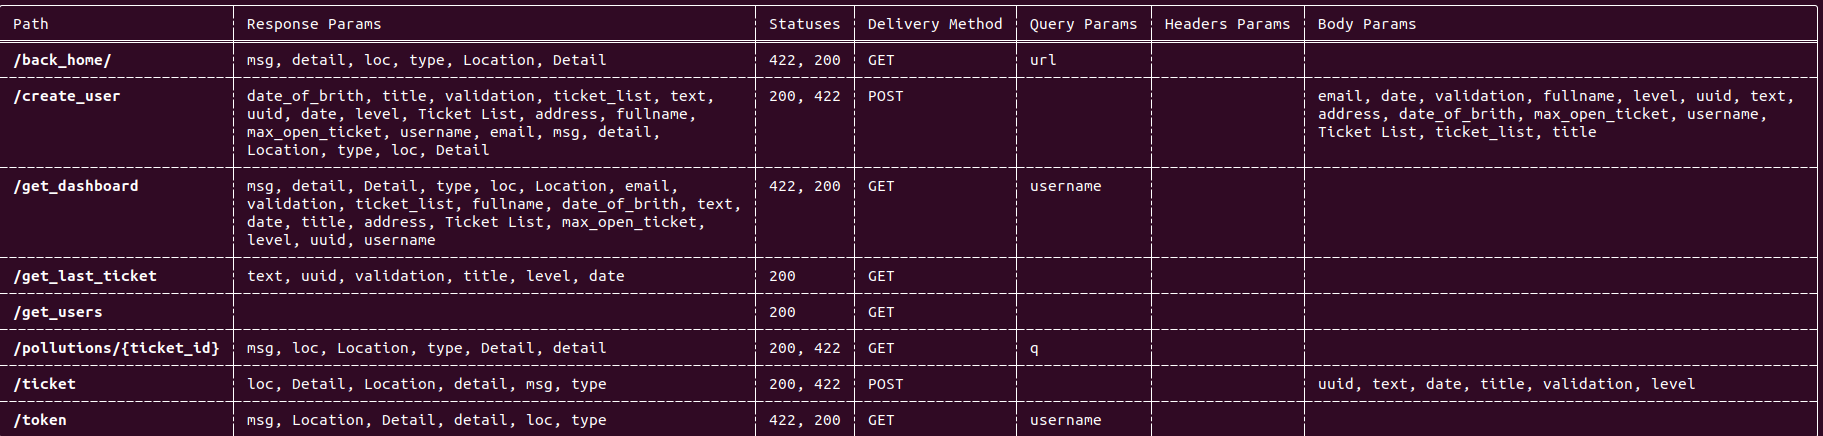 blst-security/cherrybomb
CLI tool that audits OpenAPI specifications, validates them against best practices, and runs automated security tests to detect vulnerabilities and…
 dolevf/graphw00f
GraphQL server engine fingerprinting tool that sends benign and malformed queries to identify backend technology and assess security defenses via the…