
knocker
 fariszr/knocker
Knocker, a knock based access control service for your homelab
api-securityauthenticationcloud-security+2
13625 days ago
fariszr/knockerKnocker, a knock based access control service for your homelab
 eddiejibson/limitrr-php
Better PHP rate limiting using Redis.
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 openziti/ziti
Zero-trust networking platform that makes services invisible with cryptographic identity, policy-based access, and end-to-end encryption. Replaces…
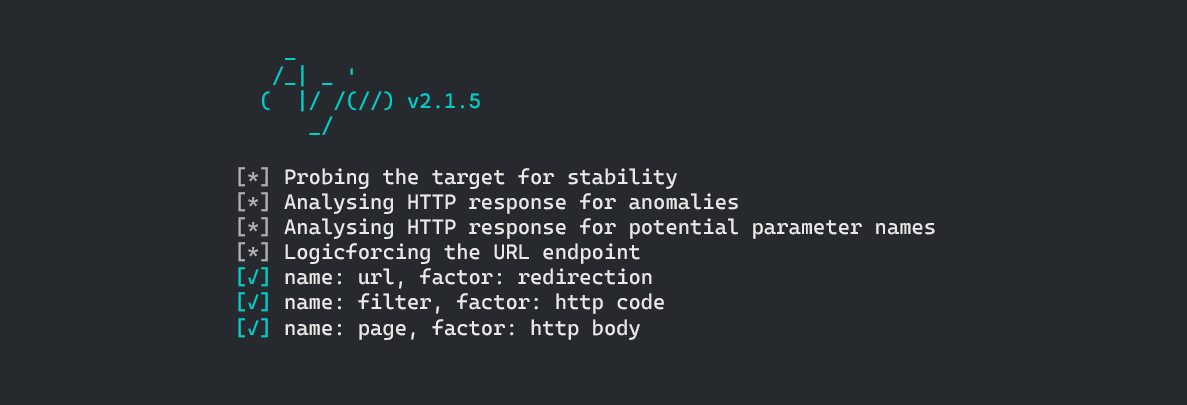 s0md3v/arjun
HTTP parameter discovery tool that finds valid query parameters for URL endpoints using a large dictionary, supporting GET/POST/JSON/XML requests,…
 ory/oathkeeper
A cloud native Identity & Access Proxy / API (IAP) and Access Control Decision API that authenticates, authorizes, and mutates incoming HTTP(s)…
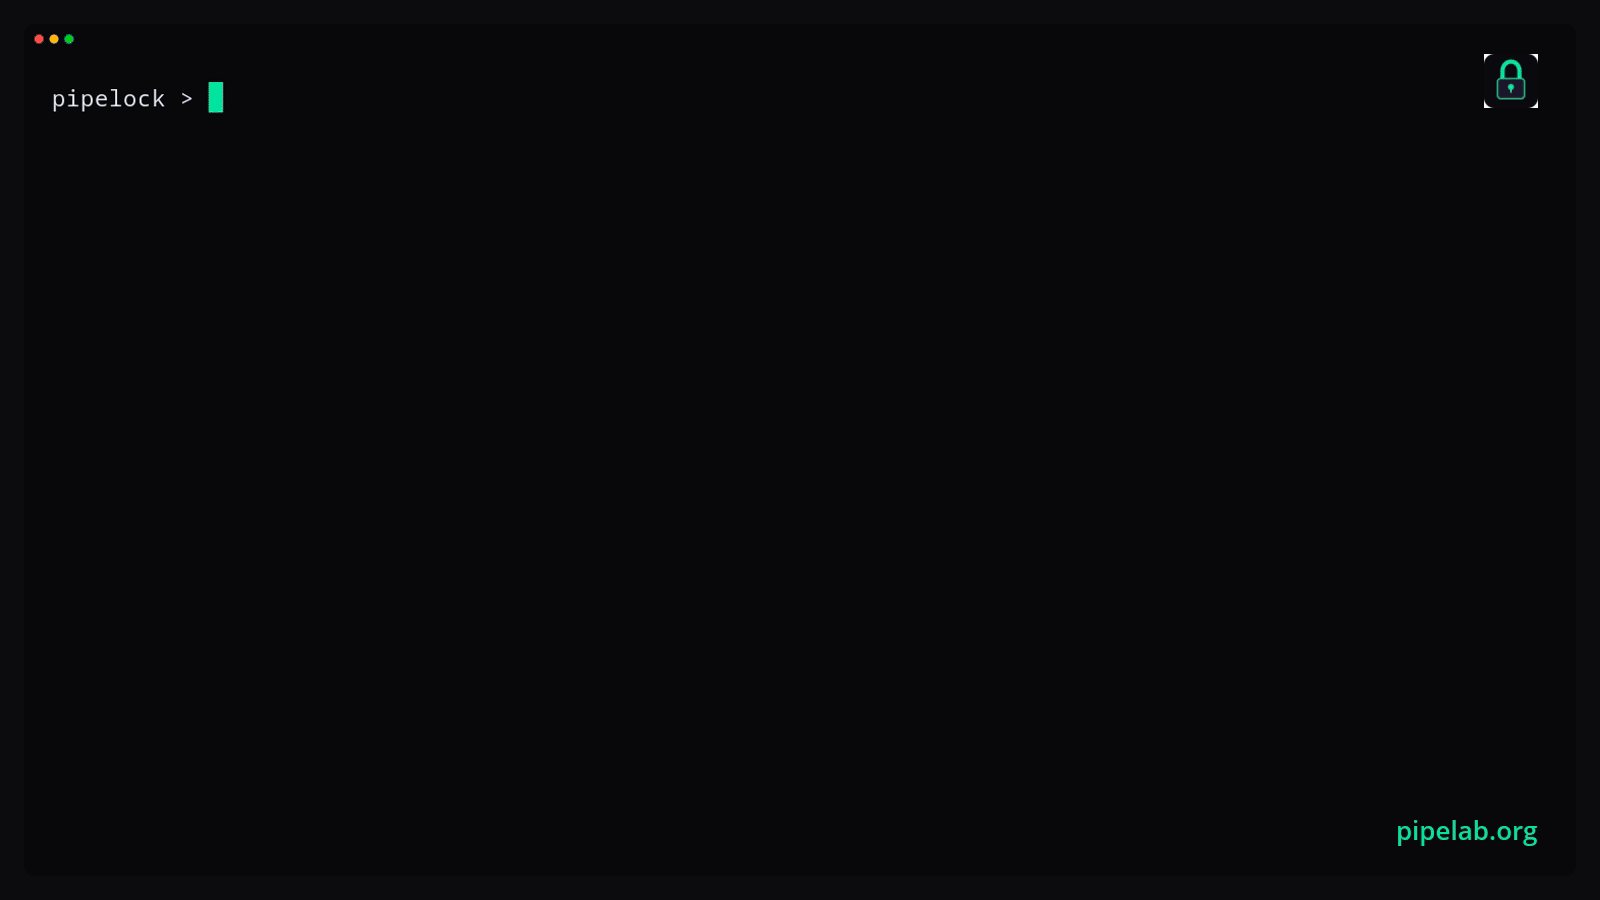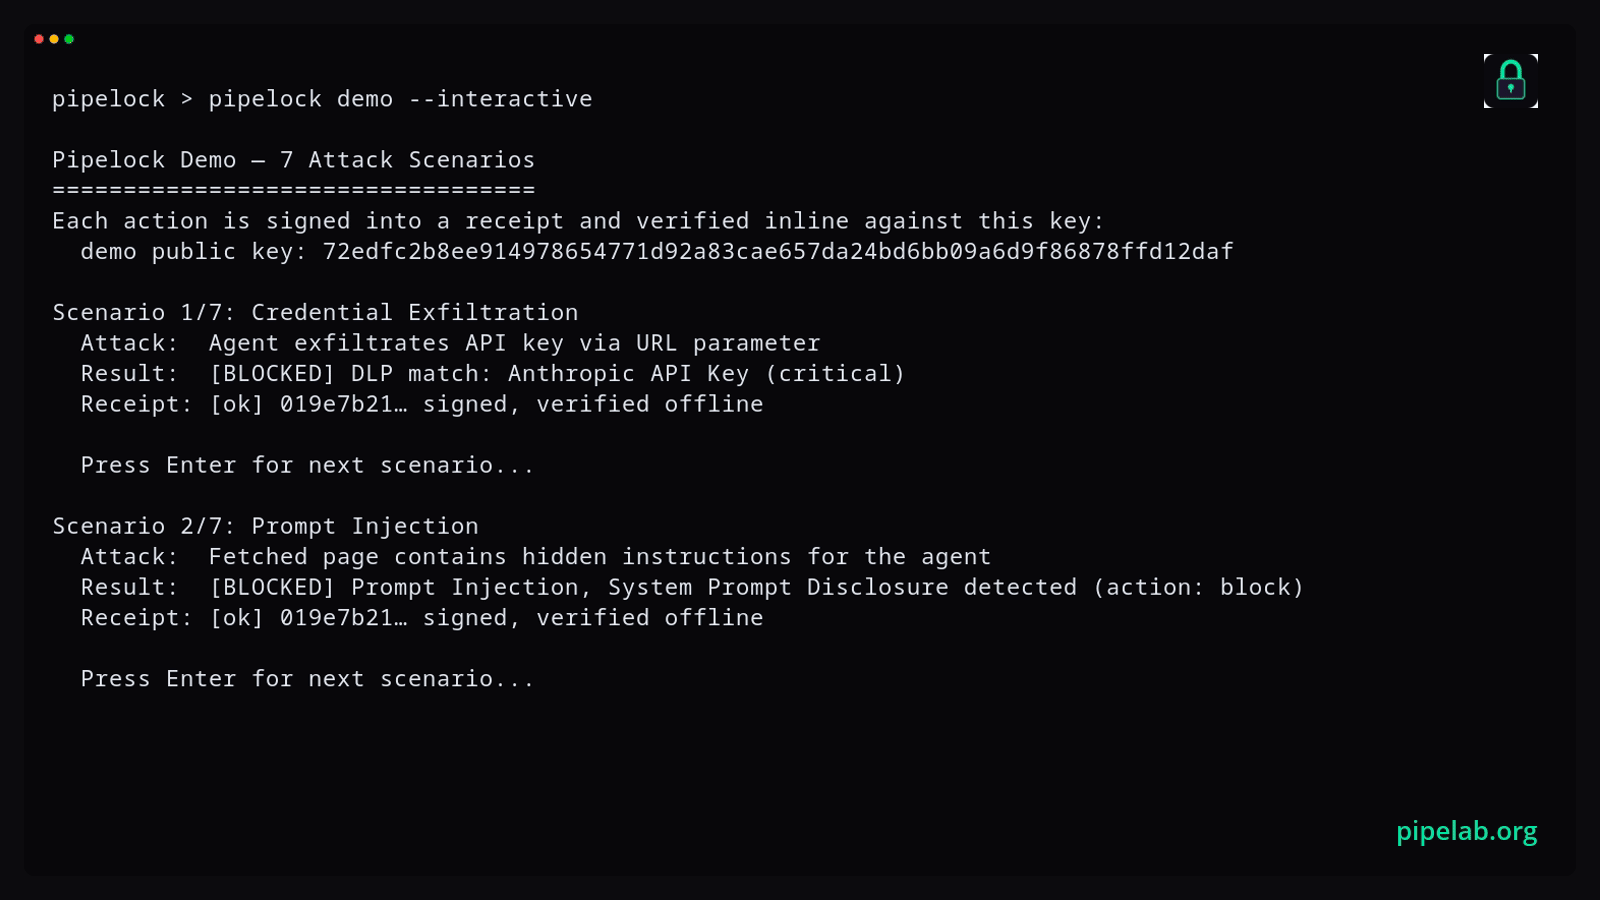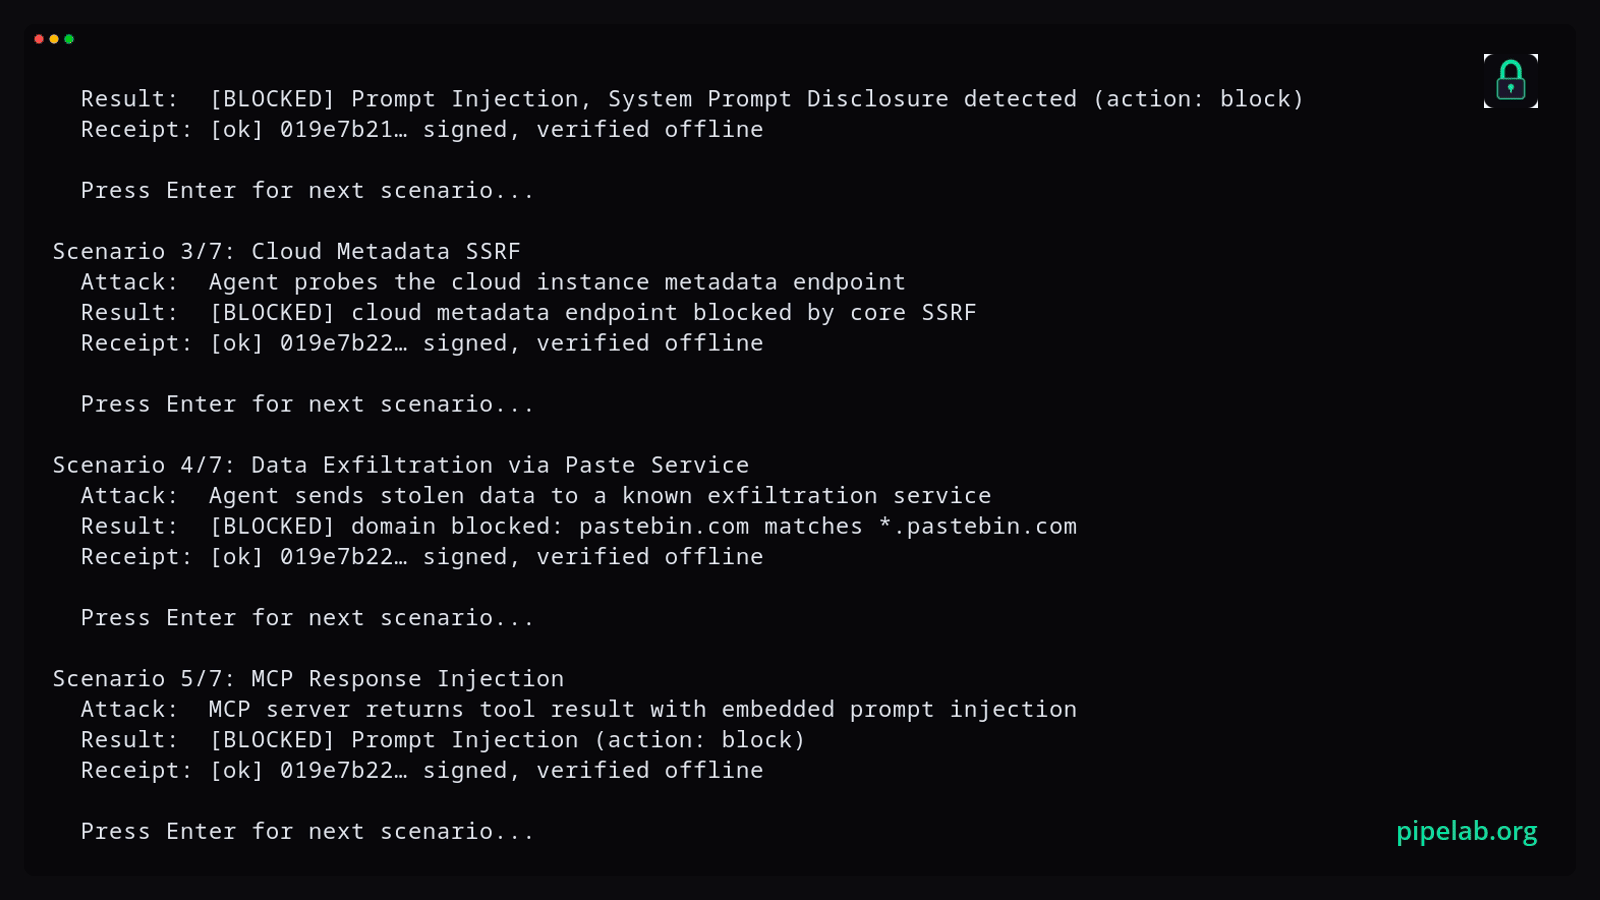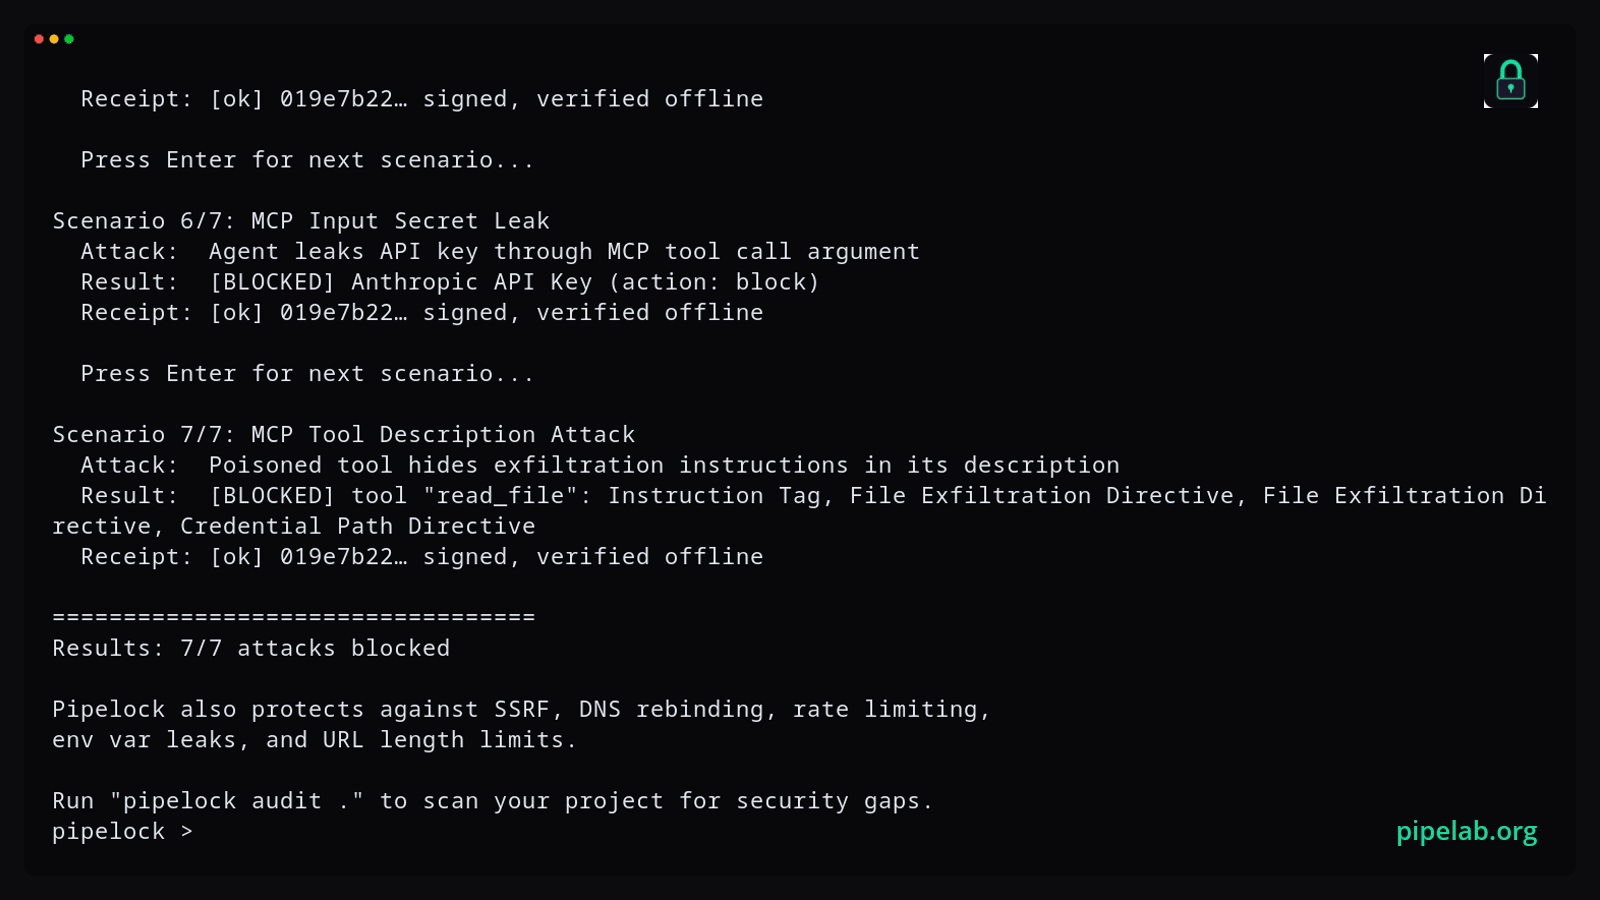 luckypipewrench/pipelock
Open-source AI agent firewall that scans HTTP, MCP, A2A, and WebSocket traffic for exfiltration, SSRF, and prompt injection, emitting verifiable…
 denoland/clawpatrol
Wire-level proxy firewall for AI agents that intercepts and gates SQL, Kubernetes, and HTTP traffic using HCL rules, with per-process tunnel…
 owasp/offat
Automated API security testing tool that generates tests from OpenAPI specs, fuzzes inputs, and checks for OWASP API Top 10 vulnerabilities including…
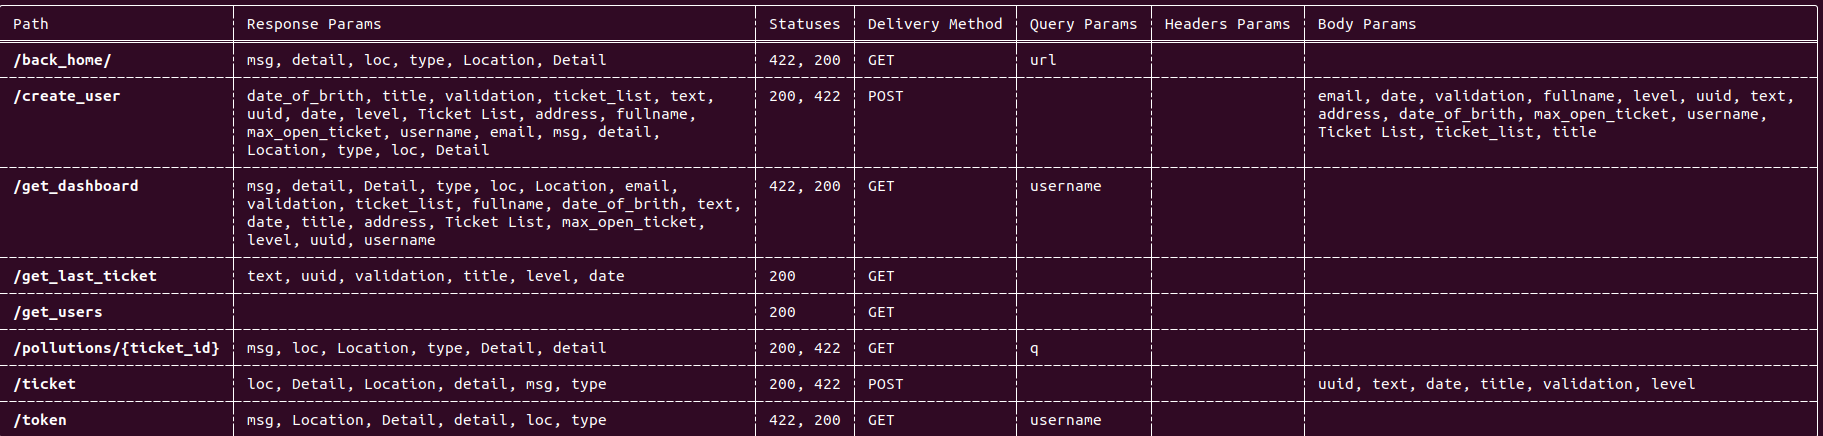 blst-security/cherrybomb
CLI tool that audits OpenAPI specifications, validates them against best practices, and runs automated security tests to detect vulnerabilities and…
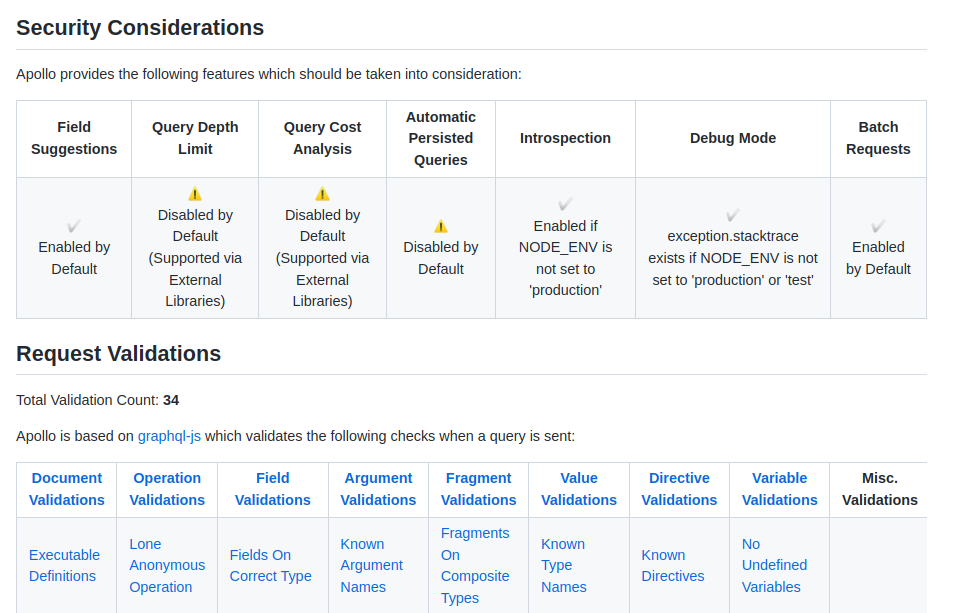 dolevf/graphw00f
GraphQL server engine fingerprinting tool that sends benign and malformed queries to identify backend technology and assess security defenses via the…
 imperva/automatic-api-attack-tool
Imperva's customizable API attack tool takes an API specification as an input, generates and runs attacks that are based on it as an output.
 watchdogsecurity/porch-pirate
Porch Pirate is the most comprehensive Postman recon / OSINT client and framework that facilitates the automated discovery and exploitation of API…
 undeadsec/swaggerspy
Automated OSINT tool that scans SwaggerHub API documentation to discover exposed secrets, credentials, and sensitive information using regex-based…
 sentrypeer/sentrypeer
Distributed SIP honeypot that detects and shares fraud data on VoIP attacks. Collects bad actor IPs and phone numbers via peer-to-peer network, with…
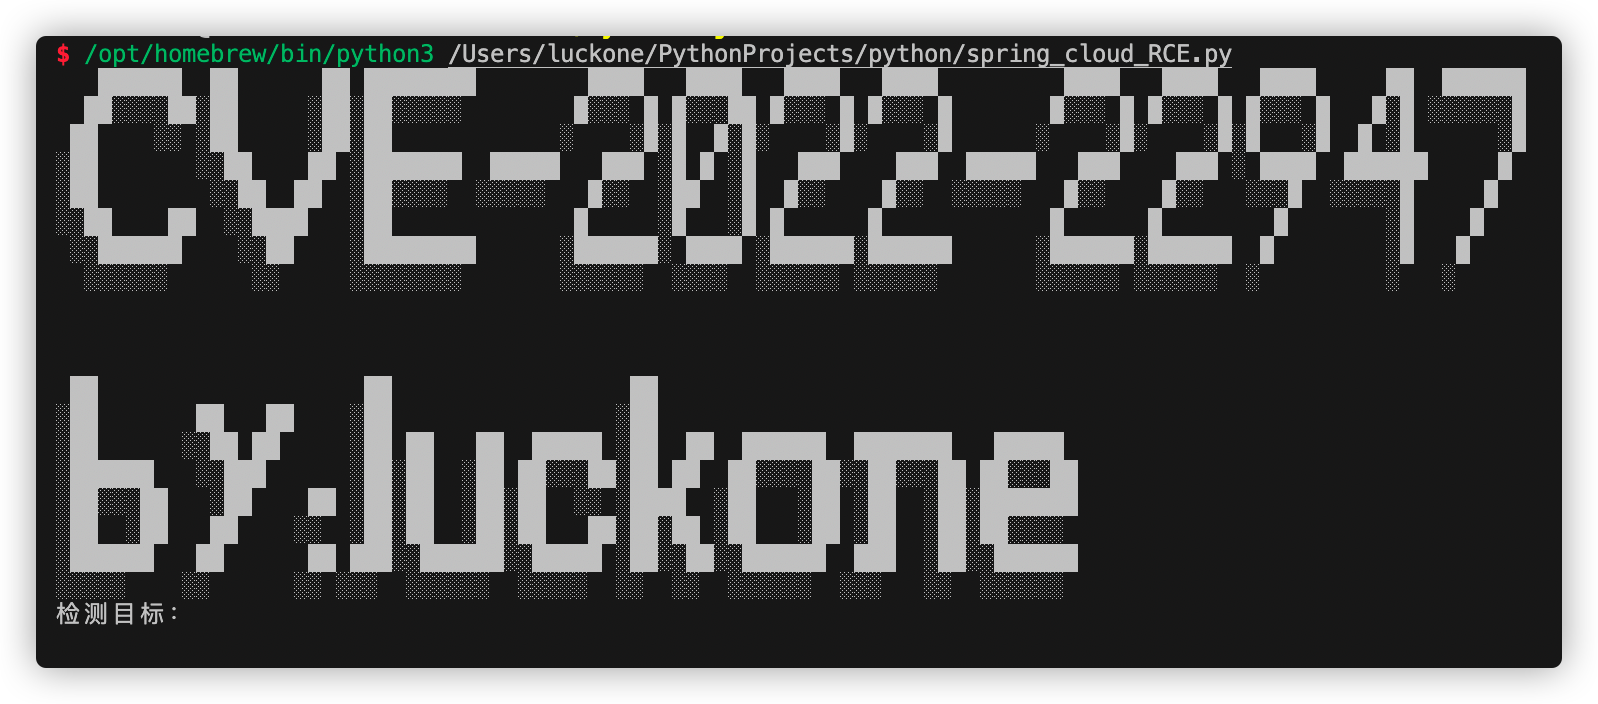 lucksec/spring-cloud-gateway-cve-2022-22947
Exploit for CVE-2022-22947: remote code execution in Spring Cloud Gateway via crafted requests to the Actuator endpoint. Includes Python script and…
 dhiyaneshgeek/my-presentation-slides
Collection's of Tech Talk that are presented by me :)
 cspf-founder/api-scanner-docker
Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …