

noir
 owasp-noir/noir
Hunt every Endpoint in your code, expose Shadow APIs, map the Attack Surface.
api-securitydevsecopspenetration-testing+3
owasp-noir/noirHunt every Endpoint in your code, expose Shadow APIs, map the Attack Surface.
 owasp/nest
Your gateway to OWASP. Discover, engage, and help shape the future!
 akto-api-security/akto
Open-source API security platform for continuous API discovery, vulnerability testing, and runtime threat detection. Integrates with CI/CD pipelines…
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
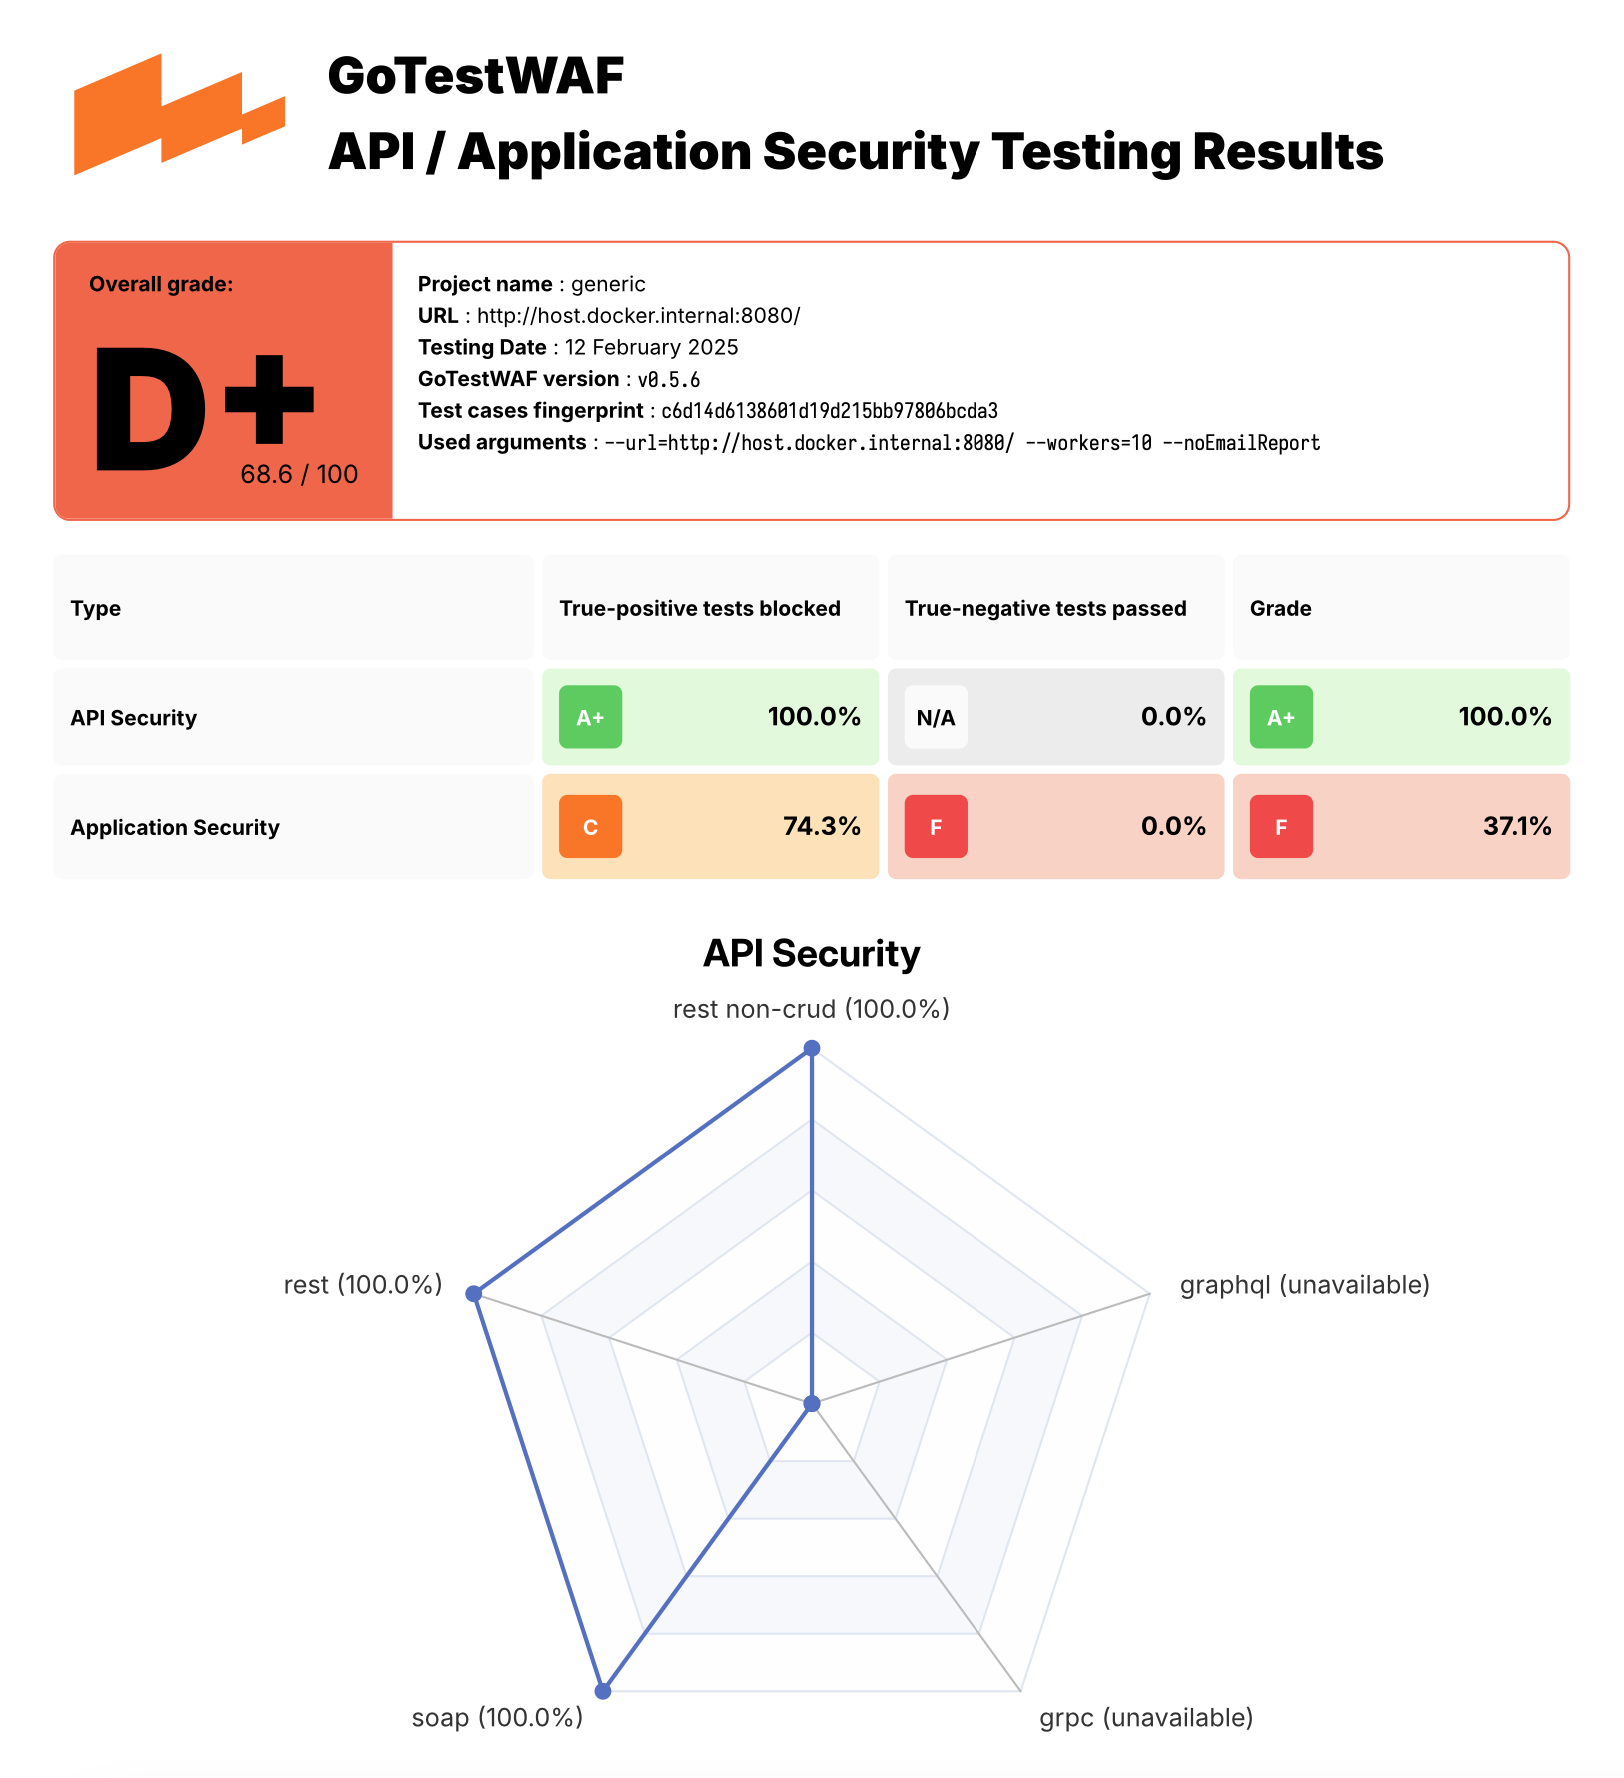 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 owasp/asvs
Application Security Verification Standard
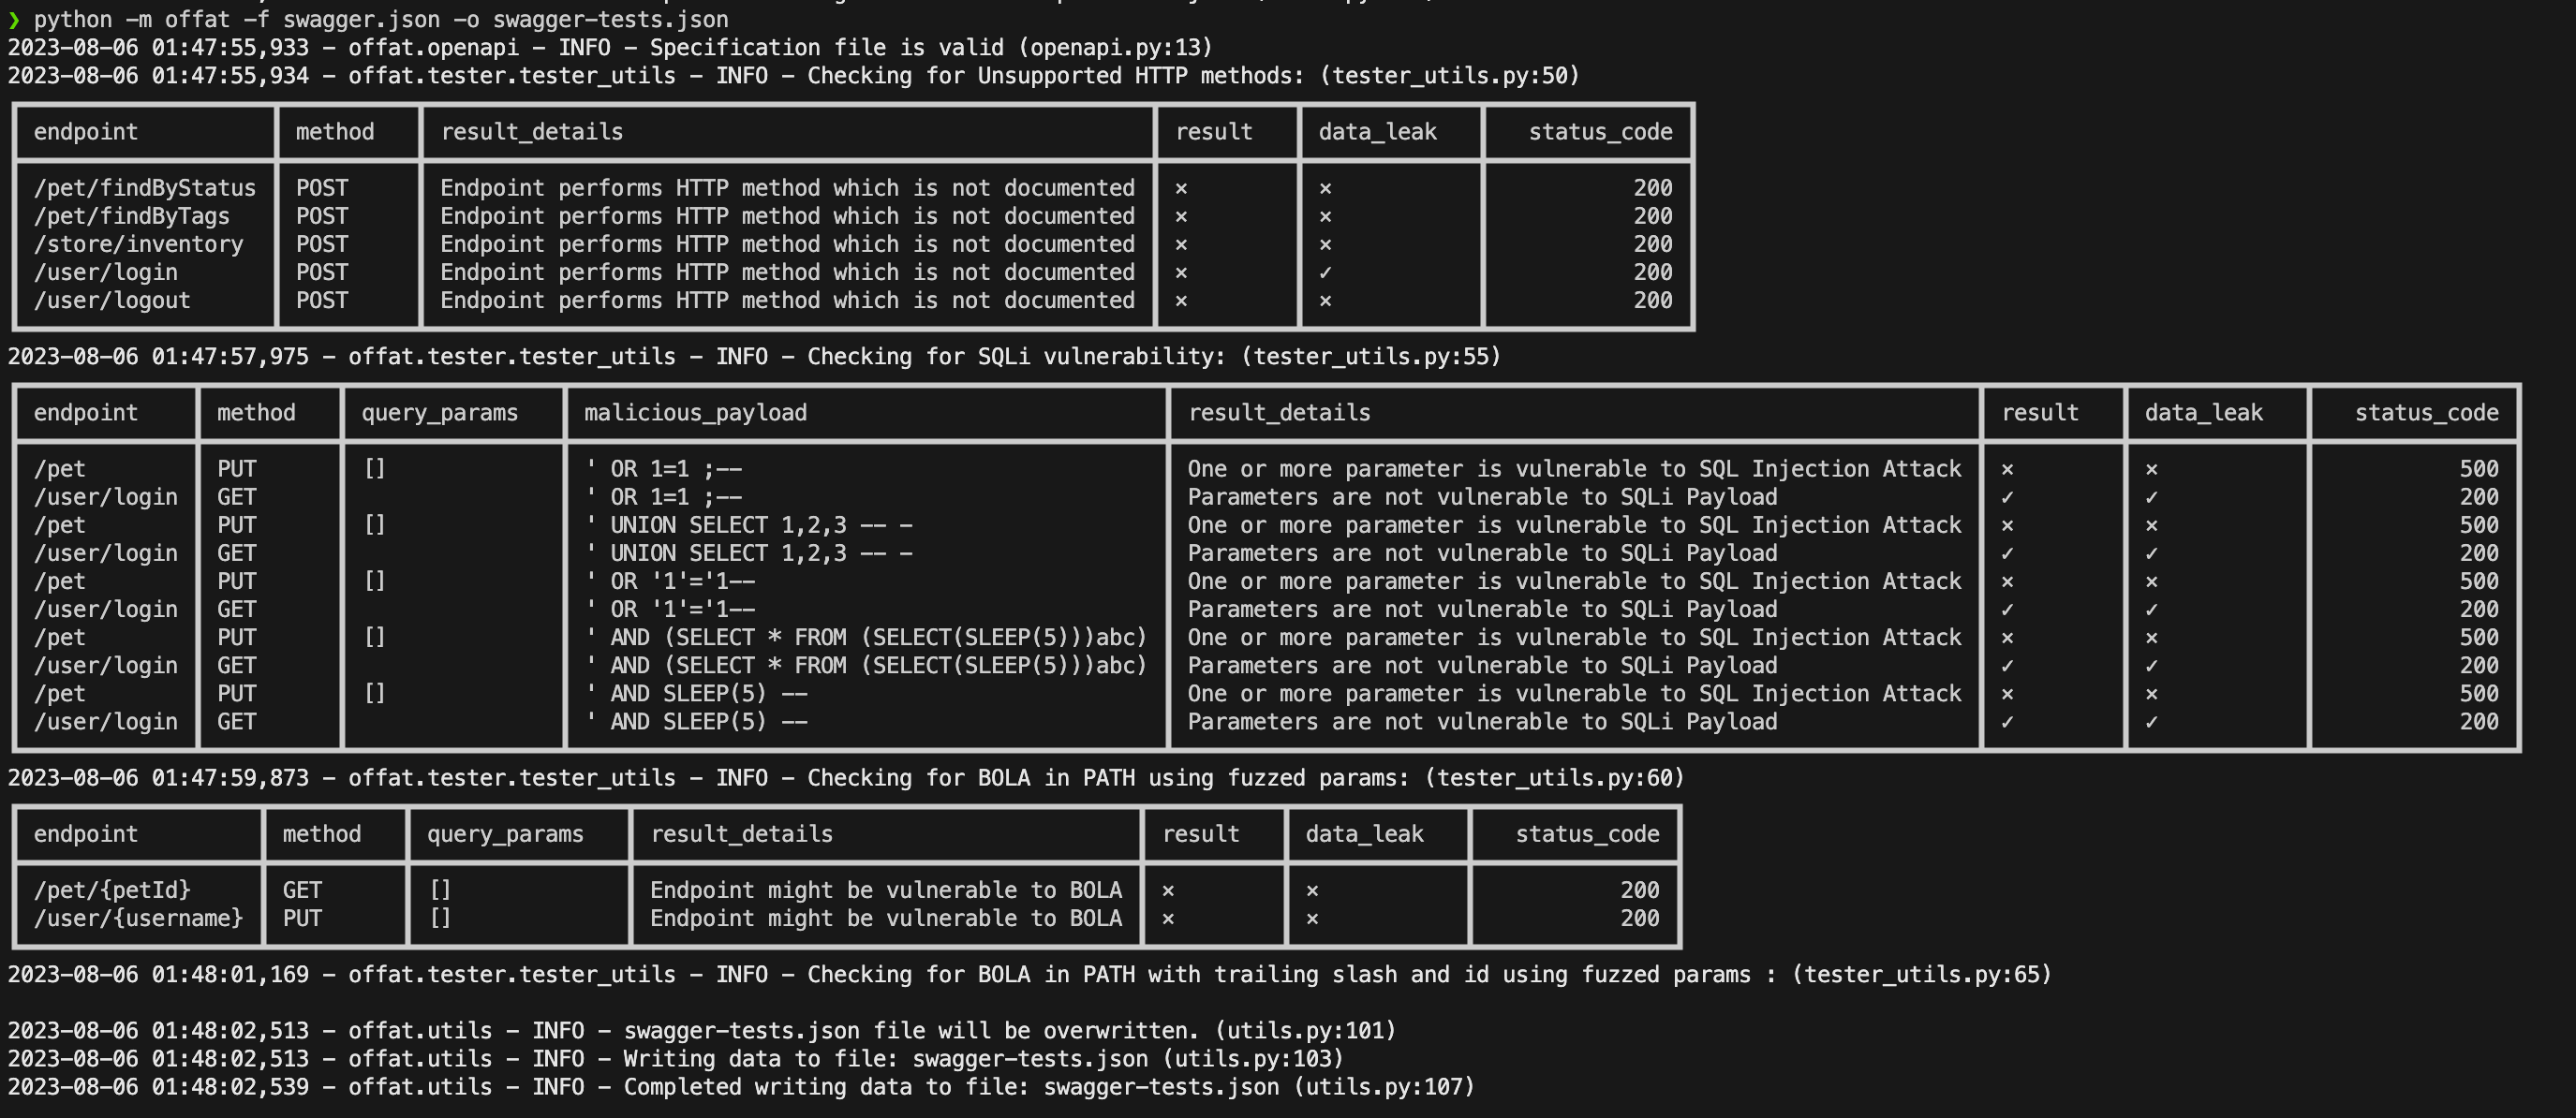 owasp/offat
Automated API security testing tool that generates tests from OpenAPI specs, fuzzes inputs, and checks for OWASP API Top 10 vulnerabilities including…
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
 owasp/threat-dragon
An open source threat modeling tool from OWASP
 owasp/secure-agent-playbook
OWASP Secure Agent Playbook Project
 owasp/secretsifter
OWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).
 owasp/java-html-sanitizer
Takes third-party HTML and produces HTML that is safe to embed in your web application. Fast and easy to configure.
 pie-script/llm-agent-testbed
An empirical security testbed evaluating prompt injection, confused-deputy vulnerabilities, and tool-calling defenses in LLM agents.
 jay123anta/laravel-threat-detection
Passive Laravel middleware that detects and logs SQL injection, XSS, RCE, bot scanners, and 175+ attack patterns. Features a built-in dashboard,…
 hakaioffsec/cve-2026-16764
Python exploit for CVE-2026-16764, a privilege escalation in OWASP DefectDojo where an is_staff REST API bypass lets a low-privileged user gain…