

pipelock
 luckypipewrench/pipelock
Open-source AI agent firewall that scans HTTP, MCP, A2A, and WebSocket traffic for exfiltration, SSRF, and prompt injection, emitting verifiable…
ai-securityapi-securitycloud-security+8
957
luckypipewrench/pipelockOpen-source AI agent firewall that scans HTTP, MCP, A2A, and WebSocket traffic for exfiltration, SSRF, and prompt injection, emitting verifiable…
 owasp/offat
Automated API security testing tool that generates tests from OpenAPI specs, fuzzes inputs, and checks for OWASP API Top 10 vulnerabilities including…
 owasp/threat-dragon
An open source threat modeling tool from OWASP
 ambitsecurity/jshound
Find every API request a web app makes, from the JavaScript it ships: method, URL, body, headers and GraphQL operations. One command.

 abraxas/jellyfin-playlist-itemids
Jellyfin Server 12.2 - High - Remote - IDOR - public playlist ItemIds leftover of GHSA-9x85 then unauth stream
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
 abraxas/pfsense-api-acb-userkey
pfSense Plus MIM API toolkit b4acd7ca - High - Remote - IDOR - ACB userkey capability URL
 abraxas/pfsense-api-acme-key-dump
pfSense Plus MIM API toolkit b4acd7ca - High - Remote - Privilege leftover - GET /services/acme dumps keys
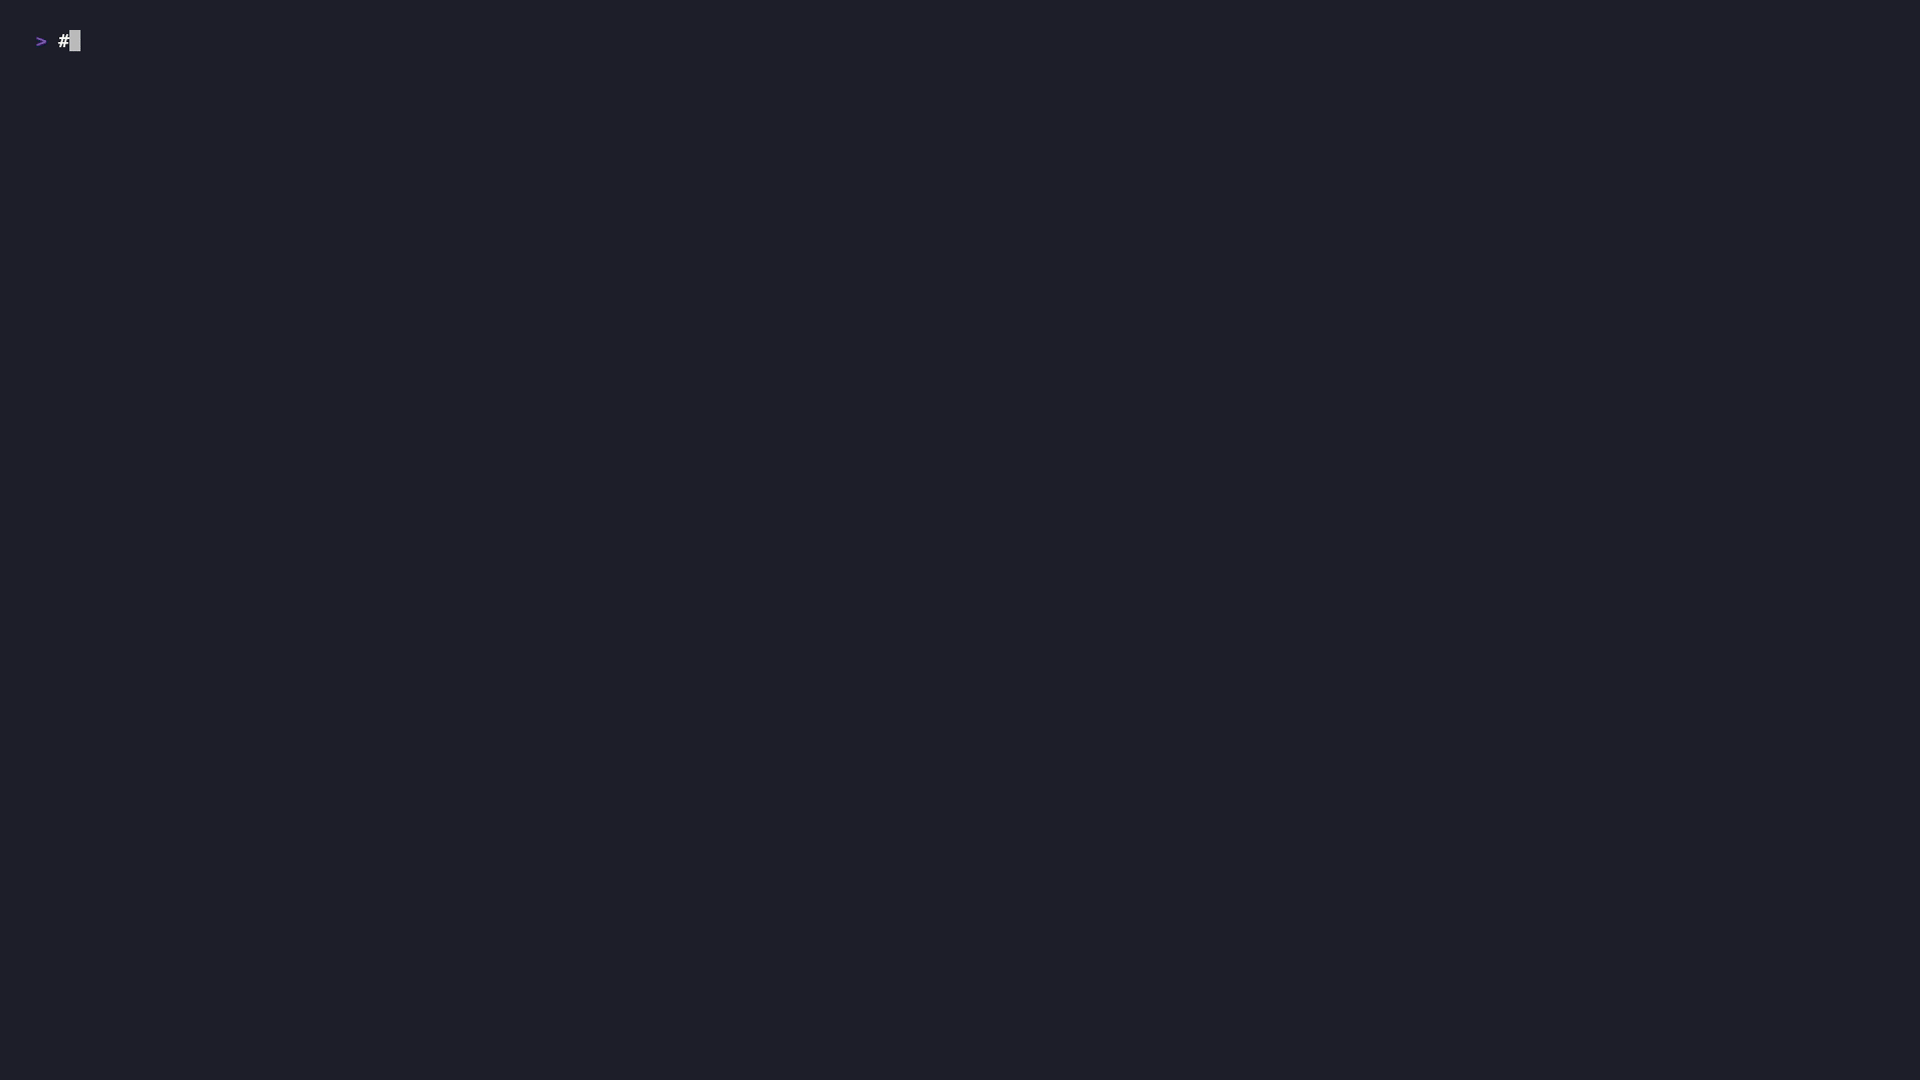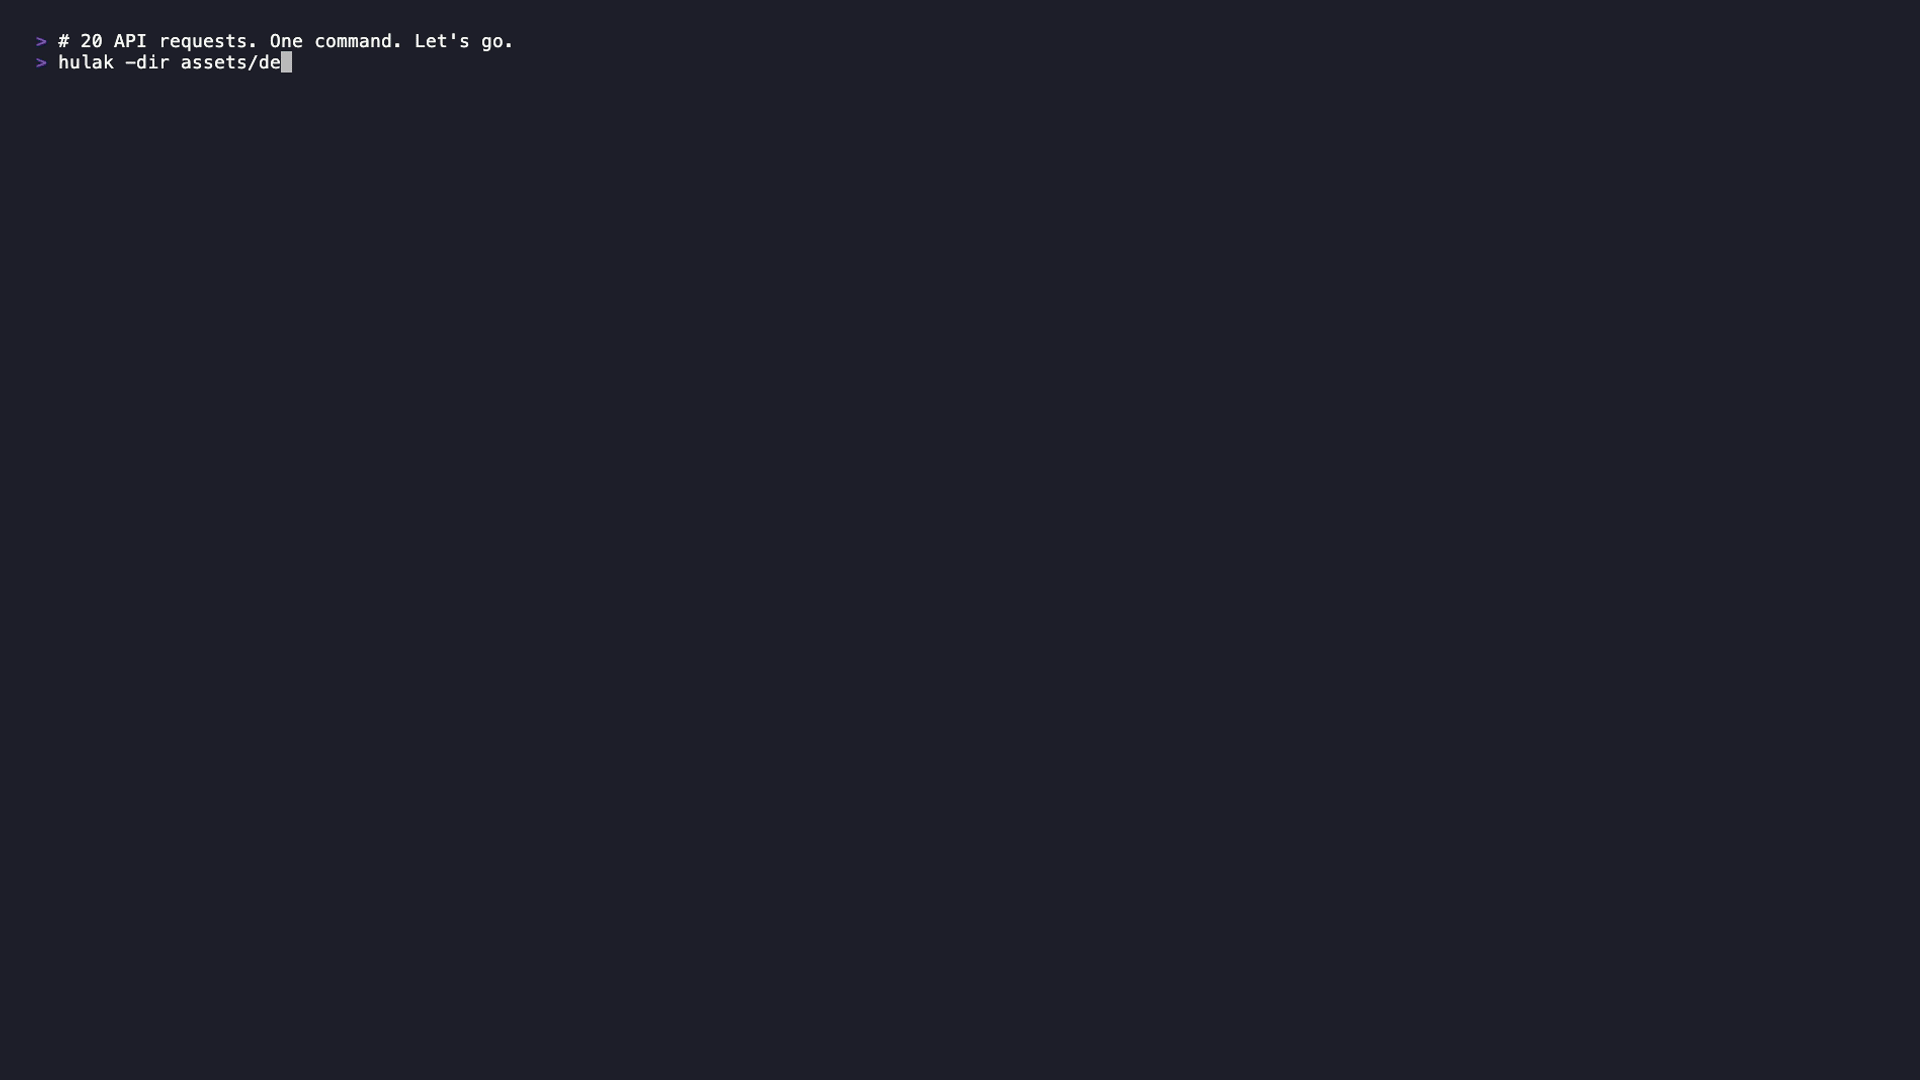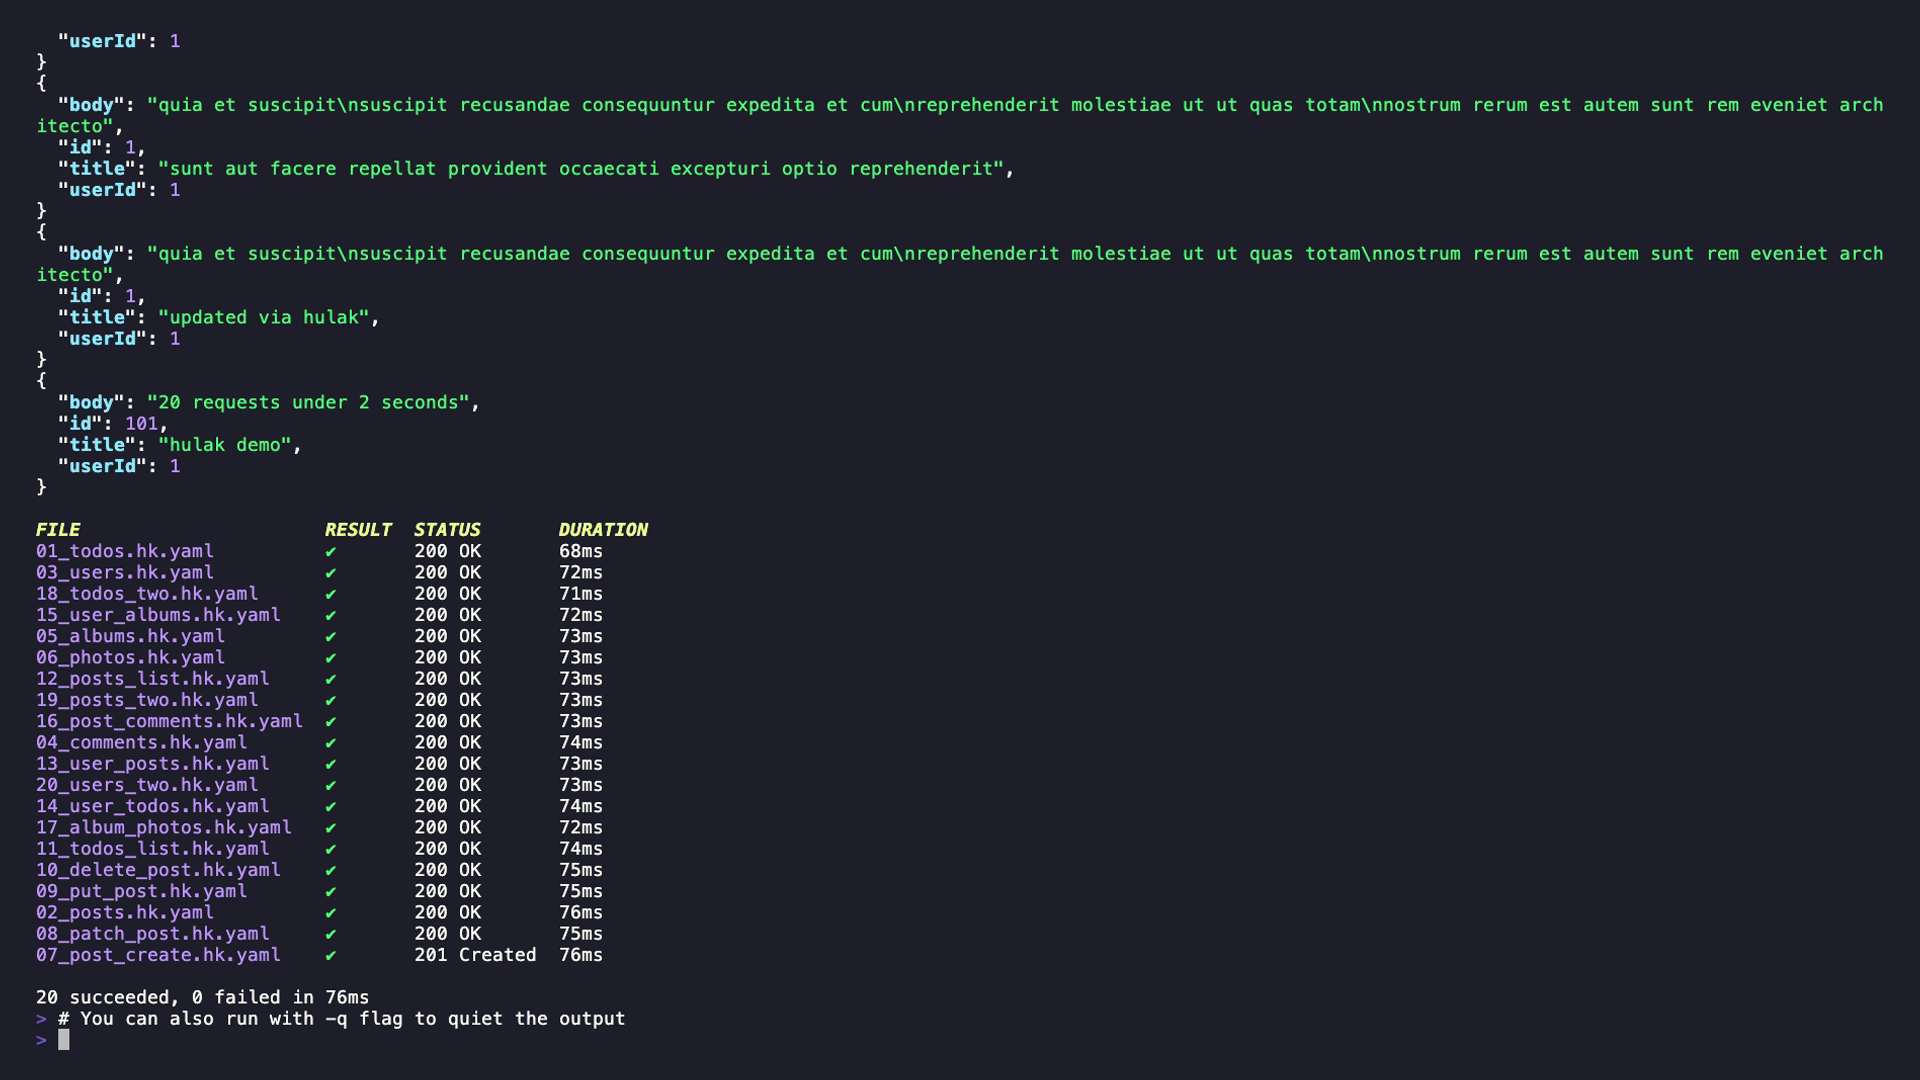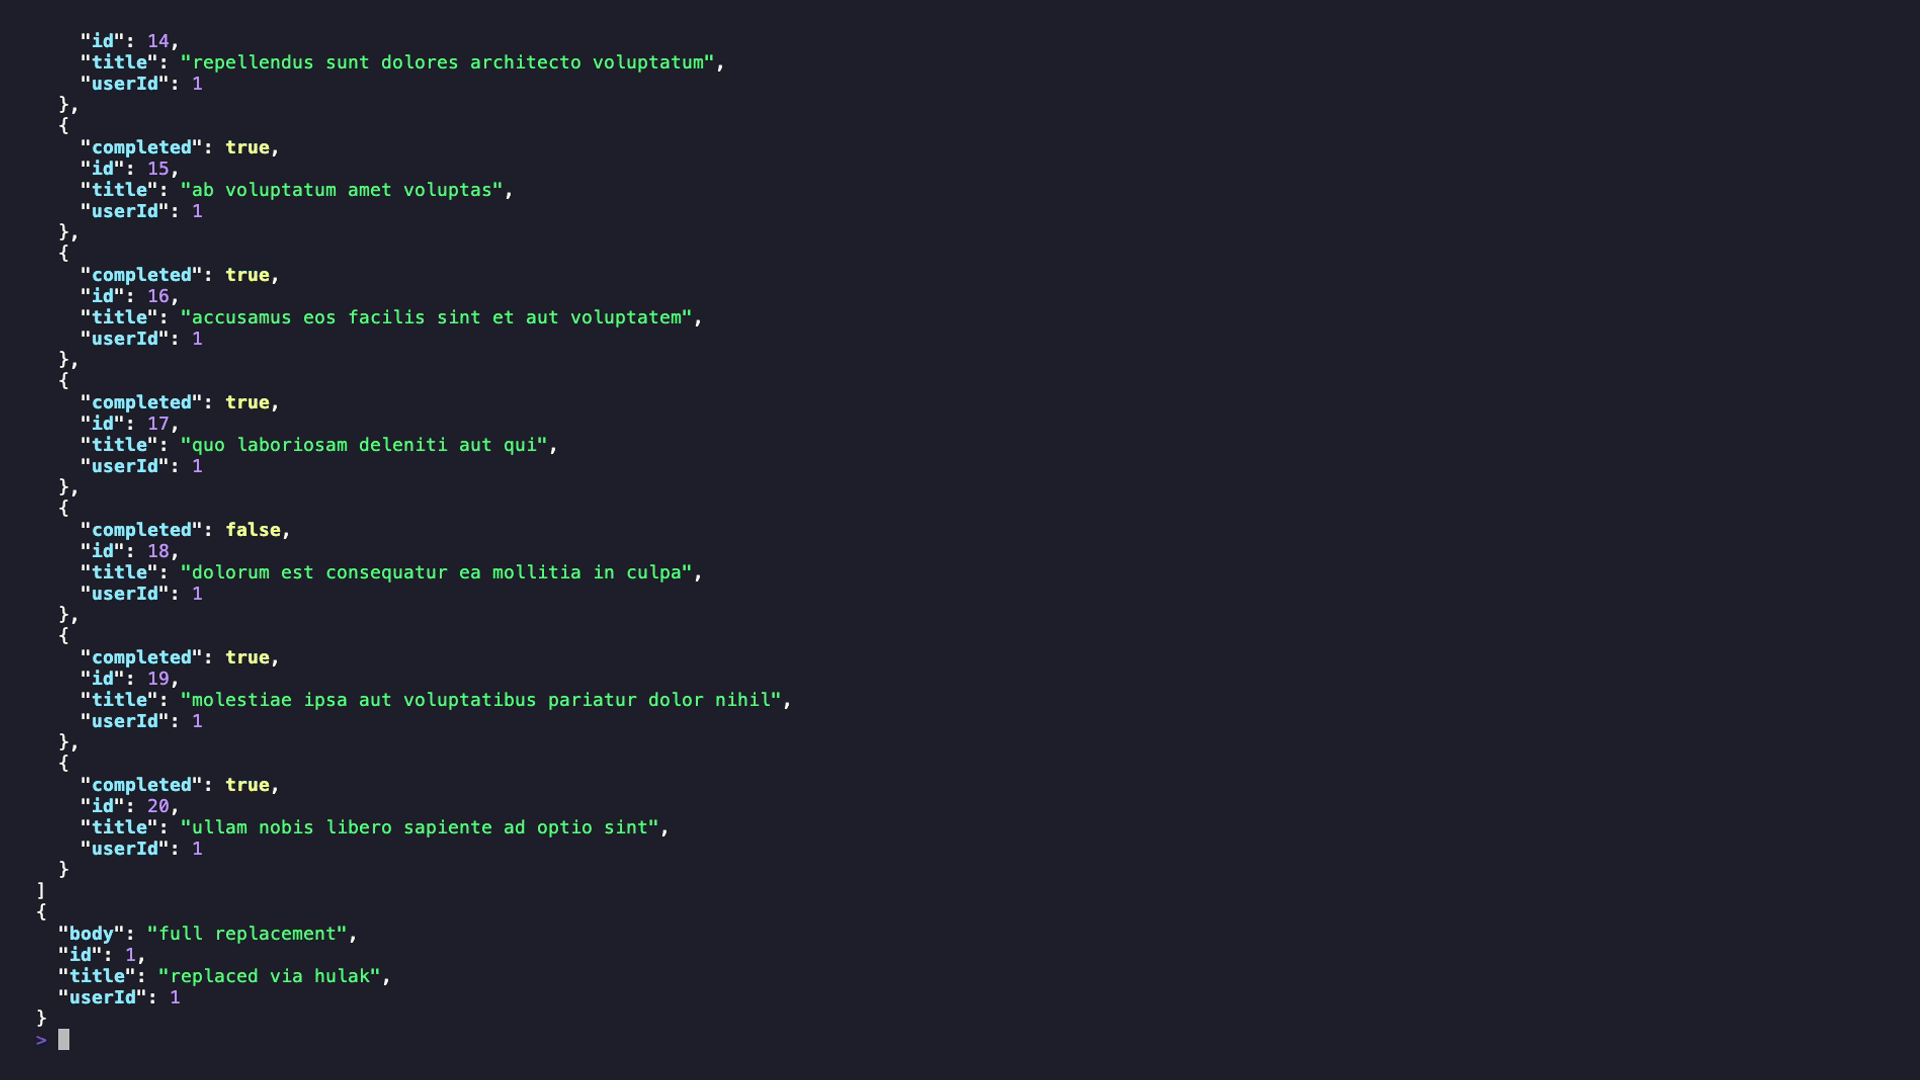 xaaha/hulak
A lightweight, file-based CLI API client with age-encrypted secrets, first-class GraphQL support, and a built-in MCP server for AI agent workflows.
 abraxas/cve-2026-15583
Proof-of-concept client and Docker lab reproducing CVE-2026-15583, an unauthenticated confused-deputy SSRF in Grafana MCP Server that leaks…
 tirrenotechnologies/tirreno
Open-source security framework for real-time event tracking, threat detection, and risk scoring. Monitors user behavior, detects fraud, bot attacks,…
 mevislobo2006/threatripper
Offline heuristic analyzer that scores suspicious SMS, chat messages and links for scam and phishing indicators, explaining each warning sign with…
 rmhowe425/poc-cve-2026-93680
Proof-of-concept exploit for CVE-2026-93680 demonstrating MCP SSE authentication bypass and data exfiltration via tool invocation.
 hashicorp-forge/grove
A Software as a Service (SaaS) log collection framework.
 uziii2208/cve-2026-86259
OpenMAIC 1.0.0: Unauthenticated Outbound SSRF to Cloud Metadata Service via Fail-Open Middleware and Environment-Gated Validation Bypass
 faceless0x7/cve-2026-89012
Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…
 arian-gogani/enforcement-coverage
Finds API routes carrying weaker authorization than their siblings. Recovered CVE-2026-45316 from source. Includes the negative results.