
TurkoRat
 cryst4linqq/turkorat
Fully undetected grabber (grabs wallets, passwords, cookies, modifies discord client etc.)
anti-botdata-exfiltrationinformation-gathering+5
1844 years ago
cryst4linqq/turkoratFully undetected grabber (grabs wallets, passwords, cookies, modifies discord client etc.)
 zeromemoryex/bypass-sandbox-evasion
C++ tool that patches Windows API calls to bypass sandbox RAM size checks, enabling malware to evade detection in isolated analysis environments.
 xiaolichan/redcaddy
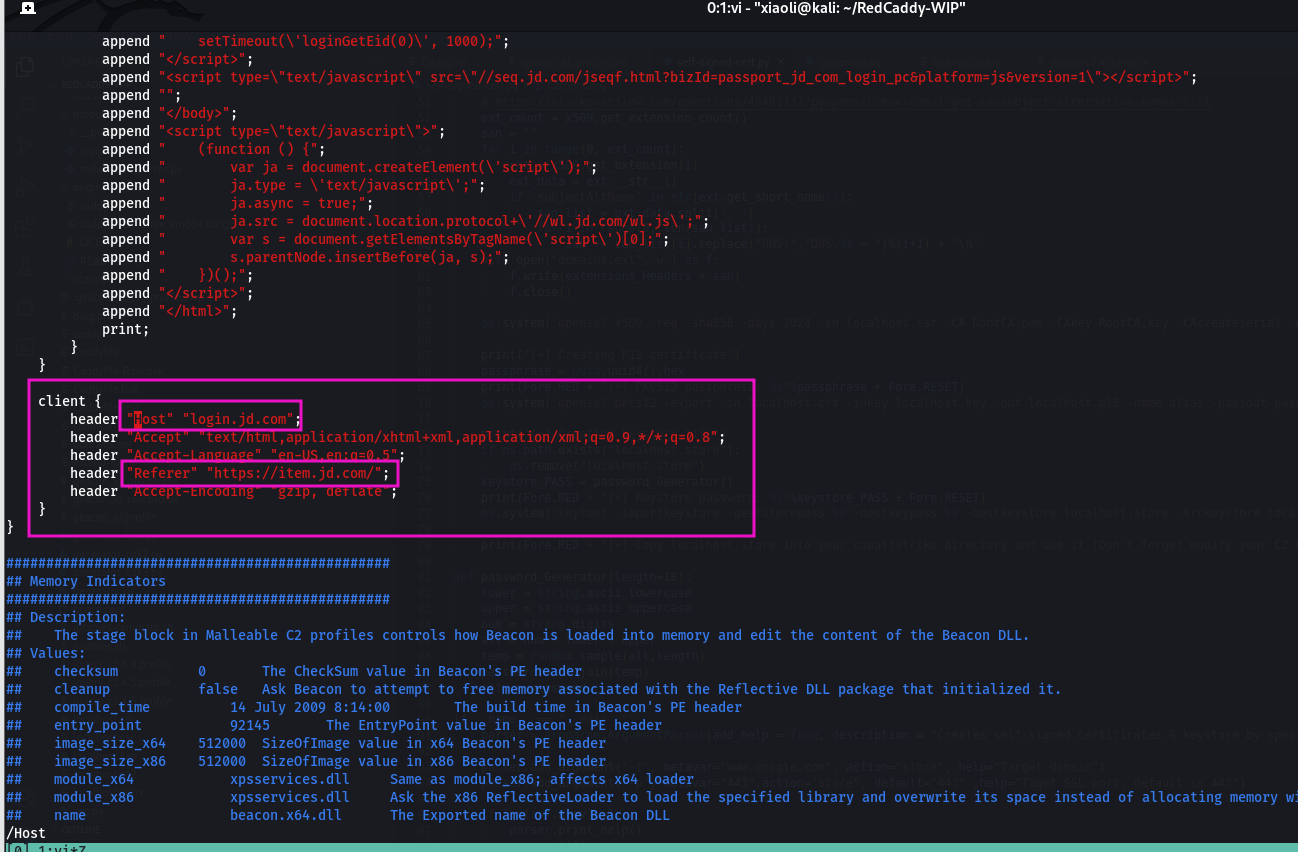
C2 redirector base on caddy
 xkiian/datadome-vm
Reverse engineering the new Datadome VM 🔥
 pinoywh1z/aoratoswin
A tool that removes traces of executed applications on Windows OS.
 duhirsch/moveedr
Permanently disable EDRs as local admin
 nuclearphoenixx/fake-sandbox
👁🗨 This script will simulate fake processes of analysis sandbox/VM software that some malware will try to avoid.
 tg12/phantomstars
Automated detection and tracking of fake engagement on GitHub — daily CI, zero infrastructure
 jay123anta/laravel-threat-detection
Passive Laravel middleware that detects and logs SQL injection, XSS, RCE, bot scanners, and 175+ attack patterns. Features a built-in dashboard,…
 gmh5225/fakeenclave
Proof-of-concept that abuses Windows Enclave to implement anti-tamper and anti-cheat evasion techniques at the driver level.
 0vercl0k/kepaboo
Neutralize KEPServerEX anti-debugging techniques
 mwhammadrezss/midonescanner-android
Scanner CDN Detection, Real Bandwidth Test, Throttle Detection
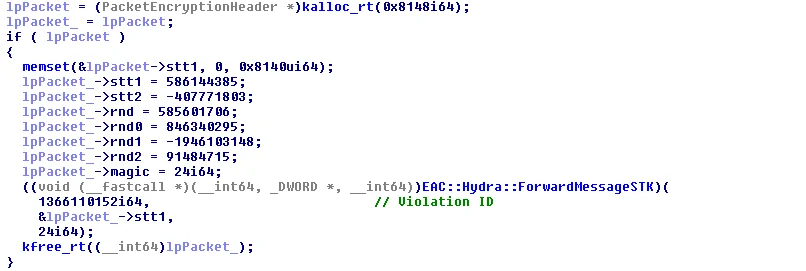 gmh5225/eac-kernel-packet-fucker
Reverse-engineered Easy Anti-Cheat kernel driver bypass that intercepts memory allocation to suppress violation packets, with report decryption…
 theqmaks/resolver
This extension integrates popular CAPTCHA solution services into BurpSuite to process different types of CAPTCHAs without manual intervention.
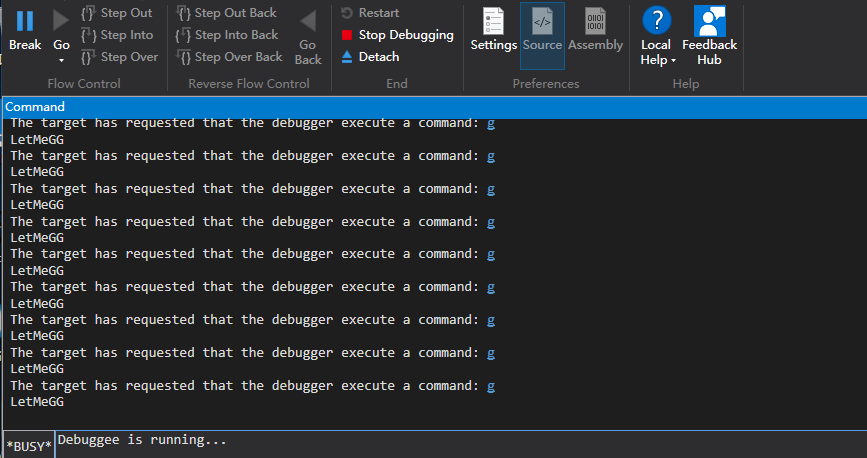 gmh5225/letmegg
Windows kernel proof-of-concept demonstrating an anti-debugging technique that prevents WinDbg from breaking by manipulating the kernel exception…