
aegis
 1llu50ry/aegis
Single-header C++20 software protection SDK with polymorphic VM code virtualization, compile-time MBA and string obfuscation, 25+ crypto primitives,…
anti-botbinary-analysiscryptography+6
3
1llu50ry/aegisSingle-header C++20 software protection SDK with polymorphic VM code virtualization, compile-time MBA and string obfuscation, 25+ crypto primitives,…
 gmh5225/mapped-dumper
A program written in C++ for remotely dumping manual mapped modules.
 gmh5225/lithium-kernel
Windows kernel-mode driver with user-mode client exposing IOCTL-based physical and virtual memory read/write, page table walking, pattern scanning,…
 justasmasiulis/lazy_importer
library for importing functions from dlls in a hidden, reverse engineer unfriendly way
 uazo/cromite
Hardened Chromium/Bromite fork for Android, Windows and Linux with built-in ad blocking, anti-fingerprinting mitigations and privacy-focused patches.
 akatorich/kernelflirt
Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
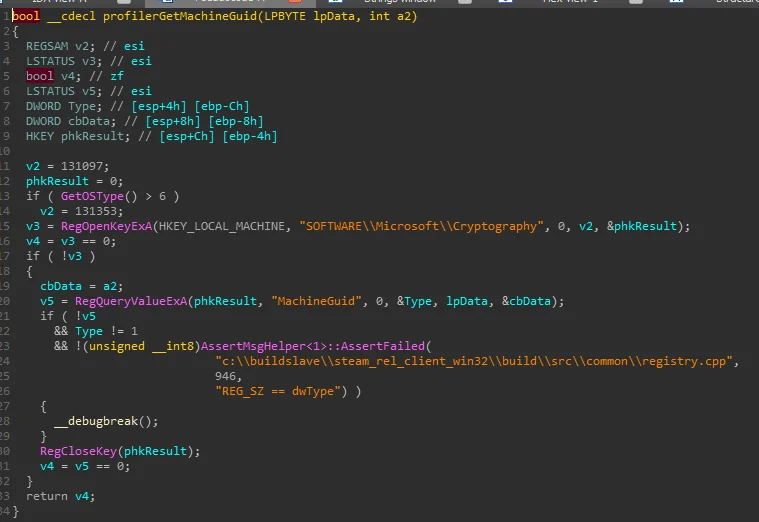 gmh5225/hwid-steamspywareterminator
Work-in-progress library injected into Steam to block the hidden CFillMachineInfoThread that collects HWID, disk, network adapter, and registry…
 notrequiem/antidbg
A stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering
 gmh5225/f31
Tool for hiding Kali Linux on the network
 gmh5225/fakeenclave
Proof-of-concept that abuses Windows Enclave to implement anti-tamper and anti-cheat evasion techniques at the driver level.
 ivankovic/stop-bots
Automate stopping bad bots from accessing your server
 kitsune-de/stealth_call
Header-only Windows x64 indirect syscall library. Zero CRT, zero IAT, VEH anti-BP, AMSI/ETW bypass, W^X memory, per-call dynamic stubs.
 openresty/lua-resty-limit-traffic
Lua library for limiting and controlling traffic in OpenResty/ngx_lua
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
 sarperavci/googlerecaptchabypass
Solve Google reCAPTCHA in less than 5 seconds! 🚀
 alphadelta/secure-desktop
Anti-keylogger/anti-rat application for Windows
 xkiian/awswaf
AWS WAF Solver, full reverse implemented in 100% Python & Golang.
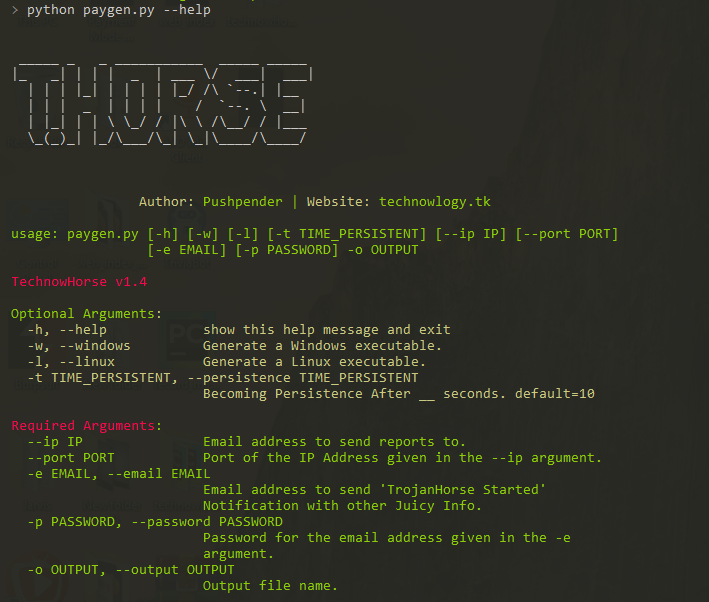 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.