
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
8 results
columbo preview

columbo

GitHubvisma-prodsec/columbo

ML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…

anomaly-detectionbinary-analysisdigital-forensics+3
61
4 years ago
patriot preview

patriot

GitHubjoe-desimone/patriot

In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…
anomaly-detectionbinary-analysisdefensive-tools+3
1644 years ago
SysTrace preview

SysTrace

GitHubtracebyte8/systrace

Linux system-call monitor using ptrace to trace file, process, network, and memory activity, with namespace isolation and machine learning…
anomaly-detectiondynamic-analysis-sandboxingmachine-learning+1
2426 days ago
WindowsMemPageDelta preview

WindowsMemPageDelta

GitHubnccgroup/windowsmempagedelta

A Microsoft Windows service to provide telemetry on Windows executable memory page changes to facilitate threat detection
anomaly-detectiondefensive-toolslog-analysis+1
335 years ago
MemProcFS-Analyzer preview

MemProcFS-Analyzer

GitHublethal-forensics/memprocfs-analyzer

Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
anomaly-detectiondigital-forensicsincident-response+5
73727 days ago
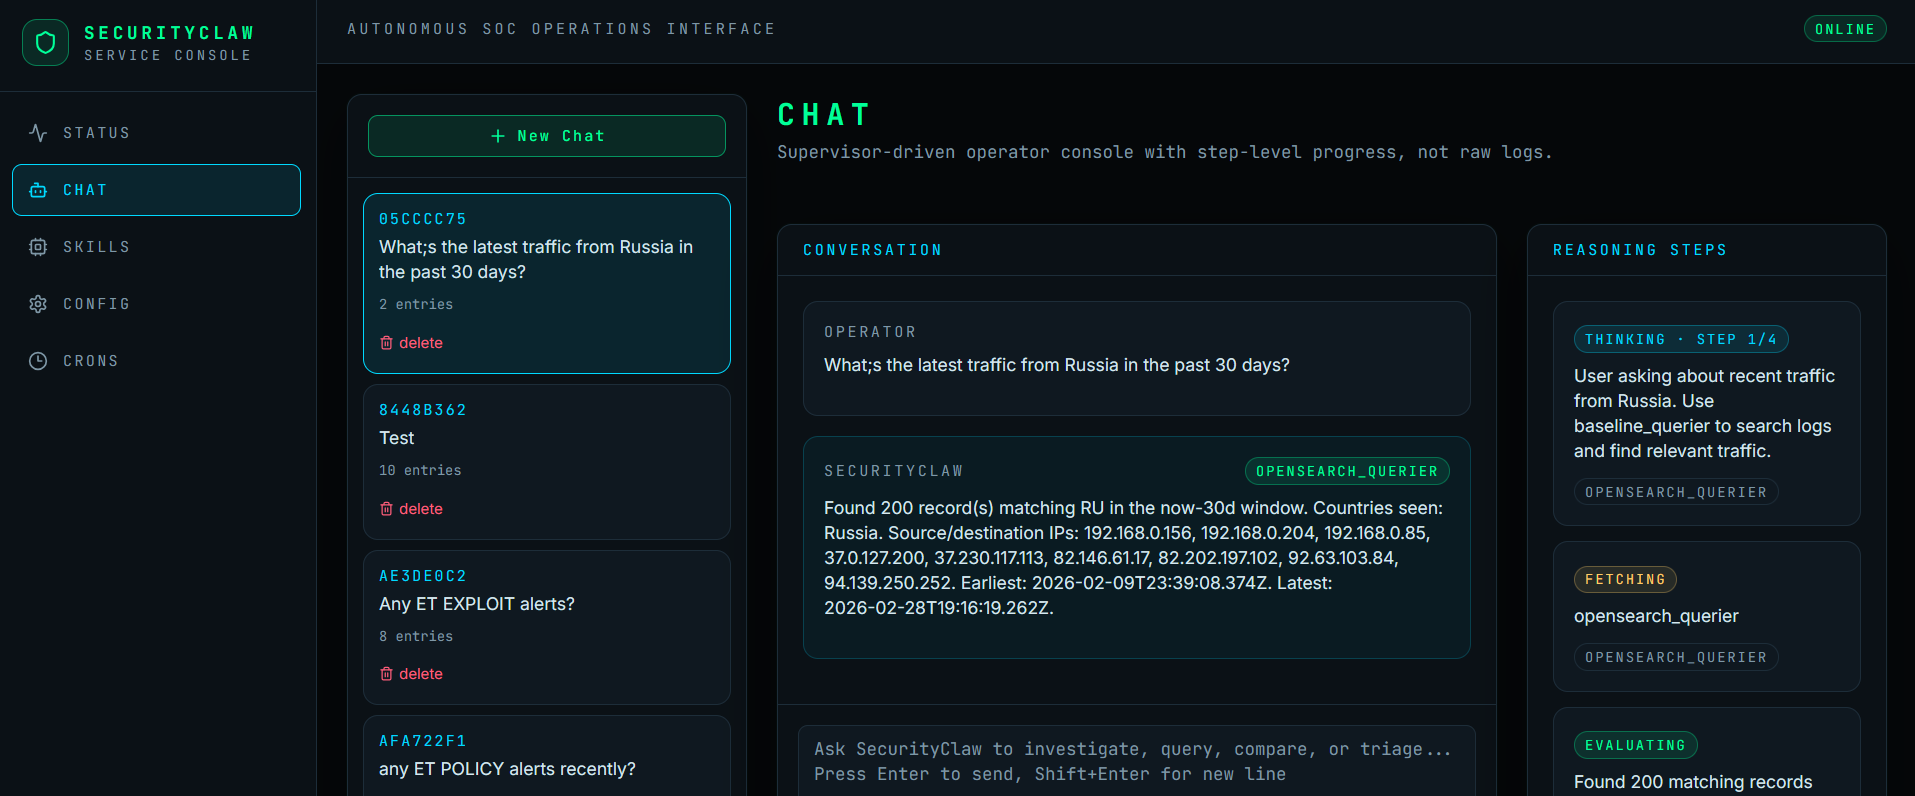
SecurityClaw preview

SecurityClaw

GitHubsecurityclaw/securityclaw

A modular, skill-based autonomous Security Operations Center (SOC) agent that monitors OpenSearch/Elasticsearch data, builds RAG-based behavioral…
ai-securityanomaly-detectionforensics+8
2722 months ago
MappedImagesDetector preview

MappedImagesDetector

GitHubadem-hosni/mappedimagesdetector

Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk
anomaly-detectionbinary-analysisdefensive-tools+4
18 months ago
0xGUARD preview

0xGUARD

GitHubgmh5225/0xguard

Simple Anti-cheat library for applications that use C++ on windows. #PastedProtection

anomaly-detectionbinary-analysiscode-analysis+1
22 years ago