
PortEx
 struppigel/portex
Java library to analyse Portable Executable files with a special focus on malware analysis and PE malformation robustness
anomaly-detectionbinary-analysisforensics+3
537
struppigel/portexJava library to analyse Portable Executable files with a special focus on malware analysis and PE malformation robustness
 theflink/hunt-weird-syscalls
ETW based POC to identify direct and indirect syscalls
 0xkirisame/spica
eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…
 joe-desimone/patriot
In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…
 amavis/amavis
amavis is a high-performance email content filter framework written in Perl.
 visma-prodsec/columbo
ML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…
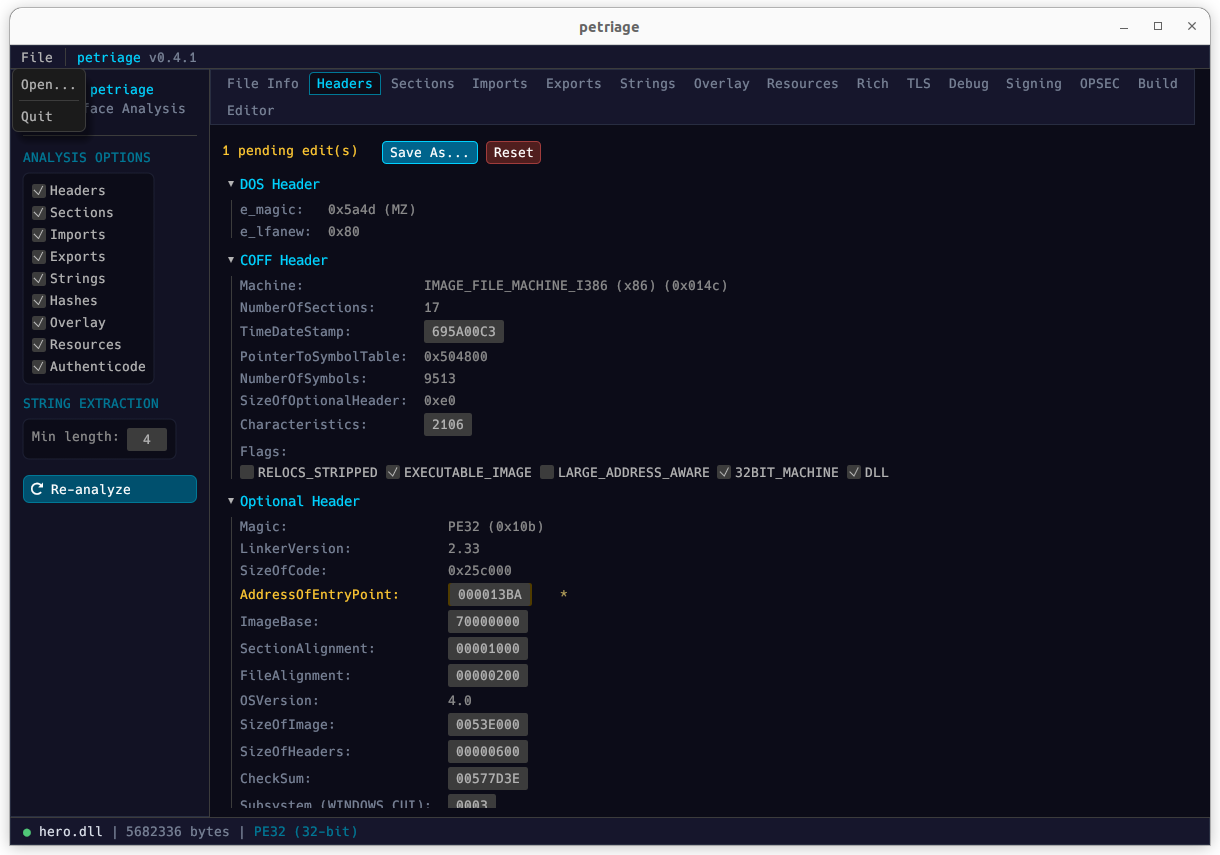 uky007/petriage
PETriage: A symbol-unified PE file reader for triage, built for multi-platform and multi-interface use.
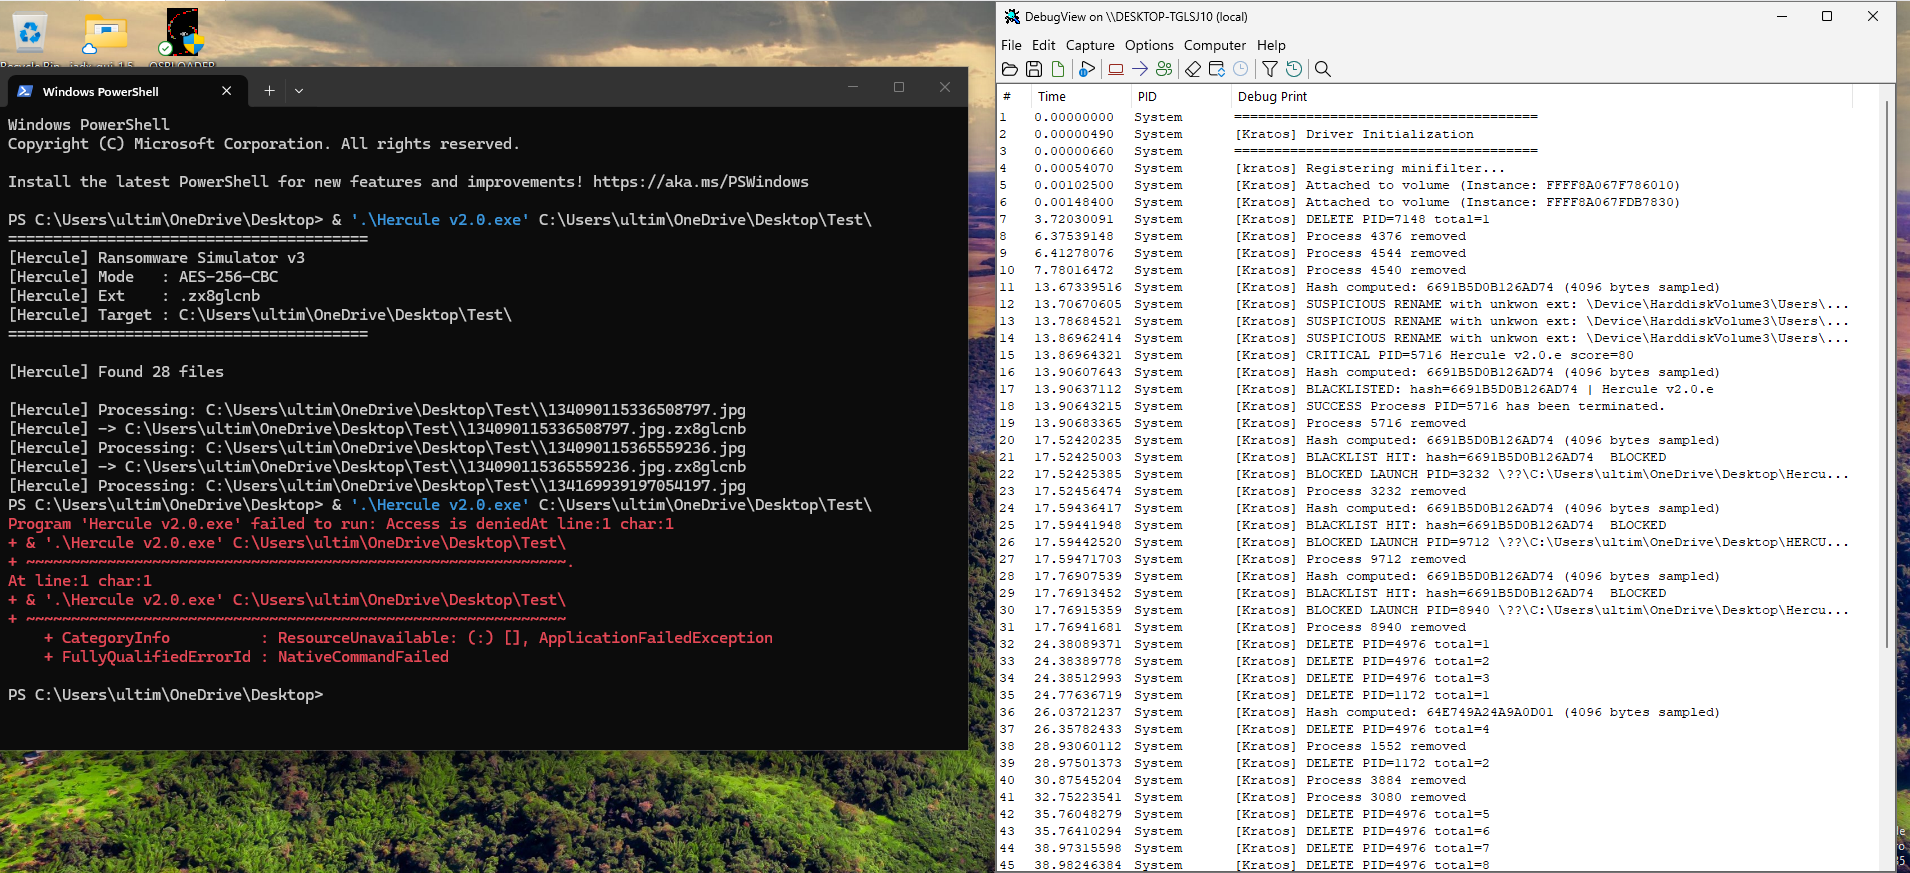 mukendi/kratosminifilter
Kratos is a high-performance Windows File System Minifilter driver designed to detect, block, and permanently immunize
 corelight/zeek-xor-exe-plugin
Zeek plugin to detect and decrypt XOR-encrypted EXEs
 corelight/zeek-quasarrat-detector
Zeek detector for QuasarRat
 malwaremorghulis/sunburst
Detection for SUNBURST C2 Stage-1 using Shannon Entropy
 corelight/zeek-asyncrat-detector
A Zeek based AsyncRAT malware detector.
 gmh5225/0xguard
Simple Anti-cheat library for applications that use C++ on windows. #PastedProtection
 adem-hosni/mappedimagesdetector
Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk