
ForensiX-Studio
 aquibpro/forensix-studio
Forensic intelligence platform that analyzes files, correlates threat indicators, maps behavior to MITRE ATT&CK, and generates actionable security…
anomaly-detectiondigital-forensicsforensics+4
1
aquibpro/forensix-studioForensic intelligence platform that analyzes files, correlates threat indicators, maps behavior to MITRE ATT&CK, and generates actionable security…
 osquery/osquery
SQL powered operating system instrumentation, monitoring, and analytics.
 struppigel/portex
Java library to analyse Portable Executable files with a special focus on malware analysis and PE malformation robustness
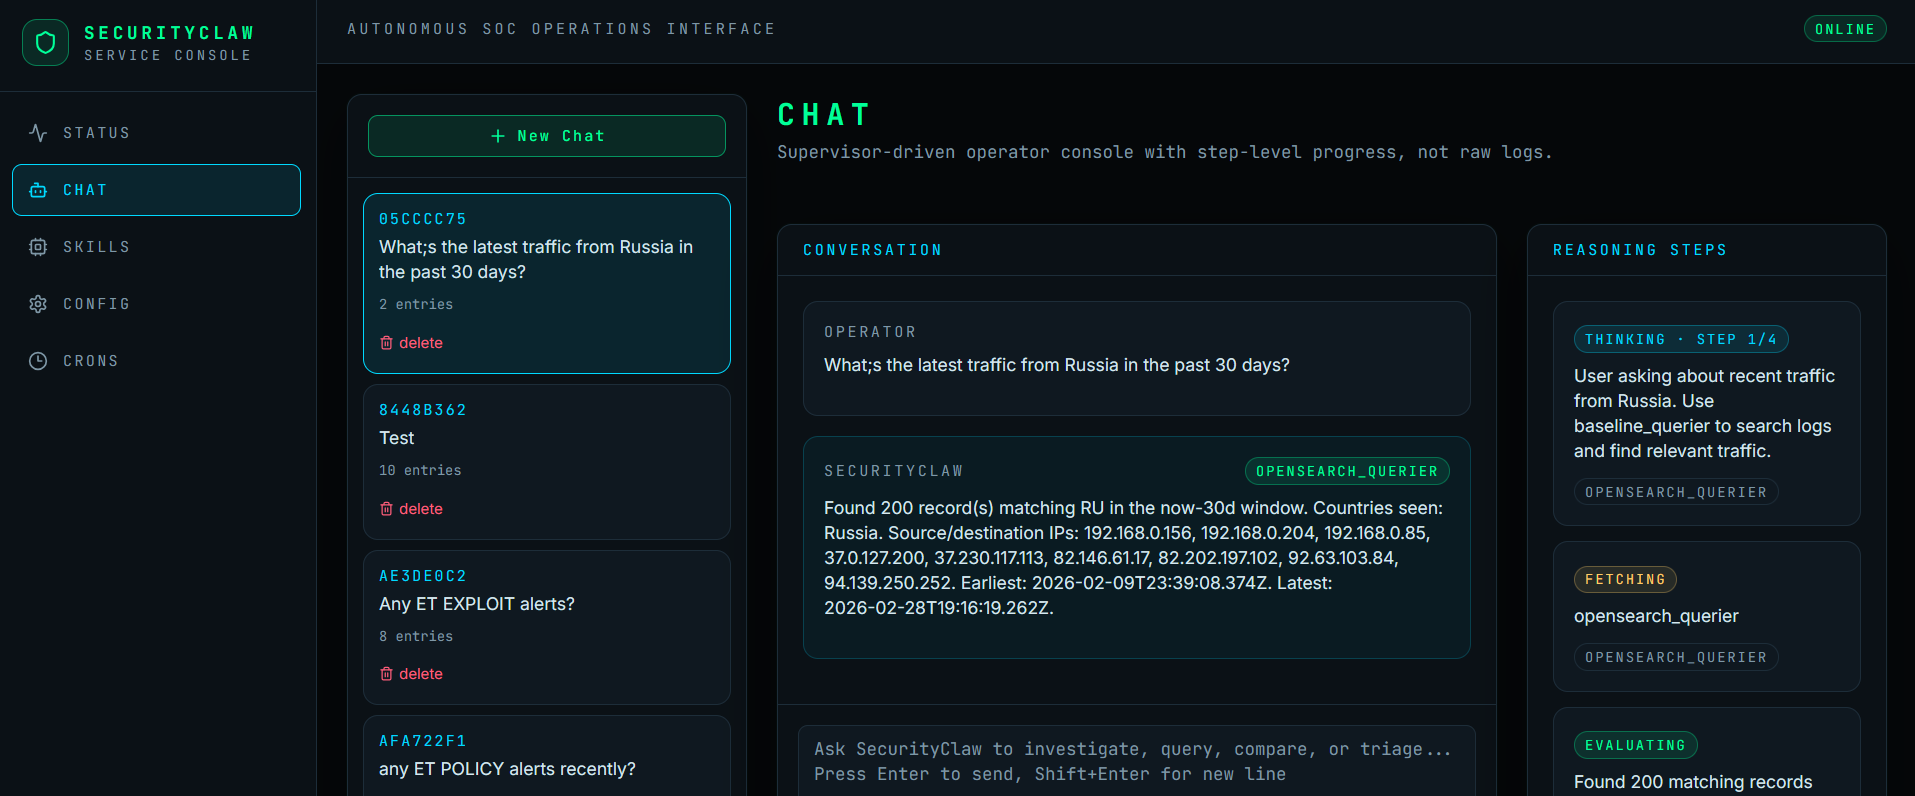 securityclaw/securityclaw
A modular, skill-based autonomous Security Operations Center (SOC) agent that monitors OpenSearch/Elasticsearch data, builds RAG-based behavioral…
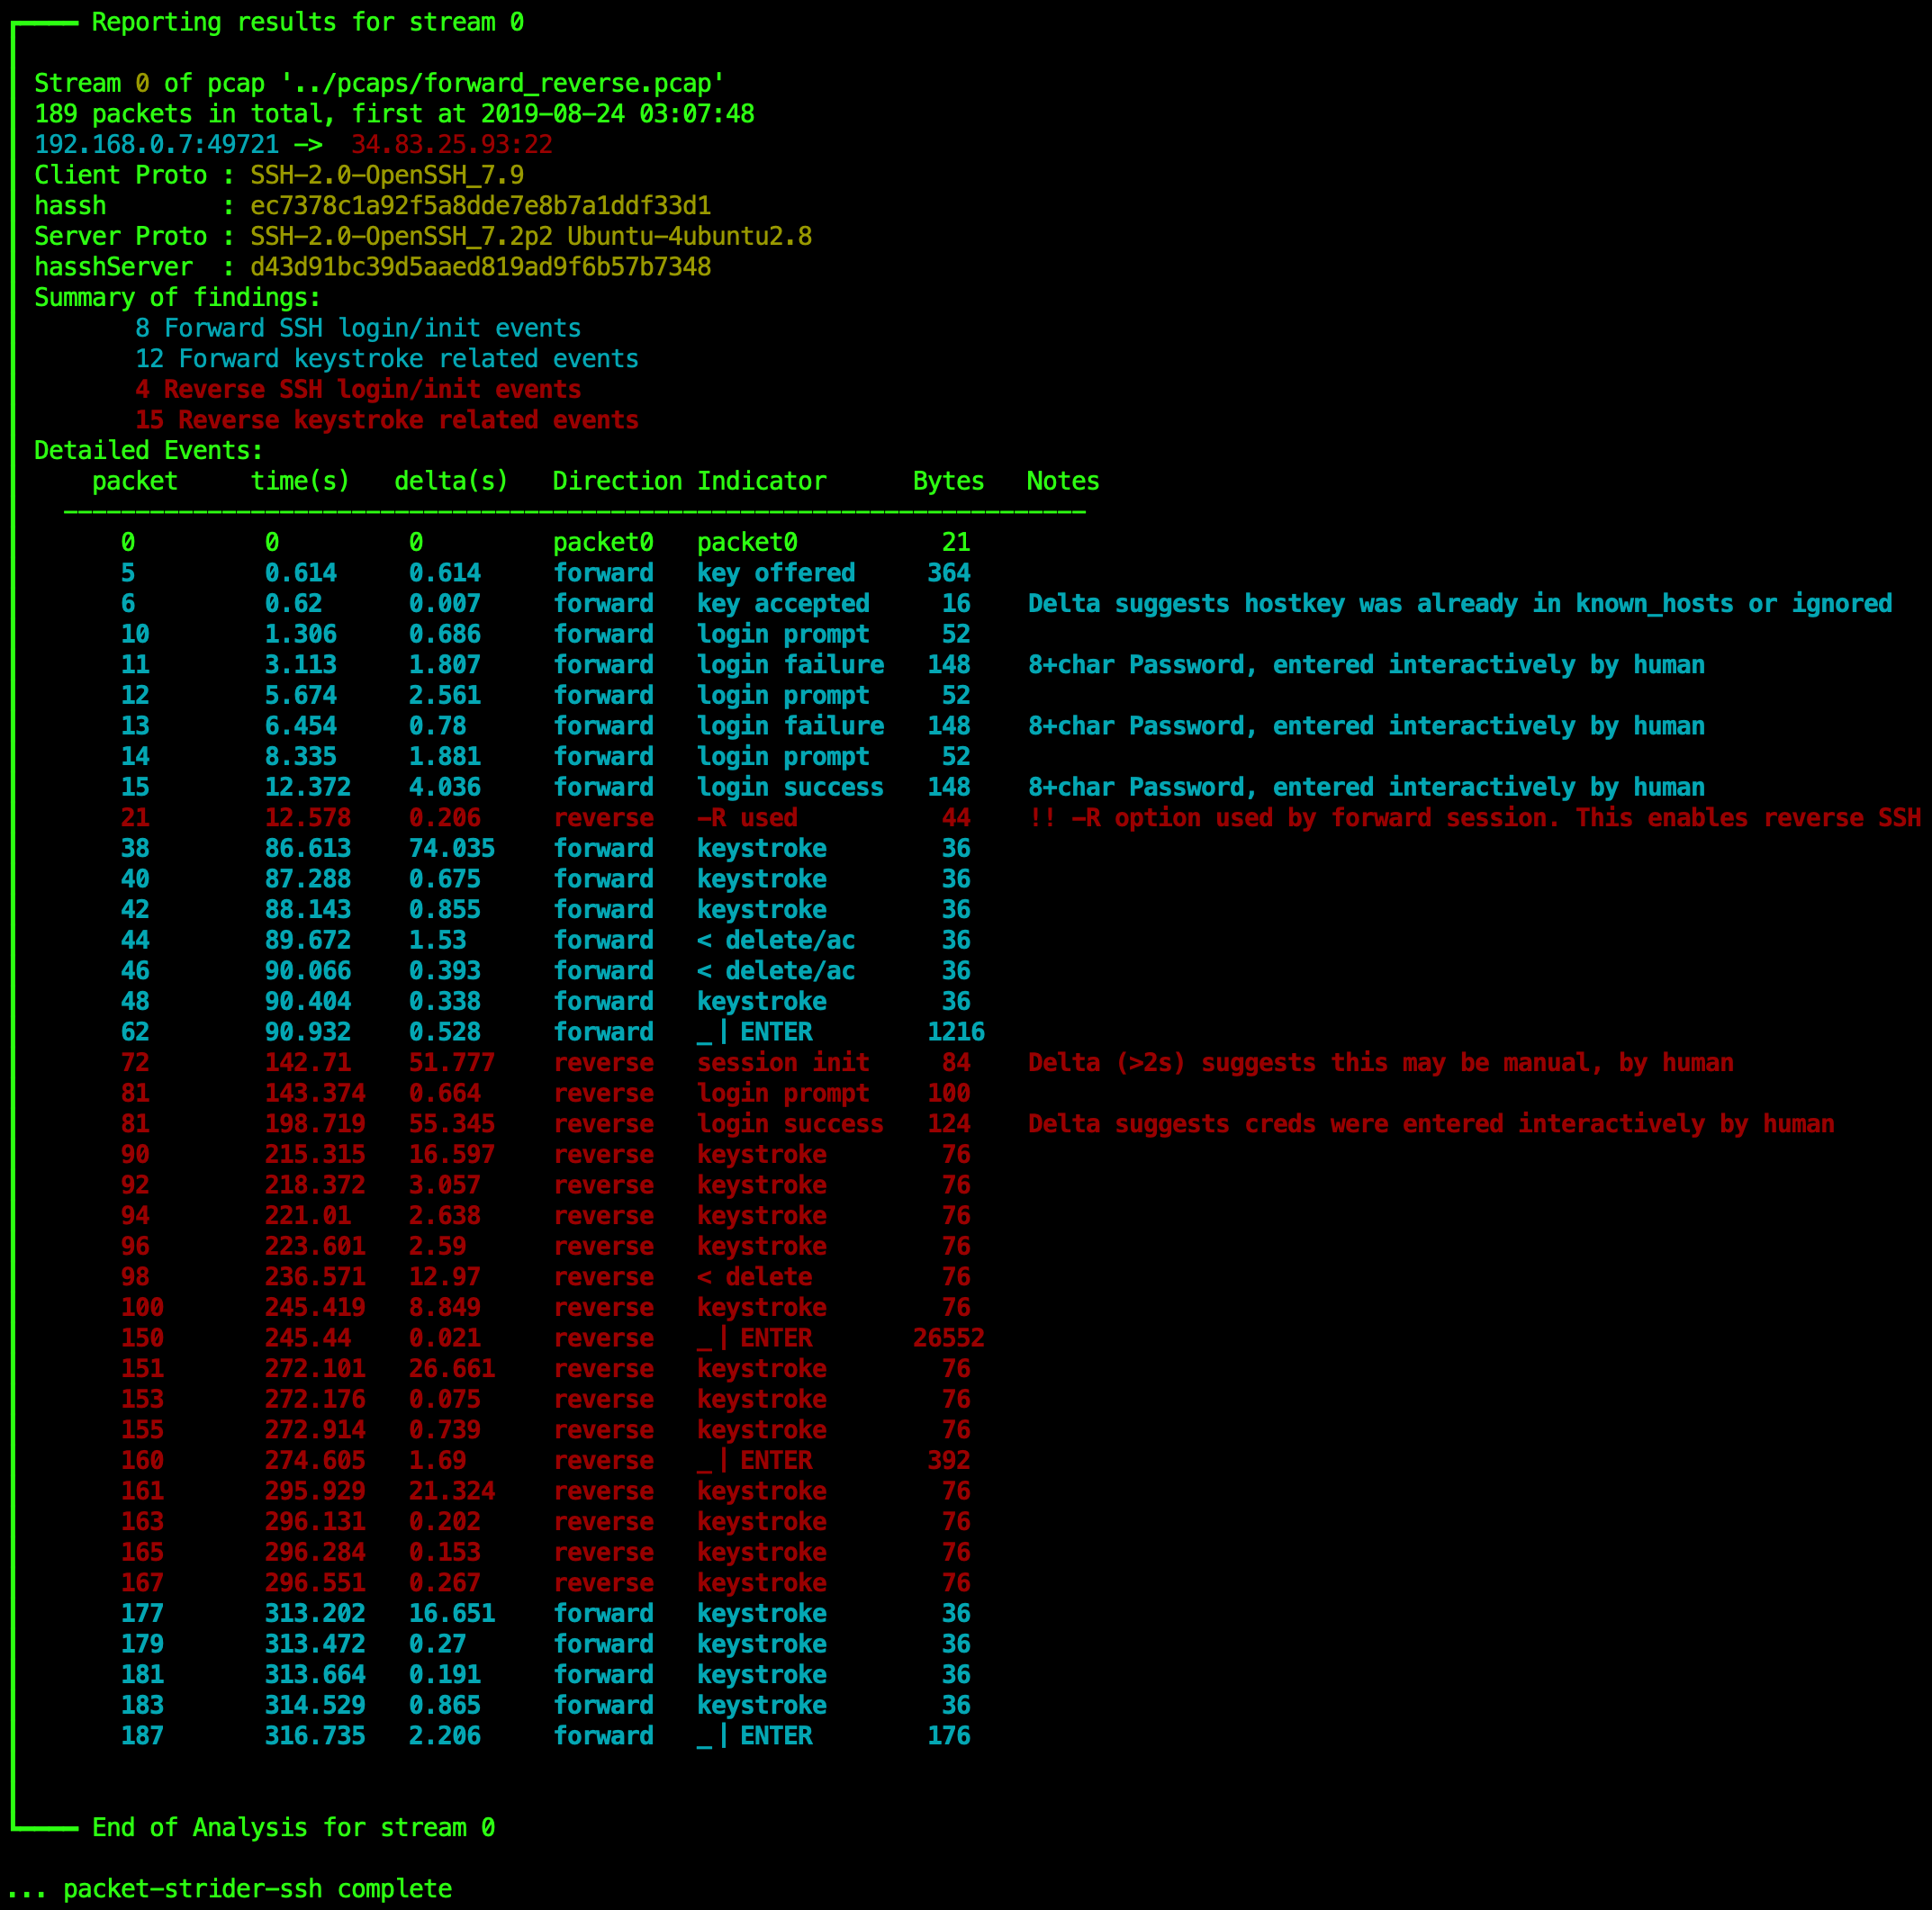 benjeems/packetstrider
A network packet forensics tool for SSH
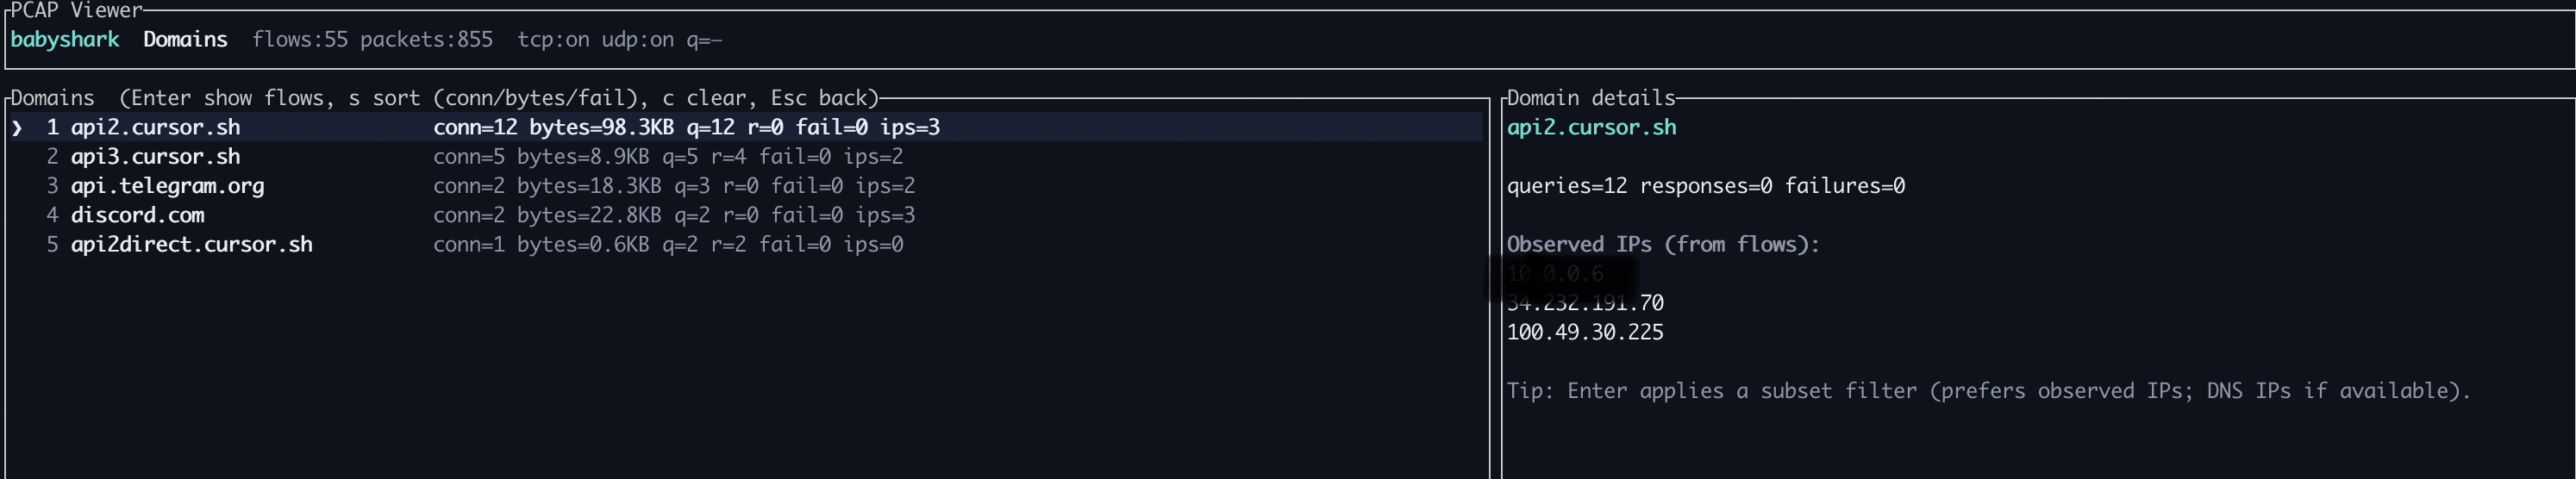 vignesh07/babyshark
Flows-first PCAP TUI (case files, gorgeous UX). Do do do do.
 nccgroup/detectwindowscopyonwriteforapi
Enumerate various traits from Windows processes as an aid to threat hunting
 visma-prodsec/columbo
ML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…
 camp0/aiengine
Programmable packet inspection engine with NIDS, DNS classification, frequency analysis, and auto-regex generation. Supports Python/Ruby/Java/Lua…
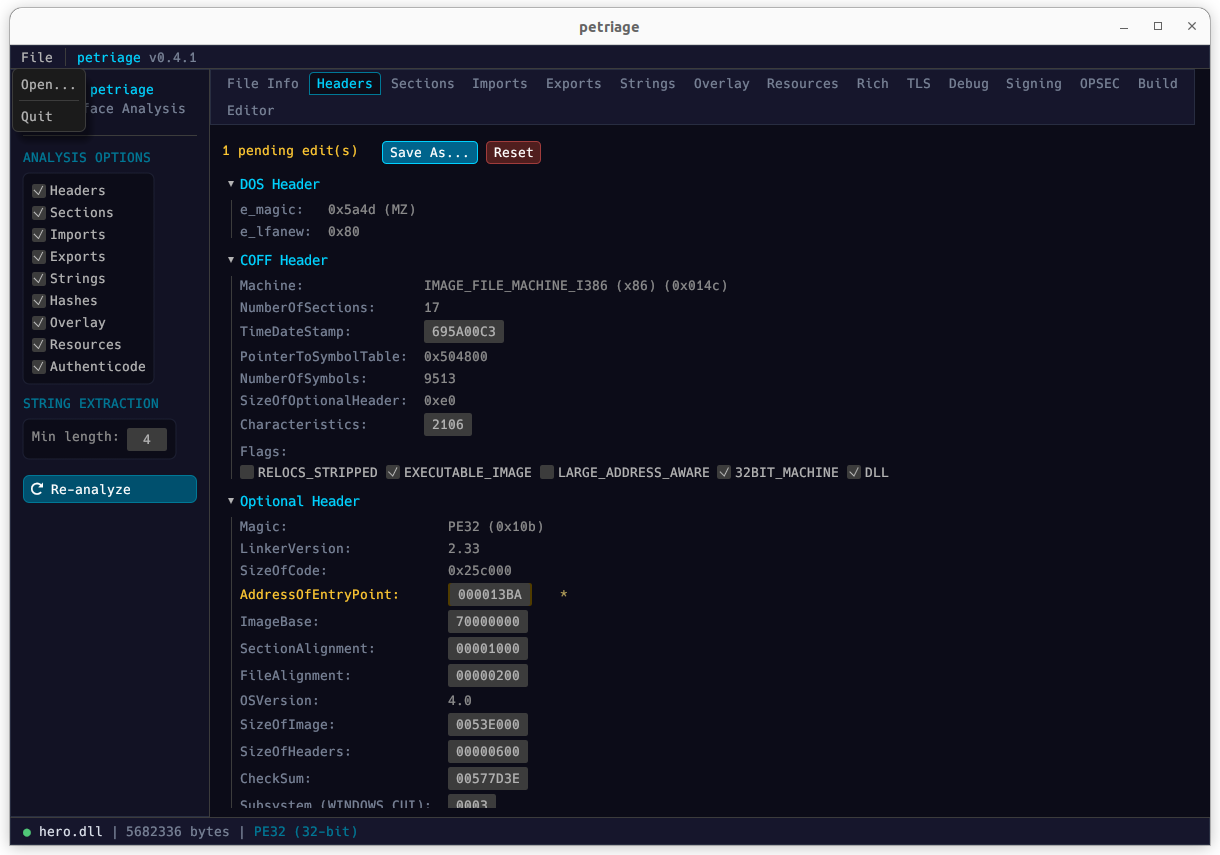 uky007/petriage
PETriage: A symbol-unified PE file reader for triage, built for multi-platform and multi-interface use.
 nccgroup/impossibletravelloganalysis
Basic log analysis tool to detect impossible travel via IP address geographic information
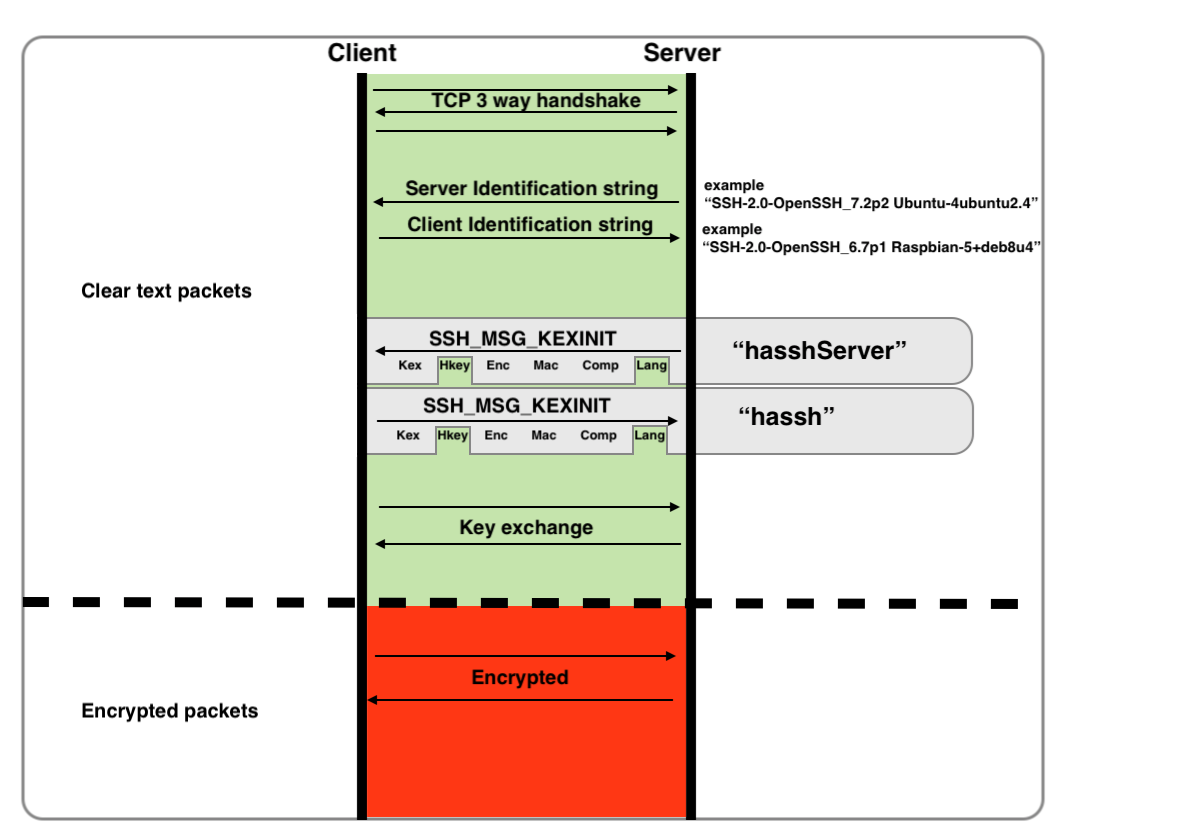 corelight/hassh
Fingerprint SSH clients and servers.
 gmh5225/maldec-edr
Unix endpoint detection and response solution using kernel-level mechanisms to detect anomalies and malware attacks in real time.
 salesforce/hassh
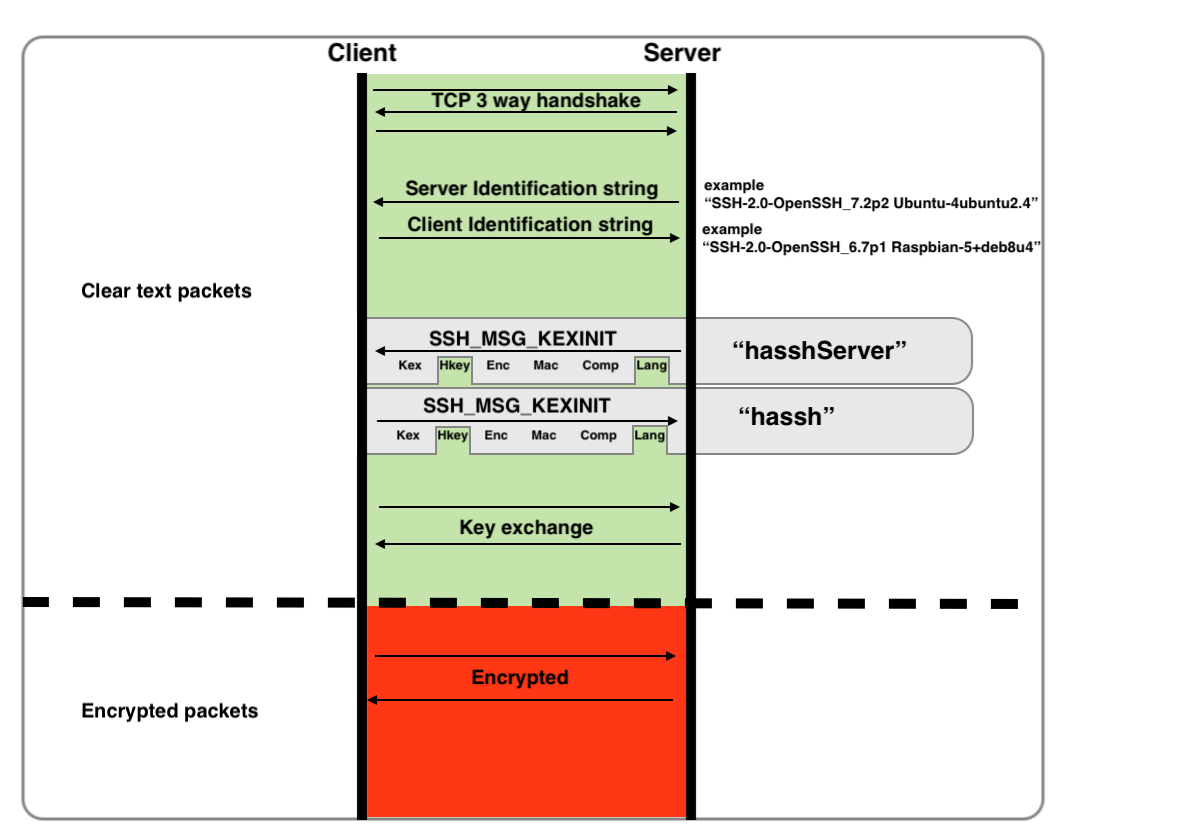
HASSH is a network fingerprinting standard which can be used to identify specific Client and Server SSH implementations. The fingerprints can be…
 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 functori/argos/argos
Analysis and Representation of Graphs of Suspicious Operations (Analyse et Représentation des Graphes des Opérations Suspectes)