

maltrail
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
anomaly-detectionanti-botdefensive-tools+11
8.6k
stamparm/maltrailReal-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 francescopace/espectre
ESPectre - Motion detection system based on Wi-Fi spectre analysis (CSI), with Home Assistant integration.
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
 osquery/osquery
SQL powered operating system instrumentation, monitoring, and analytics.
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
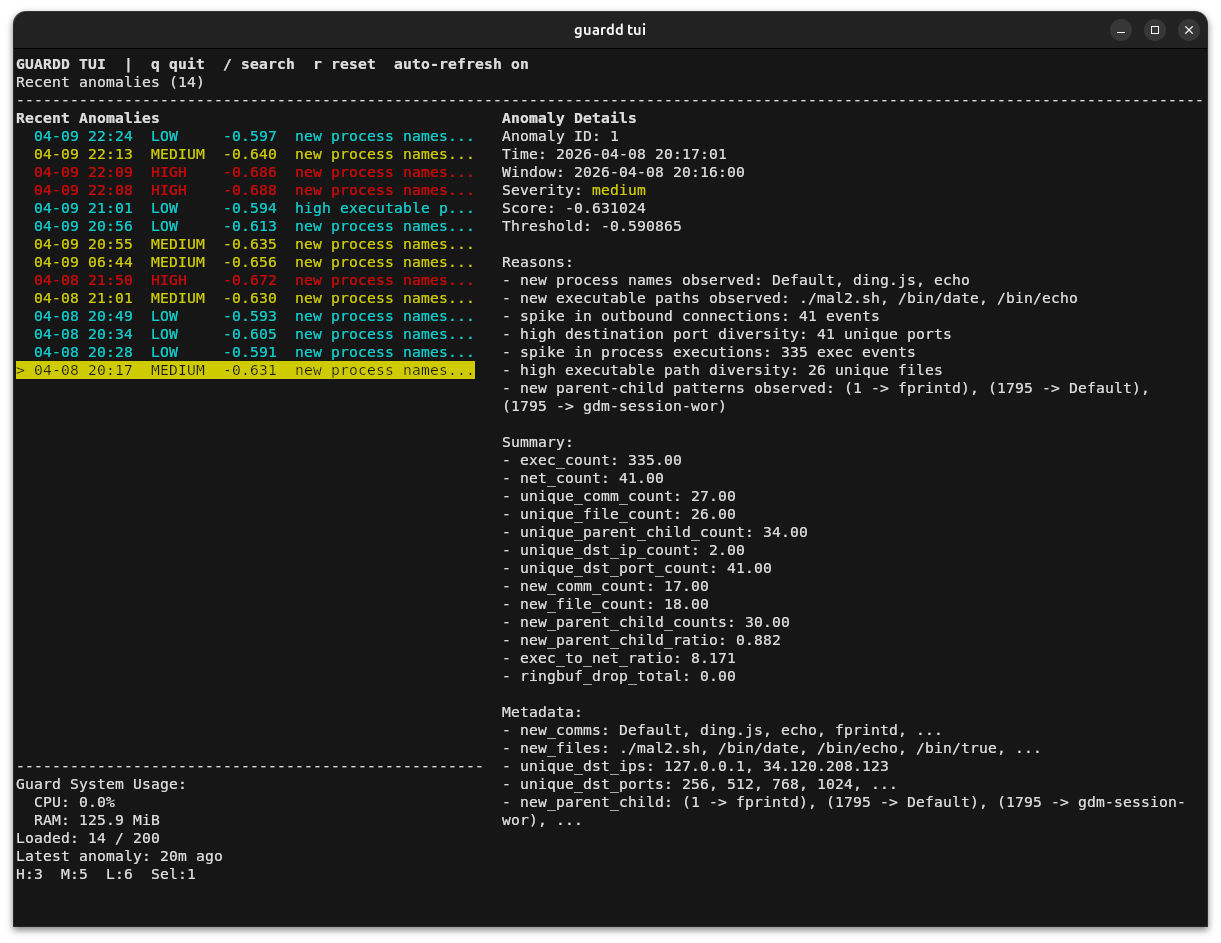 benny-e/guardd
ML-Based behavioral endpoint detection system for Linux machines
 ziad-hsn/cpra
CPRA is a high-performance infrastructure monitoring system designed for platform teams managing large-scale microservice architectures. Built on…
 vedantk6403/koobe-guard
Linux kernel module using Kprobes to detect and neutralize CVE-2024-1086 heap double-free exploits via temporal gap tracking and active register…
 0xkirisame/spica
eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…
 chainguard-dev/osquery-defense-kit
Production-ready detection & response queries for osquery
 abdeljalilait/kerneleye
Kernel-level security & attack response for Linux servers.
 reyjesusq/sentinel-mcp
Autonomous AI-powered cyber defense system using MCP, Gemini 2.0 Flash, Dynatrace observability and MongoDB. Google Cloud Hackathon submission.
 owasp/intrusion-alert-educational-network-ids
Lightweight Python-based IDS that monitors network traffic in real-time using Scapy, detecting DoS/DDoS attacks via per-IP request rate analysis with…
 safeagent-beihang/clawguard
Enterprise AI agent security toolkit providing pre-flight auditing, configuration hardening, runtime threat detection, and active defense against…
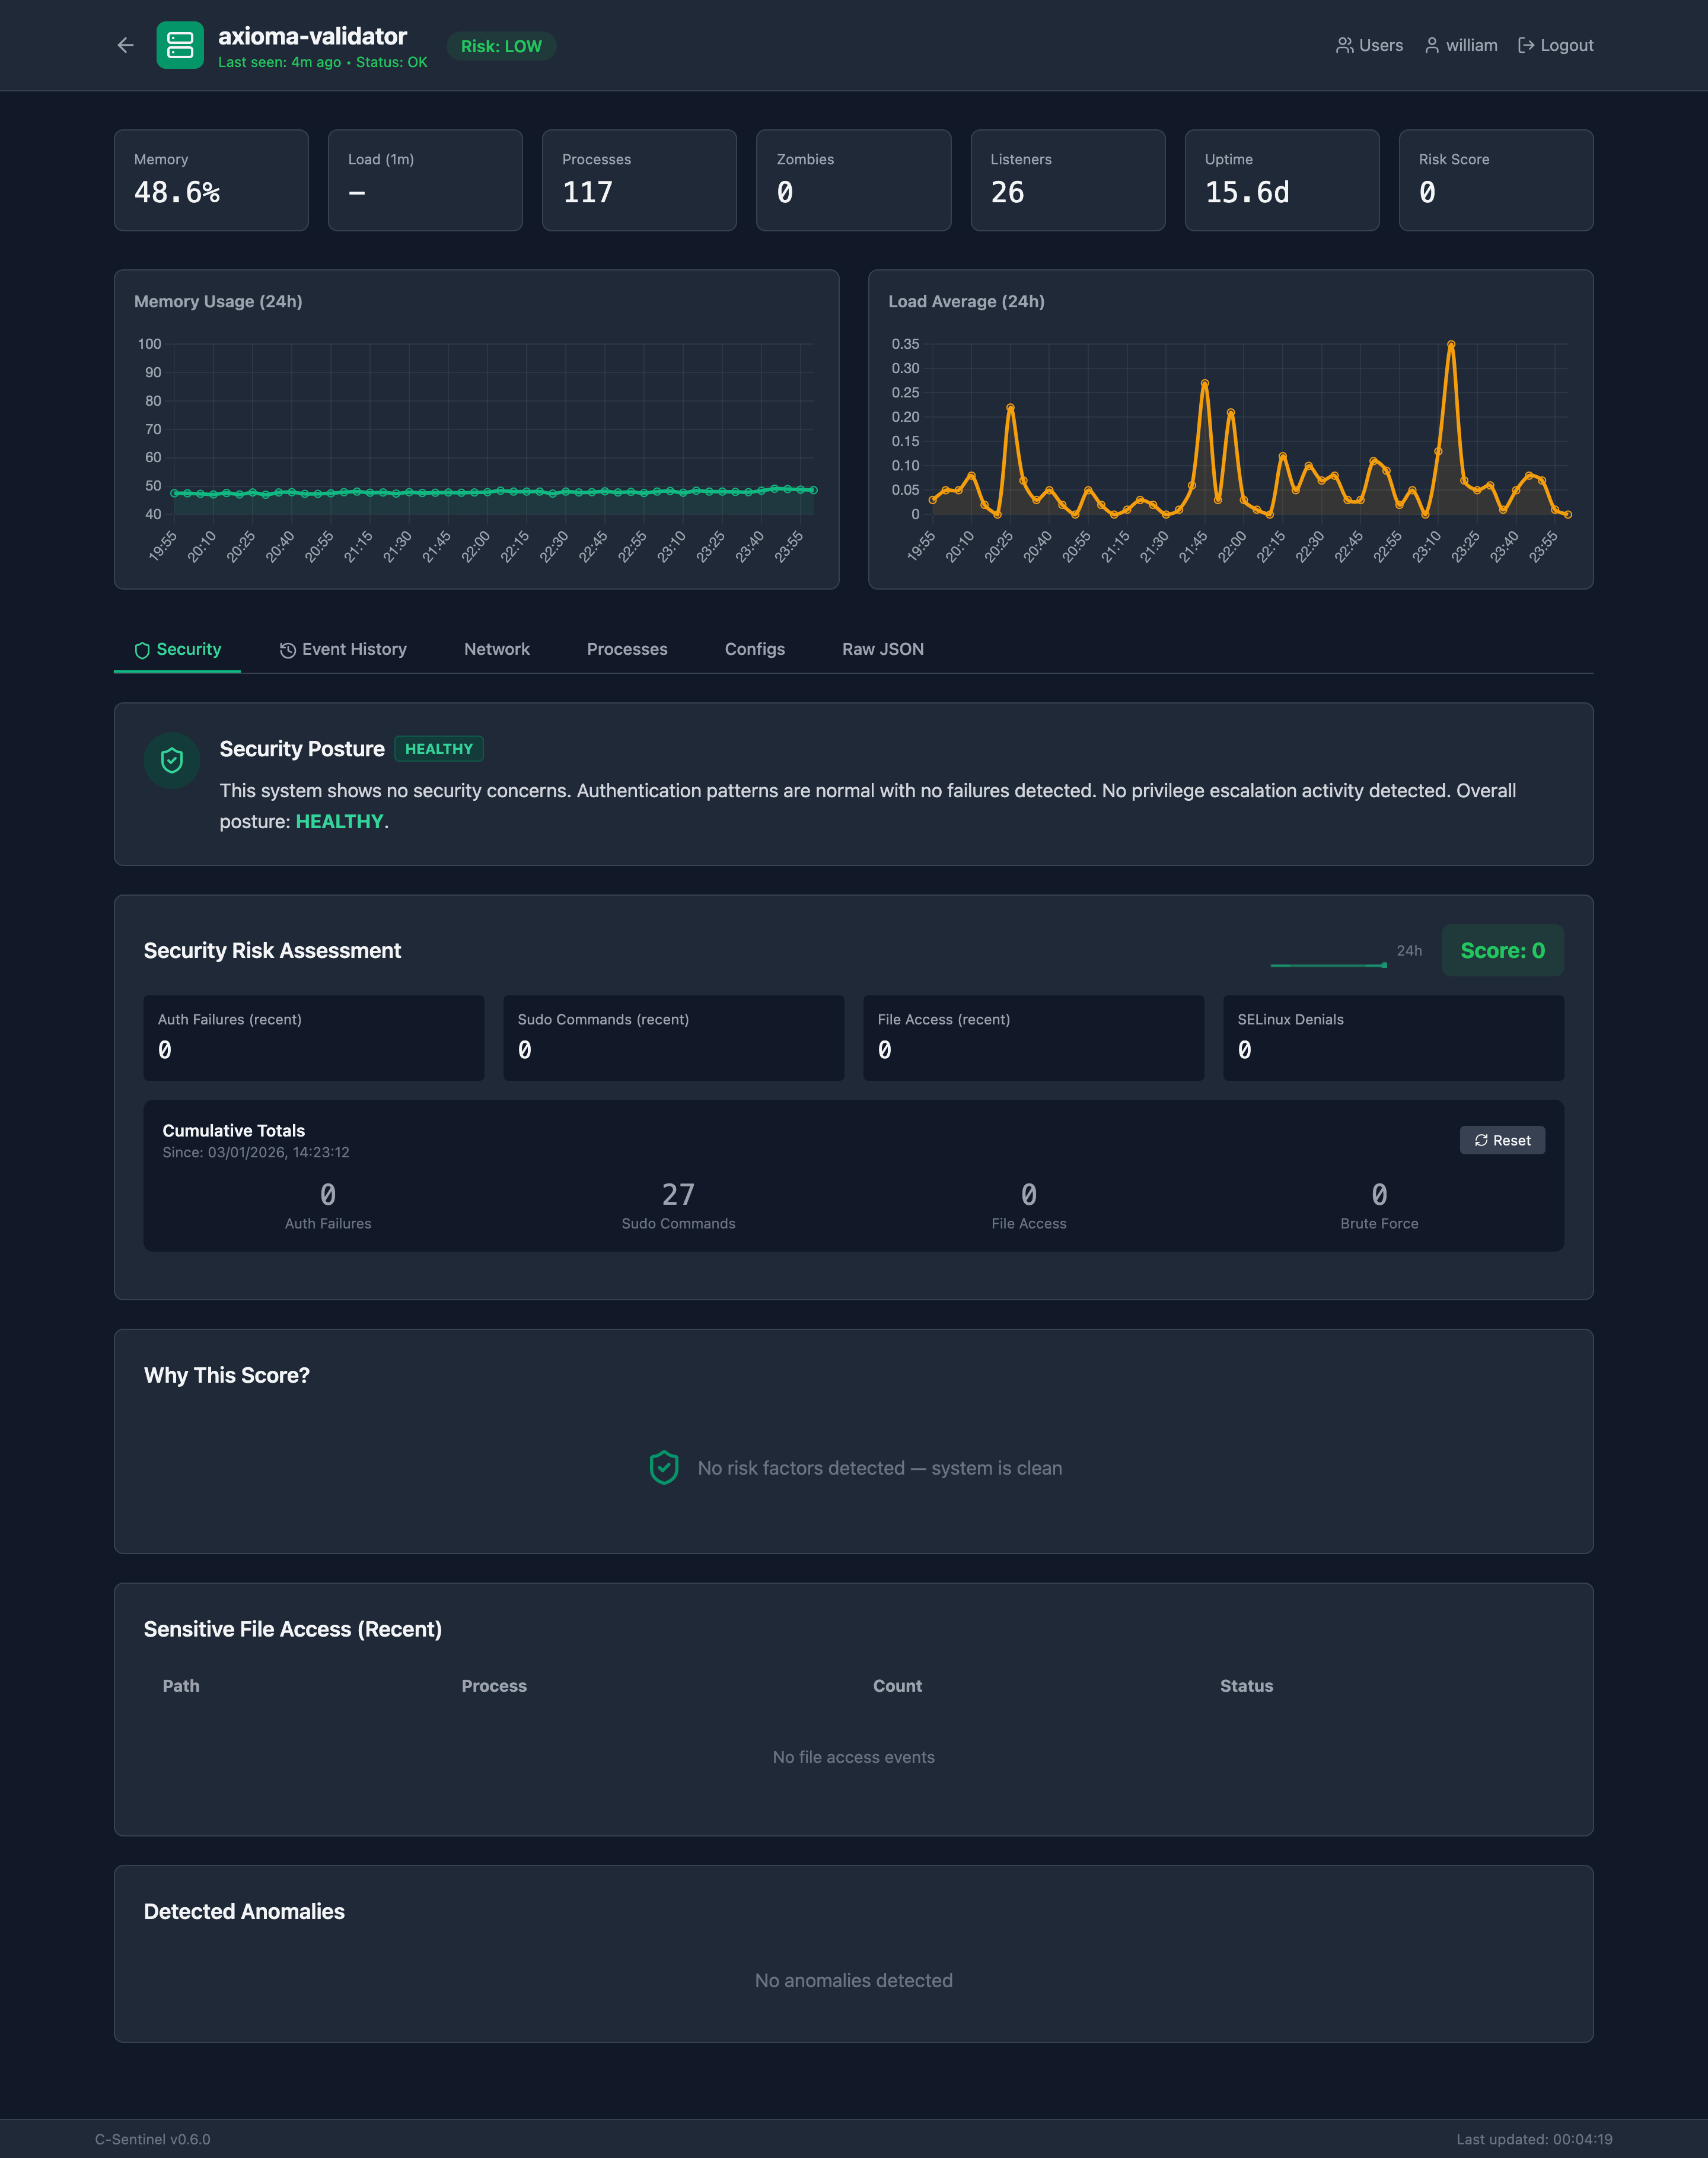 speytech/c-sentinel
Semantic Observability for UNIX Systems - A lightweight C-based system prober with AI-powered analysis
 0warn/defender
This is a bash script focus on hardening linux. This is a custom think of windows defender but unlike of their privacy issue. User can feel freedom…
 mcastens/alycon-threat-landscape
Training-free anomaly detection framework using Shannon Entropy, Fisher Information, and Wasserstein Distance to map system states into geometrically…
 cyberdudebivash/cyberdudebivash-5g-core-key-rotation-ghost-admin-auditor
Production-grade tool for detecting & remediating CVE-2026-0622 (Ghost Admin privilege escalation & master key exposure in 5G core software).