

Argos
 functori/argos/argos
Analysis and Representation of Graphs of Suspicious Operations (Analyse et Représentation des Graphes des Opérations Suspectes)
anomaly-detectiondigital-forensicsinformation-gathering+3
1
functori/argos/argosAnalysis and Representation of Graphs of Suspicious Operations (Analyse et Représentation des Graphes des Opérations Suspectes)
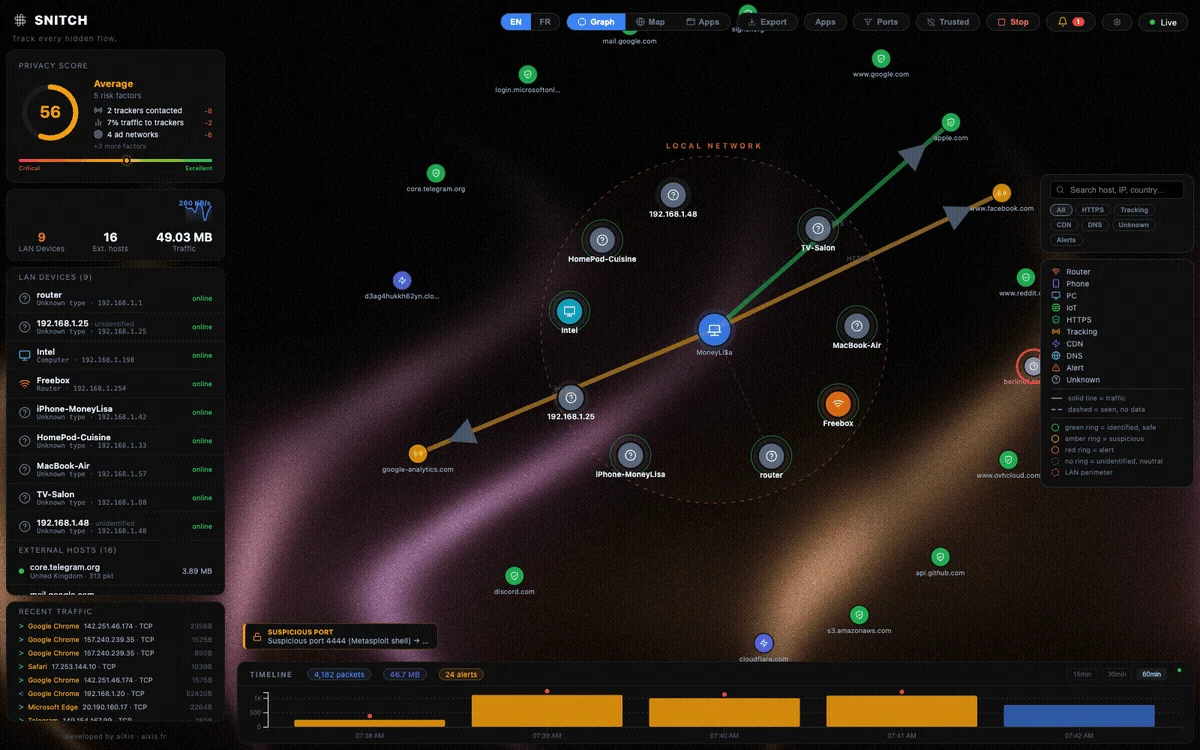
 aixisstudio/snitch
Real-time network monitor + outbound firewall — see & block every connection. Privacy-first, local-first, Rust fleet agent, SIEM exports, 8…
 dragon-lady/netward-standalone
User-space bot and DDoS deflection for small HTTP services
 kennbroorg/poorskeme
OSINT - Data Visualization - Blockchain - Awareness - Scam
 microlaser/dns_watchdog_windows2
PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…
 jamalrfordii-arch/vanguard-map
3D multi-domain tactical intelligence map — live ships, flights, satellites, cables & space weather in the browser. Time scrubbing, scenario replay,…
 mcastens/alycon-threat-landscape
Training-free anomaly detection framework using Shannon Entropy, Fisher Information, and Wasserstein Distance to map system states into geometrically…
 echowei/deeptraffic
Deep Learning models for network traffic classification
 pentagridsec/pentagridresponseoverview
Response Overview Extension for BurpSuite - Find exotic responses by grouping response bodies
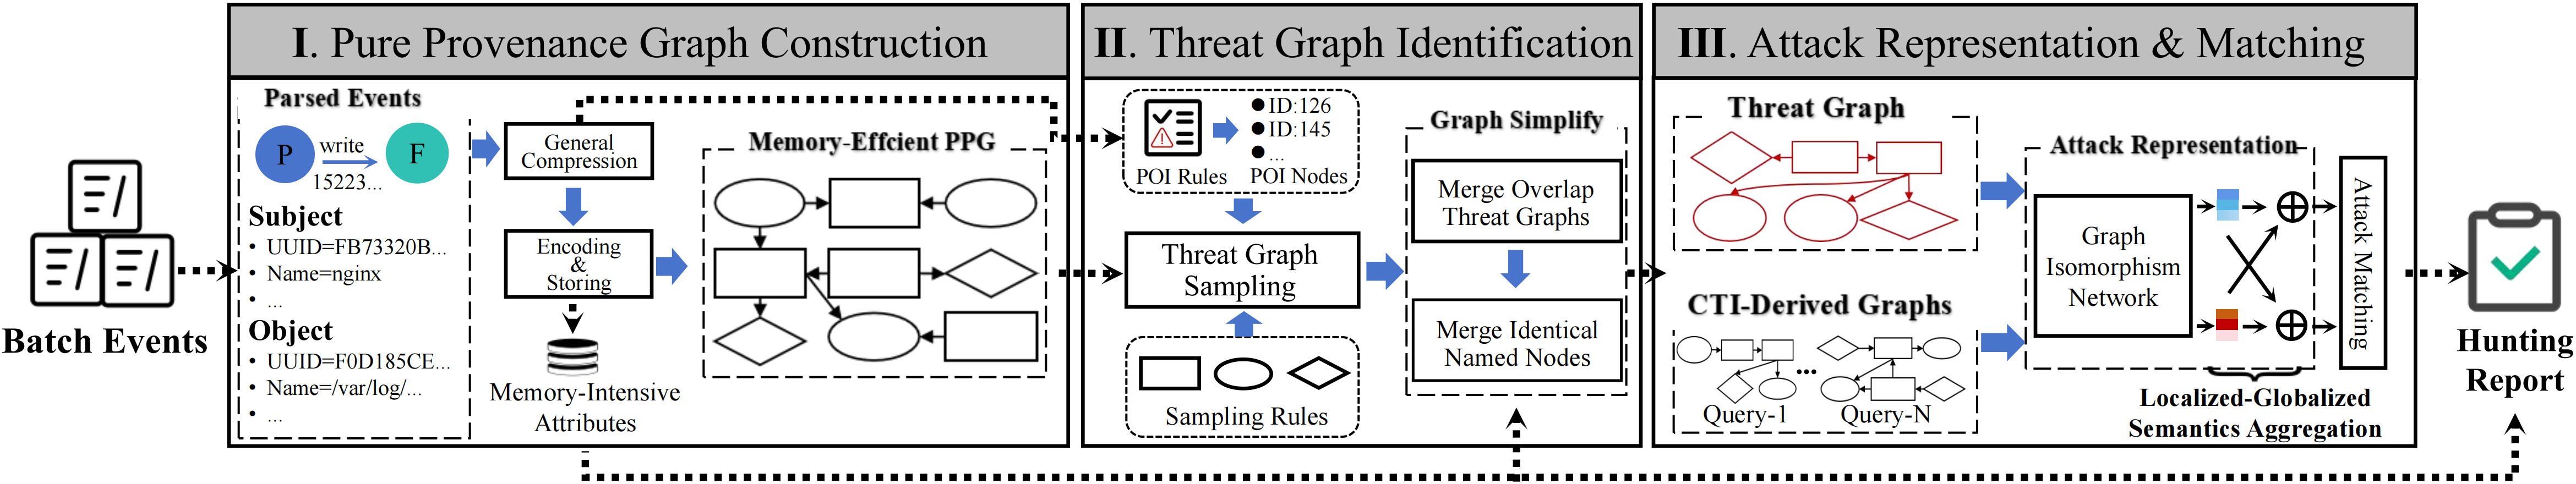 xueboqiu/prohunter
Graph-based threat detection system using inexact graph vector matching to compare threat graphs with CTI-derived attack query graphs for automated…
 itzmeshervin/siem-dashboard
A lightweight, real-time Security Information and Event Management (SIEM) dashboard built using Streamlit. It collects system logs, detects USB and…

 silverfort-open-source/latma
Collects and analyzes AD and Azure AD authentication logs to detect lateral movement attacks using graph-based anomaly detection, visualizing…
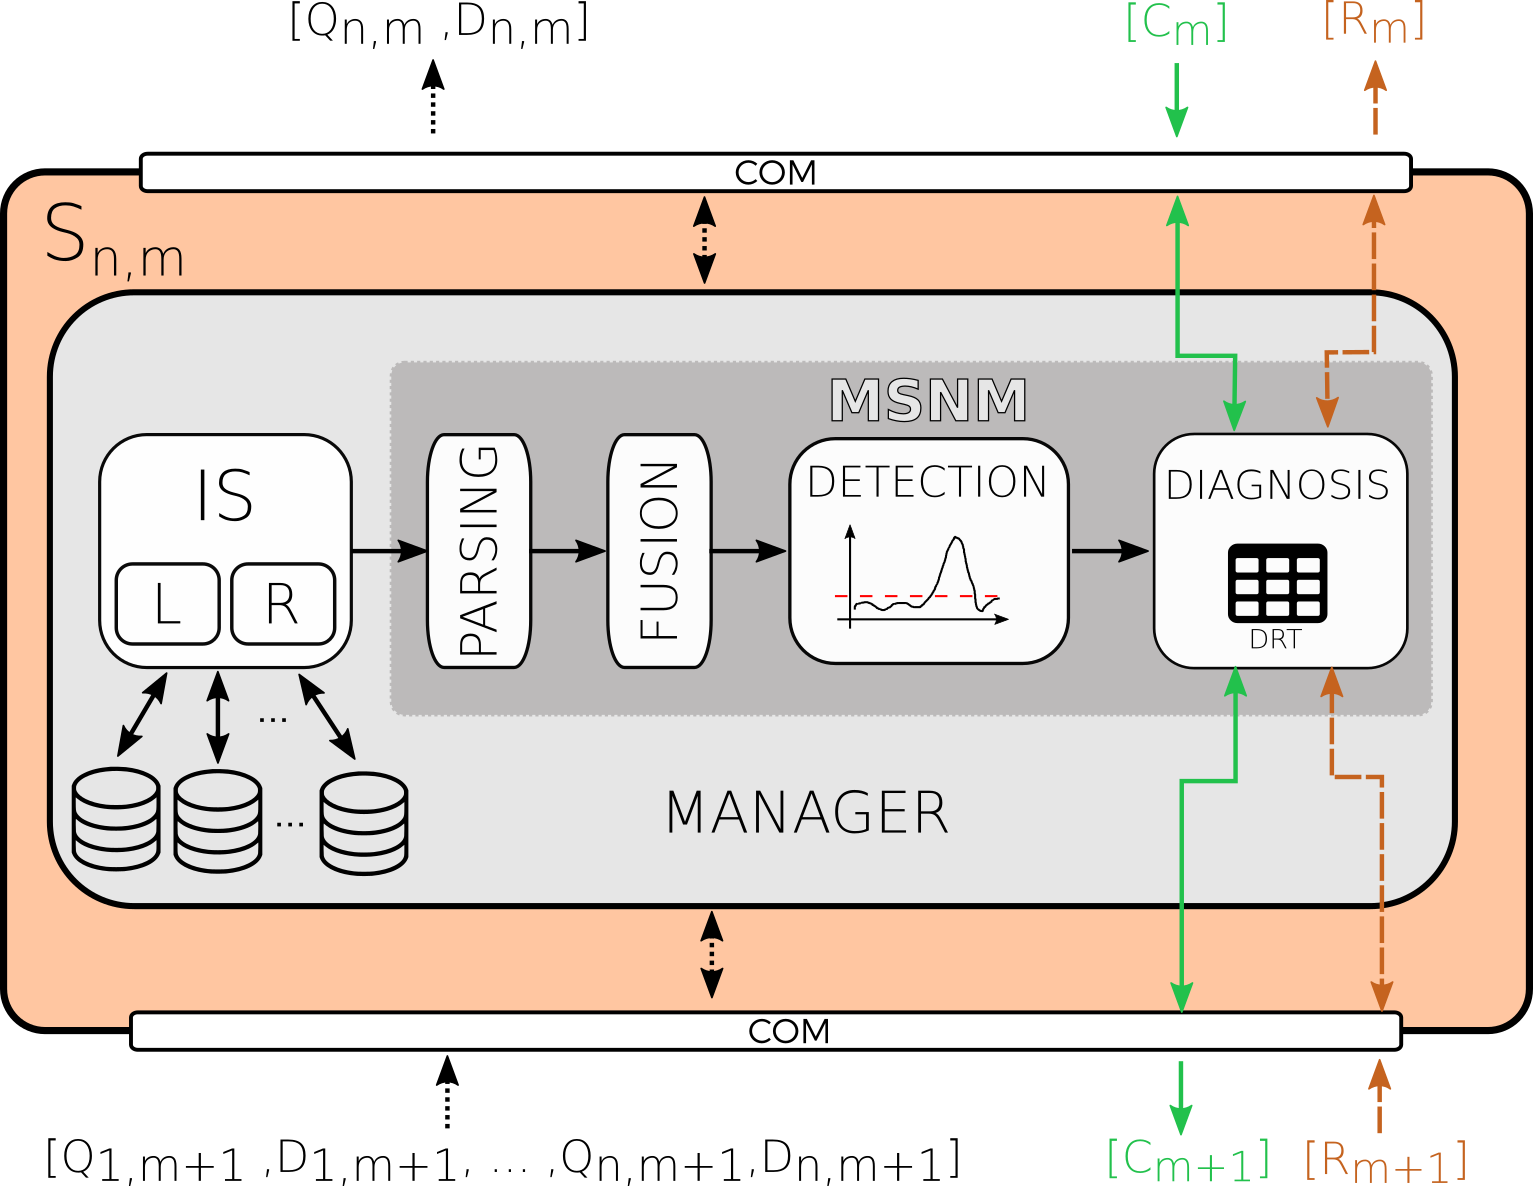 nesg-ugr/msnm-sensor
Multivariate statistical network monitoring sensor that detects anomalies using PCA-based techniques, aggregating lightweight statistics from…
 delvelabs/batea
AI-based, context-driven network device ranking
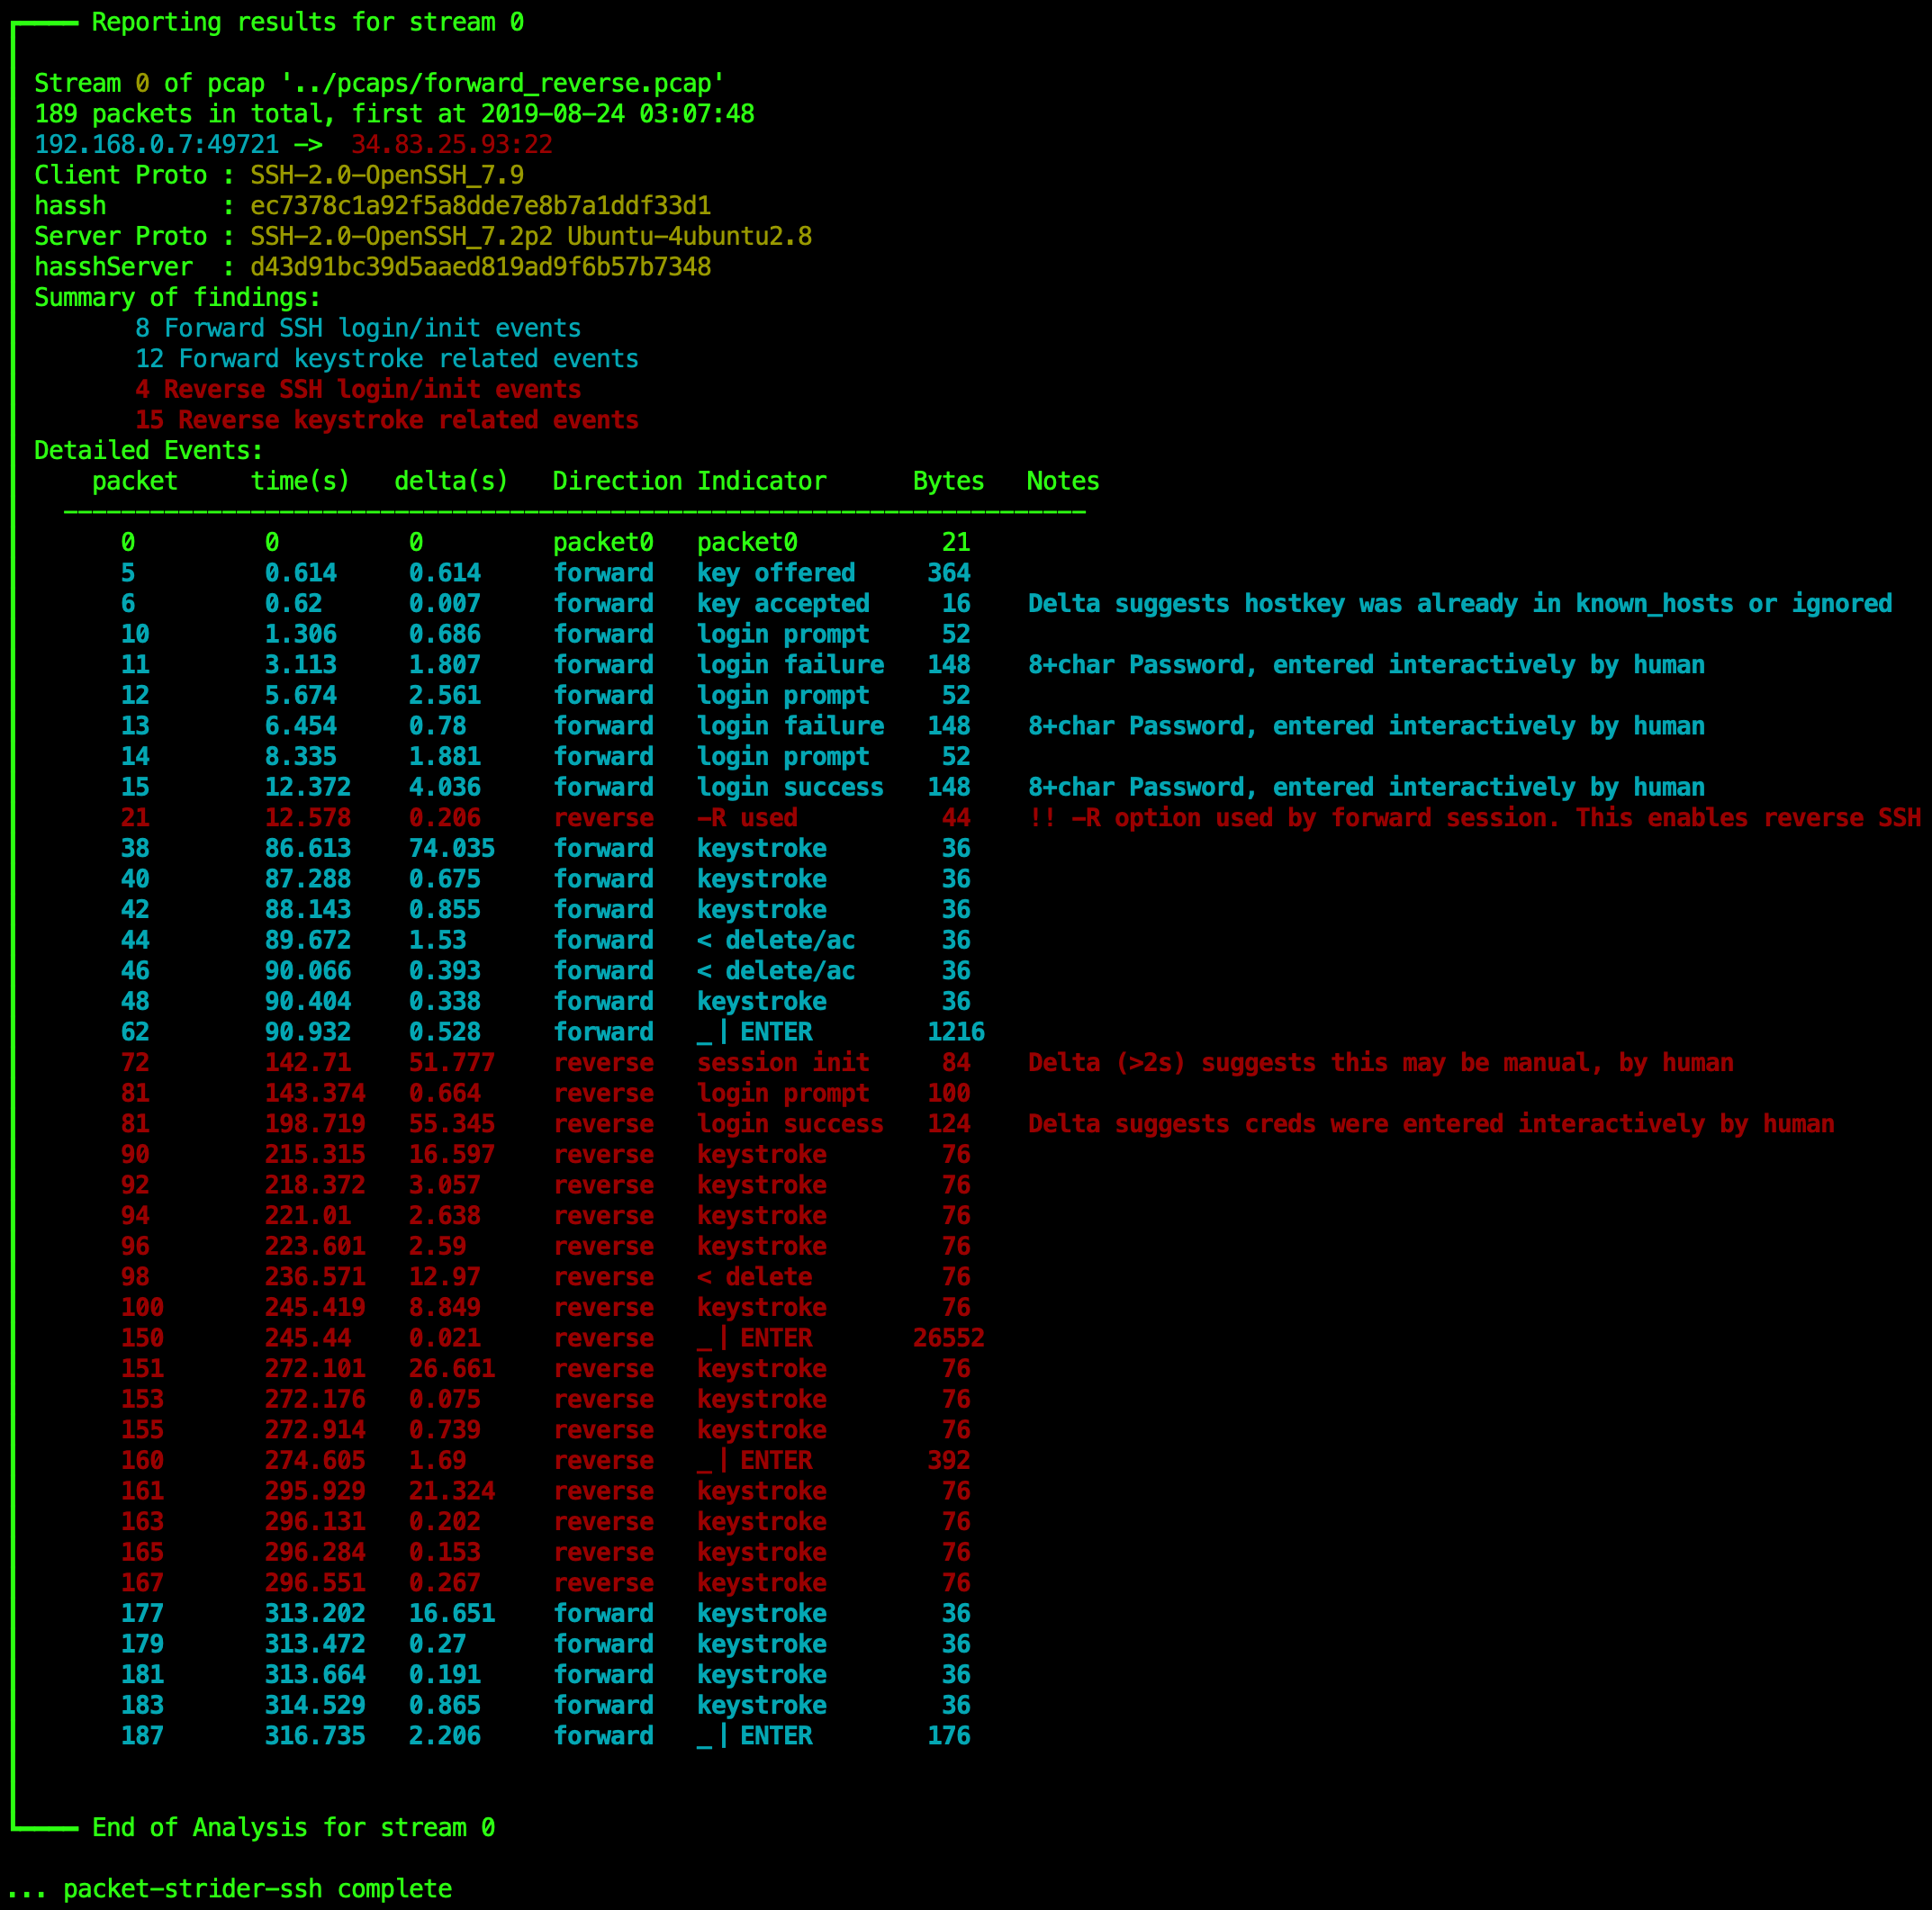 benjeems/packetstrider
A network packet forensics tool for SSH
 nccgroup/impossibletravelloganalysis
Basic log analysis tool to detect impossible travel via IP address geographic information