Mobile-Intrusion-Detection-System

Unsupervised deep autoencoder that flags anomalous mobile traffic: 25,000+ HTTP/HTTPS flows intercepted from a live iOS device with mitmproxy,…

Unsupervised deep autoencoder that flags anomalous mobile traffic: 25,000+ HTTP/HTTPS flows intercepted from a live iOS device with mitmproxy,…

Collects multi-source security logs from reproducible Docker attack scenarios, builds attack chains, and provides the SecLog-Bench-216 benchmark for…

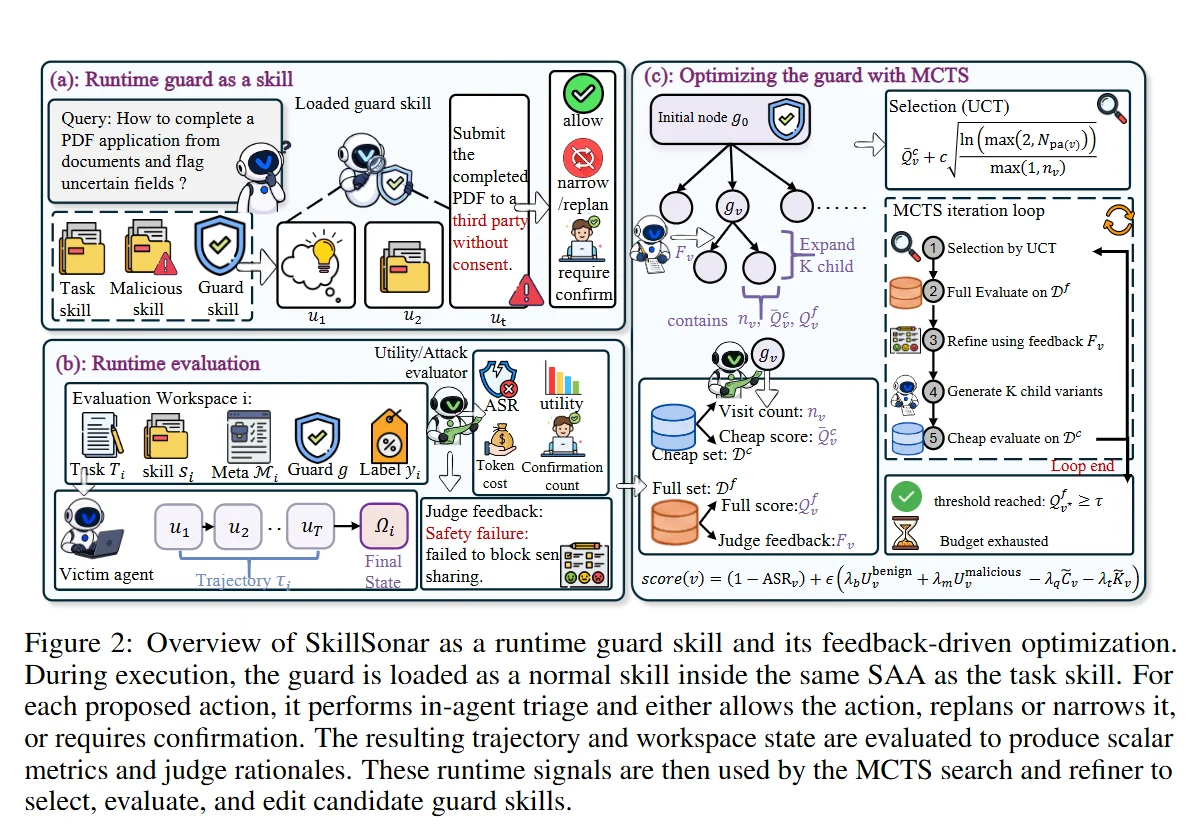
Runtime guard skill that detects and blocks malicious skill-induced attacks in skill-augmented agents, with an MCTS loop that evolves the guard…

Blazing-Fast Token-Efficient Intrusion Detection System (IDS) based on TypeSafe's Jev.

DNS Proxy that is simple and fast with not so simple features. Focused on routed DNS forwarding, filtering and parental control.

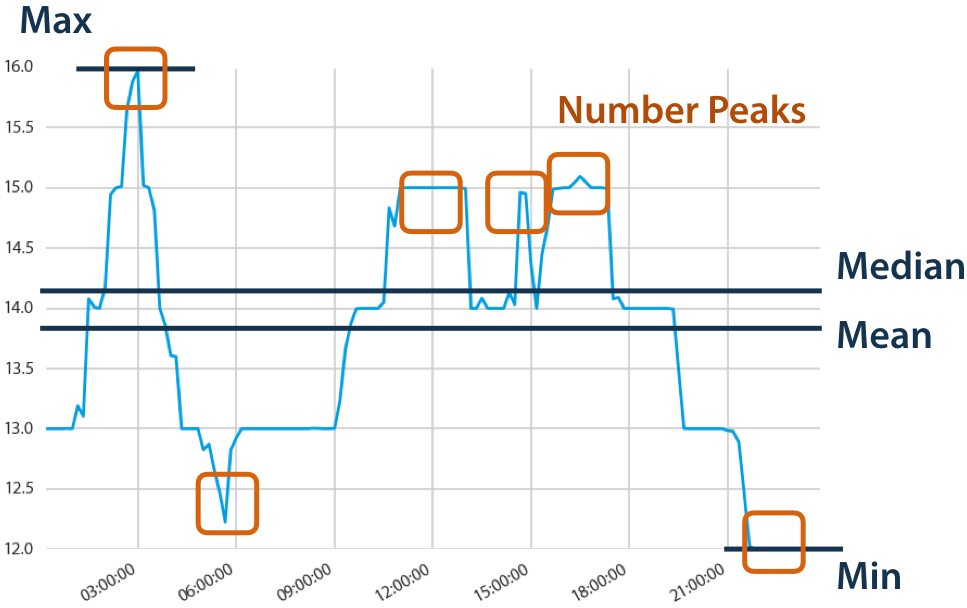
Automatic extraction of relevant features from time series:

Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.

Enumerate various traits from Windows processes as an aid to threat hunting

A canary designed to minimize the impact from certain Ransomware actors

The Console Monitor Driver is a KMDF kernel-mode filter driver that captures certain Fast I/O operations (input and output) that is sent to or from…

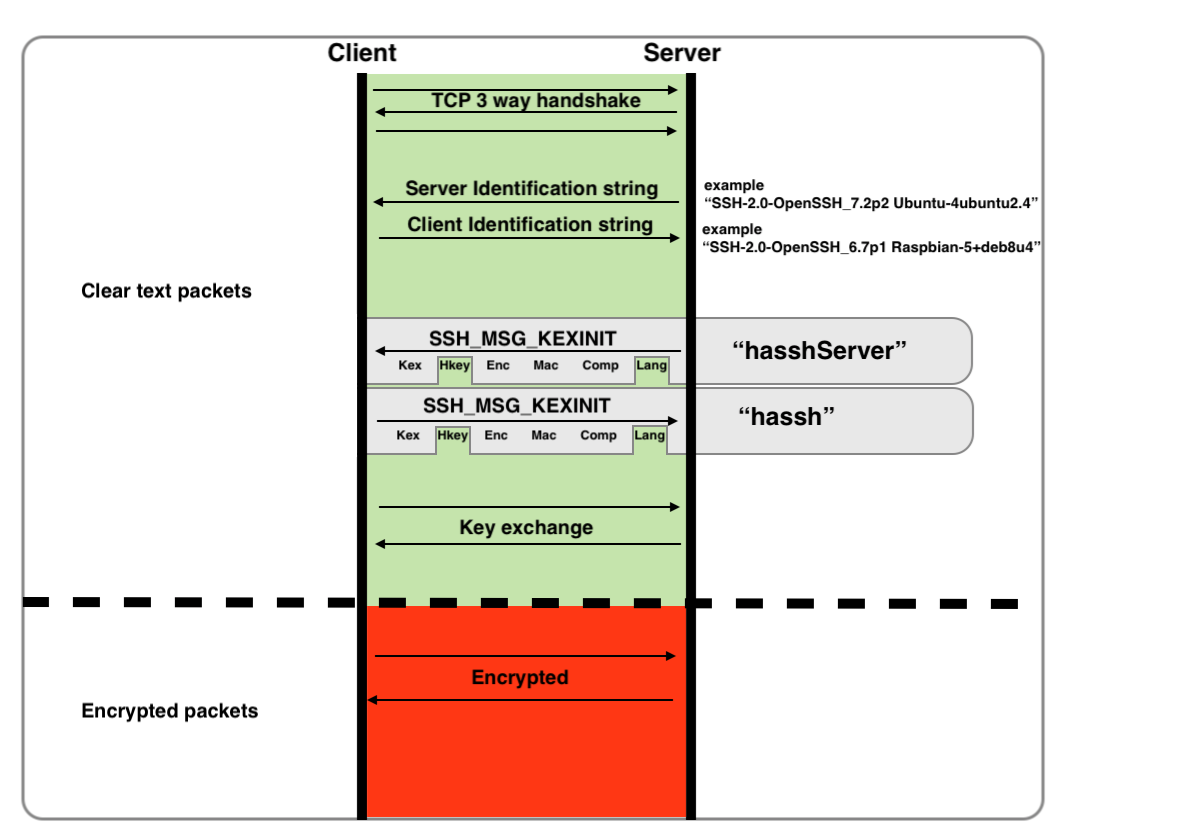
Fingerprint SSH clients and servers.

amavis is a high-performance email content filter framework written in Perl.


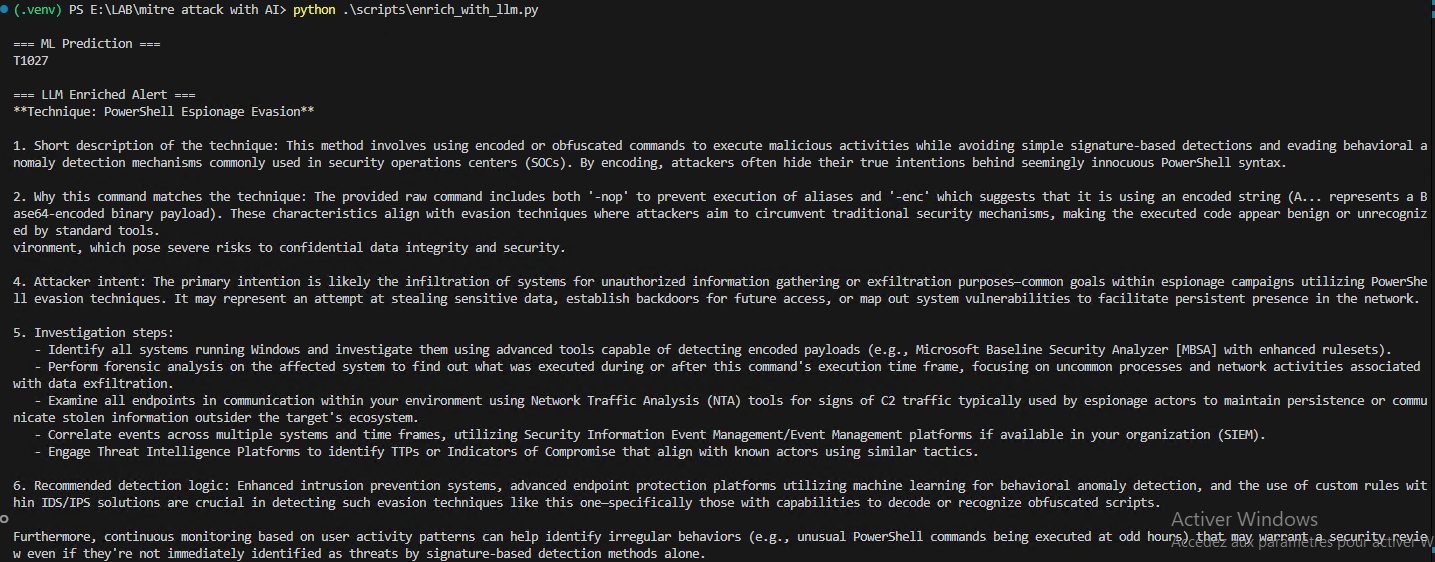
This repository demonstrates a machine learning pipeline for detecting MITRE ATT&CK techniques from logs and enriching the output using a local LLM.

Research related to the Power Tracks discovered in market microstructure.

Graph-based insider threat detection using GCN-BiLSTM and attention models on CMU CERT datasets. Includes data preprocessing, feature extraction, and…


Monitor large transactions on Polymarket and Kalshi prediction markets with anomaly detection