
logparser
 logpai/logparser
A machine learning toolkit for log parsing [ICSE'19, DSN'16]
anomaly-detectionlog-analysismachine-learning+1
logpai/logparserA machine learning toolkit for log parsing [ICSE'19, DSN'16]
 googlecloudplatform/professional-services
Collection of Google Cloud solution examples and operational utilities for audit log monitoring, DLP de-identification, encryption key management,…
 logpai/loglizer
A machine learning toolkit for log-based anomaly detection [ISSRE'16]
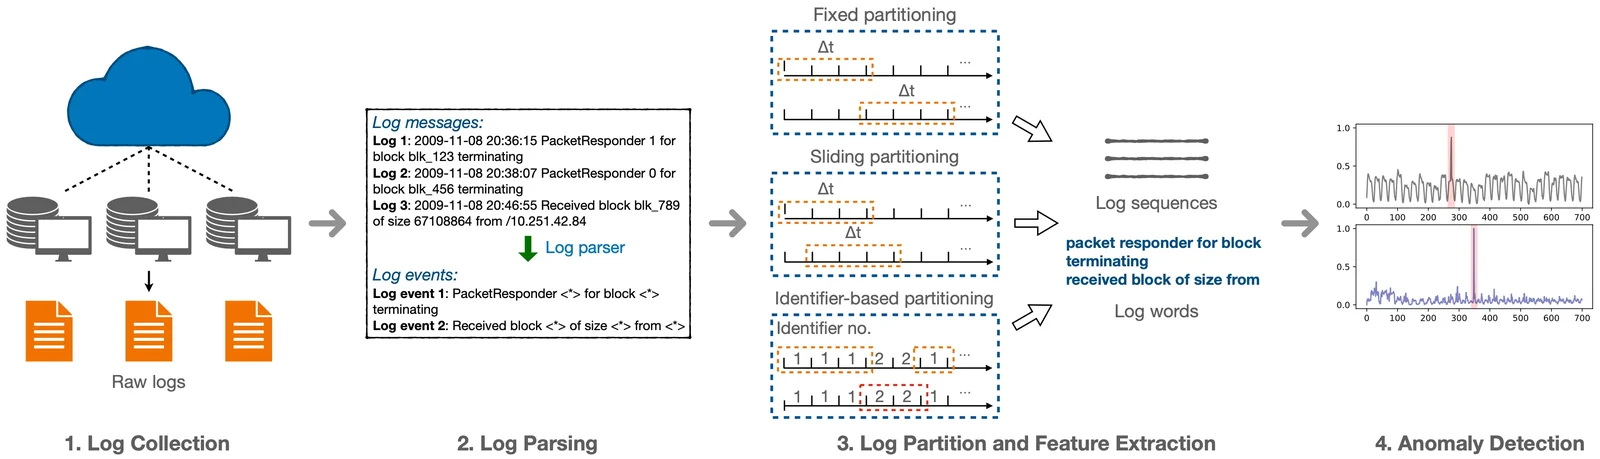 logpai/deep-loglizer
A deep learning toolkit for log-based anomaly detection
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 cyb3r-monk/rita-j
Implementation of RITA (Real Intelligence Threat Analytics) in Jupyter Notebook with improved scoring algorithm.
 pe3zx/crowdstrike-falcon-queries
A collection of Splunk's Search Processing Language (SPL) for Threat Hunting with CrowdStrike Falcon
 1-bit-wonder/kestrel
Single-host runtime-security dashboard on eBPF — Go agent + SvelteKit. Live process tree, network map, and rule-based alerts for plain Linux hosts.
 lethal-forensics/memprocfs-analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
 nccgroup/impossibletravelloganalysis
Basic log analysis tool to detect impossible travel via IP address geographic information
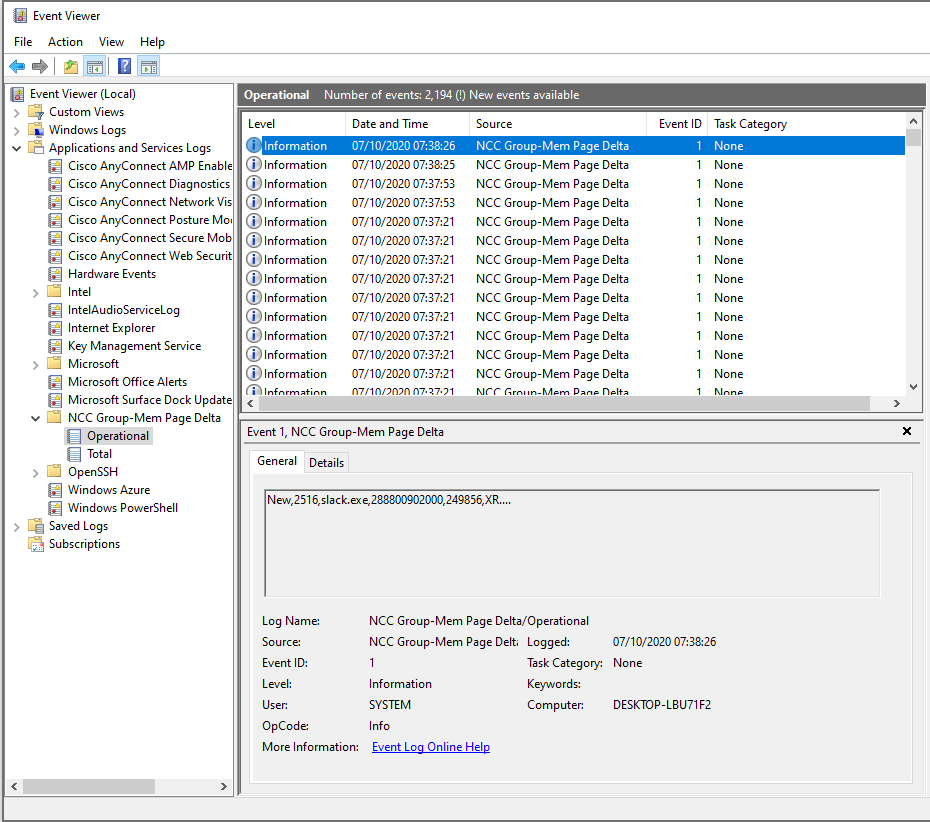 nccgroup/windowsmempagedelta
A Microsoft Windows service to provide telemetry on Windows executable memory page changes to facilitate threat detection
 corelight/conn-burst
A Bro package to identify connections that are bursting (lots of data and transferring quickly).
 corelight/corelightforsplunk
Splunk app for integrating and analyzing Corelight network detection data, enabling real-time threat hunting and incident response.
 corelight/zeek-endpoint-enrichment-conn
Enrich the conn.log with EDR data
 shoucheng3/graylog2__graylog2-server_cve-2023-41044_5-1-2
Open source log management platform for centralized log aggregation, real-time analysis, and security event monitoring with customizable dashboards…
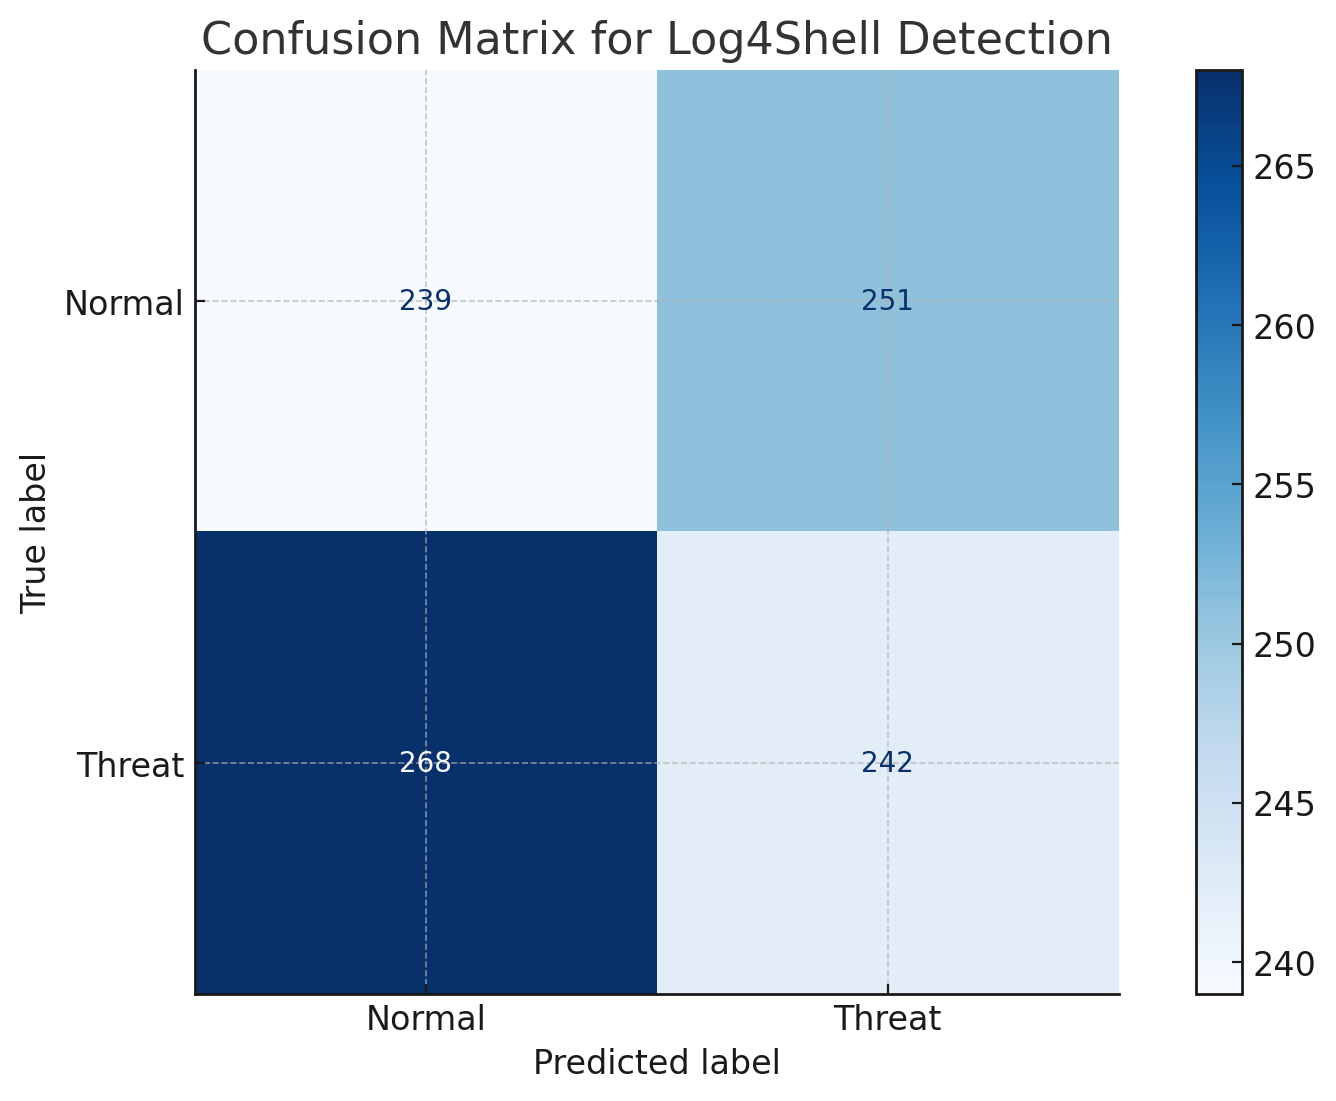 yadavmukesh/log4shell-vulnerability-cve-2021-44228-
This repository provides an in-depth analysis of the Log4Shell vulnerability (CVE-2021-44228) and implements a machine learning-based approach to…
 betterdb-inc/monitor
Real-time monitoring and slowlog analysis for Valkey and Redis databases with anomaly detection, ACL auditing, and Prometheus metrics export.
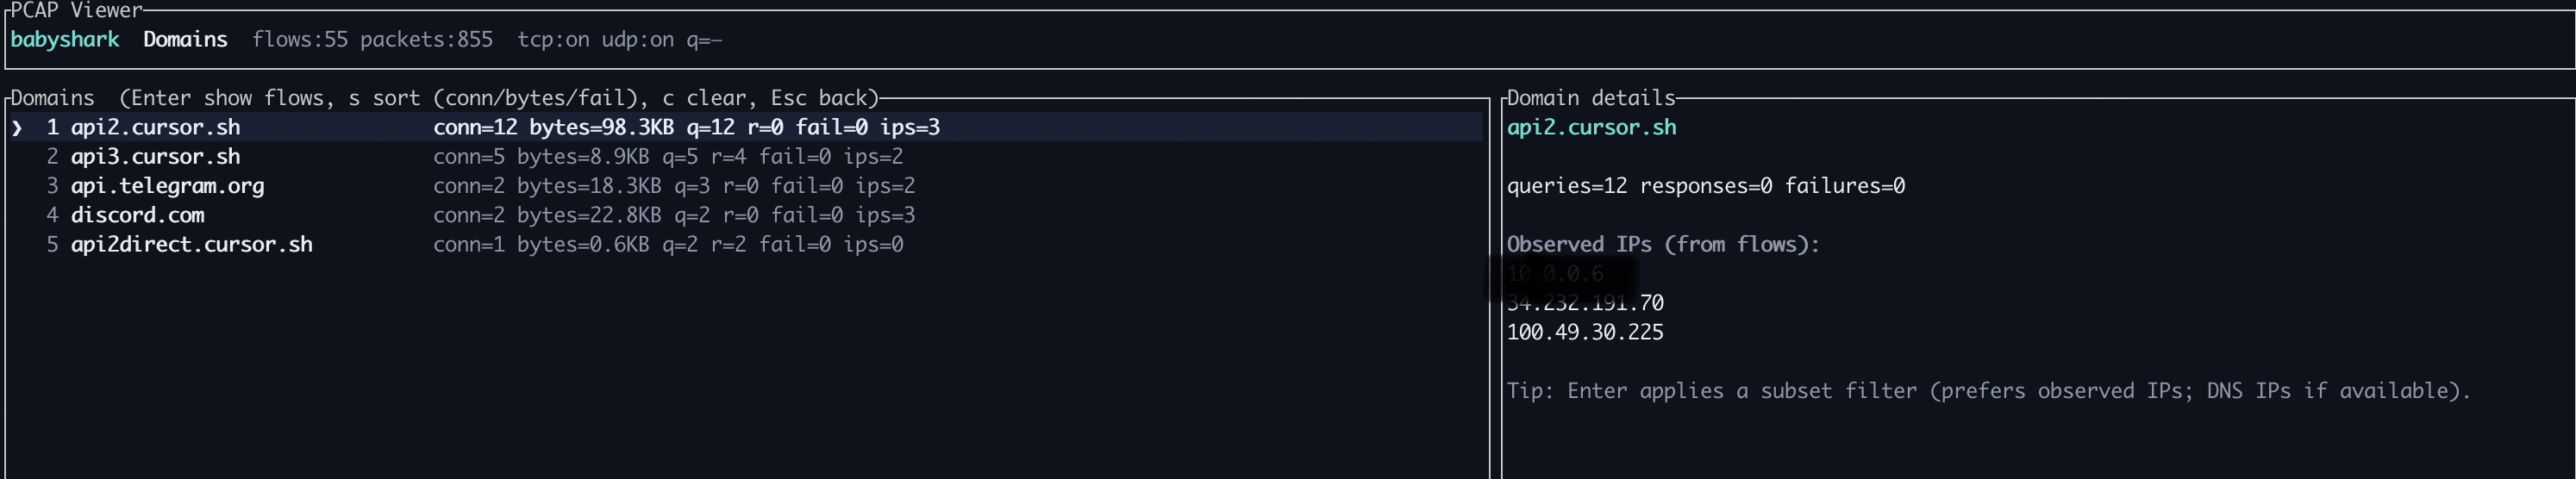 vignesh07/babyshark
Flows-first PCAP TUI (case files, gorgeous UX). Do do do do.