

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
14 results
zeek preview

zeek

GitHubzeek/zeek

Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
anomaly-detectionanti-botdefensive-tools+14
8.2k9h 26m ago
Snitch preview

Snitch

GitHubaixisstudio/snitch

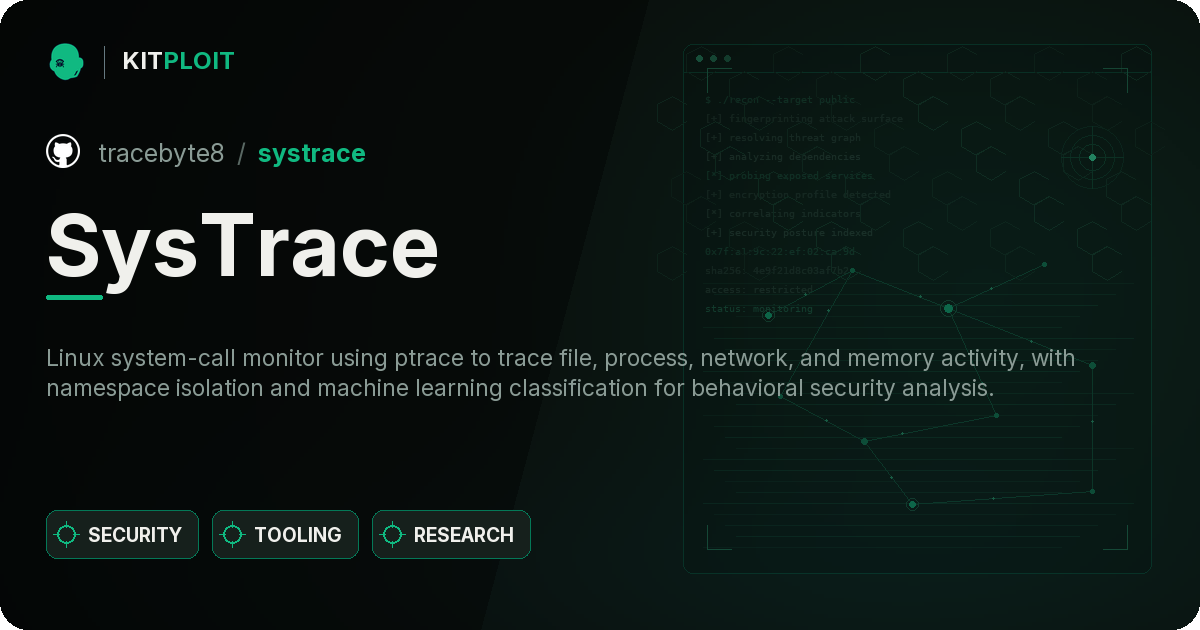
Real-time network monitor + outbound firewall — see & block every connection. Privacy-first, local-first, Rust fleet agent, SIEM exports, 8…
anomaly-detectiondefensive-toolsdns-analysis+6
6751 day ago
SysTrace preview

SysTrace

GitHubtracebyte8/systrace

Linux system-call monitor using ptrace to trace file, process, network, and memory activity, with namespace isolation and machine learning…
anomaly-detectiondynamic-analysis-sandboxingmachine-learning+1
251 month ago
Network_Assessment preview

Network_Assessment

GitHubalperenugurlu/network_assessment

With Wireshark or TCPdump, you can determine whether there is harmful activity on your network traffic that you have recorded on the network you…
anomaly-detectionintrusion-detectionnetwork-security+2
1483 years ago
bluehood preview

bluehood

GitHubdannymcc/bluehood

Monitor your local neighbourhood's bluetooth activity
anomaly-detectionbluetooth-securityeducation+8
1.2k1 month ago
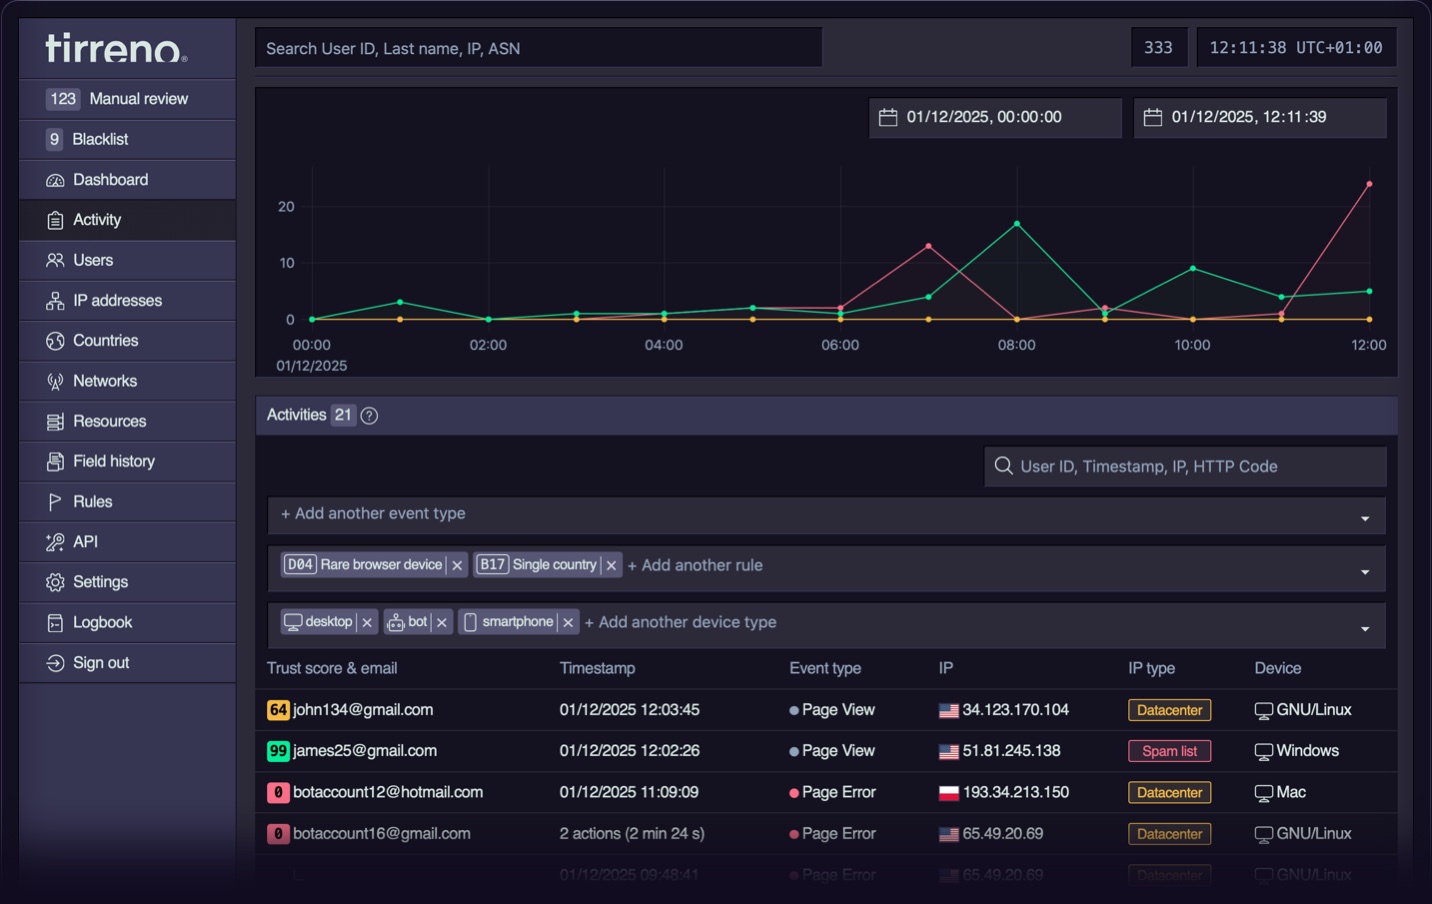
tirreno preview

tirreno

GitHubtirrenotechnologies/tirreno

Open-source security framework for real-time event tracking, threat detection, and risk scoring. Monitors user behavior, detects fraud, bot attacks,…
anomaly-detectionanti-botapi-security+3
1.6k6 days ago
Intrusion-Alert-Educational-Network-IDS preview

Intrusion-Alert-Educational-Network-IDS

GitHubowasp/intrusion-alert-educational-network-ids

Lightweight Python-based IDS that monitors network traffic in real-time using Scapy, detecting DoS/DDoS attacks via per-IP request rate analysis with…
anomaly-detectiondefensive-toolseducation+3
6 months ago
eBPF-hid_guard preview
Archived

eBPF-hid_guard

GitHubfusion1110/ebpf-hid_guard

Linux kernel-space HID injection attack detector using eBPF. Monitors USB and Bluetooth HID devices for anomalous keystroke timing and automatically…
anomaly-detectionbluetooth-securitydefensive-tools+2
54 months ago
polymaster preview

polymaster

GitHubneur0map/polymaster

Monitor large transactions on Polymarket and Kalshi prediction markets with anomaly detection
anomaly-detectioncrawlerdata-exfiltration+3
271 month ago
openrasp preview

openrasp

GitHubbaidu/openrasp

Runtime application self-protection engine that hooks into application servers to monitor and block malicious database queries, file operations, and…
anomaly-detectiondefensive-toolsdevsecops+2
3.0k1 year ago
apache_skywalking preview

apache_skywalking

GitHubshanika04/apache_skywalking

CVE-2020-9483 OR CVE-2020-13921
anomaly-detectionapi-securitycloud-infrastructure-security+9
15 years ago
mimikatz-detector-condrv preview

mimikatz-detector-condrv

GitHubnccgroup/mimikatz-detector-condrv

The Console Monitor Driver is a KMDF kernel-mode filter driver that captures certain Fast I/O operations (input and output) that is sent to or from…
anomaly-detectiondefensive-toolsincident-response+3
434 years ago
tirreno preview

tirreno

GitLabtirreno/tirreno

Open security analytics.

anomaly-detectionapi-securityauthentication+7
11 months ago
Hunt-Weird-Syscalls preview

Hunt-Weird-Syscalls

GitHubtheflink/hunt-weird-syscalls

ETW based POC to identify direct and indirect syscalls

anomaly-detectiondefensive-toolsintrusion-detection+1
1973 years ago