

maltrail
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
anomaly-detectionanti-botdefensive-tools+11
8.6k
stamparm/maltrailReal-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 roxanne_ardary/nexora
AI-driven endpoint governance platform that monitors software usage, applies deterministic policy-based risk classification, and generates structured…
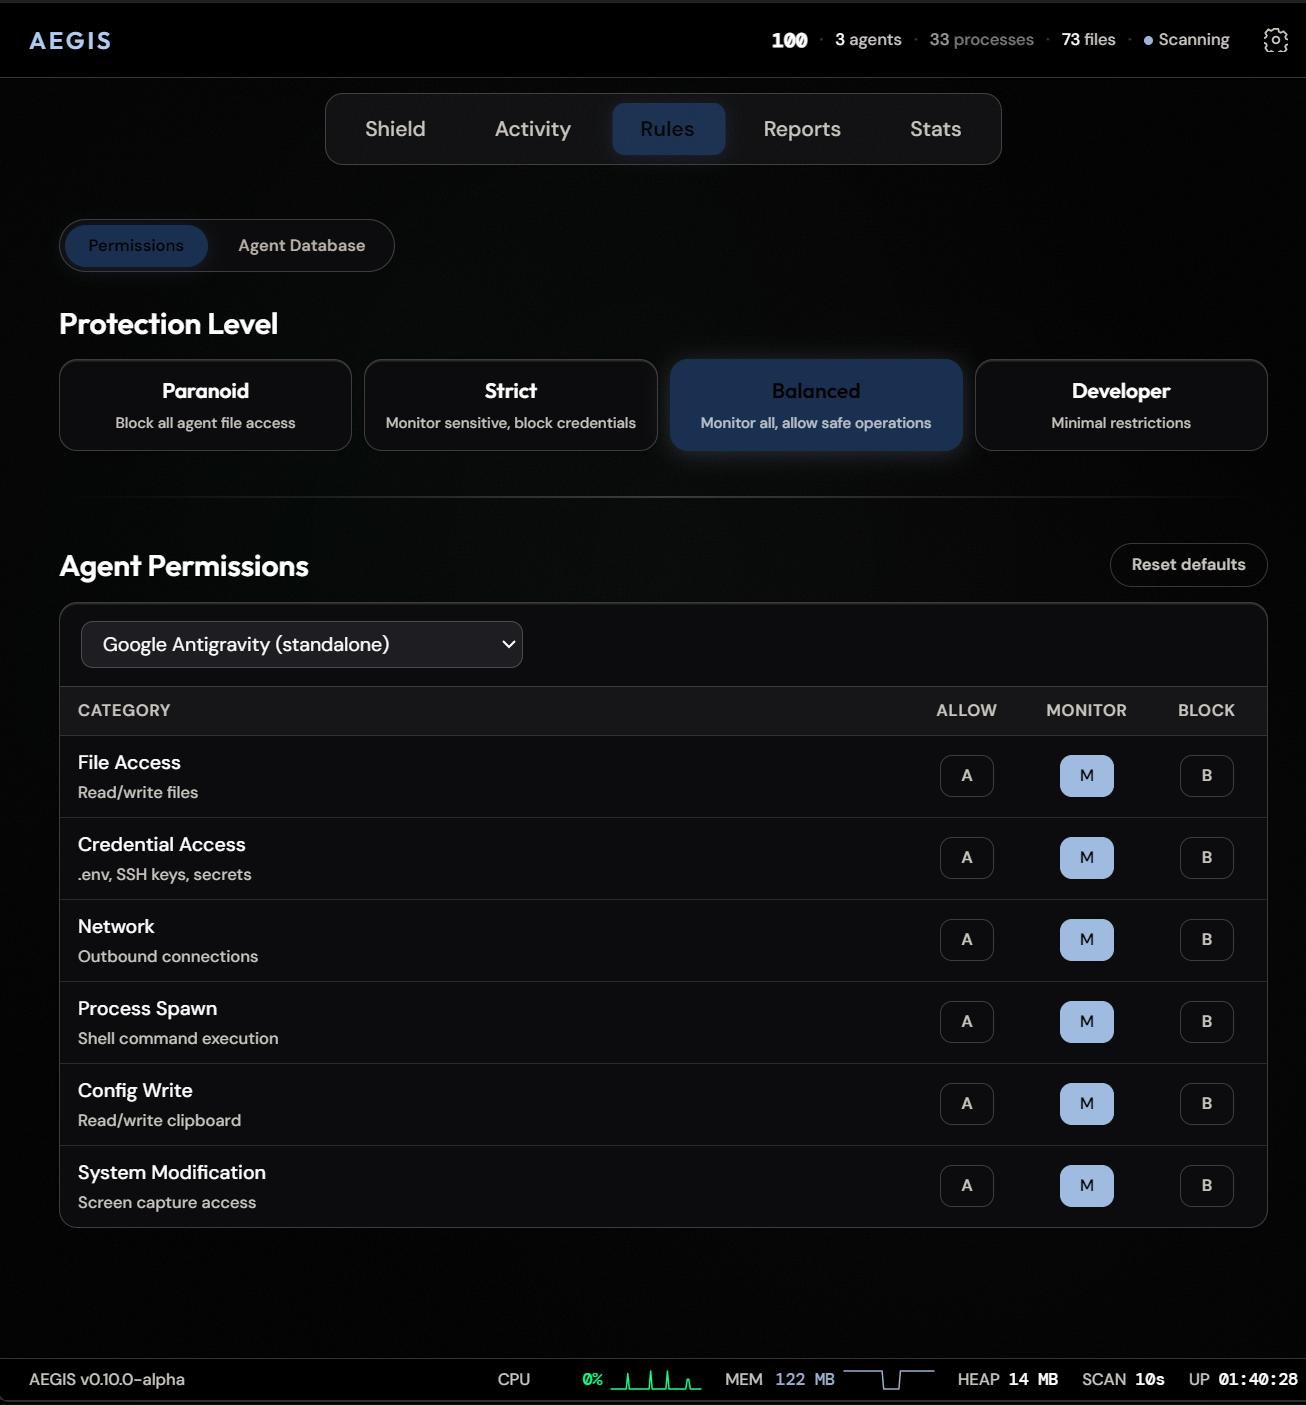 antropos17/aegis
Desktop monitoring and local security reviews for AI agents, with opt-in policy-controlled execution and MCP action tools. Windows primary;…
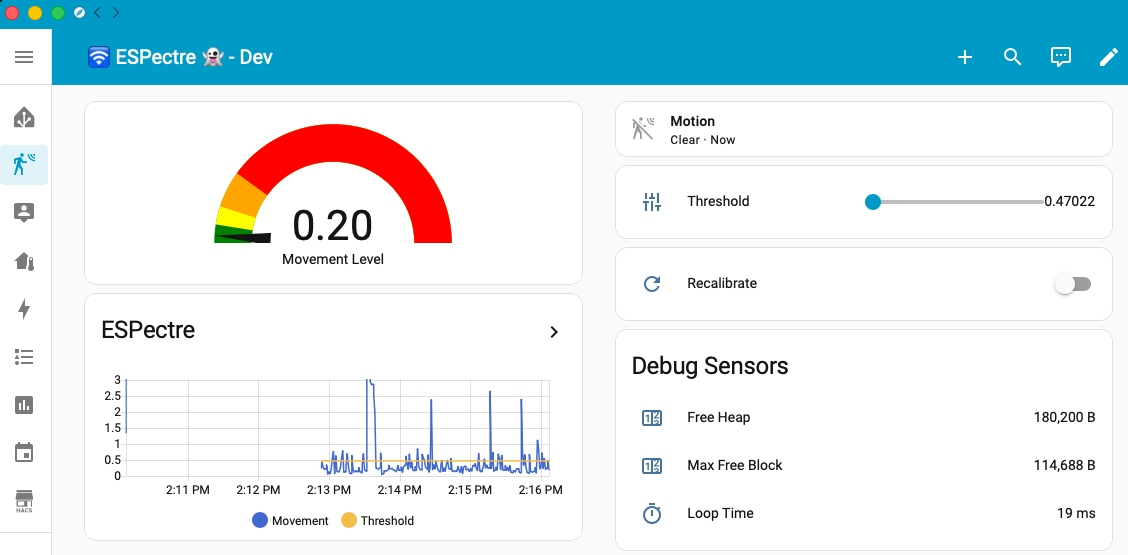 francescopace/espectre
ESPectre - Motion detection system based on Wi-Fi spectre analysis (CSI), with Home Assistant integration.
 pavel-odintsov/fastnetmon
Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support
 tracebyte8/systrace
Linux system-call monitor using ptrace to trace file, process, network, and memory activity, with namespace isolation and machine learning…
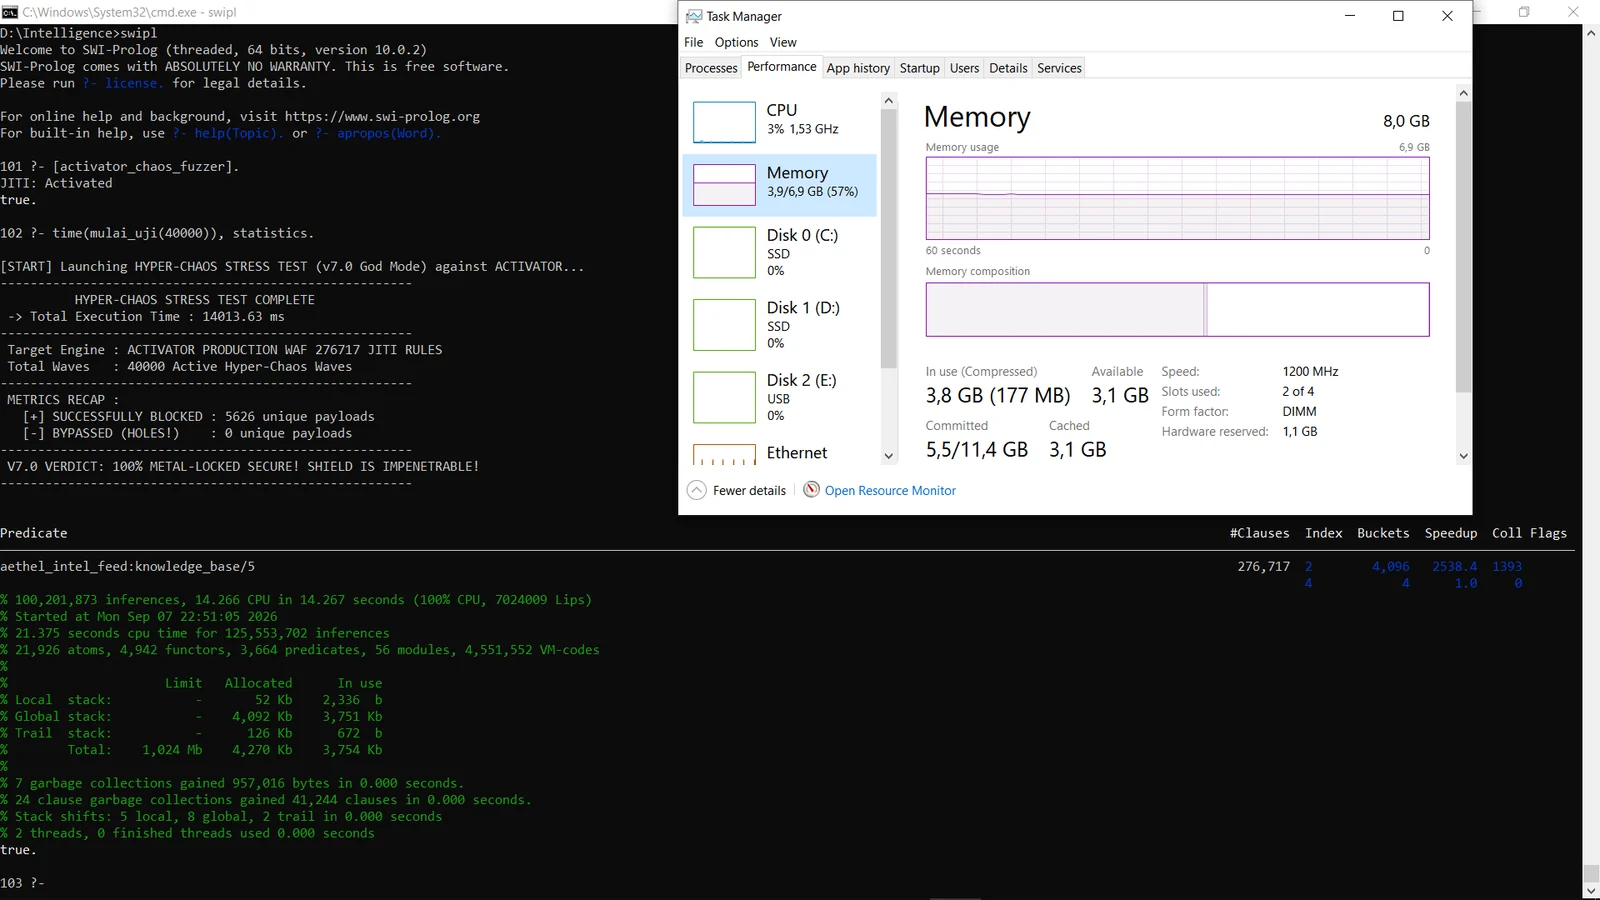 lokinpendawa/aethel_core
Next-gen logical WAF engine built in SWI-Prolog. Features an inductive learning brain running at 2M+ LIPS with an integrated recursive decoder to…
 activecm/rita
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
 betterdb-inc/monitor
Real-time monitoring and slowlog analysis for Valkey and Redis databases with anomaly detection, ACL auditing, and Prometheus metrics export.
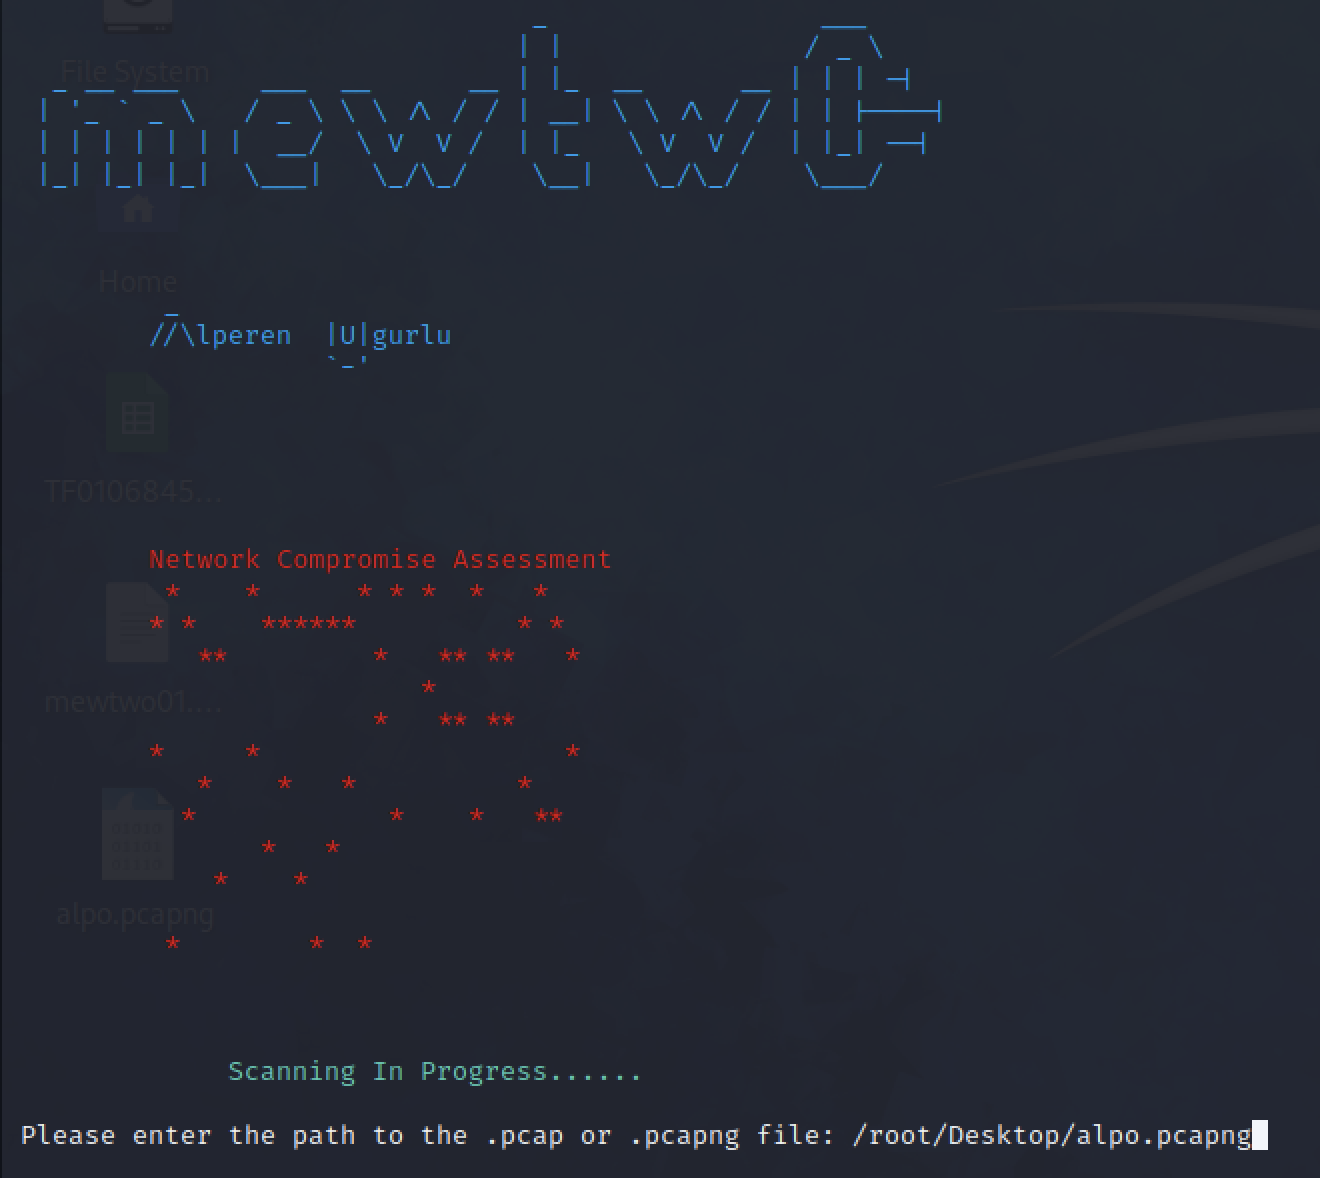 alperenugurlu/network_assessment
With Wireshark or TCPdump, you can determine whether there is harmful activity on your network traffic that you have recorded on the network you…
 gpt-laboratory/trustworthyrag
An Evaluation Agent for Detecting Misinformation and Knowledge Poisoning in Retrieval-Augmented Generation Systems.
 shuangliangx/learning-to-detect
Detects unknown jailbreak attacks in large vision-language models using hidden state analysis and autoencoders, with training and evaluation…
 mlily2024/final-project-sql-injection-pipeline
Hybrid machine-learning pipelines for detecting SQL injection in web traffic, combining DistilBERT and BERT-GNN models with adversarial training and…
 yeasen-z/leakgauge
Detects LLM context-leakage attacks by training lightweight behavior probes on log-probabilities, with vLLM offline/server detection pipelines.

 gmh5225/0xguard
Simple Anti-cheat library for applications that use C++ on windows. #PastedProtection
 rob-med/awesome-ts-anomaly-detection
List of tools & datasets for anomaly detection on time-series data.