
Archived
ColorOS-CVE-2025-10184
 yuuouu/coloros-cve-2025-10184
ColorOS短信漏洞,以及用户自救方案
android-securitydatabase-securitydata-exfiltration+6
386
yuuouu/coloros-cve-2025-10184ColorOS短信漏洞,以及用户自救方案
 hluwa/frida-dexdump
A frida tool to dump dex in memory to support security engineers analyzing malware.
 interplains/zero-breach-toolkit
Free, open-source, offline checks for traces of known mercenary spyware. Works on Windows, macOS and Linux, Android phones and iPhone backups.
 linuxoid-cn/mi8e5-unlocker-by-cve-2026-43499
基于 CVE-2026-43499 的 8E5 机型自动化解锁辅助工具,仅限授权安全研究与自有设备使用。
 liznzn/cve-2019-2215
Temproot for Bravia TV via CVE-2019-2215.
 fengguan/arpcut
Rooted Android app that scans LAN devices and cuts or restores their network access via ARP spoofing, with OUI vendor lookup, whitelist, and…
 androidhooker/hooker
Hooker is an opensource project for dynamic analyses of Android applications. This project provides various tools and applications that can be use to…
 b3nac/injuredandroid
A vulnerable Android application that shows simple examples of vulnerabilities in a ctf style.
 superandroidanalyzer/super
Secure, Unified, Powerful and Extensible Rust Android Analyzer
 sonyxperiadev/apkanalyser
Static analysis tool for Android APKs that inspects Dalvik bytecode, decodes XML resources, and detects potential issues. Supports binary…
 google/enjarify
Translates Dalvik bytecode (DEX/APK) to equivalent Java bytecode, enabling Java analysis tools to process Android applications with high correctness…
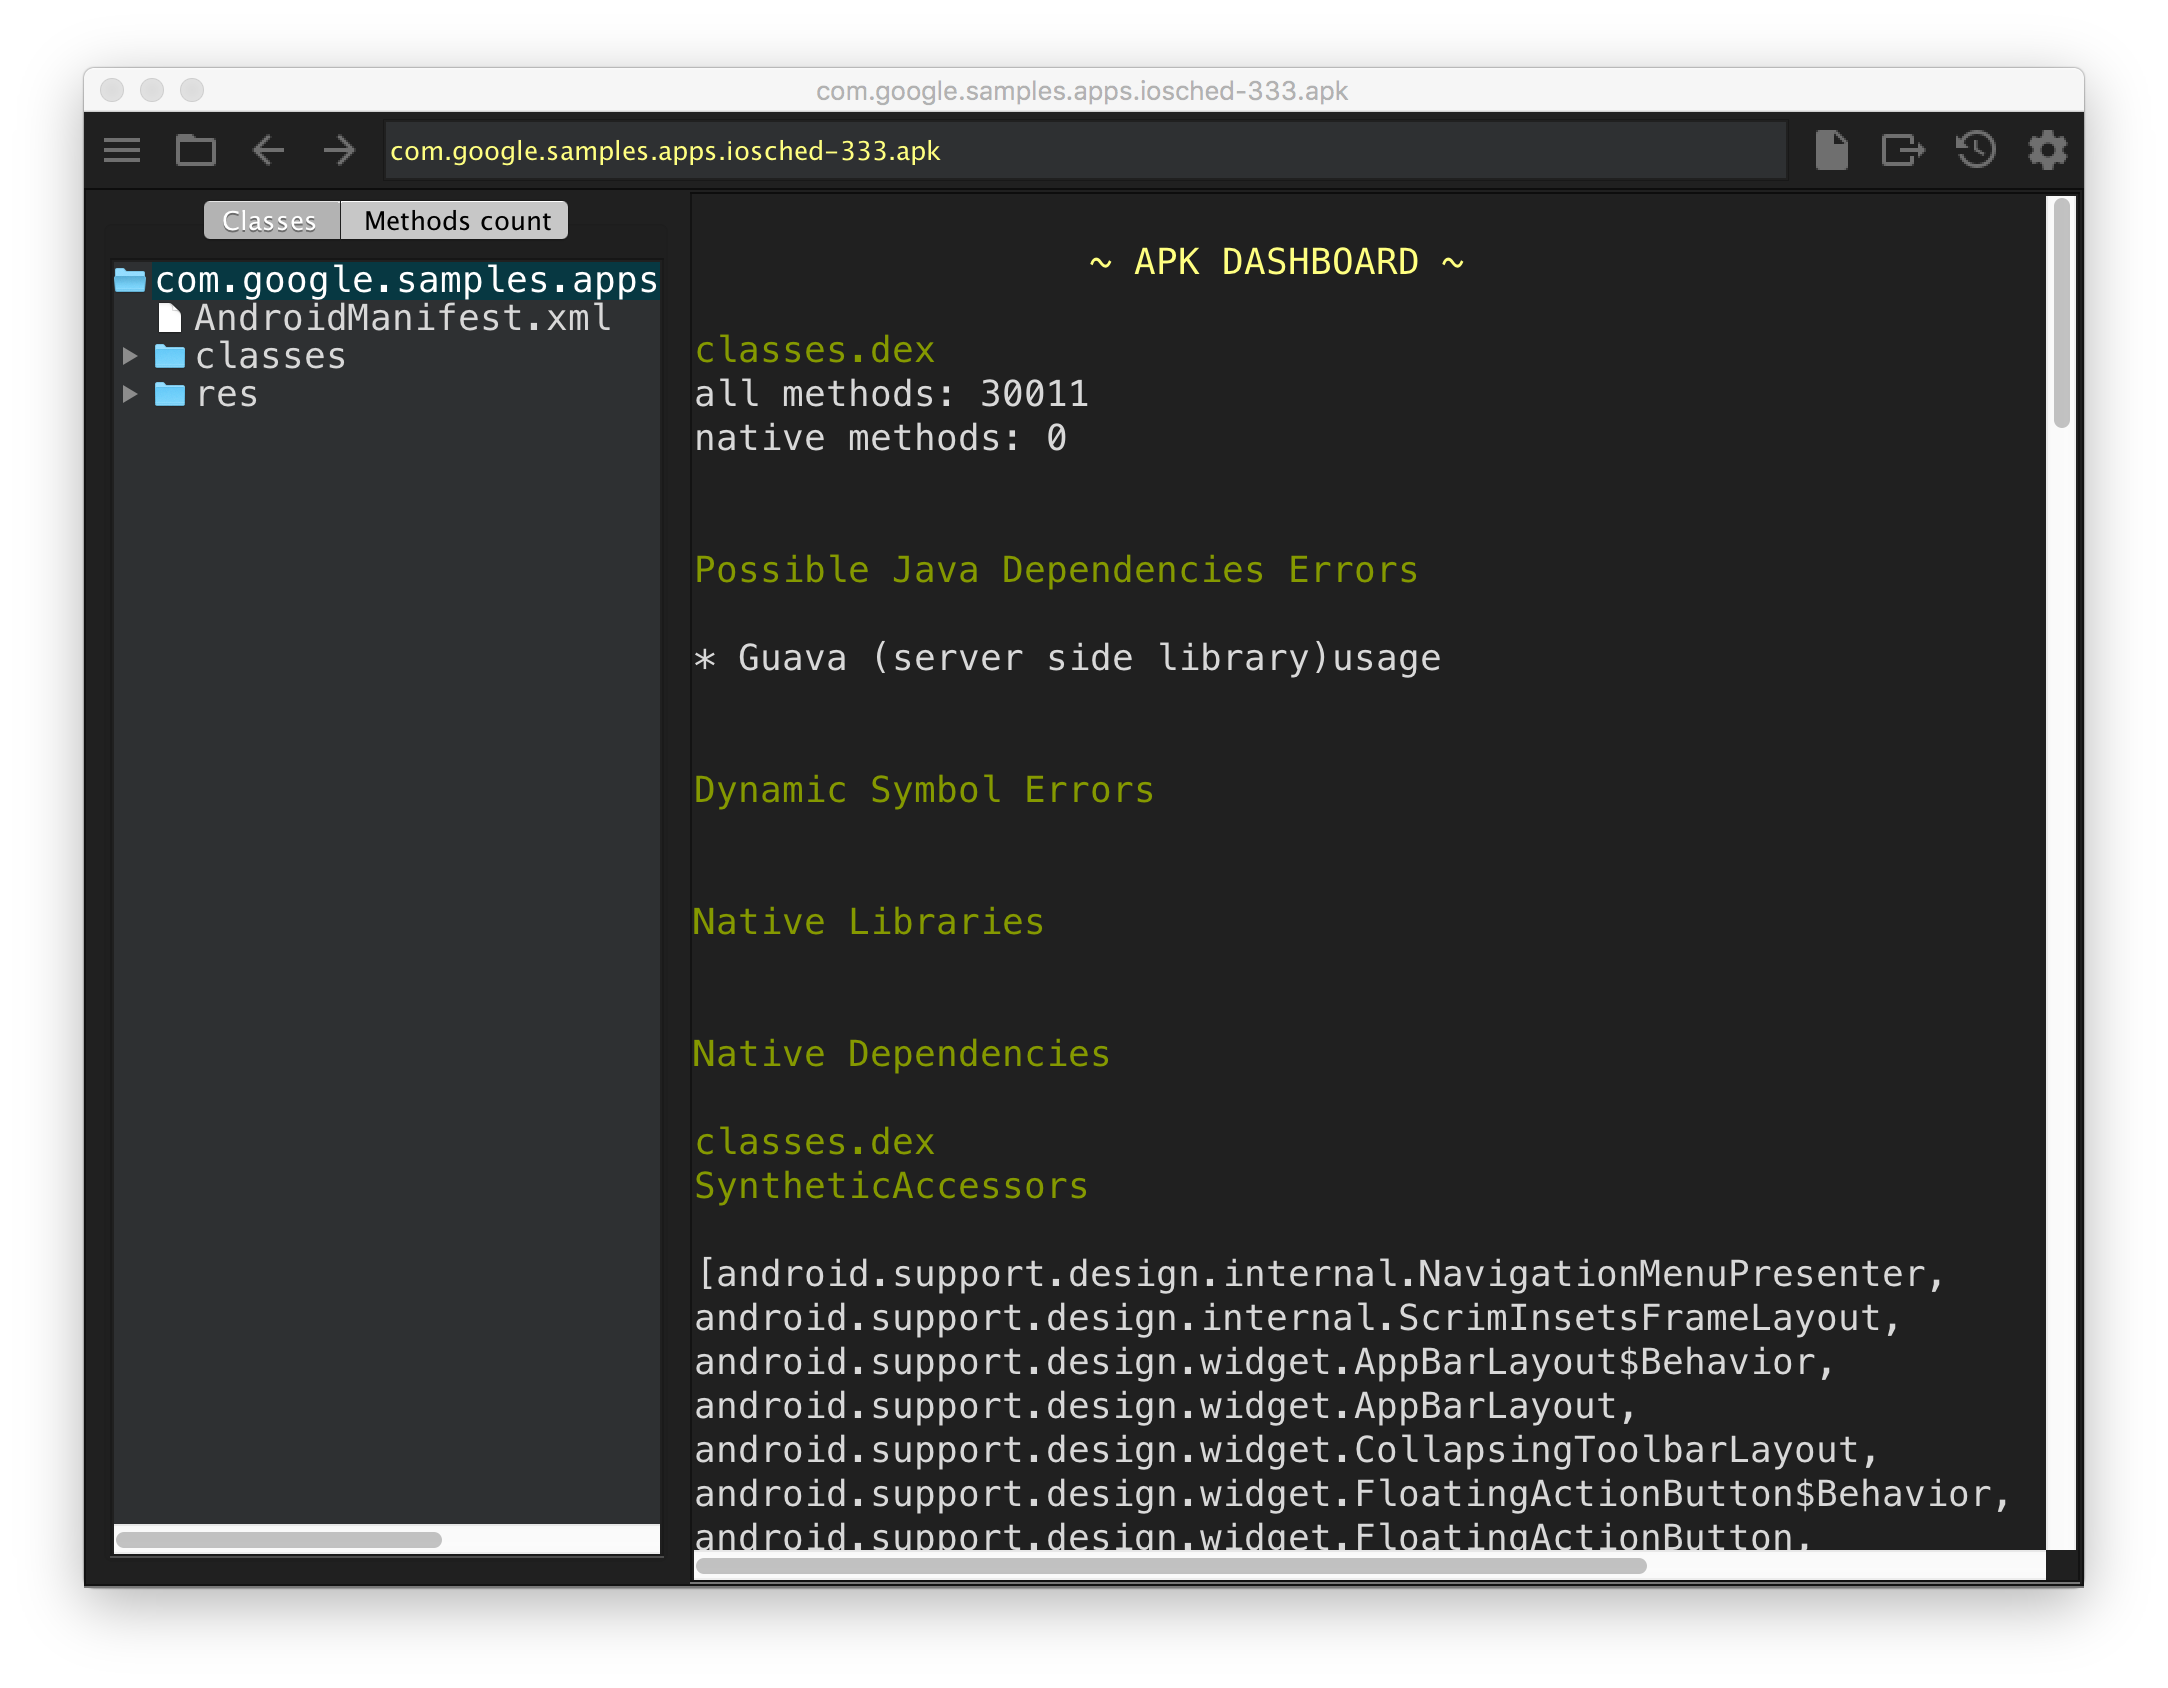 google/android-classyshark
Android and Java bytecode viewer
 meowkis/tcp-zerocopy-sm
ghostlock + tcp-zerocopy hybrid CVE-2026-43499 adaptation for samsung kernel
 indiandragon/shellshock-vulnerability-scan
Android app to scan for bash Vulnerability - CVE-2014-6271 also known as Shellshock
 certcc/keyfinder
A tool for finding and analyzing private (and public) key files, including support for Android APK files.
 abhi-r3v0/adhrit
Android Security Suite for in-depth reconnaissance and static bytecode analysis based on Ghera benchmarks.
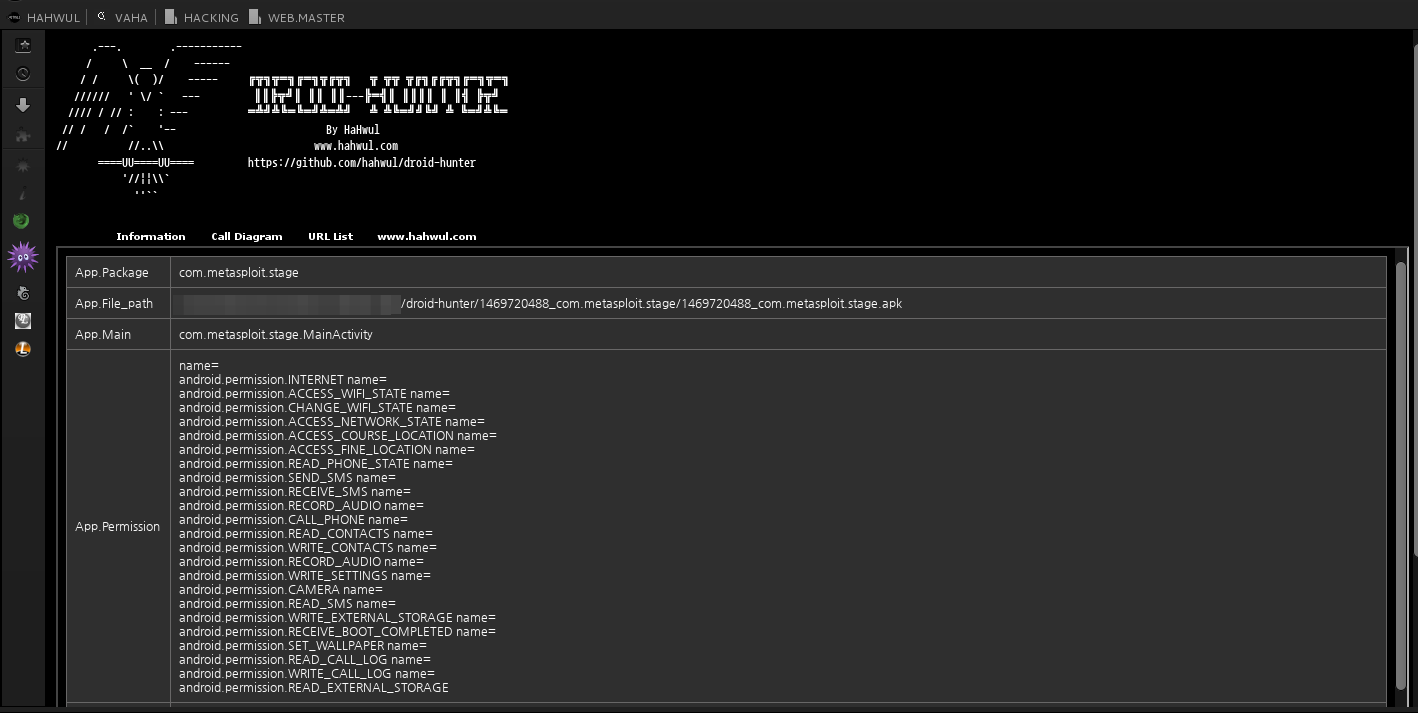 hahwul/droid-hunter
(deprecated) Android application vulnerability analysis and Android pentest tool
