
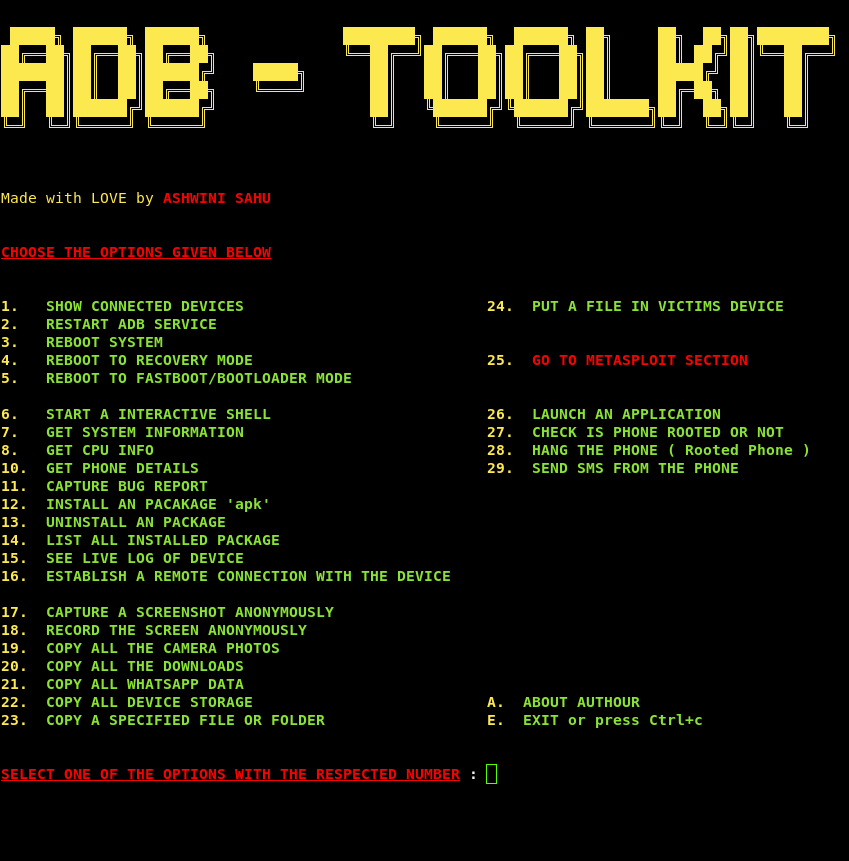
ADB-Toolkit
 ashwin990/adb-toolkit
ADB-Toolkit V2 for easy ADB tricks with many perks in all one. ENJOY!
android-securityexploit-frameworksinformation-gathering+3
2.0k
ashwin990/adb-toolkitADB-Toolkit V2 for easy ADB tricks with many perks in all one. ENJOY!
 m4sc3r4n0/evil-droid
Framework to create, generate, and embed APK payloads for Android penetration testing, leveraging Metasploit for exploitation and Apktool for…
 sensepost/kwetza
Python script to inject existing Android applications with a Meterpreter payload.
 maaaaz/androwarn
Yet another static code analyzer for malicious Android applications
 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
 barghest-ngo/mesh
Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
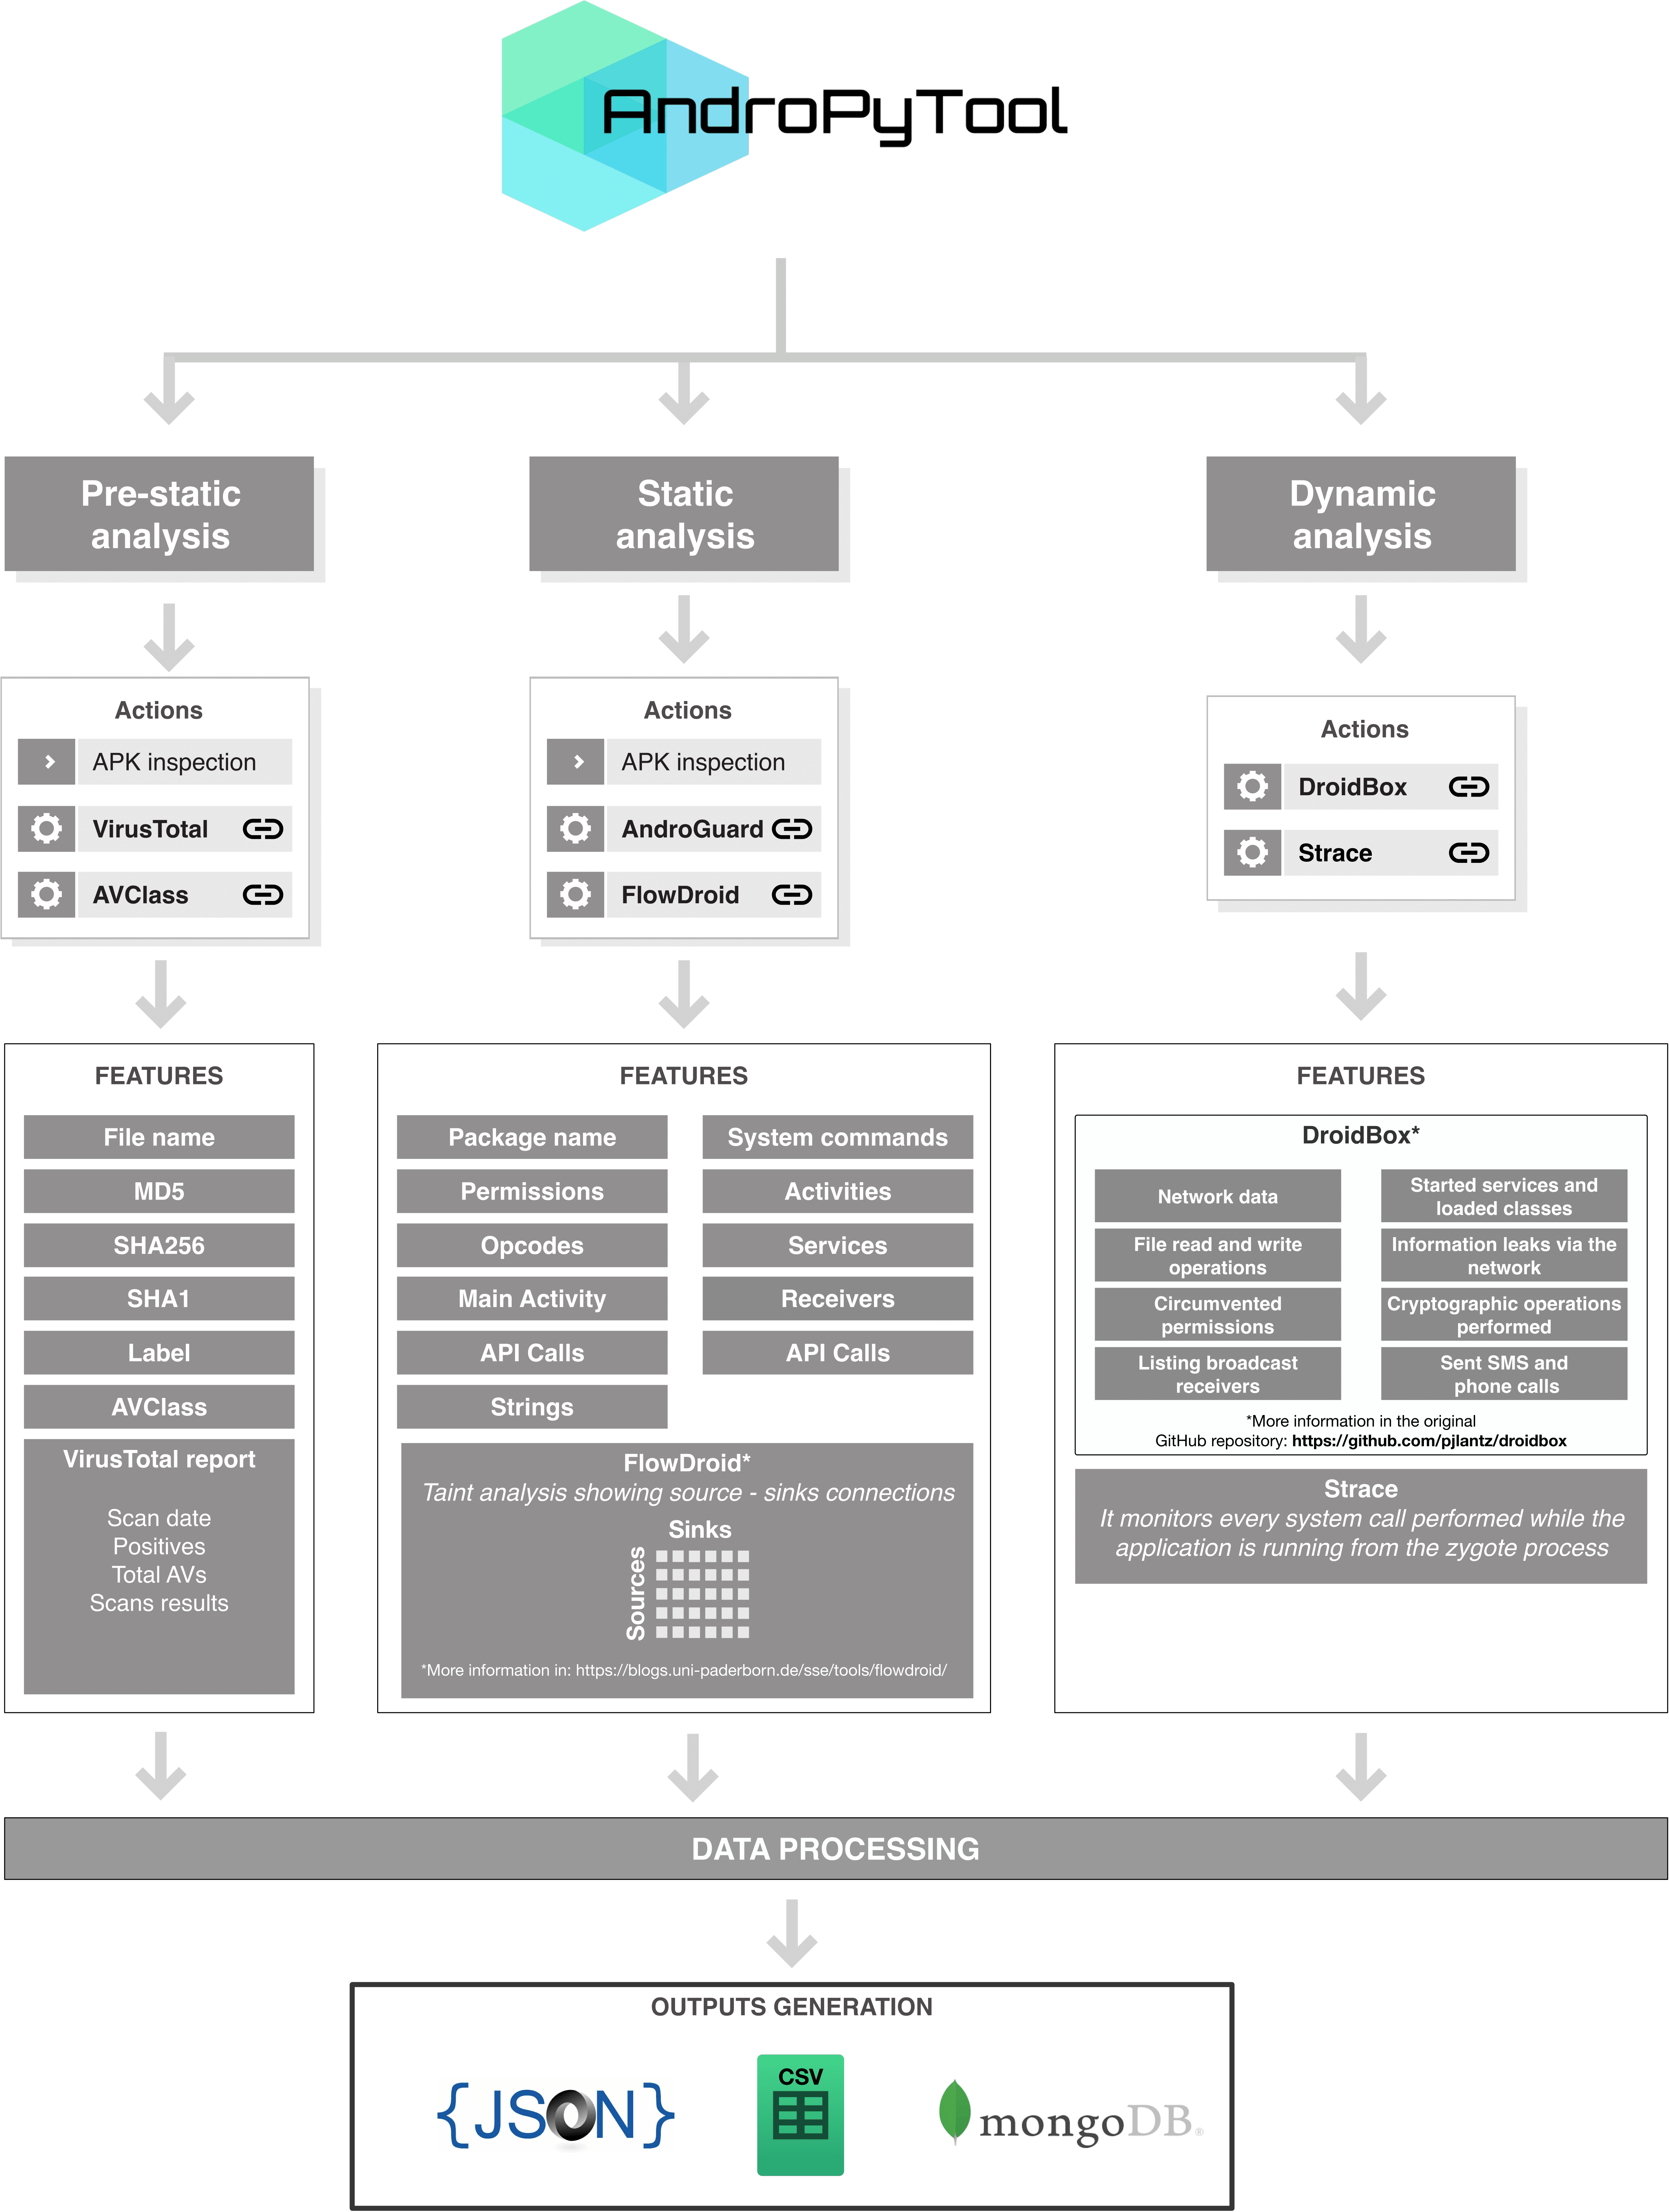 alexmyg/andropytool
A framework for automated extraction of static and dynamic features from Android applications
 rovellipaolo/ninjadroid
Ninja Reverse Engineering on Android APK packages
 plum-umd/redexer
The Redexer binary instrumentation framework for Dalvik bytecode
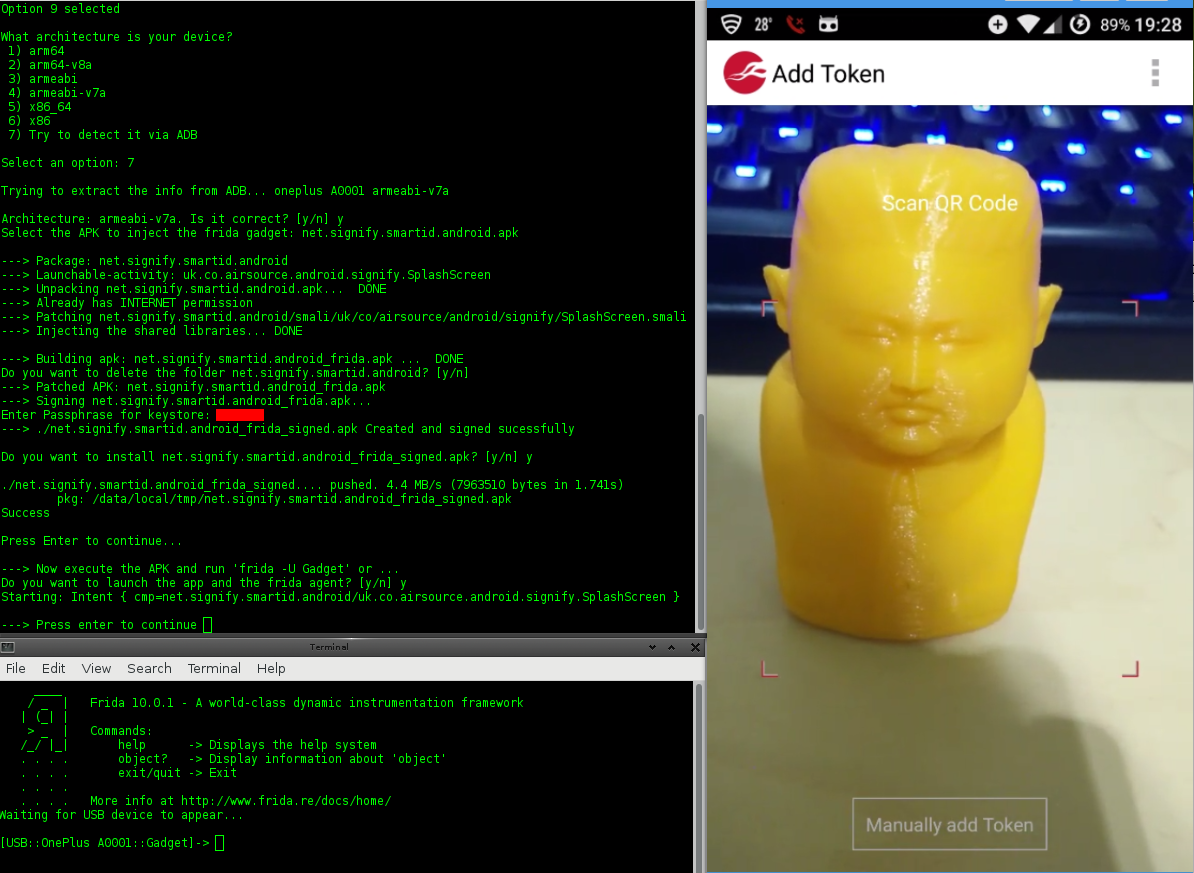 nccgroup/lazydroid
bash script to facilitate some aspects of an Android application assessment
 dkhuuthe/madlira
Malware detection using learning and information retrieval for Android
 0xdad0/papimonitor
Frida-based runtime API monitor for Android apps that logs invoked APIs, parameters, return values, and call origins across predefined or custom…
 cybersecsi/robodroid
Manage Android machines with pre-defined behaviors for Cyber Range environments.
 0xbinder/cve-2026-0073
An automated exploit for CVE-2026-0073 (Android ADB TLS Auth Bypass). Features a built-in mDNS/Zeroconf scanner to instantly discover randomized…
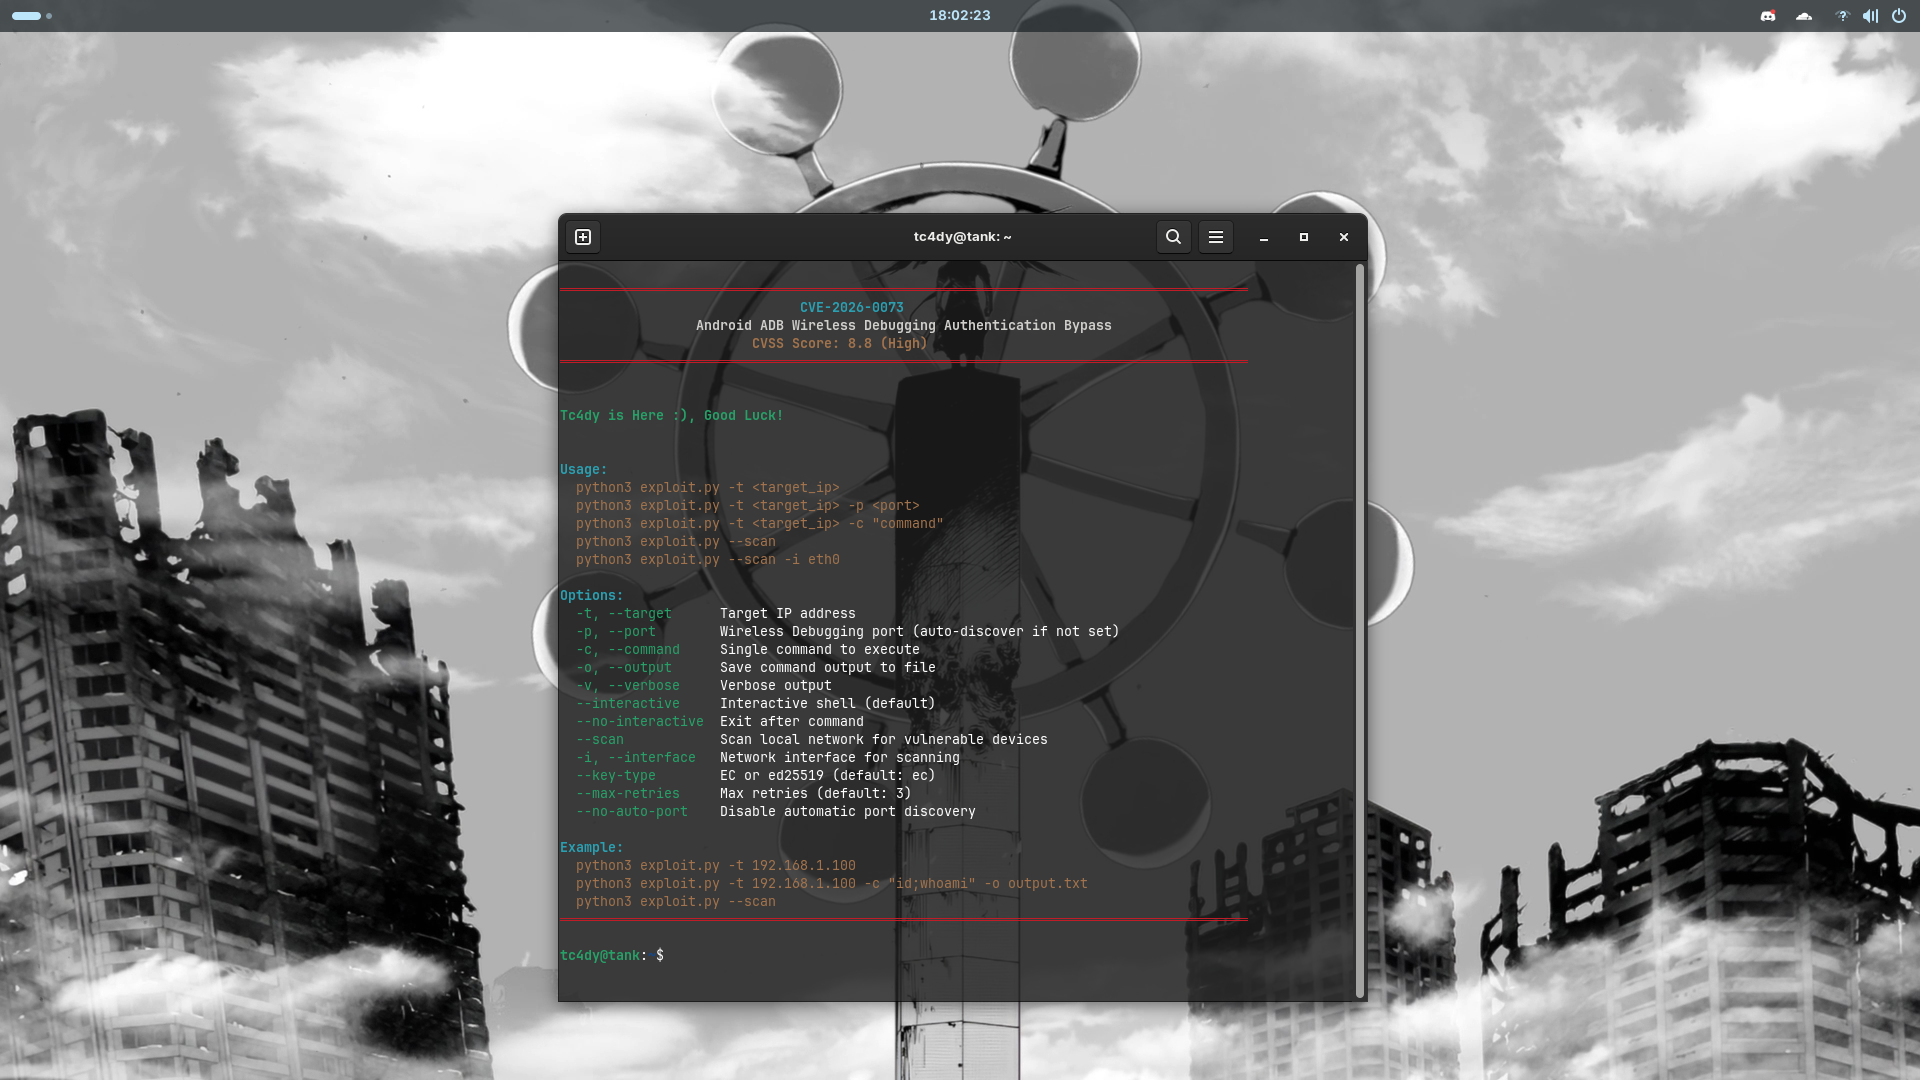 tc4dy/cve-2026-0073-poc-exploit
Zero-click authentication bypass exploit for Android ADB Wireless Debugging (CVE-2026-0073). Provides interactive shell, command execution, and…
 rev-code/androidclient
Android remote administration client
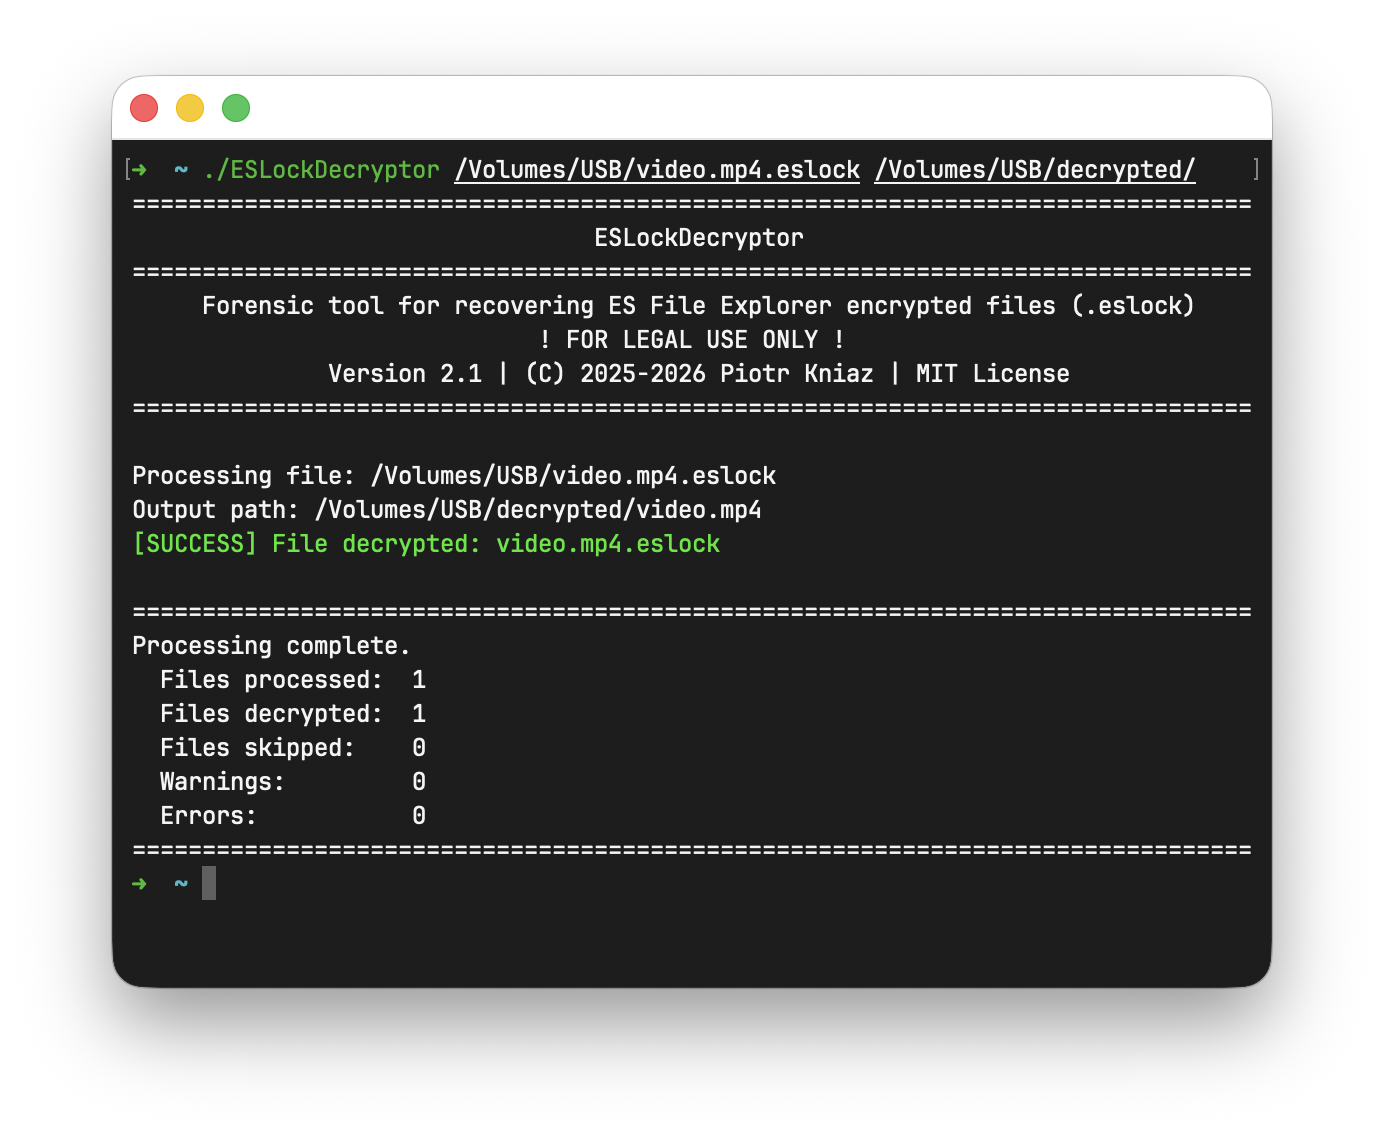 piotr-kniaz/eslockdecryptor
Utility for recovering ES File Explorer encrypted files (.eslock)