

 1-3-7/disrobe
Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
 sysnets/atfuzzer
Grammar-guided evolutionary fuzzer for dynamic analysis of AT command interfaces on Android smartphones via Bluetooth and USB, uncovering DoS,…
 census/whatsapp-mitd-mitm
PoC and tools for exploiting CVE-2020-6516 (Chrome) and CVE-2021-24027 (WhatsApp)
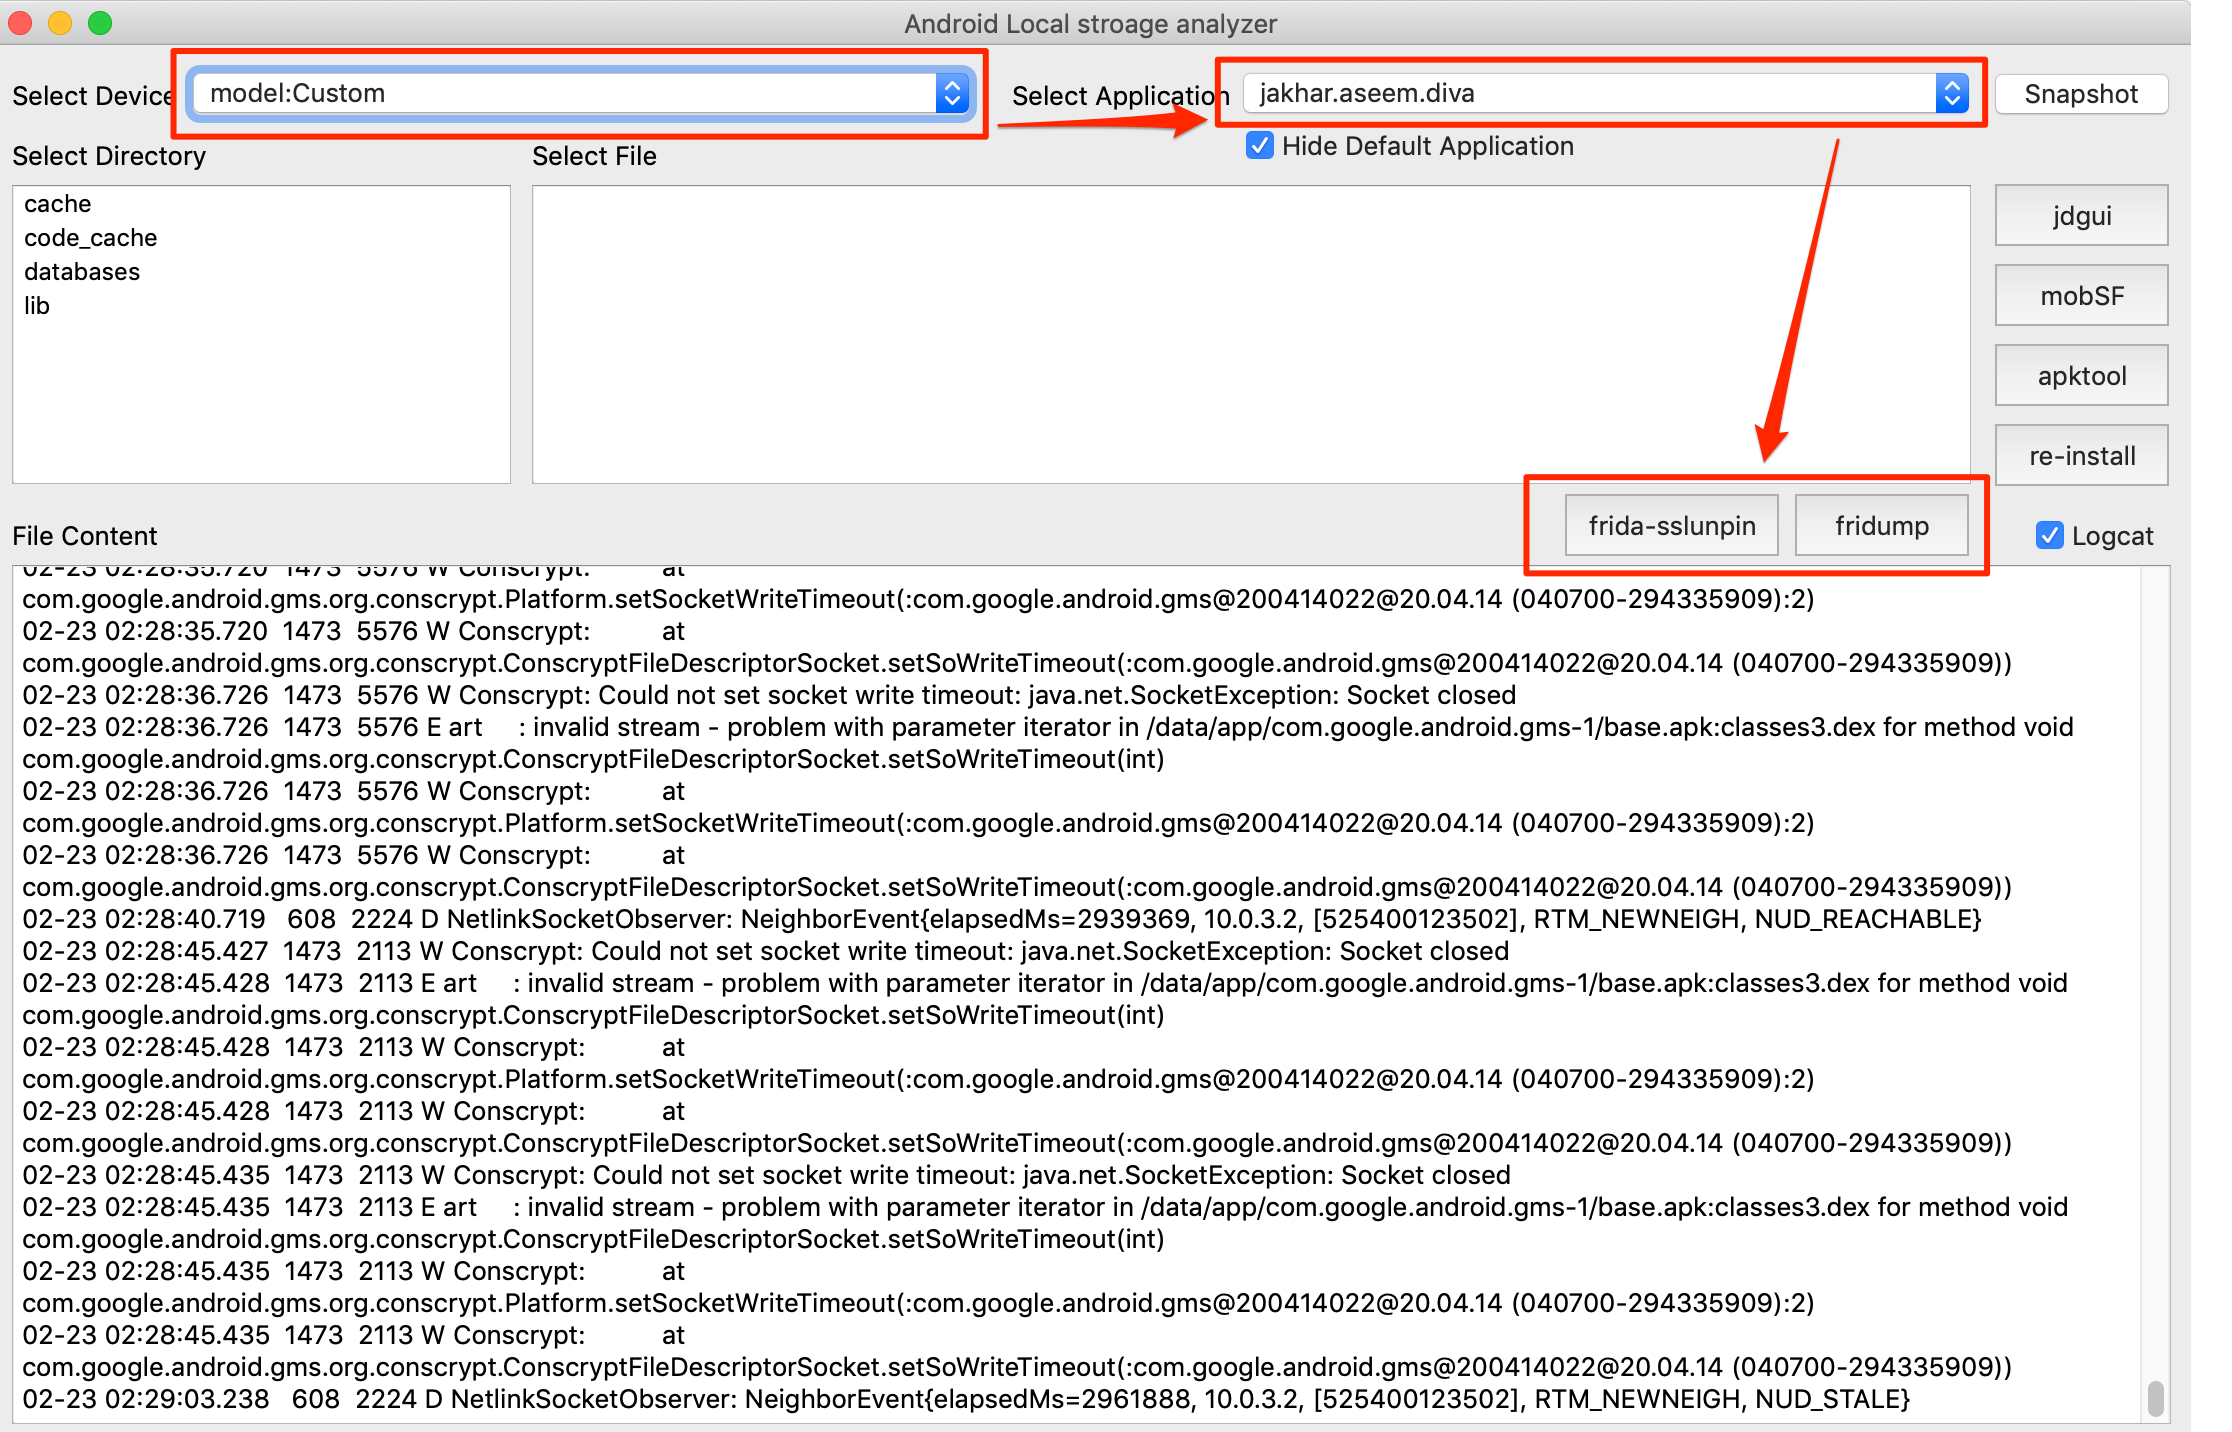 notsosecure/android_application_analyzer
The tool is used to analyze the content of the android application in local storage.
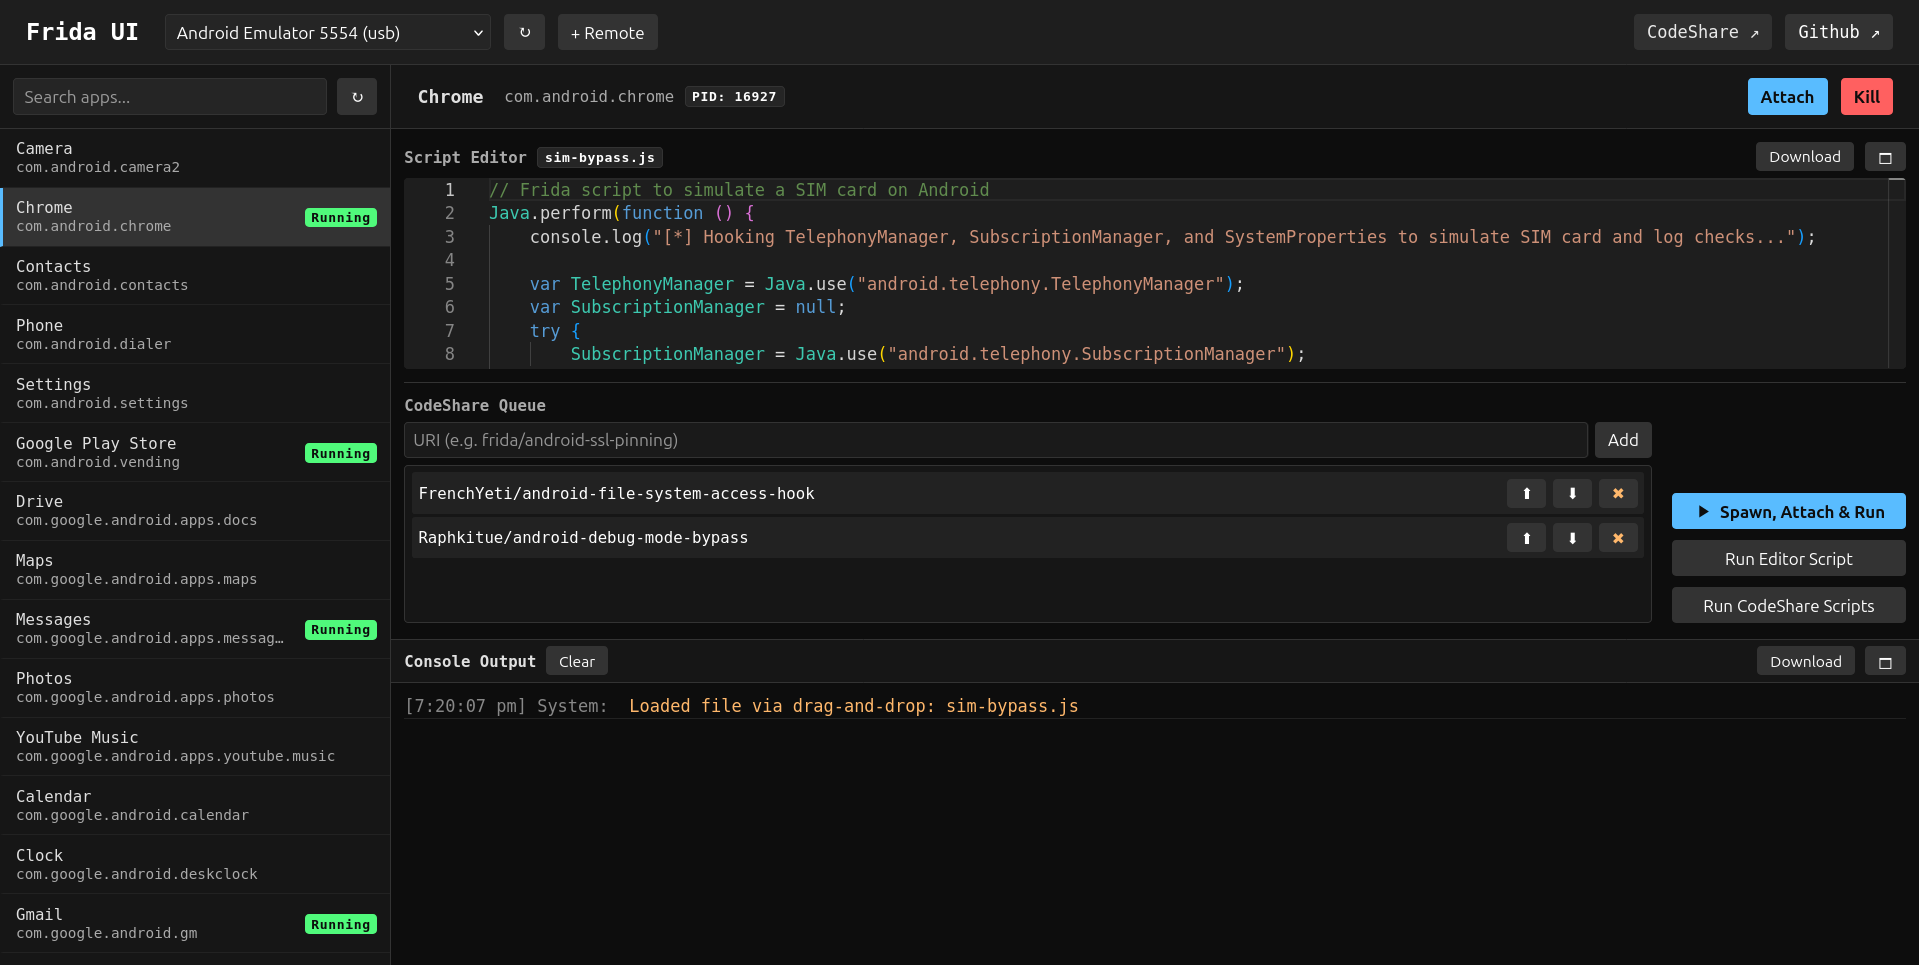 adityatelange/frida-ui
Interact with Frida devices, processes, and scripts directly from your browser.
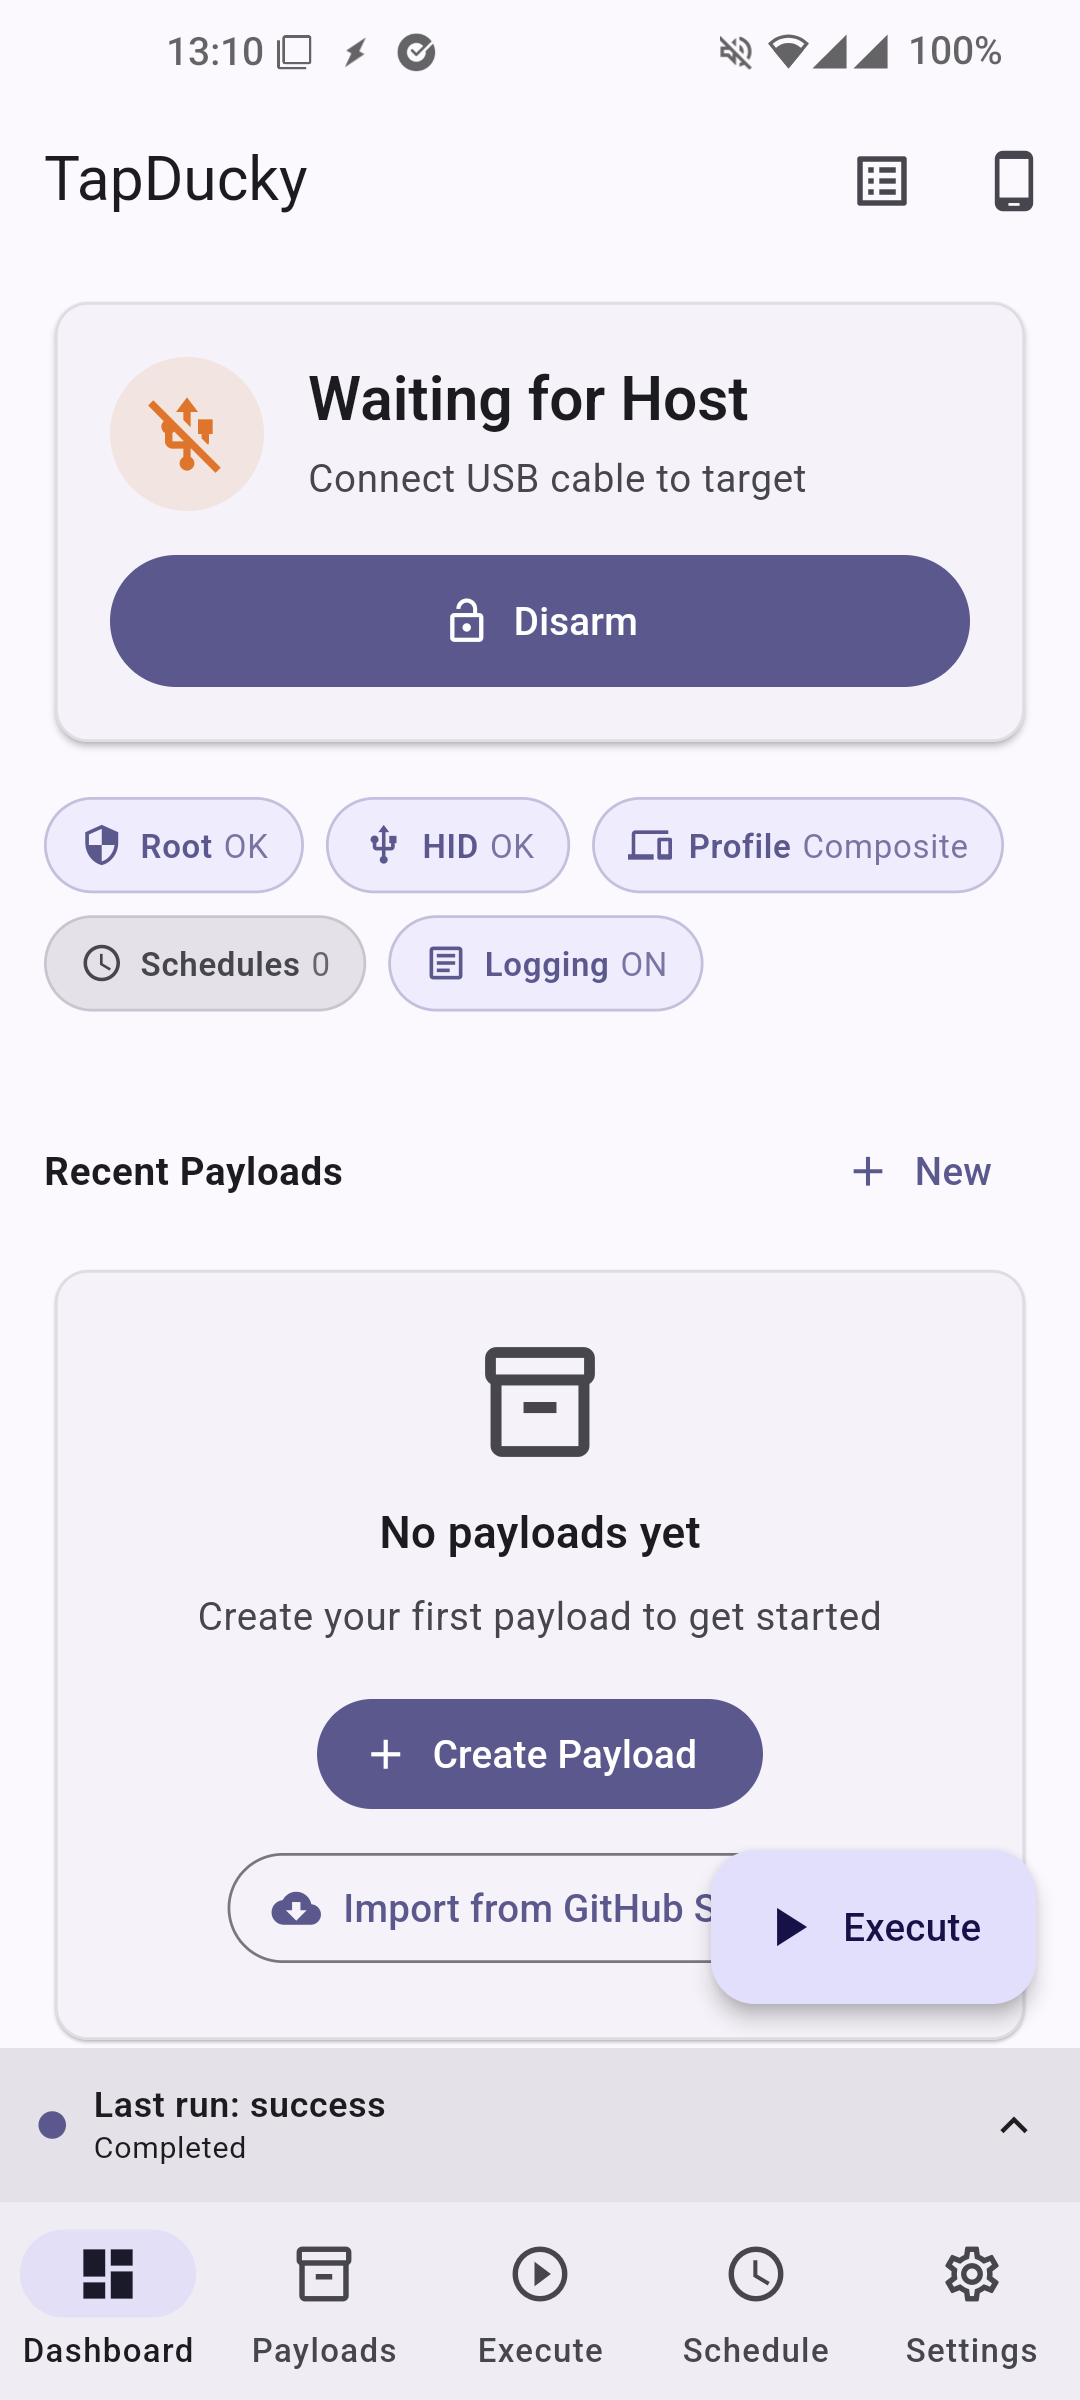 iodn/tap-ducky
Turns any rooted phone into the legendary USB Rubber Ducky. Android USB HID Keystroke Injector
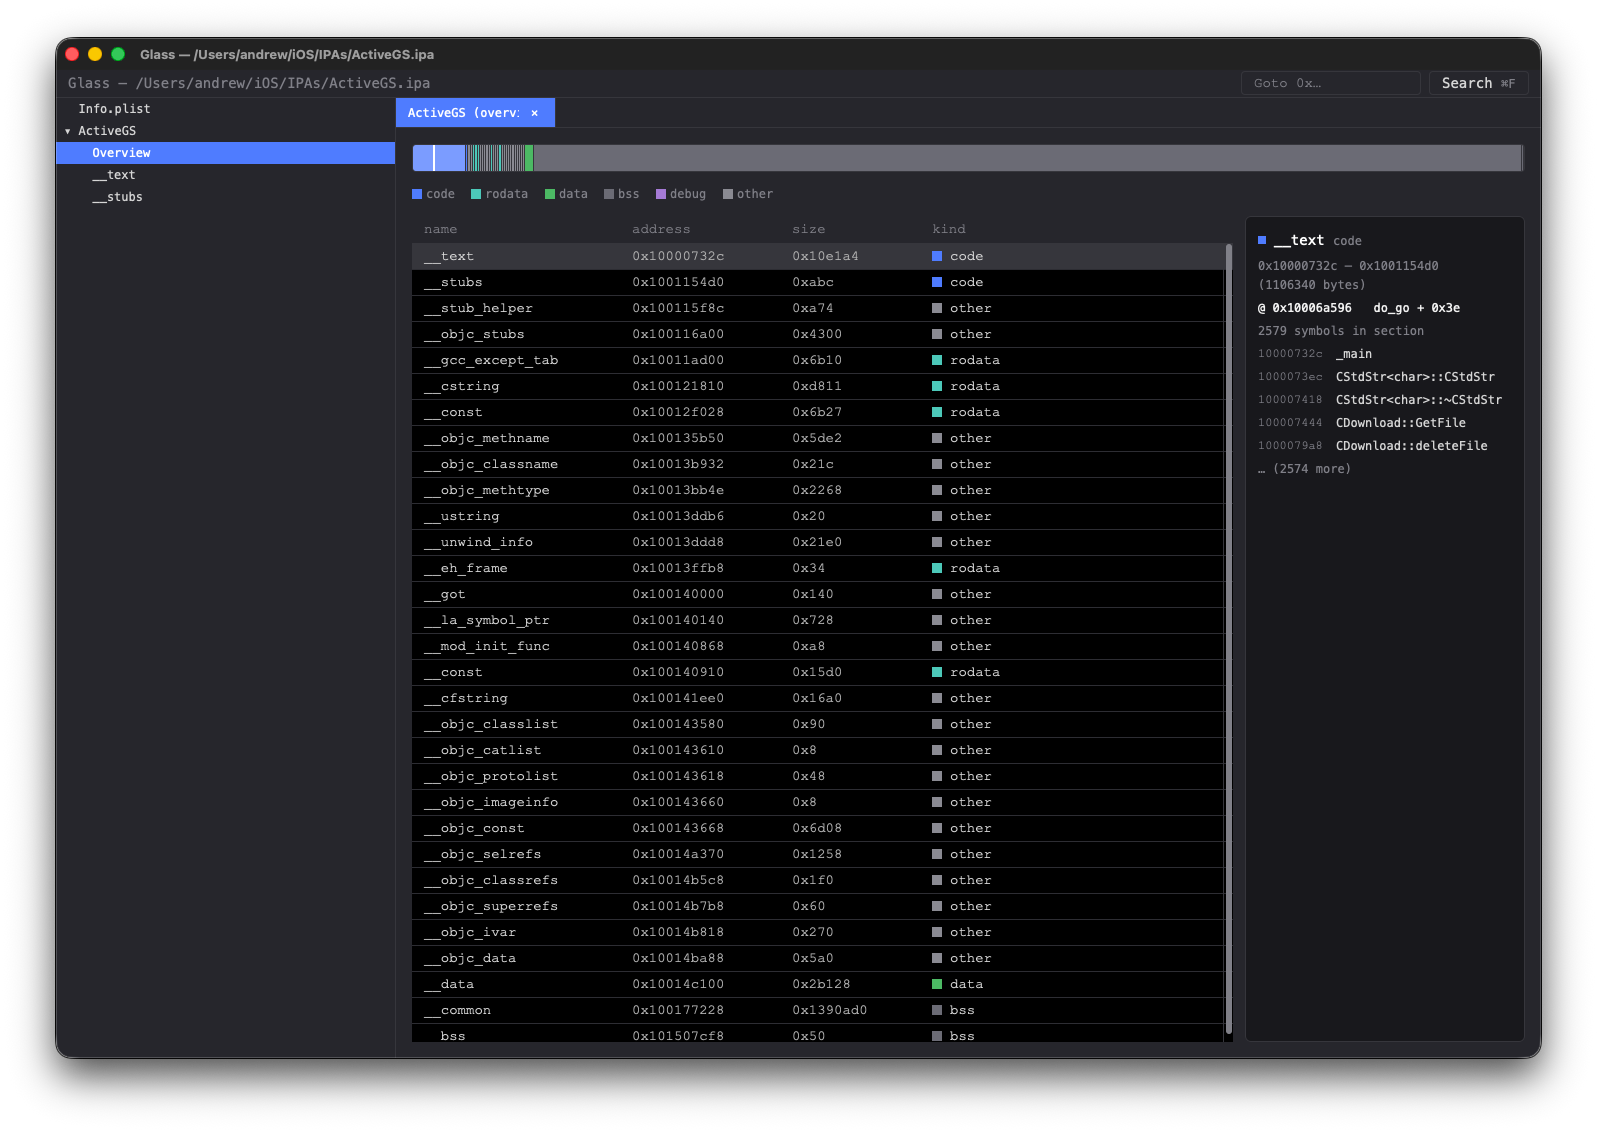 azw413/glass
Glass - a fast and free IDA Pro alternative
 r0rt1z2/automatedroot
Root your MediaTek device with CVE-2020-0069
 maldroid/maldrolyzer
Simple framework to extract "actionable" data from Android malware (C&Cs, phone numbers etc.)
 user1342/obfu-de-scate
Fuzzy comparison tool for deobfuscating Android APKs by identifying renamed functions across versions, generating mapping files and interactive HTML…
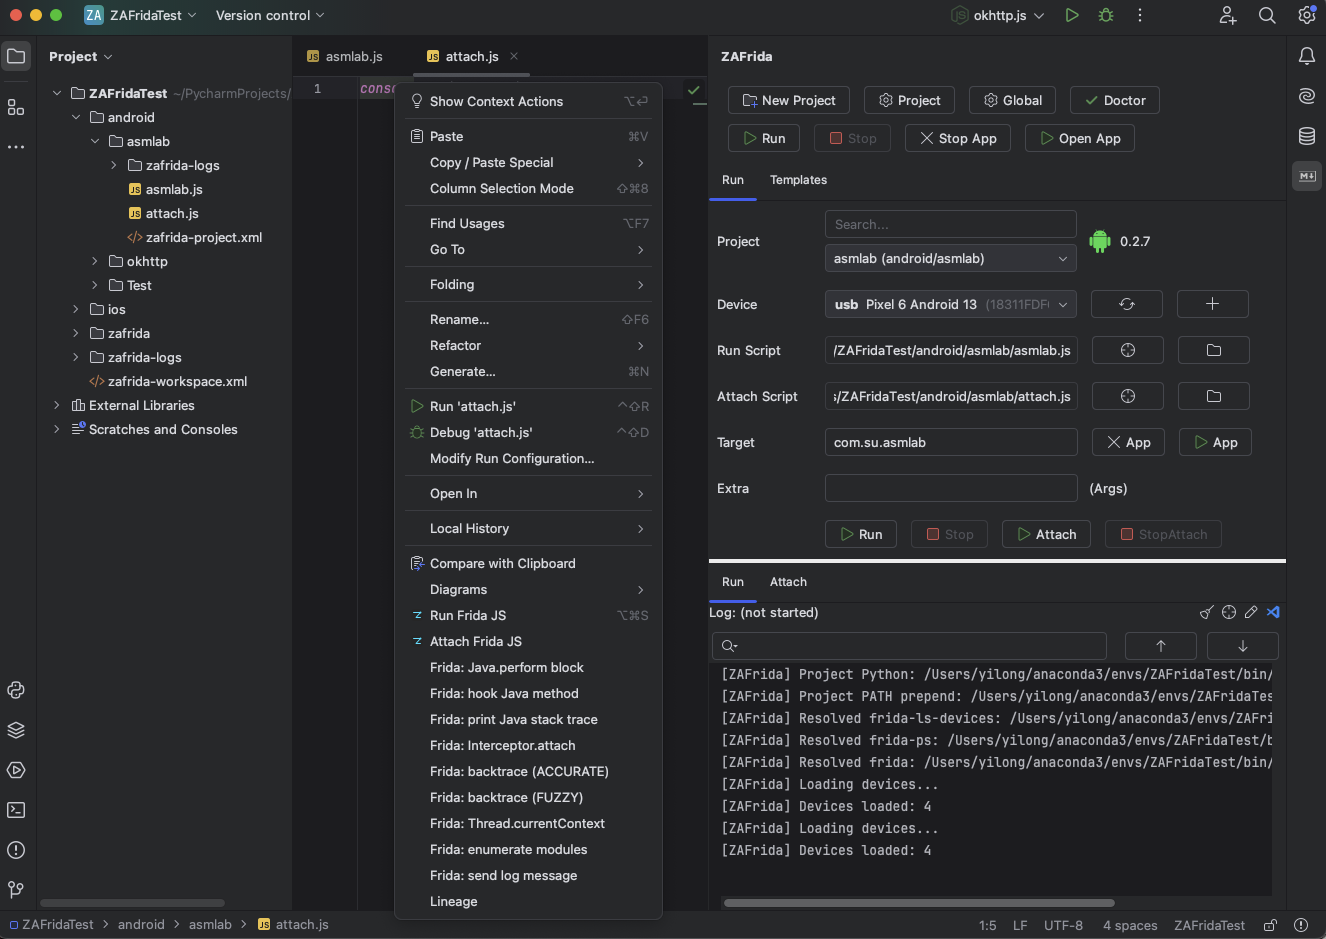 yilongmd/zafrida-ui
A Frida UI tool window inside PyCharm / JetBrains IDEs.
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
 federicodotta/ghidra2frida
Ghidra extension bridging static and dynamic analysis via Frida, enabling scriptable runtime instrumentation for reverse engineering binaries on…
 kasnria001/pwnage24mtk
Cert exploit for MTK devices.There is a logic flaw in MTK cert verification process.Similar to CVE-2023-20696.
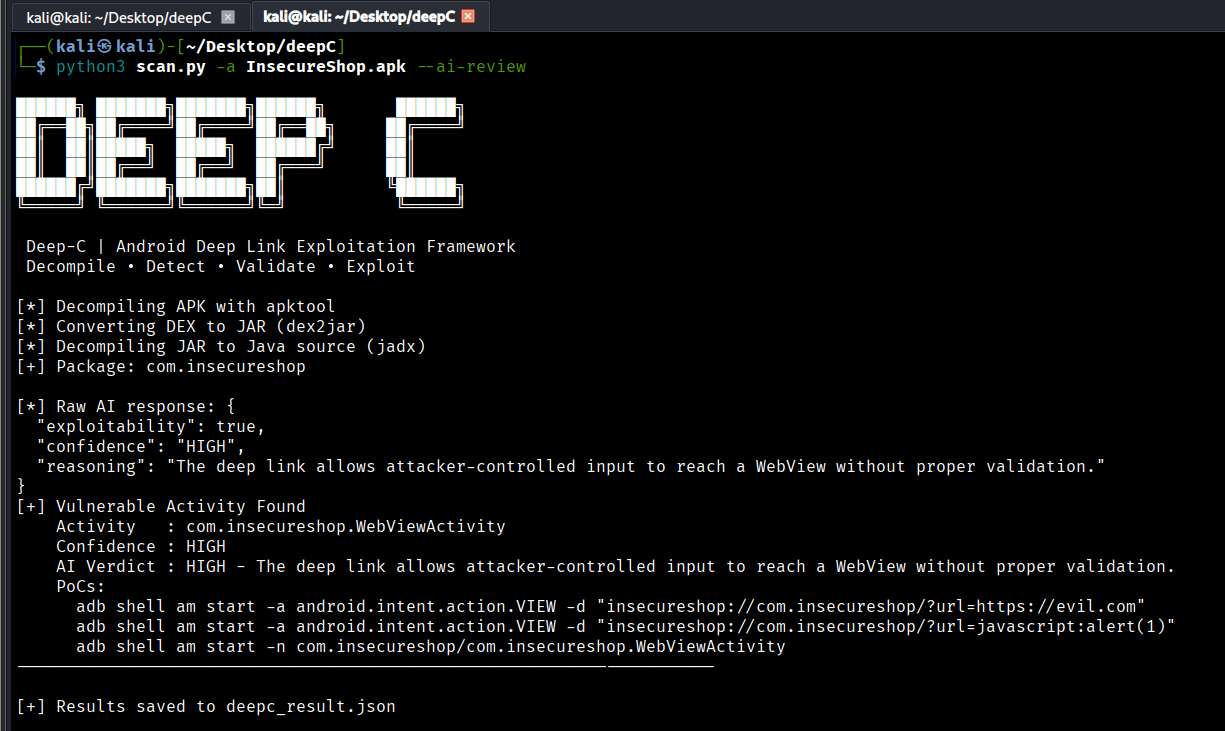 kishorbal/deep-c
Android deeplink misconfiguration detector and exploitation tool
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 donctl/sandy
Release of the sandy framework.