
frameworks_av_CVE-2023-20933
 trinadh465/frameworks_av_cve-2023-20933
Exploit or patch for Android media framework vulnerability CVE-2023-20933, targeting frameworks_av component.
android-securitybinary-exploitationexploitation+2
trinadh465/frameworks_av_cve-2023-20933Exploit or patch for Android media framework vulnerability CVE-2023-20933, targeting frameworks_av component.
 likekabin/cve-2017-0478
Proof-of-concept exploit for CVE-2017-0478, a remote code execution vulnerability in Android's mediaserver via crafted WebP images. Includes…
 satheesh575555/frameworks_native_aosp10_r33_cve-2020-0392
Exploit code and analysis for CVE-2020-0392, a vulnerability in Android's frameworks_native component, targeting AOSP 10 r33.
 nanopathi/packages_apps_nfc_cve-2020-0453
Exploit for CVE-2020-0453 targeting Android NFC stack vulnerability, enabling local privilege escalation via crafted NFC packets.
 pazhanivel07/hardware_interfaces-a10_r33_cve-2021-0510
Exploit or analysis code for CVE-2021-0510, a vulnerability in Android hardware interfaces, targeting A10_r33 builds.
 pazhanivel07/frameworks_base_cve-2020-0209
Android framework base repository containing proof-of-concept exploit code for CVE-2020-0209, a privilege escalation vulnerability in Android's…
 ratiros01/cve-2014-8609-exploit
Proof-of-concept exploit for CVE-2014-8609, demonstrating Android pending intent vulnerability exploitation for security research and mobile…
 trinadh465/platform_frameworks_base_cve-2023-20918
Repository dedicated to CVE-2023-20918, an Android framework vulnerability, providing analysis and potential patch or exploit research for Android…
 sahalll/cve-2024-50657
Provides a proof-of-concept exploit for CVE-2024-50657, an incorrect access control vulnerability in Owncloud Android app, demonstrating passcode…
 0xkol/badspin
Bad Spin: Android Binder Privilege Escalation Exploit (CVE-2022-20421)
 koozxcv/cve-2014-7911-cve-2014-4322_get_root_privilege
CVE-2014-7911 vulnerability and CVE-2014-4322 vulnerability to get root privilege!
 secmob/cve-2015-6612
Proof-of-concept exploit for Android CVE-2015-6612, demonstrating a privilege escalation vulnerability with a working PoC for security research and…
 smiletablabo/cve-2022-46395
Exploit for CVE-2022-46395, an Arm Mali kernel driver vulnerability, achieving arbitrary kernel code execution to disable SELinux and gain root on…
 koharin/cve-2020-0041
Exploit for CVE-2020-0041, an Android kernel privilege escalation vulnerability in the Binder driver, enabling local root access.
 supersonic/cve-2022-20494
Exploit app for CVE-2022-20494, a high severity permanent denial-of-service vulnerability that leverages Android's DND (Do not disturb) feature
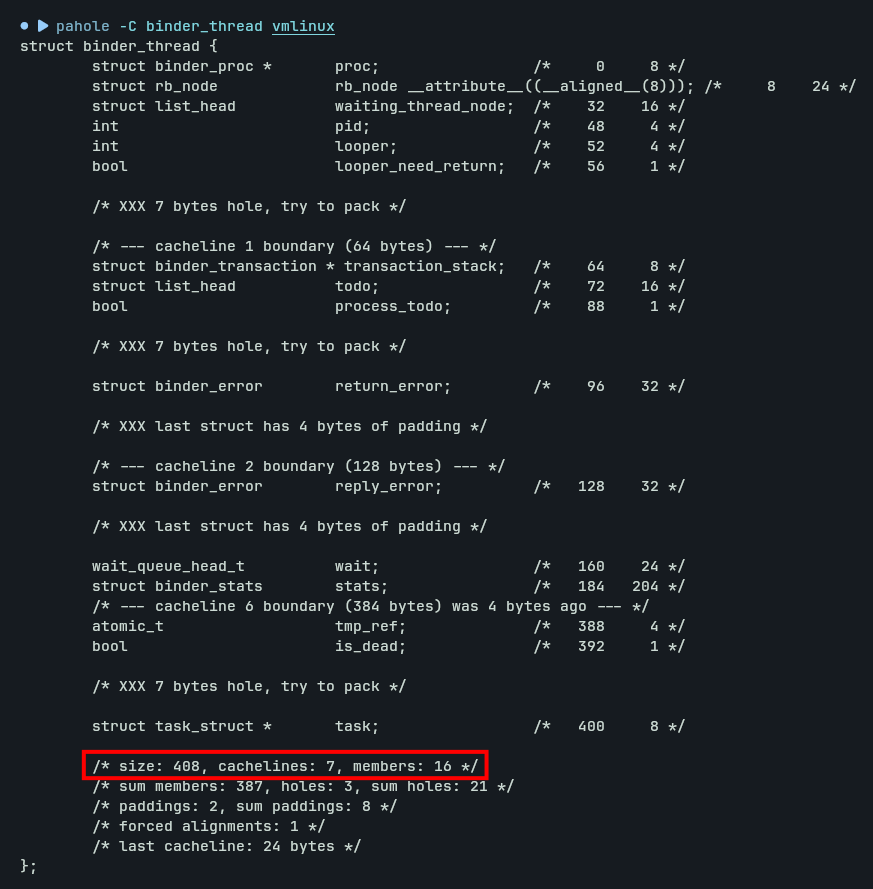 0xbinder/cve_2019_2215
Proof-of-concept LPE exploit for Android Binder UAF that uses iovec spraying and addr_limit overwrite to achieve arbitrary kernel read/write.
 absholi7ly/poc-for-cve-2024-7014-exploit
Proof of Concept (PoC) for CVE-2024-7014 (EvilVideo) Exploit
 timwr/cve-2019-2215
Android kernel privilege escalation exploit for CVE-2019-2215, providing a proof-of-concept to achieve root access via a use-after-free vulnerability…