
CVE-2023-27703
 happy0717/cve-2023-27703
CVE-2023-27703 An Android version of pikpak version V1.29.2 element debugging interface leakage vulnerability
android-securityinformation-gatheringmobile-security+2
3
happy0717/cve-2023-27703CVE-2023-27703 An Android version of pikpak version V1.29.2 element debugging interface leakage vulnerability
 lienby/pssroot
One-Click-Root program based on CVE-2016-5195, that works on the old 'PlayStation Certified' android devices
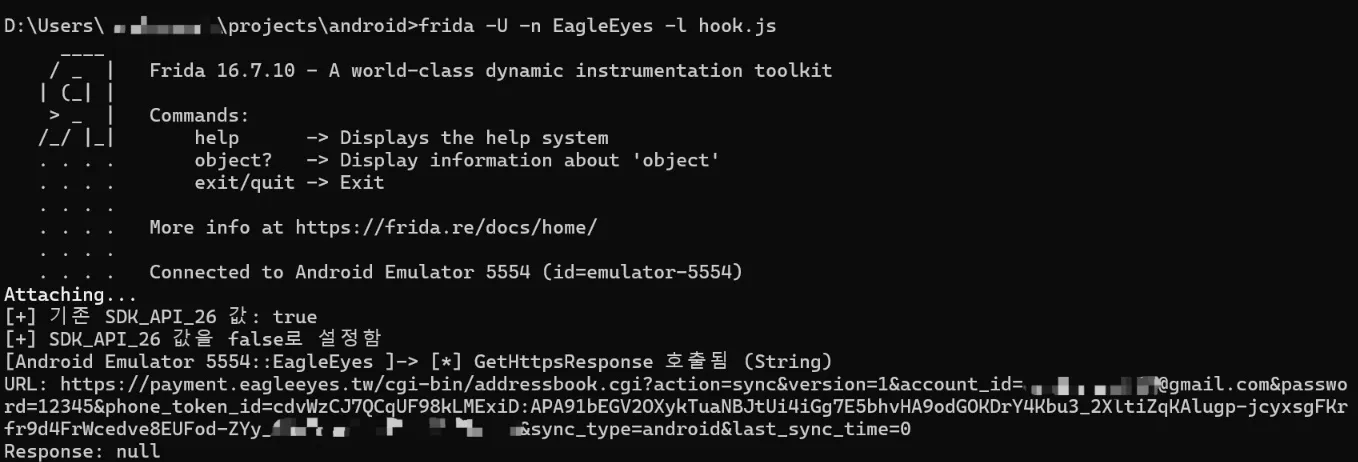 shinycolumn/cve-2025-46408
Improper Hostname Verification in EagleEyes Lite Android Application
 fredevsec/cve-2026-0073
0-Click RCE Android Adb TLS Wireless Debugging
 onesmiledx/cve-2026-43499
A modified method to root Android device with locked bootloader via new exploit. (Only for Samsung now or smthing like that devices cuz i ported it…
 purseclab/cve-2023-33768
DoS against Belkin smart plugs via crafted firmware injection
 iwallplace/cve-2026-26897-ecoonline-deeplink
Public advisory & PoC for CVE-2026-26897 — Deep Link Bypass in EcoOnline EHS Android (com.airsweb.v10), fixed in 0.2.500
 xqi1337/cve-2026-0073-android-adbd-bypass-poc
CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…
 a1lin/cve-2022-1364
Proof-of-concept exploit for CVE-2022-1364 targeting Chromium-based Bromite on Android (arm_ChromePublic.apk), demonstrating a browser memory-safety…
 actuator/ekoparty
Ekoparty Miami | Interface Anti-Patterns: Exploiting Insecure Navigation in 3rd Party Android App Lockers
 xckevin/androidwebviewinjectdemo
An app demo for test android webview security issue: CVE-2012-6636
 aureliusivaninvenioptl/ubl-itel-s23
Unlock Bootloader for Itel S23 (S665L) / Unisoc T606 using CVE-2022-38694

 actuator/com.phlox.tvwebbrowser
CVE-2023-43955
 mazx0p/cve-2014-8609-poc
pendingintent vulnerability
 shinycolumn/cve-2025-50944
Improper Certificate Chain Validation in EagleEyes Lite Android Application
 edwins907/xiaomi-cve-2024-45352
Reporte técnico sobre vulnerabilidad crítica de Xiaomi
 aymankhalfatni/cve-2017-0785
CVE-2017-0785: BlueBorne PoC