CVE-2026-43499-aristotle-apk

Android kernel exploit for CVE-2026-43499 (Futex-PI use-after-free) that gains temporary root on Xiaomi XIG04 to enable ADB. Includes automated…

Android kernel exploit for CVE-2026-43499 (Futex-PI use-after-free) that gains temporary root on Xiaomi XIG04 to enable ADB. Includes automated…

CVE-2019-5700

Bootloader unlock (CVE-2022-38694) & root guide for Realme C53 / RMX3760 (Unisoc T612)

a vulnerability affecting Android version 12 & 13

CVE-2022-40297 - Proof of Concept: Privilege escalation in Ubuntu Touch 16.04 - by PIN Bruteforce

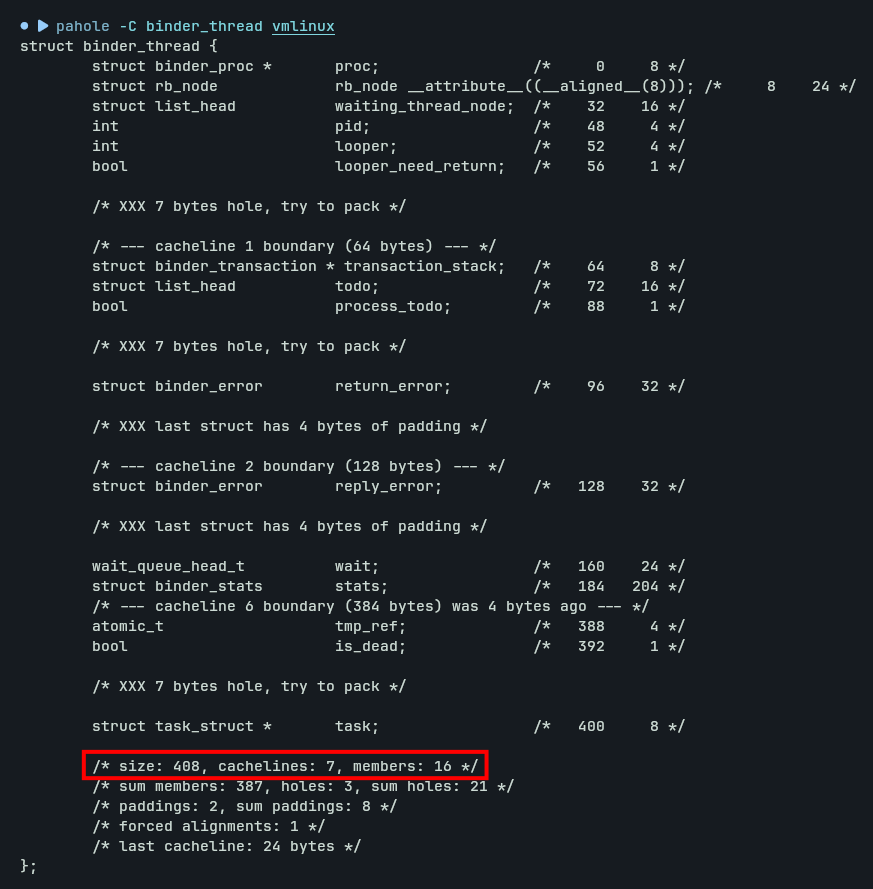
Proof-of-concept LPE exploit for Android Binder UAF that uses iovec spraying and addr_limit overwrite to achieve arbitrary kernel read/write.

This package is not a complete root. It flips SELinux to Permissive and holds reclaim long enough for follow-on work. Host `uid=0` is not achieved…

CVE-2026-43499 futex PI stack UAF ???????? - Android GKI 6.1~6.12 ??????? pselect() + futex PI ????????????,??? root ??? SELinux??? OPPO Find…

Exploit for CVE-2019-2215 (bad binder) for Huawei P20 Lite

Local privilege escalation exploit for Redmi K50G/POCO F4 GT using CVE-2026-43499 (futex UAF) to gain temporary root and load KernelSU without…

PoC of StrandHogg2 (CVE-2020-0096)

Complete RMGP (CVE-2026-43499) workspace + experiment-state handoff for SM-A376B/A376BXXU1AZB7

Generates per-device kernel offsets from boot.img and compiles a preload library to exploit CVE-2026-43499 Android arm64 local privilege escalation.

vivo X200 设备端一键 root App(Shizuku 授权 shell 域执行,CVE-2026-43499)

CVE-2016-5195 dirtycow by timwr automated multi file patch tool

Local privilege escalation exploit for Android Binder bug CVE-2020-0041 (Pixel 3a)

CVE-2022-38181 POC for FireTV 3rd gen Cube (gazelle)

This is a critical UAF vulnerability exploit that affected the android binder IPC system used in the wild and discovered by P0