

rasputin
 frenchyeti/rasputin
Ressources and papers related to my conferences and work on (un)RASPs. These work is in progress, please be patient :) Don't hesitate to contribute /…
android-securitybinary-analysiscurated-resources+4
62
frenchyeti/rasputinRessources and papers related to my conferences and work on (un)RASPs. These work is in progress, please be patient :) Don't hesitate to contribute /…
 bugel/cve-2026-43499-m3q-azf1
This package is not a complete root. It flips SELinux to Permissive and holds reclaim long enough for follow-on work. Host `uid=0` is not achieved…
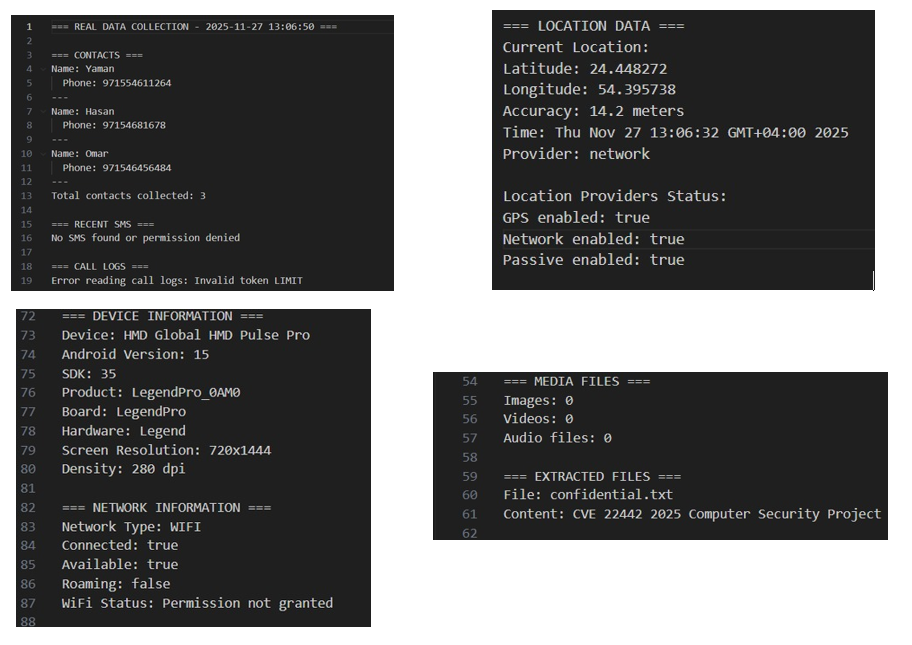 hasan-al-hussein/android-workprofile-exploit
Controlled defensive analysis of CVE-2025-22442 work-profile provisioning, policy timing, and enterprise isolation.
 wired0ut/cve-2020-0423
An exploit to CVE-2020-0423, which is a Binder deffered work UAF.
 lienby/pssroot
One-Click-Root program based on CVE-2016-5195, that works on the old 'PlayStation Certified' android devices
 sparrow-labz/cve-2020-0423
Researching CVE published originally by longterm.io
 sparrow-labz/cve-2020-11179-adreno-qualcomm-gpu
Productization efforts of CVE-2020-11179 Adreno-Qualcomm-GPU bug, original poc by Ben Hawkes of P0
 scs-labrat/android_autorooter
Exfiltrate sensitive user data from apps on Android 12 and 13 using CVE-2024-0044 vulnerability remotely
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
 pxb1988/dex2jar
Tools to work with android .dex and java .class files
 bluepigeonproject/blue-pigeon
Blue Pigeon is a Bluetooth-based data exfiltration and proxy tool to enable communication between a remote Command and Control (C2) server and a…
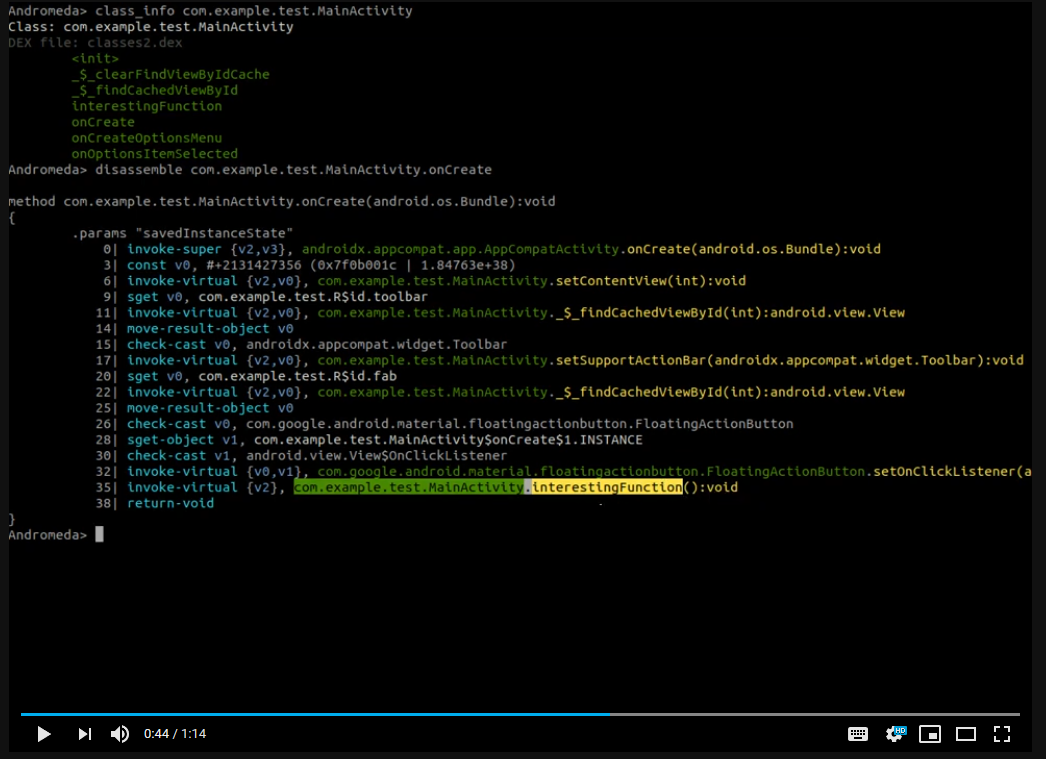 secrary/andromeda
C/C++ interactive reverse engineering tool for Android applications, enabling fast static analysis and binary inspection of APK files.
 santoku/santoku-linux
Linux Distro for Mobile Security, Malware Analysis, and Forensics